

An email says your car used an Austrian motorway without a valid vignette. It offers a surprisingly small payment to put things right.
The ASFINAG vignette email scam wraps that offer in official-looking language. Before dealing with it, take a closer look at the demand.
Overview
The small amount is part of the lure
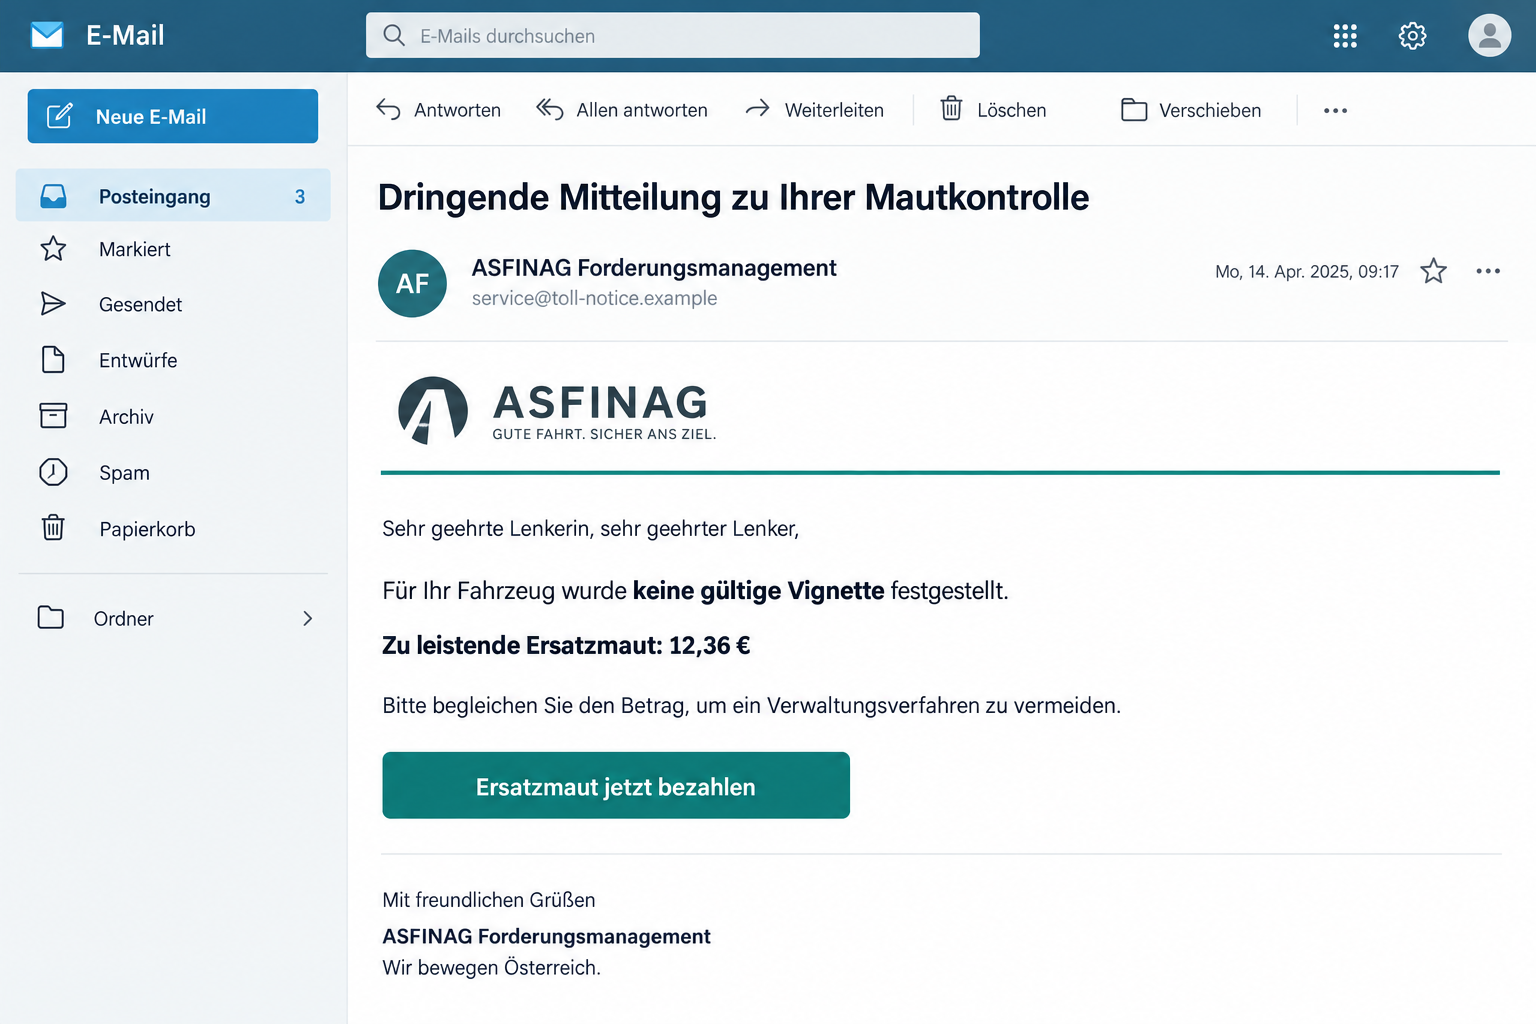
The message claims a missing vignette can be settled for €12.36. It gives you a convenient button and a reason not to postpone payment.
That convenience hides the real problem: an impostor is using a toll-enforcement story to collect information through a phishing destination.
ASFINAG has explicitly disowned the emails
In its June 2026 warning, ASFINAG described a nationwide wave of fake notices and identified personal and card details as targets.
The road operator isn’t offering this settlement. Its name and design are being used to give the message authority it doesn’t have.
A false email and a real toll issue are different matters
Receiving this demand doesn’t establish that you drove without a vignette. Equally, recognizing phishing doesn’t resolve an unrelated genuine enforcement notice.
- Don’t use the email’s payment button or provide a card to its form.
- Check any genuine toll question through ASFINAG’s independently located channels.
- If a card was exposed, contact its issuer rather than waiting for an ASFINAG refund.
- Preserve evidence of the fraudulent demand without reopening the payment destination.
The lead image illustrates the email’s pretext. Its interface details aren’t an authentic record of an enforcement case or a particular delivery date.
Why Drivers Can Mistake It for a Real Notice
A road trip leaves plenty of small things to remember. Which route did you take? When did the vignette begin? Was the number plate entered correctly?
An unexpected message can turn those ordinary uncertainties into a reason to pay quickly. The reader starts checking their memory instead of checking the sender.
That’s especially effective after travel, when receipts, bookings and fuel payments are still arriving. Another administrative email doesn’t feel out of place.
The low amount changes the calculation. You might decide it’s easier to settle than to work out whether the journey details make sense.
But the price in the email isn’t the size of the information request. A small alleged balance can still lead to full card details.
The message also benefits from a real background fact: Austria does have toll requirements. Scammers don’t need to invent a completely unfamiliar institution.
They instead attach a false collection route to a real subject. The familiar road operator’s name becomes a shortcut around proper verification.
If you’ve never used those roads, that’s an obvious contradiction. If you have, you still need an independent check rather than a payment made from memory.
How the ASFINAG Vignette Email Scam Works
Step 1: A supposed toll problem arrives in the inbox
The email presents an enforcement issue as something already detected. It asks the recipient to respond to an accusation, not consider an optional offer.
That framing can make an innocent driver feel they must explain themselves. You don’t owe an unverified sender that explanation.
A label such as ASFINAG collection management can sound convincing in an email reader. It isn’t an independently authenticated department.
Read the actual sender address, but don’t let one familiar-looking field settle the question. The request needs to make sense through the genuine service too.
Don’t reply with a number plate, journey date or vignette receipt. Those details belong in a legitimate inquiry, not a conversation with an unknown sender.
Keep your receipt privately. It can help you investigate a genuine toll concern without feeding extra context to the impersonator.
Step 2: A cheap settlement is paired with a larger threat
The offer gives you an apparent escape from a worse outcome. Paying a modest amount is made to feel sensible compared with a formal proceeding.
Urgency matters here because a pause could lead you to the real road operator. The email wants its convenient payment route to remain your first choice.
Watch the relationship between the two claims: a serious violation is supposedly solved by a quick, unusually cheap online action.
The wording doesn’t make that route legitimate. References to administrative authorities are statements inside the suspicious message, not proof that a case exists.
Nor should you treat an email deadline as a verified legal deadline. If real correspondence exists, check its instructions independently.
You can leave the message untouched while contacting ASFINAG. A scammer’s demand for speed isn’t a reason to surrender the right to verify.
Step 3: The button moves the problem to a payment page
The browser is where the recipient may stop thinking about verification and start completing a task. A polished form encourages that change.
It can display the same operator name and a payment heading, while a different party controls the fields underneath.
An Austrian government cyber-safety alert documented autobahnen-asfinag.eu as one destination used by a related variant.
That is a documented example, not a safe address to visit. A different hostname can carry the same pretext after earlier links stop working.
Don’t use a stopped or unavailable page as reassurance that the original demand was genuine. Availability doesn’t authenticate a message.
A working form can still take your details for someone else. Ask ASFINAG about the demand before treating its checkout as an authorized toll service.
Step 4: The form seeks more than the advertised fee
Contact information and card details can outlast the tiny payment story. Once supplied, they may be used in attempts unrelated to a vignette.
A card request exposes a payment instrument, not just the amount shown beside a button. Don’t assume €12.36 caps the possible consequences.
If a banking confirmation appears, inspect it separately. A displayed merchant, amount or action that doesn’t match your intention is a reason to stop.
The documented warning doesn’t establish an identical authorization sequence for every victim. Tell the issuer exactly which prompts appeared in your case.
You may receive an error or no useful receipt. Neither tells you whether the form already captured what you entered.
At that point, leave the page and move to the issuer’s genuine support route. Another attempt to finish payment adds risk, not certainty.
What This Warning Does and Doesn’t Say About ASFINAG
ASFINAG operates Austria’s motorway toll system. This article concerns a counterfeit email demand, not an accusation that its real toll rules are fraudulent.
Drivers can have genuine disputes about a vignette, registration detail or enforcement decision. Those need the real operator’s process and their own supporting records.
A phishing form isn’t an appeal channel. It can’t reliably tell you whether the car was checked or whether a replacement toll is owed.
Don’t send a genuine letter, receipt or identity document to the email’s alleged caseworker to prove you already paid.
Instead, use contact information obtained from the operator’s established website. Explain that you want to verify a notice before sending additional details.
If you hold real enforcement correspondence, keep its reference distinct from the phishing email. Combining them can make a false demand seem connected.
The scam doesn’t require an actual roadside incident. The inbox message supplies its own story, which is precisely why memory alone isn’t enough.
A Safer Way to Check a Vignette Question
Bring your own record, not the email’s button
Locate the purchase receipt or confirmation you already hold. Note the registration, product and validity period before seeking an explanation.
That gives you concrete questions for the operator. It doesn’t require sharing your banking password or testing the suspicious checkout.
If the vehicle was rented, ask the rental company through your existing booking contact what documentation applies. Don’t trust an address supplied by the unexpected demand.
A rental or company car can complicate who receives legitimate correspondence. Resolve that ownership question separately from whether this email’s link is safe.
Don’t turn a scam warning into an excuse to ignore real mail
If a genuine notice exists, preserve it and check the appropriate response time with the operator. This article can’t determine your individual toll liability.
The right distinction is between refusing an unverified online collection attempt and addressing a verified transport matter.
When you’re unsure, ask the genuine service to identify the proper channel. Avoid searching for a payment portal using the suspicious email’s exact domain.
A search can lead you back to the same imitation. Start from the institution, then find the relevant account or support page.
Check card activity without using the phisher’s reassurance
Open your banking app independently and review what actually happened. A website saying payment failed doesn’t override the issuer’s transaction information.
If nothing is visible yet, tell the issuer about the exposed details anyway. Protective action doesn’t have to wait for a posted charge.
Keep the original advertised amount alongside any actual entry. Those may differ, and that difference matters when you explain the incident.
Don’t accept an emailed refund link from the same sender as the solution. Recovery should come through the payment provider’s authenticated process.
What to Do if You Have Fallen Victim to This Scam
If the email reached a work inbox, tell the person handling travel expenses. An apparent toll charge might otherwise be paid twice by different colleagues.
Keep it out of the normal invoice queue while it is checked. A forwarded screenshot doesn’t need an instruction to process the payment.
For a shared or borrowed car, ask the driver for existing trip records privately. Don’t send a group reply containing their registration or personal details.
One person should handle the genuine operator inquiry and another the card issue if necessary. That division keeps payment protection from waiting on travel paperwork.
Make the distinction explicit in any expense note: a suspicious demand was received, not a verified toll was incurred.
-
Stop the payment attempt. Close the suspected website and decline further prompts. Don’t try another card because the first submission seemed unsuccessful.
If you only read the message, no submitted payment data needs protecting. Report it and verify any genuine road issue separately.
-
Contact your card issuer promptly. Say you used a fake ASFINAG toll page and identify the information entered.
Ask whether the card should be blocked or replaced and whether pending authorizations need attention. Use the app or a number from your existing card records.
Describe any approval, merchant name or amount shown by the bank. Don’t reduce the incident to the small figure advertised in the email.
-
Record and dispute unfamiliar transactions. Save dates, amounts, references and the issuer’s instructions for the relevant dispute route.
Be accurate about whether you entered details or approved a payment. A useful account of the event helps the provider assess what happened.
No article can promise reimbursement. Ask your issuer about deadlines and evidence requirements rather than relying on a stranger’s guaranteed recovery offer.
-
Secure any additional account information. If the site also collected a password, change it through the genuine account, including other services using the same password.
An email address or phone number alone calls for vigilance, not an assumption that all accounts are compromised. Watch for contact using the toll story.
-
Check downloads or unexpected browser permissions. If you installed something, remove it and follow appropriate cleanup instructions for the device.
A scan with Malwarebytes on a supported platform can help investigate software concerns, but it won’t cancel charges or recover card details.
AdGuard may help reduce malicious advertising exposure during later browsing. Neither tool makes a payment demand authentic.
-
Preserve the message and notify the real operator. Use ASFINAG’s official website to locate its help channels.
Include the sender, subject and destination as evidence, without making the link active for other recipients. Don’t include your full card number in a public report.
If money was lost or details were misused, report the incident to police and retain the reference with your banking case records.
-
Warn other drivers without spreading the trap. Tell travel companions or colleagues what the false demand looks like.
A screenshot or short explanation is safer than forwarding a clickable payment button. Make clear that genuine toll obligations still need proper handling.
If somebody offers paid help to erase the supposed case, verify that offer independently. The original phisher doesn’t become trustworthy by changing the sales pitch.
Frequently Asked Questions
Is the €12.36 ASFINAG email a real settlement?
No. ASFINAG has disowned the documented campaign. Don’t confuse the email’s cheap settlement story with a verified toll-enforcement process.
What if I recently drove through Austria?
Check your existing vignette records and contact the genuine operator. A plausible travel connection doesn’t authenticate an unsolicited payment destination.
Does the ASFINAG logo prove the notice is genuine?
No. A copied design isn’t authorization to collect money or card details. Verify the demand outside the email.
Can I lose more than the amount advertised?
Yes, exposed payment details can create risks beyond the bait amount. Your issuer should assess what was shared and any authorizations or transactions.
Should I ignore every replacement-toll notice?
No. Genuine notices are a separate matter. Refuse the phishing route while checking authentic correspondence through official channels.
Who should I contact if I entered my card?
Contact the card issuer first for payment protection. The real road operator can clarify toll questions but doesn’t control your card’s security.
The Bottom Line
Don’t pay through the ASFINAG vignette email scam. The €12.36 settlement story leads to an unauthorized request for sensitive information.
If you supplied a card, speak to its issuer immediately. Check any genuine vignette issue independently, without returning to the email’s payment page.








