


Your documents suddenly have unfamiliar endings, and opening them no longer works. Beside them sits a short note with a name you have never seen before.
If that name is ByteBane, take a moment before following anything the note says. The first decisions matter more than the pressure on the screen.
Overview
ByteBane changes files and leaves a ransom demand
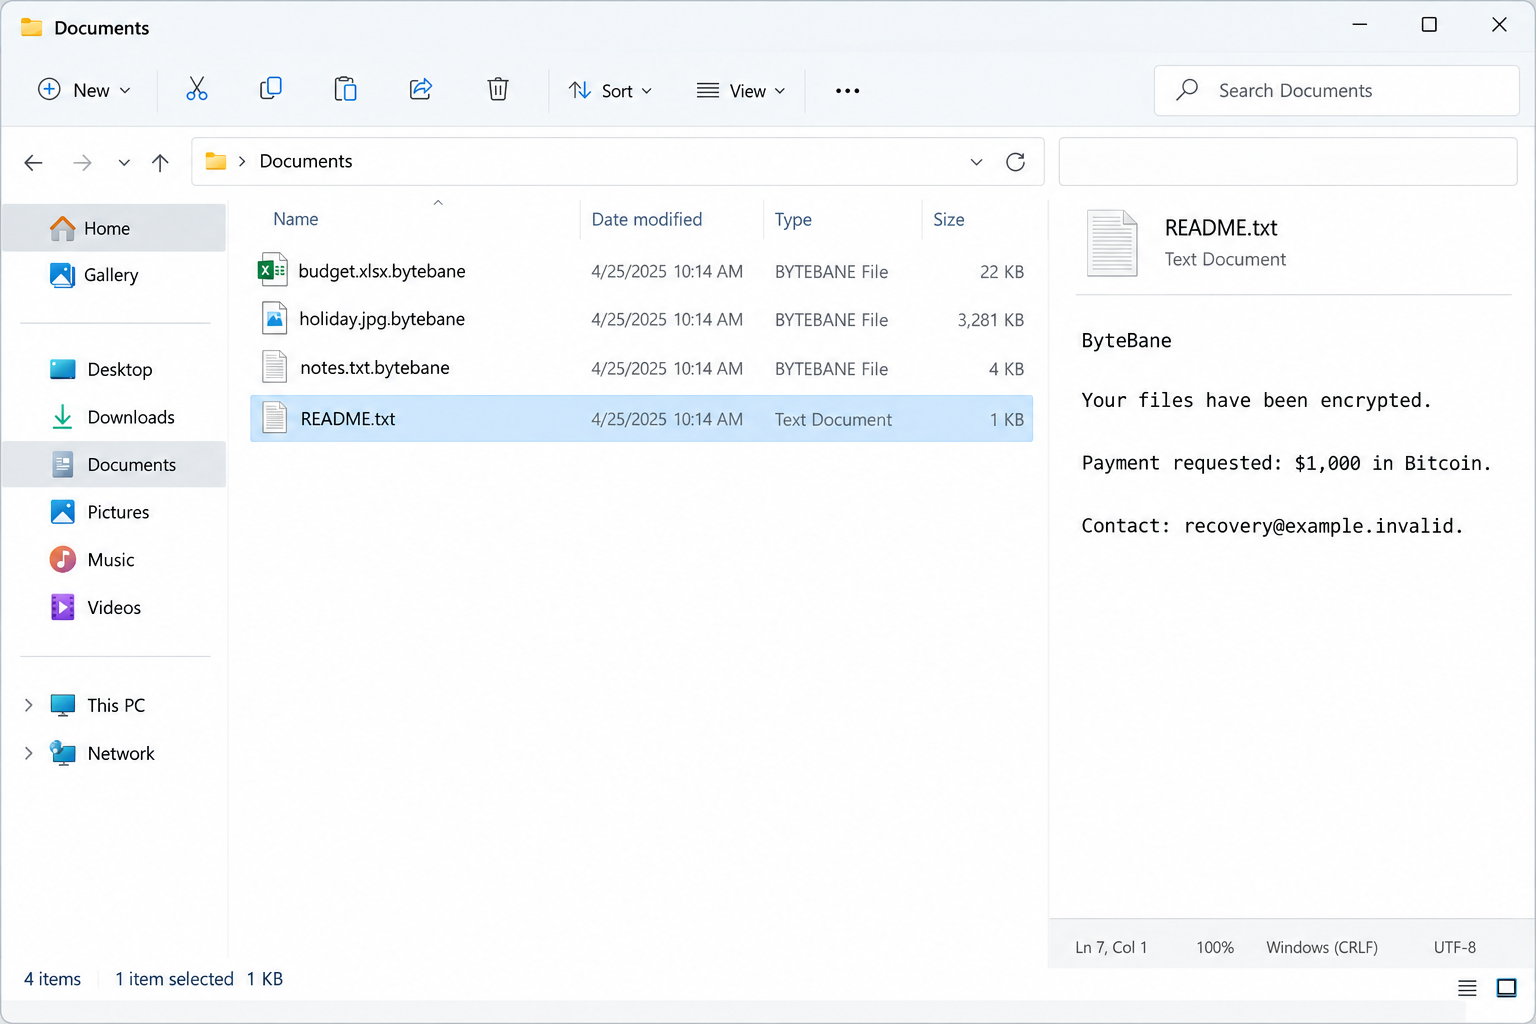
ByteBane is ransomware associated with encrypted files carrying the .bytebane extension. Reported examples include ordinary documents and images that no longer open normally.
The malware also leaves a note named README.txt and changes the desktop wallpaper. The note requests $1,000 in Bitcoin for purported recovery.
That demand comes from the attacker. It is not a verified price for a working recovery service, and payment does not guarantee usable files.
The lead illustration uses example filenames and a fictional contact address. It demonstrates the visible symptoms without presenting a copied ransom screenshot or an active payment destination.
Several statements in the note are attacker claims
The note describes AES-256 and RSA-4096 encryption and claims personal information was copied. Those assertions should not be mistaken for independently verified cryptographic or exfiltration findings.
A data-theft claim deserves investigation, especially for an organization. It does not prove that every listed category of information was actually removed.
The contact address reported with the sample contains another ransomware name. That alone does not establish affiliation with the group using that name.
Likewise, a timer on the wallpaper is not proof that a displayed deadline controls deletion. Treat it as pressure, not an authoritative incident-management instruction.
Removal and file recovery are different tasks
Stopping malicious activity protects the remaining environment. It does not automatically turn encrypted documents back into readable files.
There is no verified ByteBane-compatible public decryptor established in the material checked for this guide. That assessment may change as researchers develop or validate tools.
- The .bytebane extension and README.txt note are useful incident indicators.
- The ransom amount and theft statements are demands and claims, not assurances.
- Backups must be checked without exposing them to the affected computer.
- Keep encrypted copies for possible future recovery instead of deleting them in frustration.
A careful response isolates the incident, preserves evidence, removes the threat, and then evaluates recovery options. Skipping directly to payment can leave the original access unresolved.
How a ByteBane Incident Can Unfold
Step 1: Malicious code reaches the computer
The specific initial delivery route for the reported ByteBane sample is not established here. Do not assume every incident began with the same email or download.
Investigators should review recent execution, remote access, account activity, and relevant security events. The filename extension alone cannot identify how the intruder first gained access.
For a home user, a timeline of recent installations can help support. For a business, preserving logs may be more useful than immediately removing every unfamiliar item.
Avoid running a suspected file again to reproduce the event. The recovery process should not create another opportunity for encryption.
Step 2: Files become unreadable and acquire a new extension
Reported affected files have .bytebane added to their existing names. The original filename may remain recognizable even though the content is no longer usable.
That difference is important. The familiar name does not mean the document itself survived intact, and the additional extension is not the encryption mechanism.
Renaming a file back to its former name will not decrypt its contents. Keep a separate copy if a specialist needs to examine a sample.
Do not assume every file on the device was affected equally. Inventory the damage without opening or modifying large numbers of files unnecessarily.
Step 3: The note frames payment as the only solution
The README.txt message asks for $1,000 in Bitcoin and describes a route to purported assistance. It is written to make the victim dependent on the attacker.
Strong-sounding algorithm names reinforce that message. They are not a substitute for independent analysis of the actual implementation or available recovery methods.
The note also claims data was copied. That introduces a second fear beyond lost files and may pressure an organization to negotiate quickly.
Preserve the note, but do not treat its descriptions as a complete forensic report. Investigate what happened using trusted evidence and professional help where needed.
Step 4: Wallpaper pressure narrows your attention
A changed desktop keeps the demand visible even after you close the note. A countdown or warning can make ordinary recovery steps seem dangerous.
The reported message discourages rebooting or shutting down. An attacker’s instruction should not decide your response to active malicious activity.
Start by disconnecting network access. That limits communication and exposure of reachable resources, but does not necessarily stop encryption already running locally.
If encryption appears ongoing, seek immediate incident-response help about containment. Power decisions can affect both damage and volatile evidence; there is no universal instruction for every situation.
Step 5: Recovery depends on containment and trustworthy copies
Once the environment is made trustworthy, existing clean backups may restore the missing data. Backups created after encryption are not equivalent to earlier unaffected versions.
Some services retain version history, but retention varies. Review the actual account’s options rather than assuming that syncing files automatically provided an independent backup.
A public decryptor, if one becomes available, must match the ransomware and affected variant. A tool for another family cannot be chosen by name similarity.
These are recovery paths to evaluate, not promises that every encrypted file can be restored. Keep the distinction clear while planning what matters most.
What to Do if Your Files Have the .bytebane Extension
Isolate the affected computer. Disconnect Ethernet and Wi-Fi. Keep external backups unplugged and avoid opening shared drives from the affected system.
For a managed device, contact IT immediately. If local encryption continues, ask a trusted responder how to contain it without unnecessarily destroying useful evidence.
Document the incident before major cleanup. Photograph or capture the note, filenames, visible warnings, and relevant detection results. Record when normal access last worked.
Do not include personal records in public screenshots. A professional investigation may need a preserved disk image or logs before removal changes the evidence.
Remove the active threat through verified tools. Use the MalwareTips Malwarebytes scan guidance below. Follow the product’s findings instead of deleting random system files.
Our HitmanPro download route provides another established scanning option. Additional scanning does not guarantee that an extensively compromised system should remain in service.
Assess the original access and connected accounts. Review remote-access software, administrator changes, and relevant sign-ins with trusted support. Rebuild when that is needed to restore confidence.
Change exposed credentials from clean equipment and revoke unwanted sessions. The visible ransomware may be only one part of the intrusion.
Preserve encrypted files separately. Make offline copies when safe to do so. Keep the ransom note and several representative samples available for identification.
Do not discard originals after an unsuccessful tool attempt. Work on copies, and do not upload sensitive business documents to unverified recovery websites.
Check recovery options after containment. Inspect offline backups, cloud versions, and trusted decryptor listings. Confirm a tool’s compatibility before attempting it.
Restoring into a still-infected environment can expose the recovered data again. Verify both the backup’s condition and the destination computer’s trustworthiness.
Report the attack and possible data exposure. Contact appropriate law enforcement and, for an organization, involve its security, legal, and privacy teams.
The FBI’s ransomware guidance explains why payment is not a recovery guarantee. Notify your insurer when applicable without accepting the attacker’s claims as established facts.
Reject unverified rescue offers. Do not install a “ByteBane unlocker” from an advertisement or pay someone who guarantees decryption without examining compatibility.
AdGuard helps limit exposure to deceptive ads and certain unsafe destinations. It cannot decrypt .bytebane files or replace incident response.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Remove ByteBane Ransomware From the Affected Computer
The following MalwareTips removal instructions address active malware and continuing access. Complete containment and evidence preservation before cleanup, particularly when a business investigation is underway.
Contain the incident before running cleanup tools
Disconnect the affected computer from Wi-Fi and wired networks. Unplug external storage and leave backup drives disconnected while you assess what happened.
Pause synchronization from a clean device where possible. Otherwise, encrypted versions may replace usable cloud copies while you are trying to rescue them.
At work, contact your IT or incident-response team immediately. A ransomware screen on one computer may be the visible part of a larger intrusion.
Keep the ransom note, filenames, discovery time, and any security alerts. A specialist may need disk or memory evidence before cleanup changes the machine.
If you cannot isolate a computer and encryption is visibly continuing, seek immediate assistance about shutting it down. Powering off can lose volatile evidence.
Do not repeatedly restart, reinstall, or experiment with utilities. Those actions can overwrite recovery evidence without addressing the underlying access problem.
Use trusted scanners on an isolated personal computer
For a home computer, arrange cleanup after preserving the evidence you need. Obtain security tools through their official websites using an unaffected system.
Malwarebytes can scan for malicious programs and related unwanted software. It is an infection-removal tool, not a way to decrypt already encrypted documents.
Install a current copy, update its detection data when safely possible, and run the available comprehensive scan. Review detections before applying the recommended quarantine actions.
Keep the scan report. It can help distinguish the ransomware payload from another infection, a suspicious installer, or a remote-access program.
Windows Security also provides scan options. Microsoft Defender Offline restarts into an offline scanning environment, so save your work before starting it.
Follow Microsoft’s ransomware protection guidance rather than instructions in the criminal’s note. A note telling you to disable protection is not trustworthy advice.
If Windows will not start or the scanners cannot operate, stop improvising. Use reputable technical assistance instead of downloading a supposed one-click emergency decryptor.
Do not upload the executable to unfamiliar recovery websites or run it elsewhere for testing. A second execution can create another incident.
Verify the environment before restoring anything
A completed scan is useful, but it cannot establish that every account, remote session, or networked computer is safe.
Check for unauthorized remote-access software, suspicious accounts, changed security settings, and unknown scheduled tasks. Business environments require coordinated investigation beyond this home-computer checklist.
Change exposed passwords from a clean device. Prioritize email, cloud storage, administrator access, and any account whose credentials were saved on the affected system.
Enable multifactor authentication where supported and revoke suspicious sessions. Simply changing the password may leave an existing signed-in session active.
A trusted reinstall may be appropriate when system integrity remains uncertain. Preserve recoverable data first, and reinstall from authentic installation media.
AdGuard can help reduce exposure to malicious advertising during future browsing. It neither cleans an infected system nor reverses file encryption.
Keep backup media offline until cleanup and access checks are complete. Reconnecting your only good copy too early can turn a recovery opportunity into another loss.
Recover Files Encrypted by ByteBane Ransomware
No verified ByteBane-compatible decryptor was established for this guide. Use the recovery instructions below to evaluate copies and tools without confusing malware removal with decryption.
Make a recovery copy, not another damaged original
Keep an untouched copy of the encrypted data whenever practical. Include the ransom note and retain the original directory structure.
Use a separate destination for recovery experiments. Never let a utility overwrite your only encrypted copy or replace an intact backup.
Before sharing samples, consider their sensitivity. Choose an ordinary, nonconfidential file and ask the service about handling rules if business or personal information is involved.
The note’s name, complete filename suffix, and contact details can help identify a variant. An extension alone is not enough to establish decryption compatibility.
For example, two infections can use the same suffix while generating different keys. A familiar family name can also hide a newer, unsupported version.
Record the exact error or result from each attempt. Keep a simple checklist so another helper does not repeat risky tests on the same files.
Check recognized decryption projects
Visit the No More Ransom decryption catalog from a clean browser. Look for the actual variant and read the tool’s requirements carefully.
A tool for a related family does not automatically unlock your files. Some decryptors support only older versions, certain keys, or specific encryption mistakes.
Download through the catalog’s trusted vendor link, not a sponsored search result or an unsolicited message offering guaranteed recovery.
Test only a duplicate sample first. Successful decryption should produce a usable document or image, not merely remove the added extension.
If the utility reports an unsupported file or key, stop. Changing the filename to resemble a supported variant does not change its encrypted contents.
When no compatible tool is available, preserve your encrypted archive. Researchers sometimes release new tools later, but future recovery cannot be promised.
Look for copies that existed before encryption
Check disconnected drives, backup software, cloud version history, another computer, and files previously sent to trusted contacts. You may have more copies than you remember.
Cloud synchronization is not automatically a backup. Confirm that an earlier usable version survives and that the account itself has not been compromised.
Restore into a cleaned environment. Open a selection of documents, photos, and project files before assuming the recovered collection is complete.
Compare important dates and contents. An older spreadsheet might open perfectly while still missing the transactions you needed to recover.
Windows Previous Versions or existing snapshots may offer additional copies. Availability depends on prior configuration and whether those snapshots survived the incident.
Do not create new restore points expecting them to contain yesterday’s files. Recovery depends on copies that already existed before the damage.
Deleted-file recovery utilities are a different category. They may locate unencrypted originals in some circumstances, but they do not mathematically decrypt overwritten data.
If you want a specialist to investigate that possibility, minimize writes to the affected storage. Continued installations can overwrite remnants that might otherwise be recoverable.
Evaluate recovery offers without surrendering control
Be wary of anyone who contacts you first, claims exclusive access to a secret decryptor, or requests an advance payment in cryptocurrency.
Ask a recovery provider what method it intends to use, what evidence supports success, and whether it would negotiate with the attacker.
Get the scope, fee, privacy terms, and limitations in writing. A legitimate assessment should distinguish a possibility from a demonstrated recovery result.
Do not provide remote administrator access to an unknown helper. Recovery desperation can make a second scam feel like the only remaining option.
If you already paid, retain receipts, transaction references, wallet addresses, and correspondence. Contact the payment provider promptly and report the extortion.
Recovery is sometimes partial. Prioritize irreplaceable files, verify them individually, and keep your evidence archive until the investigation and restoration decisions are settled.
ByteBane-specific limits to keep in mind
A Chaos-related antivirus label does not establish decryptor compatibility. Have the actual encrypted sample assessed; do not choose a tool by a similar family name.
The note’s algorithm and data-theft statements remain attacker claims. Neither the $1,000 demand nor its contact address verifies a working recovery method or group identity.
If you investigate deleted originals, our EaseUS Data Recovery Wizard route is for file recovery, not ByteBane decryption. Work on copies and minimize storage writes.
ShadowExplorer can help inspect existing Windows shadow copies where usable snapshots survive. Their availability depends on prior configuration and this incident’s effects.
Do not install either utility onto storage holding your only recoverable remnants. Restore output elsewhere, preserve originals, and ask a qualified specialist about imaging valuable evidence.
Before You Put the Computer Back Into Service
Recovering documents does not explain how the ransomware arrived. Close the original access route where it can be identified, rather than treating file restoration as complete containment.
Install operating-system and application updates through official channels. Remove unnecessary remote-access tools with trusted help, preserving evidence when an investigation requires it.
Review account recovery methods and administrative access. A new copy of Windows does not remove an attacker’s access to an online account established elsewhere.
Build backups that are not continuously writable from the everyday computer. Test recovery periodically with harmless sample files instead of waiting for a ransomware incident.
For shared business resources, coordinate restoration. One cleaned workstation does not establish that every server, endpoint, or account connected to it is safe.
Maintain an incident timeline covering the first unreadable file, network disconnection, scans, and restoration attempts. It helps separate original damage from changes made during recovery.
If email access might also be compromised, discuss recovery through an independently verified channel. An intruder could observe ordinary correspondence about backups or administrator actions.
Prioritize essential records instead of reconnecting every storage device at once. Restoring a small, verified set can support immediate needs while a broader review continues.
For business continuity, document which services can operate without the affected machine. Temporary alternatives should not bypass account protections or expose surviving clean copies.
Retain recovery logs alongside the preserved samples. Future support is more effective when it can see which methods were attempted and which originals remain untouched.
Frequently Asked Questions
What does the .bytebane extension mean?
It is associated with files affected by ByteBane ransomware. Preserve samples and the note for identification; an extension alone does not describe the entire intrusion.
Will renaming the files make them open again?
No. Removing the added extension does not decrypt changed contents. Keep original copies so an unnecessary rename does not complicate identification.
Does ByteBane definitely steal personal data?
The ransom note claims copying occurred. Treat that as a serious allegation to investigate, not proof of exfiltration on every affected computer.
Is there a free ByteBane decryptor?
No verified compatible public tool was established for this guide. Check trusted listings for updates and avoid guarantees from unverified unlocker websites.
Can Malwarebytes restore encrypted documents?
Malwarebytes addresses malicious software. It does not automatically decrypt affected documents; file recovery requires compatible tools, clean backups, or other recoverable copies.
Will paying $1,000 guarantee recovery?
No. Payment cannot guarantee a working decryptor, complete restoration, deletion of stolen information, or removal of the original access route.
The Bottom Line
ByteBane requires containment and recovery, not obedience to its ransom note. Isolate affected equipment, preserve evidence, and remove the threat before restoring valuable data.
Protect encrypted originals and evaluate verified recovery routes carefully. A demand for $1,000 is not proof that payment will solve either the file loss or the intrusion.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.