


A chargeback invoice lands in your inbox, apparently ready for a quick review. The attached spreadsheet seems to contain everything you need.
If you handle orders or payments, it is an easy message to open between other tasks. Pause before treating its attachment as routine paperwork.
Overview
The invoice is a reason to ask for your password
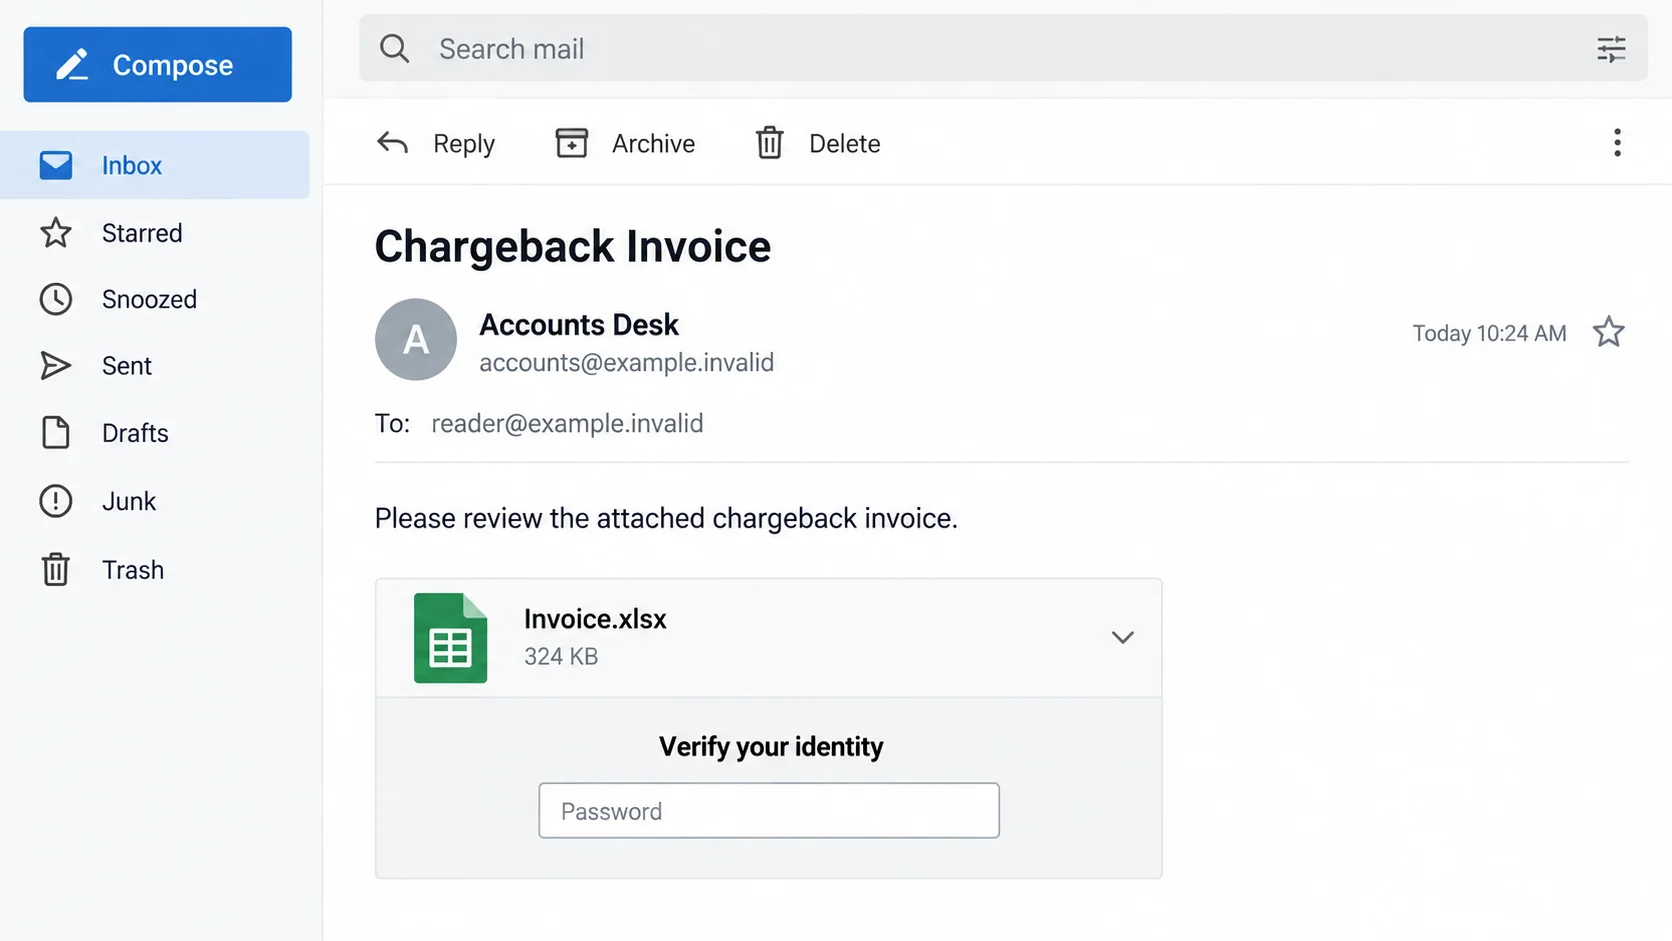
The chargeback invoice email scam uses a familiar business document to introduce an unrelated request: verify your identity by entering an account password.
The reported message describes its invoice as already authorized for processing. It asks you to review an attachment called Invoice.xlsx and confirm the details.
Inside that supposed review process, the recipient encounters a password request. Instead of resolving a payment question, the interaction exposes information that could unlock an account.
No legitimate dispute has been established by the email alone. The sender’s claim that processing is authorized should not become your authorization to supply a secret.
Financial language makes a vague request feel important
A chargeback can affect a business’s revenue, so the subject creates a reason to act even when the sender gives little transaction information.
Someone responsible for bookkeeping may assume another colleague already checked the customer or order. The phrase about prior authorization encourages exactly that shortcut.
- The subject introduces a chargeback invoice rather than an ordinary conversation.
- The main details are supposedly inside an attached spreadsheet.
- The sender asks you to confirm information that has allegedly been approved already.
- The attachment then turns document review into account-password verification.
These details belong together. A spreadsheet filename is not suspicious by itself, but an unsolicited attachment is not a trusted place to authenticate your mailbox.
An attachment label is not a technical diagnosis
The original file was not available for independent examination. Its reported behavior supports a credential-theft warning, not a claim about a particular executable or macro.
The image above is an original illustration with fictional addresses. It explains the attachment lure without pretending to show a recovered email or a tested sample.
Do not conclude that every file named Invoice.xlsx is malicious. Equally, do not assume an Excel-looking name makes an identity form safe.
Your response should depend on what happened: receiving a message, opening a file, entering a password and running software are different exposures.
Find the Actual Payment Question Before Opening the File
Start with the transaction, not the attachment. Which order is disputed, which payment provider is handling it, and who inside your organization owns the case?
If those answers are missing, the email has not supplied enough context to justify a financial action. Ask through your established accounting or payment-support channel.
A real customer dispute can exist at the same time as a fraudulent message. Finding a genuine chargeback elsewhere does not authenticate this particular attachment.
Open the payment service through your saved bookmark or normal application. Look for the case there, using information from your own records.
For example, Stripe’s dispute guidance explains how cases are reviewed in its Dashboard. Other providers have their own established processes.
The point is not that all merchants use Stripe. It is that the provider handling your real transaction should be able to identify the dispute independently.
If a deadline is genuine, record it from that verified case. Do not let checking a fake email cause you to miss the actual response window.
Likewise, do not issue a separate refund simply because the attachment says one is due. First establish what has already happened through the processor.
How the Chargeback Invoice Email Scam Works
Step 1: Put an Unfinished Financial Task in Your Inbox
The message arrives as paperwork needing your attention. It does not need to promise a prize or threaten the immediate loss of your account.
Its leverage is the work itself. People handling payments are accustomed to invoices, adjustments, reconciliation questions and requests to confirm information.
A short message can seem normal in that setting. You may assume the attachment provides the context omitted from the body.
That assumption moves the trust decision to the wrong place. You are opening an unknown file to find out whether you have a relationship with its sender.
The reported wording also says the invoice has been authorized. That suggests someone else already made the difficult decision, leaving you only an administrative check.
Before continuing, identify that supposed decision-maker. If nobody in your organization recognizes the transaction or approval, do not manufacture the missing context yourself.
Step 2: Make the Spreadsheet the Only Route to the Details
The attachment name, Invoice.xlsx, looks ordinary enough to belong in an accounts inbox. A different filename could serve the same purpose in another version.
The request places all relevant information inside the file. To understand what you are being asked to approve, you are encouraged to enter the document first.
That is useful to the sender because the email can avoid exposing a weak or nonexistent financial explanation in plain sight.
A preview, workbook-looking page or file icon can reinforce the impression of office software. None of those visual details identifies who receives information entered there.
Do not enable editing, active content or additional downloads just to reveal an unexpected invoice. Ask the verified sender for the transaction details through an established channel.
If the file opens automatically in a browser or another application, do not treat the change of window as a change of trust.
Step 3: Replace Invoice Review With Identity Verification
The decisive shift comes when the document asks for a password. You came to read numbers, but now you are being asked to disclose account access.
A malicious document can describe that request as encryption, confidentiality or verification. The label does not explain why your existing email password would be needed.
Real password-protected documents do exist. A password deliberately assigned to a specific file is different from a demand for the secret you use on another service.
Microsoft documents Excel file-level password protection. Its existence does not make an unsolicited identity form part of that legitimate feature.
If a known supplier intentionally encrypted a workbook, agree on the document password separately. Do not try your mailbox password to see whether it happens to work.
The reported attachment seeks a password under an identity pretext. No safe outcome is demonstrated by a loading animation, access error or apparently successful submission afterward.
Step 4: Use the Secret Somewhere Other Than the Invoice
A collected password can be tested against the service it actually belongs to. If reused, it may also expose other accounts with the same secret.
For a work mailbox, the practical concern includes supplier conversations, invoice histories and messages used to reset access elsewhere.
An intruder who reaches those conversations may have enough context to impersonate a real colleague. Future payment instructions could arrive inside a thread people already recognize.
That is a possible consequence, not a finding that a particular recipient lost money. Account activity and organizational records determine the scope of an actual incident.
Changing the attachment’s filename will not address that problem. A password submitted to the wrong recipient must be handled at the account level.
Device investigation is a separate question. It matters if the attachment ran active content, downloaded software or triggered behavior your security team needs to examine.
Three Checks for an Accounts or Bookkeeping Team
Match the case to an existing record
Ask for the order number, payment reference and provider case identifier. Compare them with records obtained before this email arrived.
A reference printed in a suspicious file is only a claim until it matches the real system. Do not upload customer records to an unknown verification page.
If a colleague recognizes the customer but not the dispute, ask that colleague to check through the original customer relationship. Recognition alone is not approval.
For a shop with several payment accounts, identify which account processed the order. A dispute involving one provider should not require signing into an unrelated mailbox.
Check the recipient role too. An employee copied on accounting correspondence may not be the person authorized to answer the processor.
Route the verified case to that person without opening the suspicious attachment again. They can collect transaction evidence from existing business records.
This keeps a useful division of work: accounting handles the actual payment question, while security handles the file and any exposed account.
Separate document access from payment authority
Someone may be authorized to read an invoice but not issue refunds, change bank details or approve a dispute response. Keep those permissions distinct.
A message saying processing is authorized should name a process your business actually uses. It should not bypass the person responsible for financial approval.
If you receive a follow-up asking for a different payment destination, stop and verify it separately. A convincing document cannot authorize a new recipient by itself.
Keep the investigation from becoming another exposure
Do not ask coworkers to open the file on their computers to see whether it behaves differently. That spreads the same uncertainty across more devices.
Use your organization’s designated reporting method. Security staff may need the original message and attachment, but they should decide how to collect and inspect them.
A screenshot can explain what you saw. It does not replace the original email when investigators need routing details or the exact attachment.
What to Do if You Have Fallen Victim to This Scam
Stop the attachment’s verification process. Close the document or page without supplying another password, code or download permission.
Keep a note of the filename, sender and action you took. If this happened at work, use the normal incident-reporting route promptly.
You do not need to finish the invoice review before reporting it. Explain whether you merely opened the attachment or actually entered information.
Protect the account whose password you entered. Reach the correct service independently, preferably from a device you trust.
Replace the exposed secret and any identical password used elsewhere. Include unsuccessful attempts: a form can collect a password even when it rejects the login.
If access is already lost, use the provider’s recovery process. Do not buy recovery help offered by a stranger responding to your report.
Have account access reviewed, not just the password. Ask the administrator to inspect unfamiliar sessions, recovery changes, forwarding rules and connected applications.
Tell them about any authentication prompt you approved. A password change alone should not be presented as confirmation that every existing session has ended.
For a shared finance mailbox, involve its actual owner. Several employees may rely on the account, and quiet forwarding could affect messages they never saw.
Check the real payment workflow. Confirm the chargeback through the provider and review any financial instructions sent after the suspected compromise.
If money moved, contact the bank or payment service immediately with the transaction reference. Explain accurately whether you authorized the transfer after deception.
Keep legitimate dispute deadlines visible while handling the phishing report. The fake spreadsheet and a real customer case require different responses.
Investigate relevant device exposure. If you enabled active content, installed software or noticed unexpected behavior, tell your security team exactly what occurred.
On a personal computer, an updated Malwarebytes scan can help investigate possible malware. It cannot revoke a stolen cloud session or settle a chargeback.
AdGuard can reduce intrusive advertising and some dangerous browsing exposure. Neither tool makes an unverified attachment or an unknown sign-in request trustworthy.
Preserve the trail and warn affected colleagues. Retain the original email through the approved reporting process, along with screenshots and any provider case number.
If fraudulent replies left your account, identify the recipients with your administrator. Warn them through a clean channel rather than continuing a potentially compromised conversation.
Microsoft’s phishing guidance provides reporting and verification advice. Follow your employer’s evidence-handling instructions before deleting the message.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is every chargeback email fraudulent?
No. Payment providers send legitimate dispute notices. Verify the case inside your established provider account rather than trusting an unexpected attachment’s request for credentials.
Does Invoice.xlsx prove the attachment contains a macro?
No. The filename does not establish its internal contents. This warning concerns the reported password-verification lure, not a tested macro or a confirmed malware family.
Can a real Excel file have a password?
Yes. A separately arranged document password is different from entering your email account password into an unsolicited identity prompt.
What if I opened it but entered nothing?
Report what happened and whether you enabled content or ran anything. Opening alone does not establish account takeover, but the file may warrant controlled inspection.
Should I pay or refund the amount mentioned?
Not on the attachment’s authority. Check the actual order and dispute with the payment provider before making a financial adjustment.
Will a clean scan fix a disclosed password?
No. Secure the affected service and review access separately. A device scan addresses possible software threats, not permission to an online account.
The Bottom Line
Do not provide an account password to review this chargeback invoice. The attachment turns a bookkeeping task into a credential request without authenticating a real dispute.
If you already entered a secret, secure its actual account and involve the responsible administrator. Handle any genuine payment case through the provider you already use.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.