


A message says your cPanel account has changed status. Suddenly, keeping your website and email running seems to require attention.
That warning feels urgent when your business depends on both. Before dealing with its deadline, look at what the notice asks.
Overview
The warning ties a routine-sounding check to a serious disruption
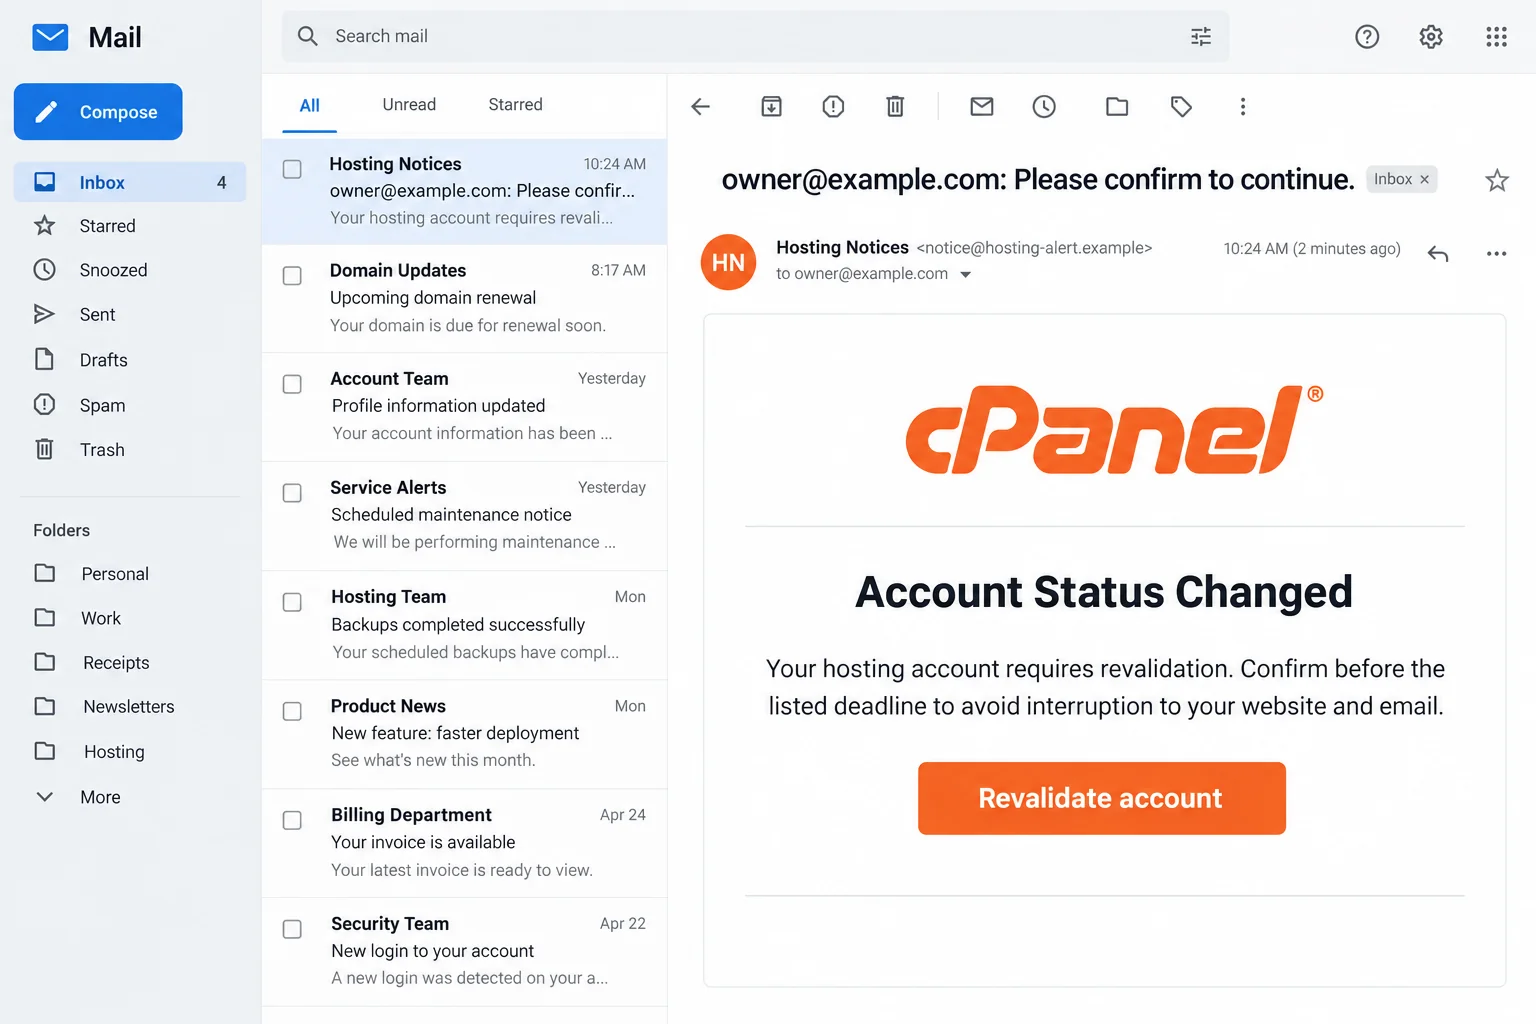
The cPanel Account Status Changed email scam claims the recipient must revalidate an account before a stated date to keep website and email access.
That combination matters. A hosting account can support customer inquiries, a shop, appointment bookings, and the address used for recovering other accounts.
The email makes an administrative task feel urgent without first showing a real problem inside the hosting account.
A reported subject includes the recipient’s address followed by “Please confirm to continue.” That wording can also appear in unrelated phishing campaigns.
The message discussed here specifically uses the changed-account-status story. It should not be confused with every genuine notification a hosting provider sends.
cPanel is real, but this revalidation notice is an impersonation
cPanel is software used by hosting providers. A scammer can borrow its name without controlling your host or knowing anything about your actual account.
Logos, a businesslike layout, and your email address do not authenticate the sender. Addresses can be collected or guessed from public information.
The email illustration above uses fictional contact details. It shows the kind of revalidation request involved, not an original message from a particular recipient.
The reported destination was unavailable when the campaign was originally examined. Its exact working form and subsequent behavior therefore cannot be described as observed.
The practical concern is a phishing handoff: a false service warning sends an account owner toward a place where private account details may be requested.
The right question is whether your host confirms the issue independently
Do not let the button become the only route to checking the claim. Open your established hosting portal separately.
Use a saved bookmark, a previously verified provider address, or the contact details on an existing contract. Avoid contact information supplied by the suspicious message.
- Check whether the provider dashboard shows an actual restriction or support ticket.
- Compare the affected service with what your hosting plan really includes.
- Ask the host to verify the notice through an established support channel.
- Keep the original email if you already interacted with it.
A working website does not prove every account setting is safe. Equally, a temporary website error does not make an unrelated revalidation email genuine.
Why This Hosting Warning Can Feel So Convincing
Website owners already expect technical maintenance
Domains renew, certificates change, storage fills, and providers send service notices. An attacker places a fabricated request among tasks that are genuinely part of ownership.
Consider a shop owner checking email between orders. A notice mentioning both the storefront and mailbox sounds more consequential than a random advertising message.
There is no need for a long story. The threat of interrupted business supplies the pressure, while “revalidation” sounds like a harmless administrative correction.
That is a reason to change how you verify the request, not a reason to feel embarrassed if you opened it.
A mailbox password and a hosting password have different reach
Your host may offer separate logins for billing, cPanel, individual mailboxes, and a website administrator. Some providers connect these through single sign-on.
Which credential you entered matters more than the logo on the page. A mailbox login does not automatically provide server-wide administrative access.
A hosting-panel password, however, may expose files, email settings, databases, or other functions allowed by that account’s permissions.
Note which account and credential you used, without writing down the password itself. Your provider can help identify the services requiring attention.
How the cPanel Account Status Changed Email Scam Works
Step 1: A status-change notice arrives outside your normal workflow
The process begins with an unsolicited email presenting itself as a hosting notification. Its subject may include the address receiving it.
Personalization makes the notice easier to accept, especially if that address really belongs to the website owner or administrator.
But naming an address is not evidence that the sender checked the account. Public contact pages and old data leaks can supply that detail.
Look at the full sender address rather than the display name alone. A label such as “Hosting Notices” is just text.
Do not reply to ask whether the sender is legitimate. That leaves the impersonator in charge of explaining its own message.
Step 2: The email creates a deadline for keeping services available
The body claims an account status change requires revalidation. Website and email continuity become the reason to act before the listed date.
A deadline discourages a slower comparison with old provider correspondence. It also gives the button an apparent purpose: prevent disruption now.
The missing piece is independent confirmation. A date printed in an email does not create a real restriction in your hosting account.
If your provider actually requires action, its established support team should be able to explain the service, reason, and appropriate account procedure.
Keep that conversation separate from the email. The sender’s urgency does not require you to use the sender’s route.
Step 3: Revalidation sends the reader away from the trusted account route
The link is the handoff between the warning and whatever page the sender controls. Button wording does not reveal the complete destination.
A copied sign-in page can look familiar even when its address is unrelated to the host. Branding can be reproduced without permission.
Because the reported destination was down, there is no basis for promising that every version displays one specific login screen or collects identical fields.
The safe response does not depend on finding a working version. There is no legitimate need to revive a suspicious link just to inspect it.
On a work account, send the message to IT through the approved reporting feature. They can examine headers and links without making you the tester.
Step 4: A routine-looking login request can expose the wrong secret
If a destination asks for your hosting or email password, entering it gives that page information it did not previously have.
A familiar background, a padlock, or an error after submission does not change what was sent. Encryption protects the connection, not the recipient’s honesty.
Even an apparently unsuccessful login can matter. Treat a password typed into an untrusted form as exposed rather than waiting for an account alert.
A later request for a verification code or approval is another security decision. Do not approve it simply because you already supplied a password.
Stop at that point and contact the actual provider. Describe what you entered, including any second-factor prompt, rather than only saying you clicked.
Step 5: The damage depends on the access obtained afterward
A stolen credential may be used to read mail, change forwarding, alter recovery details, or attempt access to another account using the same password.
Those are risks to check, not proof that every recipient experienced all of them. Access logs and account settings help establish what actually happened.
For a hosting login, the provider may also need to inspect website files, newly created users, scheduled tasks, and configuration changes.
Changing a password is important, but it should not end the investigation if an attacker already added a separate way back in.
The goal is to restore control of the affected services, not merely make the original email disappear from the inbox.
Sender, Link, and Account Checks That Actually Help
Compare the complete address with your provider’s records
A host may use its own domain for customer notices. That is why a simple rule that every legitimate email must end in cpanel.net would be misleading.
Start with the provider you already pay. Compare the notice with its dashboard and ask support which account communication routes it uses.
Read domains carefully. A trusted brand inside a longer hostname or a link’s visible wording is not necessarily the organization receiving the connection.
Do not paste a private password-reset URL into public discussion boards. Some legitimate links contain tokens granting temporary account access.
Preserve headers instead of forwarding a screenshot alone
A screenshot preserves appearance. Full headers can help a provider understand the delivery route, authentication results, and addresses involved.
Use your mail application’s original-message or phishing-report feature when available. Ask support how to submit evidence if you are unsure.
cPanel’s phishing guidance explains that realistic-looking messages can lead to counterfeit login pages and recommends reporting with full headers.
Do not alter your server’s mail rules or security settings just because a stranger claims that is required to restore service.
Look for changes that survive a password reset
Review mailbox forwarding, filters, recovery addresses, and unfamiliar application access. An attacker may use these to keep reading messages or hide security notices.
For hosting access, ask the provider which account-level functions were available. Request a review of changes made during the suspected exposure window.
cPanel’s security best practices also discuss compromise recovery and checking suspicious email forwarders and filters.
Save a dated note of what was checked and corrected. It makes follow-up easier if customers later report unusual mail or website behavior.
What to Do if You Have Fallen Victim to This Scam
Pause the revalidation process. Close the suspicious page and stop replying. Preserve the message, destination address, and approximate interaction time before deleting anything.
If you only received the email, report it as phishing. Receiving a false status notice alone does not require changing a working hosting configuration.
Contact your real hosting provider. Open the known customer portal or use previously verified contact details. Explain that a cPanel-themed revalidation request may have captured credentials.
Ask which account was affected and whether sessions can be terminated. If the site handles orders, mention that business impact immediately.
Replace exposed passwords from a trusted device. Change the exact hosting or mailbox credential entered. Replace reused passwords on other services with distinct ones.
Secure the recovery mailbox too. Review available multifactor options with the provider rather than enabling an unfamiliar app offered by the suspicious page.
Review access and account changes. Check forwarding, filters, recovery information, new users, and login records. Ask the host to assess website changes if panel access was exposed.
Keep suspicious records for support before removing unauthorized settings. A provider can help distinguish legitimate maintenance from changes needing investigation.
Address software exposure separately. If you installed a suggested tool, ran a file, or granted remote access, disconnect and contact IT before using that device for recovery.
Malwarebytes can help check for malicious software. A scan cannot revoke stolen account sessions or undo changes made through a valid login.
Warn affected people with verified details. If unauthorized messages were sent, tell recipients which requests to disregard using a trusted communication route.
If an invoice or payment destination changed, contact the payment provider promptly. Preserve transaction references instead of negotiating through the suspicious mailbox.
Reduce repeat exposure. Update the browser, remove unwanted notifications, and consider AdGuard for malicious-ad blocking. Keep only the extensions you intentionally use.
Do not pay someone promising to “reactivate cPanel” through a private message. Your existing hosting provider is the appropriate starting point.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Before You Call the Incident Resolved
Test the services that matter to you: sending and receiving mail, receiving website inquiries, and reaching the legitimate administration portal.
Use a harmless test message from an account you control. Do not send passwords, customer documents, or payment details merely to check whether delivery works.
If a business website changed, compare it with a known-good backup or deployment record. Restoring appearance alone may leave unauthorized access untouched.
Ask your provider whether the suspected access window can be reviewed. A short written timeline is more useful than a vague report of an old scam.
Continue watching account alerts after the immediate cleanup. Report new forwarding rules, unexpected reset messages, or unfamiliar administrative users rather than repeatedly changing passwords without investigation.
Frequently Asked Questions
Is the cPanel Account Status Changed email genuine?
The revalidation campaign described here is an impersonation. Check any real account issue through your established hosting dashboard or provider, not its email button.
Does my email address in the subject make it authentic?
No. The sender can know your address without having access to your hosting account. Personalization is not the same as provider authentication.
What if the destination no longer opens?
A dead page does not make the email safe or genuine. You can report the message without reopening the destination or searching for a replacement.
Should I change every password after simply reading it?
Reading alone is different from submitting credentials or running software. Match your response to what you did, and involve IT if the exposure is unclear.
Can this email shut down my website by itself?
The warning does not establish any real shutdown. Website changes require actual access or another vulnerability; ask your provider to investigate if credentials were exposed.
Will an antivirus scan restore my cPanel account?
No. Scanning addresses device threats. Password replacement, session termination, and review of hosting or mailbox settings address account control.
The Bottom Line
Do not revalidate through the cPanel Account Status Changed email. Its service-interruption warning is a reason to verify separately, not to trust its link.
If you supplied credentials, contact your host, secure the affected account, and review changes. Keep device cleanup separate from restoring website and mailbox control.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.