


A delivery failure lands just when you’re waiting for a reply. It says your outgoing email was flagged, but offers a button to send it anyway.
Before you try that fix, check which message supposedly failed. A familiar bounce notification can hide a very unfamiliar request.
Overview
A failed-delivery story disguises the next request
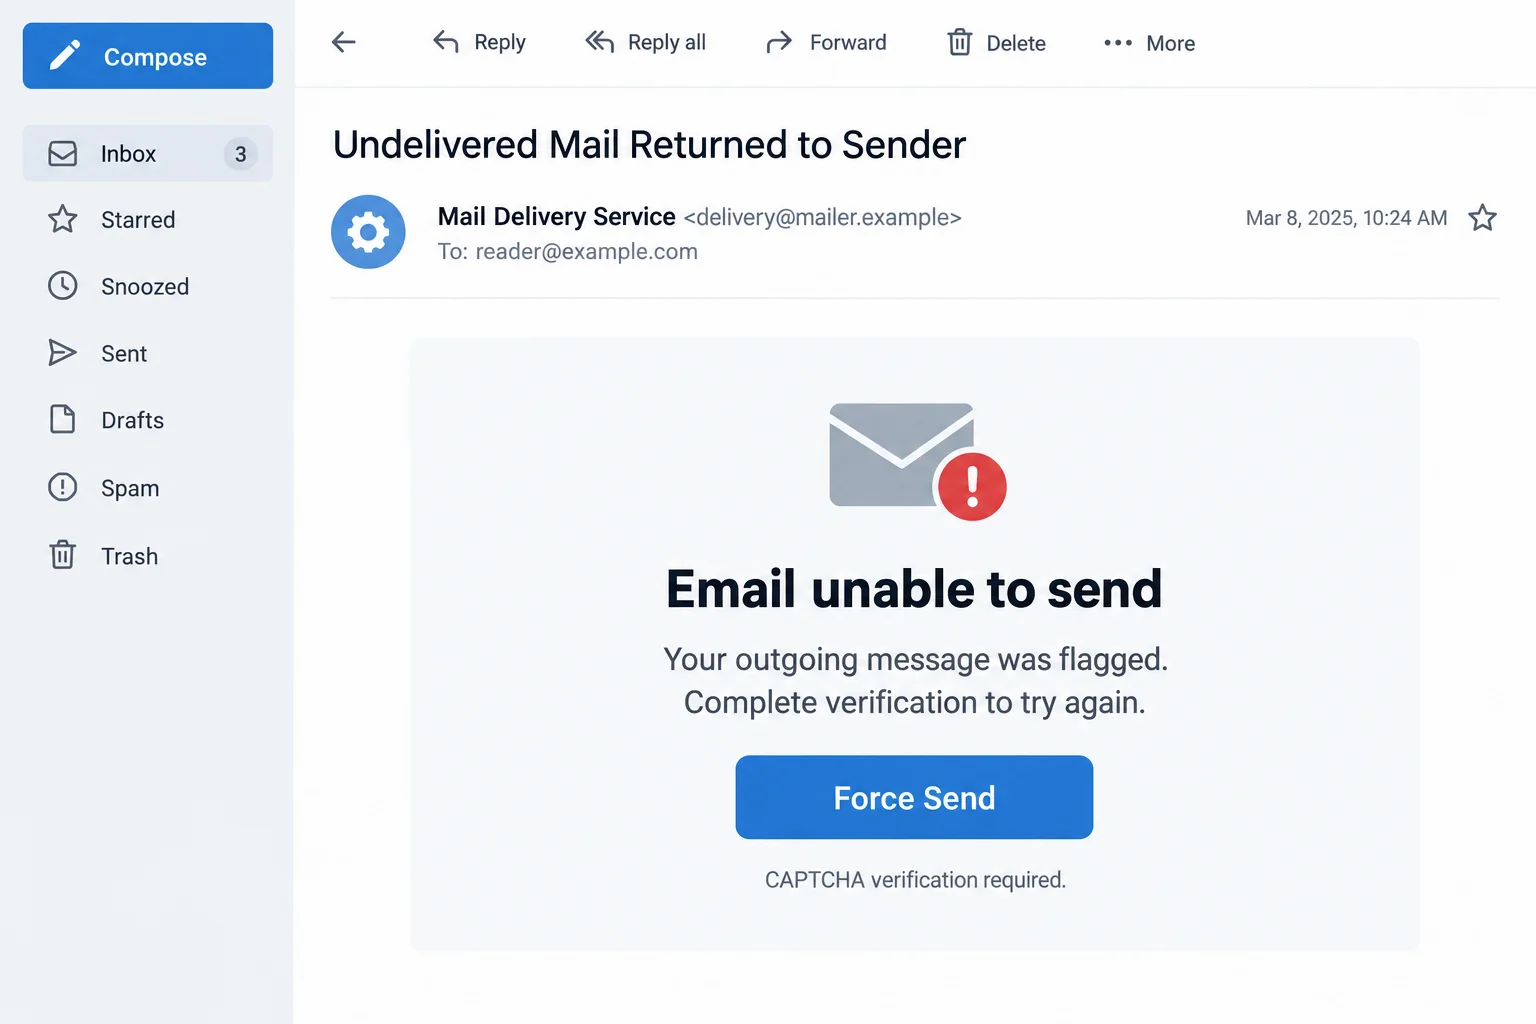
The Email Unable to Send scam impersonates an automated mail-delivery service. Its subject resembles a returned-message notice, while the body says an outgoing email was identified as spam.
The proposed solution is a Force Send button followed by CAPTCHA verification. That promise makes a separate website sound like part of routine delivery troubleshooting.
The danger is not an ordinary delivery report. It is an unsolicited repair route that can move you toward surrendering your mailbox credentials.
The reported destination is unavailable
The original linked page is inactive. That limits what can be said about its precise design, provider branding, and any subsequent screens.
Credential harvesting is the reported purpose of this campaign. A provider-themed login is a known continuation of this pattern, not a page you should visit to investigate.
The illustration uses fictional sender details and a nonfunctional button. It shows the delivery pretext, not a genuine failure recorded by your mail service.
Check the delivery problem separately from the proposed fix
- Find the original outgoing message in your own Sent folder.
- Compare the recipient and timing with the alleged failure.
- Read any genuine error through your established mail service.
- Never enter your mailbox password into an unfamiliar resend page.
A convincing subject line is not enough. Real bounce messages exist, and scammers borrow their appearance because people have legitimate reasons to act on them.
A Real Bounce Message Explains a Delivery Failure
An email can fail for many ordinary reasons. An address may contain a typo, the recipient’s mailbox may be full, or a server may temporarily reject delivery.
Spam filtering can also affect genuine correspondence. That possibility makes the scam’s explanation plausible without making its button trustworthy.
What helps is the relationship to a message you actually sent. Start with your own records rather than accepting a vague statement about your last outgoing email.
For example, an incorrect address calls for correcting the destination. A full recipient mailbox may require contacting that person another way or waiting.
Those situations are different from handing a mailbox password to a website that promises universal delivery. Authentication doesn’t erase the recipient’s server rules.
Google’s bounce-message troubleshooting guide explains how Gmail delivery reports describe errors and how different failures call for different responses.
The article is useful because it starts with the actual error. It doesn’t treat every rejected message as a problem fixed by one external verification button.
A genuine provider may ask you to sign in while troubleshooting. Open that provider yourself, and verify the request within the service you intended to use.
Don’t use spelling alone as your test. Automated reports can be awkward, while fraudulent notices can be polished and grammatically correct.
Likewise, a message appearing in the inbox instead of Spam is not a guarantee. Filtering is useful protection, not proof of the sender’s authority.
How the Email Unable to Send Scam Works
Step 1: The message arrives as a familiar delivery notice
A returned-mail subject suggests that a system, rather than a stranger, is contacting you. That can lower your guard before you reach the body.
The sender’s display name may sound technical. Remember that a name like Mail Delivery Service can be typed by someone who does not operate your mailbox.
The message then supplies a convenient explanation: your outgoing email was flagged as spam. It makes the problem feel connected to something you already tried to do.
If you send many emails, you might fill in the missing details yourself. Stop and identify the actual message instead of assuming the notice must concern one.
Step 2: Force Send promises a quick override
The button offers an immediate way past the supposed restriction. That is more appealing than investigating a server error while another task is waiting.
The label also changes the question. Instead of asking whether the notice is genuine, the reader starts thinking about whether the message still needs sending.
A legitimate delivery issue doesn’t give an unknown sender permission to choose your repair process. The proposed shortcut needs verification of its own.
Don’t repeatedly press the button when nothing obvious happens. Each attempt can return you to the same untrusted route without clarifying the original delivery status.
Step 3: CAPTCHA language makes the detour sound routine
The email says verification is required before the message can be forced through. CAPTCHA is familiar enough that the extra task may seem harmless.
But the word CAPTCHA is not a security certificate. It tells you what the page claims to do, not who controls it.
A genuine visual challenge should not become an excuse to disclose a password to a different service or run a system command.
This campaign’s inactive destination does not establish that a command-based challenge was used. If any copy adds that instruction, refuse it rather than treating it as normal verification.
Step 4: A login request can turn a resend attempt into account theft
A copied sign-in page can ask for credentials before delivering the promised result. The user thinks they are authorizing an email, while an impersonator receives the secret.
That access could expose far more than the supposedly blocked message. An inbox may contain recovery links, business discussions, and information used to impersonate its owner.
Those are risks to investigate, not proof that every person who received the email lost an account. What you submitted determines the response.
Do not test a suspicious form with another real password. An error message or apparent success cannot authenticate the website receiving it.
Was There Really an Email Waiting to Be Resent?
Match the notice to your own activity
Open the mailbox independently and find the message you believe failed. Compare the address, time, subject, and any reference supplied by the notice.
If no related message exists, that mismatch is a reason to distrust the claim. Don’t create a new account problem to explain an unfamiliar notification.
If a matching message does exist, continue checking. A real recent email can coincide with a fraudulent bounce or be referenced in an unrelated impersonation.
Distinguish a bounce from a message that is merely unanswered
No reply doesn’t mean delivery failed. The recipient may not have read the message or may need more time to respond.
If the matter is urgent, contact the recipient through an established alternative. Ask whether the message arrived without forwarding the suspect repair button.
A read receipt, delivery report, and personal reply also answer different questions. Avoid treating the absence of one as proof that you need a special resend service.
Keep business information out of public troubleshooting
A screenshot can expose names, customer addresses, private subjects, or attachment details. Remove unrelated information before asking for public help.
Your company’s IT team may prefer the original message with headers. Follow that private process instead of publishing the email’s complete contents online.
Never post a password or authentication code as evidence. The fact that a page requested a secret is useful; the secret itself is not.
A False Bounce Can Reveal a Separate Account Problem
Sometimes genuine bounce reports arrive for messages you didn’t send. That deserves attention, but it doesn’t automatically mean the visible account was compromised.
A sender address can be forged. A criminal may also use an actual compromised mailbox, so check real account activity rather than choosing one explanation immediately.
Look for unknown sent messages, sign-ins, or rules. Absence of a message from Sent is useful context, not a complete forensic conclusion.
If your provider reports unauthorized activity, follow its recovery instructions through the trusted account interface. Don’t use the original bounce as your recovery portal.
For work mail, ask the administrator to examine sending records. Server-side information may clarify what the desktop application cannot show.
Keep this separate from the Force Send lure. A genuine account issue would make a trustworthy repair route more important, not less.
Also avoid buying a delivery-fix utility from a stranger. A software download cannot be assumed necessary just because the email calls the message blocked.
If an unexpected program was already installed, the device needs assessment alongside the account. Resetting a password does not remove software from the computer.
What to Do if You Have Fallen Victim to This Scam
Leave the resend page. Don’t complete another challenge, submit another login, or approve a notification it tells you to expect.
Return to your mail service through a saved bookmark or installed app. Keep the fraudulent notice separate from any genuine delivery report.
Preserve the original notification. Record when it arrived and which action you took. Your mail provider’s phishing-report option can retain useful information.
If this is a work account, send the report through the established internal route. A screenshot alone may omit the actual destination or sender headers.
Secure a password you disclosed. Change it using the real provider’s settings, preferably from a device you know has not run suspicious software.
Replace reused passwords elsewhere and review existing sessions. Follow the provider’s recovery process if the intruder has already changed your access details.
Review the inbox for unauthorized changes. Inspect forwarding, filters, recovery contacts, and connected applications that your service lets you manage.
For business mail, ask IT to investigate wider access. Don’t delete potentially useful evidence before the team has decided what it needs.
Follow up with affected recipients. If your account sent fraudulent mail, warn those contacts using a trustworthy channel and identify the relevant time period.
For a legitimate unsent message, verify the destination and resend only through your normal mail application after the delivery issue is understood.
Check downloads and installed software. If the verification page prompted a download or you opened an unfamiliar file, assess that exposure separately.
Malwarebytes can help inspect the affected device. Use the operating-system section in the guide below, and retain the scan report for any further assistance.
Deal with money or identity information actually shared. Contact the relevant institution directly, explain what was disclosed, and keep its incident reference.
Don’t pay someone claiming they can force mail delivery or erase stolen account information. A fee does not make that promise credible.
Make the next false repair easier to reject. Keep email filtering, browser warnings, and software updates enabled.
AdGuard can reduce some risky advertising and redirect exposure. It cannot authenticate a mail sender or undo credentials typed into an imitation form.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Before You Send the Important Message Again
Once the account is safe, return to the original task. Check that the recipient address and attachments are correct before resending.
If a payment, contract, or deadline depends on that email, confirm receipt directly. Avoid sending several conflicting versions while troubleshooting.
A technical bounce and a fraudulent repair request can exist together. Resolve each through the party actually responsible for it.
If the original message included confidential material, avoid sending it repeatedly to variations of an address while guessing the correct recipient.
Confirm the address through an existing relationship first. A corrected delivery should not become an accidental disclosure to someone with a similar-looking mailbox.
For invoices or payment instructions, use your organization’s normal verification process before making any financial change suggested in a follow-up reply.
An attacker who knows a message was important may try another approach. Treat a new support call or replacement login link as a separate request requiring confirmation.
You can explain that you are resolving delivery without sharing the account password. A real recipient does not need your mailbox credentials to confirm receipt.
Keep a note of the final outcome, especially in business correspondence. That prevents a later reminder from sending you back into the same false delivery story.
Frequently Asked Questions
Is every Undelivered Mail Returned to Sender email a scam?
No. Genuine delivery failures exist. The warning here concerns the Force Send and verification lure, not every automated bounce report.
Can a CAPTCHA make an email bypass a recipient’s spam filter?
Don’t accept that promise from an unsolicited page. Diagnose the actual error through your provider instead of giving an unknown site control of the repair.
What if I clicked Force Send but entered nothing?
Close the page and check for downloads or permissions you granted. Clicking alone doesn’t establish that your mailbox password was stolen.
Why did I receive a failure for mail I never sent?
Possible explanations include a forged sender address or unauthorized account use. Review actual account activity with your provider rather than assuming one cause.
Will a virus scan restore my email account?
A scan addresses device threats. Account access, sessions, forwarding, and credentials require checks through the email provider.
Should I open the suspicious page to get its address?
No. Preserve the original message for reporting. You don’t need to revisit a dangerous destination to begin recovery or confirm a delivery problem.
The Bottom Line
Don’t use the Email Unable to Send notice’s Force Send button. Investigate a real delivery failure inside your normal mail service.
If you gave the page a password, recover the mailbox and inspect its access settings. Check the device separately if verification involved software or a download.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.