


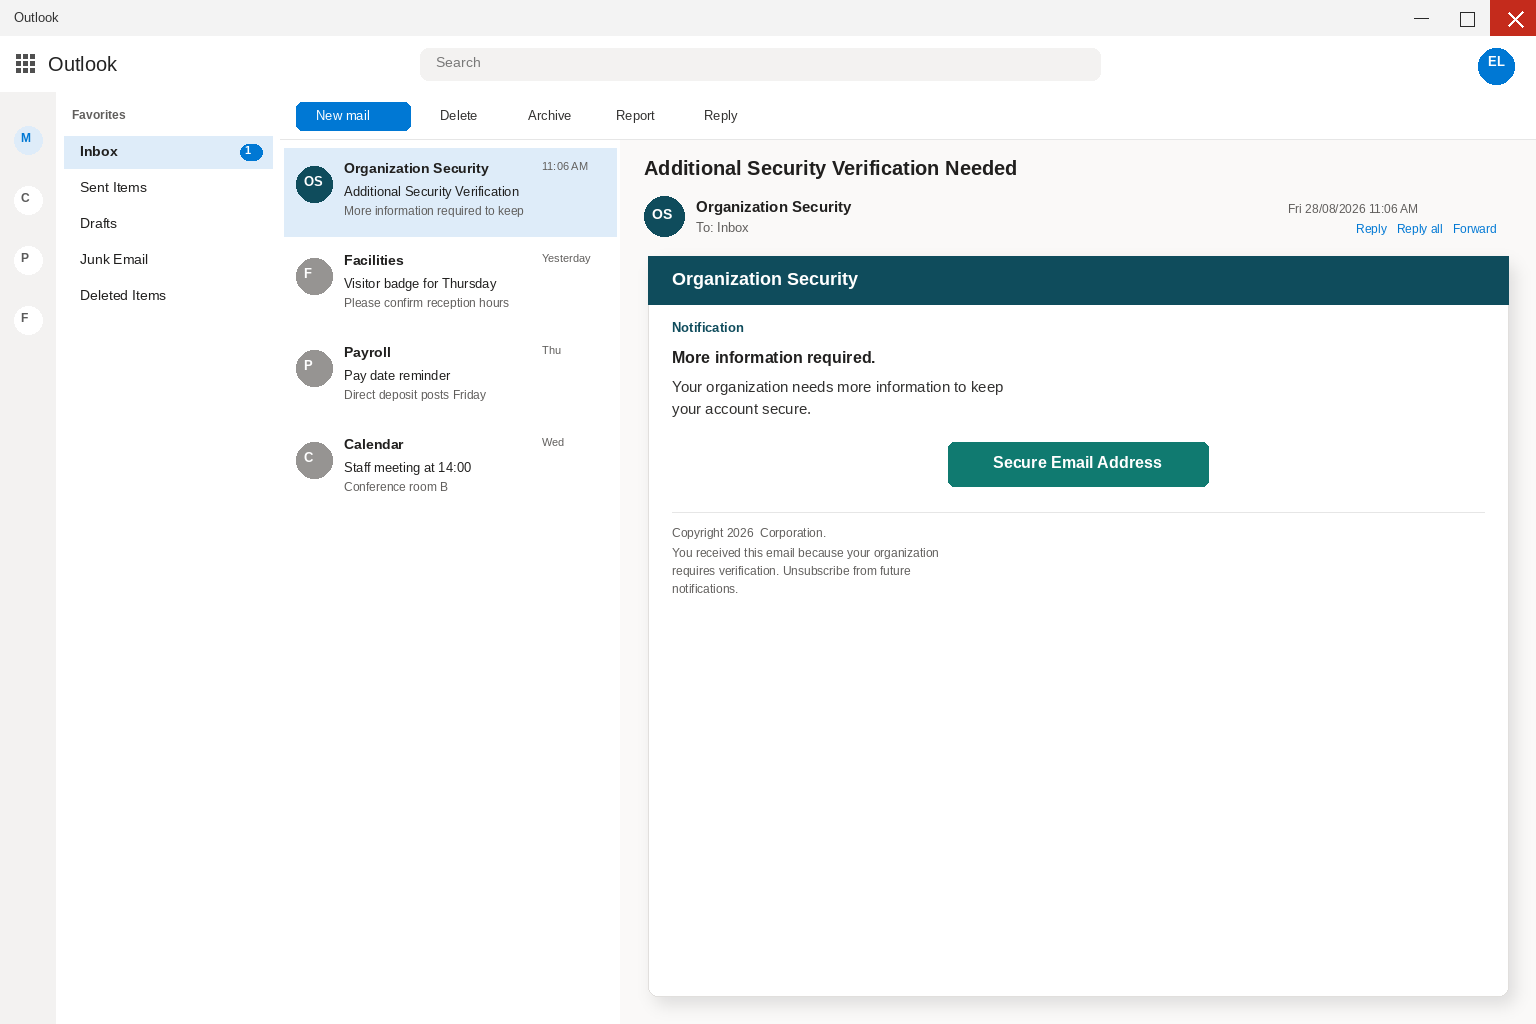
“Additional Security Verification Needed” sounds like a routine workplace task. The message depends on that familiarity before it asks the recipient to leave the inbox.
The large verification button is not there to secure an address. It leads to a credential-harvesting page chosen by the sender.
Overview
The organization language creates trust
The message says more information is needed to keep an account secure.
It sounds like a routine policy task, especially when the recipient already uses the mailbox for work.
The button hands the session to a copied portal
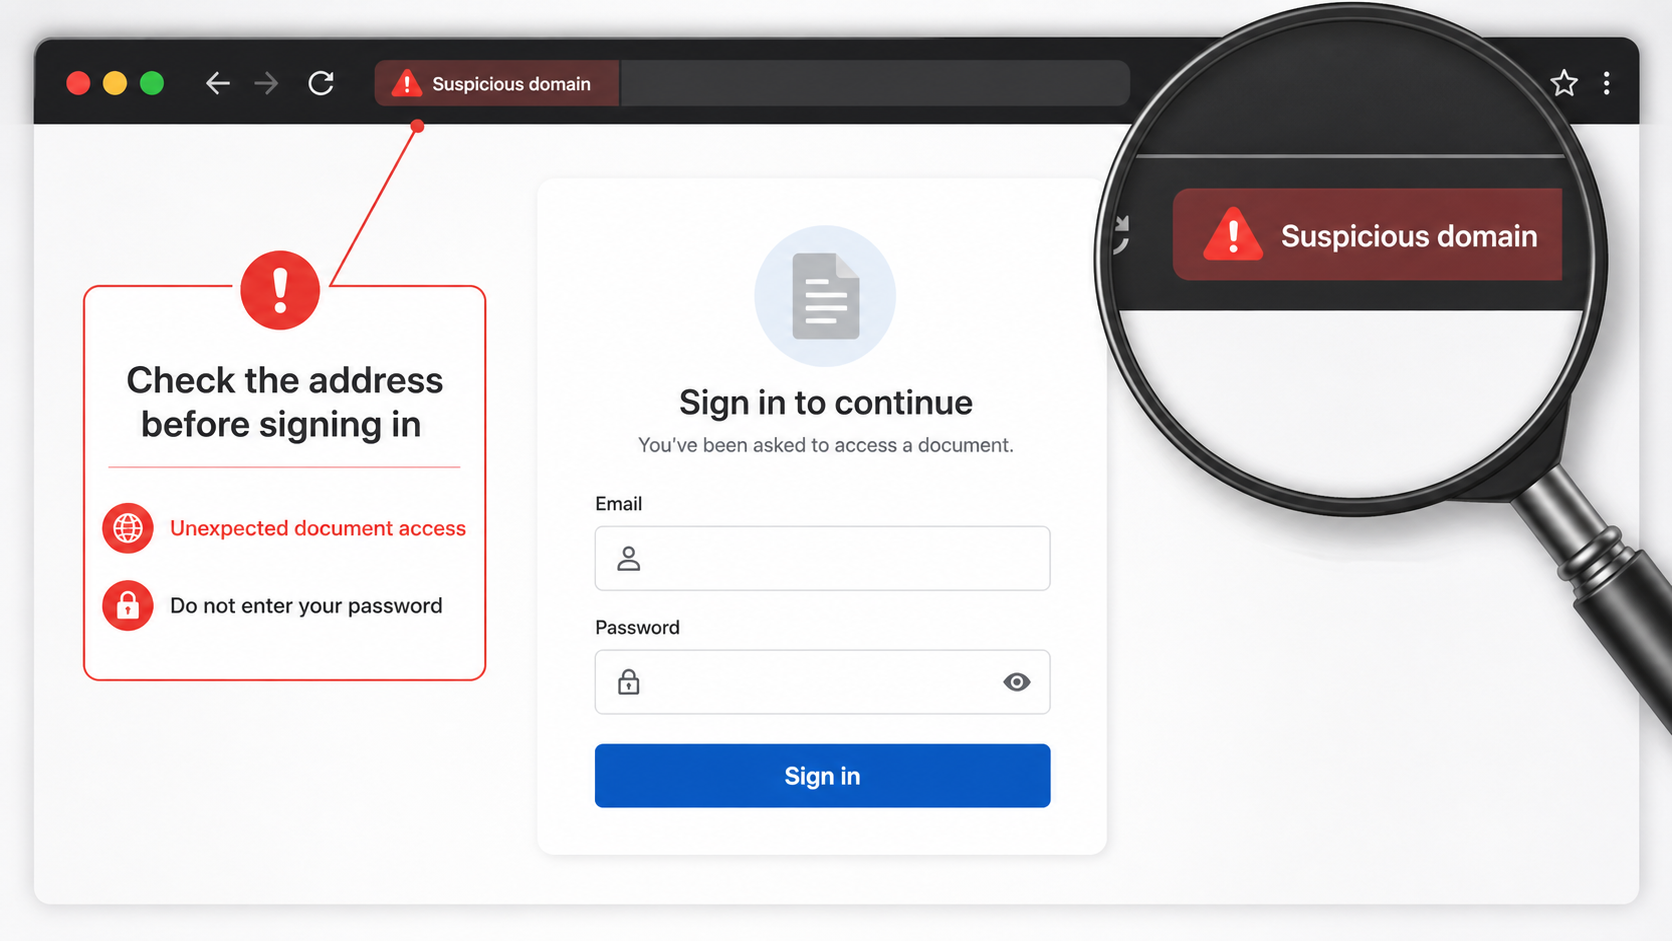
Instead of opening an internal setting, the button leads to a fake sign-in experience. The form can imitate the email service that the victim expects to see.
A stolen work inbox can cause a second loss
Once criminals control a mailbox, they can inspect invoices, reset linked accounts, and impersonate the employee in conversations that already look legitimate.
You are looking at a phishing letter, not a notice from the organization that pays your mailbox, because Secure Email Address does not lock anything down and,
does not confirm a workplace record.
The click opens a page that copies a Google login and asks for the email address plus the password that already opens the inbox you are sitting,
in, which is the whole harvest.
Once those two fields are typed, the people who wrote the notice can open the mailbox and read the threads you already trust.
They can also reset other logins that use that address, and they can send the next scare from your name.
The message poses as an organizational security notification, claims more information is required to keep the account secure, and treats Additional Security Verification Needed as if a,
desk already had a ticket waiting.
They also take the reset codes that arrive an hour later, and the threads with clients who already trust the address.
A copied Google sign-in is useful costume for that harvest, because a workplace button that then looks like a morning product feels like a continuation.
It does not feel like a stranger asking for a key, which is why the next screen gets finished before the address bar is read.
Google is a real company that runs a real account product, which is why a cloned Google login is useful to a thief and why a cloned,
login is not proof that Google sent the letter.
Anyone can put Organization Security on a From line, and anyone can stamp Notification above More information required.
Anyone can paste a 2026 copyright line onto a card that then offers an unsubscribe link as if this were a newsletter.
A real vendor does not collect a mailbox password through a surprise Secure Email Address button in a cold security note.
If you need Google’s own pages, type google.com yourself and open the account from a screen you already trust, rather than letting this letter choose the next tab.
steal passwords, account numbers, or Social Security numbers.
This letter applies the same pressure by claiming the organization needs more information to keep the account secure.
That habit is the opposite of fetching an extra verification from an organization-security letter you did not request.
It is also the opposite of typing a password into a copied Google door that the letter already picked.
An organization really can ask for more information, because workplaces do review accounts, and some mail products do prompt you to add a recovery address or a,
second factor after you open the product yourself.
the host you already pay.
It does not live behind a teal rectangle that chooses the next screen for you after a cold inbox notice.
Needed wants you to sit.
Secure Email Address is the click they need
mailbox you are already sitting in.
Additional Security Verification Needed has already done the shouting, the deadline, and the claim that the organization needs more information.
a help desk already opened with your name on it.
warning rather than as a badge you can trust.
On a phone that hover is awkward, and many people never see the real address before they tap.
The organization name is borrowed letterhead
the company you work for.
A real workplace exists, and people really do receive security mail from it, which is why the phrase is useful and why the phrase is not proof,
that the desk on your floor wrote this note.
People who steal mailbox passwords borrow letterhead from offices that already feel like policy, access reviews, and a badge you swipe in the morning.
They want you to treat the note as ordinary mail from your own building, rather than as a stranger asking for the key.
Anyone can set a display name to Organization Security, anyone can put Notification above More information required, and anyone can stamp Copyright 2026 on a card that,
then invites you to unsubscribe from future notifications.
Delivery only proves they knew the address that received the mail, and it does not prove they sat in a security office, reviewed an account, or had,
a ticket waiting for you.
If a partner who truly worked at that organization needed you, they would already have a thread, a portal you type yourself, or a phone you used last year.
They would not need a cold button that promises to secure an email address from a surprise card.
they chose for that purpose.
Do not call a number that appears only in the letter, and do not follow an unsubscribe link that sits under a security claim.
Those controls are part of the same costume, rather than a way to opt out of a real desk.
If you have an actual account with the workplace named in the body, pick up the number from a badge, a last year’s directory, or the site you typed yourself.
Ignore a stolen name on a verification card, even when the card already used the word organization.
Additional verification is not a help desk
The card only needs a little more information to keep the account open, which is how a request for a password gets dressed as care.
You are asked to secure an email address so the account can stay yours, which is a request for the key wearing quieter clothes.
The sentences inside the card are not random, because more information required makes the account feel incomplete and your organization needs more information makes the request feel local.
Keep your account secure makes a missed click feel like a dark inbox, which is enough pressure for a tired thumb.
help desk you already pay.
An unsubscribe line under a 2026 copyright is part of the same reversal, because a genuine access review is not a mailing list you opt out of.
A genuine security desk does not hide a login hunt under a newsletter footer either, which is why that line is costume.
- The vague organization label presents a security task without identifying a real department or a recognized internal case.
- The card writes Notification and then More information required, which turns an ordinary access review into a short emergency you can finish on a phone.
- It claims your organization needs more information to keep your account secure, so a missed click feels like a workplace failure rather than a postponed chore.
- The Secure Email Address button leads outside the organization’s usual account-management route.
- A copyright line and an unsubscribe option do not make an unexpected IT request legitimate.
- The copied Google-style page asks for work credentials instead of showing a verified workplace security review.
How The Scam Works
Step 1: A security notice lands
The display name says Organization Security as if a desk already had a queue waiting for you.
is a Monday that will not wait.
A tool the boss will ask about does the same work, and the costume only has to last until the button.
Step 2: The name copies the organization
The footer already copies a 2026 copyright line plus an unsubscribe offer as if a mailing had closed.
A teal bar plus More information required do the rest of that glance for a reader who only has five seconds.
the mailbox it just delivered mail into.
Step 3: Additional verification is the hurry
Additional Security Verification Needed sits over that claim as the subject, which makes the hurry look measured rather than theatrical.
walk without proving your password to a stranger.
That advice is the opposite of finishing an extra verification through a rectangle the letter provided.
Step 4: Secure Email Address is the handoff
The next page is not a console where an email address is hardened, and it is not a log of last week’s access review you can match,
against a ticket you already opened.
Step 5: The page copies Google
rather than like a stranger asking for a key.
Other addresses can be shown the layout they already see every morning, which is how the door adapts without changing the story on the button.
continuation rather than like a new request.
The fraudulent login used woodedreview.su, a domain unrelated to Google or a workplace security department.
the same verification notice.
wanted to secure an email address.
Step 6: They want the mailbox password
multifactor authentication if it is not already on.
those other accounts either.
notice becomes a payment problem.
That is why a verification notice that asked for a password was never about keeping an account secure.
Step 7: A second crew sells recovery
you is not your incident responder.
A security desk that called you after Secure Email Address is not the organization whose name was printed on the card, and it is not Google either.
Why Workplace Verification Notices Get Clicked
Employees are trained to respond to security notices and policy reminders. A generic organization label takes advantage of that helpful instinct during a crowded workday.
The email does not need to know much about the recipient. Familiar words such as verification, compliance, and secure access are enough to resemble internal correspondence.
A large button reduces the moment available for thought. It frames the action as a one-click administrative task instead of a decision to trust an outside website.
Real internal processes are usually visible in the tools employees already use. A message that creates a brand-new route deserves a second look before it is opened.
The Recipient Is Pushed Outside Normal Workflows
The fraudulent button attempts to move the employee from a known mailbox into a page chosen by the attacker. That change is the central risk in this campaign.
A genuine administrator can direct staff to an established identity portal or support channel. They do not need a surprise form to establish account ownership.
The fake page may imitate a popular mail product instead of the employer’s own site. That visual familiarity is meant to hide the unrelated address in the browser bar.
Before signing in, workers should compare the web address with the domain used by their organization. A small spelling change or unrelated ending is enough to stop.
A Compromised Work Inbox Creates Leverage
Business email often contains supplier threads, password resets, meeting invitations, and financial documents. Access lets criminals learn how real conversations are written and timed.
They can use that context to send a convincing request from the employee’s account. A forged payment change can look ordinary when it appears in an existing thread.
Mailbox rules can hide warnings while the attacker works. Reviewing forwarding, filters, delegates, and recent sent items is an important part of containment.
The earlier the workplace knows about the exposure, the easier it is to block abuse. A quick report can protect people beyond the person who clicked.
Verification Must Begin With a Known Contact
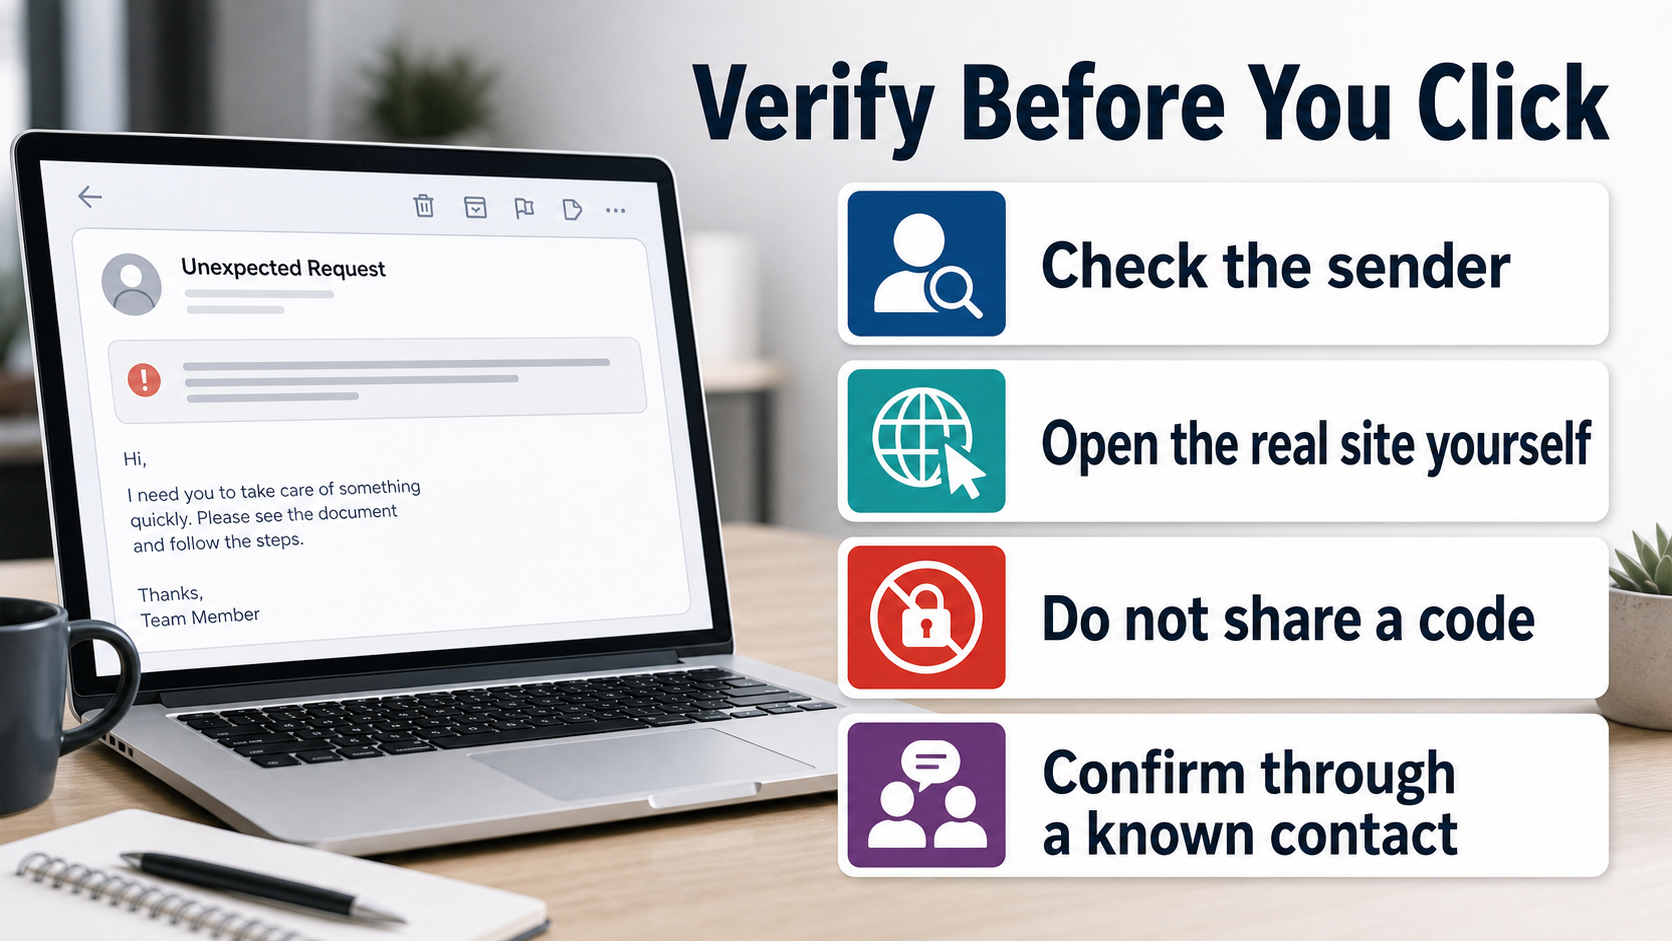
Use the company directory, help-desk portal, or a manager’s known contact details to check the claim. Do not use any address or phone number supplied by the email.
If the message is real, the security team can confirm it through an independent route. If it is false, they can warn others before the same button reaches them.
Never approve an authentication prompt that you did not start yourself. A code or confirmation can be as valuable to an attacker as the password.
The best test is not whether the email feels professional. It is whether the request appears inside the organization’s normal, independently verified workflow.
Company, Address, and Fulfillment Checks
A display name can borrow workplace authority
“Organization Security” is a label, not a verified department. Inspect the address behind the display name and compare it with messages your real support team has sent before.
The destination must match the service you use
A security review should appear inside the established mail product or company portal. An unrelated domain is a stop sign, even when the page uses a familiar logo.
The real help desk does not arrive through the lure
Call a number from the company directory or open a known support ticket.
The reply address, unsubscribe control, and phone number in the suspicious message are not safe verification paths.
The scam is built around access, not verification
The form wants the email password and may continue with a code prompt. Those details let an attacker bypass the very security process the message pretends to protect.
What to Do if You Have Fallen Victim to This Scam
- Save a screenshot of the message without clicking the button, then note whether you submitted a password or approved an authentication request. Give those details to the real IT or security team.
- Use the organization’s normal webmail route to change the affected password. Choose a fresh password that was not used on any personal or business service.
- Review active sessions, registered apps, recovery options, and recent sign-ins. Remove anything you cannot identify, then re-enroll multifactor authentication from the real account settings.
- Search mail rules, forwarding addresses, mailbox delegates, and sent messages. Attackers often hide their activity by moving security alerts or forwarding client conversations elsewhere.
- Warn finance, payroll, vendors, and close contacts if the inbox contains business communications. A quick out-of-band warning can prevent a forged invoice or changed payment instruction from succeeding.
- If a link downloaded a file or opened an unusual installer, run a complete Malwarebytes scan. Use AdGuard to block malicious advertising and reduce accidental visits to scam pages while you secure accounts.
- Report the email to the provider and workplace security team, then ignore follow-up callers who say they can finish the verification for a fee or by remote access.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Why does this message mention my organization?
The campaign can use a generic organizational phrase or information taken from public profiles. That wording does not prove the real employer sent the email.
Is it safe to press Secure Email Address just to look?
No. Unexpected verification buttons can redirect to credential pages or tracking links. Verify from a site or application you open yourself.
What does a fake sign-in page do with my password?
It sends the credential to the scam operator. They may try to access the mailbox immediately or use the password on other services.
What should a business do after one employee enters credentials?
IT should revoke sessions, reset the password, inspect mail rules, and watch for fraudulent messages or payment changes from that account.
Can HTTPS make the page legitimate?
No. HTTPS protects the connection to a site, but it does not prove that the site belongs to the brand or organization displayed on the page.
Should I forward the original email to coworkers?
Forwarding a live phishing link can create risk. Use the provider’s report option or send a screenshot and the message headers to the security team instead.
The Bottom Line
This campaign disguises a work-login theft attempt as a quiet organizational security task. The “Secure Email Address” button is the trap, not a tool for protecting the mailbox.
Use a known portal or a known contact to check security notices.
If credentials were entered, act quickly to regain control and warn anyone who could be targeted through the account.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.