


A signing request lands in your inbox without much context. It says the document is confidential, which might explain why you can’t see what it’s about.
The next screen is where the story starts to change. If you’re wondering whether a reader update is normal, it’s worth stopping there.
Overview
The first screen borrows a trusted signing service
The fake DocuSign document review email begins as a familiar work request.
It says a document needs your signature and suggests your access is being checked before you can view it.
There’s little to tell you who commissioned the document, how it relates to your work, or why the sender chose you.
The email leaves you to fill in those blanks.
Confidentiality provides a plausible explanation for that lack of detail. It doesn’t take away your ability to verify who sent a real request through a separate conversation.
Docusign is a real e-signature service. The email and the download page in this case are imitations, not evidence that Docusign or Adobe distributed a bad update.
An unfamiliar file replaces the agreement
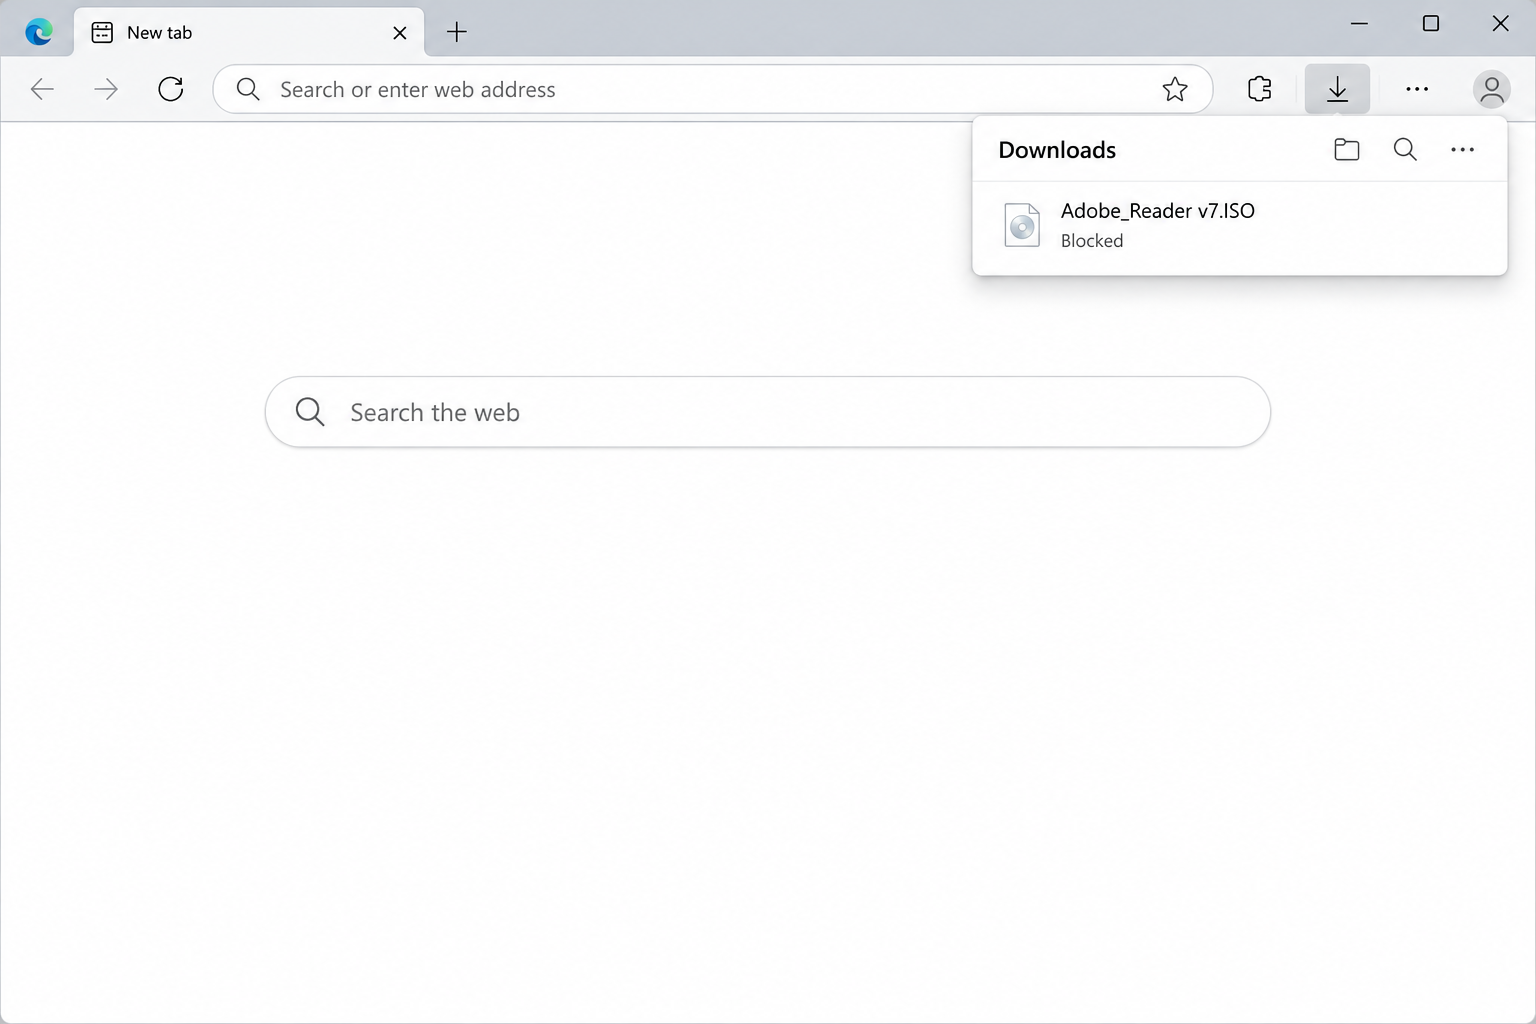
The page that follows claims an outdated copy of Adobe Reader is blocking access. Instead of an agreement, the reported download was named Adobe_Reader v7.ISO.
An ISO is a disk image, a container that can hold multiple items. It isn’t a PDF, and its familiar-looking name doesn’t make it an official installer.
The reported image contained a harmful Windows script. The important distinction for recovery is whether the file merely arrived in Downloads or whether something inside the image was run.
The lead image depicts the filename in a browser download panel. It doesn’t establish that your browser blocked the download or that the browser displayed that exact warning.
Identify what actually happened on your device
People often say they “opened the DocuSign” when they mean different things. That description can cover anything from reading the email to approving a Windows prompt.
An accurate account of your last action makes the response much easier to choose:
- Reading the email is not the same as visiting the linked page.
- Closing the page doesn’t necessarily erase a file the browser already downloaded.
- Seeing a disk image listed is different from opening its contents or running something inside.
- Entering a password on any later page adds an account problem, even if nothing ran on your computer.
The precise final payload wasn’t identified in the available case material. Don’t assume that a specific named Trojan was installed, and don’t assume it was harmless if a script executed.
How the Fake DocuSign Document Review Scam Works
Step 1: An unexpected signature becomes a small obligation
The email does not need to convince you that you signed anything. It just needs to make checking the request seem like part of your normal day.
That can be enough for someone in legal, sales, real estate, or purchasing. New signing requests are routine in those jobs, and their subjects don’t always tell the whole story.
Treat a request without a known sender or business context as something to confirm, not something to investigate using the link it supplied.
Step 2: The page explains the missing document with an update
Instead of showing the agreement, the next page looks like an Adobe Reader notice. It claims the software you need to view the document is out of date.
The brand switch is the warning. A signature request has unexpectedly become a software installation task, and the website making that demand isn’t an Adobe update channel you chose.
People who use PDFs every day can still miss this. An update dialog is something they have learned to clear quickly, especially while another person supposedly waits for a signature.
Step 3: The download goes into a different category
The reported package uses an Adobe-like filename with a disk-image extension. A familiar first half of the name does not change the kind of file that actually arrived.
Windows may hide some filename extensions in its usual folder view.
If you’re checking an unexpected item, look at the browser’s download history or use the file listing without opening it.
A download entry can also be marked blocked or removed. Read the actual status, not just the file’s name. Don’t override a block to see whether the item is safe.
Step 4: Running a script changes the response
The suspicious image carried code rather than the promised document. Executing untrusted code is the point where a misleading email can become a device compromise.
Not all harmful changes announce themselves. No new window, no error, and no visible document don’t tell you whether that execution succeeded.
Don’t try the file on a second device or run it again for a screenshot. The relevant evidence is what happened on the first computer, when, and under which account.
How to Check a Real Signature Request Without Touching the Download
Verify the sender on a route you control
Call or message the person who supposedly sent it using a contact you already know.
Ask for the matter, organization, and document title without repeating any sensitive information from the email.
If the request was unexpected but genuine, the sender can confirm its purpose and resend through the agreed channel. A real deadline doesn’t prevent that conversation.
An apparent reply address isn’t an independent channel. Even a reply from a known mailbox may be misleading if the mailbox itself has been taken over.
Use the real signing or software service
Open the signing service from your usual bookmark or work portal. Docusign’s safety center explains the official ways to report a suspicious signing request.
If a supposed document viewer tells you to update, close the external page. Use the software’s own update mechanism or follow Adobe’s official Reader instructions.
Managed computers often get updates through a company portal. A webpage cannot grant permission to bypass that process, even if it appears at the exact moment you expected a document.
Give your IT team a useful timeline
Include the subject, the email time, and whether you saw a browser page before the download. Identify the computer if your account signs in to more than one.
Tell them if the browser blocked anything, if a file appeared, or if you clicked a permission prompt.
Those are more useful facts than whether the page looked exactly like Adobe.
Use the reporting route your organization provides. Don’t attach an untrusted disk image to an ordinary email thread or upload a confidential signing message to a public inspection service.
What to Do if You Have Fallen Victim to This Scam
The scan guide after this list is for suspected device exposure. A signing email in the inbox isn’t itself a reason to run it.
If you only saw the message, report it as phishing. Close any message preview that makes you uneasy. You don’t have to click the button to check whether it works.
On a work mailbox, leave the original available to IT through the usual reporting tool. It’s useful for finding other deliveries of the same campaign.
If you reached the page, check for a download. Close the tab. Use the browser’s own Downloads panel and note whether an ISO appeared and whether it was blocked.
Do not click Open, Keep, or a similar action to investigate. Your security team may want the preserved evidence even if the download never ran.
If you started anything from it, stop using that device for sensitive work. Disconnect it from Wi-Fi or Ethernet if safe. Call IT from an unaffected device.
Report whether you saw a system prompt and what you selected. On a managed device, let IT decide whether to collect evidence, quarantine, scan, or rebuild.
Secure any accounts you exposed. From a clean device, change passwords you entered on a suspicious screen and notify the relevant service. Tell IT if you approved a sign-in prompt.
A scanner won’t sign out an intruder or undo an approval. Have the provider review recent access and terminate sessions that shouldn’t be there.
Check for follow-up contact. A second message may claim to be “IT” or the original sender helping you finish. Use only the case number and contact route you established independently.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Run Malwarebytes on personal Windows if you executed something or have credible evidence it ran. On a work device, stop and follow your organization’s response procedure.
AdGuard may help reduce exposure to some malicious pages in the future. It doesn’t remove a file you already ran or determine whether a work endpoint is safe.
Check a Personal Windows Computer After Possible Execution
Decide who should do the cleanup
If your device belongs to work or handles sensitive client records, let the incident team direct the response. Uncoordinated restarts and cleanup can erase clues they need.
For personal Windows, use a trusted device to obtain tools, and keep the affected one away from banking, email, and shared drives while you arrange cleanup.
Use an authorized Windows scan and read the results
Start by opening Windows Security and checking Virus & threat protection. Review Protection history for detections close to the time of the download or execution.
Microsoft’s Windows Security guide explains Full scan and Microsoft Defender Offline. The offline option restarts Windows, so save safe work and confirm access to your recovery key.
Use the installed scanner or obtain a known installer through the site’s verified download in the scan guide. Leave detections quarantined unless a trusted technician confirms a mistake.
If the scanner won’t start, protection has been disabled, or detections return after restart, seek help instead of repeatedly trying the same cleanup.
Match the result to what was exposed
An empty scan isn’t evidence that every earlier action was benign. If you signed into important services after running the file, tell their support teams what happened.
On a work incident, preserve the security report and note any accounts used on that device. Those details help the organization decide whether other people or systems need checking.
Don’t wipe the system just to clear the browser record. If rebuilding is needed, plan how to preserve files safely and restore only from trusted, verified sources.
The Update Question Is Separate From the Signature
An installed reader already has a trusted update path
A genuine PDF that needs a feature your version lacks can still be checked through the sender. Ask for another format or use software your organization already approves.
Open the installed reader on its own if you need to check its version. Don’t let a message dictate where you get an installer. Use an official software source.
An Adobe logo is not the same thing as a confirmed publisher. Don’t try to settle that question by opening a file you got through an unrelated signing link.
A successful download is not a signed agreement
If you expected a contract, notify the sender that it hasn’t been signed. Some teams move on when they think the other party received the request, so clarify the status.
If it did come from a customer or coworker, ask them for their usual signing channel. If they don’t recognize the request, share the phishing report with your own organization.
Staff who handle documents for several clients should also record which client environment was active. That can matter when access needs to be suspended without disrupting unrelated work.
Don’t let a cleanup erase the only useful clue
Keep the reported filename and the time even if the file is gone. A browser warning and the security product’s identification are more useful than a recollection of “something Adobe.”
If you spoke to IT already, attach new information to the same ticket. That keeps the mail, endpoint, and account findings together when different teams review them.
Frequently Asked Questions
Is the DocuSign document review email actually from Adobe?
No. The email imitates a signing request. The reported browser page then imitates an Adobe update notice to make the unexpected Windows download look routine.
Is Adobe_Reader v7.ISO a PDF attachment?
No. In this campaign it was a downloaded disk image, not the agreement and not a PDF. Don’t open it to check its contents.
What if the browser says it blocked the file?
Don’t override the block. Report the message and note the filename and time. If you didn’t run another copy, the block is useful information for IT.
What if the ISO showed up but I never opened it?
Don’t open it now. Preserve the details for IT if it’s a work computer. A completed download alone doesn’t establish that its contents executed.
Does this email prove that someone stole my passwords?
No. Receiving the message doesn’t establish password theft. Executing its file or entering a password on another suspicious page calls for a separate account and device review.
Can I confirm a genuine signing request without the email button?
Yes. Contact the sender independently and use the official signing service or approved company workflow. A page that requires an unfamiliar update is not a verification route.
The Bottom Line
Don’t use the DocuSign document review email to install Adobe Reader. Verify the signature request separately, and get any updates from Adobe or your organization.
If you ran anything from the download, isolate the affected computer and get help from a clean device. Report exactly what ran, even if Windows looks normal.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.