

If only the browser is blocked: press Esc to leave full screen, then close the tab. If it will not close, press Ctrl + Shift + Esc, select the browser in Task Manager, and choose End task. Reopen it without restoring the scam tab. Use the recovery options below if Windows itself remains locked or you ran a downloaded file.
Remove any Police Ukash,MoneyPak or PaySafecard virus
This page is a comprehensive guide, which will remove the Police Ukash or Moneypak infection from your computer. Please perform all the steps in the correct order. If you have any questions or doubt at any point STOP and ask for our assistance. The Police Ukash or Moneypak will start automatically when you login to your computer and display its screenlocker so that you are unable to access your computer, therefore we will need to remove this infection by using any of the below methods: OPTION 1: Remove Police Ukash or Moneypak lock screen virus with System Restore OPTION 2: Start Windows in Safe Mode and run the removal tools OPTION 3: Remove Police Ukash or Moneypak virus with Kaspersky Rescue Disk
OPTION 1: Remove Police Ukash or Moneypak lock screen virus with System Restore
System Restore helps you restore your computer’s system files to an earlier point in time. It’s a way to undo system changes to your computer without affecting your personal files, such as e‑mail, documents, or photos. If the lock screen prevents normal access, open Windows Recovery Environment to use System Restore. On Windows 10 and 11, use the recovery menu below rather than repeatedly pressing F8. Have the BitLocker recovery key for this PC ready if it is requested.STEP 1: Restore Windows to a previous state using System Restore
- At the Windows sign-in screen, hold Shift while choosing Power → Restart. If Windows already shows Automatic Repair, choose Advanced options. If you cannot reach either screen, boot from official Windows installation media and choose Repair your computer.
On an older Windows 7 PC, F8 may still open Advanced Boot Options. Windows 10 and 11 normally use the recovery menu above; do not keep interrupting startup to chase the old menu.
- Choose Troubleshoot → Advanced options → System Restore. Select your Windows installation and account if asked, and unlock the drive with its recovery key if prompted.
- Click Next in System Restore and choose a restore point from before the lock screen appeared. If no restore point is available, cancel and try another recovery option; do not create a new restore point expecting it to undo an existing infection.
The older rstrui.exe command opens System Restore from a working Windows session or a compatible Safe Mode session. You do not need that command when you opened System Restore through the recovery menu.
- System Restore should start, and you will display also a list of restore points. Try using a restore point created just before the date and time the Police Ukash or Moneypak lock screen virus has infected your computer.
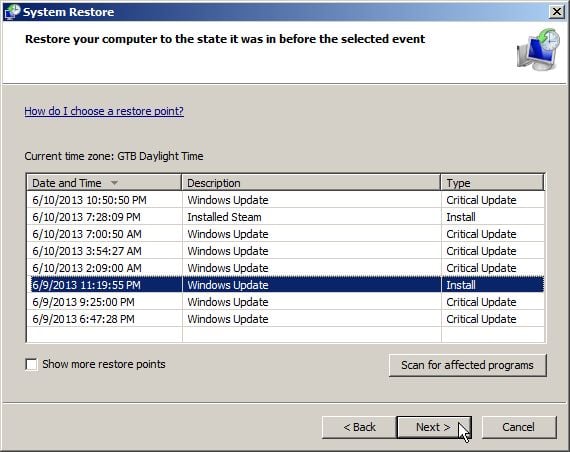
- When System Restore has completed its task, start your computer in Windows regular mode, and perform a scan with Malwarebytes Anti-Malware and HitmanPro, as seen in the next step.
STEP 2: Remove Police Ukash or Moneypak malicious files with Malwarebytes Anti-Malware Free
Malwarebytes Anti-Malware Free uses industry-leading technology to detect and remove all traces of malware, including worms, Trojans, rootkits, rogues, dialers, spyware, and more. It is important to note that Malwarebytes Anti-Malware works well and should run alongside antivirus software without conflicts.- You can download download Malwarebytes Anti-Malware from the below link. Download MalwarebytesFree official installer. Your download starts right away.
- Save your work, open Downloads, and double-click the current MBSetup installer. Approve the Windows prompt only after checking that it identifies Malwarebytes.
 You may be presented with a User Account Control dialog asking you if you want to run this file. If this happens, you should click “Yes” to continue with the installation.
- When the installation begins, you will see the Malwarebytes Anti-Malware Setup Wizard which will guide you through the installation process.
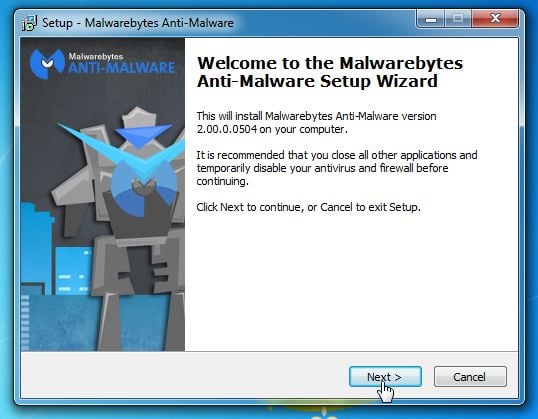 To install Malwarebytes Anti-Malware on your machine, keep following the prompts by clicking the “Next” button.
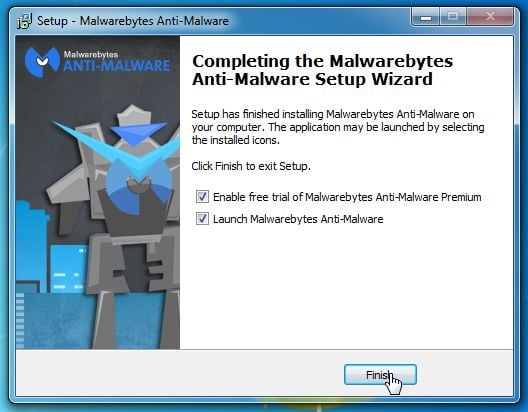
- Open Malwarebytes and click Scan on the dashboard. The normal Threat Scan checks common malware locations. If setup offers a subscription or optional browser extension, review it and skip offers you do not want. For a targeted scan, open the scanner options and choose Custom Scan; a rootkit check is optional there and is unavailable on Windows ARM.
- Allow Malwarebytes to update its detection database before the scan. If the update fails, check your connection and retry; record any error instead of assuming that old definitions are current.
- Malwarebytes Anti-Malware will now start scanning your computer for the pop-up virus. When Malwarebytes Anti-Malware is scanning it will look like the image below.
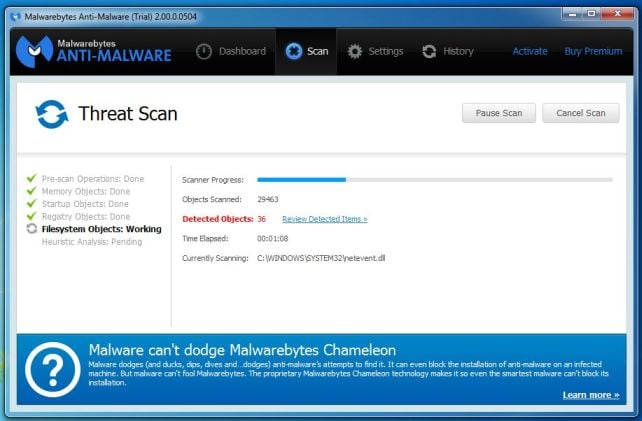
- When scanning finishes, review the detected items. Leave confirmed threats selected and click Quarantine. Save the report if you need help assessing an item before excluding or restoring it. Please note that the infections found may be different than what is shown in the image.
- Malwarebytes Anti-Malware will now quarantine all the malicious files and registry keys that it has found. When removing the files, Malwarebytes Anti-Malware may require a reboot in order to remove some of them. If it displays a message stating that it needs to reboot your computer, please allow it to do so.
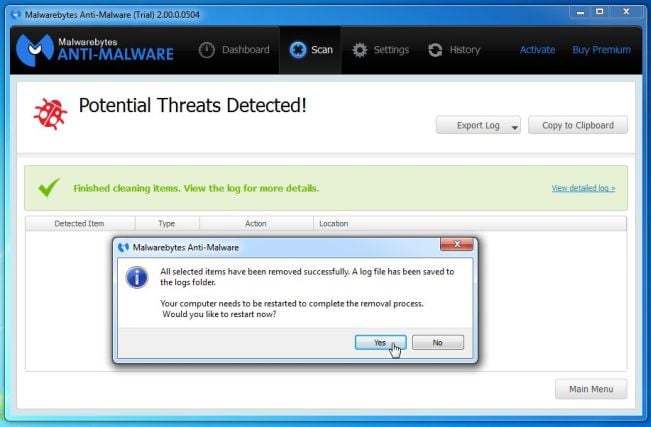 After your computer will restart, you should open Malwarebytes Anti-Malware and perform another “Threat Scan” scan to verify that there are no remaining threats
 You may be presented with a User Account Control dialog asking you if you want to run this file. If this happens, you should click “Yes” to continue with the installation.
 To install Malwarebytes Anti-Malware on your machine, keep following the prompts by clicking the “Next” button.
 After your computer will restart, you should open Malwarebytes Anti-Malware and perform another “Threat Scan” scan to verify that there are no remaining threats
STEP 3: Double-check for the Police Ukash or Moneypak virus with HitmanPro
HitmanPro is a second opinion scanner, designed to rescue your computer from malware (viruses, trojans, rootkits, etc.) that have infected your computer despite all the security measures you have taken (such as anti virus software, firewalls, etc.). HitmanPro is designed to work alongside existing security programs without any conflicts. It scans the computer quickly (less than 5 minutes) and does not slow down the computer.- You can download HitmanPro from the below link: Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats.
- Double-click on the file named “HitmanPro.exe” (for 32-bit versions of Windows) or “HitmanPro_x64.exe” (for 64-bit versions of Windows). When the program starts you will be presented with the start screen as shown below.
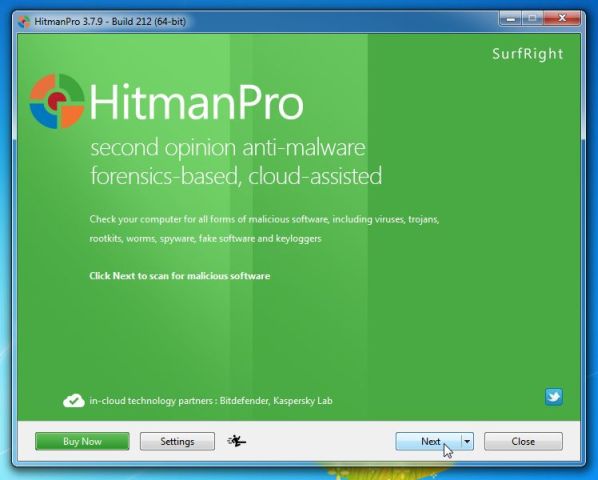 Click on the “Next” button, to install HitmanPro on your computer.
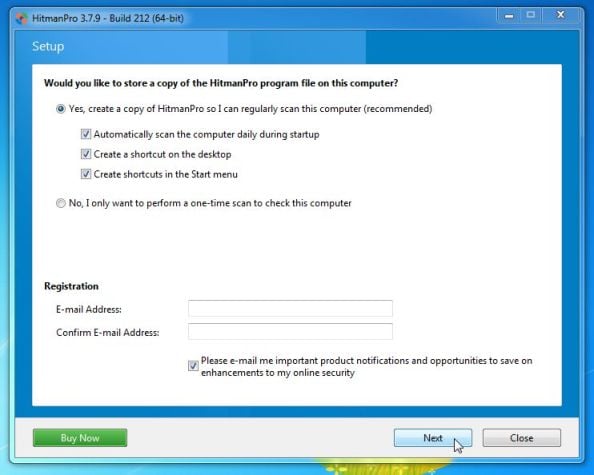
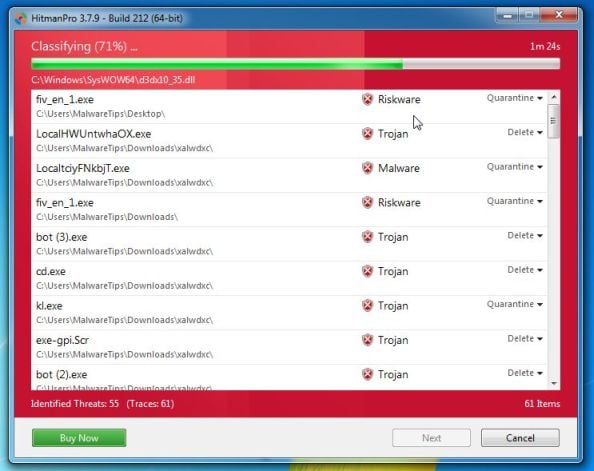
- HitmanPro will now begin to scan your computer for any malicious files that may be on your machine.
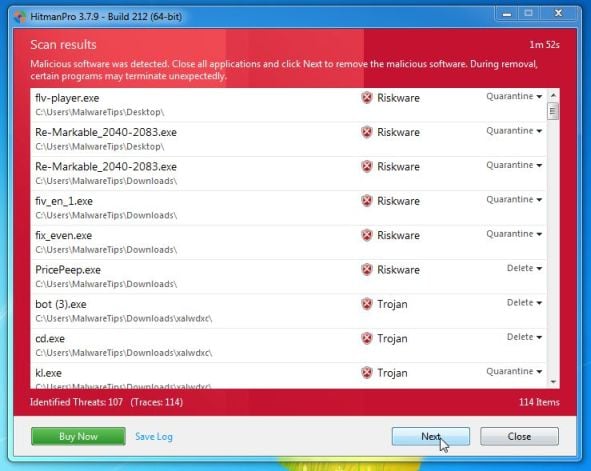
- When it has finished it will display a list of all the malware that the program found as shown in the image below. Click on the “Next” button, to remove any virus that has been found.
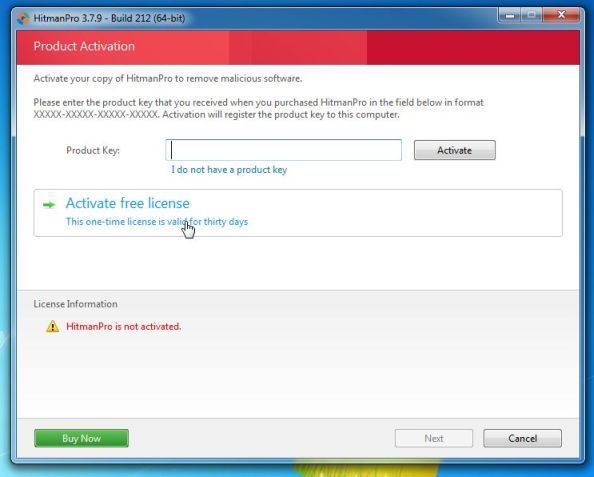
- If this PC is eligible, click Activate free license and follow the prompts for the one-time 30-day trial. If it was already used, an existing paid license is required for removal; scanning remains free. Keep the report if you need help deciding what to remove.
 Click on the “Next” button, to install HitmanPro on your computer.
OPTION 2: Start Windows in Safe Mode and run the removal tools
If System Restore is unavailable, try Safe Mode to reach Windows without the screen locker starting normally. The older HitmanPro Kickstart USB instructions do not describe the current HitmanPro download. Do not look for a Kickstart USB button or download an old copy from an unofficial site.
Open the recovery menu.
At the sign-in screen, hold Shift and choose Power → Restart. If you cannot reach it, use Advanced options on the Automatic Repair screen, or boot Windows installation media and choose Repair your computer. Keep your BitLocker recovery key available.
Start Safe Mode.
Select Troubleshoot → Advanced options → Startup Settings → Restart. Press 4 or F4 for Safe Mode. If you need online scanner updates, 5 or F5 requests Safe Mode with Networking, although Wi-Fi may be unavailable.
Sign in and run a scan.
You may need your account password rather than your PIN. Run the Malwarebytes steps above. If a scanner cannot install or work in Safe Mode, do not keep forcing it; use the rescue-disk option or ask for removal help. A clean computer can be used to download the installer to a USB drive, but that does not make the installer a bootable rescue disk.
Use HitmanPro when Windows can run it.
The download below is the normal Windows scanner. Follow the HitmanPro steps above when it runs successfully and has a working connection for cloud checks. Removal requires an eligible trial or a license.
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats.Restart into normal Windows and check again.
After quarantining detected threats, restart normally. Confirm that the lock screen is gone and review the scan reports. If it returns, save the exact detection names and ask for help instead of paying the demand. If files are also encrypted, preserve the ransom note and encrypted originals before attempting recovery.
OPTION 3: Remove Police Ukash or Moneypak virus with Kaspersky Rescue Disk
If any of the above methods did not clean your infected computer, we can use a Kaspersky Rescue Disk Bootable to clean the Windows registry and to perform a system scan to remove the Police Ukash or Moneypak virus. To create a bootable Kaspersky Rescue Disk, we will need the following items:- A clean (non-infected) computer with Internet access
- A blank DVD or CD
- A computer with a DVD or CD burner
STEP 1: Download and create a bootable Kaspersky Rescue Disk CD
- You can download Kaspersky Rescue Disk utility from link below: Download Kaspersky Rescue DiskOpens the download page in a new tab.
- To create the bootable rescue disk, we will need to use the ImgBurn program. You can download ImgBurn from the below link, then install this program. Download ImgBurnOpens the download page in a new tab.
- Insert your blank DVD or CD in your burner, then start ImgBurn and click on the Write image file to disc button.
- Under Source click on the Browse for file button, then navigate to the location where you previously saved the Kaspersky Rescue Disk utility (krd.iso), then click on the Write button.
 That’s it, ImgBurn will now begin writing your bootable Kaspersky Rescue Disk.
 That’s it, ImgBurn will now begin writing your bootable Kaspersky Rescue Disk.
STEP 2: Start your computer using the Kaspersky Rescue Disk
- Once you’ve got the Kasperky Rescue Disk in hand, insert it into the infected computer, and turn off and then turn it on again.
- Choose the USB drive or DVD from the computer’s one-time Boot Menu, using the key specified by its manufacturer. Follow the rescue startup prompts and choose your language.
- Choose Graphic mode and wait for the rescue environment to load. If that mode fails, try Limited graphic mode. Read and accept the displayed agreements if you agree.
STEP 3: Scan your system with Kaspersky Rescue Disk
- Wait for Kaspersky Rescue Tool to open. If the Windows drive uses BitLocker, unlock it with your recovery key or other supported credentials; do not format it.
- If the tool reports outdated databases, click Update now, let the download finish, and restart the scanning application if prompted. You can check the database date in About.
- Review the scan scope, include the Windows drive you intend to check, and click Start scan. Let it finish and review the results.
- Review each detection and the proposed action. Use disinfection when available for an infected system file; do not blindly delete Windows components. Save the report and seek help if you cannot assess a detection.
- When the antivirus scan has completed, you can restart back into Windows regular mode, by clicking on the Kaspersky Start button
 (lower left corner), and selecting Restart.
Once your computer will start in Windows regular more, download Malwarebytes Anti-Malware and HitmanPro, and scan your computer for any left over infections.
 (lower left corner), and selecting Restart.
Once your computer will start in Windows regular more, download
Your computer should now be free of the Police Ukash or Moneypak infection. If your current anti-virus solution let this infection through, you may want to consider purchasing the PRO version of Malwarebytes Anti-Malware to protect against these types of threats in the future, and perform regular computer scans with HitmanPro. If you are still experiencing problems while trying to remove Police Ukash or Moneypak virus from your machine, please start a new thread in our Malware Removal Assistance forum.

Hello,
Spyhunter is not a good on-demand scanners, I don’t know what infection is reporting, but I recommend that you run instead a scan with the below tools, just to be on the safe side:
STEP 1: Run a scan with ESET Online Scanner
1.Download ESET Online Scanner utility.
ESET Online Scanner Download Link : http://download.eset.com/special/eos/esetsmartinstaller_enu.exe
2. Double click on the Eset installer program (esetsmartinstaller_enu.exe).
3.Check Yes, I accept the Terms of Use, then click the Start button.
4.Check Scan archives and push the Start button.
5. ESET will then download updates for itself, install itself, and begin scanning your computer. Please be patient as this can take some time.
6. When the scan completes, click on the Finish button.
STEP 2: Run a scan with Kaspersky Virus Removal Tool:
1. You can download from Kaspersky Virus Removal Tool from here : http://www.kaspersky.com/antivirus-removal-tool?form=1
2. Double click the setup file to run it, then follow the onscreen prompts until it is installed
Click the Options button (the ‘Gear’ icon), then make sure only the following are ticked:
System Memory
Hidden startup objects
Disk boot sectors
Local Disk (C:)
Also any other drives (Removable that you may have)
3. Then click on Actions on the left hand side
4. Click Select Action, then make sure both Disinfect and Delete if disinfection fails are ticked
5. Click on Automatic Scan, then click the Start Scanning button, to run the scan
I swear I never did anything of what I was accused in the message. I have in the past use system restore, but now even if I am able to run it in full, I cannot go on line because the UKASH message comes up immediately. Any advice ?
Hello Bambolo,
This notification is a scam, so I believe you when you say that you did not do anything! To remove this infection however, you will need to create a bootable HitmanPro USB stick or Kaspersky Rescue Disk as seen in this guide.
Thank Christ- actually shat myself when I saw this message. Was determined to watch my downloaded version of dexter before the police came knocking though….
Hello,
That’s strange. :)
HitmanPro has a free 30 days trial for home users, only those who are using a corporate or business computer will not get the free trial.
Anyway, the Kaspersky Rescue Disk should do it’s job fairly well. Good luck! And keep me up-to-date. :D
Stelian: Yep, it’s on a domain, it’s a business PC. The Kaspersky scan is rather comprehensive – looks like it’ll take nearly 2 hours! Hasn’t found anything yet though.
Also, had nothing but problems creating a bootable USB key for Kaspersky – the supplied utility (https://support.kaspersky.com/8092) failed to create a bootable partition on two USB keys! Good thing I still have a spindle of blank CDs/DVDs and ImgBurn is brilliant.
Can you let me know if you have any success with making a bootable USB key with it? Just had a thought as to why it failed – Trend WFBS (Corporate AV) blocking it. It’s not the first time.
Cheers,
-timb
Hello,
Yes, the Kaspersky scan will take awhile, however this bootable disk will allow you to view files on your computer and access the Internet, so you’ll have something to do.
FYI, you could browse to the infected file, and just delete it from your machine, if you know what you are doing then this is the most fastest way to solve this issue.
Here are the usual locations for this type of infections:
(malware path)(random).exe”
(malware path)(random).dll
%AppData%(random characters)
%CommonAppData%(random characters)
%LocalAppData%(random characters)
%UserProfile%Templates(random characters)
File Location Notes:
%UserProfile% refers to the current user’s profile folder. By default, this is C:Documents and Settings(Current User) for Windows 2000/XP, C:Users(Current User) for Windows Vista/7/8, and c:winntprofiles(Current User) for Windows NT.
%CommonAppData% refers to the Application Data folder for the All Users Profile. By default, this is C:Documents and SettingsAll UsersApplication Data for Windows 2000/XP and C:ProgramData in Windows Vista, Windows 7, and Windows 8.
%AppData% refers to the current users Application Data folder. By default, this is C:Documents and Settings(Current User)Application Data for Windows 2000/XP. For Windows Vista and Windows 7 it is C:Users(Current User)AppDataRoaming.
%LocalAppData% refers to the current users Local settings Application Data folder. By default, this is C:Documents and Settings(Current User)Local SettingsApplication Data for Windows 2000/XP. For Windows Vista, Windows 7, and Windows 8 it is C:Users(Current User)AppDataLocal.
%CommonAppData% refers to the Application Data folder in the All Users profile. For Windows XP, Vista, NT, 2000 and 2003 it refers to C:Documents and SettingsAll UsersApplication Data, and for Windows Vista, Windows 7, and Windows 8 it is C:ProgramData.
Stay safe!
PS. I also have issues while trying to create a USB stick with Kaspersky, so it’s not your fault. I have sent an email to the Kaspersky devs awhile ago and they said it would be fixed….. I’m still waiting. :)
Awesome! Thank you!
Thank you! I have used the HitmanPRO USB stick! Thank you!
Hello,
Can you please start a thread in our Malware Removal Assistance forum: http://malwaretips.com/Forum-Malware-Removal-Assistance
It’s free, and this will allow us to take an in-depth look at what’s going on your machine. :)
Hello,
Yes, the Kaspersky Rescue Disk will work on any operating system, including Windows XP.
Hello,
Your Windows Hosts file is most likelyinfected. Please run this fix file: http://go.microsoft.com/?linkid=9668866
Then run a computer scan with Malwarebytes and HitmanPro.
Good luck! Stay safe!
Not tried yet, hopefully will work
thanks
Hello,
ImgBurn is a safe program, you antivirus is generating a false possitive detection/…You can ignore this alert.
Alternatively, you can use another burning program like Nero.
Stay safe!
Hello David,
Did you try to scan with the HitmanPro Kickstart program?
The infected file should be on the C: drive….. Can you try to load again the CD, and see if this will fix your issue. Alternatively, you can start Kaspersky in Text Mode rather then Graphic, and see if C: is detected there.
Lets try to clean your registry:
Click the button К ; in the bottom right corner of the screen and in the menu select Terminal. In the command prompt enter the command windowsunlocker and press Enter on the keyboard. After the registry cleanup process has completed, try to see if the screen locker was removed.
If not, you will need to open Kaspersky File Manger, and go to either:
C:Documents and SettingsApplication Data for Windows 2000/XP. For Windows Vista and Windows 7 it is C:UsersAppDataRoaming.
OR
For Windows XP go to C:Documents and SettingsAll UsersApplication Data, and for Windows Vista, Windows 7, and Windows 8 it is C:ProgramData
And find and delete any suspicious file. Usually this is a .exe file or a .dat program.
Good luck!
Thank you for your help!
I did not try to scan with the HitmaPro, i just put Kaspersky instead.
While my laptop was scanning, it found ‘Trojan program HEUR:Trojan. Scriptlframer’ As a result, I deleted it. Is this the virus?
Hello David,
Yes, it’s a virus, and most likely the entry point of this infection. Nevertheless there might be other malicious files on this computer. Let the scan complete and then try to start your computer in Windows regular mode.
Stay safe!
Hello Ewan,
This infection, is not to related to this ransomware, nevertheless we need to remove it.
Lets run a scan with the following tools:
Run a scan with RogueKiller
1. Please download the latest official version of RogueKiller.
RogueKiller Download Link : http://www.sur-la-toile.com/RogueKiller/RogueKiller.exe
2. Double click on RogueKiller.exe to start this utility and then wait for the Prescan to complete.This should take only a few seconds and then you can click the Scan button to perform a system scan.
3. After the scan has completed, press the Delete button to remove any malicious registry keys.
Run a scan with ESET Online Scanner
1.Download ESET Online Scanner utility.
ESET Online Scanner Download Link : http://download.eset.com/special/eos/esetsmartinstaller_enu.exe
2. Double click on the Eset installer program (esetsmartinstaller_enu.exe).
3.Check Yes, I accept the Terms of Use, then click the Start button.
4.Check Scan archives and push the Start button.
5. ESET will then download updates for itself, install itself, and begin scanning your computer. Please be patient as this can take some time.
6. When the scan completes, click on the Finish button.
Great post, I have used this advise many times on clients computers and have shared a link to your page on our forum.
Thank you! A good and effective description that saved my pc. ;-)
Thank you! I have used HitmanPro Kickstart, and removed the FBI moneypak virus within a few minutes!
Again, thank you!!
Thank- you! You saved my life the night before a midterm!