

A failed-payment notice can feel urgent when a business, portfolio, or family email depends on one domain staying online.
The message looks like an ordinary Hover billing reminder, yet its safest next step is nowhere inside the email.
Overview
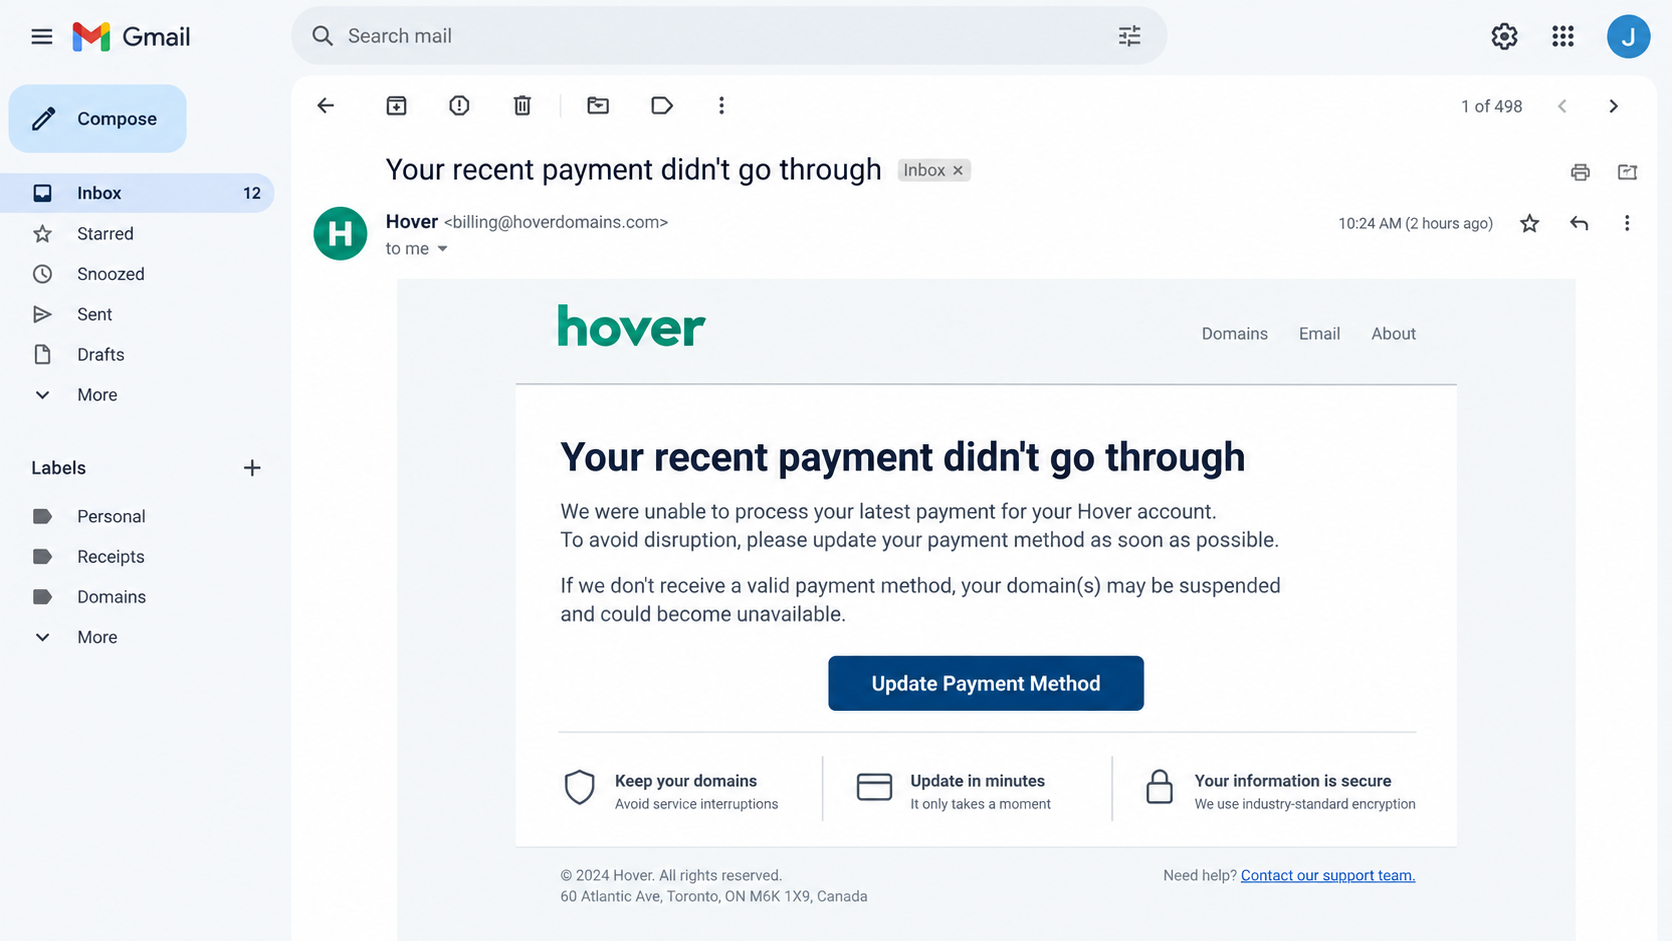
The email imitates a believable billing problem
The phishing message claims a recent Hover payment failed and warns that a domain or service could be suspended.
It includes an Update Payment Method button, familiar colors, billing language, and a short deadline.
That situation is plausible for any domain owner, which makes the message more effective than an extravagant promise.
The button leads away from account safety
Instead of asking the recipient to open Hover independently, the email directs them through a link controlled by the sender.
The destination may copy a Hover sign-in page, collect credentials, request card details, or route through several tracking addresses.
A page can reproduce branding accurately while sending every typed character to a criminal.
Hover provides a safer verification route
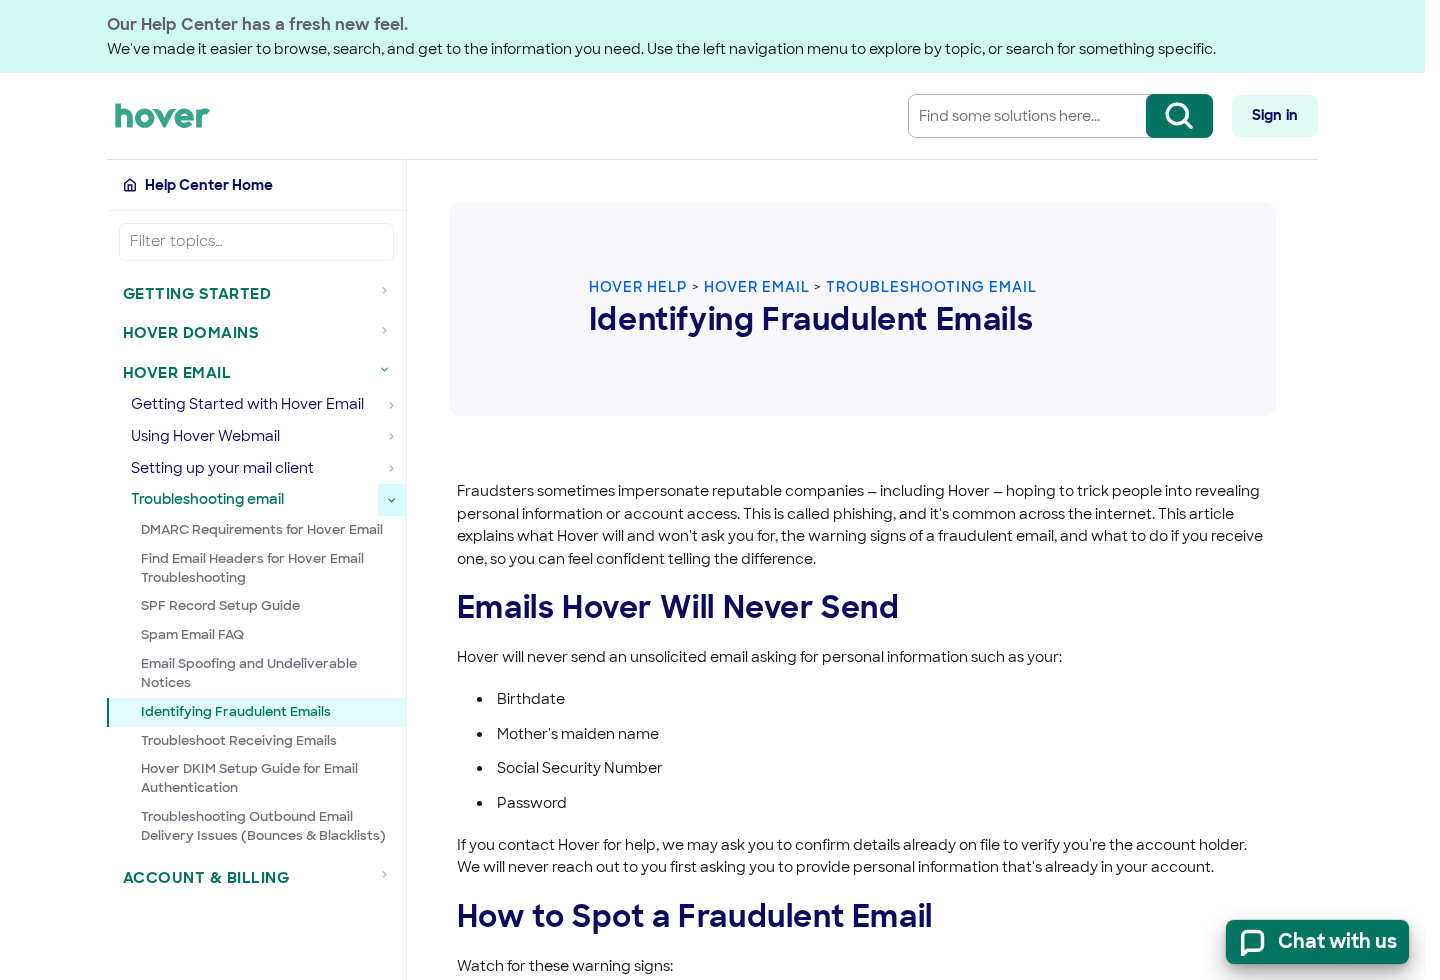
Hover’s own support guidance explains how to identify fraudulent emails and what information the company will not request unexpectedly.
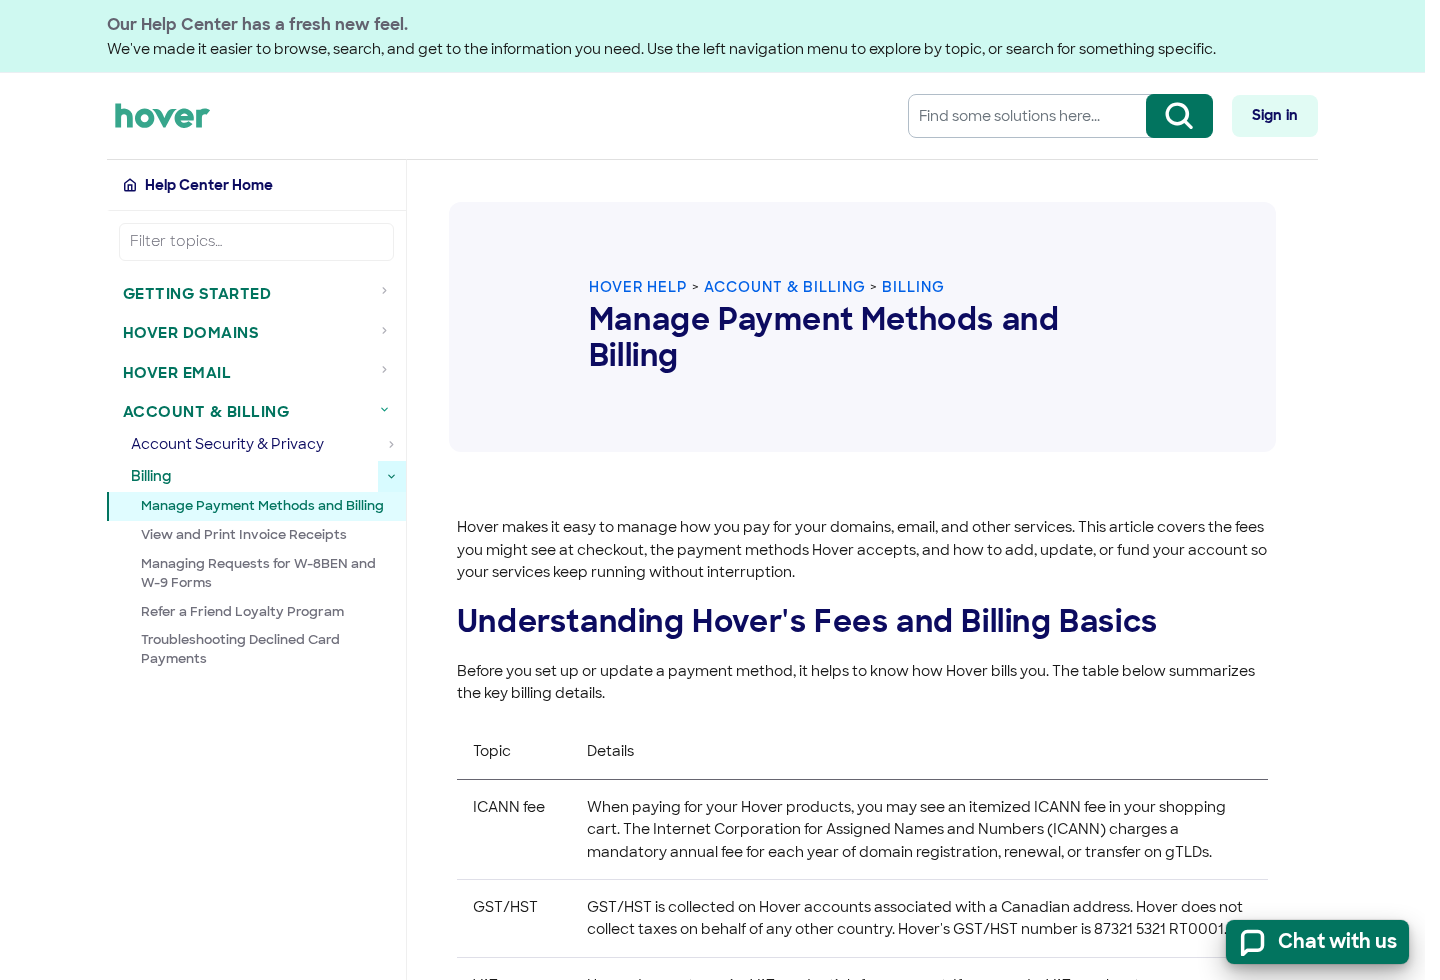
Customers can manage billing through the official account control panel rather than a button inside an alarming message.
The main points are straightforward:
- Do not sign in through the email link.
- Inspect the full sender and reply addresses.
- Open Hover by typing its address or using a saved bookmark.
- Check billing status inside the authenticated account.
- Review domain names and renewal dates individually.
- Report the message if the account shows no problem.
Why Domain Owners React Quickly
A domain is not merely another subscription. It may control a website, company email, customer portal, and public identity.
Losing service can sound catastrophic, so a warning about suspension creates immediate pressure.
Phishers understand that the recipient may click before checking whether the named domain, amount, or renewal date is even correct.
The timing can appear surprisingly accurate
Domain registration data, website records, old breaches, and marketing lists can reveal ownership clues and approximate renewal periods.
Some phishing is broad, but other messages use a real domain name to feel tailored.
Correct information does not authenticate the sender. Attackers often build deception around facts that are publicly available.
The alleged consequence affects more than money
A fake shopping receipt threatens an unwanted charge. A domain notice threatens the recipient’s online presence.
That operational risk can make even experienced users bypass routine caution.
The safest response is still to leave the message and check the account from a known route.
The design requires little originality
Brand colors, logos, footer language, and email layouts can be copied from genuine notifications.
Criminals can host the imitation on a different domain while making the visible button look completely normal.
Visual polish should never outweigh the address bar and authenticated account record.
How the Hover Payment Failed Email Scam Works
Step 1: The phisher sends a billing warning
The subject uses phrases such as Your recent payment didn’t go through or We have a problem with your Hover account.
The message may claim a card expired, renewal failed, or service suspension is approaching.
Its wording is specific enough to feel operational but vague enough to reach many recipients.
Step 2: Urgency narrows the recipient’s attention
A short deadline and fear of losing a domain encourage the reader to focus on the button rather than the sender details.
The email may say immediate action will preserve ownership, mail delivery, or website access.
Real account issues remain visible after a customer signs in independently. Fraud requires the supplied route.
Step 3: The link hides its real destination
Button text can say Hover while the underlying address points to an unrelated domain, redirector, compromised site, or tracking service.
On a phone, the destination may be harder to inspect before tapping.
A padlock at the destination means the connection is encrypted, not that Hover owns the page.
Step 4: A copied sign-in page collects credentials
The fake page asks for the account username and password, then records them before displaying an error or forwarding elsewhere.
Some versions request an email-based verification code, allowing the attacker to complete a genuine login in real time.
Entering a code into a page you reached through email can surrender the protection it was meant to provide.
Step 5: A payment form captures card data
The next screen may request card number, security code, billing address, telephone number, and account-holder name.
A small verification charge can test whether the card works. Larger unauthorized transactions may follow.
Even when no charge appears immediately, the stolen details retain criminal value.
Step 6: The attacker targets the domain account
With working credentials, an intruder may change contact details, alter DNS, redirect a website, or interfere with email delivery.
Domain control can support further phishing because messages and pages then appear under a trusted business identity.
The attacker may also search the account for other domains worth transferring or abusing.
Step 7: The victim sees a plausible ending
The phishing site may display Payment updated, a temporary error, or a redirect to the real Hover homepage.
That ending reduces suspicion and delays password changes.
By the time the recipient checks again, the criminal may have established persistence or changed recovery settings.
How to Inspect the Email Without Taking the Bait
Start with the sender’s complete address, not its display name. Expand the header and compare every character carefully.
Look for substitutions, added words, unexpected country endings, and reply-to addresses that differ from the visible sender.
Remember that a forged From field can still resemble a legitimate address. Authentication results and account verification matter too.
Check the exact domain mentioned
A mass campaign may omit the domain name or mention one the recipient does not own.
A targeted email might use a real name but invent the payment date, amount, or card ending.
Compare those details with records inside the official control panel, not with information on the linked page.
Inspect links without opening them
Hover over a button on desktop or use a safe link-preview method on mobile. Read the registrable domain, not just familiar words.
Long prefixes can place hover, billing, or account before the attacker’s actual domain.
Shortened links and redirect services conceal ownership. Do not follow them to discover where they go.
Notice what the email requests
Hover states that it will not send unsolicited messages asking for a birth date, mother’s maiden name, Social Security number, or password.
A request for any password or verification code should end the interaction.
Support may verify information during a contact initiated by the customer, which is different from an unexpected inbound demand.
Open the real account separately
Type Hover’s address yourself or use a trusted bookmark. Do not use a search advertisement when responding to an urgent billing concern.
Sign in, inspect the billing section, review payment methods, and confirm the renewal status for each domain.
If no warning appears, capture the suspicious email and contact Hover support through the official site.
What a Genuine Hover Billing Issue Should Show
A real account problem should be reflected inside the authenticated control panel, where the customer can review services and billing details.
The domain, renewal state, invoice record, and payment method should correspond to the warning.
If the email claims suspension but the account shows successful renewal, the message should be treated as hostile.
Billing changes belong inside the account
Customers should add or update payment methods only after navigating independently to Hover and signing in.
That practice remains safe even when the original message happens to be genuine.
Security habits should not depend on guessing whether a particular design looks authentic.
Renewal notices should identify the service
A useful notice connects to a domain, product, renewal date, or account event the customer can verify.
Generic panic language without checkable details is a warning sign.
Do not disclose information to help an unknown sender fill in the missing facts.
Support will not need your password
No legitimate support agent needs the customer’s password or complete multifactor code.
If an agent requests remote computer access to resolve a domain renewal, end the contact and report it.
Use official support channels to reopen the case from a clean session.
The Damage Can Extend Beyond One Card
A stolen card can usually be replaced. A compromised registrar account can affect websites, business email, and password recovery across other services.
DNS changes can redirect visitors to malware or fake login pages while the original domain still looks trustworthy.
Email-routing changes can let an attacker receive reset messages and impersonate employees.
Domain hijacking creates leverage
An attacker may change registrant details, disable protections, or attempt a transfer to another registrar.
Recovering control can require documentation and time, especially if contact information was changed first.
Registrar locks and strong multifactor authentication reduce this risk but do not excuse entering credentials on a fake page.
Business email compromise can follow
Control over a domain or mailbox allows convincing payment requests to customers, suppliers, and employees.
The next scam may arrive from a genuine company address and reference real conversations.
Organizations should treat domain-account compromise as an incident affecting identity, email, and financial workflows.
Stolen credentials may work elsewhere
Password reuse lets attackers test the same combination against email, hosting, cloud storage, and financial services.
Unique passwords limit the blast radius. A password manager makes them practical.
Changing only the Hover password is insufficient when the same secret protected other accounts.
Company, Address, and Fulfillment Checks
The real company should be reached independently
Hover is an established domain and email provider with an official help center and authenticated account area.
That real presence is precisely what the phisher abuses. Contact it through a manually entered address, not the message.
An impostor’s use of correct branding does not create any relationship with Hover.
The sender address may only imitate the brand
Inspect the full mailbox and the domain after the final at sign. Extra words or lookalike characters can be easy to miss.
Reply routing can lead somewhere different from the displayed sender.
Forward the message with headers when reporting so technical teams can examine its origin.
The phone number may be another trap
Some emails include a billing-support number designed to move the attack into a live conversation.
Search advertisements can also promote impostor support lines. Use the official help center instead.
Never install remote-control software at the direction of an unexpected billing agent.
Account records are the fulfillment evidence
A successful renewal should appear in the real account with the correct domain, date, invoice, and payment status.
A screenshot supplied by the email sender cannot replace that record.
If charges exist without matching services, dispute them and ask Hover to investigate the account activity.
How to Harden a Domain Account
Use a long, unique password stored in a reputable password manager. Never reuse the mailbox password that receives account recovery messages.
Enable the strongest available multifactor protection and guard every verification code as carefully as the password.
Turn on sign-in notifications and review account activity. Investigate logins from unfamiliar browsers, locations, or times.
Keep registrant and recovery information current so legitimate security notices reach the right person.
Use registrar lock features and document who may authorize DNS, contact, billing, or transfer changes.
For organizations, avoid relying on one employee’s personal mailbox as the only recovery route.
Record important domain names, renewal dates, payment owners, and support procedures in an internal inventory.
Limit administrative privileges. Marketing staff may need website access without needing registrar control.
Back up DNS records and website content. Recovery is faster when the last known configuration is available.
Practice the response before an incident. Know who contacts the registrar, bank, host, and email provider.
What to Preserve Before Deleting the Message
Save the original email as a message file when possible. A screenshot alone omits routing and authentication information.
Record the visible sender, reply address, delivery time, subject, linked domain, and any attachment names.
If the page was opened, copy its address without revisiting it and note what information was entered.
Keep genuine Hover alerts received afterward because they can establish sign-in attempts or account changes.
This evidence helps support teams, payment providers, and investigators connect the message with related attacks.
Preserve everything.
What to Do if You Fell Victim to This Scam
- Open Hover independently. Use a clean browser session and check whether your password, contacts, DNS, or domains changed.
- Reset exposed credentials. Change the Hover password and every account that reused it, starting with the recovery mailbox.
- End active sessions. Use account security controls to revoke unfamiliar logins and review sign-in notifications.
- Contact official support. Report the phishing page, request an account review, and flag unauthorized domain activity immediately.
- Call the card issuer. Replace any card entered on the fake page and dispute unauthorized transactions.
- Restore domain protections. Recheck registrar locks, nameservers, DNS records, forwarding, and transfer settings.
- Preserve evidence. Save the message with headers, phishing URL, screenshots, transaction records, and account alerts.
- Scan the device. Run Malwarebytes if a file opened, software installed, or browser extension appeared during the incident.
- Block repeat exposure. AdGuard can filter many malicious pages and advertisements, though it cannot undo disclosed credentials.
- Warn affected contacts. Notify employees or customers if compromised email or web services could send convincing follow-up messages.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is every Hover payment-failed email fake?
No. Genuine payment problems can occur. The safe rule is to ignore the embedded link and verify inside the independently opened account.
That method handles both real and fraudulent notices.
What if the email names my real domain?
A domain name is often public information. Its appearance makes the message more targeted but does not authenticate the sender.
Check the billing record directly.
Can I trust the Hover logo and correct address?
No. Logos and footer details can be copied, while sender fields may be forged or visually disguised.
Account evidence and independent navigation are stronger.
What if I clicked but entered nothing?
Close the page and clear any downloads. Risk is lower if nothing was submitted, but review the browser and run a security scan.
Report the URL to Hover.
What if I entered only my password?
Change it immediately from the real site, revoke sessions, protect the recovery email, and replace the password anywhere it was reused.
Monitor domain settings closely.
Could the phishing page bypass two-step verification?
Real-time phishing can request a current code and relay it to the genuine service.
Never enter verification codes on a page opened from an unexpected message.
The Bottom Line
The Hover payment-failed email succeeds by threatening an asset people cannot afford to lose. Its polished design is not evidence of origin.
Leave the message, open Hover through a trusted route, and act quickly if credentials, card details, or domain controls were exposed.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.