

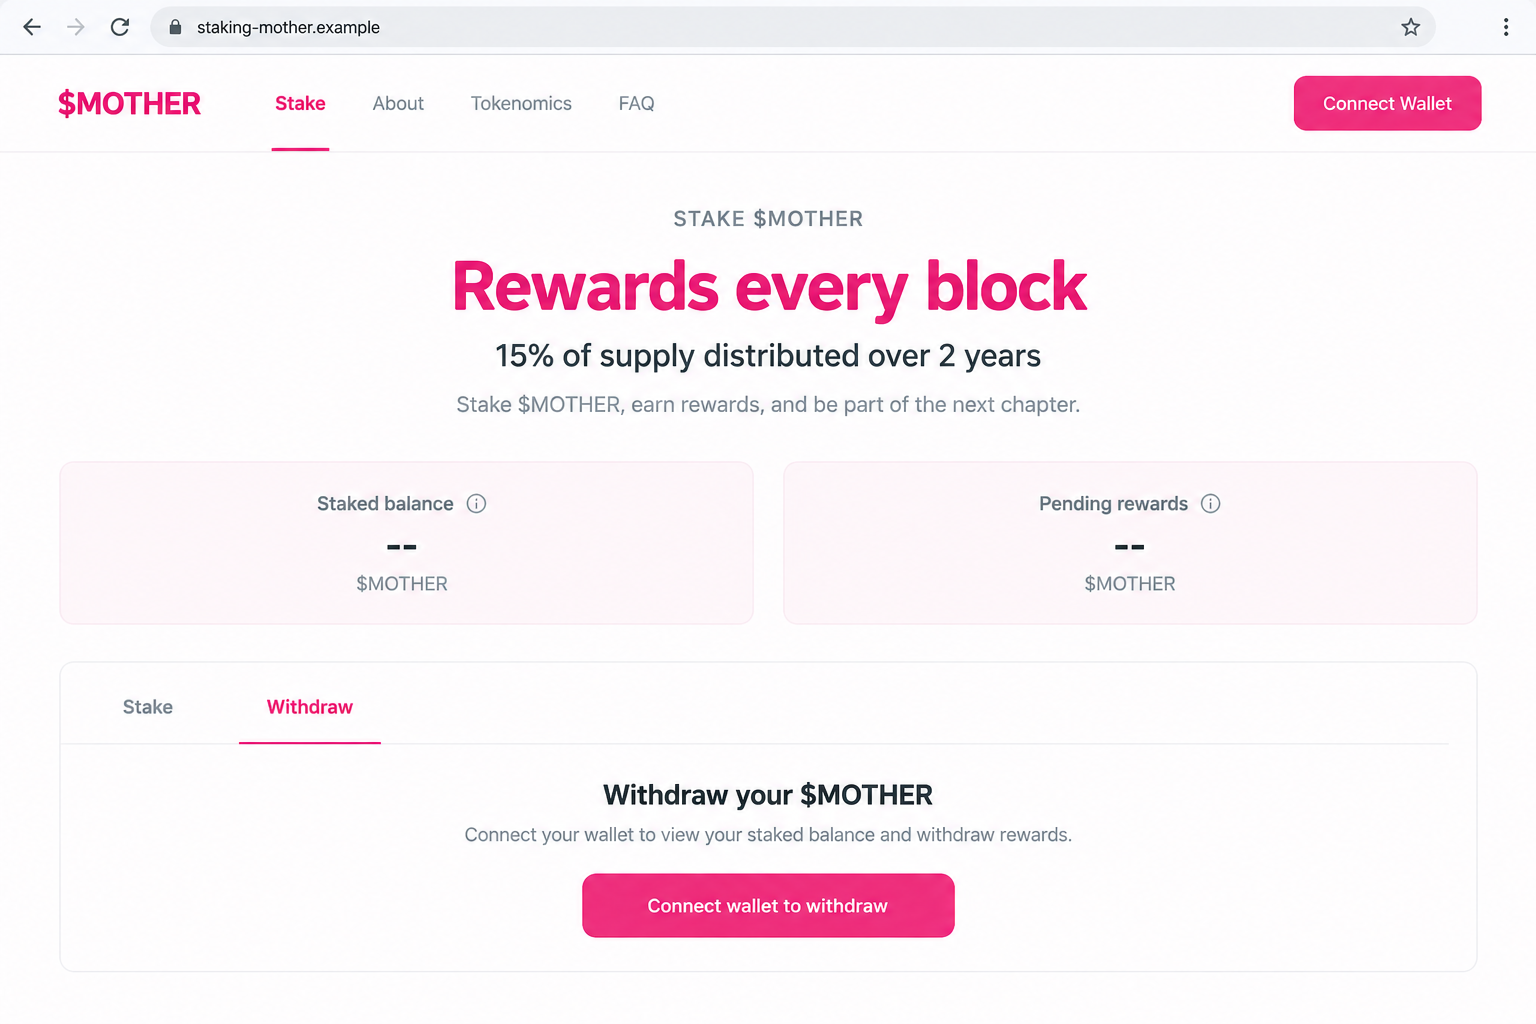
A MOTHER staking page promises rewards every block and presents a withdrawal option. For a token holder, checking that balance can feel like collecting something already earned.
That feeling deserves a pause before the wallet opens. Look at how the reward claim was established and what the proposed withdrawal actually asks your account to do.
Overview
A counterfeit staking page uses the MOTHER identity
The MOTHER staking scam concerns an imitation rewards site, not a conclusion that every MOTHER token or discussion of that token is fraudulent.
A page documented in July 2024 appeared at staking-mother[.]fun. It offered staking rewards and used a withdrawal workflow to encourage wallet interaction.
The recorded investigation identified the imitation as a crypto drainer. Its exact transaction instructions and every victim’s resulting loss have not been independently verified for this article.
The evidence supports warning about that counterfeit solicitation. It does not support accusations about the genuine token’s market value, quality, or present development.
The supply allocation claim is not a guaranteed return
The historical copy described rewards arriving each block and 15% of supply distributed over two years. Those are the page’s promises, not verified current token economics.
A supply allocation is different from a holder’s personal yield. A displayed pool percentage does not tell you what your account will receive or whether any pool exists.
- A staking-themed address does not authenticate a token project’s involvement.
- A rewards schedule does not establish a valid staking position.
- A withdrawal button must be checked against the wallet’s actual requested action.
- Completed transfers, token permissions, and exposed recovery secrets need different responses.
The reward story becomes dangerous when it persuades someone to approve an unwanted transaction or permission. Reading a page alone is not universal authorization to spend.
This is a historical case with clearly stated limits
The recorded imitation is older than this review. We are not claiming a newly discovered October 2026 campaign or that its original hostname still serves the same page.
The original promotional address mother.fun could not be independently verified through our web check today. It is not offered here as a current recommended transaction route.
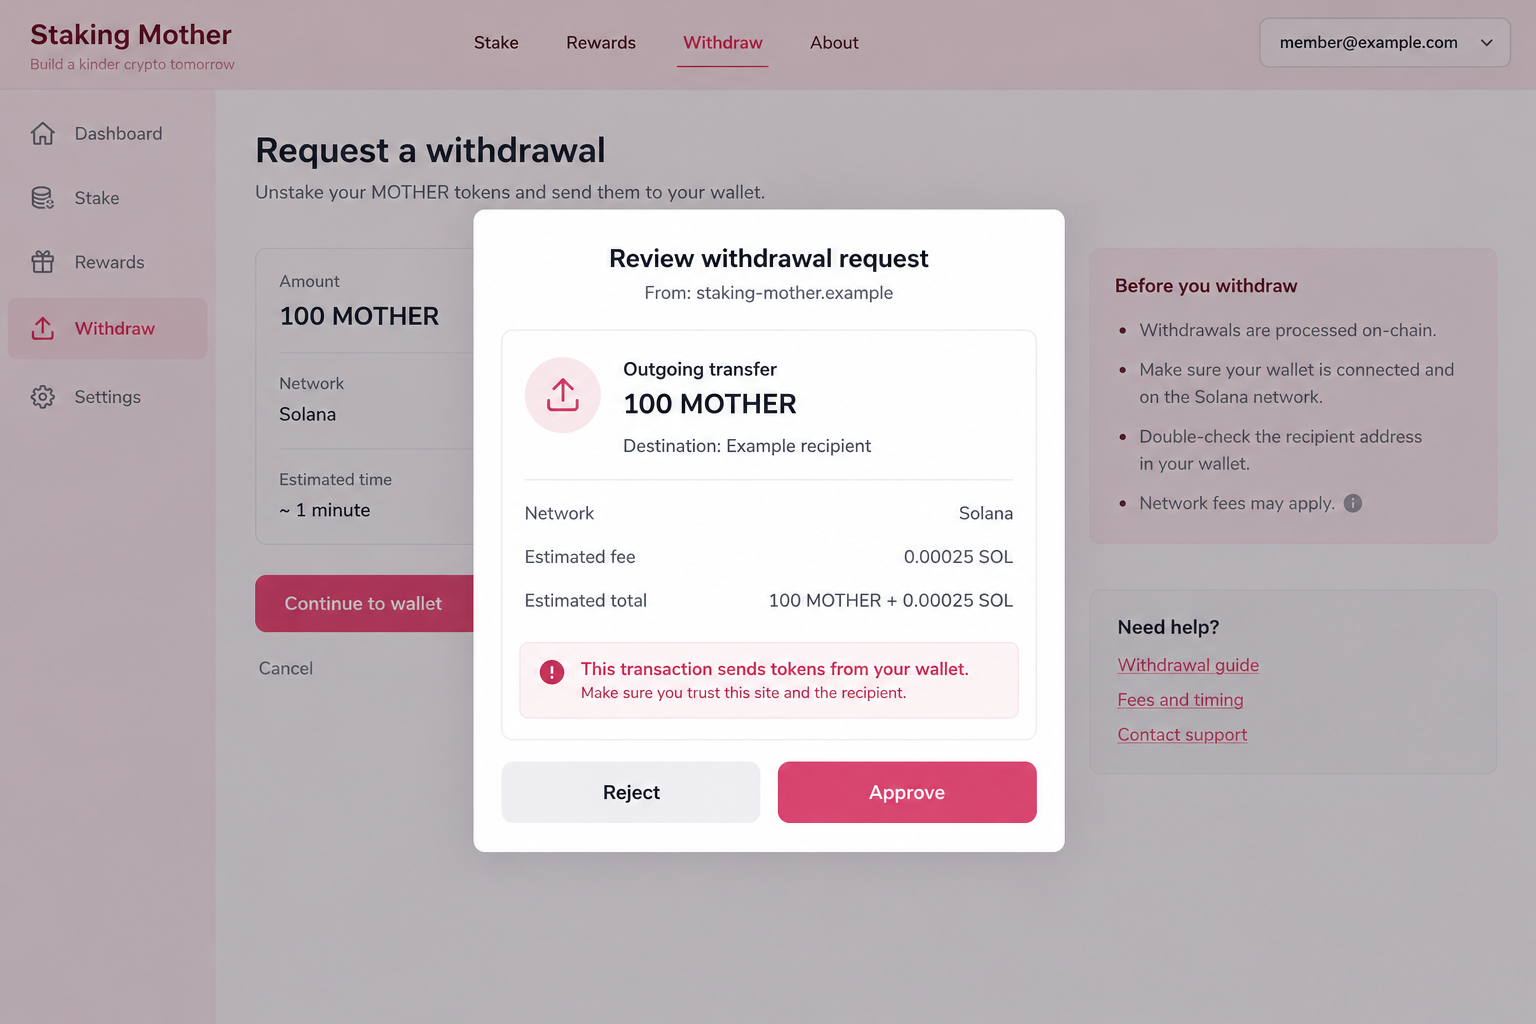
Our images show fictional, nonfunctional interfaces. The pictured Solana transfer is a hypothetical example of a misleading withdrawal label, not a captured request from the historical copy.
If you encountered a similar page, investigate your own account record. A claimed reward balance should not substitute for evidence of a real deposit or position.
Why the Withdrawal Story Can Be More Persuasive Than Staking
Collecting money feels different from risking money
People are often cautious about an unexpected investment. They can be less cautious when a website tells them the investment already produced something ready to collect.
The decision then seems to be whether to retrieve a balance. The reader may not notice that no trustworthy evidence established that balance in the first place.
Imagine a holder seeing a forwarded staking page and checking its withdrawal tab. That example illustrates the temptation; it is not an account of a specific victim.
Before trying to collect, ask when and where you actually deposited tokens. A page claiming entitlement cannot invent a genuine staking history for your account.
Block-by-block rewards create a sense of a running system
References to blocks make the offer sound technically connected to a blockchain. They suggest that rewards accrue automatically whether or not the visitor watches.
That vocabulary is not proof of a deployed program. A website can describe a schedule without showing an authentic contract, funded distribution, or verifiable relationship to the project.
Even a changing counter can be a display effect. To establish what you own, consult your account and the independently verified terms of an actual arrangement.
Do not confuse the pace of a promotional counter with urgency. A real balance should be evaluated through records, not rescued by signing a request you cannot explain.
A two-year distribution plan can sound like due diligence
A specific timeline gives the page more substance than a vague claim about free tokens. It can look like the outline of a long-term incentive program.
Nevertheless, the figure does not explain eligibility, custody, withdrawal conditions, dilution, price, or which party controls the relevant funds.
Neither does 15% of supply mean a 15% personal annual return. The denominator is different, and the claim still needs a genuine issuer and verifiable implementation.
This distinction is useful even for real crypto programs. Numbers deserve interpretation before they become a reason to approve financial authority.
How the MOTHER Staking Scam Works
Step 1: A recognizable token leads into an unfamiliar staking page
The counterfeit uses the token’s name to make its offer relevant. The visitor may know the asset while knowing nothing about the operator of this particular site.
That gap is important. Owning a genuine token does not authenticate every application that offers to stake it or reward its holders.
A forwarded link can bridge the gap emotionally without providing evidence. It may arrive from someone enthusiastic about the token who has never examined the proposed transaction.
Look for a verifiable program announcement before assuming that the page belongs to the community. Do not use its own branding as its sole identity check.
The recorded case does not prove one universal route by which visitors arrived. Treat your own message, advertisement, or referral as part of the evidence to preserve.
Step 2: Reward language gives the page an apparent operating history
The historical page describes continuing block rewards and a planned distribution period. A reader can infer an established system even without seeing an authentic staking record.
Staking and withdrawal tabs reinforce that impression. They make the site look capable of managing a position before the visitor has established that any position exists.
Interface completeness is not proof of financial activity. A page can present tabs and balance fields without controlling a legitimate reward pool.
Compare the claim with transactions you actually initiated. If you never entered an authenticated staking program, a new page cannot establish one simply by recognizing your address.
Leave any unsupported balance claim unresolved rather than paying to investigate it. The operator should establish entitlement before asking you to make a consequential request.
Step 3: Withdrawal becomes the reason to connect a wallet
The documented copy encourages wallet connection to withdraw staked tokens. That wording can make the connection feel protective: you are retrieving funds instead of surrendering them.
A legitimate application may also require connection for a withdrawal. The safety question is the application’s identity and the precise actions requested afterward.
Simply revealing a public address is not the same as approving a transfer. However, a fraudulent page can use the connection to place further requests in the wallet.
Keep reviewing after the first dialog. Do not assume that approving a connection means every subsequent screen belongs to the same harmless operation.
A recovery phrase entry is not an ordinary connection. Stop immediately if a website claims it needs that secret to recognize or release a staking balance.
Step 4: A withdrawal label can conceal an outgoing action
The illustration shows a page calling the task a withdrawal while the wallet describes tokens leaving the account. Its amount and destination are fictional teaching details.
That inconsistency must be understood before signing. Receiving an advertised reward and sending existing holdings to another address are different financial actions.
Some genuine withdrawal arrangements involve multiple instructions. Complexity does not justify accepting a mismatch without verifying the program and understanding why the action is necessary.
A malicious request might instead delegate token authority or ask for another consequential signature. We cannot claim the historical page always used the illustrated transfer.
Read the transaction preview as the financial decision. The website’s reassuring button label is not a replacement for the wallet’s explanation.
Step 5: A harmful authorization changes the recovery problem
An unwanted transfer moves assets. A spending permission can create exposure to later transfers. A leaked controlling secret compromises the wallet more broadly.
Those outcomes are not interchangeable, so “I clicked Withdraw” is not enough information to diagnose them. The account history and authorization details matter.
The website may show a pending status or failure after a harmful action. Its response does not establish whether an on-chain transaction completed.
Check independently before trying again. Repeating a request to make the displayed withdrawal finish may authorize an additional action rather than correct the first.
Do not send money to unlock the balance. An unverified reward claim cannot justify another payment merely because the page says your funds are waiting.
Check the Wallet on the Correct Network
Use the actual asset identifier, not only MOTHER in a label
Token names and symbols can be reused. An interface displaying MOTHER does not establish which asset a proposed transaction concerns.
Compare the token identifier and network with trustworthy records. Do not obtain every verification detail from the same page requesting a withdrawal.
A token balance visible in your wallet is stronger evidence than a website’s pending-rewards field. It still does not authenticate an external staking application.
Unexpected assets can carry enticing links in their metadata. Merely receiving a token is different from following those links or approving transactions connected with it.
Solana spending authority is not an Ethereum allowance screen
If your interaction occurred on Solana, follow guidance for that network and wallet. Do not assume an Ethereum-focused approval checker examines every permission involved.
Solflare explains token delegations, including requests that allow future spending. Such authority can be legitimate, but an untrusted application can misuse it.
A wallet warning about later spending deserves attention even when the website calls the action a withdrawal. Understand which account and token the authority affects.
The right review depends on the transaction. Ask official wallet support how to inspect your situation rather than applying a random cleanup tutorial from a direct message.
Records matter more than a success animation
Use an explorer reached through a verified wallet route to inspect transactions. Preserve the network, signature or hash, addresses, timestamps, and assets involved.
Do not publish sensitive information merely to obtain informal help. A transaction identifier can support analysis without revealing a private key or recovery phrase.
Blockchain records can provide a public trail. They do not give the wallet provider a standard way to reverse a completed transfer.
Contact legitimate authorities about significant losses. Avoid anyone who turns the existence of a trace into a promise that another payment guarantees recovery.
What to Do if You Have Fallen Victim to This Scam
- Stop repeating the withdrawal request.
Do not reconnect to make a stalled counter update. Record the page you used and whether you approved any request beyond the initial connection.
If you only looked at the interface, do not assume tokens were stolen. Begin with the actions that actually occurred.
- Preserve the wallet’s record of the interaction.
Save relevant transaction identifiers and the affected token details. Note what you expected to receive and what the wallet record shows instead.
Keep the original invitation too. That can identify the route into the copy even if the staking site later disappears.
- Review connections and spending permissions separately.
Disconnect the suspicious application and inspect any continuing authority on the correct network. Use official wallet guidance to revoke unwanted permissions where applicable.
Solflare’s compromise guidance describes its spending-approval controls. Follow the instructions for your own wallet rather than expecting every interface to match.
- Abandon an exposed recovery secret.
If the site or a helper received your phrase or private key, establish a new wallet with fresh credentials on a secure device.
Do not create another account from the compromised phrase and call it new. The attacker can retain control derived from the same secret.
Phantom’s scam-response guidance distinguishes this exposure from a malicious-app interaction. It also warns that support will not ask for your recovery phrase.
- Protect remaining legitimate holdings carefully.
Investigate before adding fresh funds to an account that shows unexplained withdrawals. Automatic theft can make repeated transaction-fee top-ups another loss.
Use reputable assistance if a safe transfer requires technical work. A public reply offering instant rescue is not a verified professional relationship.
- Address any device or browser compromise.
If a staking tool was installed or unexplained redirects continue, inspect extensions, downloads, and notification settings. Updated Malwarebytes can help identify unwanted software.
AdGuard may reduce some scam-ad and malicious-site exposure. It cannot retrieve an on-chain transfer or make a previously disclosed phrase private again.
- Report and avoid follow-up collection traps.
Report the link to the platform where you found it and submit the financial evidence to appropriate authorities. Warn anyone you sent the invitation to.
Reject “release,” “validation,” or “recovery” payments requested by strangers. The next claim about money waiting for you may repeat the same collection pretext.
Frequently Asked Questions
Does this article say the MOTHER token itself is fake?
No. It concerns a counterfeit staking-and-withdrawal website. Token valuation and the genuine project’s current activity are separate questions not resolved by this investigation.
Is the 15% supply figure my annual return?
No. The historical copy described a supply distribution, not a verified personal APR. Eligibility, share, value, and even the claimed pool require independent evidence.
Was this staking page newly discovered in October 2026?
No. The documented example dates to July 2024. This review explains its mechanism and current wallet-safety guidance without claiming a new outbreak.
Does a withdrawal button mean I am receiving tokens?
Not necessarily. Read the wallet request and verify the program. An outgoing transfer or broad spending permission needs an explanation beyond the button’s label.
Should I use an Ethereum approval tool for a Solana interaction?
Use tools and guidance appropriate to the actual chain. A checker designed for one network does not automatically inspect another network’s token authority.
Can changing my wallet password fix a leaked recovery phrase?
No. An attacker with that controlling secret can use it separately. Create a fresh wallet on a trusted device and carefully secure remaining legitimate assets.
The Bottom Line
The MOTHER staking scam uses promised rewards and a withdrawal option to make a counterfeit wallet journey feel like collecting earned funds. The account record matters more than that story.
Do not authorize a request merely to uncover a supposed balance. If you already acted, assess the correct network, permissions, and secrets before attempting further withdrawals.








