


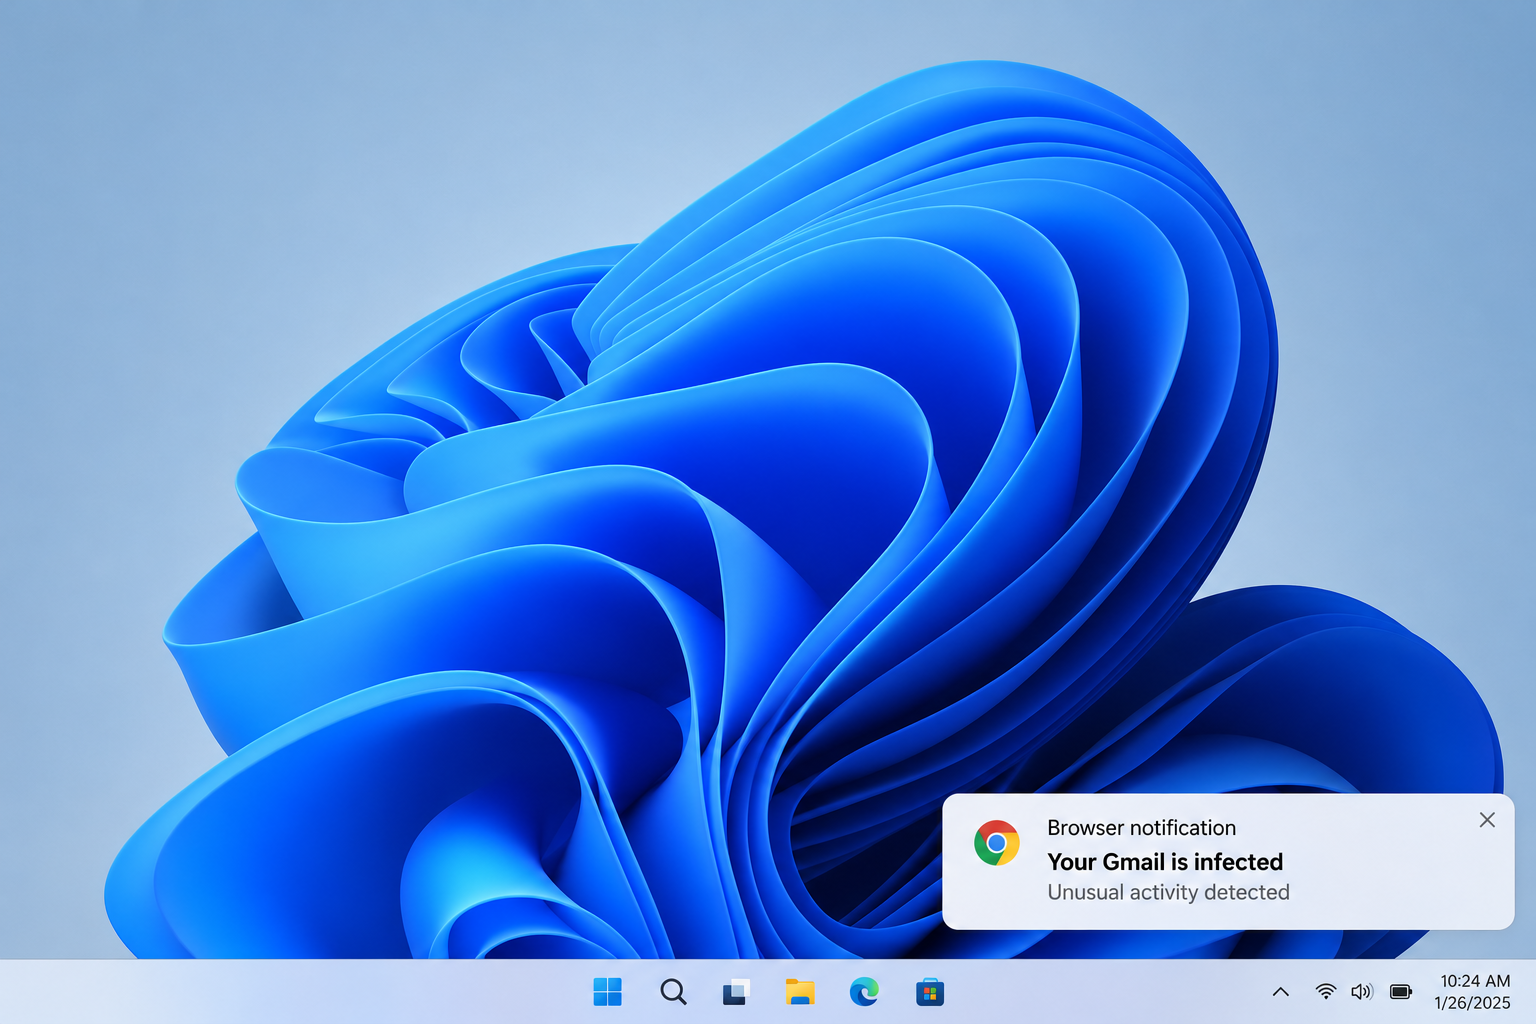
A warning says Gmail is infected, but it didn’t come from an email. It appeared in the corner of your desktop, where real system alerts usually show up.
If you saw Nexorbytecove.com on the card, take a closer look at the sender. The fix depends on where the warning came from.
Overview
The fake scan and the desktop alert are different things
The Nexorbytecove.com pop-up scam starts with a web page that imitates an antivirus scan. The documented page claimed it found five viruses and said a McAfee subscription had expired.
A browser notification permission prompt appeared during that display. The page and the prompt have different jobs: the scan is site content; the prompt is a real browser control.
If you allow notifications, the site can send alerts through the browser. They can arrive while you’re doing something unrelated, which makes the connection easy to miss.
Why a notification can mention Gmail
In one documented message, the sender claimed Gmail was infected and offered to scan or delete a virus. Another notice referred to Windows protection and displayed Chrome branding.
Gmail is an online account. A third-party website notification cannot tell you whether someone signed into that account, whether a message contains malware, or whether Windows detected a threat.
The following details help you separate the warning from a real security event:
- The notification card may identify Chrome or another browser as the application delivering it.
- A website name can appear as the sender even when the headline claims to represent Gmail or Windows.
- The warning tells you to click its own repair or scan button rather than check a known app.
- Your real antivirus history and account security activity can be checked without using the warning.
Removing the permission may be enough
Receiving a notification is not the same as installing software. If the alerts began after you accepted a site prompt, blocking that sender is the right first move.
The response changes if you followed one of the alerts and ran an installer, entered a password, or gave remote access. Those actions are separate from the notification setting.
The documented messages show what the site claimed. They do not show that your PC is infected, that Gmail is compromised, or that every alert opens the same destination.
How the Nexorbytecove.com Pop-Up Scam Works
Step 1: A web page borrows the look of an antivirus scan
A page can draw a progress bar, imitate a familiar program and show a list of supposed problems. Those graphics don’t make it an installed security application.
The reported display used a five-virus claim and a subscription warning. They seem to answer two questions at once: what is wrong and why your protection did not stop it.
Don’t wait for the animation to finish. Closing the tab won’t interrupt a real antivirus task. Check the program you use from its own shortcut.
You may not remember opening the site intentionally. A redirect can land you on a page you didn’t request. Note what you were doing without trying to reproduce the redirect.
Step 2: The browser asks for permission while your attention is elsewhere
The browser may offer Allow or Block for website notifications. The page can put that prompt beside an alarming message, but it cannot redefine what the permission does.
Allow gives the site a way to send alerts. It does not authorize a virus scan or repair a subscription. Block declines the request without changing your antivirus settings.
If you dismiss the prompt, don’t assume the page itself is safe. Close the tab, especially if it keeps putting fake controls in front of you.
If an ad opens another tab, use the browser’s tab close button. Don’t use a button inside the page that claims it will close the warning for you.
Step 3: Later alerts appear where normal notifications appear
Website notifications are delivered through the browser and may show in the operating system’s notification area. Familiar placement makes the message feel like it came from the device.
The claimed sender can change from one card to the next. A Gmail headline and a Windows warning don’t mean two independent products detected the same problem.
Look at the smaller sender information if it is visible without opening the card. The visible website can be more useful than the largest text or icon.
If the card is already gone, go to your browser’s allowed sites. You don’t need to wait for another one or visit the suspicious address.
Step 4: The next click creates a new risk
A fake alert can lead to a checkout, a password form, a phone number, or a download. The headline doesn’t tell you what happens next.
Judge the next action by what happened. Paying someone, submitting a Gmail password and downloading a file are not interchangeable. Each one needs a different response.
Someone who saw an alert and dismissed it shouldn’t assume they need to reset every password. Someone who approved a remote session shouldn’t stop at turning off notifications.
How to Stop Nexorbytecove Notifications
Step 1: Identify the browser that delivered the alert
Open notification history or the notification center if your device offers it. Look for the application listed on the card without pressing the card’s advertised action.
Check which browser profiles you use. A profile for work may have different site permissions from one for personal browsing, even on the same computer.
If you use more than one browser, start with the application shown in the alert. The site won’t appear in a permission list belonging to the wrong browser.
Step 2: Block the site in its own permission settings
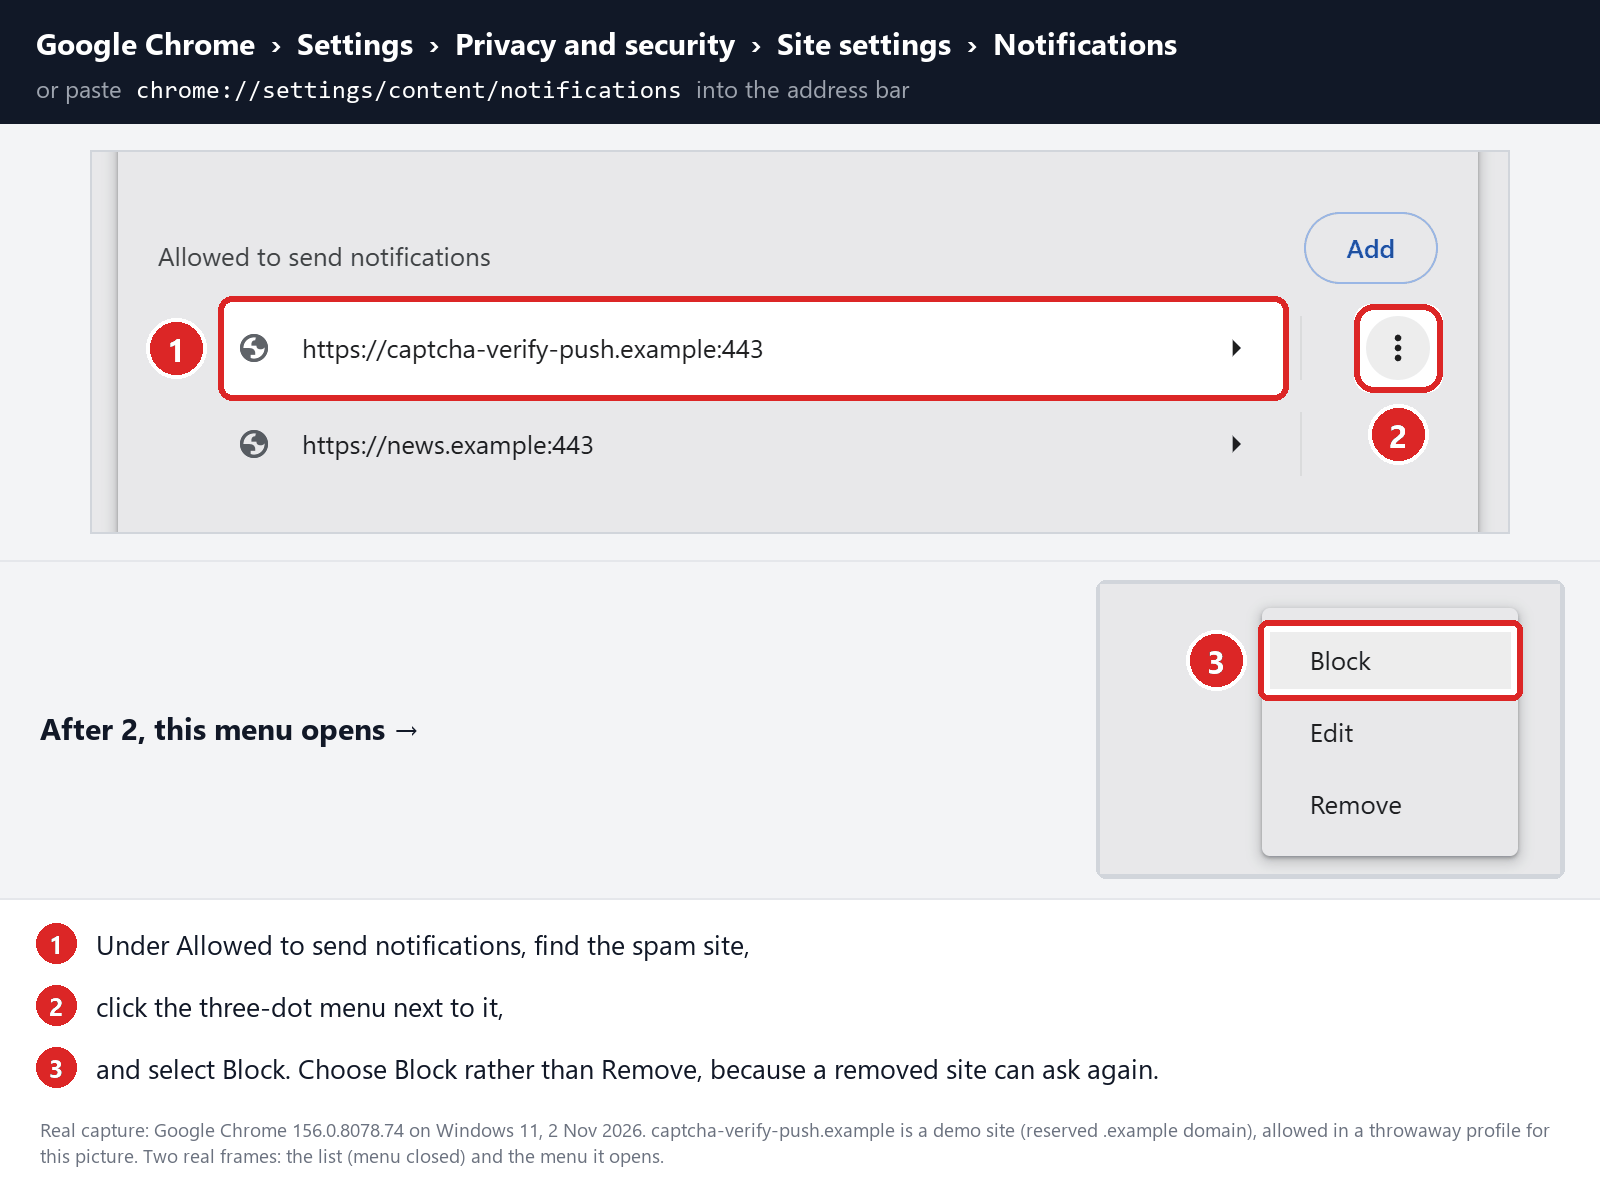
In desktop Chrome, open Settings, select Privacy and security, then Site settings and Notifications. In the allowed section, find the suspicious sender and choose Block from its menu.
Chrome’s notifications help shows the permission controls. Use that list rather than revisiting the site or turning off all desktop notifications.
Check the domain carefully. You are blocking the sender shown on the card, not Gmail, Chrome itself, or every site that uses the same parent domain.
In Microsoft Edge, use Microsoft’s website notification instructions. Open the settings from Edge itself and find the allowed entry under website permissions.
If Chrome on Android delivered the warning, open its settings and check Site settings and Notifications. On a managed device, ask IT if the setting is locked.
Step 3: Check whether the alerts stop
Dismiss old cards from the notification center. Blocking the sender stops new permission-based alerts from that site; old items may still be visible until you clear them.
If a new card appears, compare the sender and browser with the first one. Check another profile or another allowed domain before assuming a setting change failed.
If you keep getting new tabs or redirects without notifications, inspect extensions and recently installed apps with help if needed. Blocking one site doesn’t remove an installed program.
What to Do if You Have Fallen Victim to This Scam
Close the page without clicking the advertised action.
If you only received a browser card, record the sender and block that site. Leave genuine account and system settings alone unless there is another reason to change them.
Check the real account from a route you already use.
If the card named Gmail, open Gmail or your Google account directly. Look for genuine security activity instead of asking the alert to scan the account.
If you typed a password or approved a sign-in on the fake route, replace the password from a trusted device and review access and recovery settings.
Treat a payment as a payment problem.
Use your bank or card issuer’s usual app or number. Explain whether you entered card details, authorized a charge, or paid somebody claiming to offer support.
Check for later charges. A checkout selling real security software does not make the false warning legitimate.
Take action if someone got remote access.
Disconnect the affected device if a stranger is still controlling it. Use another device to reach your bank or IT team and explain what the caller could see.
Save the session time and application name. Don’t reopen the session to ask the caller to undo anything.
Check the device if you installed or ran something.
For an affected personal PC, Malwarebytes can help check a suspicious installer. If this is a work device, notify your support team before making cleanup changes.
AdGuard can reduce some unwanted ad redirects, but it won’t revoke site permissions or undo a sign-in. Fix those directly in the browser or account.
If it keeps happening, keep a short record.
Note whether new notices appear after the permission is blocked, which app sends them, and whether new tabs open independently. That helps support narrow down the cause.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
What the Real Security Screens Can Tell You
A Windows Security history item is not the same as a Chrome notification. It belongs to an app you can open on its own and check without visiting the site.
Open your usual security app and inspect recent findings. Note the time and item for any real detection. You don’t need the browser alert to act.
If a warning names a particular file, compare it with the app’s record. A file name on a website isn’t enough reason to delete anything manually.
For a Gmail account, the useful screen is your Google account’s security activity. Check any unrecognized sign-ins there. A site naming Gmail is not a substitute for that review.
Do not give a caller control of the PC to prove the warning is fake. If you need help, ask a person or support service you already know.
If the browser is set to run in the background, a notification can arrive without a visible tab. That does not prove the browser secretly installed a separate program.
If the original page seemed to be a normal site, you can report the redirect to that site’s owner without including personal details. Save the time and what you clicked.
The MalwareTips guide to tracing unwanted activity explains why a notification, a browser redirect, and an installed application call for different checks.
What to check if your browser list doesn’t match the card
Some cards list the browser at the top and the site below. A red shield in the middle is part of the content, not a reliable sender label.
Open the browser profile you actually used when the fake scan appeared. If that profile is closed, use its profile picker rather than assuming all profiles share notification settings.
When a host isn’t present, look at the blocked list too. You may already have blocked it. Old cards can remain visible until cleared, even after new ones stop.
Check whether the new message is a desktop card or a new browser tab. A redirect to a new tab doesn’t require the same setting as a desktop notification.
If redirects happen repeatedly, note whether they only occur on one site. An ad on that site and an extension affecting every tab are different leads for cleanup.
Handle a genuine purchase separately from the false alert
If you paid for software after following the alert, get the receipt and check which company actually billed you. The name in the warning may not match the merchant.
Use the seller’s verified account or contact details to ask about the order. If you don’t recognize the charge or exposed your card elsewhere, call the issuer.
Make a record of any subscription or renewal you see in the genuine account. Deleting the website permission does not cancel billing or remove payment information a checkout received.
Keep copies of the receipt and cancellation confirmation. If another charge appears, those records help the issuer distinguish an unwanted renewal from a card transaction you never authorized.
Frequently Asked Questions
Is Nexorbytecove.com a real Gmail security warning?
No. The documented alerts came from a website through browser notifications. If you want to check Gmail, open your actual account independently.
Did a website really find five viruses?
The documented scan was a website simulation. Check your installed security tool’s own history for actual detections instead.
Why does the notification show a Chrome icon?
Chrome can deliver alerts from websites. The icon can identify the delivery application without endorsing the claim inside the card.
Do I have to block all notifications?
Usually not. Start by blocking the sender in the browser’s site permission list. That lets you keep legitimate notifications you still want.
What if I clicked Allow but never followed an alert?
Remove the permission. That action alone doesn’t prove a password was stolen or a program was installed.
Why do the alerts keep appearing after I closed the tab?
Closing a tab doesn’t revoke a previously granted permission. Block the site and check the same browser profile that delivered the alerts.
The Bottom Line
Don’t use a Nexorbytecove notification to scan Gmail, renew antivirus protection, or call for repairs. Block the sender in the browser where the alerts appear.
If you entered a password, paid, or ran software after clicking an alert, handle that exposure separately. Stopping the messages doesn’t undo what happened on the next page.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.