

In 2026, the Robux giveaway scam is not “new.” It’s just better dressed.
It shows up as a clean-looking “Milestone Event 2026” page that feels official. It shows up as a Roblox chat message that repeats so often you start to wonder if everyone is actually doing it. It shows up as a Discord “event server” with staff roles, ticket bots, and a confident tone that makes the whole thing feel real.
And it always leads to the same promise: free Robux, fast.
Here’s the truth that cuts through all the noise. Any site promising free Robux is a scam. Roblox itself is clear that offers of free Robux, memberships, or valuable items are scams designed to trick users into giving up passwords, personal info, or clicking harmful links.
This article breaks down the Robux giveaway scam 2026 tactics in a way that’s easy to recognize, easy to explain to kids, and practical to act on if you already clicked.
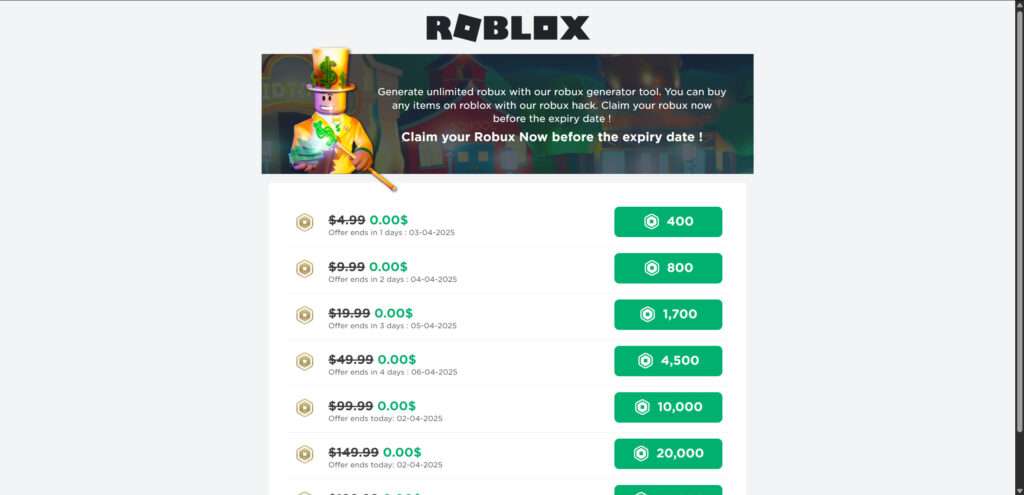
Scam Overview
The “Robux giveaway scam” has been around for years, but the 2026 playbook is more polished, more social, and more aggressive. Instead of one obvious “generator” page, scams now operate like campaigns with multiple moving parts: chat spam, short-form video hype, affiliate funnels, and Discord-based manipulation.
The story changes constantly, but the structure stays the same.
The core rule that never changes
If you remember one sentence, make it this:
Robux does not come from random websites.
Roblox has repeatedly warned users that “free Robux” generators and similar offers are scams. Their goal is to steal accounts, Robux, and items, or push users into unsafe links and data collection.
So when a site claims “Free Robux for everyone” or “Roblox giveaway event,” it’s not a misunderstood promotion.
It’s bait.
What scammers are selling in 2026
Scammers have learned that different people fall for different hooks, so they vary the packaging. In 2026 you’ll commonly see:
- “Roblox Milestone Event 2026” giveaway pages
- “Claim 5,000 Robux” countdown pages
- “No password needed, username only” pages
- “Human verification required” pages
- “Join Discord to claim your reward” pages
- “Creator event,” “partner event,” or “official event server” claims
The theme is always designed to make the scam feel normal.
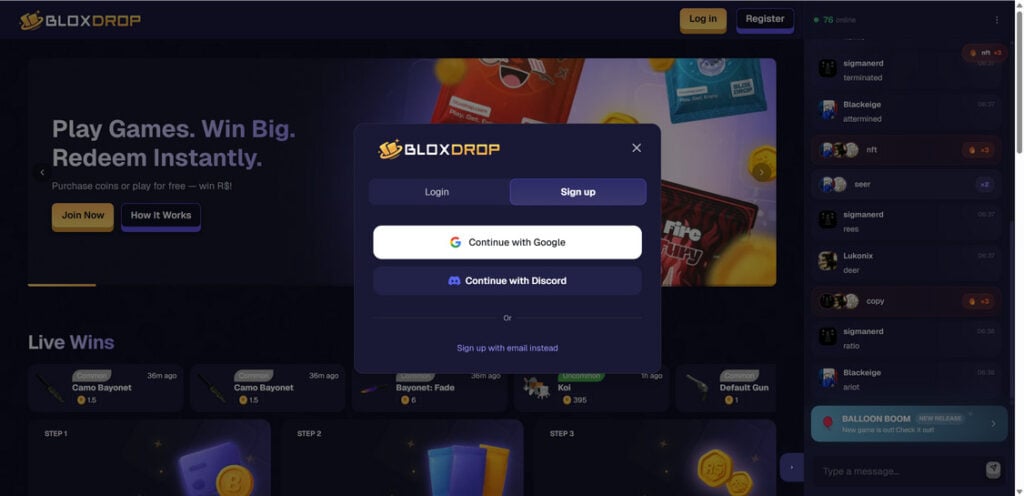
A celebration. A limited-time event. A community reward. A special partnership.
But Roblox does not distribute mass Robux through third-party giveaway sites, and Roblox’s official guidance treats these offers as scams.
Why 2026 tactics work better than older scams
The newest versions succeed because they focus on psychology, not technology.
They use:
- Speed: click now, claim now, act fast
- Social proof: chat feeds, “recent winners,” “I got paid” comments
- Personalization: username entry, avatar display, “your reward is ready” screens
- Friction tricks: endless verification steps and “processing” delays
- Authority: Discord staff roles, “support tickets,” official-looking copy
- Distribution: spam inside Roblox servers, plus TikTok and YouTube Shorts
This is why people can be skeptical and still get pulled in.
It looks familiar. It looks popular. It looks easy.
The 3 main money engines behind Robux giveaway scams
Most “free Robux” scams make money through one or more of these engines.
1) Affiliate offers and offerwalls
This is the most common.
The scam site tells you to “verify” by completing a task:
- Install an app
- Sign up for a trial
- Fill out a survey
- Download a browser extension
- Enter an email and confirm
The scammer earns money when you complete those offers. The Robux never comes.
This model is widely discussed in “human verification required” scam breakdowns, where offer completion generates revenue for the publisher, not the victim.
2) Subscription traps
Some “verification” offers are actually paid trials.
They may appear as:
- $1 “verification fee”
- A “free trial” that requires a card
- A mobile subscription that renews automatically
People often don’t notice the fine print, especially kids.
The result is real charges, and a lot of confusion.
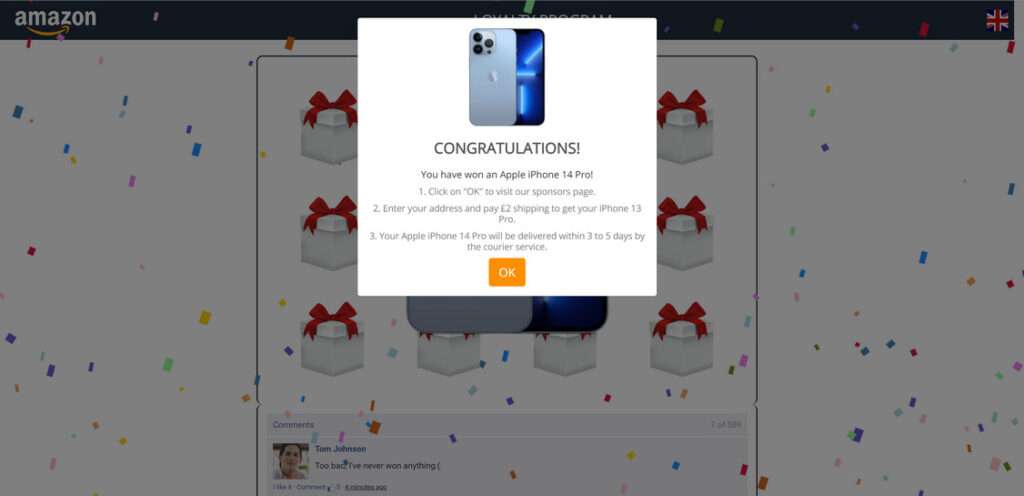
Consumer protection agencies regularly warn parents about unexpected payments and the importance of purchase controls and review habits, especially in gaming contexts.
3) Account theft via phishing and session hijacks
Some scams escalate to account takeover attempts.
This can happen through:
- Fake Roblox login pages
- “Verify your Roblox account” prompts
- Discord QR code login traps
Discord specifically warns users that QR code login requests from strangers may be phishing attempts, and advises caution.
Once a Roblox account is stolen, scammers use it to spread more scam links and drain Robux or items.
The “username first” trick is not harmless
A lot of people think, “If I only typed my username, it’s safe.”
Typing a username is not the same as giving your password, but it still matters because it is a commitment device. It makes the scam feel personalized and “in progress.”
From there, the site can:
- Show your avatar
- Pretend it is connecting to Roblox
- Create a “claim steps” flow
- Push you into the real trap, the tasks or Discord funnel
In 2026, this is one of the most effective conversion tactics.
The spam-in-Roblox-chat tactic is a huge tell
A legitimate platform does not need to flood public Roblox servers with repeated “free Robux” messages.
Spam campaigns often look like:
- The same message repeated across multiple games
- A steady timing rhythm that feels automated
- Accounts that appear and disappear quickly
- Messages that claim “it works” or “I got paid”
Even Roblox community discussions note ongoing problems with bots sending scam messages and tricking players into losing accounts.
If the link came from server spam, treat it as dangerous immediately.
Discord is the new “second stage” of the scam
A big 2026 trend is that the website is only step one.
Step two is Discord.
Why? Because Discord lets scammers apply pressure and guide victims in real time, which increases success rates. Discord’s own safety guidance warns users not to click suspicious links, not to download unknown programs, and not to scan QR codes from unverified sources.
Once you’re in a Discord server, the scam can shift from “do tasks” to “talk to staff,” which feels more legitimate to kids.
And that is where scams can turn into account theft very quickly.
The evergreen truth about “Robux giveaway sites”
No matter what they call it in 2026, these sites share one reality:
- There is no giveaway.
- There is no generator.
- There is no hack.
- There is no legit free Robux website.
The entire system is engineered so scammers make money and players take the risk.
How The Scam Works
Below is a step-by-step breakdown of the most common Robux giveaway scam 2026 tactics, including the affiliate task funnel, the Roblox chat spam funnel, and the Discord takeover funnel. You’ll notice that scams can branch, but they always follow the same logic: hook, personalize, push friction steps, profit.
Step 1: Distribution where kids already are
Scammers don’t wait for someone to search.
They push the link into high-traffic places:
- Public Roblox servers (chat spam)
- TikTok and YouTube Shorts (“proof” clips)
- Discord servers and DMs
- Comment sections under Roblox videos
The message is designed to create urgency and curiosity:
- “Free Robux 2026 event”
- “Milestone reward”
- “Claim 5,000 Robux now”
- “No password needed”
It’s not an argument.
It’s a trigger.
Step 2: A clean landing page that imitates trust
Most scam pages in 2026 are visually polished.
They use:
- Roblox-like colors and layout
- Official-sounding headlines
- Minimal clutter
- A short “FAQ” that answers your doubts
- A progress bar or “connection” animation
This design is deliberate. It reduces skepticism long enough to get you to the next click.
Step 3: Username entry and fake personalization
Now comes the most common setup:
- Enter your Roblox username
- Choose a Robux amount
- Click continue
Then the site “confirms” you:
- Your username appears on the page
- Sometimes your avatar displays
- A reward screen claims “your Robux is ready”
This is where many users become emotionally invested.
They feel like they already started the claim process.
Step 4: The “connection” theater
The site often runs a fake sequence:
- “Connecting to Roblox servers…”
- “Verifying username…”
- “Generating Robux…”
- “Preparing reward…”
This is only for psychology.
No third-party site is generating Robux into your account.
Roblox’s own guidance makes clear that these “free Robux” offers are scams.
Step 5: The real trap appears: verification steps
Once you are invested, you hit the paywall, but it’s disguised as verification.
Common prompts:
- “Complete 1 task to verify you are human”
- “Finish an offer to unlock your Robux”
- “Install 1 app to claim”
- “Join Discord to receive payout”
This is the moment the scam begins making money.
From here, the funnel usually branches.
Branch A: Username to tasks (affiliate scheme)
This is the highest-volume scam format.
What you see
A list of “offers”:
- Install an app
- Complete a survey
- Sign up for a trial
- Download a browser extension
Often with a “Get” button and a promise that it only takes 1 minute.
What’s really happening
The scammer earns affiliate commission if you complete the offer, and you either:
- Get nothing
- Get stuck in an endless “didn’t verify, do another task” loop
- Get pushed into subscriptions and recurring charges
This “human verification required” pattern is a known scam structure where offers generate revenue for the publisher.
The loop tactic
Many victims say: “I completed the task and it still didn’t work.”
That can happen because:
- The offer has hidden requirements
- The crediting fails
- The page intentionally ignores completions to force more tasks
From the scammer’s perspective, the best outcome is not “you verified.”
The best outcome is “you keep trying.”
Branch B: Roblox chat spam to scam site
This is how scammers scale.
How it looks in servers
You see repeated messages like:
- “I just got Robux from this site”
- “Use this code”
- “Milestone event reward link”
The messages often:
- Repeat in multiple games
- Appear at a steady rhythm
- Look copy-pasted
- Come from accounts that disappear quickly
Roblox community discussions continue to report chat spam bots pushing scam sites and causing account losses.
Why this works
In-game chat feels local and safe.
Kids assume anything posted inside a game is “part of the game world.” Scammers exploit that trust.
Branch C: Discord “claim” and verification scams
This is the most dangerous branch in 2026.
Stage 1: The site pushes Discord
The scam site says:
- “Join Discord to claim your reward”
- “Open a ticket for payout”
- “Verify to receive Robux”
This makes victims feel like there’s a real support team.
Stage 2: Discord creates authority
Inside Discord, scammers often use:
- Staff roles and badges
- Ticket bots
- “Support” channels
- Rules and announcements
- Pinned messages that sound official
This reduces resistance, especially for kids.
Stage 3: Account theft tactics
Common methods include:
- QR code login traps: scan a code, approve a login, and your account access is handed to the scammer
- Fake login pages: “verify your Roblox account” on a lookalike site
- Downloads: “verification tool,” “anti-bot,” “reward app”
- Token or session tricks: requesting screenshares or “proof” that leaks access
Discord warns that QR login requests from people you don’t know may be phishing, and that users should avoid scanning untrusted QR codes.
Step 6: The stalling promise
A classic line is:
“Your Robux will arrive in 24 to 48 hours.”
That delay is strategic.
It keeps victims waiting instead of reporting, and it gives scammers time to:
- Collect more completions
- Push more links
- Rotate domains
- Keep the scam running
Step 7: Monetization, even if no one gets Robux
This is the part many people miss.
The scam does not need to deliver Robux.
It only needs to make money through:
- Affiliate commissions
- Subscription sign-ups
- Ads and tracking
- Data collection
- Account takeovers
The “Robux” is just the bait that makes you walk through the funnel.
Step 8: Rebranding and repetition
When a domain gets reported, the scam doesn’t end.
It relaunches:
- New domain name
- Same template
- Same steps
- Same Discord server or a new copy
- Same spam tactics
That’s why the scam feels everywhere in 2026.
Because it is designed to be replaceable.
What To Do If You Have Fallen Victim to This Scam
If you clicked a link, entered your username, joined a Discord, completed tasks, or entered login information, take a breath.
You can reduce damage quickly by taking the right steps.
Follow the steps that match what happened to you.
1. If you entered your Roblox password anywhere, change it immediately
Do this right now:
- Change your Roblox password to a new, unique password
- Enable 2-step verification on Roblox
- Confirm your email and phone on the account are still correct
- Review recent logins, transactions, and trades
Roblox provides steps for enabling 2-step verification and improving account security.
2. Secure your email account, because it controls password resets
If a scammer gets your email, they can reset Roblox.
- Change the email password
- Turn on 2-factor authentication for your email
- Check for suspicious forwarding rules and filters
- Review recent login activity
3. Check your Robux balance, purchase history, and trades
Look for:
- Robux spent without your approval
- Items missing
- Trades you didn’t make
- Unfamiliar messages sent from your account
If your account was compromised, Roblox’s help resources for hacked accounts emphasize securing the account and using support if needed.
4. Remove browser notification permissions
Many scam sites push notification popups.
If you clicked “Allow”:
- Go to your browser notification settings
- Remove and block the scam domain and any unknown domains
This helps stop persistent popups and scam redirects.
5. Remove suspicious extensions, apps, and downloads
If you installed anything because the site or Discord told you to:
- Uninstall it
- Remove any new browser extensions you don’t recognize
- Run a trusted security scan on the device
- Restart your browser and re-check extensions
Do not keep “verification tools.” That’s a common malware route.
6. If a card was used, check statements and cancel subscriptions
If you entered payment details for a “verification” offer:
- Check bank and card statements
- Look for subscriptions that may renew
- Cancel anything you didn’t intentionally sign up for
- Contact your bank or payment provider if you see unauthorized charges
The FTC has guidance for parents and families around unexpected payments and safer purchase controls.
7. If Discord was involved, lock down Discord security
If you joined a server or interacted with “support”:
- Leave the suspicious server
- Enable 2-factor authentication on Discord
- Review Authorized Apps and remove anything unfamiliar
- Do not scan QR codes for login unless you initiated it
- Do not click verification links from strangers
Discord’s safety guidance explicitly warns against scanning unknown QR codes and clicking suspicious links.
8. Warn friends and family, especially kids, without blaming anyone
If a child fell for it, keep it calm.
A simple message works best:
- “These sites are designed to trick people.”
- “There is no free Robux website.”
- “Ask before clicking any Robux link.”
Fear and shame make kids hide problems. Calm rules prevent repeats.
9. Report the spam where you saw it
Reporting reduces spread:
- Report the Roblox chat spam messages if possible
- Report the video or account posting scam links on social media
- Report the Discord server if it’s running phishing or scam verification
10. Save evidence if money was lost or accounts were compromised
Save:
- Screenshots of the scam page
- The domain name
- Discord server name and invite link (if safe to copy)
- Charges or subscription receipts
- Roblox transaction history screenshots
Evidence helps if you need to dispute charges or contact support.
How to Remove Unwanted Apps and Malware
If a pop-up scam tricked you into downloading an unwanted program — or you suspect your device is infected — follow the free, step-by-step removal guide below to clean it completely.
Please follow the steps in order. If you get stuck or have doubts at any point, stop and ask for help in our free support forum — our team will guide you personally.
 Remove Unwanted Apps and Malware from Windows
-
 Remove Unwanted Apps and Malware from Mac
 Remove Unwanted Apps and Malware from Android
- Remove Unwanted Apps and Malware from iPhone and iPad
Remove Unwanted Apps and Malware from Windows
- STEP 1: Uninstall malicious programs from Windows
- STEP 2: Reset browsers back to default settings
- STEP 3: Use Malwarebytes Anti-Malware to remove malware and unwanted programs
- STEP 4: Use HitmanPro to scan your computer for badware
- STEP 5: Use AdwCleaner to remove adware and malicious browser policies
STEP 1: Uninstall malicious programs from Windows
In this first step, we will manually check if any unknown or malicious programs are installed on the computer. Sometimes adware and browser hijackers can have a usable Uninstall entry that can be used to remove them.
-
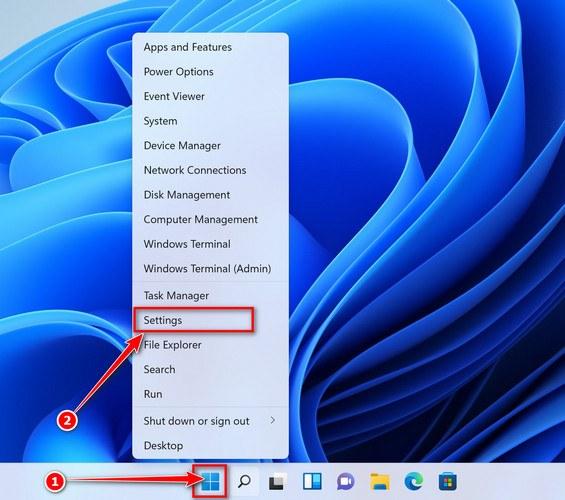
Open the Settings app
Press Windows + I on your keyboard to open Settings. Alternatively, right-click the Start button and select “Settings” from the menu.
-
Go to “Apps & Features”
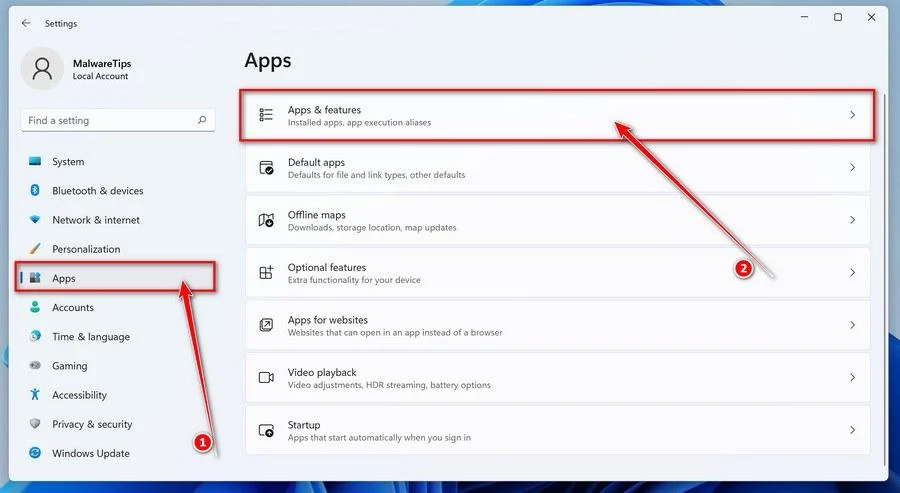
In the Settings window, click “Apps” in the sidebar, then select “Apps & Features“.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click the three dots next to it and select “Uninstall“.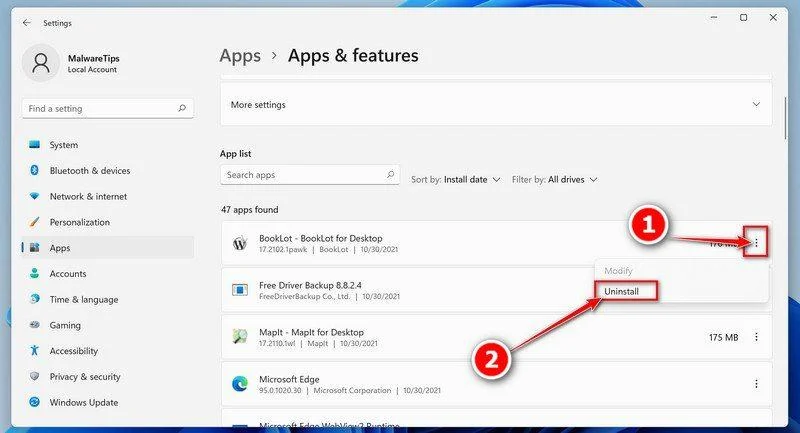 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.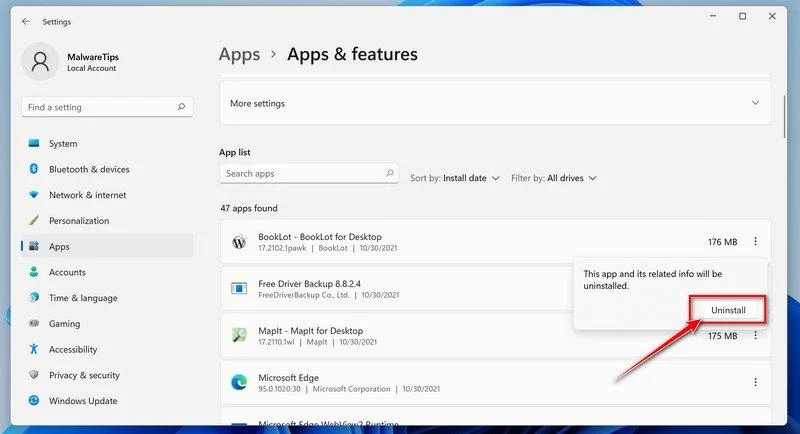
-
Open the Settings app
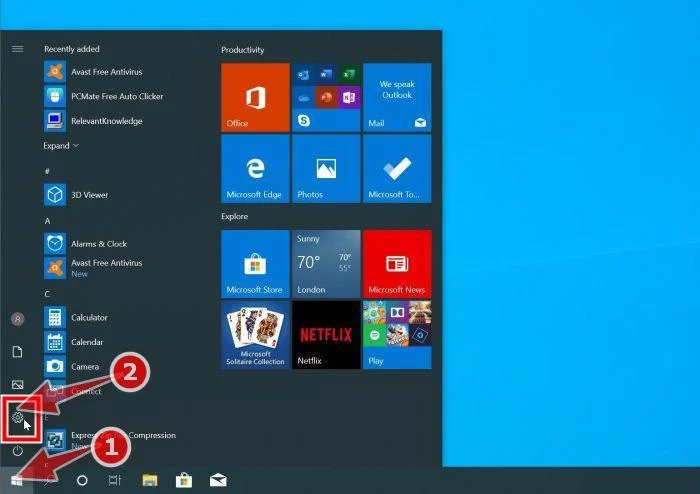
Press Windows + I on your keyboard to open Settings. Alternatively, click the Start button on the taskbar and select “Settings” (the gear icon).
-
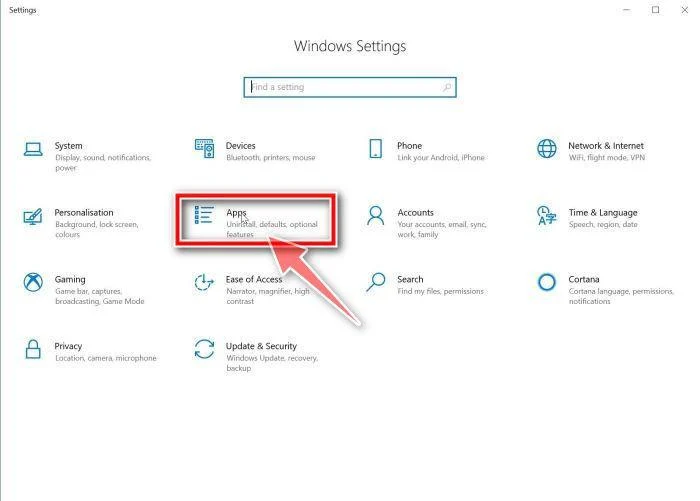
Click on “Apps”
In the “Windows Settings” window, click “Apps“. The “Apps & Features” section should open by default — if it doesn’t, select it from the list on the left.
-
Find and uninstall the malicious program
Scroll through the list of installed apps and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name.
Quick tip: click “Sort by” and choose “Install date“. Malware is usually one of the most recently installed programs, so it will appear near the top.
When you find the malicious program, click on it and select “Uninstall“.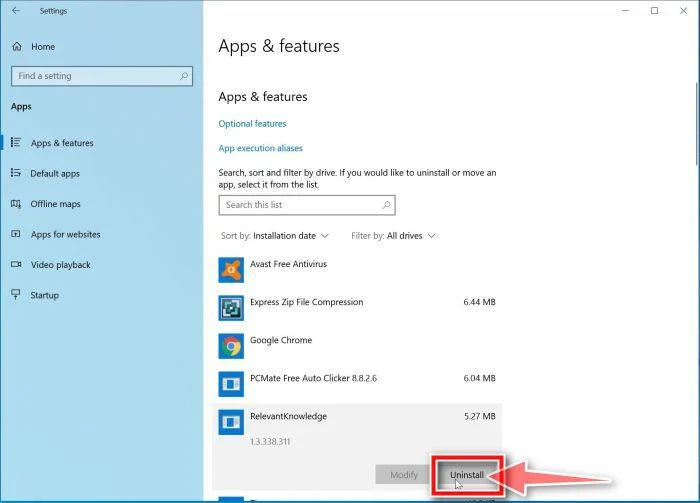 Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.
-
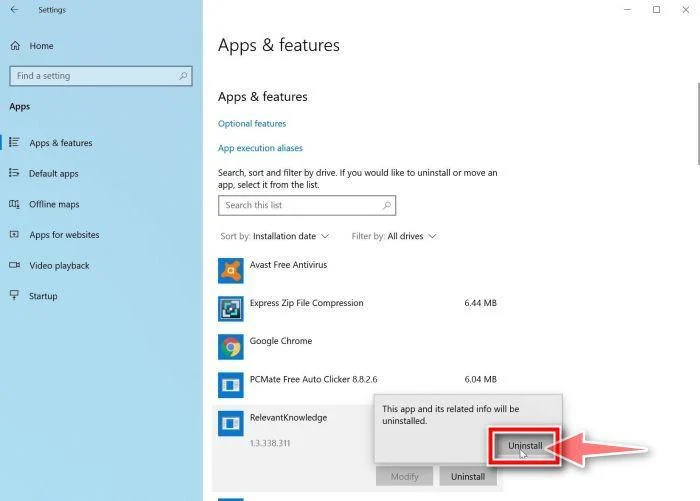
Complete the uninstall
Confirm by clicking Uninstall in the message box, then follow the remaining prompts.
Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
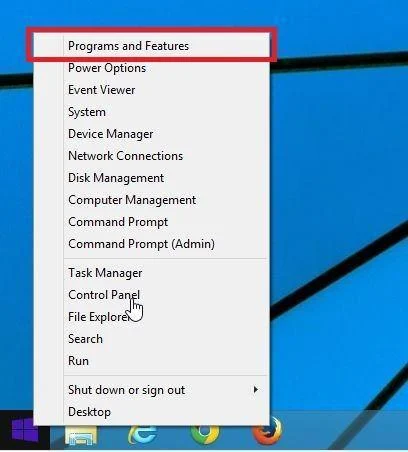
Open “Programs and Features”
Right-click the Start button in the taskbar, then select “Programs and Features“. This takes you straight to the list of installed programs.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.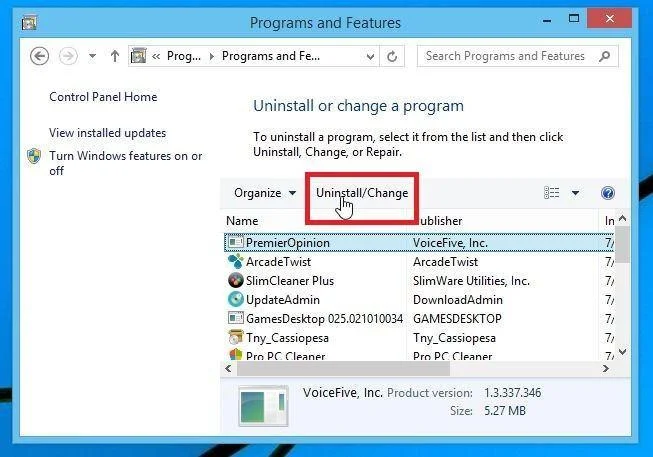
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
-
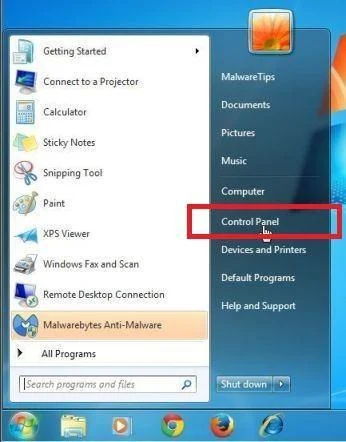
Open the Control Panel
Click the “Start” button, then click “Control Panel“.
-
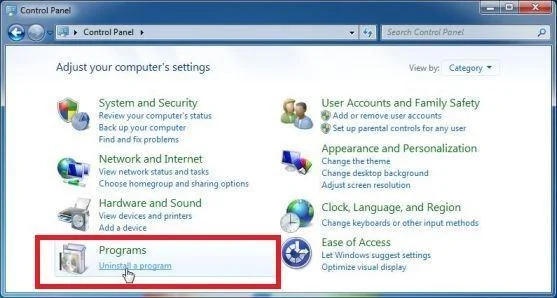
Click on “Uninstall a Program”
In the Control Panel, click “Uninstall a Program” under the Programs category.
-
Find and uninstall the malicious program
Scroll through the list of installed programs and look for anything suspicious — a program you don’t remember installing, or one with a strange or generic name. Click to highlight it, then click the “Uninstall” button.
Didn’t find any suspicious programs? That’s fine — not all infections install visible apps. Just continue with the next step in this guide.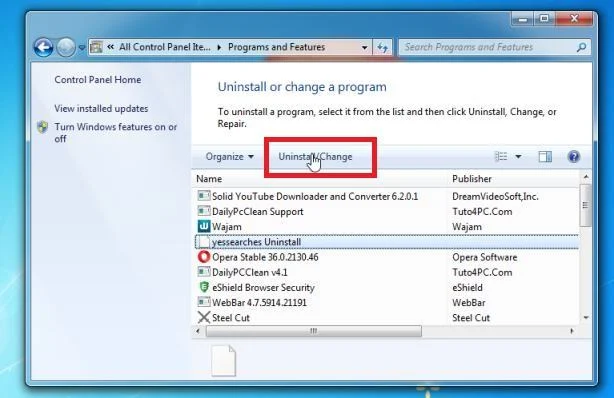
-
Complete the uninstall
Confirm by clicking Yes in the message box, then follow the remaining prompts. Read each prompt carefully — some malicious programs use confusing wording or pre-ticked boxes hoping you’ll click through without looking.
With the malicious programs removed, you’re ready for the next step in this guide.
STEP 2: Reset browsers back to default settings
In this step, we will remove spam notifications, malicious extensions, and change to default any settings that might have been changed by malware.
Please note that this method will remove all extensions, toolbars, and other customizations but will leave your bookmarks and favorites intact. For each browser that you have installed on your computer, please click on the browsers tab below and follow the displayed steps to reset that browser.
Reset Chrome for Windows to default settings
We will now reset your Chrome browser settings to their original defaults. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
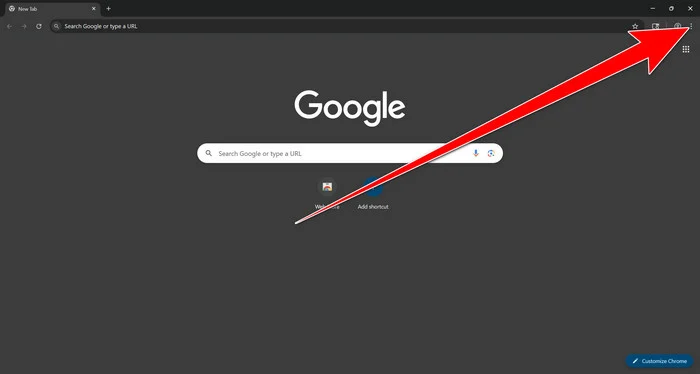
Open the Chrome menu
Open Google Chrome and click the three-dot (⋮) icon in the top-right corner.
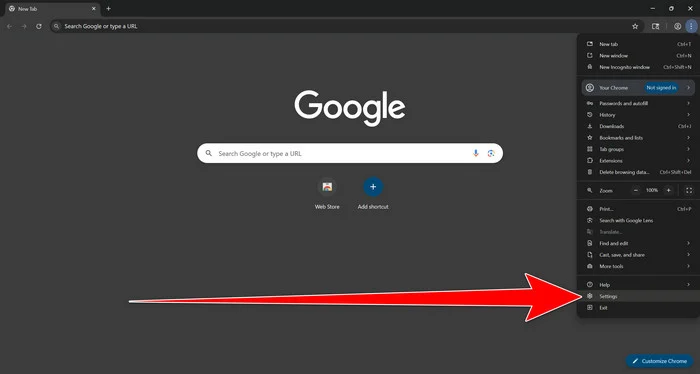
Open Chrome Settings
Select Settings from the Chrome menu.
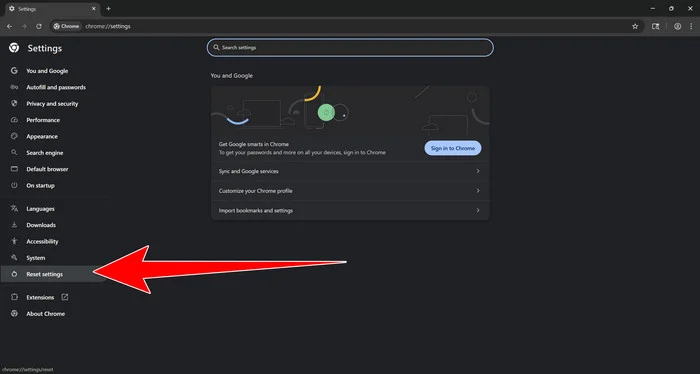
Select “Reset settings”
Look at the menu on the left side of the Settings page. Scroll down and click Reset settings.
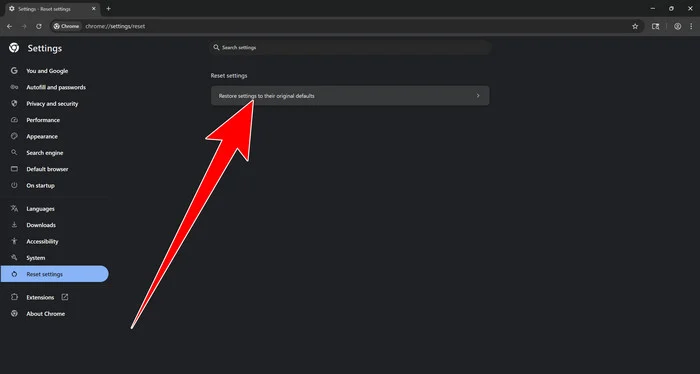
Restore Chrome’s original settings
Click Restore settings to their original defaults.
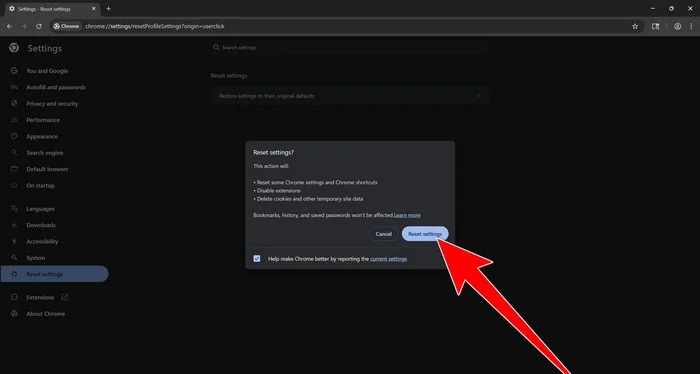
Confirm the Chrome reset
A confirmation window will appear. Click Reset settings.
This will:
- Restore the default search engine, homepage, and new tab page
- Reset startup pages and pinned tabs
- Disable installed extensions
- Clear temporary cookies and website data
Don’t worry: Chrome will not delete your bookmarks, browsing history, or saved passwords.
Restart Chrome and perform a test search. If your searches now open normally in Google, you can stop here.
If searches are still redirected through shady domains complete the additional step below.
Remove persistent search hijacker data
Only complete this step if the redirect continues after resetting Chrome.
Some browser hijackers hide inside Chrome’s local search-engine database. A standard Chrome reset may not remove this database, which is why searches can continue to pass through shady sites.
The following procedure creates a backup of the affected database and allows Chrome to build a new, clean version. This is safer and less disruptive than deleting the entire Chrome profile.
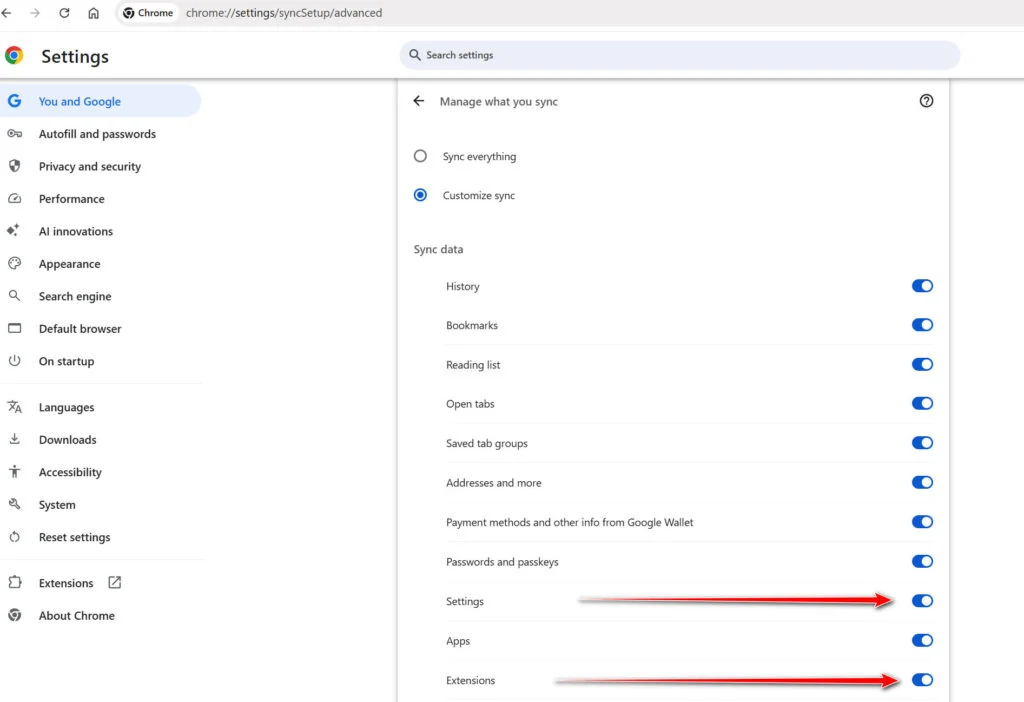
First, prevent Chrome Sync from restoring the hijacked settings:
- Open a new Chrome tab.
- Copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/syncSetup/advanced - Under Manage what you sync, select Customize sync.
- Turn off Settings and Extensions.
- You can leave Bookmarks and Passwords enabled so your important data remains synchronized.
Note: Some newer Chrome versions may automatically redirect this address to the Google Account settings page. If that happens, locate the list of synchronized Chrome data and turn off Settings and Extensions there.
Now save anything you are working on and close every Chrome window.
Run the cleanup command:
- Press the Windows key on your keyboard.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command shown below.
- Right-click inside the PowerShell window to paste the command, then press Enter.
- If Windows warns you about pasting multiple lines, select the option to continue.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"

Get-Process chrome -ErrorAction SilentlyContinue |
 Stop-Process -Force

$root = "$env:LOCALAPPDATA\Google\Chrome\User Data"

if (Test-Path $root) {
 $profiles = Get-ChildItem $root -Directory |
 Where-Object {
 $_.Name -eq "Default" -or
 $_.Name -match "^Profile \d+$"
 }

 foreach ($profile in $profiles) {
 foreach ($name in @(
 "Web Data",
 "Web Data-journal",
 "Web Data-wal",
 "Web Data-shm"
 )) {
 $file = Join-Path $profile.FullName $name

 if (Test-Path $file) {
 $backup = "$file.search-hijacker-backup-$stamp"
 Move-Item -LiteralPath $file -Destination $backup
 Write-Host "Backup created: $backup"
 }
 }
 }
}

Write-Host ""
Write-Host "Chrome search data has been cleaned."
Write-Host "You can now reopen Chrome."
Wait until PowerShell displays the following message:
Chrome search data has been cleaned.
You can now reopen Chrome.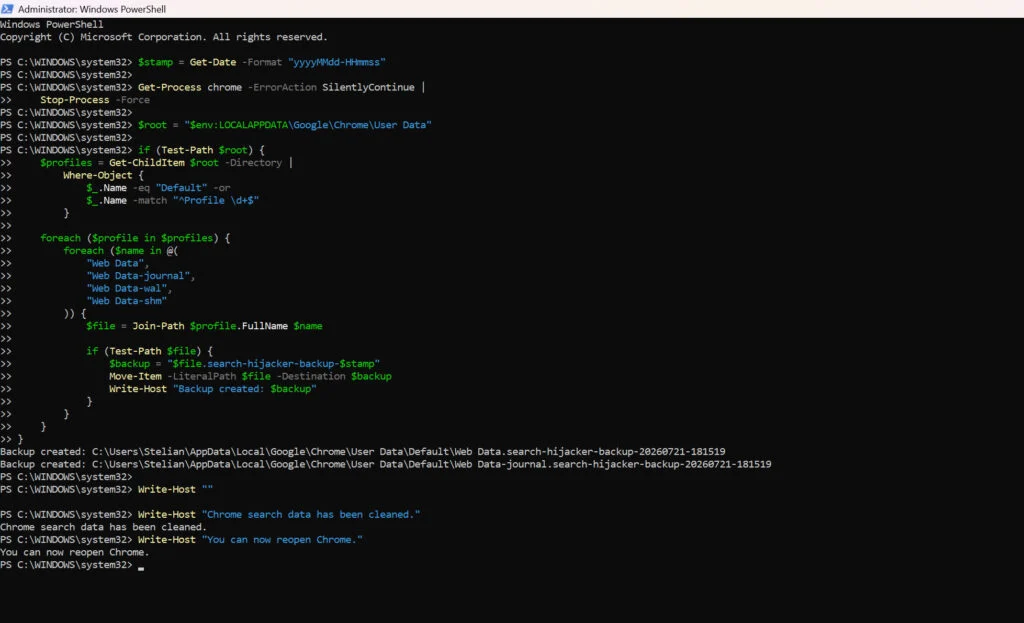
Close PowerShell and reopen Google Chrome. Chrome will automatically create a clean search database for every local profile.
Next, copy the following address, paste it into Chrome’s address bar, and press Enter:
chrome://settings/searchEnginesMake sure Google is selected as the default search engine. Test several searches from the address bar and confirm that they no longer pass through shady search engines.
Your important Chrome data is protected: the PowerShell cleanup does not remove bookmarks, saved passwords, browsing history, cookies, or installed extensions. However, it may reset locally stored Autofill addresses and form suggestions.
The original search database is not deleted. PowerShell renames it and adds
search-hijacker-backupto its filename so it can be recovered if necessary.Keep Settings and Extensions synchronization disabled while testing Chrome. Do not enable every extension at once. Enable only the extensions you recognize, one at a time, and test Chrome after each one.
If the redirect returns after enabling a particular extension, remove that extension immediately.
Reset Firefox for Windows to default settings
We will now reset your Firefox browser settings to their default. The reset feature fixes many issues by restoring Firefox to its factory default state while saving your essential information like bookmarks, passwords, web form auto-fill information, browsing history, and open tabs.
-
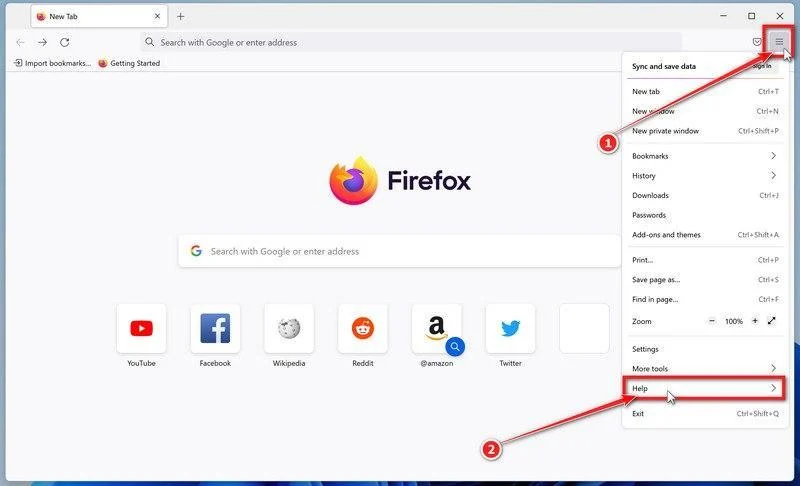
Open the Firefox menu and click “Help”
Click the three horizontal lines in the top-right corner of Firefox to open the main menu, then select “Help“.
-
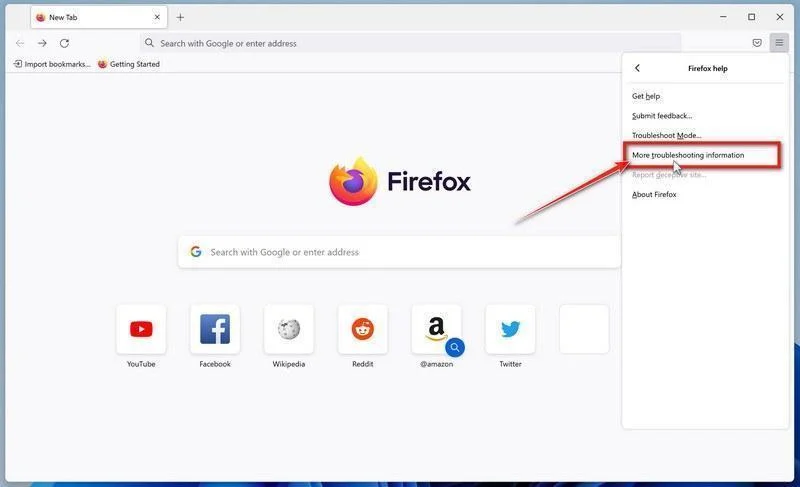
Click “More troubleshooting information”
In the Help menu, click “More troubleshooting information“.
-
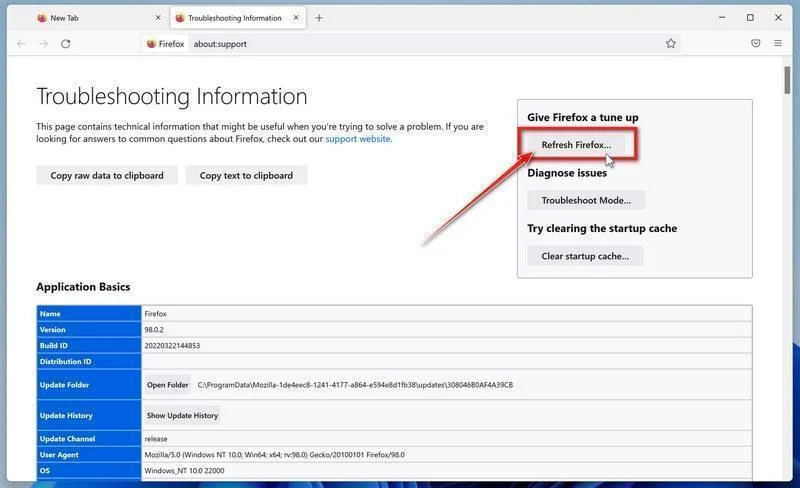
Click “Refresh Firefox”
On the “Troubleshooting Information” page, click the “Refresh Firefox” button in the top-right area of the page.
-
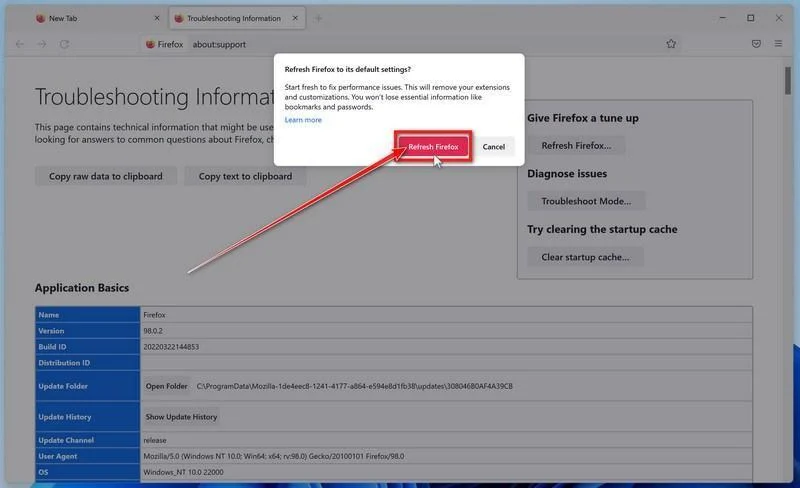
Confirm the refresh
In the confirmation window, click “Refresh Firefox” again. This removes extensions, themes, and customized settings — the usual hiding places for browser hijackers — while keeping your bookmarks, history, and saved passwords safe.
-
Click “Finish”
Firefox will close, reset itself to default settings, and reopen with a window listing the information that was restored. Click “Finish” — your Firefox is now clean.
About the “Old Firefox Data” folder: Firefox saves a copy of your old profile on your desktop. If something you need is missing after the reset, you can recover it from this folder. Otherwise, delete the folder — it contains sensitive data like passwords and cookies, and may also still hold the malicious files you just removed.
Reset Microsoft Edge to default settings
We will now reset your Microsoft Edge browser settings to their default. This will reset your startup page, new tab page, search engine, and pinned tabs. It will also disable all extensions and clear temporary data like cookies. Your favorites, history, and saved passwords will not be cleared.
Updated for Microsoft Edge on Windows 10 and Windows 11 — July 2026.
-
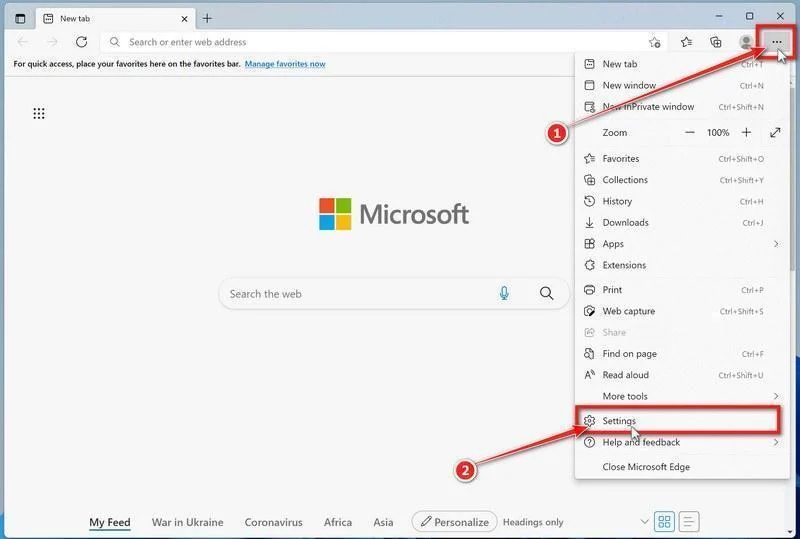
Open the Edge menu and click “Settings”
Open Microsoft Edge. In the top-right corner, click the three-dot (…) icon, then click Settings.
-
Prevent the unwanted settings from returning through Edge Sync
If you are signed in to Microsoft Edge, a bad setting or extension may be stored in your Microsoft account and return after the reset.
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/profiles/syncOn the Sync page, turn off these two options:
- Settings
- Extensions
You can leave Favorites and Passwords turned on.
If Edge says that sync is already off, simply continue to the next step.
Important: Edge Sync settings are separate for each profile. If you use more than one Edge profile, switch to each affected profile and repeat this step.
You do not need to sign out of your Microsoft account or delete the Edge profile.
-
Open “Reset settings”
In the left sidebar, click Reset settings.
You can also open the reset page directly. Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/reset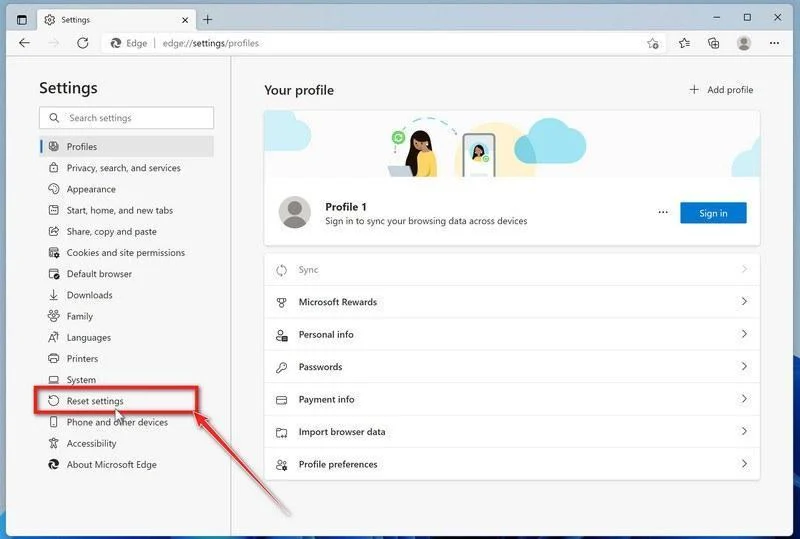
-
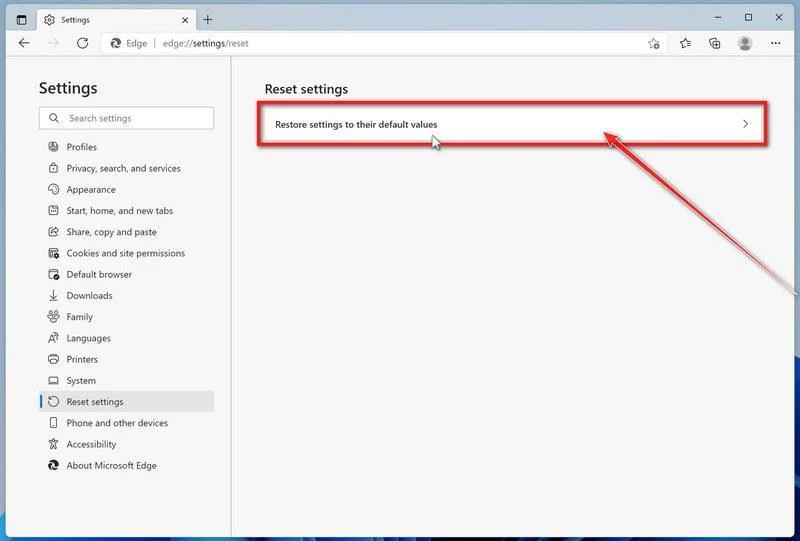
Click “Restore settings to their default values”
Click Restore settings to their default values.
-
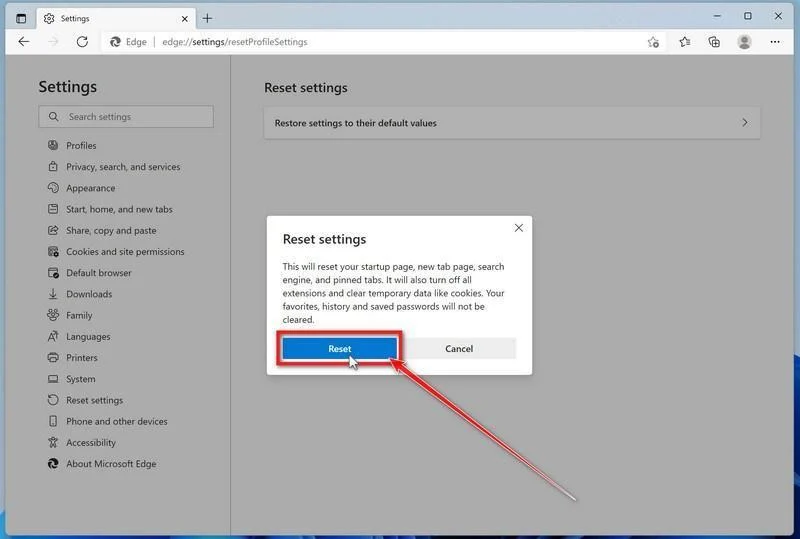
Confirm the reset
In the confirmation dialog, click Reset.
This resets the startup page, new tab page, search engine, and pinned tabs. It also disables all extensions and clears temporary site data, such as cookies.
Don’t worry: your favorites, browsing history, and saved passwords will not be deleted.
-
Check your extensions before turning them back on
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://extensionsRemove any extension you do not recognize or no longer use. Pay particular attention to extensions related to search, coupons, shopping, PDF conversion, browser protection, new tabs, or video downloading.
Do not turn all extensions back on at the same time. Enable only the extensions you recognize and trust.
-
Select a trusted search engine
Copy the following address, paste it into the Edge address bar, and press Enter:
edge://settings/searchEnginesSelect Bing, Google, DuckDuckGo, or another search provider you trust and make it the default.
Remove any unknown search engines, especially providers with strange names or addresses that you did not add yourself.
Restart Edge and perform a search from the address bar. If searches are no longer redirected, you can stop here.
-
If the redirect remains, clean the corrupted search data without deleting the Edge profile
Use this additional step only if Edge continues to redirect searches after the normal reset.
This command cleans the search-engine database from every local Edge profile while keeping your favorites, saved passwords, browsing history, cookies, and profiles.
Before continuing: save anything you are working on because the command will close Microsoft Edge.
- Open the Windows Start menu.
- Type PowerShell.
- Open Windows PowerShell. Administrator access is not required.
- Copy the entire command below.
- Paste it into PowerShell and press Enter.
$stamp = Get-Date -Format "yyyyMMdd-HHmmss"
$root = Join-Path $env:LOCALAPPDATA "Microsoft\Edge\User Data"

Get-Process -Name msedge -ErrorAction SilentlyContinue |
    Stop-Process -Force -ErrorAction SilentlyContinue

Start-Sleep -Seconds 2

if (-not (Test-Path -LiteralPath $root)) {
    Write-Host "The Microsoft Edge profile folder was not found:"
    Write-Host $root
    return
}

$profiles = Get-ChildItem -LiteralPath $root -Directory |
    Where-Object {
        $_.Name -eq "Default" -or
        $_.Name -match "^Profile \d+$"
    }

$movedFiles = 0

foreach ($profile in $profiles) {
    foreach ($name in @(
        "Web Data",
        "Web Data-journal",
        "Web Data-wal",
        "Web Data-shm"
    )) {
        $file = Join-Path $profile.FullName $name

        if (Test-Path -LiteralPath $file) {
            $backup = "$file.search-reset-backup-$stamp"

            try {
                Move-Item -LiteralPath $file -Destination $backup -ErrorAction Stop
                Write-Host "Cleaned: $($profile.Name)\$name"
                $movedFiles++
            }
            catch {
                Write-Warning "Could not clean: $file"
            }
        }
    }
}

Write-Host ""

if ($movedFiles -gt 0) {
    Write-Host "Microsoft Edge search data has been cleaned." -ForegroundColor Green
    Write-Host "You can now reopen Microsoft Edge."
}
else {
    Write-Host "No Edge search database files were found." -ForegroundColor Yellow
}
The command does not permanently delete the original files. It renames them as backup files, and Edge creates a clean search database when it starts again.
Note: this additional cleanup may also reset saved form-fill suggestions, saved addresses, and manually added search engines. It does not delete favorites, passwords, or browsing history.
-
Reopen Edge and test the browser
Open Microsoft Edge again, visit edge://settings/searchEngines, and select your preferred search engine.
Perform several searches from the address bar to confirm that the redirect is gone.
Keep synchronization for Settings and Extensions turned off until you are certain that the computer and extensions are clean. If you enable them again, turn them on one at a time and test Edge after each change.
-
If Edge still redirects your searches
Open edge://policy. If this is your personal computer and Edge displays unknown policies such as ExtensionInstallForcelist or DefaultSearchProvider, the hijacker may be installed outside the browser profile.
In that situation, continue with the next malware-removal steps and run a complete antivirus scan. If the computer belongs to a company or school, contact its IT administrator before changing any policies.
Reset Internet Explorer to default settings
We will now reset your Internet Explorer browser settings to their default. You can reset Internet Explorer settings to return them to the state they were in when Internet Explorer was first installed on your computer.
-
Go to “Internet Options”.
Open Internet Explorer, click on the gear icon in the upper-right part of your browser, then select “Internet Options“.
-
Select the “Advanced” tab, then click “Reset”
In the “Internet Options” dialog box, select the “Advanced” tab, then click on the “Reset” button.
-
Click on “Reset”.
In the “Reset Internet Explorer settings” section, select the “Delete personal settings” checkbox, then click on the “Reset” button.
-
Click on “Close”.
When Internet Explorer has completed its task, click on the “Close” button in the confirmation dialogue box.
Close your browser and then you can open Internet Explorer again.
STEP 3: Use Malwarebytes Anti-Malware to remove malware and unwanted programs
In this third step, we will install Malwarebytes to scan and remove any infections, adware, or potentially unwanted programs that may be present on your computer.
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

STEP 4: Use HitmanPro to scan your computer for badware
In this next step, we will scan the computer with HitmanPro to ensure that no other malicious programs are installed on your device.
HitmanPro is a second-opinion scanner — it’s designed to catch what your main antivirus might have missed. Instead of relying on a single detection engine, it checks the behavior of files in the locations where malware usually hides. Anything suspicious gets sent to the cloud, where it’s analyzed by two of the best antivirus engines available: Bitdefender and Kaspersky.
Good news: scanning is completely free, with no limits. You only need a license when it’s time to remove what was found — and even then, you can activate a free one-time 30-day trial to clean your PC at no cost. (A full license is $24.95 per year for 1 PC.)
-
Download HitmanPro
Click the button below to download HitmanPro. Remember — the scan is free, so you have nothing to lose by checking your PC.
Download HitmanProFree scan. Removing threats needs the free 30-day trial. Opens the official HitmanPro page in a new tab. HitmanProSecond-opinion malware scanner from Sophos
-
Install HitmanPro
When the download finishes, open your Downloads folder and double-click the file: “hitmanpro.exe” on 32-bit Windows, or “hitmanpro_x64.exe” on 64-bit Windows.
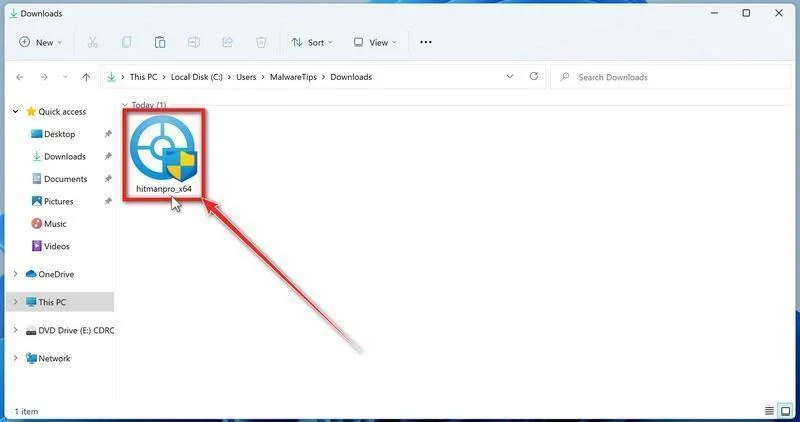
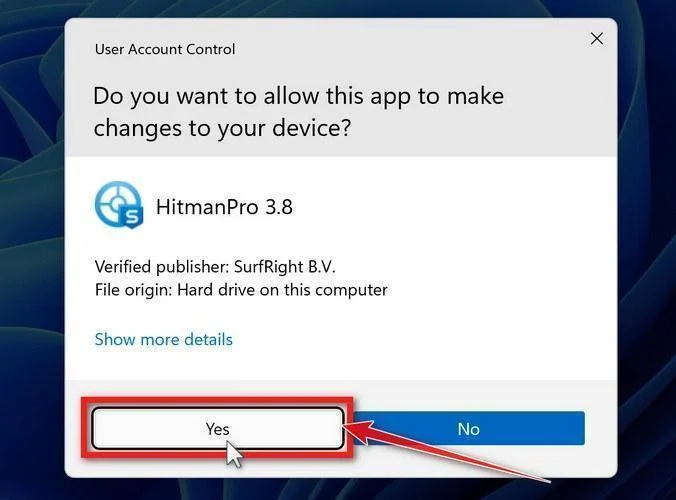
If a User Account Control pop-up asks whether HitmanPro can make changes to your device, click “Yes” to continue.
-
Follow the On-Screen Prompts
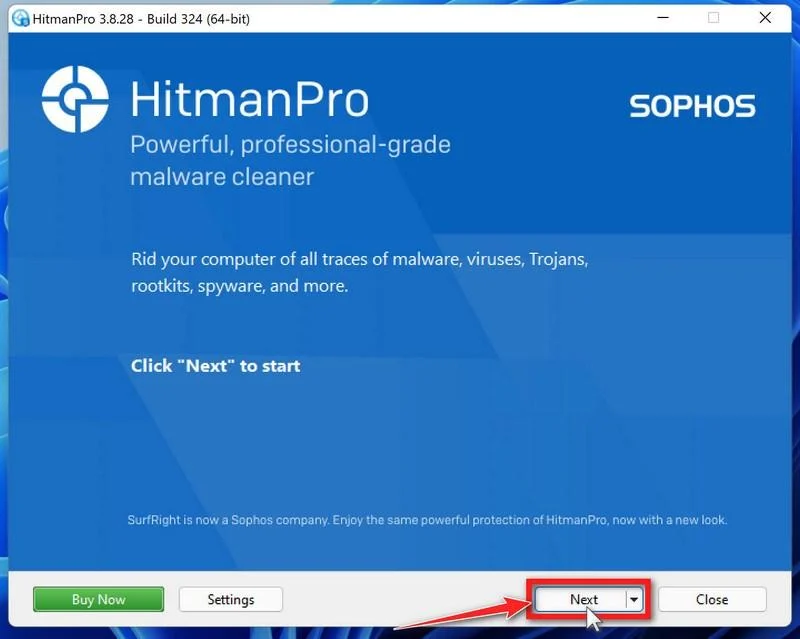
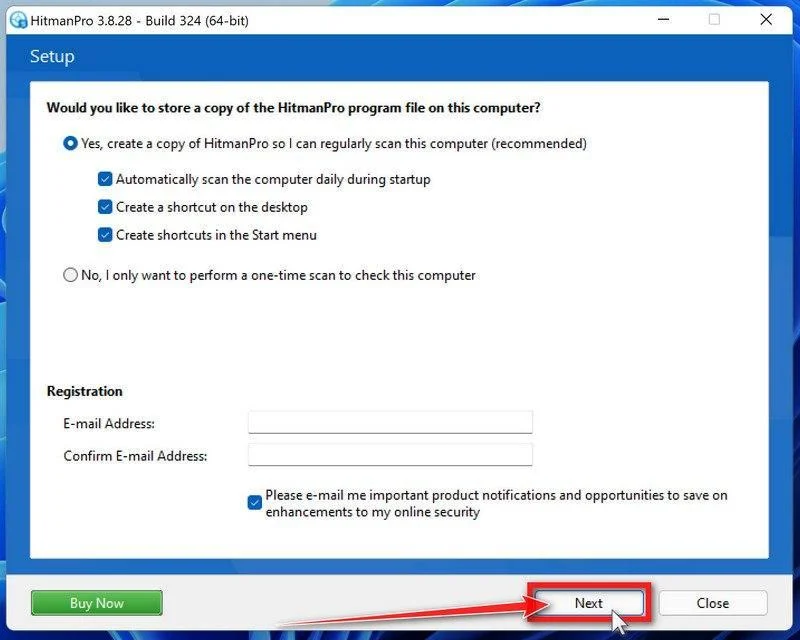
On the HitmanPro start screen, click “Next” to begin the system scan. No lengthy setup required — it goes straight to work.
-
Wait for the Scan to Finish
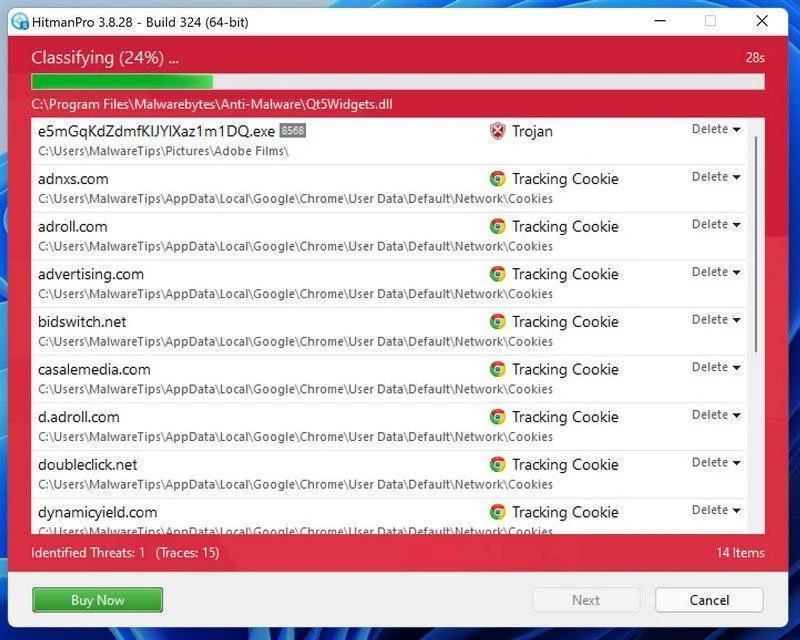
HitmanPro will now check your computer for malicious programs. This usually takes just a few minutes thanks to its cloud-based scanning.
-
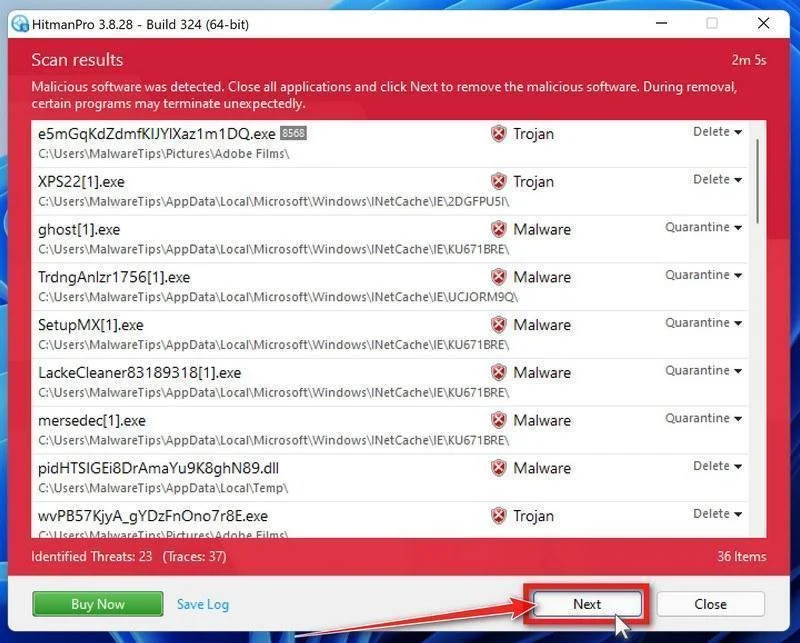
Review the Results and Click “Next”
When the scan is done, HitmanPro will show you everything it found. Click “Next” to remove the detected threats.
-
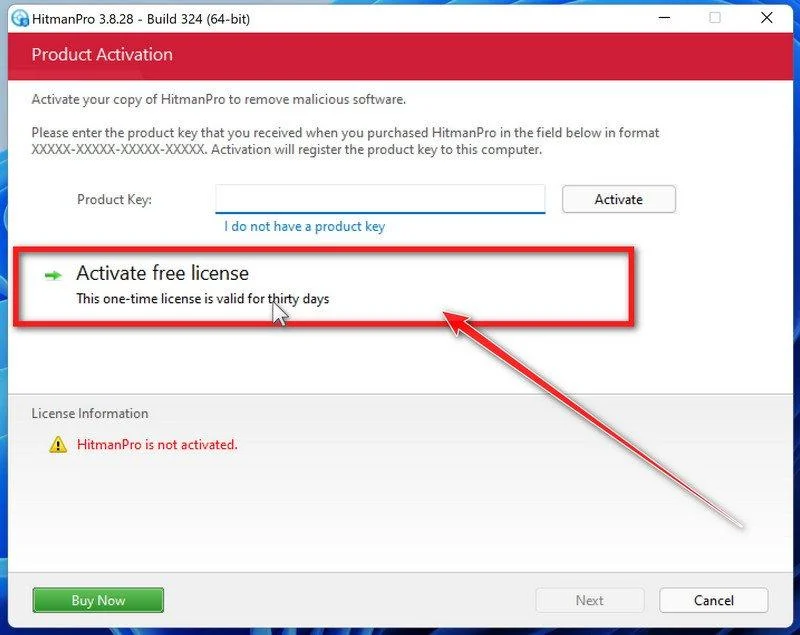
Click “Activate Free License”
To remove the malicious files, click the “Activate free license” button. This starts your free 30-day trial — no payment details needed — and unlocks the full cleanup.
When the removal is complete, HitmanPro will show a summary of everything it cleaned. Click Next, then click Reboot if prompted. If there’s no reboot prompt, just click Close — your PC is clean.
STEP 5: Use AdwCleaner to remove adware and malicious browser policies
In this final step, we will use AdwCleaner to remove the malicious browser policies that were set by browser hijackers on your computer and delete malicious browser extensions.
AdwCleaner is a free on-demand scanner that specializes in adware, browser hijackers, and unwanted toolbars — the exact threats that mainstream antivirus programs often miss. It also includes tools that repair the damage malware leaves behind, like hijacked browser settings and malicious policies. It’s a quick scan that’s well worth running.
-
Download AdwCleaner
Click the button below to download AdwCleaner — it’s free, portable, and requires no installation.
Download AdwCleanerOpens the official download page in a new tab. Malwarebytes AdwCleanerRemoves adware and unwanted programs at no cost
-
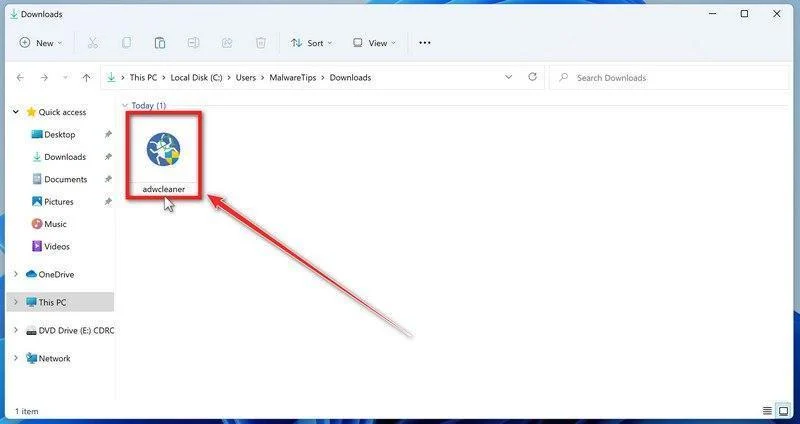
Run AdwCleaner
Open your Downloads folder and double-click the file named “adwcleaner.exe“. There’s no installation — the program starts right away.
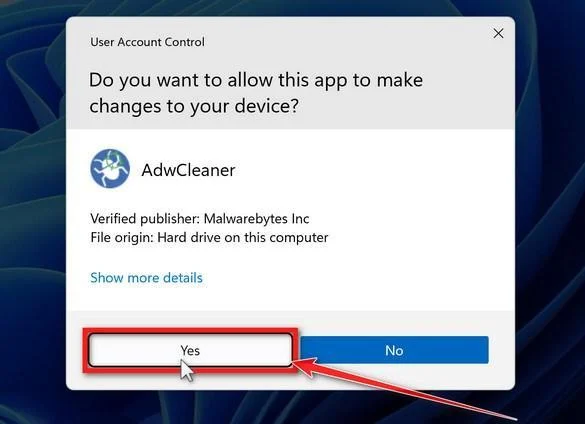
If Windows asks whether you want to allow AdwCleaner to run, click “Yes“. When the license agreement appears, click I agree to continue.
-
Enable “Reset Chrome policies”
This setting removes malicious browser policies — a trick malware uses to lock your browser settings so you can’t change them back. Click “Settings” on the left side of the window, then turn on “Reset Chrome policies“.
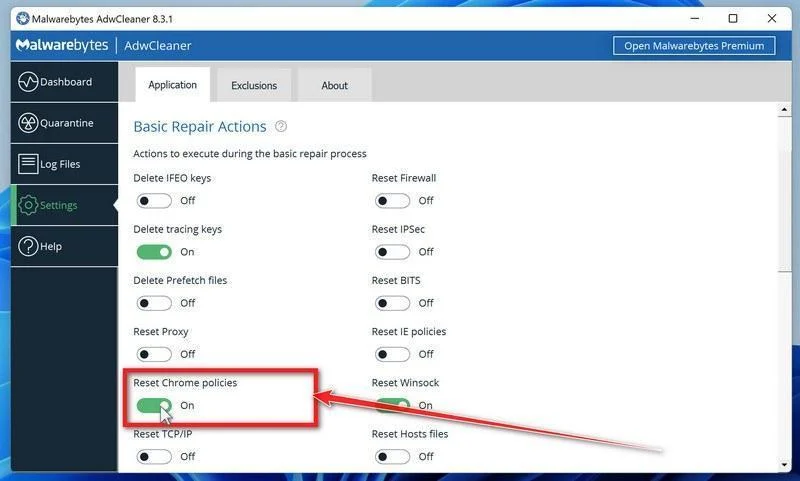
-
Start the Scan
Click “Dashboard” on the left side of the window, then click the “Scan” button.
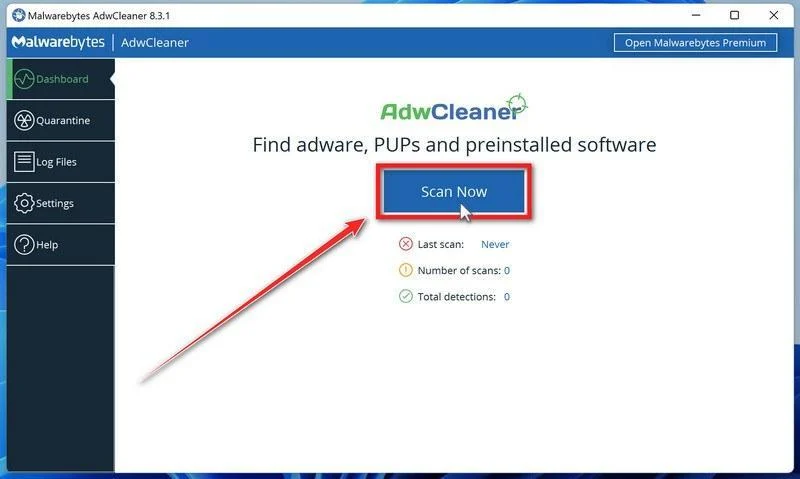
-
Wait for the Scan to Finish
AdwCleaner will now check your computer for adware and other malware. This usually takes only a few minutes — it’s one of the fastest scanners around.
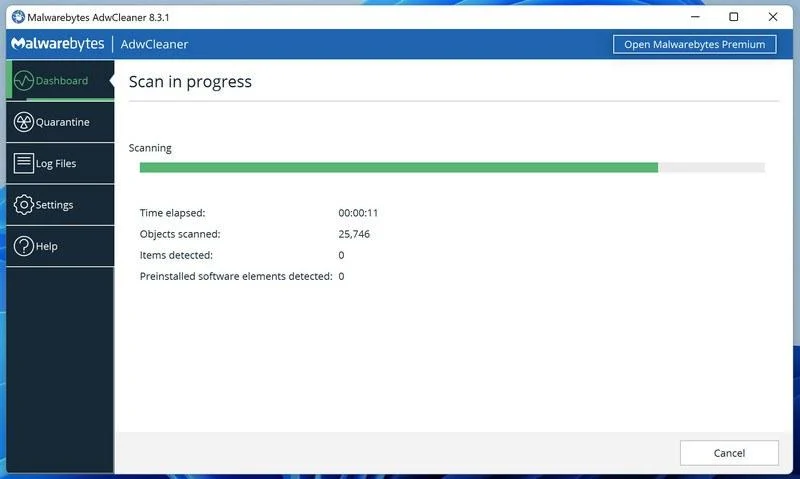
-
Quarantine the Detected Threats
When the scan finishes, AdwCleaner will list everything it found. Click the “Quarantine” button to remove all the malicious items at once.
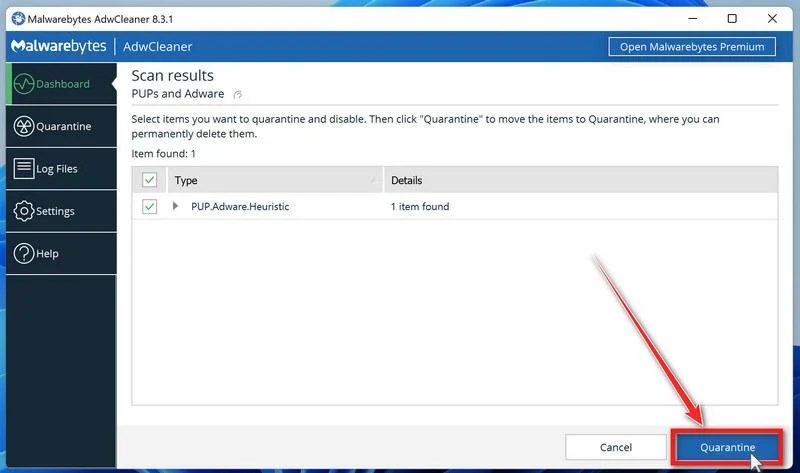
-
Click “Continue” to Finish the Cleanup
Save any open work first — AdwCleaner needs to close your open programs before it can clean. When you’re ready, click the “Continue” button.
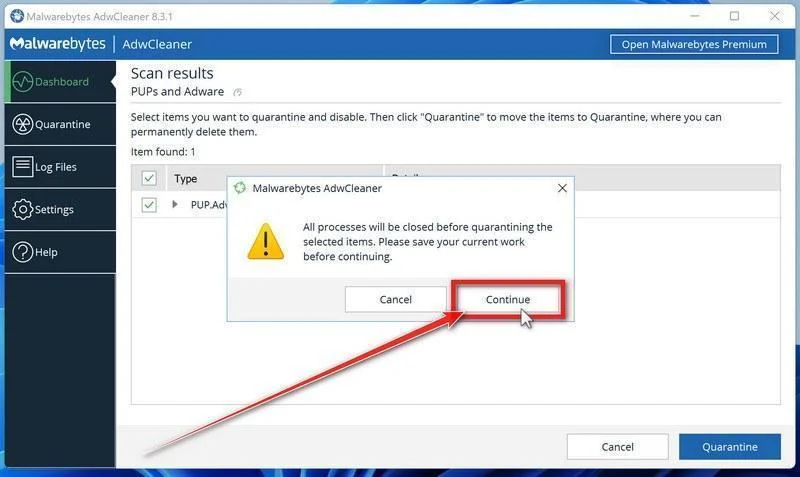
AdwCleaner will now delete all detected malware from your computer. If it asks you to restart your PC, allow it — your computer will be clean when you log back in.
That’s it — your Windows computer is now clean. The unwanted apps, adware, and any other malware have been removed.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Remove Unwanted Apps and Malware from Mac
- STEP 1: Remove malicious profiles
- STEP 2: Delete malicious apps
- STEP 3: Reset browsers back to default settings
- STEP 4: Run a scan with Malwarebytes for Mac to remove malware
STEP 1: Remove malicious profiles
Profiles are used by IT admins in businesses to control the behavior of their Macs. These profiles can configure a Mac to do many different things, some of which are not otherwise possible.
When it comes to home users, adware and browser hijackers are using the configuration profile to prevent users from removing malicious programs from the computer. This also prevents the user from changing that behavior in the browser’s settings.
In this first step, we will check your computer to see if any configuration profiles are installed. To do this, follow the below steps:
-
Open “System Settings”
From the Apple menu () in the top-left corner of the screen, select System Settings. (On macOS Monterey and earlier, this is called System Preferences.)
-
Look for “Profiles”
In the System Settings window, search for Profiles — on newer macOS versions you’ll find it under Privacy & Security, or you can type “Profiles” in the search box.
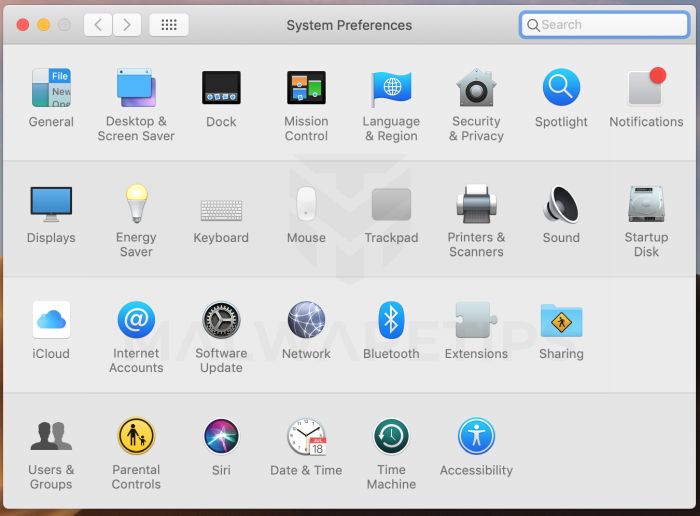 No Profiles section? Good news — that means no profiles are installed on your Mac, which is completely normal. Skip ahead to the next step of this guide.
-
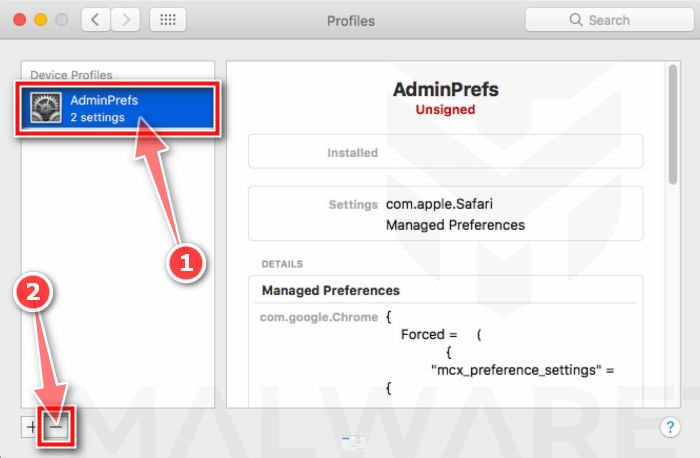
Remove the malicious profiles
Malware uses configuration profiles to lock your browser settings — forcing a fake search engine or homepage on you and preventing you from changing it back. If you see a profile you don’t recognize (and your Mac isn’t managed by your workplace or school), select it, press the − (minus) button, and click Remove to confirm.
STEP 2: Delete malicious apps
In this second step, we will try to identify and remove any malicious apps and files that might be installed on your computer. Sometimes redirects or adware programs can have usable Uninstall entries that can be used to remove these programs.
-
Quit the malicious programs
Check the Apple menu bar in the top-right corner of your screen. If you see an icon you don’t recognize, click it and select Quit. This stops the malware from running so it can’t interfere while we remove it.
-
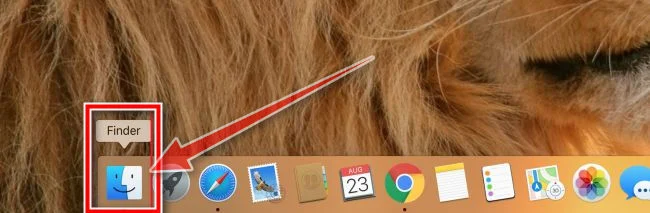
Open “Finder”
Click the Finder icon in your dock.
-
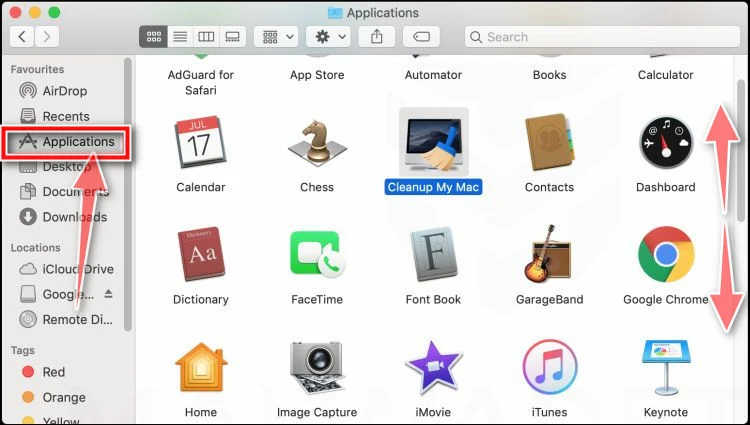
Click on “Applications”
In the Finder sidebar, click “Applications“.
-
Find and remove the malicious app
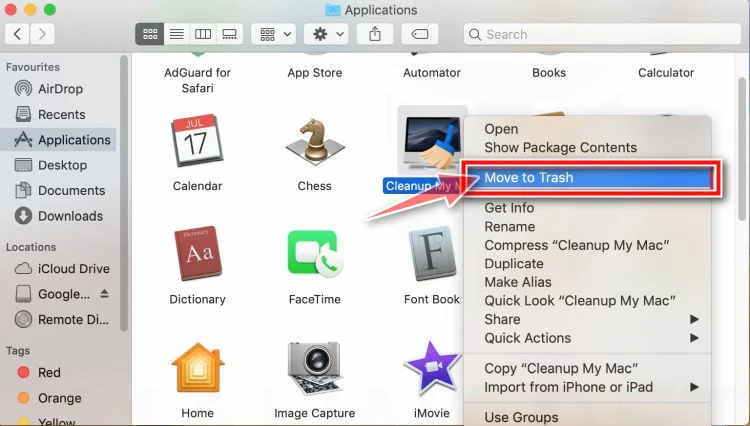
Scroll through the list of installed apps and look for anything suspicious — an app you don’t remember installing, or one with a strange or generic name. When you find it, right-click it and select “Move to Trash“.
Some known malicious programs to look for: SearchMine, TakeFresh, TopResults, FeedBack, ApplicationEvents, GeneralOpen, PowerLog, MessengerNow, ImagePrime, GeneralNetSearch, Reading Cursors, GlobalTechSearch, PDFOnline-express, See Scenic Elf, MatchKnowledge, Easy Speedtest, and WebDiscover. The names change constantly, though — so treat any app you can’t account for as suspect.
-
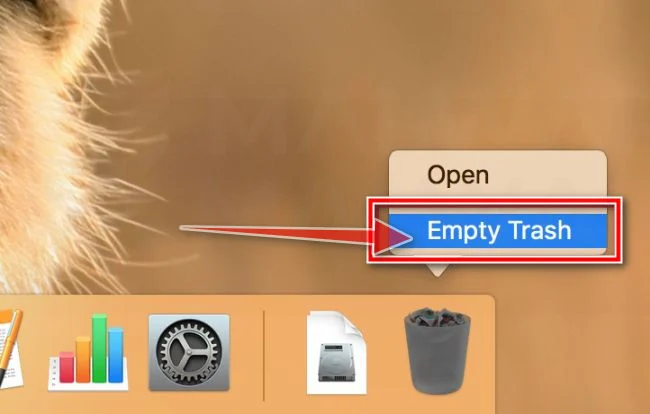
Empty the Trash
Right-click the Trash icon in your dock and select “Empty Trash“. This permanently deletes the malicious app you just removed — until you do this, the malware is still on your Mac.
Find and remove the malicious files
Malware on Mac uses launch agents and launch daemons — small files that automatically restart the malware every time you boot your Mac. We’ll check the four folders where they hide:
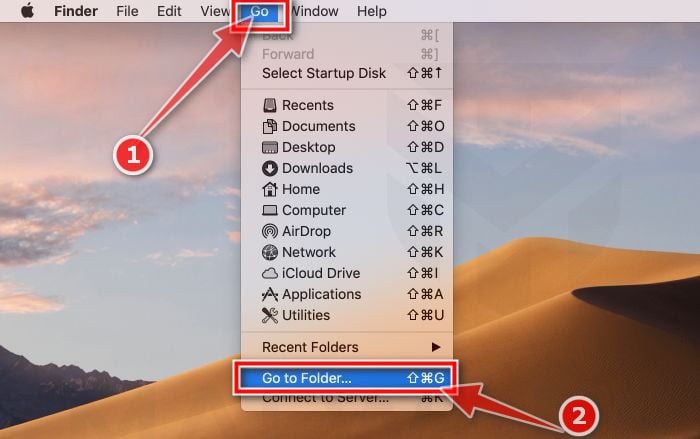
- Click the desktop to make sure you’re in Finder, then open the “Go” menu and click “Go to Folder“.
- Copy and paste each of the paths below into the window, one at a time, and click Go after each:
- /Library/LaunchAgents
- ~/Library/LaunchAgents
- /Library/Application Support
- /Library/LaunchDaemons
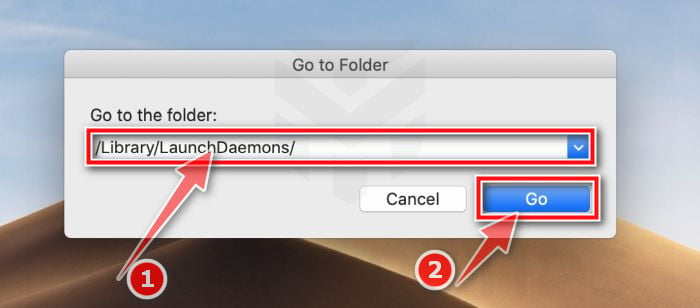
- In each folder, look for suspicious .plist files — typically named after the malware or with odd, random-looking names. Some known examples: “com.adobe.fpsaud.plist”, “installmac.AppRemoval.plist”, “myppes.download.plist”, “mykotlerino.ltvbit.plist”, and “com.myppes.net-preferences.plist”. When you find a malicious file, move it to the Trash — then empty the Trash again when you’re done.
Be careful: these folders also contain files belonging to legitimate apps — especially /Library/Application Support, where programs like Adobe, Google, and Microsoft store their data. Only delete files you’re confident are malicious. If you’re unsure about a file, search its exact name online first — or skip it; the Malwarebytes scan in the next step will catch what you miss.
- Click the desktop to make sure you’re in Finder, then open the “Go” menu and click “Go to Folder“.
STEP 3: Reset browsers back to default settings
In this third step, we will remove spam push notifications and malicious extensions, and change to default any settings that might have been changed by malware.
For each browser that you have installed on your computer, please click on the tab below and follow the displayed steps to reset that browser.
Remove malicious extensions and settings from Safari
To remove malware from Safari we will check if there are any malicious extensions installed on your browser and what settings have been changed by this malicious program.
-
Go to Safari’s “Preferences”.
On the menu bar, click the “Safari” menu and select “Preferences”.
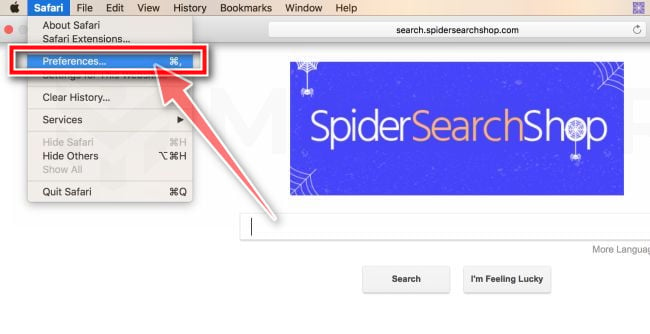
-
Check Homepage.
This will open a new window with your Safari preferences, opened to the “General” tab. Some browser hijackers may change your default homepage, so in the Homepage field make sure it’s a web page you want to use as your start-up page.
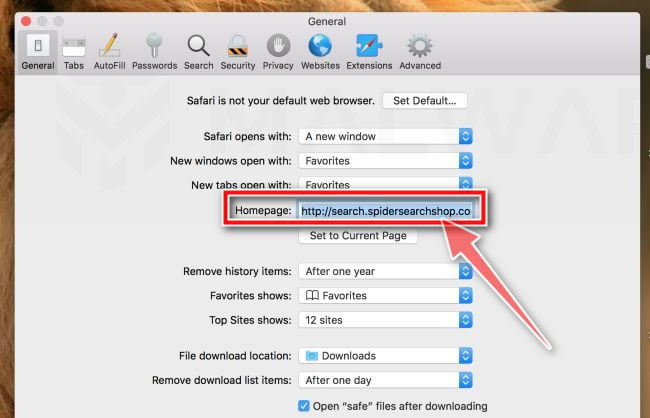
-
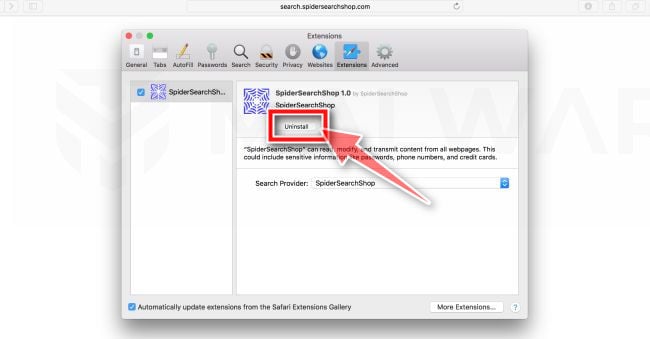
Click “Extensions”
Next, click on the “Extensions” tab.
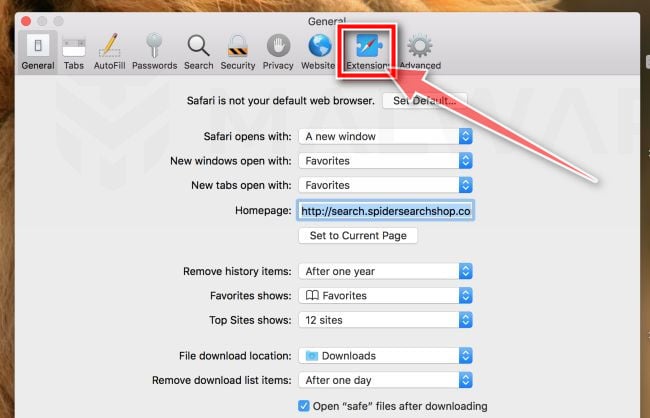
-
Find and uninstall malicious extensions.
The “Extensions” screen will be displayed with a list of all the extensions installed on Safari. Look out for any suspicious browser extension that could be behind all the drama – anything you don’t remember downloading or that doesn’t sound like a genuine extension. By default, there are no extensions installed on Safari so it’s safe to remove an extension
-
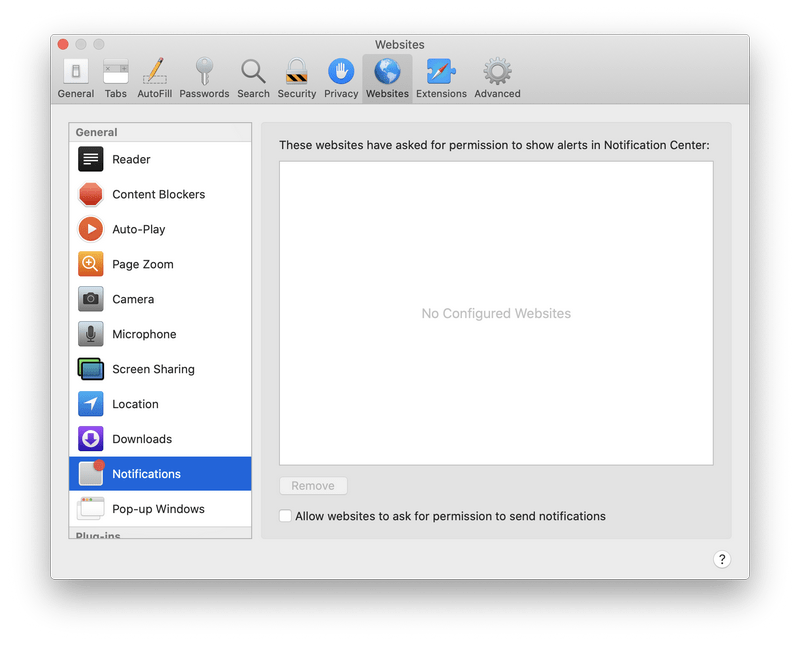
Remove spam notifications ads
Click Preferences, click Websites, then click Notifications. Deselect “Allow websites to ask for permission to send push notifications”.
-
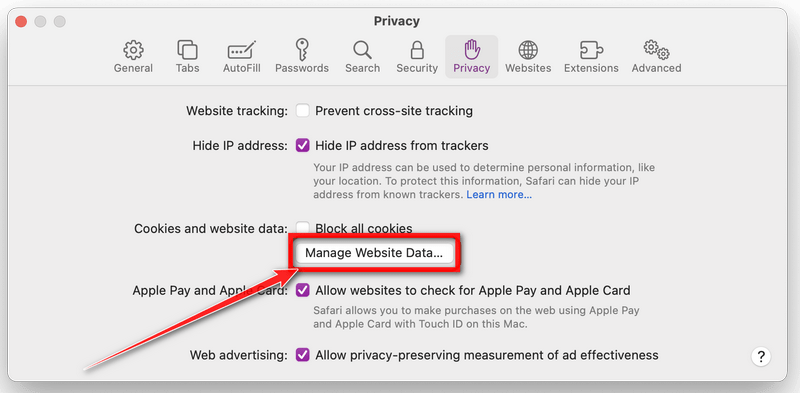
Remove all data stored by websites on your computer.
In the Safari menu, choose “Preferences…”, select “Privacy” at the top of the new window that appears, and then click the “Manage Website Data” button.
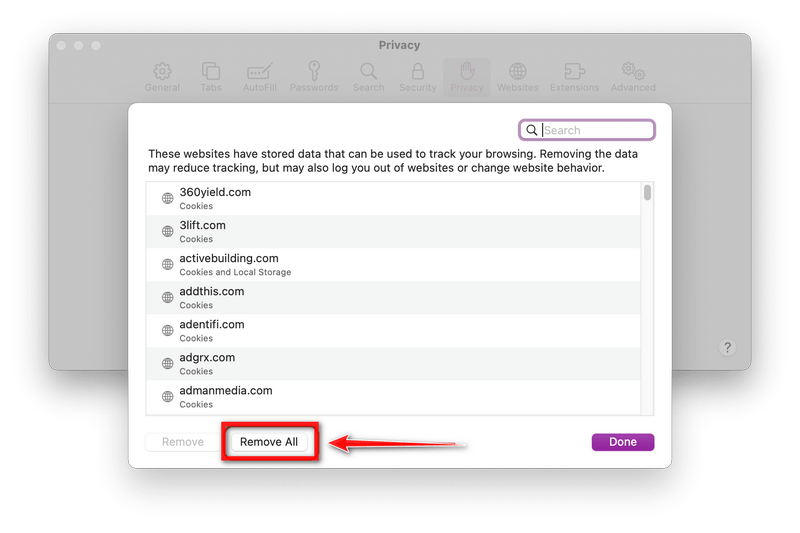
In the next dialog box, click “Remove All“. It will ask you if you are sure you want to remove all data stored by websites on your computer. Select “Remove Now” to clear data that could be used to track your browsing.
-
Empty Safari Caches.
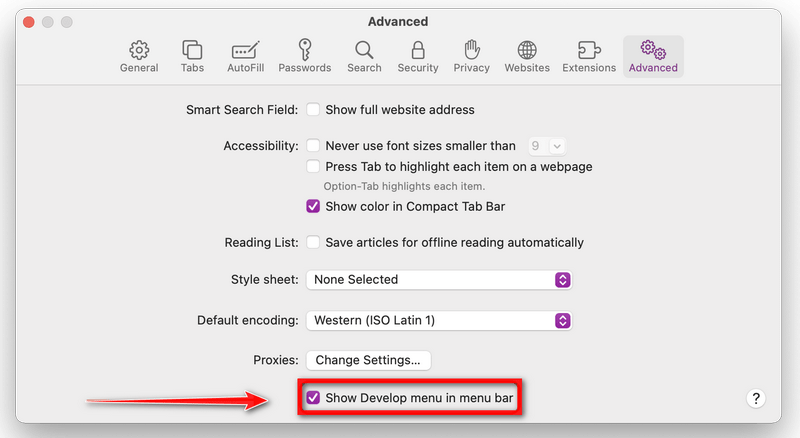
From your Safari menu bar, click Safari and select Preferences, then select the Advanced tab. Enable the checkbox to “Show Develop menu in menu bar“.
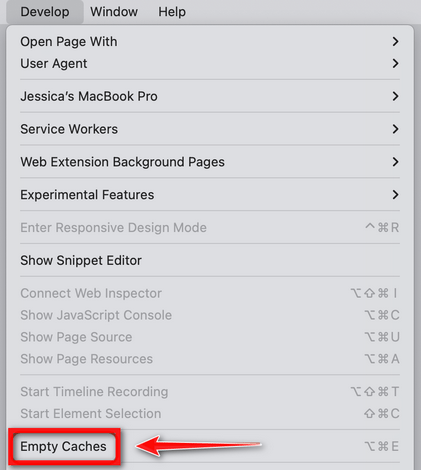
From the menu bar select Develop, then click on Empty Caches as seen in the image below.
Remove malware from Chrome for Mac
To remove malware from Chrome for Mac we will reset the browser settings to their default. Doing these steps will erase all configuration information from Chrome such as your home page, tab settings, saved form information, browsing history, and cookies. This process will also disable any installed extensions. All of your bookmarks, though, will be preserved.
-
Click on the three dots at the top right and go to Settings.
Click on Chrome’s main menu button, represented by three dots at the top right corner. Now click on the menu option labeled Settings as shown by the arrow in the picture below, which will open the basic settings screen.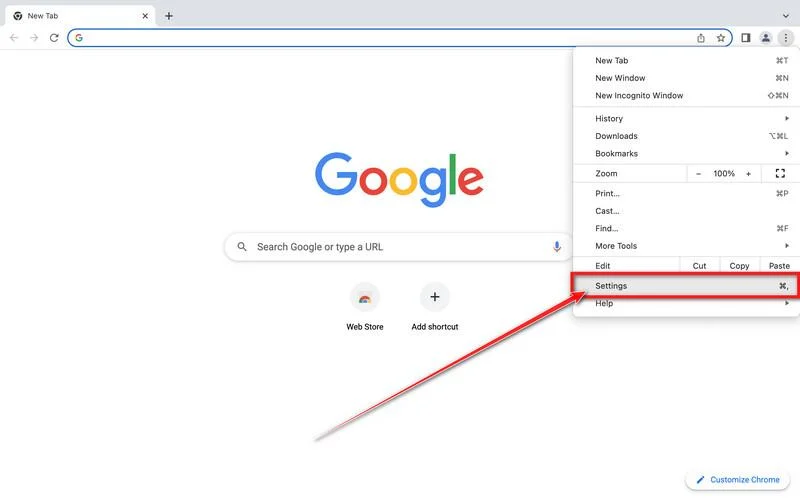
-
In the left sidebar, click on the “Reset and Cleanup” option.
In the left sidebar, click on “Reset and clean up“.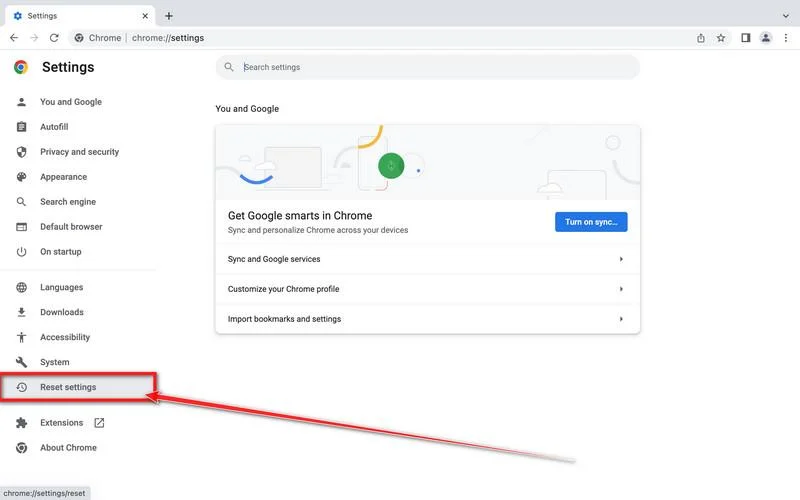
-
Click “Reset settings to their original defaults”.
Now click on the “Reset settings to their original defaults”. link as shown in the image below.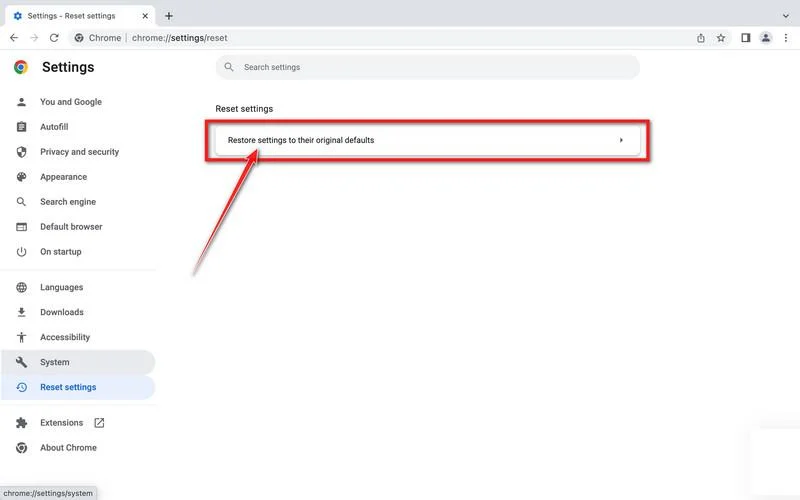
-
Click “Reset Settings” button.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, click on the “Reset Settings” button.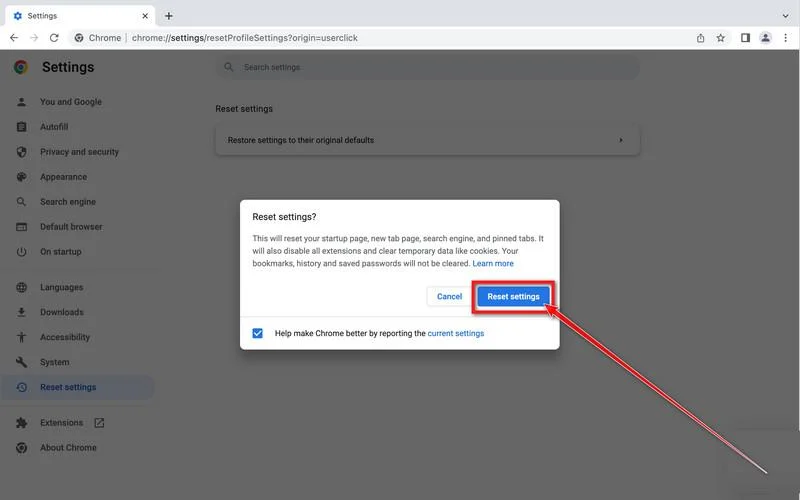
-
(Optional) Reset Chrome Data Sync.
In case a malicious extension reinstalls itself even after performing a browser reset, you have an additional option to reset the data sync for your browser. To do this, navigate to chrome.google.com/sync and click on the Clear Data button.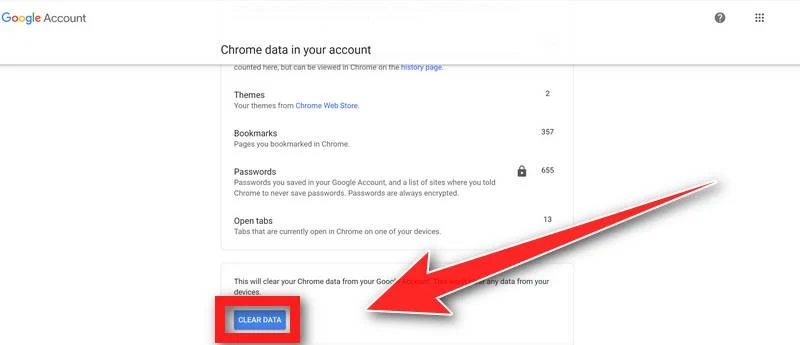
Remove malware from Firefox for Mac
To remove malware from Firefox for Mac we will reset the browser settings to its default. The reset feature fixes many issues by restoring Firefox to its factory default state while saving your essential information like bookmarks, passwords, web form auto-fill information, browsing history, and open tabs.
-
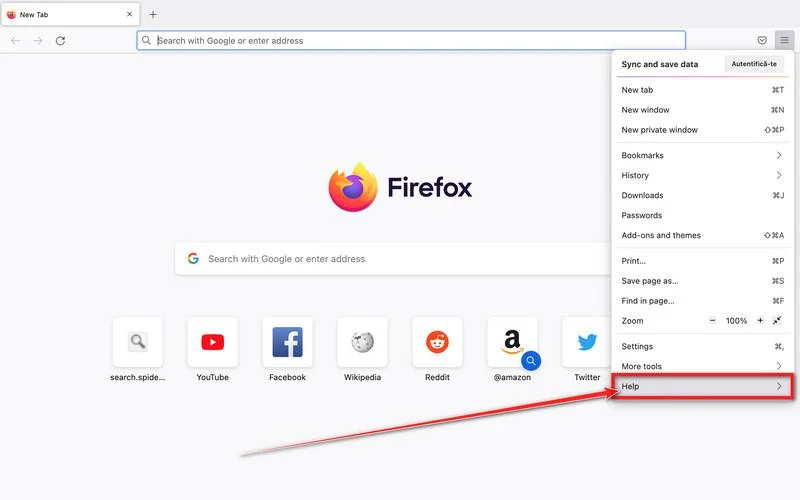
Go to the “Help” menu.
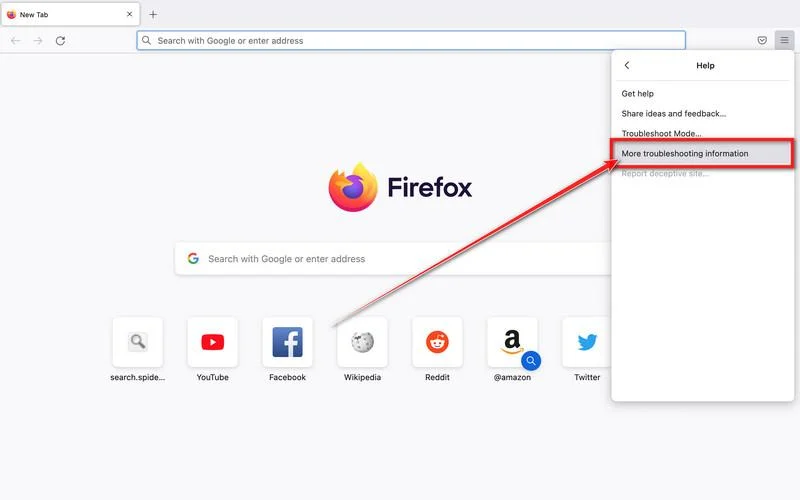
Click on Firefox’s main menu button, represented by three horizontal lines. When the drop-down menu appears, select the option labeled “Help“.
-
Click “Troubleshooting Information”.
Next click on the “Troubleshooting Information” option as indicated by the arrow in the image below. This will bring you to a Troubleshooting page.
-
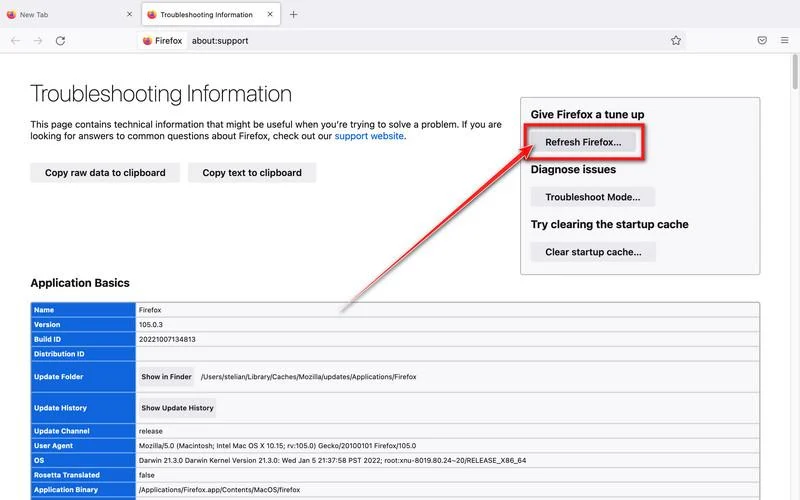
Click on “Refresh Firefox”
Click the “Refresh Firefox” button in the upper-right corner of the “Troubleshooting Information” page.
-
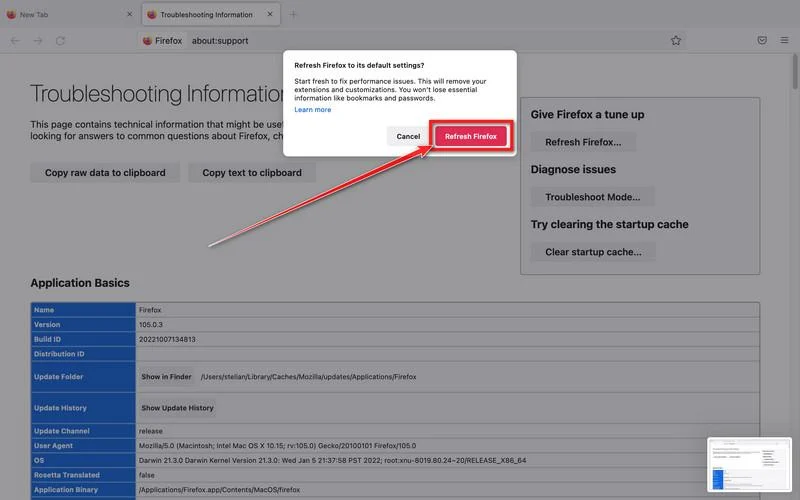
Confirm.
To continue, click on the “Refresh Firefox” button in the new confirmation window that opens.
-
Click on “Finish”.
Firefox will close itself and will revert to its default settings. When it’s done, a window will list the information that was imported. Click on the “Finish“.
STEP 4: Run a scan with Malwarebytes for Mac to remove malware
In this final step, we will scan the computer with Malwarebytes for Mac to find and remove any malicious programs that might be installed on your Mac.
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now clean. The unwanted apps, adware, and any other malware have been removed.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Remove Unwanted Apps and Malware from Android
- STEP 1: Uninstall malicious apps
- STEP 2: Reset browsers back to default settings
- STEP 3: Use Malwarebytes for Android to remove malicious apps
STEP 1: Uninstall malicious apps
In this first step, we will check if any malicious apps are installed on your phone. Sometimes browser hijackers or adware apps can have usable Uninstall entries that can be used to remove these apps.
-
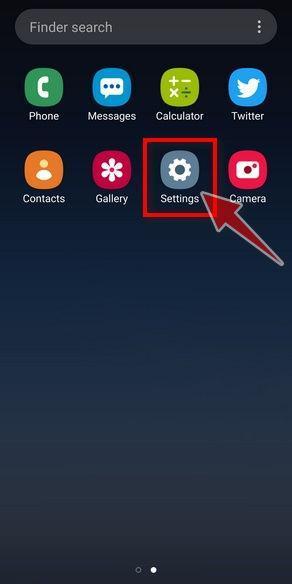
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
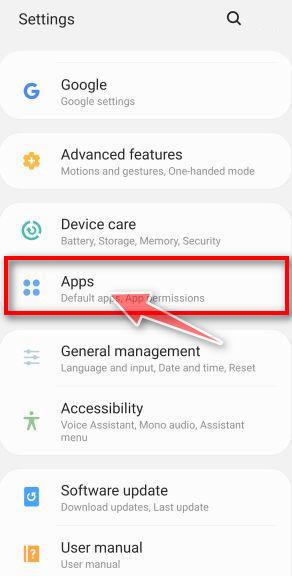
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find the malicious app.
The “Apps” screen will be displayed with a list of all the applications that are installed on your phone. Scroll through the list and look out for any suspicious app that could be behind all the drama – anything you don’t remember downloading or that doesn’t sound like a genuine program.
Most often, cyber criminals hide malware inside video or photo editing apps, weather apps, and camera apps.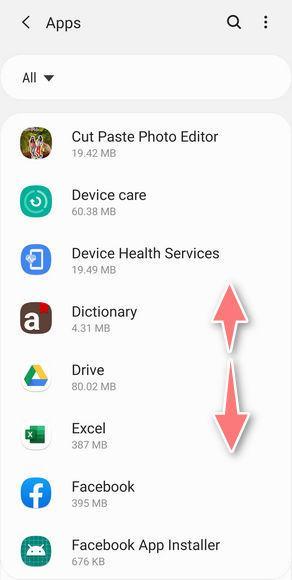
-
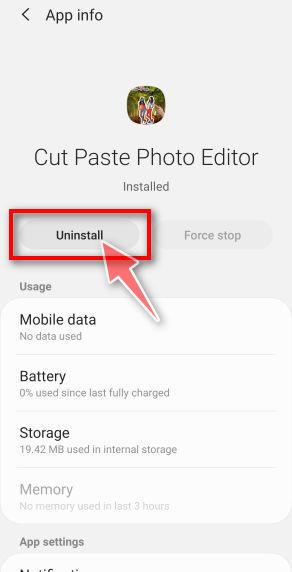
Uninstall the malicious app
When you find a suspicious or malicious app, tap on it to uninstall it. This won’t start the app but will open up the app details screen. If the app is currently running press the “Force stop” button, then tap on “Uninstall”.
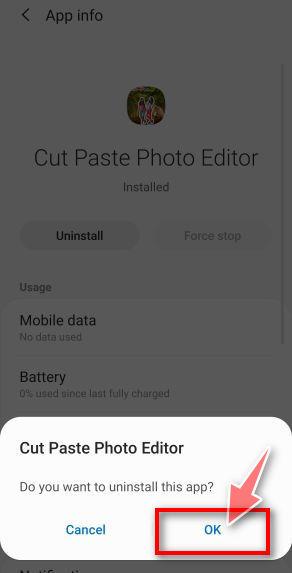
A confirmation dialog should be displayed to confirm you want to uninstall the app, tap on “OK” to remove the malicious app from your phone.
STEP 2: Reset browsers back to default settings
In this second step, we will reset your browser to its default settings to remove spam notifications, unwated search redirects, and restore its factory settings
Resetting the browser settings to their default it’s an easy task on Windows or Mac computers; however, when it comes to Android, this can’t be done directly because it’s not an option built-in into the browser settings. Restoring the browser settings on Android can be done by clearing the application data. This will remove all the cookies, cache, and other site settings that may have been saved. So let’s see how we can restore your browser to its factory settings.
Remove malware from Chrome for Android
To reset Chrome for Android to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
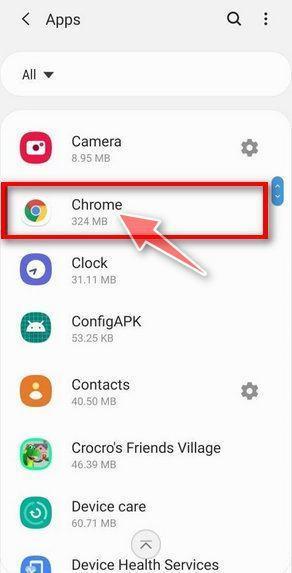
Find and tap on Chrome.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Chrome app, then tap on it to open the app’s details.
-
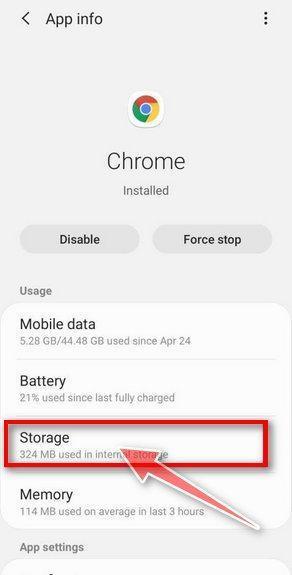
Tap “Storage”.
When Chrome’s app info menu is displayed, tap on “Storage“.
-
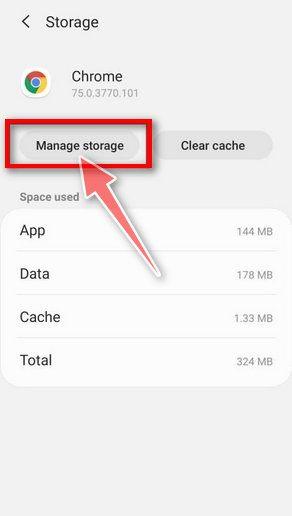
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
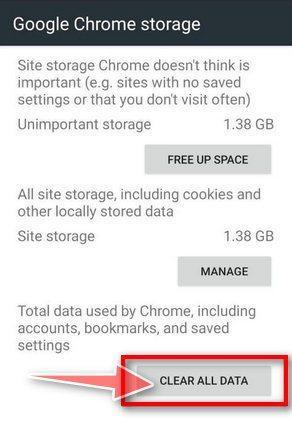
Tap “Clear all data”.
Tap “Clear all data” to delete all Chrome’s data including accounts, bookmarks, and your settings to reset the default settings.
-
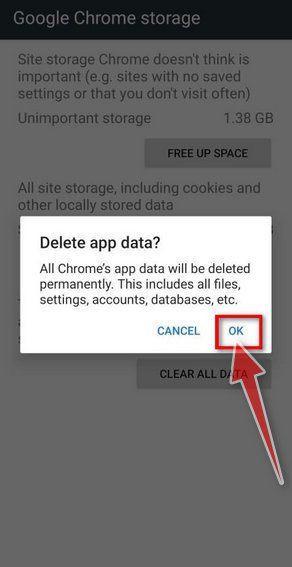
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from Firefox for Android
To reset Firefox for Android to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Firefox.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Firefox app, then tap on it to open the app’s details.
-
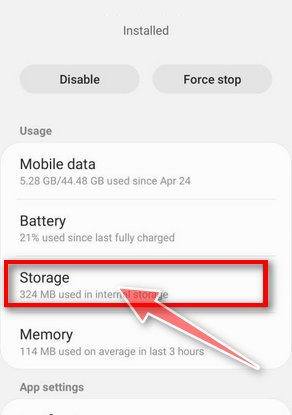
Tap “Storage”.
When Firefox’s app info menu is displayed, tap on “Storage“.
-
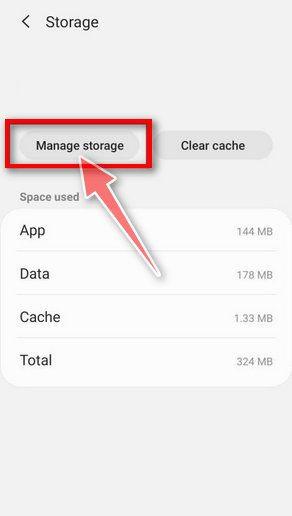
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
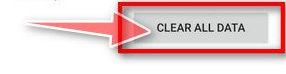
Tap “Clear all data”.
Tap “Clear all data” to delete all Firefox data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from the Opera browser
To reset the Opera browser to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Opera.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Opera app, then tap on it to open the app’s details.
-
Tap “Storage”.
When Opera’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
Tap “Clear all data”.
Tap “Clear all data” to delete all Opera’s data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from Samsung Internet Browser
To reset the Samsung Internet Browser to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Samsung Internet Browser.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Samsung Internet Browser app, then tap on it to open the app’s details.
-
Tap “Storage”.
When the Samsung Internet Browser’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
Tap “Clear all data”.
Tap “Clear all data” to delete all Samsung Internet Browser’s data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
Remove malware from Microsoft Edge for Android
To reset the Microsoft Edge for Android to its default settings, follow the below steps:
-
Open the “Settings” menu.
Tap on the “Settings” app from your phone menu or home screen.
-
Tap on “Apps”.
When the “Settings” menu opens, tap on “Apps” (or “App Manager”) to see all the installed applications on your phone.
-
Find and tap on Microsoft Edge.
The “Apps” screen will be displayed with a list of all the apps installed on your phone. Scroll through the list until you find the Microsoft Edge app, then tap on it to open the app’s details.
-
Tap “Storage”.
When the Microsoft Edge’s app info menu is displayed, tap on “Storage“.
-
Tap “Manage Space”.
Under the storage settings, you will get two options — Manage Space and Clear Cache. Tap on “Manage Space“.
-
Tap “Clear all data”.
Tap “Clear all data” to delete all Microsoft Edge’s data including accounts, bookmarks, and your settings to reset the default settings.
-
Confirm by tapping “Ok”.
A confirmation dialog should now be displayed, detailing the components that will be restored to their default state should you continue with the reset process. To complete the restoration process, tap “Ok“.
STEP 3: Use Malwarebytes for Android to remove malicious apps
In this final step, we will install Malwarebytes for Android to scan and remove malicious apps from your phone or tablet.
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android device is now clean. The malicious apps, adware, and browser redirects have been removed.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Remove Unwanted Apps and Malware from iPhone and iPad
STEP 1: Clean your browser
First, we’ll clean Safari using the built-in “Clear History and Website Data” feature. This removes your browsing history, cookies, and cached data — including the stored data that scam sites use to keep showing you pop-ups and redirects. Don’t worry: this won’t delete your photos, apps, or saved passwords.
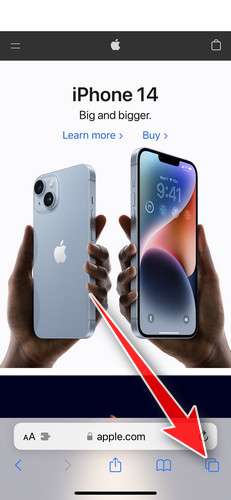
- Don’t tap anything inside the scam page or pop-up — the buttons are designed to trick you. Instead, tap the tabs icon in the lower-right corner of Safari, as shown below.
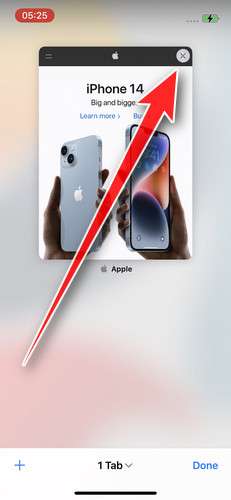
- Tap the X on the malicious tab (or swipe it up) to close it safely.
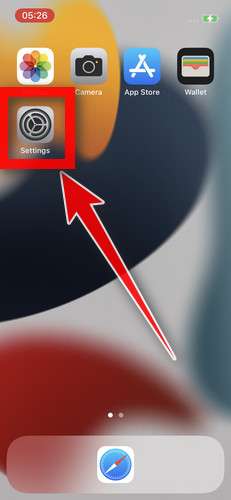
- Open the Settings app.
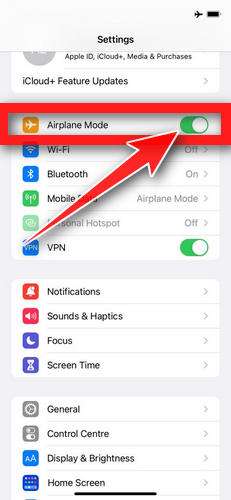
- Turn on Airplane Mode. This temporarily disconnects your iPhone from the internet, so the scam site can’t load anything while we clean up. We’ll turn it back off at the end.
- Scroll down and tap Safari.
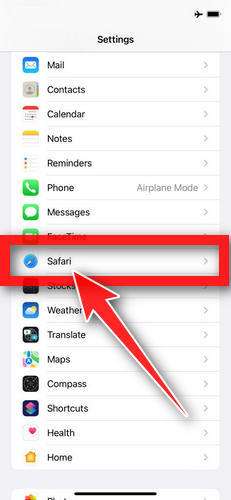
- Tap Clear History and Website Data.
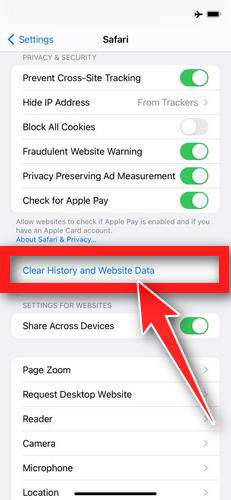
- Confirm by tapping “Clear History and Data” in the pop-up.
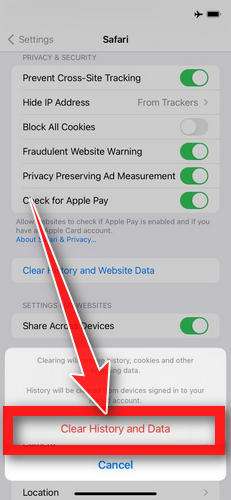
- While you’re still in Safari settings, turn on Block Pop-ups and Fraudulent Website Warning. These two switches stop most scam pages before they can even load.
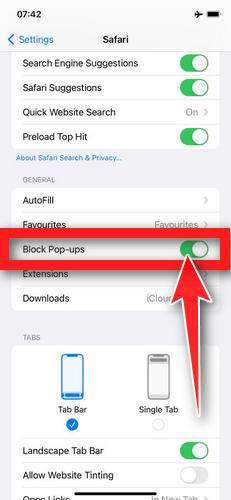
- Tap Settings in the upper-left corner to return to the main Settings menu.
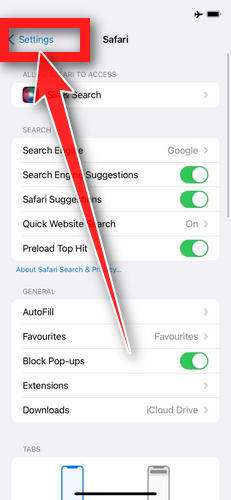
- Turn Airplane Mode back off to reconnect your iPhone to the internet.
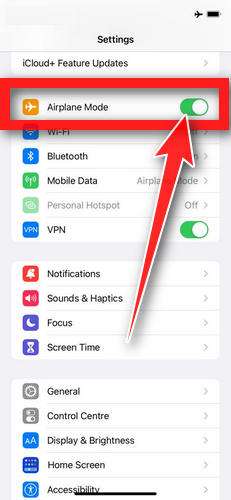
STEP 2: Delete unwanted apps
Next, we’ll remove any suspicious apps from your iPhone. If a shady website redirected you to the App Store and you installed an app — or you spot an app you don’t remember downloading — delete it now:
-
On the home screen, tap and hold the unwanted app’s icon until the icons start to wiggle.
-
Tap the minus (–) badge in the corner of the app icon, then tap Delete App. (On older iOS versions, this badge appears as an “X”.)
-
Confirm by tapping “Delete“.
That’s it — your iPhone is now clean and safe to use.
To stop these scam pages from coming back, we recommend installing an ad blocker like AdGuard. It blocks the malicious ads and redirects that cause these pop-ups in the first place.
Still having issues after completing these steps? Try one of the following:
- Run a scan with Malwarebytes for iOS
- Ask for help in our free Mobile Malware Removal Help & Support forum — our team will assist you personally.
That’s it — your iPhone or iPad is now clean.
FAQ
What is the Robux giveaway scam in 2026?
It’s a rotating set of fake “event” or “giveaway” pages that promise free Robux, then push you into steps that earn money for scammers or put your account at risk. The packaging changes (milestone events, “claim now” pages, Discord “event servers”), but the outcome is the same: no real Robux payout.
Are any websites giving away free Robux legitimately?
No. Roblox explicitly states that any offer of free Robux, memberships, or valuable items is a scam, and that there is no such thing as a Robux generator.
Why do these scam sites ask for my Roblox username first?
Because it feels “safe” and makes you emotionally commit. After you type your username, the page can show your avatar, run fake “connecting” animations, and steer you into the real trap: tasks, downloads, or Discord “verification.”
What is the most common 2026 tactic?
The “username then task” funnel:
- Enter username
- Pick a Robux amount
- Watch fake progress bars
- “Complete a quick task to verify”
Those tasks are usually offerwalls (app installs, surveys, trials) that generate affiliate revenue for scammers.
Why do they keep saying “human verification required”?
It’s a profit step disguised as safety. “Verification” typically means you’re being routed into offers, data collection, or paid trials. Roblox does not require third-party verification tasks to receive Robux.
Can these “verification” steps cost real money?
Yes. Some offers include “free trials” that convert into paid subscriptions or require payment details upfront. If a child used a card, review statements quickly and cancel any unwanted subscriptions as soon as possible.
I saw the link in Roblox chat. Does that matter?
Yes. Spam in public Roblox servers is a major red flag. Legitimate promotions don’t need bot-like chat flooding to reach players. If the link came from repeated chat spam, treat it as unsafe.
Why are Discord “Robux giveaway” servers so common now?
Because Discord lets scammers apply pressure in real time using fake staff roles, ticket bots, and “support” scripts. Discord warns users not to scan QR codes from people they can’t verify and flags QR login requests from strangers as possible phishing attempts.
What is the Discord QR code scam and how does it connect to Robux giveaways?
Some fake giveaway servers ask you to scan a QR code to “verify” or “claim.” That can hand your Discord session to the attacker. Discord explicitly warns that if someone you don’t know asks you to log in using a QR code, it may be phishing.
If a site never asked for my Roblox password, can I still be harmed?
Yes. You can still be pushed into:
- Paid trials and subscriptions
- Data harvesting (email, phone, profile info)
- Notification spam
- Risky downloads or extensions
Also, some funnels start with username-only and later pivot into a fake Roblox login page.
I entered my Roblox password on a “giveaway” page. What should I do right now?
Act immediately:
- Change your Roblox password
- Change the password on the email linked to Roblox
- Enable 2-step verification
- Review trades, purchase history, and security settings
Roblox’s guidance is clear that these scams aim to take accounts, Robux, and items.
What’s the safest way to get Robux?
Only through official Roblox methods. Roblox also warns that “Robux generators” are scams and should be reported
The Bottom Line
The Robux giveaway scam 2026 tactics are louder, cleaner, and more social than older scams, but the heart of the con is unchanged.
Scammers promise free Robux. They ask for your username to make it feel real. Then they push you into tasks, subscriptions, spam, or Discord “verification” traps that generate money or access for the scammers.
Roblox’s own guidance is clear: offers of free Robux and similar rewards are scams.
There is no giveaway. There is no generator. There is no hack.
If a site promises free Robux, the safest move is to close it immediately, report the spam, and protect your account with 2-step verification.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.