

A group wants a safari, the itinerary looks promising, and the inquiry could be worth several thousand. Your email says you have only days to respond.
For a tour operator, that sounds like work worth prioritizing. Before opening the full request, check which service is actually asking you to sign in.
Overview
A valuable inquiry is the bait for the operator
The SafariBookings quote request email scam imitates a travel-business notification. It asks an operator to review an apparent lead before the opportunity goes elsewhere.
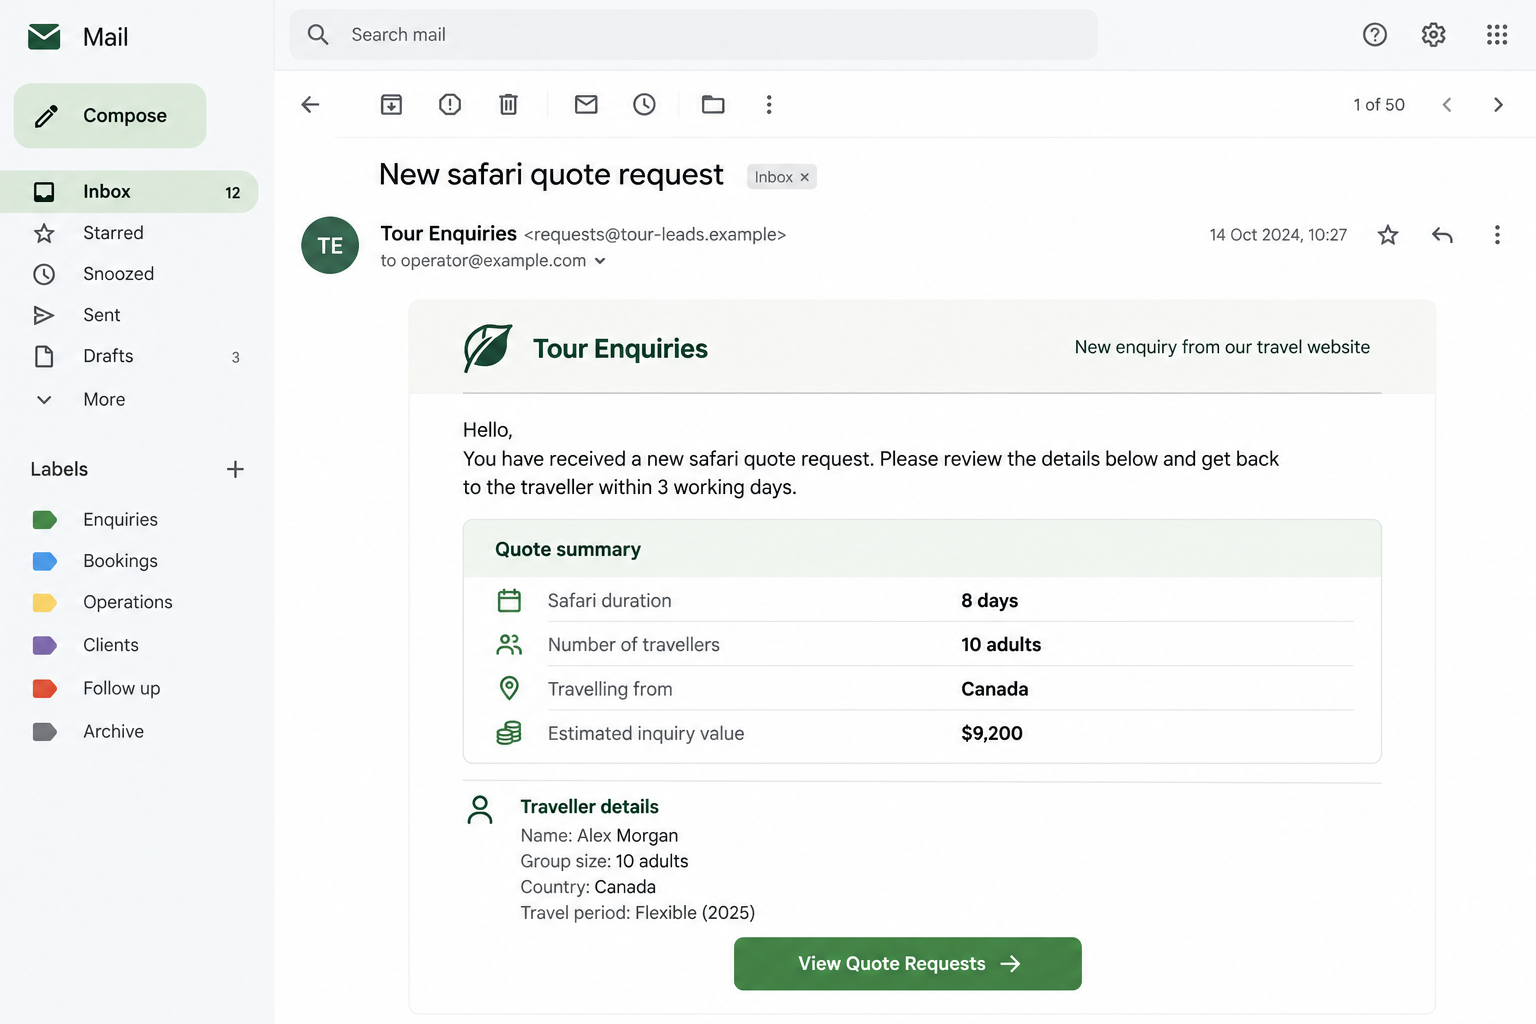
One version advertises an eight-day safari for ten adults from Canada, with a supposed inquiry value of $9,200 or €9,000.
Those are figures printed in the message, not a confirmed booking or currency conversion. The recipient has not received payment simply because the email displays an estimated value.
The request opens a false document-login page
The reported view-request link leads to a document-looking page asking for an email address and password. The goal is collecting credentials rather than arranging a safari.
SafariBookings is a legitimate platform. The fake notification does not establish that it or a real traveler is responsible for the phishing page.
The image uses fictional contact details to illustrate the lure. No original customer, trip, mailbox submission, or completed account takeover was verified for this article.
How to check without abandoning a genuine lead
- Open the real Tour Operator Admin independently and look for the inquiry there.
- Do not give your mailbox password to a page that merely displays a travel document.
- Check the complete hostname rather than trusting a familiar platform name in the design.
- Ask genuine platform support about a doubtful request through its established channels.
- Separate a disappointing inquiry from a proven impersonation or password trap.
SafariBookings’ own phishing advice says its staff will not ask for your password. A professional-looking quote notice does not override that warning.
Why Tour Businesses Are Attractive Targets
Responding quickly is part of running a successful travel business. An operator may be comparing dates, checking rooms, and preparing options while managing several inquiries at once.
A large group can make one message stand out from the rest. Even an estimated value may suggest that the lead deserves immediate attention.
The scam exploits that commercial instinct. It presents a password request inside a task that appears connected to earning revenue.
There is also a plausible reason for paperwork. Tour itineraries, guest details, and booking documents are ordinary parts of the business.
But a plausible business context does not explain why an unrelated website should receive the password to your email account.
The right question is not whether group safaris exist. It is whether this request appears in the genuine service and whether the proposed sign-in belongs there.
You can answer that question without rejecting every unfamiliar traveler. Verify the communication route, then handle any real inquiry through your normal process.
How the SafariBookings Quote Request Email Scam Works
Step 1: A detailed travel request attracts attention
The message resembles a notification from a service an operator might use to find customers. A traveler profile and trip summary make it feel like a specific opportunity.
Details such as party size, duration, and country help the reader picture the work. That can shift attention toward availability and pricing before the sender is checked.
A name in the message does not identify the person operating the scam. It may be invented or copied from somewhere else.
Do not investigate by sending the supposed traveler sensitive material. First establish whether the inquiry exists through the platform that allegedly delivered it.
If the message reaches a shared reservations inbox, tell colleagues it is unverified. Otherwise, another team member may continue while you are still checking.
Use the trip details to search genuine business records, not as proof that the email came from the platform.
Step 2: A response deadline adds competitive pressure
The original reported lure gives the operator three working days to accept or decline. It says another vendor will receive the request if no action is taken.
That is a different pressure from a threatened account closure. The fear is losing a customer to someone who replies faster.
For a small business, missing a valuable group can feel costly. A brief login may then seem like a reasonable way to protect the opportunity.
Pause before accepting the email’s timetable as an authenticated platform rule. A deadline printed by an impostor does not bind your business.
If a genuine inquiry has a response requirement, the real operator account or verified support should help establish it.
Do not let the prospect of losing a lead make you bypass the checks you would use for any other account-access request.
Step 3: The quote button changes the destination
A view-requests button promises access to travel details. In the reported flow, it instead opens a deceptive page with a document-style background.
The visitor may assume that the document is protected and needs authentication. A familiar login layout can make the interruption seem routine.
Look at the address before typing. A travel-service label inside a page is not the same as being on that service’s authenticated website.
A related host was reported as usc1.contabostorage[.]com. That is shared storage infrastructure, not proof that every object or customer using that provider is malicious.
The complete destination matters. A hosting provider’s name cannot tell you who uploaded a particular document-looking page or whether your request belongs there.
You do not need to open other files on that host to find out. Leave the link and check your real operator account independently.
Step 4: A document excuse collects the wrong password
The fake page requests an email address and password to reveal a document. That is where the sales opportunity becomes an account-security problem.
Your email address may reasonably appear on business correspondence. The password controlling that mailbox should not be supplied to a stranger’s document form.
A prefilled address would not establish that your provider recognized you. A website can display information included in the link or supplied earlier.
If the form rejects the password, stop rather than trying alternatives. A failed-looking result does not establish that the information was never received.
Keep track of which credential you actually entered. An operator-platform password and a business-mailbox password may require different recovery steps.
If you reuse the same secret across both, treat both as exposed. Do not assume fixing the travel account automatically secures the inbox.
Step 5: Business correspondence can become the next target
If the attacker gains mailbox access, they may see guest conversations, supplier messages, itineraries, and payment-related correspondence.
Those records could support later impersonation, including messages that appear to continue a genuine booking discussion. That is a possible consequence, not a confirmed outcome for every recipient.
The damage may therefore extend beyond the missing quote. A trusted business address can make a fraudulent request more believable to existing customers.
Review actual account activity and relevant messages rather than assuming every reservation was affected. The response should follow evidence of access and changes.
If suspicious payment instructions were sent, involve the person responsible for finance and warn the affected parties through independently verified contacts.
Instead, use the real operator account to check the lead. If you entered a password, focus on securing that account before answering more messages.
SafariBookings Provides a Better Way to Verify the Request
Check the operator account, not the email’s document
The platform’s phishing guidance tells operators to verify requests in the Tour Operator Admin.
It identifies operators.safaribookings.com as the genuine operator-admin hostname. Open the established service yourself rather than following the suspicious button.
Read the hostname as an address, not a phrase to find somewhere in a long URL. A familiar name can also appear in an unrelated path.
If you cannot locate the request, ask platform support using independently obtained contact details. Do not make the unknown document page the authority on your account.
Recognize that legitimate leads do not always become bookings
SafariBookings also explains how operators can assess genuine quote requests. A traveler who stops replying is not automatically a scammer.
People compare options, change plans, or choose a different operator. Those ordinary outcomes should not be confused with an imitation page stealing a password.
This distinction protects useful business relationships. The problem here is the deceptive notification and credential request, not the existence of an inquiry that may never convert.
Do not authenticate one brand by recognizing another
Some related messages use SafariOffice-themed notifications. Recognizing software your business uses does not establish who sent a particular email.
Check the relevant application through your existing route. A copied footer or company address cannot replace that check.
Do not accuse a genuine platform, employee, or traveler because their details appear in a fraudulent message. Describe the impersonation precisely when reporting it.
Keep a Real Customer Conversation From Being Hijacked
If your mailbox was exposed, consider which active bookings involved payment discussions or documents. Those deserve priority when reviewing possible misuse.
Look for unexpected sent messages, forwarding rules, recovery changes, and conversations you do not remember starting. Ask your administrator for help with the account’s available records.
A password replacement may stop some access, but unauthorized settings can need separate attention. Do not assume the work is finished after changing one field.
If a guest received suspicious instructions, contact them through a known number or an independently confirmed channel. Do not rely on the potentially compromised thread alone.
Explain the particular concern without sending unnecessary passport details, full itineraries, or other customer information to everyone on a mailing list.
Keep copies of relevant instructions and transaction references for investigation. Avoid overwriting original correspondence while trying to tidy the inbox.
You do not need to cancel every trip because one phishing notice arrived. Protect actual affected access while preserving legitimate work.
What to Do if You Have Fallen Victim to This Scam
Stop using the false quote page. Do not enter more credentials or install a document viewer to make the inquiry appear.
Save the original notice and tell anyone handling the shared inbox that the request has not been authenticated.
Secure the account whose password you supplied. Reach the actual mail provider or operator platform independently and use its recovery process.
Choose a new, unique password. If the old one also protected another business service, replace it there through that service’s genuine controls.
Review unauthorized access and settings. Check available session history, recovery contacts, forwarding, and connected applications with your administrator.
Enable the account’s supported additional authentication. Reject unexpected approval requests and do not give codes to someone discussing the missing tour inquiry.
Ask genuine SafariBookings support to verify the lead. Follow its published advice and explain whether the platform password, mailbox password, or both were disclosed.
Do not assume one support team can secure every account you used. Keep the travel-platform response separate from email-provider recovery.
Check relevant guest and supplier communications. Prioritize payment details and messages sent during any suspected unauthorized access.
If money moved, contact the payment provider promptly with the real transaction information. An estimated tour value in the phishing email is not evidence of a payment.
Inspect device exposure if something was installed. Tell trusted technical support about any viewer, extension, or file you ran after opening the link.
Malwarebytes can assist with possible malware checks. AdGuard may help block deceptive ads, but account recovery is still necessary when a password was disclosed.
Report without spreading customer data. Use platform and email-provider reporting tools, and preserve useful evidence privately.
Keep traveler names, contact details, and booking documents out of public warnings. The people named in a fake inquiry may not be involved in the operation.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is SafariBookings itself a scam?
No. This article addresses messages impersonating a real platform. Use its genuine operator account and support channels to check a doubtful inquiry.
Does a valuable group inquiry prove the request is real?
No. Party size, itinerary length, and estimated value can be written into an email. Confirm the lead through the actual service before using its links.
Should I enter my email password to view a tour document?
Not on an unverified page reached through this notification. Open your real email provider separately if account access genuinely needs attention.
Are all inquiries that fail to convert fraudulent?
No. Genuine travelers may stop replying or book elsewhere. That differs from a fake notification directing you to a credential-harvesting page.
Is the entire storage provider behind the phishing?
A reported shared-storage hostname does not establish ownership of the scam or guilt by every customer. The particular page and uploader need separate assessment.
What if I used the same password for email and the operator account?
Replace it through both genuine services and review each account’s access. Securing one does not automatically secure the other.
The Bottom Line
Do not surrender a mailbox password to this fake SafariBookings quote request. Check the inquiry through the real operator account before committing time, information, or access.
If you already signed in, secure the affected account and review relevant customer correspondence. Verify genuine leads without letting an impersonator control the process.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.