

Security checks are supposed to protect an inbox. When a warning says protection itself requires an immediate login, that familiar safeguard can become the attacker’s disguise.
The Security Verification Needed Email Scam sets a deadline, threatens interrupted service, and sends the recipient to a counterfeit portal built to collect an email address and password.
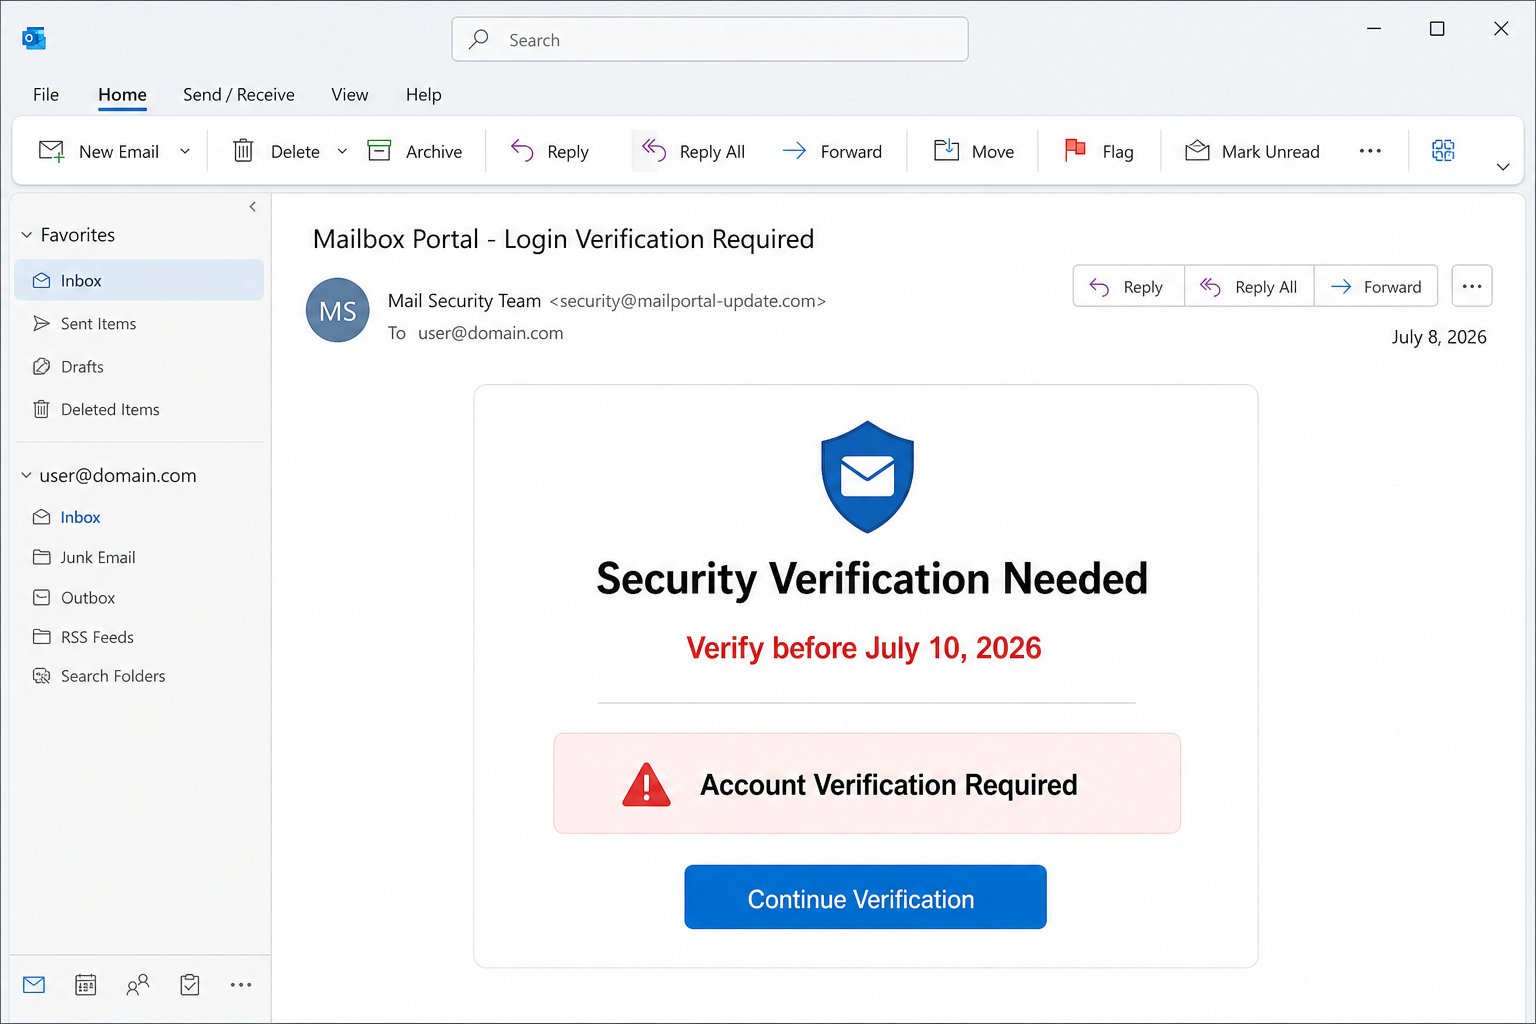
The observed subject says “Mailbox Portal – Login Verification Required.” Inside, a security notice claims verification must be completed before a precise date and time.
A button labeled “Account Verification Required” leads away from the known provider. The analyzed destination used a suspicious .su host unrelated to normal webmail authentication.
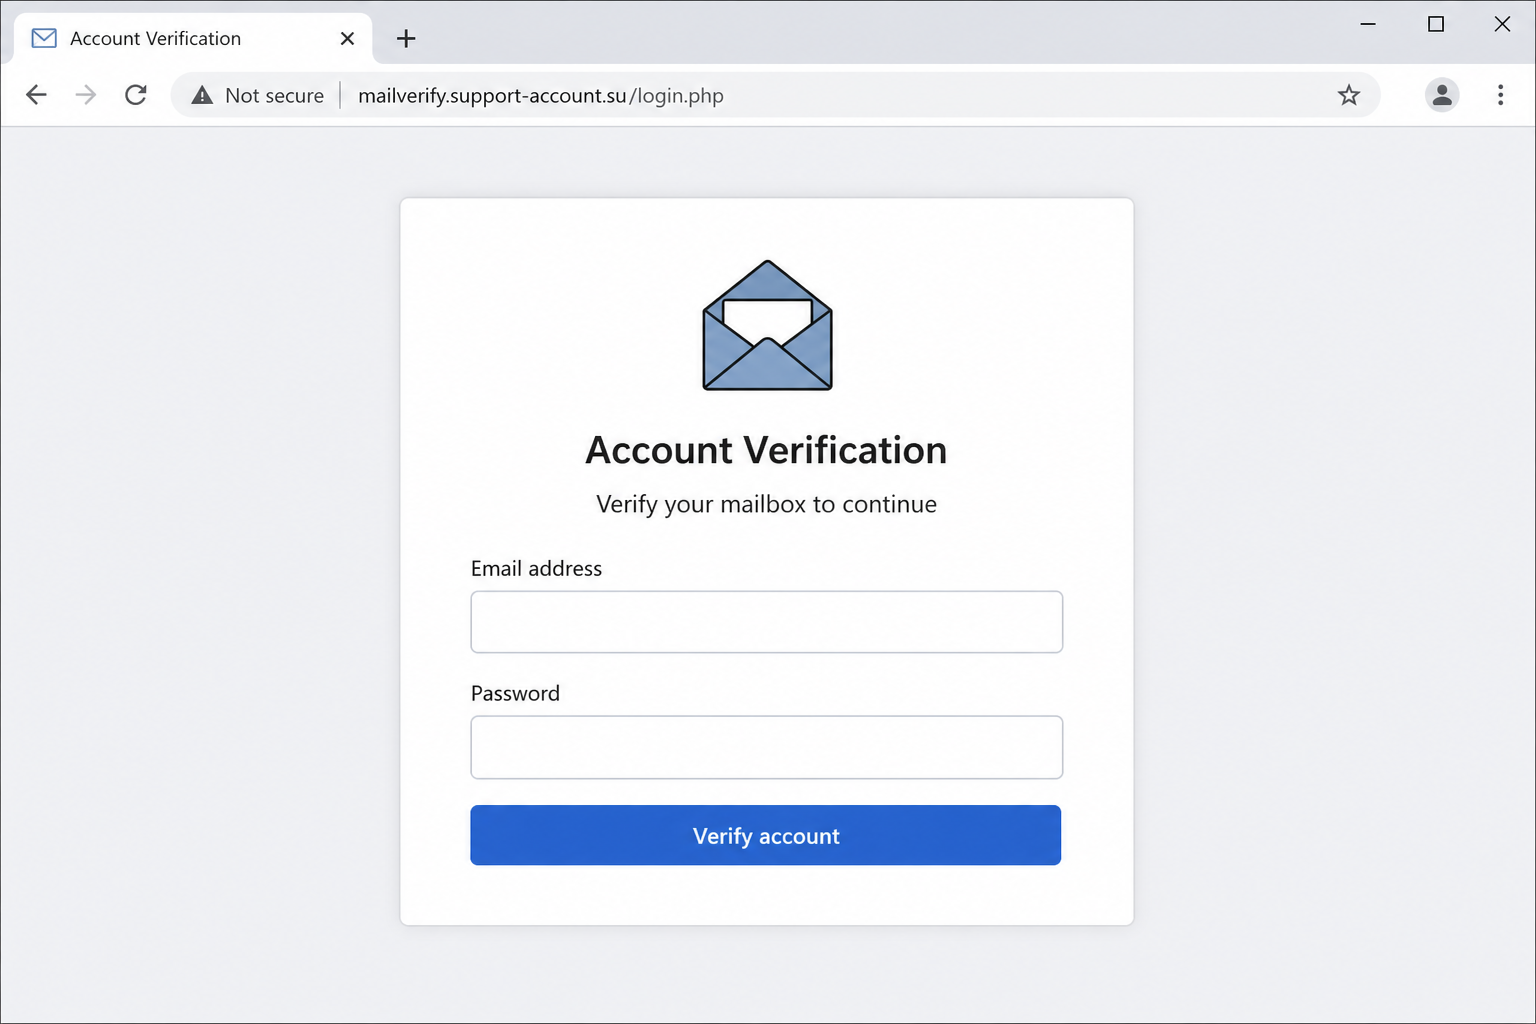
The landing page borrows familiar account imagery and asks for credentials. Its visual design cannot overcome the address-bar evidence showing where the information will actually go.
Overview
A security deadline creates forced urgency
The message frames verification as part of enhanced protection, then warns that email service will be disrupted. That pairing makes compliance feel both responsible and mandatory.
A precise timestamp can look machine-generated, but anyone can add one to a template. Legitimate status must be confirmed inside the authenticated account or through known support.
- The subject presents the request as a portal requirement.
- The body claims the measure protects personal information.
- A deadline discourages the recipient from waiting for independent advice.
- Possible service interruption raises the apparent cost of ignoring the email.
The verification page is outside the real service
The analyzed link reached sqagswr268-insider.theessencecorp[.]su. The domain does not become an email provider because the page displays a familiar sign-in design.
Counterfeit pages may adapt colors and logos to the address being targeted. The adaptation reflects information supplied in the link, not a trusted connection to the account.
- The destination uses an unrelated registered domain.
- The form requests both the account identifier and its secret.
- No security event is visible before credentials are supplied.
- The button text repeats the warning rather than explaining the alleged risk.
The stolen password can undermine other security
Email often controls recovery for other accounts. A working mailbox login may therefore expose cloud storage, social profiles, business tools, and services that send reset links.
The intruder can also watch for real security messages and delete them. That allows fraudulent activity to continue while the victim believes the verification problem was resolved.
- Saved conversations reveal contacts and normal communication patterns.
- Forwarding rules can silently copy new messages to the attacker.
- Connected applications may provide access without repeated password entry.
- Impersonation from the genuine address can target coworkers, family, and vendors.
What Legitimate Security Verification Looks Like
The alert appears in the known account
Providers may ask users to review a login, recovery method, or security setting. The same event should be visible after opening the official application or site independently.
A genuine alert normally identifies the device, location, time, or setting involved. The scam provides a generic requirement that cannot be matched to account history.
The authentication domain remains consistent
A provider may use approved single sign-on, but that relationship is documented and familiar to the organization. It does not suddenly begin on an unrelated foreign-domain page.
Bookmarks, password-manager matching, and organization portals help users stay on the correct host. An unexpected page that does not trigger the saved credential is a warning.
The user can verify without the email link
Security actions should remain available through normal settings. If the alleged requirement vanishes when the email button is avoided, ask support to confirm it.
Do not telephone a number placed inside the same message. Use the provider’s official website, app, bill, or an internal company directory.
Why Exact Deadlines Can Be Misleading
Precision is easy to manufacture
A date down to the second gives the impression that software calculated an enforcement window. The sender can generate that timestamp without querying any real account.
Compare it with the provider’s dashboard and status communications. A precise unsupported claim remains unsupported, regardless of how official the formatting appears.
Urgency narrows the recipient’s choices
The deadline encourages two options: verify now or lose service. It hides the safer third option, which is to open the genuine account and investigate independently.
Scammers benefit when users believe delay is dangerous. Real security teams prefer a cautious verification over credentials entered on an unconfirmed website.
How the Security Verification Needed Email Scam Works
Step 1: A generic security notice reaches the target
The campaign can be sent widely because almost every active address belongs to some mail provider. The message does not need to know which service is actually used.
Recipient data embedded in the URL can help the landing page choose a logo or prefill an address later, creating the appearance of provider awareness.
Step 2: The email announces mandatory portal verification
Security language positions the sender as a protective authority. The account supposedly needs verification for continued access to the webmail portal.
The message does not identify a suspicious login, changed setting, or policy. Its vagueness allows the same warning to fit many organizations.
Step 3: A deadline threatens service interruption
The recipient is told to act before a stated date. Someone who relies on email for work may prioritize continuity over a careful destination check.
The warning offers no authenticated case number or dashboard notice. The countdown exists only inside content controlled by the sender.
- The requested action is presented as compulsory.
- The consequence is broad interruption rather than a specific event.
- The deadline is precise but cannot be independently checked.
- The button is the only immediate path offered in the message.
Step 4: The button opens a deceptive .su page
The browser leaves the official service and loads the unrelated host. A copied account interface attempts to keep the transition from feeling suspicious.
Country-code domains are not inherently malicious, but they must still belong to the service collecting the credentials. This one does not match the claimed portal.
Step 5: The form captures the email address and password
The page may accept any input, show a failure, or ask twice. Its job is to record values, not to validate a genuine security setting.
Even an error message should be treated as evidence that the password was exposed. The attacker can test it outside the visible session.
Step 6: Criminals attempt account access quickly
Working credentials can be used for webmail, reused services, or automated credential-stuffing attempts.
Speed matters because victims may recognize the deception and change the password.
Multifactor prompts may follow. Approving an unexpected prompt can complete the takeover even when the password alone was insufficient.
Step 7: The mailbox is prepared for continued abuse
An intruder may add rules, register an application, alter recovery methods, and review high-value conversations. Those changes can preserve access or hide warning messages.
The account can then distribute document lures, payment changes, or new verification demands. Contacts see a genuine sender and may trust the next fraudulent request.
Company, Address, and Fulfillment Checks
The portal name is not the provider name
Phrases such as Mailbox Portal and Security Team are generic descriptions. They do not identify the organization responsible for storing or protecting the account.
Locate the real provider in account settings or billing records. The sender and link domains should have a documented relationship to that service.
A shield icon cannot establish ownership
Security graphics, lock symbols, and professional colors are simple page elements. They indicate what the designer wants the viewer to feel, not who controls the site.
Use the registered domain, certificate details, password-manager behavior, and known login route as evidence. Appearance is only a presentation layer.
Support should explain the specific event
Contact the real help desk and ask what requires verification, when it was triggered, and where it appears in the account. A genuine event leaves records.
Do not reply to the original message for confirmation. The same operator who sent the warning may answer and repeat the false instructions.
The .su destination does not match webmail ownership
The analyzed host belongs outside the normal authentication path. Familiar words placed before its registered domain cannot turn it into the recipient’s provider.
Close the page whenever the host is unexpected. Navigate from a trusted bookmark and confirm any security requirement there.
Security Verification Warning Signs
Check the evidence before the deadline
A real security event should remain visible when approached independently. The following contradictions show why the emailed route should not be trusted.
- The sender uses a generic security identity rather than a known provider address.
- The warning describes no device, location, login, or changed setting.
- The deadline is visible only inside the unsolicited message.
- The button opens a host unrelated to the normal mail service.
- The page asks for the current password before showing any account evidence.
- The visual branding changes more easily than the destination domain.
Use normal settings to review account security
Open recent activity, connected devices, recovery methods, and multifactor settings from the genuine account. Do not use the suspected page as a shortcut.
Organizations should teach employees where real alerts appear and which login domains are approved. Familiar routes reduce dependence on judgment during an urgent warning.
How Organizations Can Make Verification Safer
Replace surprise links with documented account paths
Security teams should teach users where identity alerts appear and which domains are approved. A known route gives employees something concrete to use when an urgent message arrives.
Where possible, notifications should tell recipients to open the application themselves rather than supplying a direct password link.
This design removes a behavior that phishing campaigns imitate.
Monitor for unusual mailbox rules, legacy authentication, repeated failed logins, and newly authorized applications.
Early detection matters when a victim cannot recall exactly what was submitted.
- Deploy passkeys or hardware security keys for high-risk accounts.
- Block impossible travel and require managed devices for sensitive applications.
- Give staff a one-click internal method to report suspicious verification notices.
- Test help desk identity procedures so attackers cannot bypass recovery controls.
- Review real incidents with employees without blaming the person who reported them.
What to Do if You Have Fallen Victim to This Scam
- Replace the exposed password immediately. Open the official provider from a clean device and choose a unique password. Change any other account where the same or a closely related password was used.
- Revoke sessions and application access. Sign out all devices, remove unknown app passwords, and revoke unfamiliar OAuth connections. This cuts off access that may survive the password change.
- Verify multifactor authentication. Remove devices and methods you did not register. Deny unexpected prompts, add a phishing-resistant passkey or security key if supported, and regenerate recovery codes.
- Audit mailbox rules and recovery details. Inspect forwarding, filters, delegates, deleted items, sent mail, recovery addresses, and trusted applications. Attackers often create quiet persistence before the victim reacts.
- Scan the device with Malwarebytes. The observed campaign steals credentials, but a malicious destination can change behavior. Malwarebytes can check for known malware, unwanted software, and suspicious browser changes.
- Review linked services and sensitive conversations. Check password-reset history, cloud files, finance tools, and accounts using email recovery. Warn relevant contacts if the mailbox may have sent fraudulent messages.
- Use AdGuard for additional phishing protection. AdGuard can block many known malicious domains and deceptive advertisements before they load. It complements, rather than replaces, account security and careful link inspection.
- Report the infrastructure and ignore recovery scams. Send the email and URL to the provider, employer, host, and relevant fraud authority. Do not pay anyone who promises guaranteed recovery or secret access restoration.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is Security Verification Needed a legitimate mailbox alert?
The observed version is phishing. Verify any similar request by opening the official account independently and checking whether the same security event appears in normal settings.
Why does the message include an exact deadline?
Precision creates urgency and an automated appearance. A date is not proof unless it matches an authenticated notice or a support record obtained independently.
Is every .su website malicious?
No, a domain ending does not decide safety by itself. The problem is that this unrelated host claims to authenticate an account belonging to another service.
What if the page said my password was incorrect?
Assume the value was captured. Fraudulent forms can show errors deliberately, so change the password and complete the full account review without waiting.
Can a password manager help identify the fake page?
Yes. A password manager normally offers saved credentials only on the matching legitimate domain.
An absent suggestion can warn that the host is different, although users should still inspect it.
Will multifactor authentication make the account safe again?
It helps, but recovery also requires revoking sessions, checking registered factors, removing mailbox persistence, and securing connected accounts.
Do not approve prompts generated by an attacker, even after changing the password.
The Bottom Line
The Security Verification Needed Email Scam borrows the language of protection to move a password onto an unrelated website.
An exact deadline, shield icon, and familiar login design do not authenticate the sender. Open the real account directly and verify the event through normal security settings.
If the password was submitted, revoke access as well as changing it. A complete review of sessions, factors, rules, applications, and linked services offers the strongest recovery.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.