

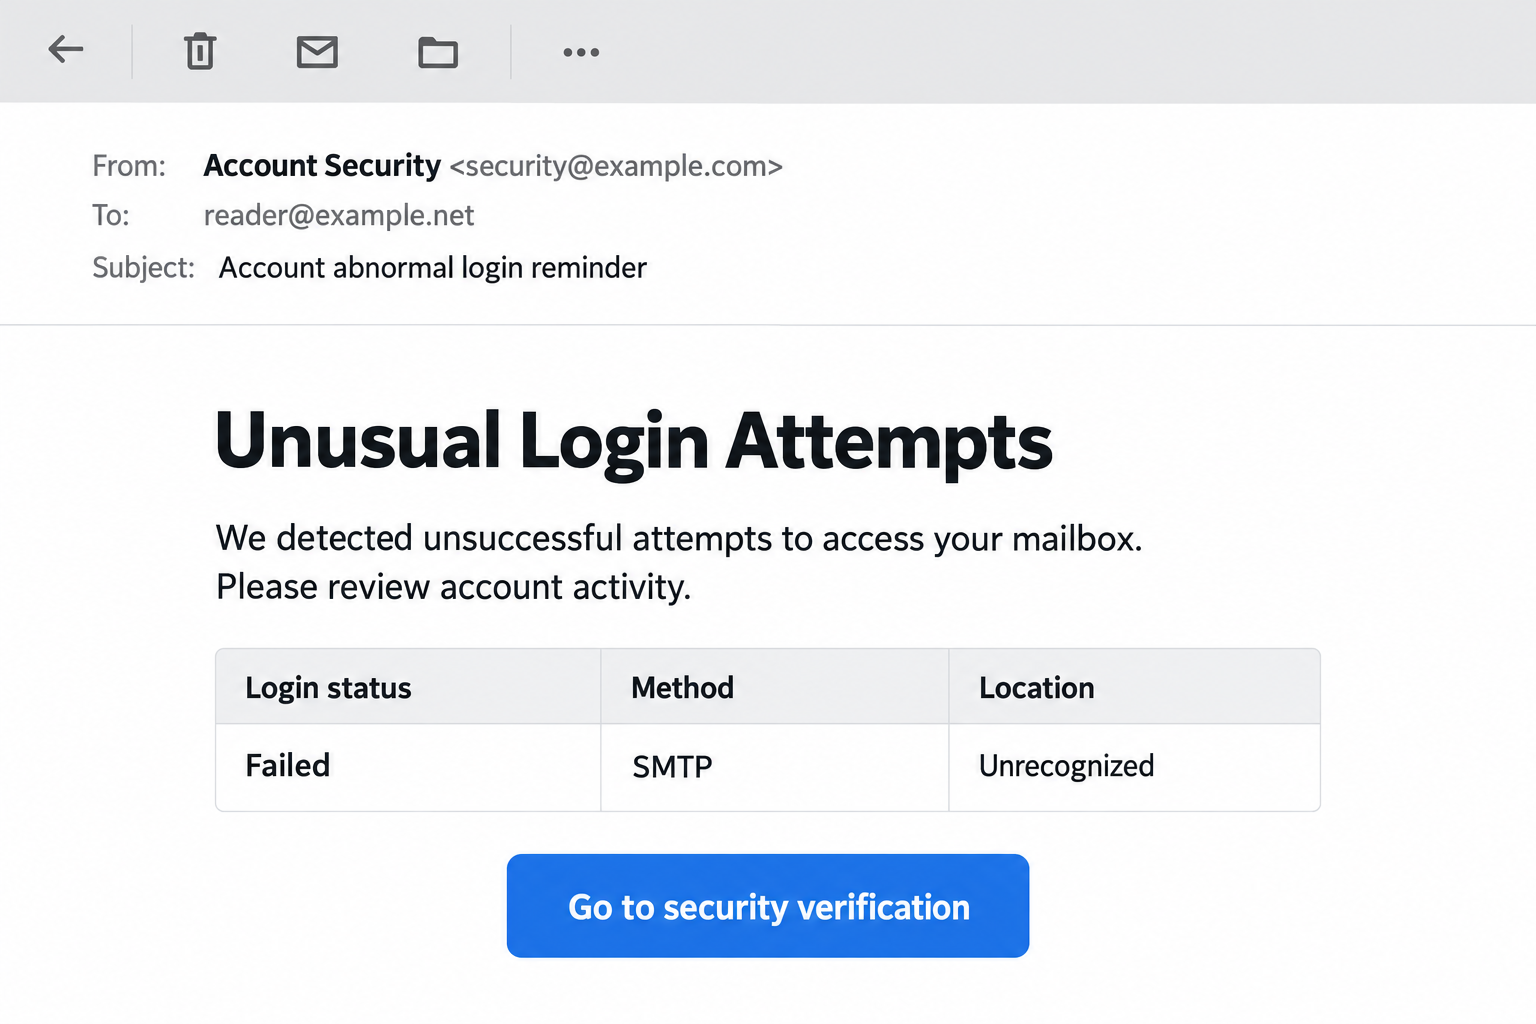
A security email says someone has been trying to enter your mailbox. It even lists an unfamiliar location and a failed login, making the warning feel specific.
Before following its verification button, take a breath. The details that make an alert look convincing also deserve a closer look.
Overview
The warning describes an attempted break-in
The unusual login attempts email scam presents itself as a mailbox security alert. It claims suspicious access has been detected and asks the recipient to verify activity.
One reported version says numerous password attacks were blocked. A table supplies an IP address, location, time, and SMTP login status to support the story.
Those entries are assertions made by the message. They are not independent evidence that someone attempted to access your account from the displayed location.
The proposed security check leads away from trusted account controls
The reported campaign links to puzm[.]life and uses a security-verification deadline to encourage a login. Its destination has been identified as a credential-theft page.
The original form is not currently available for inspection through our capture service. No password was entered, and no account was used to test the request.
The important distinction remains the same: a warning about a possible attack must not become a reason to surrender a password to an unverified site.
A real alert should be checked, not automatically dismissed
Legitimate providers also report suspicious activity. The safe response is to inspect the account independently, rather than trusting or rejecting every email with security language.
Google’s security-alert guidance explains that unfamiliar sign-ins and other important actions can generate genuine warnings.
- Open your usual account settings without using the email’s button.
- Compare the warning with activity recorded inside the real account.
- Reject unexpected approval prompts or requests to share verification codes.
- Report an exposed password promptly, even if the suspicious page displayed an error.
Why a Detailed Login Table Can Be Misleading
A table looks more objective than a vague threat. It suggests that a monitoring system recorded something measurable and is simply passing the result to you.
But anyone composing an email can insert a city, an IP address, or a timestamp. The appearance of a log is not the same as a log.
The number of supposedly blocked attempts adds another emotional cue. A reader may imagine a determined intruder and feel that immediate action is overdue.
There is also a subtle contradiction worth noticing. If the account is protected and the attempt failed, why must an unrelated website receive the current password?
That doesn’t mean every failed-login warning is fraudulent. It means the proposed remedy needs its own verification, separately from the frightening event being described.
The unfamiliar location can make the warning particularly memorable. Do not use it to identify the scammer’s nationality or accuse a person associated with that place.
Even genuine location estimates aren’t always exact. Mobile networks, VPNs, and routing can complicate geography. Account activity needs context, not conclusions drawn from a city alone.
How the Unusual Login Attempts Scam Works
Step 1: The alert gives you a problem that feels personal
An email account is a gateway to work, purchases, private conversations, and password resets. A warning about losing control of it can interrupt almost anything else.
The message doesn’t need to know what is actually inside your inbox. The recipient supplies that significance from their own circumstances.
A person expecting an important reply may worry about missing it. Someone handling invoices may worry about customers. The same broad claim can trigger different private fears.
Don’t answer the sender with your account details to establish whether the warning applies. That gives an unknown correspondent information the original message may never have contained.
Instead, move the investigation to the service you already use. Open its installed app or a saved address and look for the account’s own security information.
Step 2: Technical-looking details make the claim seem established
The access table encourages the reader to skip the question of authenticity. If a time and connection method are listed, the event appears to have already been confirmed.
SMTP is a real email protocol. Its presence in a warning doesn’t demonstrate that the message came from the organization responsible for your mailbox.
A timestamp can also create pressure by making the incident feel recent. Check the real activity history rather than trying to validate a fabricated event through the email.
You don’t need to become a network analyst to respond safely. The relevant question is whether the provider’s independently opened account controls show a problem.
If the account belongs to your employer, send the message through the established reporting process. The administrator can inspect mail headers and identity logs without using the lure.
Step 3: Verification becomes the point where a secret is exposed
The button offers relief from the warning. Its wording makes entering a password feel like defending the account rather than giving someone a way into it.
A counterfeit form can display the provider’s logo, your email address, and a familiar layout. These visible details can be reproduced without knowing the password.
A prefilled address isn’t proof that the site has access to your account. It may simply have been carried in the link or supplied by the campaign.
Stop if an unexpected warning asks you to authenticate on a destination you cannot verify. Don’t keep submitting variations when the page says the password is wrong.
A rejection message cannot prove that nothing was recorded. If a genuine password was entered, treat the credential as exposed and take recovery steps through the real provider.
Step 4: The response must contain account access, not just the email
A stolen password can be tried against the mailbox or another service where it was reused. Successful access depends on the account’s protections and other circumstances.
That uncertainty is a reason to act, not a reason to claim every recipient has been hacked. The exposure and the confirmed consequences are different facts.
Once an account may be compromised, checking sessions and recovery settings becomes important. Deleting the warning from the inbox doesn’t address access already obtained elsewhere.
If someone contacts you afterward claiming to be support, verify that contact separately. Familiarity with the suspicious incident doesn’t make the next request trustworthy.
Check the Real Activity Without Following the Lure
Begin with the correct account
People often have several email addresses open at once. Confirm which one the warning names and which account you are reviewing in the legitimate app.
A generic notice sent to an old or unrelated address may not match the account you are worried about. Don’t supply additional addresses to help the sender identify you.
If a genuine alert and a suspicious email arrive together, handle the genuine event through the provider. The coincidence doesn’t authenticate the other message.
Review changes as well as sign-ins
Look for unfamiliar devices, changed recovery information, and activity you didn’t initiate. Review available settings through the service’s ordinary security menu.
For a work mailbox, ask IT about sessions, new authentication methods, and application permissions. They may have evidence and controls unavailable in the user’s settings.
Google’s suspicious-activity checklist includes changes to recovery details and security settings, not only unfamiliar login locations.
Keep the account question separate from the computer question
A credential-phishing page can create an account problem without installing a program. Conversely, a suspicious download may require device checks even if no password was submitted.
Write down what happened in order. Did you open a page, type a password, approve a prompt, download a file, or run an application?
That simple record gives you a much better starting point than a general fear that everything is infected. It also helps support choose the appropriate response.
What to Do If You Followed the Verification Request
Stop using the suspicious verification page. Close it without entering anything further. Do not return to check whether the sender has removed it.
If you only received the email, report it as phishing and delete it after preserving any evidence your workplace needs. Receipt alone doesn’t demonstrate compromise.
Replace any password you supplied. Open the provider through a trusted route and choose a unique replacement. Use a known-safe device if suspicious software also ran.
Secure other accounts that used the same exposed password. Prioritize identities that control recovery, rather than changing unrelated secrets simply because they exist.
Check recovery methods and current access. Inspect unfamiliar devices, account changes, and any available sign-out controls. Remove access you don’t recognize through the legitimate service.
Ask your workplace administrator to investigate a work or school identity. Don’t assume the visible settings page shows every session or authorization.
Review important messages and business activity. Watch for password-reset emails, unfamiliar outgoing mail, or payment instructions you didn’t send.
If a client or colleague received a suspicious message from your account, coordinate a clear warning through a separate channel. Avoid distributing the malicious link again.
Address installed software if that was part of the encounter. On an employer-owned computer, report the action before attempting your own cleanup.
Malwarebytes can assist with checking a personal device after a risky download or installation. It does not change a stolen password or invalidate an online session.
AdGuard may reduce some malicious-ad exposure during browsing. It cannot confirm whether a login alert is authentic, so keep independent account checks in your routine.
Report actual financial or identity misuse separately. Contact the affected provider quickly and retain transaction records. A mailbox recovery ticket isn’t a bank-fraud report.
Save the original warning, destination address, approximate exposure time, and any support reference numbers. Keep passwords and recovery codes out of the evidence you share.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Make Future Alerts Easier to Judge
The best time to learn your account’s security menu is before another alarming message arrives. Save the genuine access route and know how to reach support independently.
Use a password manager with distinct passwords for different services. A mismatch between a site’s address and a saved login can provide a useful moment to stop.
Enable the provider’s stronger sign-in options where available. Do not approve an unexpected request merely because an email says that approval will stop attacks.
For a shared family or business account, agree on who handles security notifications. Confusion between multiple users can make an unexplained sign-in harder to interpret.
Keep the explanation practical when warning someone else. Tell them which message to avoid and how to open the genuine account, rather than simply saying every alert is fake.
After a confirmed incident, note what the provider established. That record can help you distinguish a continuing account issue from a later email recycling the same fear.
If you cannot regain access, use the provider’s established recovery process. Do not pay a person in a comment thread who promises an immediate private unlock.
Know whose account the alert actually concerns
An employee may receive mail for a shared inbox without managing the identity behind it. Check with its owner before changing settings that affect other people.
Similarly, a family member forwarding an alert doesn’t establish which account is at risk. Have them open their own account controls rather than sharing a password with you.
When help is needed, provide the security event and approximate time. Nobody needs to receive a current password merely to understand why the warning concerned you.
If support finds a genuine failed attempt, ask what action is appropriate for that event. A blocked attempt and a successful unauthorized session are different findings.
Keep that distinction in any warning you send onward. Saying that a password was exposed is more accurate than announcing a confirmed breach before access records exist.
After recovery, check that ordinary access still works for authorized users. Resolving the incident should not leave a shared business mailbox without a responsible owner.
Make sure future security notices reach the correct person. An alert left in an unattended recovery inbox can delay a response when a real account event occurs.
Frequently Asked Questions
Does this email prove someone tried my password?
No. The message’s access table can be fabricated. Check actual account activity through the genuine provider before treating its claims as a recorded security event.
Are all unusual-login emails fraudulent?
No. Providers send real warnings too. Inspect them through independently opened account controls instead of assuming the warning’s own link is safe.
Does the listed IP address identify the scammer?
No. It is information printed in the lure, not verified attribution. Even a genuine login location may require context before it can be interpreted reliably.
What if the security page knew my email address?
An address can be included in a link or prefilled form. Knowing it doesn’t establish control of your mailbox or prove the page belongs to your provider.
Should I approve a login prompt to block the attack?
Don’t approve a request you didn’t initiate. Open your real account settings or contact your administrator to investigate the event without following the email’s directions.
Can a scan tell me whether my mailbox was accessed?
No. Account history and provider records answer that question. Device scanning is relevant to suspicious software exposure, not a substitute for examining online access.
The Bottom Line
Do not follow the unusual-login email’s verification link. Check the real account independently, where genuine security activity can be assessed without trusting the sender’s story.
If you entered a password, secure that identity now and review its access settings. Respond to what happened, not just the fear the message created.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.