


Have you ever received an email claiming your cryptocurrency wallet was hacked? These scam emails try to trick victims into handing over wallet login details. One such scam is the “Wallet Login from Unknown Device” phishing attack.
This article will uncover everything you need to know about spotting and stopping this scam. We’ll explain how the devious phishing emails work, what to do if you fell victim, and most importantly, how to keep your digital assets safe.
With cryptocurrency adoption growing, hackers are getting sneaky with phishing techniques. But armed with the right information, these scams don’t have to succeed. Read on and protect your hard-earned crypto.
Scam Overview
The “Wallet Login From Unknown Device” scam is a sophisticated phishing attack that targets cryptocurrency owners, aiming to steal their login credentials and ultimately drain their digital wallets. Scammers employ social engineering tactics to create a sense of urgency and fear, pressuring victims to act quickly without thinking critically about the situation.
The scam typically begins with an unsolicited email that appears to be sent from a well-known cryptocurrency wallet provider, such as Blockchain.com, Coinbase, or Binance. The email’s subject line is designed to grab the recipient’s attention, often using phrases like “Urgent: Unauthorized Access Detected” or “Wallet Login from unknown device.”
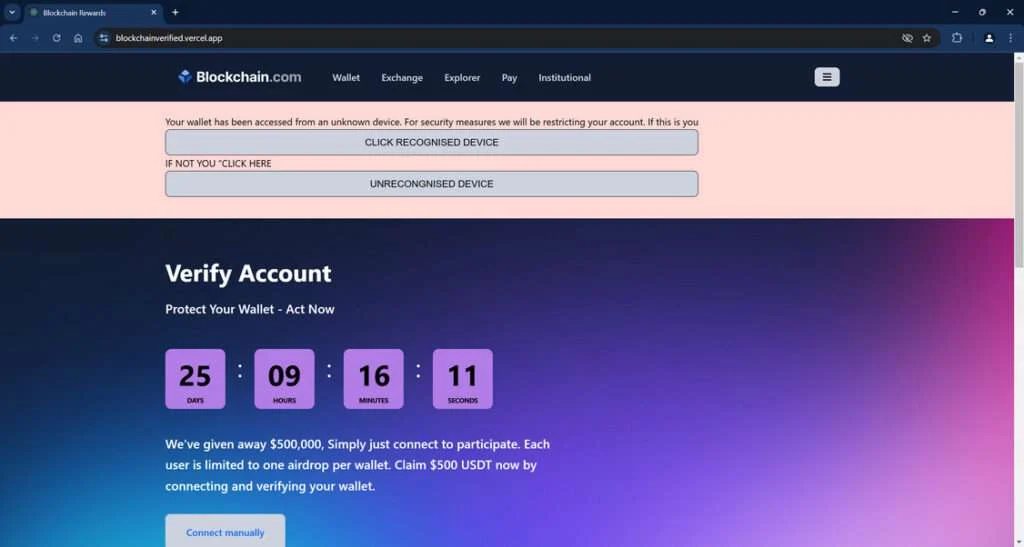
Upon opening the email, the victim is confronted with a message claiming that their wallet has been accessed from an unknown IP address. The email may include details like the supposed IP address, location, and timestamp of the unauthorized access to make the claim seem more credible. To add to the sense of urgency, the message may state that the victim’s account will be restricted or suspended unless they take immediate action to verify their identity.
The email includes two prominent links or buttons, typically labeled “CLICK HERE FOR UNRECOGNIZED DEVICE” and “CLICK HERE FOR RECOGNIZED DEVICE.” These links are designed to redirect the victim to a fake website that closely resembles the legitimate wallet provider’s site. The fake site often features the same logos, branding, and layout as the real platform, making it difficult for unsuspecting users to detect the deception.
Once on the fake website, the victim is prompted to enter their wallet login credentials, such as their email address, password, and possibly even their two-factor authentication code. If the victim falls for the scam and provides this sensitive information, the scammers gain full access to their cryptocurrency wallet, enabling them to steal all the stored digital assets.
To further entice victims, the fake website may also promote a “giveaway” or “airdrop” event, claiming that users can receive a substantial amount of free cryptocurrency (e.g., $500 USDT) by connecting their wallet to the site. This tactic exploits people’s desire for easy gains and creates an additional incentive for them to hand over their wallet access.
The “Wallet Login From Unknown Device” scam is particularly insidious because it preys on people’s fear of losing their valuable digital assets. By creating a false sense of urgency and using social engineering techniques, scammers manipulate victims into making rash decisions that ultimately compromise their wallet security.
As cryptocurrencies continue to gain mainstream adoption, scams like this are becoming increasingly common and sophisticated. It’s crucial for cryptocurrency owners to remain vigilant, educate themselves about potential threats, and follow best practices for securing their digital wallets. In the following sections, we’ll provide a more detailed breakdown of how the scam works and offer actionable advice on how to protect yourself from falling victim to this and similar attacks.
How The Scam Works
The “Wallet Login From Unknown Device” scam is a multi-step process that relies on a combination of social engineering, phishing, and website spoofing to trick victims into revealing their sensitive information. Let’s take a closer look at each stage of the scam:
Step 1: Crafting the Phishing Email
The scam begins with the creation of a convincing phishing email designed to impersonate a legitimate cryptocurrency wallet provider. Scammers often use email addresses and domain names that closely resemble those of the real company, such as “support@blockchainverified.com” instead of “support@blockchain.com.”
The email’s subject line is carefully chosen to create a sense of urgency and alarm, prompting the recipient to open the message immediately. Examples of typical subject lines include:
- “Urgent: Unauthorized Access Detected”
- “Wallet Login from unknown device”
- “Suspicious Activity on Your Account”
- “Your Wallet Has Been Compromised”
The email’s content is crafted to reinforce the false narrative of an unauthorized access attempt. It may include details like:
- The supposed IP address of the unauthorized device
- The location and timestamp of the access attempt
- A warning that the victim’s account will be restricted or suspended unless they take action
- Instructions to click on links to verify their identity
To make the email appear more legitimate, scammers often incorporate official logos, branding, and formatting that mimics the real wallet provider’s communications. They may also include a footer with a disclaimer or legal information to further enhance the illusion of authenticity.
Step 2: Redirecting to the Fake Website
The phishing email includes prominent links or buttons that urge the victim to take immediate action. These links are designed to redirect the user to a fake website that closely resembles the legitimate wallet provider’s platform.
Scammers employ various techniques to create convincing fake websites, such as:
- Using domain names that are similar to the real site (e.g., “blockchainverified.com” instead of “blockchain.com”)
- Replicating the design, layout, and branding of the legitimate site
- Incorporating security certificates (HTTPS) to make the site appear more trustworthy
- Displaying fake user reviews or testimonials to build credibility
When the victim clicks on one of the links in the phishing email, they are directed to the fake website. The site is designed to look and feel exactly like the real platform, making it difficult for the average user to detect the deception.
Step 3: Harvesting Login Credentials
Once on the fake website, the victim is prompted to enter their wallet login credentials to “verify their identity” or “secure their account.” The site may ask for information such as:
- Email address
- Password
- Two-factor authentication code
- Private key or recovery phrase
If the victim enters this sensitive information, it is immediately transmitted to the scammers, who can then use it to gain unauthorized access to the real wallet.
To create a sense of legitimacy and encourage victims to provide their login details, the fake website may display messages like:
- “Your account has been temporarily restricted for security reasons”
- “Please verify your identity to restore access to your wallet”
- “Enter your login credentials to secure your account”
Step 4: Promoting Fake Giveaways or Airdrops
In some cases, the fake website may also promote a “giveaway” or “airdrop” event to further entice victims into connecting their wallets. The site may claim that users can receive a substantial amount of free cryptocurrency (e.g., $500 USDT) by linking their wallet to the platform.
These fake giveaways often feature a countdown timer to create a false sense of urgency, pressuring victims to act quickly before the supposed opportunity expires. The site may also display fake user testimonials or social media posts to make the giveaway seem more legitimate.
If the victim falls for the giveaway scam and connects their wallet to the fake site, the scammers gain full access to their digital assets, enabling them to steal all the stored funds.
Step 5: Stealing the Victim’s Cryptocurrency
Once the scammers have obtained the victim’s wallet login credentials, they can access the real wallet and drain all the stored cryptocurrency. This process is often automated, allowing the scammers to quickly transfer the stolen funds to their own wallets before the victim realizes they’ve been compromised.
In some cases, the scammers may also use the stolen login information to access other connected accounts or services, such as cryptocurrency exchanges or online marketplaces, to maximize their ill-gotten gains.
The “Wallet Login From Unknown Device” scam is a sophisticated and evolving threat that continues to claim new victims as cryptocurrency adoption grows. By understanding how the scam works and recognizing the red flags, you can better protect yourself from falling prey to this insidious attack.
In the following sections, we’ll provide actionable advice on what to do if you’ve fallen victim to this scam and share expert tips for securing your cryptocurrency wallets against future threats.
What to Do if You Have Fallen Victim to This Scam
If you suspect that you’ve fallen victim to the “Wallet Login From Unknown Device” scam, it’s crucial to act quickly to minimize the potential damage. Here are the steps you should take:
- Immediately change your wallet login credentials, including your password and any associated email addresses. If your wallet supports two-factor authentication (2FA), enable it or update your 2FA settings to prevent further unauthorized access.
- Check your wallet’s transaction history for any suspicious activity, such as unauthorized withdrawals or transfers. If you notice any unfamiliar transactions, contact your wallet provider’s support team immediately to report the issue and request assistance.
- If you’ve provided your private key or recovery phrase to the scammers, you should consider your existing wallet compromised and create a new one. Transfer any remaining funds from your compromised wallet to the new one as soon as possible.
- Report the scam to the relevant authorities, such as your local law enforcement agency, the FBI’s Internet Crime Complaint Center (IC3), or the Federal Trade Commission (FTC). Provide as much detail as possible, including the phishing email, fake website URL, and any other relevant information.
- Notify your wallet provider and any linked cryptocurrency exchanges about the incident. They may be able to provide additional support or guidance and can help prevent similar scams from targeting other users.
- If you’ve lost a significant amount of cryptocurrency due to the scam, consider seeking legal advice from an attorney specializing in cybercrime or digital assets. They can help you explore potential options for recovering your funds or pursuing legal action against the scammers.
- Educate yourself about cryptocurrency scams and best practices for securing your digital assets. Stay informed about the latest threats and techniques used by scammers, and share your knowledge with others to help prevent them from falling victim to similar attacks.
Remember, prevention is always better than cure when it comes to cryptocurrency scams. By remaining vigilant, following best practices for wallet security, and staying informed about potential threats, you can significantly reduce your risk of falling victim to the “Wallet Login From Unknown Device” scam and other similar attacks.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About the “Wallet Login From Unknown Device” Scam
Q1: What is the “Wallet Login From Unknown Device” scam?
A: The “Wallet Login From Unknown Device” scam is a phishing attack that targets cryptocurrency owners. Scammers send an email claiming that the victim’s wallet has been accessed from an unknown device, urging them to click on links to verify their identity. These links lead to a fake website designed to steal the victim’s login credentials and drain their digital assets.
Q2: How does the “Wallet Login From Unknown Device” scam work?
A: The scam begins with a phishing email that appears to be from a legitimate wallet provider. The email claims unauthorized access to the victim’s wallet and includes links to a fake website. If the victim enters their login credentials on the fake site, scammers gain access to their real wallet and steal their cryptocurrency.
Q3: What are the signs of a “Wallet Login From Unknown Device” scam email?
A: Some common red flags include:
- Unsolicited emails claiming unauthorized wallet access
- A sense of urgency or pressure to act quickly
- Links that direct you to unfamiliar websites
- Poor grammar, spelling, or formatting in the email
- Requests for sensitive information like login credentials or private keys
Q4: How can I protect myself from falling victim to this scam?
A: To protect yourself, follow these best practices:
- Be cautious of unsolicited emails about your wallet security
- Never click on links or provide login credentials from an email
- Always access your wallet by typing the official URL into your browser
- Enable two-factor authentication on your wallet and linked accounts
- Regularly monitor your wallet’s transaction history for suspicious activity
Q5: What should I do if I’ve fallen victim to the “Wallet Login From Unknown Device” scam?
A: If you suspect you’ve fallen victim to this scam:
- Immediately change your wallet login credentials and enable 2FA
- Check your transaction history and report any unauthorized activity to your wallet provider
- If you’ve provided your private key or recovery phrase, create a new wallet and transfer your remaining funds
- Report the scam to the relevant authorities and your wallet provider
- Consider seeking legal advice if you’ve lost a significant amount of cryptocurrency
Q6: Can I recover my stolen cryptocurrency if I fall for this scam?
A: Recovering stolen cryptocurrency can be difficult, as transactions are often irreversible and scammers quickly move funds to untraceable wallets. However, reporting the incident to law enforcement and seeking legal advice may help you explore potential options for recovery.
Q7: Are there any legitimate reasons why my wallet provider would email me about unauthorized access?
A: Legitimate wallet providers may send emails about suspicious activity on your account, but they will never ask you to provide sensitive information or click on links from the email. If you receive such an email, always navigate to the official website independently to check your account status and contact support if needed.
Q8: How can I report a “Wallet Login From Unknown Device” scam?
A: You can report the scam to your local law enforcement, the FBI’s Internet Crime Complaint Center (IC3), the Federal Trade Commission (FTC), and your wallet provider. Provide as much detail as possible, including the phishing email, fake website URL, and any other relevant information.
Q9: What should I do if I receive a “Wallet Login From Unknown Device” scam email?
A: If you receive a suspicious email claiming unauthorized access to your wallet, do not click on any links or provide your login credentials. Instead, forward the email to your wallet provider’s official support team and delete it from your inbox. If you’re unsure about the email’s legitimacy, contact your wallet provider directly through their official channels.
Q10: How can I stay informed about new cryptocurrency scams?
A: To stay informed about the latest cryptocurrency scams, regularly visit reputable sources such as official wallet provider blogs, cybersecurity news websites, and cryptocurrency forums. Follow your wallet provider’s official social media accounts for updates and warnings about new threats. Educate yourself about best practices for cryptocurrency security and share your knowledge with others to help prevent them from falling victim to scams.
The Bottom Line
The “Wallet Login From Unknown Device” scam is a stark reminder of the ever-present dangers in the cryptocurrency landscape. As digital assets continue to gain mainstream adoption, scammers are becoming increasingly sophisticated in their attempts to steal from unsuspecting victims.
This scam, in particular, relies on a potent combination of social engineering, phishing, and website spoofing to create a false sense of urgency and trick users into revealing their sensitive wallet information. By impersonating legitimate wallet providers and exploiting people’s fear of losing their valuable digital assets, scammers can quickly drain victims’ wallets before they even realize they’ve been compromised.
To protect yourself from falling victim to this and similar scams, it’s essential to remain vigilant and follow best practices for securing your cryptocurrency wallets. Always be cautious of unsolicited emails claiming unauthorized access to your accounts, and never click on links or provide your login credentials in response to such messages.
Instead, if you receive a suspicious email, go directly to your wallet provider’s official website by typing the URL into your browser. Enable two-factor authentication on your wallet and any linked accounts, and regularly monitor your transaction history for any signs of unauthorized activity.
If you found this article informative and valuable, please share it with your friends, family, and colleagues who may also benefit from learning about this insidious scam. Together, we can help spread awareness and create a safer, more secure cryptocurrency ecosystem for everyone.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.