


A payment confirmation lands in your inbox, apparently from an accounts-payable employee. It says a wire has already been processed and needs your review.
The message feels important because money may be moving. Pause before treating its polished finance language as evidence that any transfer actually exists.
Overview
A Financial Notice That Targets the Mailbox
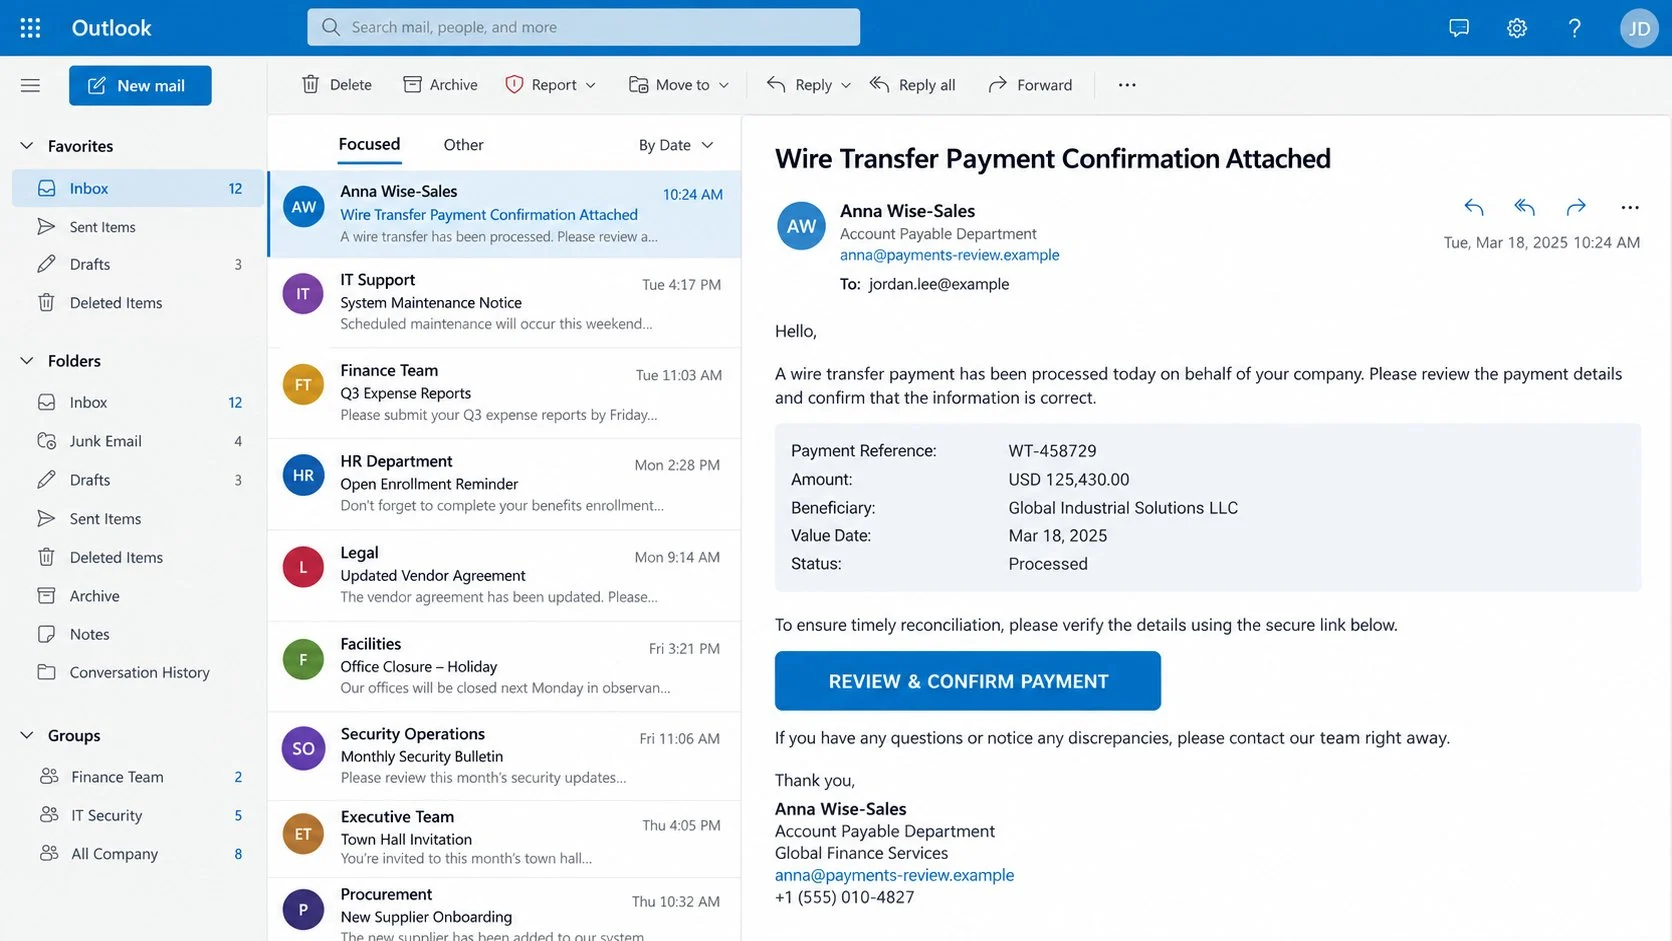
The Wire Transfer Payment Confirmation email scam pretends to document money sent on behalf of a company. It asks the recipient to review and confirm payment details.
The observed subject reads “Wire Transfer Payment Confirmation Attached.” The signature names “Anna Wise-Sales” and an “Account Payable Department.”
Despite the word “attached,” the important action is a button labeled “REVIEW & CONFIRM PAYMENT.” It leads away from the email rather than proving a transfer.
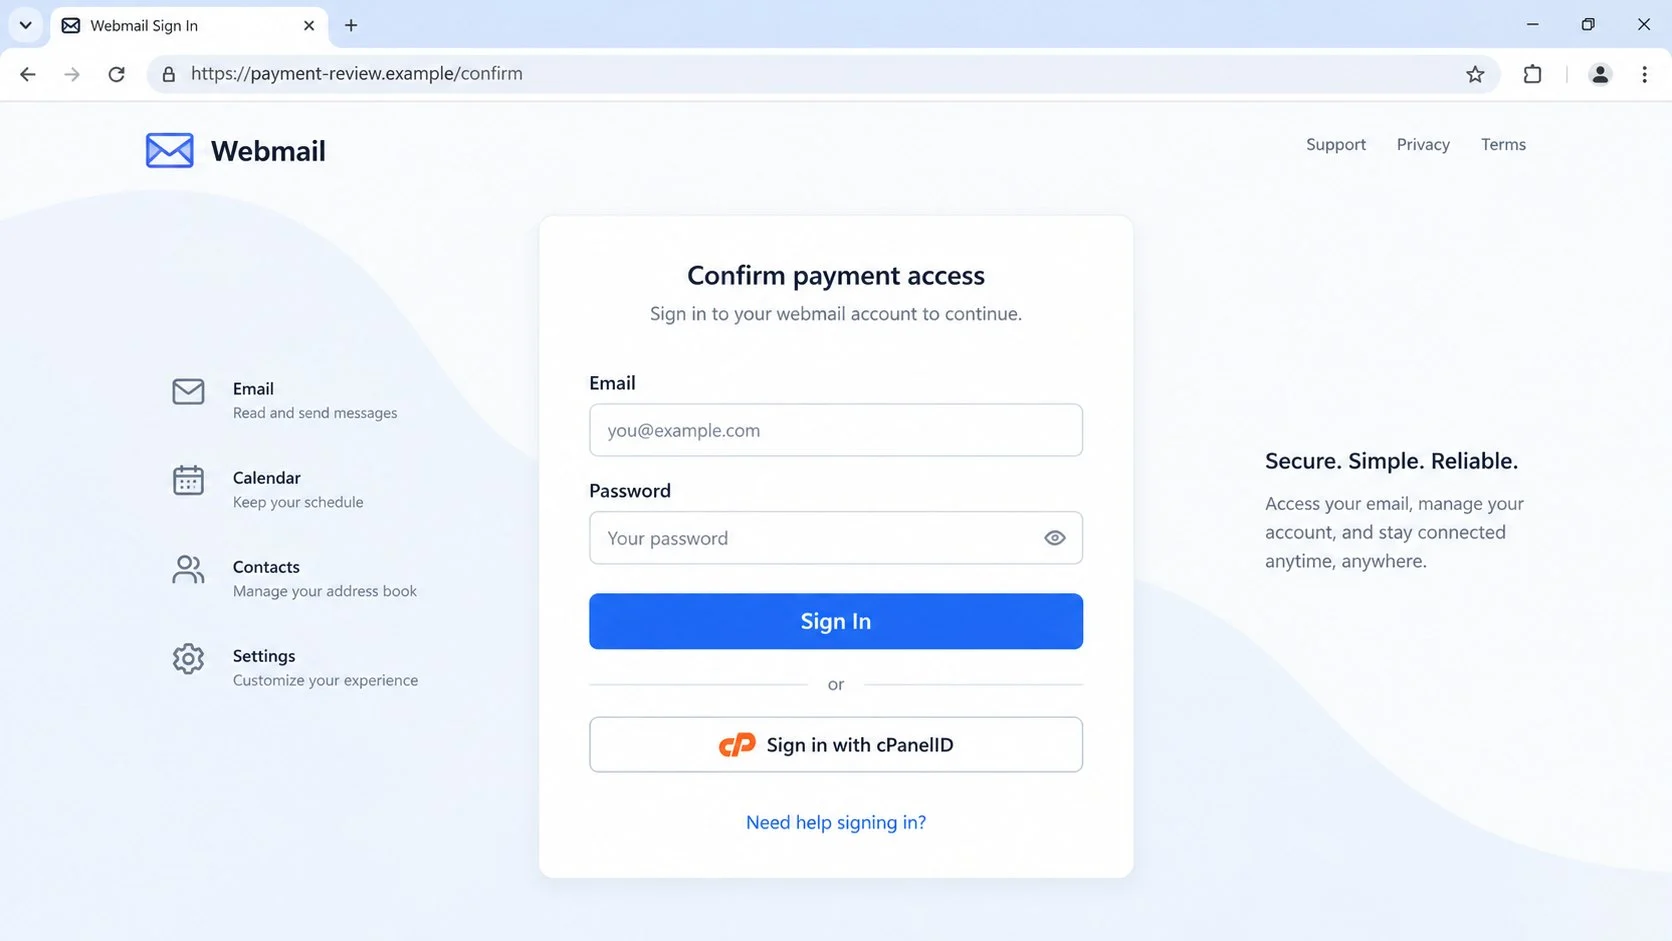
The destination presents a generic webmail sign-in page. Its requested email credentials have no legitimate role in confirming a bank wire.
Clues Specific to This Payment Lure
Finance teams see genuine receipts, remittance notices, and approval requests every day. This version borrows that vocabulary while omitting verifiable business context.
- The subject claims a transfer confirmation is attached.
- The sender persona combines a personal name with “Sales.”
- The department is written as “Account Payable,” not the more usual plural.
- The email says the payment was already processed.
- A button asks the reader to review and confirm it.
- The next screen requests webmail credentials.
- The reported destination used a third-party website-building platform.
The examined link used a page under hegelsonjames.wixstudio[.]com. Treat that address as a campaign indicator, not as proof that every future copy will match.
Wix Studio is a legitimate service and is not implicated in the fraud. An abuser can create deceptive content on a reputable platform without its endorsement.
No Confirmed Wire Is Shown
The email’s statement is merely a claim written by its sender. It does not establish that a bank accepted, transmitted, or settled a payment.
A real transfer should connect to internal records, an approved invoice, a known beneficiary, and banking activity accessible through established systems.
The immediate danger in this sample is credential capture. There is no evidence that reading the email alone moves money or installs software.
However, a compromised business inbox can later support invoice fraud. Attackers may use genuine conversations to make a separate payment diversion more convincing.
How the Wire Transfer Payment Confirmation Email Scam Works
Step 1: The Subject Creates a High-Stakes Interruption
Few employees want to ignore an unexpected wire. The subject suggests money has already left, so delay can feel professionally risky.
That emotional pressure replaces useful details. A recipient may click simply to discover which account, invoice, or vendor the message concerns.
The word “attached” also prepares the reader for protected documents. Yet the interaction may rely mainly on a button leading to a website.
When subject and contents disagree, do not resolve the confusion through the sender’s link. Check the transaction in your organization’s own records.
Step 2: A Finance Persona Supplies Borrowed Authority
A named employee sounds more credible than a generic “Payment Team.” Adding a department and signature makes the message resemble ordinary business correspondence.
Display names are not authenticated identities. The visible label can say “Anna Wise-Sales” while the underlying address belongs to an unrelated account.
The phrase “Account Payable Department” may pass during a hurried scan. Small wording oddities matter most when they accompany a sensitive request.
Even a perfectly written signature would not validate the email. Confirm people through a company directory, prior thread, or known telephone number.
Step 3: The Button Reframes a Mail Login as Payment Verification
“REVIEW & CONFIRM PAYMENT” sounds like a finance task. It gives no honest reason why the reader’s mailbox password should be required.
A legitimate approval platform might require its own authenticated session. That session should open through the organization’s recognized finance or banking service.
The scam instead sends the visitor to an unrelated site. Familiar words around the button distract from the destination underneath it.
Hovering or previewing the link can expose that mismatch before the page opens. A website-builder subdomain is not a bank or corporate payment portal.
Step 4: Generic Webmail Branding Fits Many Targets
The landing page may avoid one specific provider. A broad “Webmail” design lets the same campaign target companies using different hosting arrangements.
An optional cPanelID sign-in can make the form look suitable for business domains. It still does not connect the page to the recipient’s actual host.
The visitor may assume authentication unlocks a payment document. In reality, the form can simply forward the entered address and password to its operator.
The absence of detailed transfer information on the page is revealing. The supposed finance task remains out of reach while credentials become the only requested asset.
Step 5: The Collected Login Opens Business Opportunities
Access to a finance mailbox can reveal invoices, vendor contacts, account numbers, approval chains, and the timing of genuine transactions.
An attacker may quietly monitor those conversations. Later, they can insert altered bank details when a legitimate payment is due.
They might also impersonate the employee to request urgent transfers from colleagues. Existing message history makes that second phase harder to recognize.
None of those outcomes should be assumed without evidence. Recent sign-ins, forwarding rules, sent mail, and payment records show whether escalation occurred.
Step 6: A Quiet Redirect Can Hide the Theft
After submission, a counterfeit form may report an error or send the user to a real website. The promised confirmation may simply never appear.
A busy employee may blame a broken portal and return to work. That delay gives the operator more time to try the captured credentials.
Repeated failures are not reassurance. Each attempt can transmit another password, especially if the user cycles through familiar choices.
Report the incident based on the submission itself. Waiting for visible misuse can turn a manageable credential exposure into a wider business compromise.
How to Verify the Transfer and the Sender
Check the Ledger Before the Email
Open your accounting, treasury, or banking system through its established route. Search for the claimed transfer using date, beneficiary, amount, and internal reference.
If nothing matches, the message has not earned further trust. If something does match, verify through the transaction record rather than the embedded button.
A real payment and a phishing email can coincide. Matching timing alone does not prove the message came from the bank or finance team.
Confirm the Person Through a Separate Channel
Look up the named employee in a trusted company directory. Call or message them using contact information you already possess.
Do not reply to the suspicious email to ask whether it is real. Replies can reach the same operator and invite a persuasive explanation.
For outside vendors, use the contact from an approved contract or previous verified invoice. Never accept replacement bank details solely through email.
Compare the Link With Approved Finance Systems
Your organization may use a bank portal, enterprise resource platform, or secure document service. Staff should know which domains support those workflows.
A site-builder address cannot become an approved payment portal because it shows a webmail logo. Check the address itself, including spelling and subdomain structure.
Remember that HTTPS protects the connection, not the honesty of the site. Criminal pages can obtain certificates automatically.
Examine Headers Without Overinterpreting Them
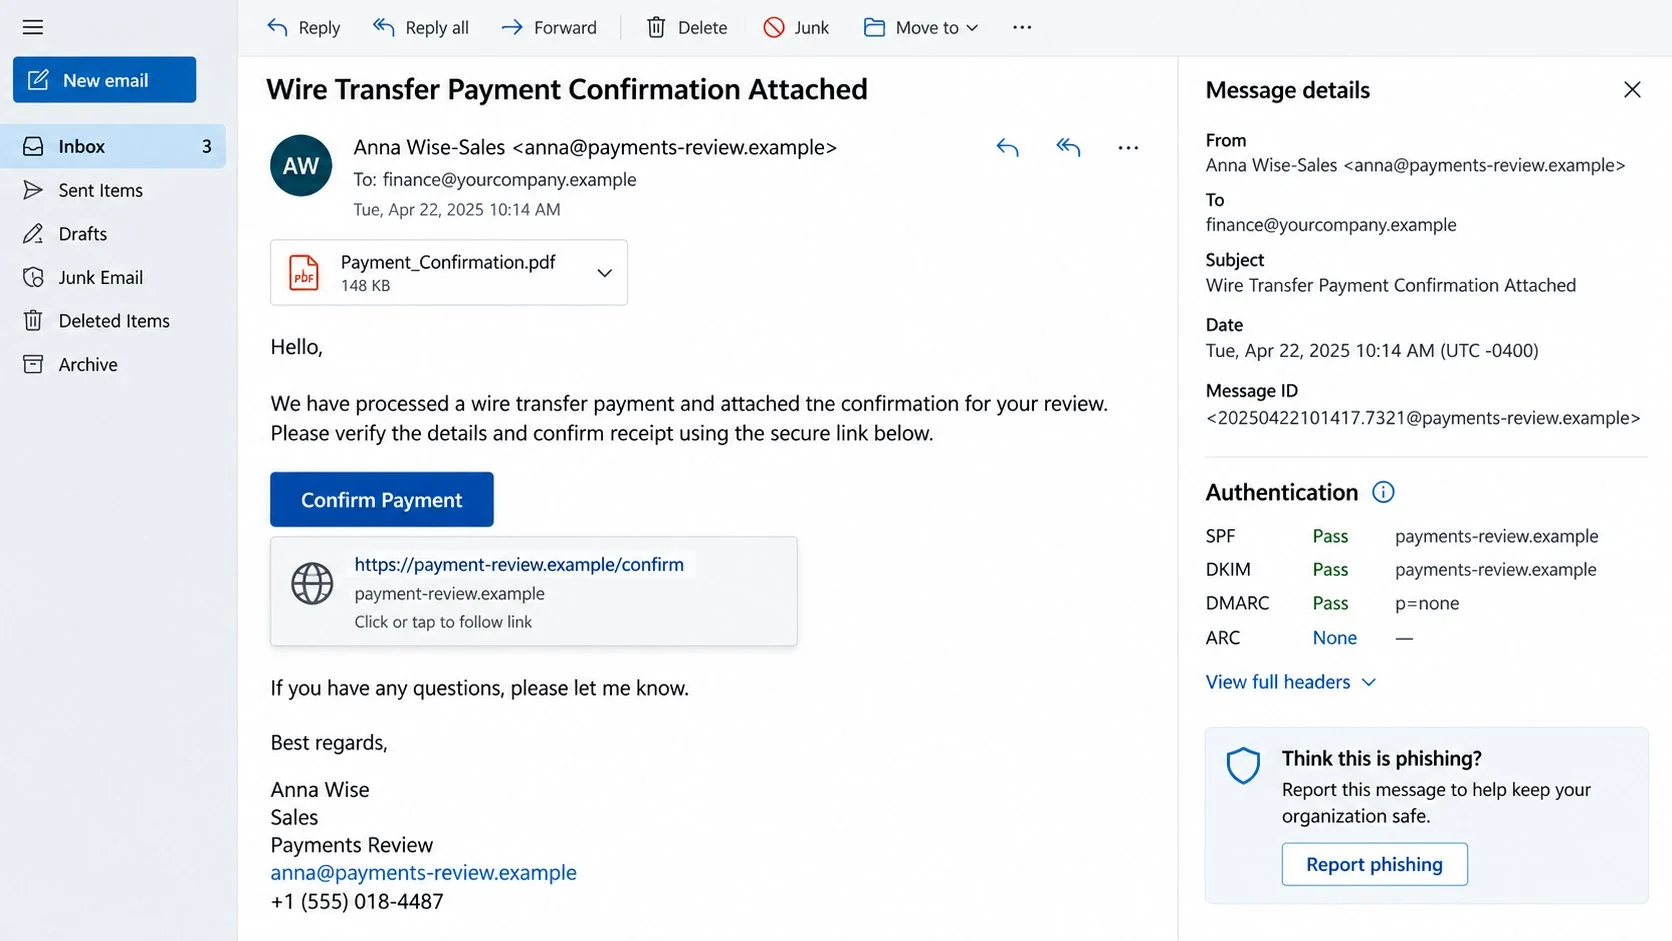
View the full sender address, Reply-To value, and authentication results. A mismatch can strengthen suspicion and help administrators trace delivery.
Passing SPF or DKIM does not prove a business claim is honest. Those checks can authenticate an attacker-controlled domain perfectly.
Likewise, a failure can result from forwarding or poor configuration. Combine header evidence with transaction records, known contacts, and the actual destination.
What to Do If You Fell Victim to the Wire Transfer Confirmation Email Scam
Separate the possible exposures. One concerns account credentials, another concerns downloaded files, and a third exists only if money or banking information was actually shared.
- Stop using the page and retain evidence.
Close the site without entering anything else. Preserve the message, full headers, visible link, and approximate time of your interaction.
In a company, contact security or IT through the documented incident channel. Fast reporting can help block the domain for colleagues.
- Replace any password entered into the form.
Use the real provider from a known-clean device. Choose a fresh password and update every account where the exposed one was reused.
Do not focus only on the payment system. The credential requested by this version belongs to the mailbox.
- Revoke access and inspect email settings.
End unknown sessions, remove unfamiliar devices, and review recovery methods. Check forwarding, delegates, filters, application passwords, and connected applications.
Look through sent and deleted folders for activity you did not create. Ask administrators to review audit logs when the account is managed.
- Warn finance contacts about possible impersonation.
Tell colleagues and relevant vendors that payment-related messages from the account may require secondary confirmation. Use a channel the attacker cannot control.
Be specific without causing panic. Explain whether credentials were entered and whether any unauthorized email has actually been found.
- Review genuine payments for unauthorized changes.
Check pending transfers, beneficiary records, approvals, and recent vendor-detail modifications. Escalate discrepancies to the bank and finance leadership immediately.
If money moved, request a recall promptly. Do not wait for the phishing investigation to finish before contacting the financial institution.
- Scan only when the interaction involved a file or software.
The documented route is credential phishing, but the subject references an attachment. Treat any downloaded item as a separate risk.
Run a complete Malwarebytes scan after opening or executing an unexpected file. A scan cannot invalidate credentials already typed into a website.
- Harden the browser against follow-up lures.
Remove notifications or extensions granted to the suspicious destination. Update the browser and delete any password it saved for the counterfeit page.
AdGuard may prevent some malicious redirects and advertisements. Continue verifying finance requests because no filter catches every newly created page.
- Report the hosted page and the email.
Use the mail provider’s phishing option and send the relevant evidence to your organization. The hosting platform can also receive an abuse report.
A report should identify the deceptive page, not accuse the legitimate platform of running the campaign. Hosted services are frequently abused by outsiders.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why This Is Not the Same as a Real Business Email Compromise
This message begins as broad credential phishing. It claims a transfer exists but directs the target to a generic webmail login.
Business email compromise often uses an already controlled mailbox or convincing impersonation to redirect a real payment. That may become a later stage here.
The distinction guides the first response. Exposed mailbox credentials require immediate account containment, even when no unauthorized transfer appears in the ledger.
If payment instructions changed, the incident has moved beyond a false confirmation. Finance staff and the bank should treat it as potential wire fraud.
Do not wait for certainty before preserving logs. Early evidence can show whether the campaign stopped at the login form or reached internal conversations.
Keep supplier verification procedures active during recovery. An attacker watching the inbox may exploit the disruption by sending a second, more specific request.
Require verbal confirmation for account changes and record who approved them. That control remains valuable after the exposed password has been replaced.
Frequently Asked Questions
Was a Wire Transfer Really Processed?
The email does not prove one. Check the bank and internal accounting systems through normal access routes.
Only a matching transaction record can establish that money moved. The sender’s text is not a receipt.
Why Does the Subject Say “Attached”?
The wording helps create an expectation of protected financial documents. Some copies may show a file, while others rely mainly on a button.
Never open an unexpected attachment merely to resolve that inconsistency. Verify the transfer independently first.
Is Anna Wise-Sales a Real Person?
The name is a persona used in the documented message. A display name alone cannot verify employment or authority.
Check a trusted directory or contact the organization separately. Do not rely on the signature’s telephone number or address.
Is Wix Studio Responsible for the Scam?
No evidence indicates that. The reported campaign abused a page hosted on its legitimate website-building infrastructure.
Platforms can remove reported content, but attackers may rebuild elsewhere. Recognize the credential request rather than memorizing one host.
What If I Clicked but Did Not Sign In?
Exit the page, report the email, and check whether anything downloaded. A visit does not automatically mean your mailbox password was stolen.
If you granted permissions or opened a file, address those actions separately. Otherwise, continue monitoring without assuming a takeover.
Should I Call the Bank?
Call if your records show an unfamiliar transfer, altered beneficiary, or actual disclosure of banking information. Use the bank’s verified number.
If only a mailbox password was entered, secure email first and alert the appropriate internal team. Review payments for related changes.
The Bottom Line
The Wire Transfer Payment Confirmation email scam turns a supposed finance document into a webmail password request. No button can substitute for a real transaction record.
Verify through accounting systems and known colleagues, then contain any exposed mailbox quickly. Treat platform branding as scenery, not proof of a payment.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.