

Apple users need to be aware of a new phishing email scam that is circulating, aimed at stealing Apple IDs and passwords. The deceptive email claims your Apple Pay account has been “temporary restricted” and will be permanently locked unless you verify your account details.
This article will provide an in-depth overview of how the “Your Apple Pay Has Been Temporary Restricted” email scam works, including a detailed analysis of the scam email itself. We’ll outline the warning signs to watch out for, provide step-by-step specifics on the scam process, and offer guidance on what to do if you fell victim.
Overview of the Scam
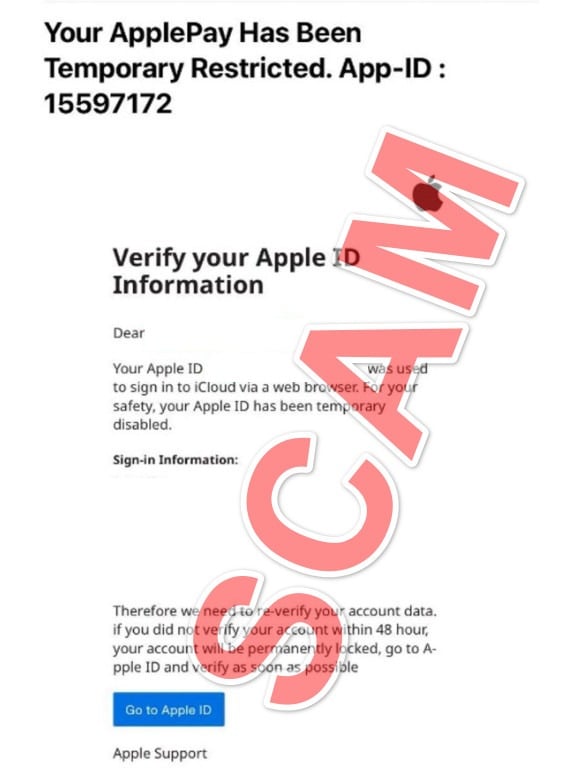
The “Your Apple Pay Has Been Temporary Restricted” scam starts with an email designed to look like it is from Apple. The email cleverly uses Apple branding elements like the logo and standard email format to make it seem legitimate.
The email states that your Apple Pay account has been temporarily restricted for security reasons. It goes on to say your account will be permanently locked in 48 hours unless you verify your account information. This creates urgency to click on the “Verify your Apple ID” button contained in the email.
Here is what the scam email usually says:
Your Apple Pay Has Been Temporary Restricted.
Verify your Apple ID Information,
Dear
Your Apple ID [mail] was used to sing in to iCloud via a web browser. For your safety, your Apple ID has been temporary disabled.Sign-in Information:
Date&Time
Operating System
Windows
IP Adress:
02.20.3.9Therefore we need to re-verify your account data. If you did not verify your account within 48 hour, your account will be permanently locked. Go to Apple ID an verify as soon as possible.
[Go To Apple ID].
The entire email is a scam aimed at stealing your Apple ID login credentials. Clicking the button leads to a fake Apple website. If you enter your Apple ID email and password, the scammers will gain access and fully compromise your account.
How the Apple Pay Account Restriction Scam Works
Here is a step-by-step breakdown of how the “Your Apple Pay Has Been Temporary Restricted” phishing scam operates:
1. You Receive the Deceptive Email
The scam starts with an email sent to your inbox that is designed to look convincingly like an official Apple communication.
The email appears to come from “Apple” and uses Apple Inc imagery including the Apple logo. The subject line reads “Your Apple Pay Has Been Temporary Restricted.”
The content of the email is modeled on Apple’s standard account notification emails. This familiar formatting lends the scam message credibility.
2. The Email Claims Your Apple Pay Account is Restricted
The body of the email states that your Apple Pay account has been “temporary restricted” due to suspicious activity.
It goes on to say that your account will be “permanently locked” in 48 hours unless you verify your account information immediately.
This threat creates urgency to take action before the short 48 hour deadline passes. Scammers use time limited offers or threats to hurry victims into making mistakes.
3. The Email Instructs You to Verify Your Account
The scam email includes a “Verify your Apple ID” button that supposedly leads to the Apple ID management site.
In reality, the button links to a fake Apple website that has been carefully designed to look exactly like the real Apple ID login page.
The sophisticated visual design tricks users into thinking they are on a legitimate Apple domain.
4. You Enter Your Apple ID Login Details
Once on the fake Apple website, you are prompted to enter your Apple ID email address and password to “verify” your account.
Since the site looks so convincing, many victims trust it and input their actual Apple login credentials.
Doing so gives the scammers direct access to the victim’s Apple account.
5. The Scammers Gain Control of Your Apple Account
After capturing your Apple ID and password, the scammers can now access your account and associated personal data.
They may change account details to maintain control, or sell the credentials on the dark web. Criminals can also use the access to commit identity fraud.
In addition to Apple Pay functions, the scammers can get into linked iCloud services, Find My iPhone, notes, photos, and more.
What to Do If You Fell Victim to the Apple Pay Restriction Scam
If you suspect you may have been compromised by the “Your Apple Pay Has Been Temporary Restricted” phishing attack, take the following steps right away:
- Change your Apple ID password – Updating your password prevents continued account access. Create a new, strong password that scammers can’t easily guess. Enable two-factor authentication for added security.
- Review account activity – Check for any unauthorized purchases, password resets, or device registrations. Look for access from new locations as an indicator of fraudulent activity.
- Check linked financial accounts – Examine any payment methods associated with your Apple ID for fraudulent transactions. Contact your bank or payment provider if you see suspicious charges.
- Deactivate and reactivate devices – Sign out of iCloud on all of your registered devices. Then reactivate your devices with your new password to lock out scammers.
- Contact Apple Support – Report fraudulent access to your account to Apple. They can take additional measures to secure your account and personal data.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About the “Your Apple Pay Has Been Temporary Restricted” Scam
1. What is the “Your Apple Pay Has Been Temporary Restricted” scam?
This is a phishing scam where targets receive an email claiming their Apple Pay account has been temporarily restricted and will be permanently locked unless they verify their account within 48 hours. The email contains a “Verify Your Apple ID” button that leads to a fake Apple website designed to steal Apple ID login credentials.
2. How can I identify the “Your Apple Pay Has Been Temporary Restricted” phishing email?
Warning signs include an urgent call to action, threats of account suspension, branded imagery like Apple logo, and a button to verify account information. Legitimate Apple emails would not threaten to lock accounts without allowing you to first verify identity.
3. What happens if I click the verification button in the email?
The button goes to a fake website impersonating Apple’s real ID login page. If you enter your Apple ID email and password, the scammers capture your credentials and gain full access to your account.
4. What do the scammers do once they have my Apple ID login?
The criminals use the stolen credentials to access your account, personal information, payment methods, and linked services like iCloud. They may change details to lock you out, steal data to commit fraud, or sell the credentials on the dark web.
5. How can I tell if a website is the real Apple login page?
Double check the URL for “apple.com” not “applesecurity.com” or variations. Real Apple sites have a green padlock and valid HTTPS certificate. Watch for poor grammar and low-quality graphics which signal a scam site.
6. What should I do if I entered my Apple ID on the fake site?
Immediately change your Apple ID password, deactivate linked devices, check for unauthorized activity, and contact Apple Support. Enable two-factor authentication for extra security against future attacks.
7. How can I protect myself from the Apple Pay restriction scam?
Carefully inspect any emails claiming to be from Apple. Avoid clicking links and instead go directly to Apple’s website. Use strong unique passwords and enable two-factor authentication.
8. Who is behind the Apple Pay phishing scam?
Cybercriminals and scammers operate these phishing attacks to steal personal data for financial gain. It’s difficult to identify the specific groups, as they use technical tricks to hide their identity and location.
9. Should I report scam emails impersonating Apple?
Yes, you can report phishing emails to Apple at phishing@apple.com. Make sure to avoid clicking any links as this verifies your email to scammers. Forward the scam message as an attachment.
10. How can I boost my online security against phishing?
Use a password manager, security keys like Yubikey, antivirus software, a VPN, privacy-focused web browsers, and caution opening links/attachments. Enabling MFA and online privacy tools will help protect your accounts.
The Bottom Line
The “Your Apple Pay Has Been Temporary Restricted” phishing scam is a serious threat all Apple users need to watch out for. The deceptive email is convincingly designed to look like legitimate Apple correspondence.
Scammers rely on creating urgency and fear to trick victims into clicking on the fake verification button and entering Apple login credentials on a phishing site. This gives them full access to compromise accounts.
Understanding how this scam operates can help Apple customers identify and avoid this insidious phishing attack. Always practice caution before clicking links or entering login information to prevent your personal data from ending up in the wrong hands.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.