


Your heart drops reading the subject line:
“Your System Has Been Hacked.”
With apprehension, you open the email. Immediately, a sinister unseen force seems to be tightening its grip around your throat.
The anonymous sender claims to have infected your computer with malware and secretly spied on your private activities through your webcam. They say they’ve recorded you in compromising situations – footage that could upend your life.
Now they’re demanding a hefty ransom in untraceable Bitcoin to destroy the videos. You have less than 3 days to comply or the incriminating content gets blasted across the internet and into the hands of authorities.
Feeling violated and terrified, paying the money seems like your only option for escaping total ruin. But is this faceless extortionist telling the truth? Can you trust them to actually delete the data if you give in to their demands?
This insidious email scam has been terrorizing countless recipients by weaponizing fear, uncertainty, and intimidation for profit. In this comprehensive guide, we’ll reveal the inner workings of the “Your System Has Been Hacked” phishing scheme and equip you to protect yourself.
Here’s everything you need to know about spotting the warning signs, guarding against manipulation, and fighting back against this brazen extortion tactic trying to scare you into submission.
Anatomy of The “Your System Has Been Hacked” Scam Email
The “Your System Has Been Hacked” scam message is carefully engineered to shock, unnerve, and ultimately extract money from recipients by holding their privacy and reputations for ransom. This is what makes it such an effective phishing tactic.
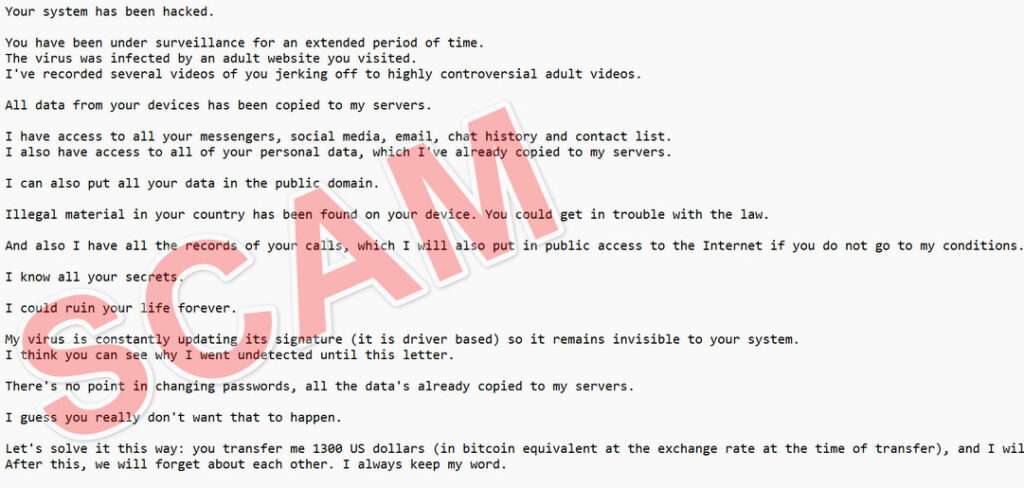
Here is how the “Your System Has Been Hacked” email scam looks:
Subject: Re:
Your system has been hacked.You has been under our surveillance for an extended period of time.
The virus was infected by an adult website you visited.
I’ve recorded several videos of you jerking off to highly controversial adult videos.All data from your devices has been copied to my servers.
I have access to all your messengers, social media, email, chat history and contact list.
I also have access to all of your personal data, which I’ve already copied to my servers.I can also put all your data in the public domain.
Illegal material in your country has been found on your device. You could get in trouble with the law.
And also I have all the records of your calls, which I will also put in public access to the Internet if you do not go to my conditions.
I know all your secrets.
I could ruin your life forever.
My virus is constantly updating its signature (it is driver based) so it remains invisible to your system.
I think you can see why I went undetected until this letter.There’s no point in changing passwords, all the data’s already copied to my servers.
I guess you really don’t want that to happen.
Let’s solve it this way: you transfer me 1300 US dollars (in bitcoin equivalent at the exchange rate at the time of transfer), and I will immediately remove all this dirt from my servers.
After this, we will forget about each other. I always keep my word.My bitcoin wallet for payment: 116A33YsSrr8xCccVYkHnzmAdpK2Q3qVFk
If you don’t know how to transfer money and what Bitcoin is. Use Google.I give you 50 hours (a little over 2 days) to complete the payment.
I get an automatic notification when I read this email. Similarly, the timer will automatically start after you read the current email.If payment is not confirmed after the given time, all data will be published on the public internet, sent to law enforcement agencies and sent to all your contacts.
Don’t waste your time sending me a reply because it won’t work (the sender address is automatically created).
Furthermore, do not try to complain anywhere because this text and my bitcoin address cannot be traced anyway.Do not try to complain anywhere, as the wallet is untraceable, the mail from where the letter came from is also untraceable and created automatically, so there is no point in writing to me.
Do not attempt to contact the police or other security services, otherwise your data will be published.
Let’s examine the key elements that make up this social engineering and fear-based scam:
Malware Infection Claims
The email claims that clicking on a malicious link or visiting an adult website led to sophisticated malware being downloaded onto the recipient’s computer. This malware supposedly gave the attacker remote access, control over the webcam, and ability to monitor all activity without detection.
Compromising Video Threats
The sender threatens that through the secret malware infection, they’ve recorded videos of the recipient in compromising sexual situations as blackmail material. This creates feelings of violation, shame, and urgency to comply with demands.
Data Breach Assertions
The email claims that the malware has copied over sensitive personal information from the recipient’s devices and online accounts, including contact lists, messages, and browsing history.
Reputational Ruin Warnings
The sender threatens to not just leak the adult videos, but also expose personal secrets and data to the public internet as well as send it all to the recipient’s friends, family, coworkers, and authorities.
Untraceable Bitcoin Ransom Demand
The extortionist demands payment equivalent to $1,300 or more in untraceable Bitcoin within 50 hours. This limited window adds pressure and limits careful thinking.
Anonymity and Encryption Techno-Babble
The email warns that contacting authorities is futile since the sender address, malware, and Bitcoin wallet can’t be traced. This is further intimidation to deter reporting.
By combining intrusion, surveillance, blackmail, extortion, and public shaming, this scam is fine-tuned to overwhelm critical thinking and compel victims to pay the ransom out of desperation. But understanding the various psychologically manipulative elements at play is key to defusing their power.
Spotting Red Flags in “Your System Has Been Hacked” Scam Emails
Now that you know the blueprint of this phishing scam, here are key warning signs to help detect “Your System Has Been Hacked” extortion attempts:
- Generic greetings like “Your system has been hacked” rather than your name. Scammers blast out emails en masse.
- Claims of adult site usage and video recording that can’t be substantiated. Sensational threats devoid of proof.
- Contradictory claims of total device access yet limited to just webcam spying and data copying. Why not more if fully hacked?
- Broken English or awkward phrasing. Many scammers operate internationally.
- Demand for payment via untraceable cryptocurrency only. Real hackers would hesitate to reveal their wallets.
- Threats of public shaming and leak promises that can’t be fulfilled. Bluffs with no intent or ability to actually post data.
- Countdown timers and high-pressure threats designed to overload critical thinking with haste and panic.
- Claims that contacting police is futile. Scammers don’t want victims talking to authorities.
- Assertions of total technical prowess yet amateur mistakes like sender email addresses that can indeed be traced.
- No actual evidence provided of videos, access to accounts, or breached data. Lots of bark with no bite.
Seeing through the gaping holes in this shoddily constructed deception helps dispel the smokescreens of technobabble designed to bewilder recipients and short circuit logic.
How The “Your System Has Been Hacked” Email Scam Works
The “Your System Has Been Hacked” scam is carefully orchestrated to manipulate emotions in order to override reason and obtain ransom payments. Here is an in-depth look at what’s happening behind the scenes:
1. Scammers Purchase Stolen Email Credentials
Criminals acquire massive databases of usernames and passwords from the dark web and leaked data breaches. This gives them a fertile starting point to target potential victims.
2. Malware Infection Story Fabricated
A fictional narrative is crafted involving the recipient’s device being infected with sophisticated malware providing secret surveillance access via the webcam.
3. Adult Videos Falsehood Spun
Imaginary illicit videos recorded through the fictional malware are described in graphic detail, intended to disgust and mortify the recipient.
4. Data Breach Embellished
For extra intimidation, the email claims that personal files, browsing history, and contact info have also been stolen, even without any hacking actually occurring.
5. Extortion Amount Calculated
A ransom amount is chosen, often between $500-$1500 worth of Bitcoin. Not so large as to seem implausible, but substantial enough to turn a profit.
6. Threats Tailored to Recipient
The scammer personalizes threats for maximum impact based on demographic data associated with the recipient’s stolen credentials.
7. Deadline Timer Initiated
A roughly 2-3 day deadline elevates urgency and limits objective scrutiny. Psychological pressure overtakes reasoned discernment.
8. Bitcoin Payment Directions Provided
Demand for anonymous, irreversible cryptocurrency payment locks in funds for the scammers and hides their trail once paid.
9. Intimidation to Deter Reporting
The email discourages contacting police and claims they won’t identify the criminals anyway. This is reverse psychology to protect the scam.
10. Emails Sent En Masse
Spoofed emails are spammed out to stolen email lists by the thousands, using botnets and malware to scale up the number of potential victims targeted.
11. Criminals Collect Ransoms
Once scared recipients pay up, the scammers withdraw and launder the Bitcoin payments, disappearing without releasing anything.
Understanding how calculated psychological manipulation, deception, and intimidation fuel this scam makes it less frightening. Knowledge dispels the technobabble smoke and mirrors.
Protecting Yourself From “Your System Has Been Hacked” Extortion Threats
If you receive a suspicious email claiming you are being watched or monitored, here are tips to protect yourself from being deceived, panicked, and exploited:
1. Don’t Open Unsolicited Attachments or Links
Opening unfamiliar email attachments or links risks malware infection. Be extra cautious of anything unprompted.
2. Scan Devices for Malware
Run comprehensive antivirus scans to check for any signs of actual malware or breaches. But don’t expect anything real to be found.
3. Change Passwords and Enable Two-Factor Authentication
Reset account passwords as a precaution. Enable 2FA for added login security on sensitive accounts. This further safeguards you.
4. Don’t Reply to the Email
Replying could confirm your email as active. Instead, report the message as spam/phishing to your email provider.
5. Watch for Further Suspicious Activity
Monitor financial statements and account activity closely for any signs of fraud. But chances are criminals don’t have anything real.
6. Never Pay Extortion Demands
Paying ransoms encourages further extortion attempts and funds criminal enterprises. Stand your ground.
7. Contact Authorities If Truly Concerned
The email tries to deter police involvement, which is a red flag. Law enforcement can provide guidance dealing with cyber threats.
Remaining calm and avoiding overreaction is key to logically recognizing the manipulative scare tactics in phishing scams like this. Don’t let brazen claims of surveillance bully you into hasty compliance.
What To Do If You Already Paid The Your System Has Been Hacked” Email Scam
If you already fell victim and paid the ransom demanded in the “Your System Has Been Hacked” email scam, here are steps to take:
1. Contact Your Bank
If you paid the ransom recently via bank account, contact your bank immediately to try stopping or reversing the transaction before the funds are withdrawn. Act quickly, as time is critical.
2. Report Fraud to Cryptocurrency Exchange
If you paid in Bitcoin, report the scam to the cryptocurrency exchange you used so they can attempt tracking the wallet address and potentially freeze the funds. The sooner the better.
3. Monitor Accounts Closely
Carefully monitor bank and credit card statements for any further suspicious charges. Scammers may attempt more fraud once they have secured an initial payment.
4. Reset All Account Passwords
Change passwords on all email, social media and financial accounts as a precautionary measure. Use unique complex passwords for each account. Enable two-factor authentication anywhere possible for added security.
5. Run Antivirus Scans
Conduct comprehensive malware scans on all computers and devices used to make the payment. Quarantine or delete anything suspicious found. Scammers may have accessed more than they claimed.
6. Place Fraud Alerts and Credit Freezes
Put a fraud alert on your credit reports and consider freezing credit reports to protect your identity and prevent fraudulent accounts from being opened.
7. Avoid Further Extortion Payouts
Disconnect from the email account used and do not respond to any further demands for money. The scammers won’t actually release anything since they don’t have anything real to begin with.
8. Report the Scam to Authorities
File a complaint with the FBI’s Internet Crime Complaint Center at www.ic3.gov and notify local law enforcement. This helps authorities track and prosecute cyber extortion scams.
9. Seek Legal Counsel if Needed
For serious extortion threats, consider consulting an attorney experienced in cybercrime matters for guidance on handling threats and minimizing potential damages.
10. Learn from This Experience
Reflect on missteps that allowed you to be deceived. Implement stronger security habits going forward and share your experience to help others avoid the same pitfalls.
Stay vigilant following any cyber extortion incident and take proactive measures to protect your identity, accounts, and data from further misuse. With caution and wisdom, you can recover both financial and peace of mind.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions About the “Your System Has Been Hacked” Email Scam
1. What is the “Your System Has Been Hacked” email scam?
The “Your System Has Been Hacked” scam is a type of sextortion phishing attack where cybercriminals send an email claiming to have infected your device with malware that gave them access to spy on you through your webcam. They threaten to release adult videos and personal data unless a ransom is paid.
2. What are the key characteristics of the scam email?
- Claims of secret surveillance through malware and webcam access
- Threats to release recordings and personal information
- Demand for ransom payment in Bitcoin within a short deadline
- Warnings not to contact law enforcement
- Intimidation tactics implying complete monitoring
3. What is the typical ransom amount demanded?
The ransom demands are often around $1,000 to $2,000 worth of Bitcoin. The extortionists want to maximize profit while still making the amount seem plausibly affordable.
4. How do criminals carry out this scam?
They send mass emails to stolen credential lists purchased on the dark web. Deception and fear-mongering tricks victims into paying the ransom, when no actual hacking takes place.
5. What persuasive tactics does the email use?
- Claims of compromised personal privacy to create feelings of violation
- Graphic descriptions of adult videos tailored to shock and shame
- Threats to send data to friends/family for maximum embarrassment
- Short deadline to eliminate careful deliberation
- Demands for untraceable crypto payment
6. Why Bitcoin ransom payment?
Bitcoin enables fast, anonymous payments perfect for quickly collecting ransoms without being tracked or identified. Fiat currency is more traceable and reversible.
7. Are the threats in the email real?
No, the threats of having intimate videos and data are a complete bluff. The scammers do not actually have anything to release about the recipient. Their goal is to fabricate threats that spark panic.
8. Should I pay the ransom?
No, you should never pay the ransom demands. This will likely result in more extortion attempts in the future. Without anything real to release, paying only enables further predatory scamming.
9. What should I do if I get the scam email?
Do not respond to the email. Report it as phishing/spam. Run malware scans as a precaution. Change account passwords and enable two-factor authentication where possible. Watch for further scam attempts.
10. What if I already paid the ransom?
If you fell victim, contact authorities to report it. Enhance account security, monitor statements closely for further fraud, and avoid any additional extortion payouts demanded.
Staying vigilant against phishing and protecting your data makes you a much harder target for “Your System Has Been Hacked” extortion scammers seeking easy paydays through deception.
The Bottom Line on Defeating “Your System Has Been Hacked” Scams
Being targeted by a ominous “Your System Has Been Hacked” email can certainly be jarring and distressing. But reacting with undue haste or gullibility only feeds the scammer’s intentions.
When faced with such brazen scams built on manipulation, the most powerful weapon is a level head. Logic dispels the fiction woven to exploit fears. Scrutiny unravels the web of deception. Patience defuses the pressure tactics pushing rashness. And courage steadies the nerves rattled by imagined threats of ruin.
While the email’s sinister development and looming deadline are crafted to seize control of your thinking, you maintain command of your mind, values and actions. Take a breath. Step back. Give the content and demands thoughtful analysis rather than a panicked response.
Talk to trusted confidants to restore perspective. Let rationality intervene against mind games seeking to obscure truth with chaos. Keep your wits and don’t relinquish them cheaply.
The sensational claims of surveillance dissolve under the light of honest scrutiny. The posturing giants of tech prowess shrink when boldly challenged for proof. Even Goliath can be felled by a steady hand and a few smooth stones of reason.
Stay vigilant, but fear not.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.