

A Security Center email says your password is nearly expired. One button offers to keep it unchanged, which sounds easier than dealing with another account update.
When your inbox holds appointments, bills, and work, losing access feels inconvenient at best. Before choosing that shortcut, take a closer look at the request.
Overview
A convenient offer attached to an alarming warning
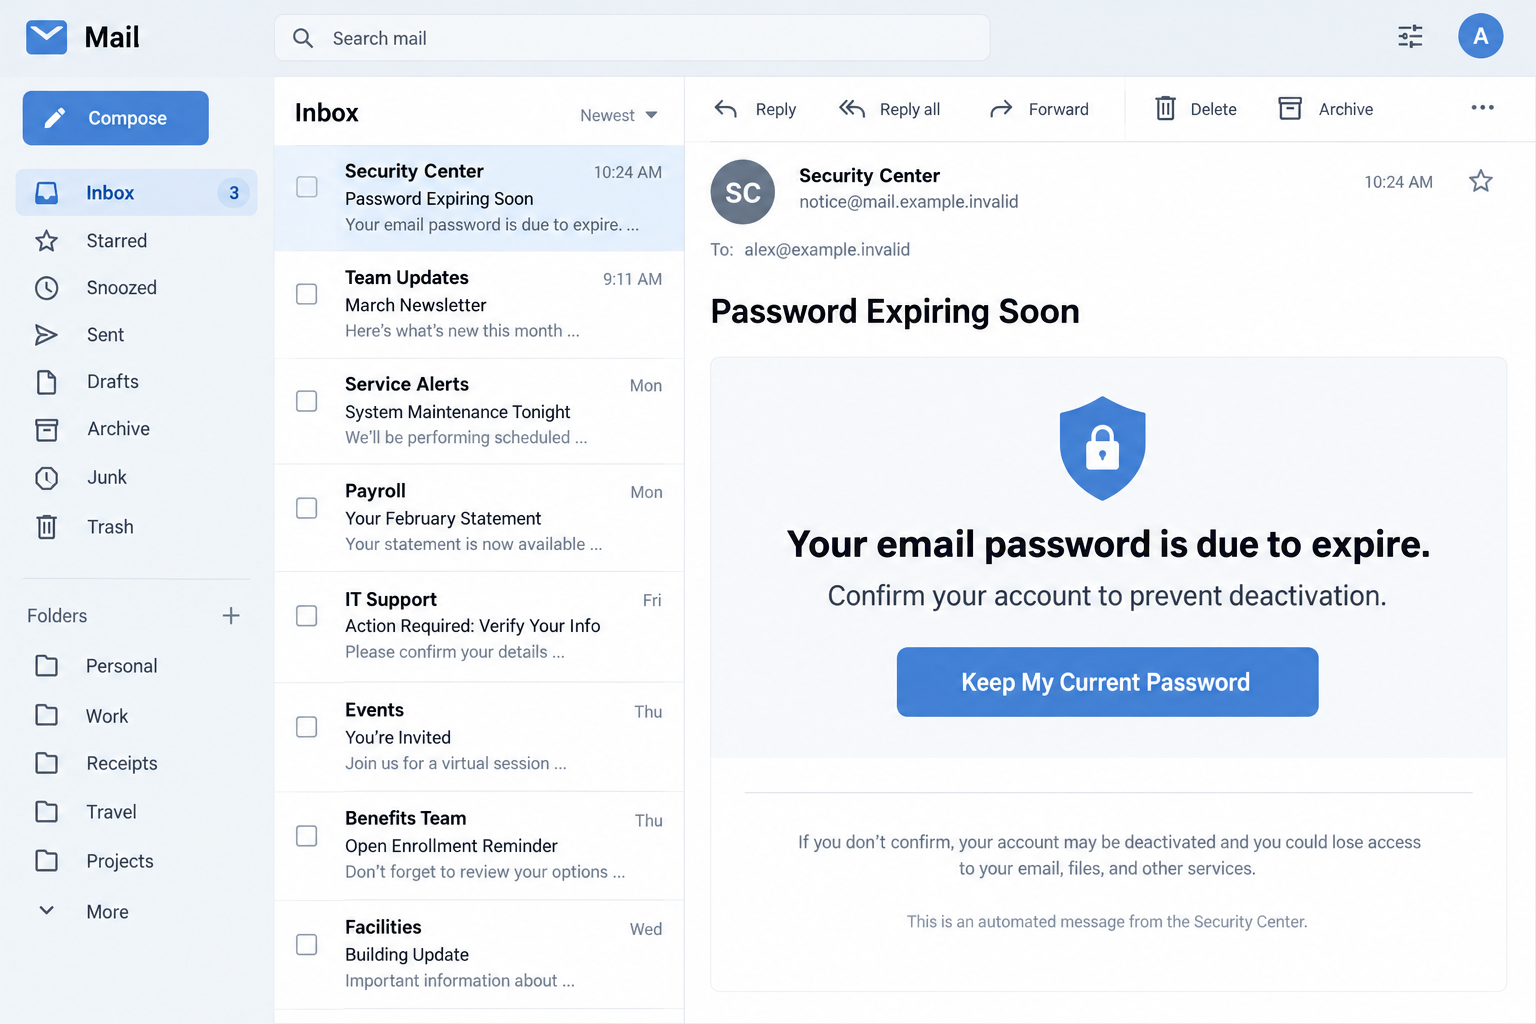
The Security Center Password Expiring Soon email scam combines an account-deactivation threat with an invitation to preserve the password you already use.
That pairing matters. You’re not being asked to invent a new secret or troubleshoot a complicated error. The message offers what looks like a quick administrative confirmation.
The campaign’s published email uses a password-expiration date and a button labeled Keep My Current Password. Following its instruction leads toward credential phishing, not legitimate account maintenance.
The familiar sign-in belongs to the deception
A reported destination used vocational-white-5xciizxu.edgeone[.]dev and displayed an imitation Gmail login. Neither its hosting platform nor Google’s branding makes the request authorized.
The specific hosted page now returns a not-found screen. Its earlier appearance should not be confused with a working form you can inspect today.
The email illustration contains fictional account information. It helps explain the request without presenting an invented recipient or reconstructed login as evidence of an actual compromise.
The password is the valuable item
This is a phishing warning about the message and its destination, not an accusation against your email provider. Real account policies still need independent checking.
The safest response is to open your usual service yourself. If you already disclosed a password, concentrate on restoring control of that account.
- A department name printed above an email does not identify its sender.
- A promise to keep a password can still involve collecting that password.
- A provider logo does not authenticate an unrelated sign-in address.
- Account recovery and device cleanup address different kinds of exposure.
Why Keeping Your Password Sounds Like the Safe Choice
Most people associate password security with changing something. This lure takes the opposite approach: it asks you to do a little work so nothing changes.
That can feel reassuring. You won’t need to update a mail app, remember another secret, or risk getting locked out during a busy afternoon.
But convenience does not change who receives the information. A false confirmation page can collect the existing password just as easily as a false password-reset page.
Picture receiving the notice while waiting for a medical appointment reminder. Your attention is on keeping the inbox available, not on evaluating a new website.
The sender benefits from that distraction. The claimed administrative task makes the password prompt seem like a necessary detail rather than a separate decision.
There is no need to argue with the warning or reply asking for reassurance. The sender would still control the answer.
Instead, move the question into the account you normally use. An independently opened security page gives you a trustworthy place to check for an actual task.
If your employer manages the account, ask its established help desk. Workplaces can have password policies that differ from personal email services.
A real policy is not an excuse to follow an unverified shortcut. Your administrator can explain the correct procedure without asking you to surrender a secret to this email.
How the Security Center Password Expiration Scam Works
Step 1: The message turns a date into a reason to act
The email presents expiration as an approaching interruption. The reader is supposed to treat the date like a deadline generated by the service.
A printed date is only part of the message, however. It is not evidence that the actual account has an expiration event scheduled.
Compare the request with your account’s normal behavior. Have you previously managed passwords through an employer portal, a hosting account, or the provider’s own security settings?
That existing route matters more than a new notice’s appearance. The sender should not get to redefine how your account is administered.
If the dates do not make sense, preserve that discrepancy for reporting. Do not assume a sensible date would make the instruction safe.
Step 2: The button offers an apparently harmless exception
Keeping an existing password sounds less consequential than changing one. The wording encourages you to think of the click as accepting a convenience.
The destination can still be unrelated to your provider. Button labels and browser addresses are different pieces of information.
On a computer, inspect the link without opening it if your mail application supports that. Look for the actual domain, not a familiar word anywhere in the address.
A long address may contain your email or your provider’s name as ordinary text. That does not grant the site permission to receive credentials.
When the address is unfamiliar, leave the button alone. A real account task should be manageable through a trusted login you opened independently.
Step 3: A provider-themed page asks for the secret
The reported form copied a recognizable sign-in style. That design tries to make the transition from email notice to authentication feel ordinary.
The essential question is not whether the colors look right. It’s whether the actual provider controls the page where you would type your password.
Google’s phishing advice recommends visiting the service directly when a questionable message leads to a password request.
If your password manager doesn’t recognize the page, pause. Do not manually paste a saved credential merely to get past the inconvenience.
It may be refusing because the website differs from the account’s saved address. That’s a useful warning, not an obstacle to defeat.
A page with your address already filled in can also be misleading. Knowing the mailbox address is different from having a legitimate relationship with its owner.
Step 4: The disclosed password can be tried elsewhere
An attacker can attempt to use the secret against the real account. Whether access succeeds depends on your protections and the information they obtained.
The website does not need to complete the promised task for disclosure to matter. A loading error can appear after information has already been received.
Additional prompts deserve separate attention. If you supplied a verification code, accepted an access request, or shared recovery details, include each action in your recovery notes.
Those are possible complications to assess, not confirmed prompts in every version of this campaign. Your response should follow what actually happened to you.
A reused password creates another concern. Accounts unrelated to email may accept the same secret, even though the lure never mentioned them.
Step 5: An apparently normal inbox can conceal continuing access
You may still receive mail and send messages after an unauthorized login. Visible usability is not a complete account-security check.
An intruder could change recovery settings, authorize another application, or arrange a way to keep reading selected correspondence. Available controls vary by provider.
Reviewing those settings is more useful than repeatedly refreshing the inbox to see whether something looks wrong.
For a shared work mailbox, the administrator may have records you cannot see. Tell the team which credential was exposed and when the interaction occurred.
The recovery goal is to remove unauthorized access, not simply to stop the warning email from appearing.
Check the Account Without Following the Notice
Use the service you already recognize
Start from a saved bookmark, installed mail application, or the provider’s established website. Do not obtain a new support route from the suspicious message.
Check recent security activity and pending account instructions. If there is a genuine problem, address it inside that trusted environment.
Some organizations place password management in a separate workplace portal. Ask your usual administrator where that portal is rather than guessing from a branded login screen.
You can investigate an account warning without proving every detail about its sender. Independent access lets you act safely while preserving the questionable message.
Distinguish a personal inbox from a managed account
Your email address may use a familiar provider while the account belongs to an employer or school. That changes who controls policy and recovery.
Do not apply a coworker’s password instructions to a personal account. Likewise, don’t change organization-wide settings to resolve a notice sent to one mailbox.
Tell support whether the exposed secret protected only email or also signed you into other workplace services. That distinction helps the team determine the response.
A narrow description avoids both panic and understatement. You know what you entered even if you don’t yet know whether an attacker used it.
Save useful details, not another risky visit
Keep the original message, visible destination, and approximate interaction time. Full email headers can help your provider investigate the sending route.
Don’t reopen the page to discover whether the form still works. Its disappearance would not restore secrecy to information already submitted.
If the site downloaded a file, record its name and whether you ran it. Account phishing and malicious software require different follow-up actions.
Never include passwords or current verification codes in a support email. Describe the disclosure without redistributing the secret.
What to Do if You Have Fallen Victim to This Scam
Stop the confirmation attempt. Close the unfamiliar page and ignore requests to try another password, browser, or security code.
If you only received the email, report it as phishing. Receipt alone is not a reason to assume your device or account has been compromised.
Change the exposed credential through the real account. Use a trustworthy device, especially if the suspicious page persuaded you to install software.
Choose a replacement you haven’t used elsewhere. If access is lost, follow the provider’s recovery process rather than buying help from the warning’s sender.
Review signed-in access. Examine unfamiliar devices and sessions, and use the service’s available controls to end unauthorized access.
For managed accounts, contact IT promptly. Some session and application controls are only available to an administrator.
Check how the account can be recovered. Review backup addresses, phone numbers, authentication methods, and permissions belonging to connected applications.
Correct unauthorized changes through trusted settings. Preserve relevant evidence first if your organization’s incident team needs it.
Inspect mail-handling settings. Look for unfamiliar forwarding destinations, filters, or rules affecting security messages and sensitive conversations.
Check recent sent mail too. If someone used the inbox to contact others, those recipients may need a warning through another established channel.
Replace reused passwords on important services. Prioritize accounts containing money, personal records, or recovery access to other accounts.
Enable supported multifactor protection. It adds a barrier to future misuse, but doesn’t undo messages or information an intruder already copied.
Assess any software exposure. If you executed a download, use genuine Malwarebytes to check a personal device, or follow your employer’s approved security response.
AdGuard can reduce some malicious advertising during browsing. It cannot revoke a stolen account session or turn an untrusted sign-in into a legitimate one.
Keep a recovery record and escalate real losses. Save account alerts, affected conversations, and any payment details related to the incident.
Contact the relevant financial institution if money moved. Update trusted support if unauthorized activity returns after your initial account cleanup.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
When a Password Change Is Necessary, Use a Real Process
Rejecting this email doesn’t mean passwords never need attention. A disclosed, reused, or administrator-managed credential may genuinely require replacement.
The difference is where the instruction comes from and where you carry it out. A trusted account process doesn’t depend on this sender’s button.
If several devices use the old password, update their saved credentials after securing the account. Don’t interpret every later sign-in error as another attack.
Write down which applications need adjustment without recording the password itself. That makes recovery easier when a desktop client and a mobile app use different settings.
If unexpected verification prompts continue, deny requests you didn’t initiate and notify support. Don’t approve one just to stop the interruptions.
Keep the same distinction throughout: restoring normal operation is one task, confirming that unauthorized access has ended is another.
Frequently Asked Questions
Is the Security Center Password Expiring Soon email trustworthy?
The campaign described here is phishing. Confirm any actual password requirement through your established account or administrator, not the notice’s button.
Can a genuine workplace password expire?
Yes, organization policies can require changes. That possibility does not authenticate this email or authorize its unrelated login destination.
Does keeping my current password avoid sharing it?
No. If the unfamiliar page asks you to enter the password, you’re still disclosing it. The button’s reassuring wording doesn’t change that.
What if the fake page is already gone?
Leave it alone. If you submitted credentials earlier, recover the account anyway. A not-found page cannot tell you whether information was collected.
Is a failed sign-in proof that my password stayed safe?
No. Treat the secret as exposed if you typed it into the untrusted form. An error message does not establish what the page recorded.
Will scanning my computer change the stolen password?
No. Security scans address software threats. Credential replacement, session review, and mailbox checks must happen through the actual account service.
The Bottom Line
Do not use the Security Center expiration notice to preserve your password. Check the real account directly and leave the unsolicited shortcut unused.
If you already entered a secret, replace it and review remaining access. A working inbox is reassuring, but it isn’t the end of account recovery.








