

A page offers free Red Kitten Crew tokens and asks you to check your wallet’s eligibility. The claim takes a moment, and the opportunity looks easy to miss.
Before opening your wallet, slow down. The important part of an airdrop invitation isn’t how attractive the reward looks, but what happens when you try to claim it.
Overview
The offer borrows a token identity
The Red Kitten Crew RKC airdrop scam promotes a supposed token distribution associated with the Solana ecosystem. A reported page used tokendisbursement[.]xyz.
Its promise of free tokens was paired with wallet-selection controls. The campaign has been identified as a wallet-draining lure, not an authenticated distribution you should claim.
That warning concerns the fraudulent invitation. A recognizable token name, ticker, or listing somewhere else would not establish that this claim portal is authorized.
The wallet request is where the risk becomes practical
Connecting an ordinary wallet does not, by itself, universally authorize spending. The danger depends on transaction approvals, delegated permissions, signatures, or secrets disclosed during the interaction.
Do not assume every wallet or network handles these requests identically. Examine what your actual wallet asked you to approve, not just the website’s friendly button.
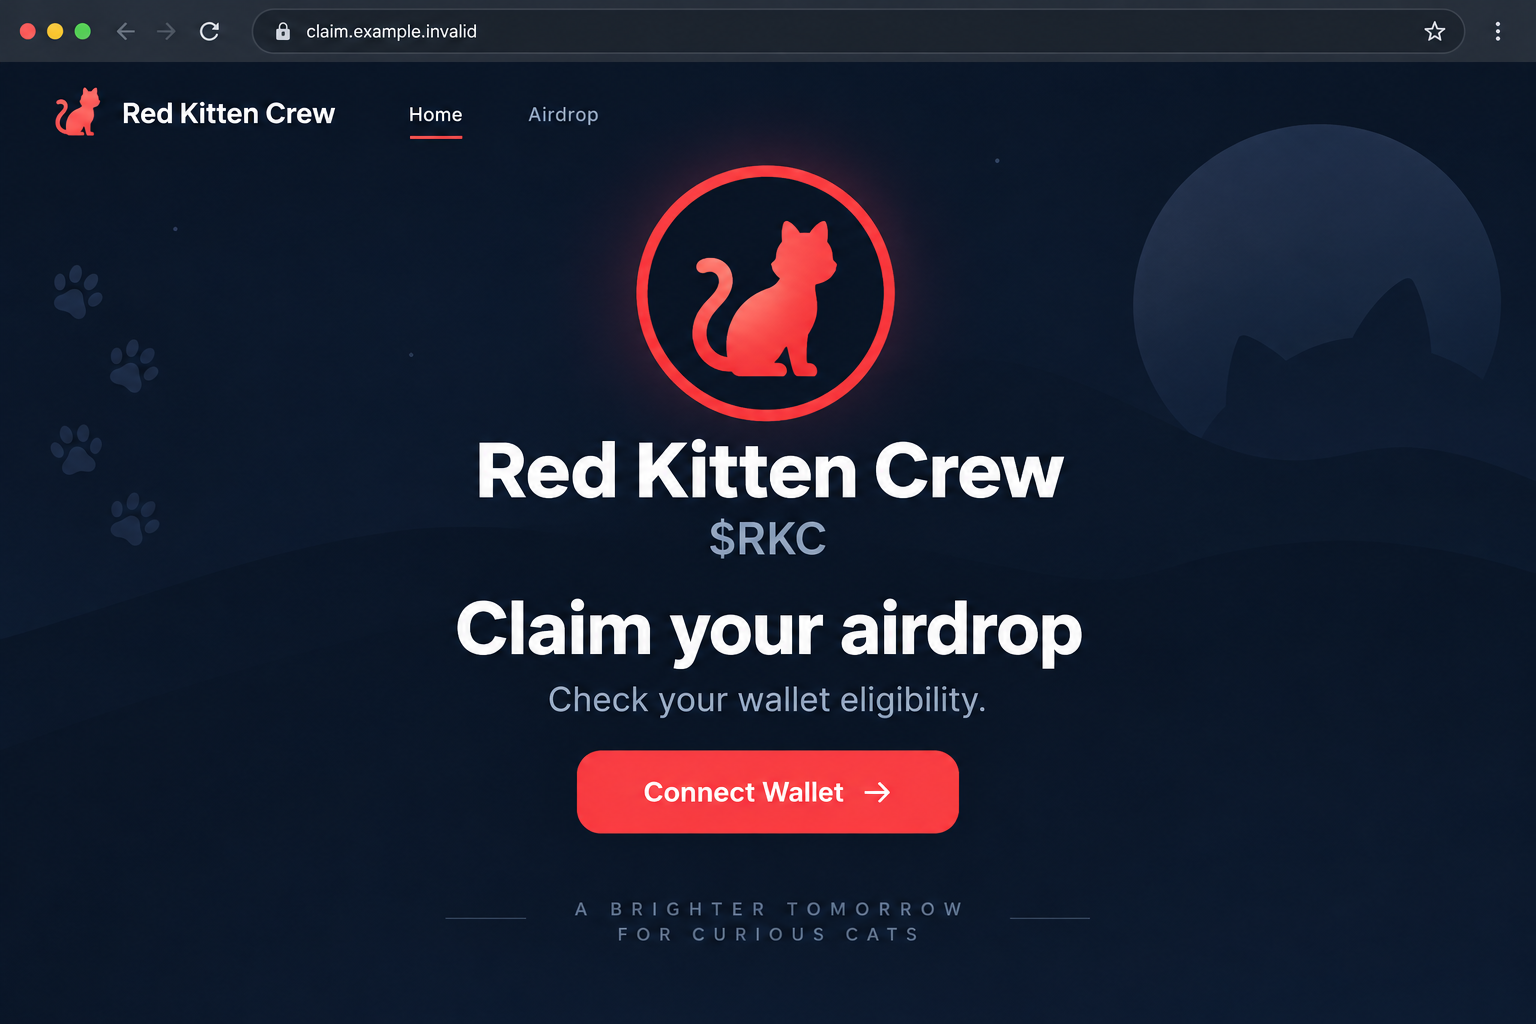
The lead illustration uses a nonfunctional address and no real wallet data. It depicts the offer’s basic premise, not a captured transaction or proof of a loss.
Leave the claim unclaimed and review any authorization you gave
Wallet dialogs can vary, and an older description cannot tell you exactly what you approved. Use your own wallet’s records to establish that.
If you encountered it, do not keep trying to reach the portal. Use your genuine wallet application to assess connections, transactions, and remaining assets.
- A free-token promise is not permission to transfer assets already in your wallet.
- A wallet logo shows compatibility or appearance, not endorsement of the website.
- Disconnecting an app and revoking spending authority are different actions.
- A recovery phrase must never be entered into an airdrop page.
A Free Reward Can Distract You From an Expensive Approval
The offer directs attention toward what might arrive. The wallet prompt should direct your attention toward what could leave.
Those aren’t the same question. A claim page can promise an allocation while requesting an action unrelated to receiving it.
Suppose a page announces an eligible reward and then your wallet displays an unfamiliar transfer. The reward’s attractiveness doesn’t explain or justify that transfer.
You can reject the request and leave the supposed bonus behind. Missing an unverified promotion is preferable to handing over authority you don’t understand.
Urgency makes that choice harder. A deadline can turn a normal identity check into something that feels like wasting an opportunity.
But there is no useful shortcut around knowing who operates the offer. A timer cannot answer that question for you.
Community language can also lower your guard. A page that speaks about holders, eligibility, and distributions can seem like part of a project you already recognize.
Evaluate the invitation separately from the token. Recognizing the name is only the beginning of checking the claim.
For the same reason, don’t ask a person in the page’s own chat to authenticate it. Their response may remain inside the same deceptive operation.
How the Red Kitten Crew Airdrop Scam Works
Step 1: The promotion introduces a distribution you weren’t expecting
The reader encounters a promise of free tokens and a route to claiming them. Promotional channels can vary, so do not assume every encounter began with the same post.
The page’s token identity supplies a familiar subject. That can make the invitation feel connected to previous community activity or a token listing.
Look for independently authenticated project communication before accepting the event. A link from an unfamiliar reply or direct message should not establish the claim portal.
A friend’s forwarded link also needs checking. They may be sharing an opportunity in good faith without having verified its operator.
Step 2: Eligibility becomes the reason to open the wallet
The first task appears to be checking whether your account qualifies. That sounds less consequential than sending money or making an investment.
However, the website still chooses what to request next. A harmless-sounding first action cannot authenticate the remainder of the interaction.
Before opening the wallet, establish the actual destination and purpose. A generic distribution domain doesn’t become official merely because it displays a token ticker.
If those details cannot be established, stop at this stage. You do not need to inspect a malicious transaction personally to decide against an unverified reward.
Step 3: Familiar wallet choices make the page feel supported
A selection dialog can display well-known wallet brands. That familiarity can be mistaken for an approval of the site by those companies.
The list only identifies ways the page wants you to interact. It does not mean a wallet provider examined or endorsed the offer.
Use the wallet you already installed through a trusted route. Never download a replacement extension or import your account because the claim page says compatibility is missing.
A hardware wallet also requires attention to the action on its screen. Its usefulness depends partly on whether you approve an unwanted request.
Do not type a recovery phrase to fix a failed connection. That disclosure would change the incident from a questionable app interaction to compromised wallet control.
Step 4: A claim instruction can conceal asset-moving authority
The wallet may present a transaction or permission request after the connection. Read that prompt as a separate decision.
Ask whether the action matches receiving an airdrop. A transfer of existing assets to an unfamiliar recipient is not explained by the word claim.
Depending on the network and wallet, a harmful authorization may permit immediate movement or continuing access. Don’t generalize one network’s approval model to all others.
MetaMask’s connection explanation distinguishes sharing an account address from granting authority to move tokens.
That distinction prevents unnecessary panic after a simple connection, while keeping attention on the more dangerous approvals that can follow.
If the prompt is unclear, reject it. Do not approve first and plan to investigate afterward.
Step 5: The response must follow the actual wallet activity
If a harmful transfer is authorized and confirmed, closing the browser cannot undo it. The wallet’s records are more useful than the claim page’s status message.
A page can continue showing a promised reward after assets leave. Its balance display is not a substitute for checking the relevant blockchain activity.
Record transaction identifiers and destinations. Distinguish confirmed activity from pending requests or a displayed allocation that never existed in your wallet.
Then address whatever authority remains. Disconnecting, reviewing permissions, securing a compromised secret, and reporting a theft solve different parts of the incident.
Check the Portal, Not Just the Token Name
Look for an independently established announcement
Use project channels you already trusted before the promotion appeared. Confirm the specific event and destination, not merely that the token exists.
A copied announcement can quote real information while replacing the link. Compare the exact address, including its spelling and domain ending.
If the available project identity is weak or unclear, that is a reason to leave the claim alone. It isn’t a reason to let the claim page fill the gap.
Never rely on a search advertisement as your sole route to a verification page. An attacker can advertise a fake support or claim service too.
Don’t confuse a public address with wallet control
A public wallet address is designed to be shareable. It is not the same as a private key or recovery phrase.
Your support request may need transaction references, but it should not need the secrets that control the wallet. Don’t send those secrets in a screenshot.
Keep the recovery phrase offline and away from claim forms. A site promising to inspect eligibility has no legitimate need to take that phrase.
Where a wallet offers account separation, understand which account a request concerns. Don’t connect every account to see which one receives a better bonus.
Check the network before choosing a recovery tool
Permissions and recovery controls differ across networks. A tool appropriate for an EVM token allowance may not answer a Solana authorization problem.
Phantom’s revocation guidance separates supported network approaches. Reach the guidance through the wallet’s established support, not a private message from a stranger.
Do not approve another unexplained request just because it is labeled a cleanup. The repair destination needs verification too.
If you cannot interpret what was signed, ask the genuine wallet provider for help identifying the action. Share public transaction details, not wallet secrets.
What to Do if You Have Fallen Victim to This Scam
Stop all interaction with the airdrop page. Reject pending prompts and close the site. Don’t complete a second claim to recover the first attempt.
Keep any visible address or error already recorded. You don’t need another visit to establish that the invitation was not trustworthy.
Identify what you actually approved. Open your genuine wallet and review its activity for the network and account involved.
Separate a connection from a signed transaction, ongoing permission, or phrase disclosure. The appropriate next action depends on that distinction.
Disconnect the suspicious app through wallet settings. This helps stop the site’s continuing interaction with the wallet interface.
Do not assume it removes every spending permission. Follow the wallet’s current guidance to review relevant approvals separately.
Revoke unwanted authority using trusted network-specific controls. Verify the tool through the wallet provider’s own documentation.
A legitimate on-chain revocation can require a network fee. That is different from sending a recovery payment to a stranger’s address.
Protect remaining assets if wallet secrets were disclosed. A shared recovery phrase or private key requires a new wallet created on trusted equipment.
Get qualified help with the transfer plan if necessary. Reusing the exposed phrase would recreate the same control problem.
Preserve a useful theft record. Save public transaction identifiers, recipient addresses, amounts, network, and the original promotion.
Report the event to the wallet provider and appropriate authorities. Confirmed transfers generally cannot be simply reversed, but timely reports can still support investigation.
Address any downloaded software separately. If the page persuaded you to install a wallet add-on or utility, stop using it and assess the device.
Malwarebytes can help check for malicious software. AdGuard can reduce some risky advertising; neither tool reverses a signed transfer or restores an exposed phrase.
Ignore unsolicited recovery promises. Do not pay someone who claims they can unlock the airdrop or retrieve funds using a secret method.
Keep support inside independently verified channels. A person who knows your public loss details is not necessarily the person who can help you.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
After a Drain, Avoid Turning One Loss Into Two
It is natural to search quickly for a fix. That urgency creates another opportunity for people offering a private recovery service.
Ask what a helper would actually do. Transaction tracing, reporting, restoring access, and reversing a confirmed transfer are not interchangeable services.
An impressive screenshot of your address doesn’t establish special access. Public blockchain data can allow someone to describe a loss without controlling a recovery mechanism.
Don’t give remote access to the device holding your wallet as an automatic troubleshooting step. The helper’s identity and proposed access still need verification.
If a remaining balance is at risk, avoid making improvised transactions while an unknown person directs you. Use the genuine provider’s assistance to plan the response.
Check other accounts only for relevant exposure. A malicious token approval on one account is not automatically proof that every wallet you own was compromised.
Likewise, don’t erase all records out of embarrassment. A clear timeline and transaction references give legitimate support a better starting point.
Retain the warning signs for future claims: an unverified operator, an unexplained authorization, or a request for a wallet secret. Any one warrants stopping.
Frequently Asked Questions
Is the tokendisbursement.xyz RKC claim safe to use?
No. The reported promotion is a wallet-draining lure. Leave it unused rather than trying to authenticate it by connecting or signing.
Does recognizing Red Kitten Crew authenticate an airdrop?
No. A token identity and a specific claim portal are separate. Verify the event through independent project communication before considering any action.
Does simply connecting automatically move all my crypto?
Not in the ordinary wallet-connection model. Examine subsequent approvals, transactions, and any disclosed secrets instead of assuming the connection alone authorized every loss.
Will Disconnect remove a token spending permission?
Not necessarily. Disconnecting and revocation are different controls. Follow your wallet’s guidance for the network and authorization involved.
Can a scanner recover tokens already transferred?
No. A malware scan deals with device threats. Confirmed blockchain activity and wallet authorization require separate investigation and recovery actions.
Should I share my recovery phrase with an airdrop helper?
Never. Anyone with that secret may control the wallet. Genuine support should work from public transaction details, not your recovery phrase.
The Bottom Line
Do not claim RKC through the reported airdrop portal. Free tokens do not justify an unverified wallet request or unexplained permission.
If you already interacted, review exactly what was authorized and secure the affected wallet. Preserve transaction records and keep strangers out of the recovery process.








