


A token-launch page says your vote can earn a larger allocation and lasting Founding Voter status. It looks like participation, not a purchase, with one wallet button to begin.
The offer makes acting early feel important. Before casting that vote, find out whether the promised event and the wallet request belong to the same legitimate project.
Overview
The reward turns a vote into an opportunity
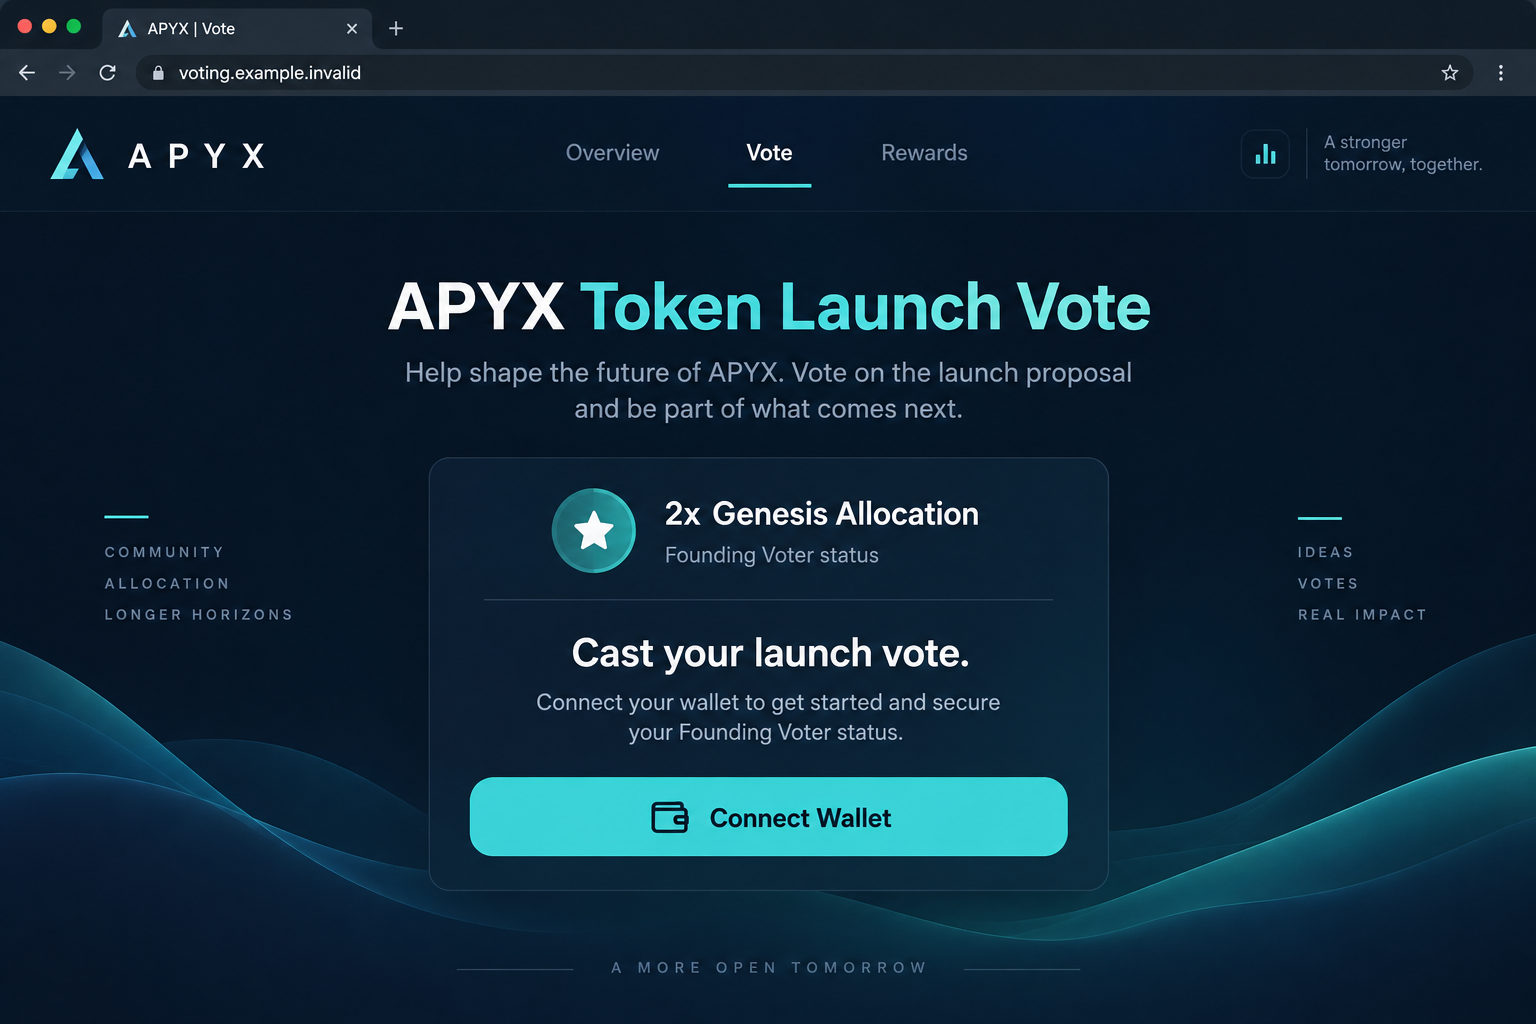
The Apyx token launch voting reward scam borrows the language of governance. Its fraudulent offer promises a 2x Genesis Allocation and permanent Founding Voter status.
Reported lookalike destinations include apyx[.]team, dapps-apyxfi[.]app, event-apyxfi[.]com, and voting-apyx[.]finance. They should not be treated as authenticated voting channels.
The purpose of this warning is to identify that deceptive promotion. It is not a verdict that the genuine Apyx protocol or every governance vote is fraudulent.
There is a real project behind the borrowed name
Apyx’s own documentation identifies its project website as apyx.fi and describes its protocol separately from the fraudulent voting offer.
That legitimate presence can give the impersonation a believable subject. It doesn’t validate another domain’s promise of a bonus or an honorary status.
The illustrated voting page is representative and uses an example address. It is not an original screenshot or an independently verified entitlement to tokens.
Wallet authority matters more than the word vote
The campaign is reported as a crypto-draining lure. Its reward story encourages visitors to proceed into wallet interaction they have not independently verified.
An ordinary connection and a spending authorization are not the same. The harmful action may depend on what you sign, approve, or disclose afterward.
- A governance label cannot make an unexplained transfer safe.
- A branded domain is not necessarily a domain controlled by the project.
- A status badge displayed on a page is not evidence of an on-chain reward.
- Recovery should follow the actual network, transaction, and permission involved.
Why a Founding Voter Badge Can Be Persuasive
The hook offers more than tokens. It suggests that you can become one of the people recognized for helping a project begin.
That kind of belonging can make the request feel like a community activity rather than a financial decision. The wallet still contains assets with real consequences.
The allocation multiplier supplies the economic incentive. The honorary title supplies the emotional one.
Neither establishes the event’s authenticity. A webpage can print a multiplier and invent a participant status without creating anything in a legitimate protocol.
Imagine a person who has followed the real project but never used its governance tools. The copied name fills part of the trust gap.
The remaining gap is the exact voting process. That is where independent project documentation and announcements should matter most.
Don’t let excitement about being early replace that check. A legitimate community benefits when people verify unfamiliar requests before authorizing them.
A vote also need not be risk-free just because it doesn’t resemble shopping. Wallet prompts can grant permissions or submit transactions outside your intended choice.
The website’s description is the pitch. The wallet’s requested action is what you would authorize.
How the Apyx Token Voting Reward Scam Works
Step 1: A launch story gives the invitation a plausible occasion
The promotion presents participation as part of a token launch. That is a recognizable setting in which crypto projects may discuss community decisions and allocations.
But a familiar occasion is not verification. Check the event through the project’s independently established communications.
If the invitation arrives in a reply thread, identify who posted it. A reply under an official account can come from someone entirely unrelated.
A copied account name or image can encourage mistaken recognition. Open the profile through a trusted project route rather than following the reply’s preferred chain.
Keep the question narrow: did the genuine project announce this particular vote and this particular destination?
Step 2: Bonus language pushes verification behind participation
The reward and status promise make proceeding feel like claiming a place. A reader may worry that waiting will mean a smaller allocation.
That pressure doesn’t need to be accompanied by a payment demand. It only needs to persuade you to open the wallet and continue.
The 2x claim doesn’t tell you the underlying amount, conditions, or legitimacy. Doubling an unverified entitlement does not create a verified one.
Before considering any authorization, locate the event’s actual rules. If the supposed benefit exists only on the suspicious page, leave it there.
You don’t have to win an argument with the promoter. Refusing the request is enough to avoid granting it authority.
Step 3: A lookalike domain supplies a convincing stage
The page uses the project’s name while operating at another address. Brand words inside a hostname can make that difference easy to overlook.
Compare the entire domain, not just the recognizable letters. Extra words, different endings, and rearranged spelling can identify an unrelated destination.
The project’s own terms identify apyx.fi. Use official documentation to establish context rather than accepting a domain from a promotional reply.
Don’t assume a change of domain is impossible for a real organization. Require independently authenticated confirmation if a new address is claimed.
An unavailable or blocked lookalike page isn’t a sign that you should find an alternate way around the warning. Stop instead.
Step 4: The wallet prompt can request more than a vote
Once the interface reaches your wallet, evaluate the request independently of the reward card. Check the network, account, recipient, and action where the wallet exposes them.
A message signature, token allowance, and asset transfer can have different effects. Do not approve a technical request just because the page calls all of them voting.
Some legitimate activities need signatures. The issue is whether the specific request is understandable and comes from a verified process.
If a prompt grants spending authority, ask why that authority is necessary for the claimed task. An unexplained broad permission deserves rejection.
MetaMask’s approval guidance explains that allowances can survive disconnection. A familiar Connect Wallet button is not the end of the security decision.
Never provide a recovery phrase to qualify for a vote. That secret controls the wallet and has no place in a token-launch form.
Step 5: A successful page message can conceal an unwanted result
The site can announce that your vote was recorded without proving what happened to the assets or permissions. Check actual wallet activity.
If an unwanted transaction is confirmed, closing the page doesn’t cancel it. Pending requests and confirmed transfers need different responses.
If a permission remains, the site may not need another visible click to exercise it. Review the authorization using network-appropriate controls.
If nothing moved, don’t assume every interaction was harmless either. Identify whether you granted ongoing access or disclosed a secret.
Your next steps should come from that record, not from the page’s congratulations screen or a stranger offering to finish the vote.
Real Apyx Documentation Versus the Fake Launch Offer
The project identity is not a recommendation to invest
The existence of Apyx documentation helps separate the genuine project from the impersonation. It doesn’t establish that its products suit your circumstances.
Evaluate any real financial product separately, including its restrictions and risks. This guide concerns the fake reward journey, not expected returns from the protocol.
Don’t move from rejecting an impersonator directly into investing because the real website looks more credible. Those are different decisions.
A truthful warning can identify a legitimate organization’s address without endorsing every claim that organization makes.
A project roadmap is not this specific invitation
Official material can discuss tokens, community incentives, or future governance. Scammers can reuse those subjects to make an invented event sound timely.
The relevant match is the exact event and its authorization process. A general mention of governance doesn’t authenticate a surprise voting portal.
Dates and plans also change. Locate current communications before accepting a time-sensitive request, rather than relying on an old screenshot circulating in a chat.
If the event can’t be located through trusted channels, decline it. You don’t need to provide a trial signature to find out whether a promise is real.
Use public records without exposing private control
Wallet providers and legitimate responders can work with transaction identifiers and public addresses. Those records help identify the action without revealing the key controlling it.
Before sharing a screenshot, remove recovery phrases, private keys, and unrelated personal data. Do not expose another account just to report the first problem.
Keep exact domain spelling and the original promotional text. These details can help distinguish a copied brand from the real project.
A person who can quote your public transaction isn’t automatically an authorized representative. Verify their identity through the provider or project itself.
What to Do if You Have Fallen Victim to This Scam
Abandon the vote and reject outstanding requests. Close the fake event rather than completing another prompt to claim the multiplier.
Do not bypass a phishing warning or search for a replacement copy of the same offer. Its promised benefit is not worth continuing the risk.
Inspect the affected account’s activity. Identify the network and examine the approvals or transactions associated with the interaction.
Keep the distinction between public-address access and asset-moving authority. Ask genuine wallet support to interpret unclear records without giving them your secrets.
Disconnect the lookalike application. Remove its connection using the genuine wallet’s available settings.
Then examine any continuing permissions. Don’t rely on the absence of a connected-site entry to establish that a token allowance disappeared.
Cancel unwanted permissions through verified controls. Use guidance appropriate to the chain rather than copying instructions for another network.
Review any fee and request before signing the revocation. A fee paid to the network differs from an advance payment demanded by a recovery operator.
Replace compromised wallet control where needed. If a phrase or private key was disclosed, arrange a fresh wallet on trustworthy equipment.
Protect remaining legitimate assets using a careful transfer plan. Don’t reuse the exposed secret or enter it into a repair site.
Report losses with concrete transaction evidence. Preserve identifiers, destination addresses, amounts, and the event’s URL.
Contact your wallet provider and relevant authorities. If an exchange was involved, notify its verified support team promptly without assuming a transfer can be reversed.
Investigate device exposure if you installed anything. A proposed voting helper, browser extension, or support utility creates a separate software question.
Malwarebytes is appropriate for relevant malware checks. AdGuard may reduce malicious-ad exposure later, but neither product revokes wallet approvals or refunds a transfer.
Refuse a paid second chance. Ignore claims that another deposit will activate the reward, verify the vote, or restore stolen funds.
Work through verified assistance. Keep a written incident summary so you don’t need to reconstruct the sequence each time you contact legitimate support.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Build an Incident Summary That Helps Someone Help You
Start with the network and wallet account used. A provider cannot interpret an Ethereum allowance from a description that only says a crypto vote went wrong.
Next, record the sequence in ordinary language: where the invitation appeared, which site opened, and which prompts you accepted.
Include whether you installed anything or typed a secret. Those details change the response more than the reward page’s claimed balance.
List actual transfers separately from losses estimated by the site’s interface. Use the asset and amount recorded in the transaction rather than an invented USD value.
Keep pending transactions distinct from confirmed ones. Ask the genuine provider what controls remain available in your wallet; don’t accept a stranger’s universal cancellation promise.
If several accounts were involved, keep a separate record for each. That helps avoid overlooking one authorization while repeatedly checking another.
Preserve communications with anybody requesting a recovery fee. Another fraudulent demand can be relevant even if it comes from a different profile.
Finally, record the actions already completed. Legitimate support needs to know whether you disconnected, revoked authority, moved assets, or replaced compromised wallet control.
Frequently Asked Questions
Is the Apyx Founding Voter reward offer authentic?
The lookalike campaign described here is fraudulent. Don’t authorize it simply because it uses the real project’s name and governance language.
Is Apyx itself the scam described in this article?
No. This warning concerns an impersonating token-vote offer. The genuine project and its financial products require separate evaluation.
Does a 2x allocation mean tokens are already mine?
No. A promotional multiplier does not establish ownership or a valid reward. Check independently authenticated rules and actual wallet records.
Can a vote require a signature without being fraudulent?
Yes, some legitimate processes use signatures. Verify the event and the exact request; a signature isn’t safe merely because a page calls it voting.
What if I disconnected immediately after approving?
Review the permission anyway. Disconnecting may leave an allowance active, depending on the network and authorization you granted.
Should I pay to unlock the reward after an error?
No. Leave the fraudulent event. A demand for another payment is not a reliable path to a bonus or recovery of lost assets.
The Bottom Line
Skip the lookalike Apyx voting offer. A multiplier and a Founding Voter badge do not justify unexplained authority over your wallet.
If you already approved a request, inspect the actual transaction and permissions now. Secure remaining assets through verified tools and report any confirmed loss.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.