


A guest wants five more nights in the same room. For a busy reservations team, that sounds like an inquiry worth answering quickly.
The email includes a booking preview and a button promising the details. Before preparing the quote, look at what that button actually asks you to open.
Overview
A reservation inquiry aimed at hotel staff
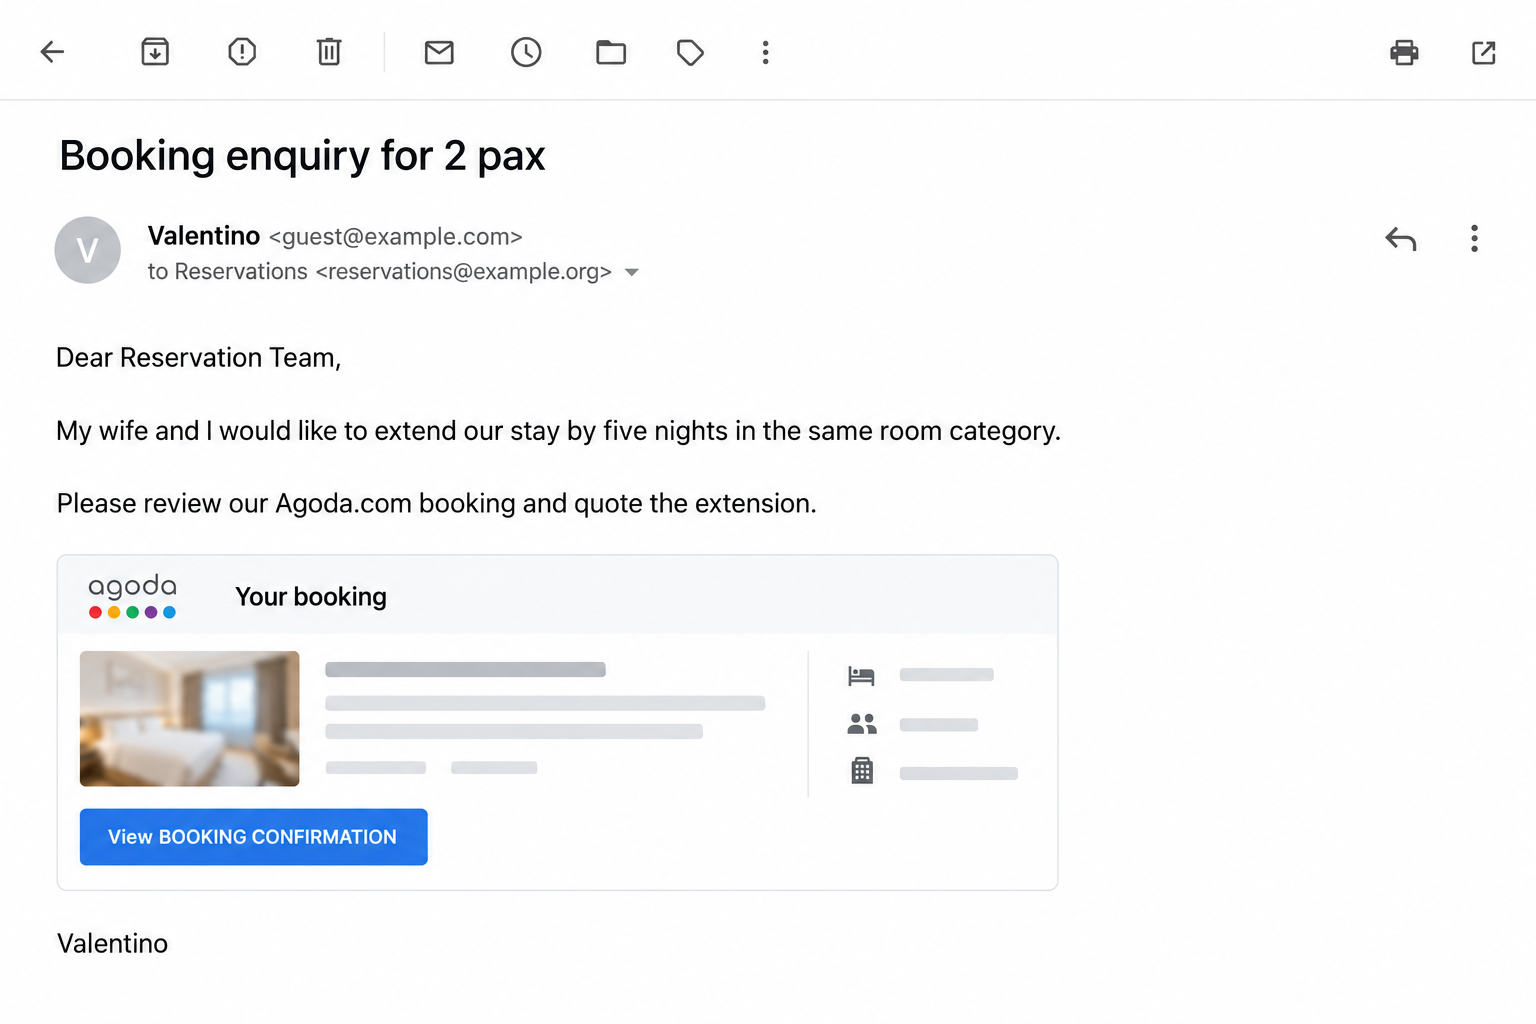
The Agoda booking email virus uses a familiar hospitality task as its opening. Someone claiming to be an existing guest asks about extending a stay.
The reported subject is “Booking enquiry for 2 pax.” The sender calls himself Valentino and describes traveling with his wife.
The request concerns five additional nights in the same room category. Those ordinary details encourage the recipient to treat the message as prospective revenue.
The confirmation button delivers a script instead of booking information
A blurry reservation preview introduces a View BOOKING CONFIRMATION link. In the reported campaign, that link downloads a malicious JavaScript file.
A downloaded .js file is not a reservation document. Running it can execute instructions on the workstation rather than reveal a clearer booking image.
The final malware family and original filename are not established. There is no basis to identify this particular payload as a named stealer or ransomware.
Agoda is the borrowed reference, not the scam operator
The message does not establish a genuine booking or a connection to Agoda. The impersonation depends on staff recognizing the travel platform’s name.
- The audience is a reservations or accommodation team.
- The promised business is a five-night extension.
- The booking preview provides a reason to open another item.
- The delivered file is executable script content, not the promised confirmation.
- The response depends on whether the script was merely downloaded or actually run.
The email image uses fictional addresses and a simplified booking preview. It illustrates the approach without exposing a real guest’s information.
Why This Request Fits So Easily Into a Hotel’s Workday
Reservations staff routinely receive incomplete requests. A guest may omit dates, attach an unclear screenshot, or use a different name from the reservation holder.
That makes this approach more effective than an obviously unrelated attachment. The requested action appears connected to work the recipient is already authorized to perform.
An extension also creates an incentive to keep the conversation moving. Staff may want to confirm availability before another guest books the same room.
However, commercial urgency does not make an unfamiliar file necessary. A booking can be checked through the property’s own records without running software supplied by a stranger.
A real traveler can be helped through a verified reservation channel. Asking for a booking reference is reasonable; opening an unexpected script is not required customer service.
Agoda’s hotel cybersecurity guidance describes phishing and malware targeting partners. It also explains why stolen partner access can put guests at risk.
A single reservations login can affect conversations with many guests. Keep that wider exposure in mind without guessing which malware this script delivered.
How the Agoda Booking Email Scam Works
Step 1: A supposed guest introduces an ordinary extension request
The message addresses the reservations team and refers to a booking made through Agoda. It asks for a price rather than immediately demanding money.
This gives the recipient a recognizable task: locate the reservation, check the room category, and calculate the additional stay.
The sender’s name is part of the presentation, not a verified identity. A genuine person sharing that name should not be associated with the attack.
Likewise, recognizing a guest name in the property’s records would not authenticate the email’s link. Confirm the relationship through the existing booking conversation.
Step 2: An unclear preview makes opening the confirmation seem useful
The booking image is difficult to read. That creates an apparently practical reason to use the larger confirmation link.
The recipient may think they are correcting an information problem, not installing anything. The surrounding travel details help sustain that assumption.
Do not rely on the preview as evidence of a reservation. Pictures of booking interfaces can be fabricated, copied, or attached to unrelated requests.
Instead, search the trusted booking system using information you can verify. If no corresponding record appears, keep the inquiry outside privileged workflows until it is clarified.
Step 3: The link substitutes a JavaScript download for a document
The important change is the type of content delivered. The reported link produces a .js file rather than an ordinary booking confirmation.
JavaScript inside a webpage and a standalone script launched on Windows are different situations. The familiar language name does not make the downloaded file safe.
Do not rename it to PDF, open it with another application, or double-click it to see whether the confirmation is hidden inside.
A filename or icon can also be misleading. Let the hotel’s security staff inspect the original download record rather than experimenting on a reservations computer.
Step 4: Running the script can deliver additional malicious software
The reported script is a malware-delivery stage. When executed, it can issue hidden instructions that retrieve and install another component.
The available case details do not identify that component. Treating the incident as confirmed ransomware, credential theft, or remote control would require additional evidence.
That uncertainty changes the investigation, not the need to respond. Staff should report execution promptly so defenders can determine what happened on the affected machine.
A quick window closing or no visible response is not reassurance. A script does not need to display a useful confirmation to have performed an unwanted action.
Step 5: The hotel must assess workstation and account exposure separately
If malicious software ran, the affected environment may include email, reservation systems, saved sessions, and documents accessible to that workstation.
Do not assume all those resources were stolen. Identify which accounts were available, examine actual activity, and let the responsible team determine the incident’s reach.
Account recovery should use a different trusted device. Logging into more services from the suspect computer can introduce additional credentials while the investigation is incomplete.
The booking request can wait. Keeping a room inquiry moving is less important than preventing an unassessed workstation from handling guest data or financial instructions.
Verify the Booking Without Following the Sender’s Route
Start inside the property’s established system
Use the partner portal or property-management system the hotel already uses. Do not reach it through the suspicious confirmation button or an advertised support result.
Compare the reservation holder, arrival dates, room category, and booking status. A matching amount alone is not enough to establish that the sender controls the reservation.
If an existing conversation is available, continue through that channel. Do not introduce an address supplied only by the questionable email.
Agoda’s guest-communication explanation describes its messaging arrangements. Staff should use the property’s approved process rather than invent a shortcut around it.
Keep the quotation separate from file execution
You can explain that the hotel needs a verifiable reference before discussing an extension. That does not require accusing an unfamiliar sender during the first exchange.
For this malicious message, stop interacting and report it. For an uncertain request elsewhere, follow the hotel’s verification policy before opening attachments or accessing internal records.
Do not ask a colleague to open the script on their computer. Moving the task to a second workstation does not resolve the original risk.
A specialist can assess suspicious material using approved methods. Front-desk staff should not be expected to discover the payload by trying different ways to launch it.
Record what happened before changing the workstation
Note the time, affected computer, email subject, and whether a file arrived. Distinguish a browser download from opening the resulting file.
If Windows displayed a warning, record the wording without reproducing the action. A warning dismissed earlier can be important to the incident timeline.
Do not forward the executable around the hotel. Preserve the original message through the approved reporting route and let security staff arrange safe collection.
Include the account used on the workstation, but not its password. The team needs to identify the affected identity, not create another copy of its secret.
What to Do If You Fell Victim
Stop the booking interaction. Close the suspicious page and do not open another confirmation supplied by the same sender.
If you only received the email, report it. Receiving a malicious inquiry does not itself establish an infected computer or a compromised hotel account.
Tell hotel IT or the responsible manager immediately. Explain whether you downloaded the script, launched it, or entered account information elsewhere.
For a shared workstation, identify who was using it and when. Prompt reporting helps other shifts avoid continuing sensitive work on the same machine.
Contain a workstation where the script ran. Disconnect its network connection and stop using it for reservations, payments, or account recovery.
Coordinate further action with the response team. Do not shut down unrelated hotel systems or erase the affected machine before necessary evidence is preserved.
Preserve the original email and download details. Keep the subject, timestamps, sender information, and security alerts through the approved private process.
Do not execute the file again for a clearer screenshot. Document what you remember and let the team collect technical evidence safely.
Secure relevant accounts from a clean device. Have administrators review partner-portal, email, and other access that the workstation could expose.
Replace affected credentials and revoke unauthorized sessions as appropriate. A malware scan does not independently undo changes made inside an online account.
Use a supported cleanup plan. Malwarebytes can help inspect unwanted software after the device has been assessed. Preserve detection reports and follow the hotel’s managed-security process.
AdGuard can reduce malicious advertising and some unsafe destinations. It is a preventive layer, not a way to make the booking script trustworthy.
Check whether guests need protection. If account activity shows unauthorized messages or payment instructions, have the hotel contact affected people through verified channels.
Do not announce a confirmed data breach without evidence. Explain established facts, preserve case records, and follow applicable organizational reporting procedures.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
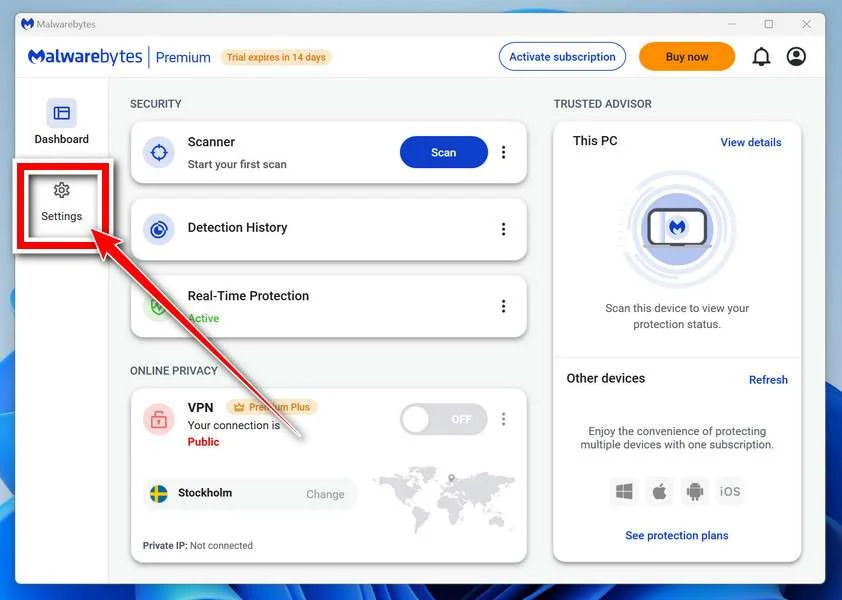
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.
In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.
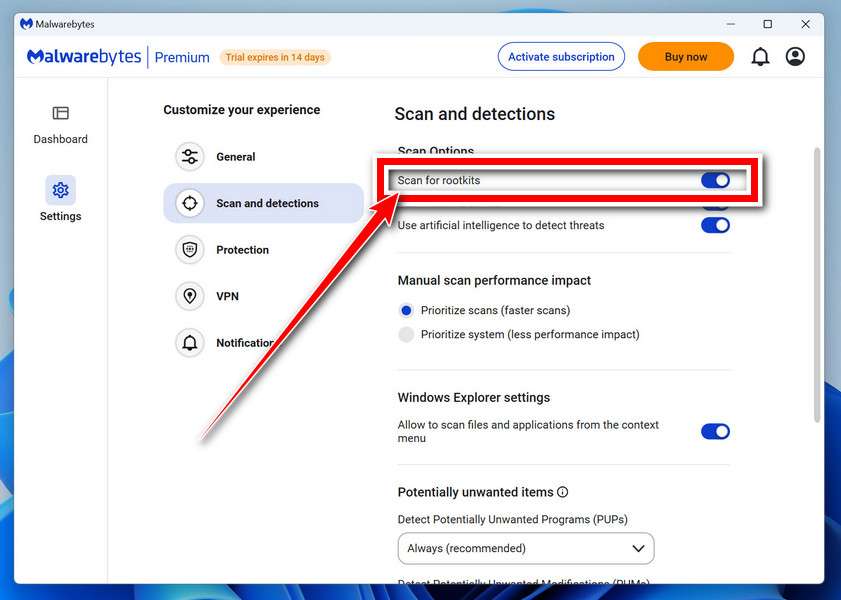
Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.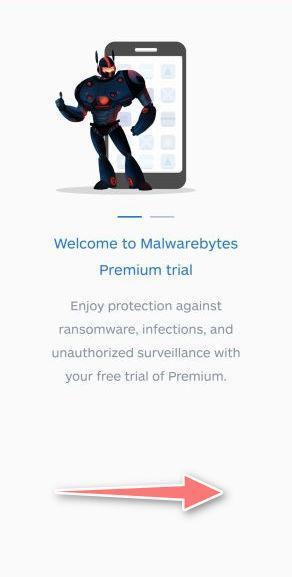
Tap on “Got it” to proceed to the next step.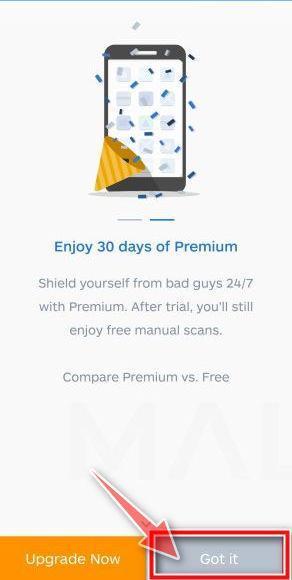
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.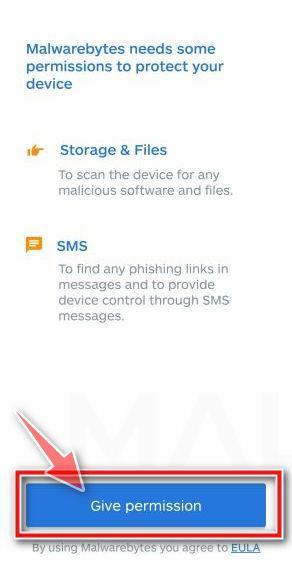
Tap on “Allow” to permit Malwarebytes to access the files on your phone.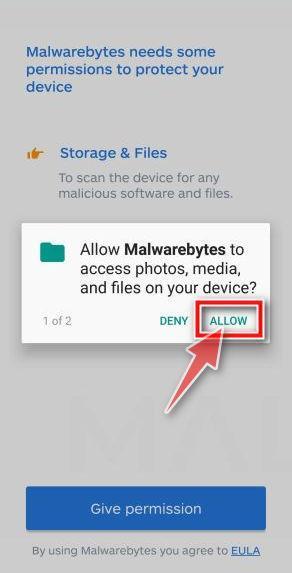
-
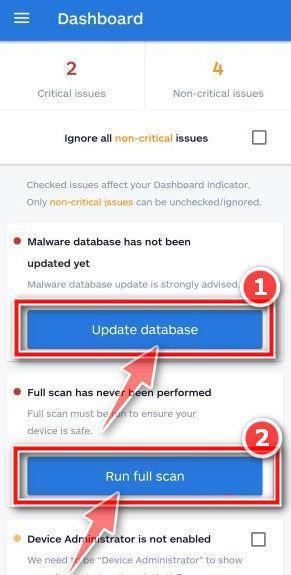
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.
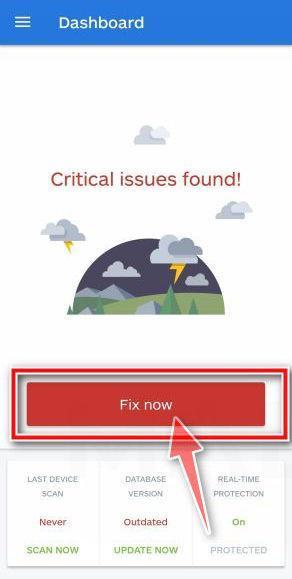
Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
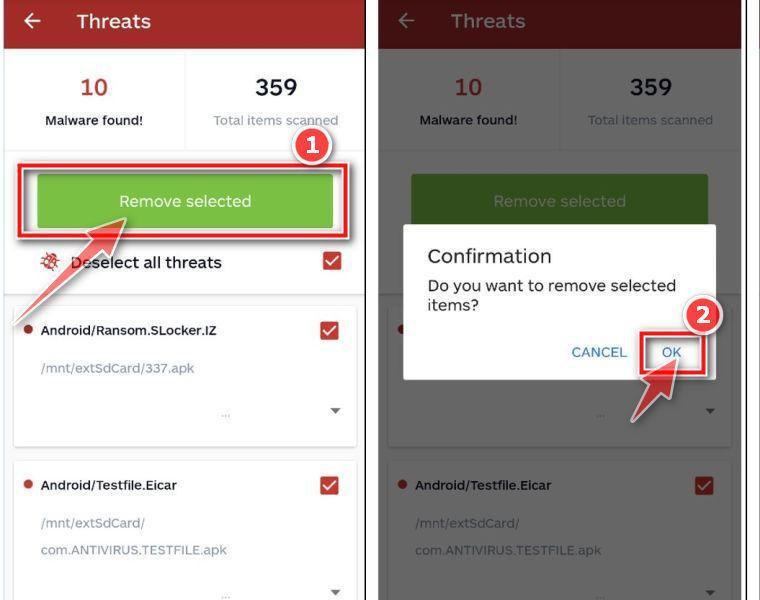
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.
-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Windows Cleanup After Opening the Booking Script
Step 1: Decide who should handle the affected computer
For a managed hotel workstation, contact its administrator before installing tools. Existing monitoring, incident evidence, and booking-system dependencies may require a coordinated response.
Keep the computer off the network until that plan is established. Do not reconnect it simply because no unusual window remains visible.
If sensitive records are involved, ask whether an image or other evidence must be retained before quarantine or rebuilding changes the disk.
Step 2: Obtain trusted security software without using the inquiry
Use the security product already managed by the hotel or obtain Malwarebytes from its official distribution channel. Never install a supposed booking-viewer repair utility.
Our optional Malwarebytes Premium route concerns paid protection. Purchasing it is not a prerequisite for confirming the reservation or identifying the unknown payload.
Read any trial or additional-feature offer separately. The current feature table distinguishes free manual Custom Scan from paid Threat Scan.
Step 3: Scan selected locations and retain the findings
In Malwarebytes, use the Scanner menu to reach Advanced Scan and Custom Scan. Select the locations the responder wants examined, then start that scan.
The official Custom Scan guide provides current controls. Review detections, quarantine confirmed threats, and save the results.
If a restart is requested, coordinate it with whoever is preserving the incident. Do not exclude a detection merely because its filename resembles booking paperwork.
Step 4: Verify recovery before resuming reservations work
A clean scan is one finding, not proof that every unauthorized change has been reversed. Administrators should assess persistence, account access, and whether rebuilding is warranted.
Restore necessary work from verified sources. Do not bring the suspicious script back in a Downloads-folder backup or reuse the original email to retrieve missing information.
Confirm the workstation is approved for normal use before signing back into partner systems. Keep the booking verification separate from the technical recovery record.
Frequently Asked Questions
Does this email prove a guest has an Agoda booking?
No. Verify the reservation in the property’s established system. A name, room category, or booking-looking preview does not authenticate the sender’s file.
Is a JavaScript file a normal booking confirmation?
No. A standalone script should not be opened to read a reservation. The reported inquiry substitutes executable content for the promised confirmation.
Was the final malware identified?
Not in the available campaign details. Do not assume a particular ransomware or stealer without examining the actual incident through a safe response process.
Am I infected if the script only downloaded?
A download and execution are different events. Report the download, avoid opening it, and let the responsible team determine whether anything ran.
Should every guest asking for an extension be treated as fraudulent?
No. Extensions are ordinary business. Verify the reservation and use approved communication channels without running unfamiliar files to handle the request.
Can we recover the booking by retrying the link?
Do not retry it. Locate the real reservation independently and let security staff handle the suspicious message and any affected workstation.
The Bottom Line
Do not open the script delivered by this Agoda-themed booking inquiry. Confirm any real extension through trusted reservation records, not the sender’s confirmation button.
If the file ran, isolate the workstation and notify hotel IT promptly. Cleanup, account protection, and any guest notification should follow the evidence, not guesswork.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.