


A project manager wants a progress claim certified and an invoice confirmed. The request looks like routine work.
Before opening the download behind “Progress Claim No. 7R,” check what the message is actually asking your computer to do.
Overview
A certification request with a download instead of an attachment
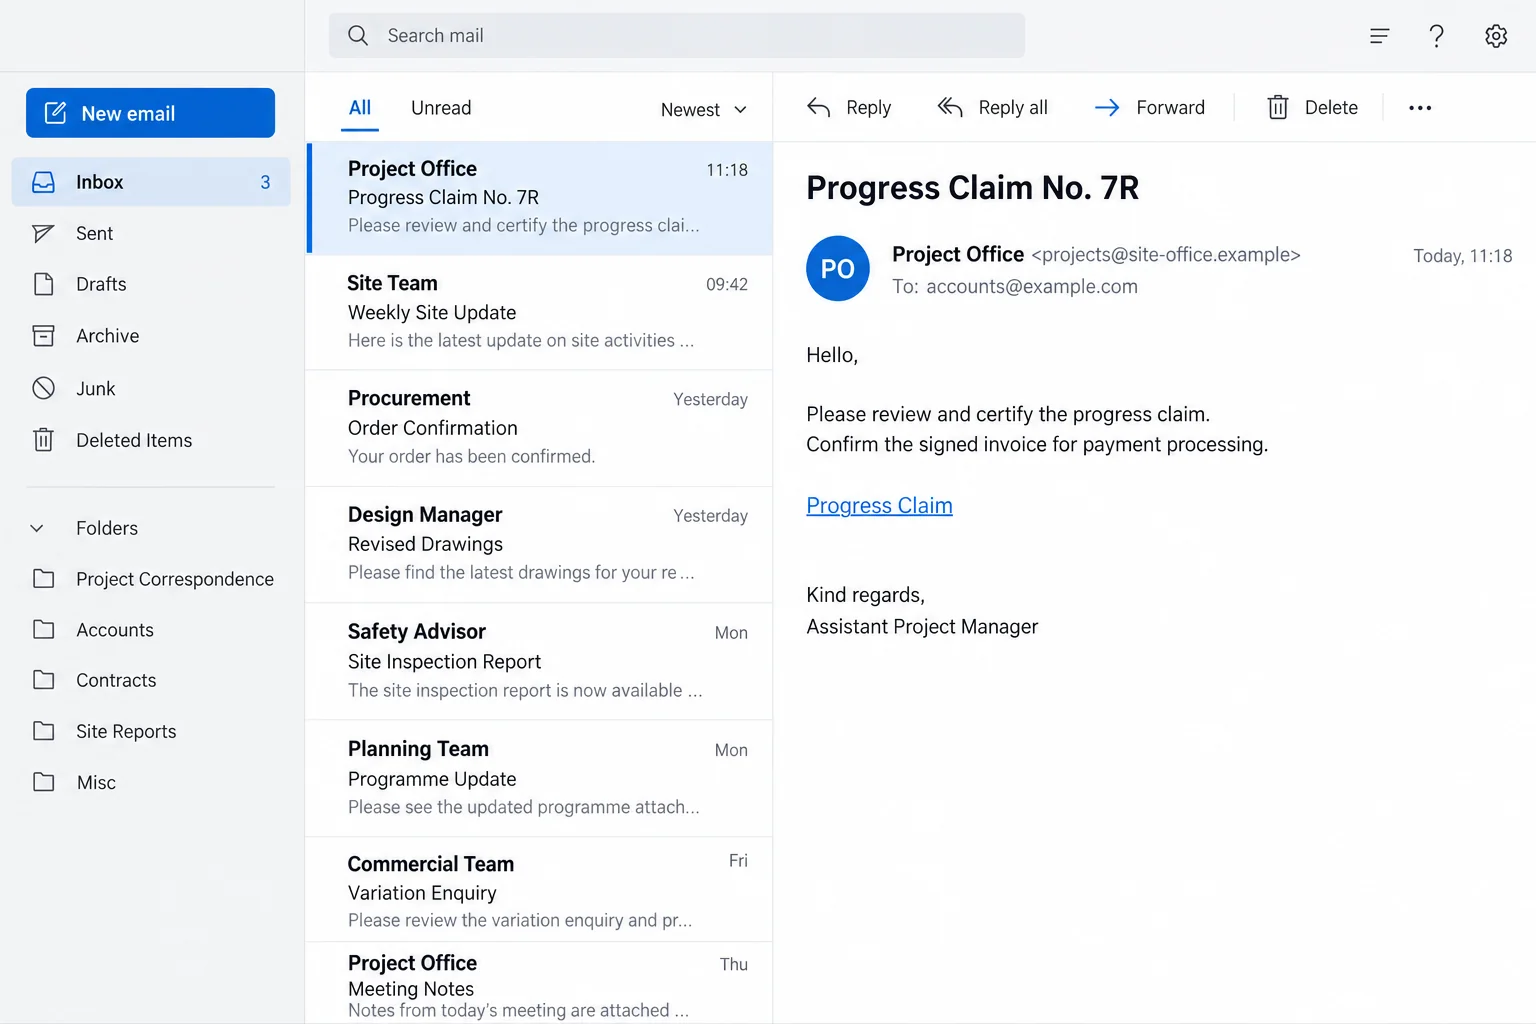
The Progress Claim review email scam poses as routine project correspondence. The reported sender claims to be an assistant project manager seeking certification and invoice confirmation.
The document is not attached. A Progress Claim hyperlink leads to an archive containing a VBScript file, identified by the .vbs ending.
That is a meaningful change from reading a claim. A script contains instructions for the computer, not simply the pages your colleague wants approved.
The illustration uses a fictional project office. It shows the business request without presenting an actual contractor, invoice, or recipient as involved.
The risk begins with executing the downloaded script
The reported script can deliver FormBook or PhantomStealer. Those names describe information-stealing threats, not the kind of software needed to certify a project document.
No archive was executed for this article. The payload named in a report is not a diagnosis of every computer that received the email.
Receiving a message, downloading an archive, extracting it, and running its contents are different stages. Your response should reflect the furthest action actually taken.
Keep project approval and computer access apart
- Ask the established project contact to confirm the claim through a separate conversation.
- Do not run a script to reveal an invoice or certify a document.
- If it ran, report the device exposure promptly and pause related financial approvals.
A real progress claim may still need review. Obtain that document through the project’s normal channel rather than trying to salvage the suspicious download.
Why This Request Fits So Easily Into a Working Day
Progress claims sit between technical review and payment. One team checks the work, another confirms paperwork, and someone else may authorize the invoice.
That handoff can leave a recipient unsure who first requested the document. A confident message from a project office seems to fill the gap.
A numbered subject adds specificity. It can suggest an ongoing sequence even when the recipient has never seen the earlier claims.
Specific wording still needs context. Does your organization recognize the project, the sender’s role, the contract, and the claim being requested?
Do not let the apparent urgency of payment substitute for those checks. A delayed approval is easier to resolve than executing a stranger’s program.
Nor should a copied company signature settle the question. Business names and job titles are often public, and legitimate correspondence can be imitated.
The best verification is practical: contact the person you already deal with and ask for the same document through an agreed system.
If certification requires a signature, confirm who is authorized to provide it. A malware email should not become an accidental approval of project work.
How the Progress Claim Review Email Scam Works
Step 1: The message puts you inside an approval process
The sender asks for a professional action rather than an unusual favor. Review, certification, and payment processing all sound like normal steps in a project.
That framing encourages the recipient to think about completing work, not evaluating a new relationship. The attached authority comes from the claimed job role.
If the request reached a general accounts mailbox, several people may see it. Do not assume another recipient has already authenticated the sender.
Assign one person to verify it and record the outcome. Parallel attempts to open the same download can expose multiple computers without providing better evidence.
A known project name would strengthen relevance, but not prove safety. Confirm the actual request instead of accepting familiarity as permission to execute files.
Step 2: The link promises the missing paperwork
The message refers to a document the reader needs before responding. A hyperlink supplies an apparently convenient route to that missing material.
Legitimate organizations share documents through links too. The issue is not that the file is online, but what is delivered and why it must run.
Before opening a download, compare the destination with your project’s approved sharing service. Ask the sender through a trusted route if the delivery method has changed.
Never bypass a blocked-download warning because a stranger says the invoice is overdue. That warning is part of the information needed to assess the request.
If no file arrived, do not chase alternate links offered by the same message. Verification should leave the suspicious thread, not deepen it.
Step 3: An archive conceals the difference between a document and code
An archive is a container. It may hold ordinary documents, but its packaging says nothing about whether the files inside are appropriate.
In this reported case, the important inner file is a script. Extracting a container does not transform that script into a signed invoice.
Show filename extensions before making decisions about unfamiliar material. A document-like icon or a long filename can distract from the actual file type.
Microsoft’s File Explorer guidance describes the File name extensions setting under View and Show.
Do not rename the file to .pdf and try again. Changing a name does not convert instructions into a safe document or establish its origin.
Step 4: Running the file changes the incident
A script can instruct Windows to perform actions without presenting a useful document. A blank window or brief activity is not a reliable sign of failure.
Once untrusted code has run, the question is broader than whether the requested invoice appeared. The device and accounts used on it need attention.
Do not rerun the file to reproduce what happened for a colleague. Describe the first attempt and let the security team assess available records.
If you are unsure whether it executed, say that clearly. A precise uncertainty helps more than guessing that nothing happened because there was no visible response.
Support may ask about the filename, location, time, and any prompts. Provide those observations without uploading the file to an unfamiliar online repair service.
Step 5: Stolen business access can create another opportunity
An information-stealing infection can put saved credentials and account activity at risk. The exact impact depends on what ran and what it could access.
A project mailbox may contain invoice discussions, supplier details, and approval chains. That context can help someone craft a convincing later message.
For that reason, device containment and payment verification should proceed together. Cleaning a computer does not authenticate an invoice or banking instruction received afterward.
Tell finance if the affected account participates in payments. Ask them to use established verification procedures for changes, rather than assuming every invoice is fraudulent.
Document actual unauthorized transactions separately. A suspicious download is a serious exposure, but it is not proof that a payment has already been diverted.
What Counts as a Meaningful Warning Sign?
The delivered format does not fit the task
A review request should supply something you can inspect using approved tools. A script presented as a prerequisite for reading deserves immediate scrutiny.
A request to change security settings or override a warning makes that mismatch worse. Do not follow it simply because the sender sounds technically confident.
There may be legitimate automated workflows elsewhere in your business. An unexpected emailed script is not authenticated by their existence.
The sender bypasses the project’s established route
Compare the message with earlier genuine correspondence. Look at the full sender address, reply destination, and the people normally included in approvals.
A new address is something to confirm, not automatic proof of a criminal sender. The dangerous download provides the stronger reason to stop this particular route.
Use an earlier verified telephone number or internal directory to ask about the change. A replacement number inside the suspicious signature cannot independently verify itself.
The supposed fix expands access
If the document fails, do not accept remote help from the sender. A failed lure should not become permission for an unknown person to control your computer.
Likewise, an online password check is not a sensible repair for a script that will not display. Each new request adds a separate potential exposure.
Keep the incident bounded. Preserve what happened and return to your actual support team rather than negotiating with the suspicious sender.
What to Do If You Opened the Progress Claim Download
-
Identify the stage you reached. Note whether you only received the email, downloaded the container, extracted files, or ran the .vbs file.
If the script stayed unopened, leave it that way. Do not double-click it merely to establish whether your security software will detect it.
Preserve the original message and filename through your workplace reporting procedure. Avoid forwarding a live malicious attachment to colleagues who might open it.
-
If code ran, contain the affected computer. Stop sensitive activity and contact IT immediately. Disconnect networking where your incident procedure calls for it.
Microsoft’s device-response guidance explains organizational isolation and investigation options. Managed environments need a coordinated response, not an improvised series of repairs.
Do not reconnect solely to download more tools without a plan. Ask support how to obtain what is needed while preserving containment.
-
Arrange trustworthy malware scanning. For a personal Windows computer, use current Windows Security and a genuine Malwarebytes installer from the site’s maintained download route.
Update the tool when safely possible, complete the recommended scan, and retain its results. Follow quarantine and restart instructions for threats actually detected.
A scan can help remove malicious software. It cannot prove that no information was copied before the infection was discovered.
-
Recover important accounts from a separate device. Prioritize the mailbox used for work and accounts whose credentials were saved or entered on the affected system.
Replace exposed passwords, review sessions, and examine recovery settings. Ask administrators to assess business access rather than resetting organization-wide credentials yourself.
If wallet secrets or financial accounts may be involved, seek appropriate official support. Never send those secrets to someone offering to inspect the script for you.
-
Confirm the real claim and protect the payment process. Contact the established project team independently and request the genuine document through its approved channel.
Tell the people responsible for payment that the suspicious request is being investigated. Verify any later bank-detail change using normal controls.
If funds were actually sent to an unauthorized recipient, contact the payment provider’s fraud team promptly with the transaction details. Do not wait for cleanup to finish.
-
Check recovery before resuming ordinary work. Follow your security team’s clearance process or obtain specialist help if detections return, scanning fails, or trust remains uncertain.
AdGuard may help filter malicious advertising during future browsing. It is not a removal tool and will not undo execution of a Windows script.
Keep backups disconnected until they can be handled safely. Do not copy the archive into a clean system along with the documents you want to preserve.
Windows Cleanup After Running the Progress Claim Script
These instructions apply to a personal Windows computer after the downloaded script may have run. Receiving the email alone is not the same exposure.
Step 1: Preserve the download timeline and arrange safe containment
Keep the email, archive name, script name, and execution time for support. On a work computer, let IT preserve the evidence before cleanup changes it.
Do not reopen the claim to collect a better screenshot. Keep backups separate and use another device for account recovery or payment verification.
Step 2: Install Malwarebytes and remove detected malicious software
Use this procedure on a personal Windows PC after preserving the incident details. For a managed computer, let your security team decide when scanning should begin.
Malwarebytes can find and quarantine threats. Its free Custom Scan is separate from paid real-time protection and Threat Scan. Neither edition supplies ransomware decryption keys.
-
Download the Windows installer.
Open the official download page using the button below. Select Free Download there and save the Windows installer.
If the affected PC cannot browse safely, use a trusted computer and arrange an appropriate transfer without exposing clean backup media.
Malwarebytes for WindowsManual scanning and quarantine, with optional paid protection.
Opens the official free-scanner page. Choose its Windows download; paid protection is optional.
-
Open the setup file.
Open Downloads and double-click the MBSetup file. If Windows requests permission, check that the prompt identifies Malwarebytes before allowing the installation.

-
Complete setup without accepting unwanted extras.
Select Install, choose the appropriate Personal or Business device option, and continue. Business-managed computers should be handled through their administrator’s process.

Review any browser extension, trial, or subscription offers. Skip optional features you do not want, then select Open Malwarebytes when setup finishes.

-
Choose a supported scan.
Find the Scanner tile on the dashboard. For a free Custom Scan, open its three-dot menu, select Advanced Scan, and choose Custom Scan.
Expand the file-location selector and select the system drive and relevant locations. Review potentially unwanted program settings, then select Start Custom Scan.
A paid or eligible trial edition may also offer Threat Scan. Use the controls available in your edition; do not disable Windows protections to unlock another option.

-
Let the scan complete and inspect its findings.
Keep the computer powered on while scanning and wait for the results. A large Custom Scan can take longer than a scan limited to common locations.
Review each detection and its location. Leave confirmed threats selected and choose Quarantine. Save the report if a detection is unclear rather than adding it to exclusions.
The results illustration uses sample detections to show the Quarantine control. Those names are not identifiers for the malware discussed in this article.

-
Finish removal and handle a requested restart.
Follow the quarantine prompts. If a restart is requested, save your work and coordinate it with anyone preserving evidence before restarting.

Reopen the application afterward and review the result. Repeated detections, blocked removal, or signs of continuing access need further investigation, not an automatic clean-device conclusion.
The screen design can vary by installed release. Follow the named controls and the vendor’s current scan instructions if your version looks different.
Step 3: Obtain another scan when the findings need clarification
HitmanPro provides an optional second opinion when a Windows infection or unresolved finding warrants another check. Run scanners sequentially, not at the same time.
Scanning is free. Removal needs an eligible one-time 30-day trial or a paid license. A computer that already used its trial may not qualify again.
-
Obtain HitmanPro from the established download route.
HitmanProOptional second-opinion Windows scanner.
Free scan. Removal requires an eligible trial or paid license.
-
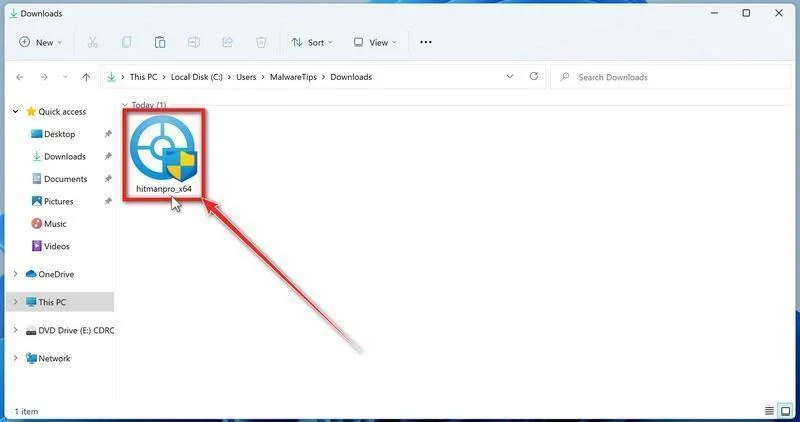
Launch the downloaded program.
Open Downloads and run the appropriate HitmanPro file for your system. Check the publisher in any Windows permission prompt before allowing it.
-
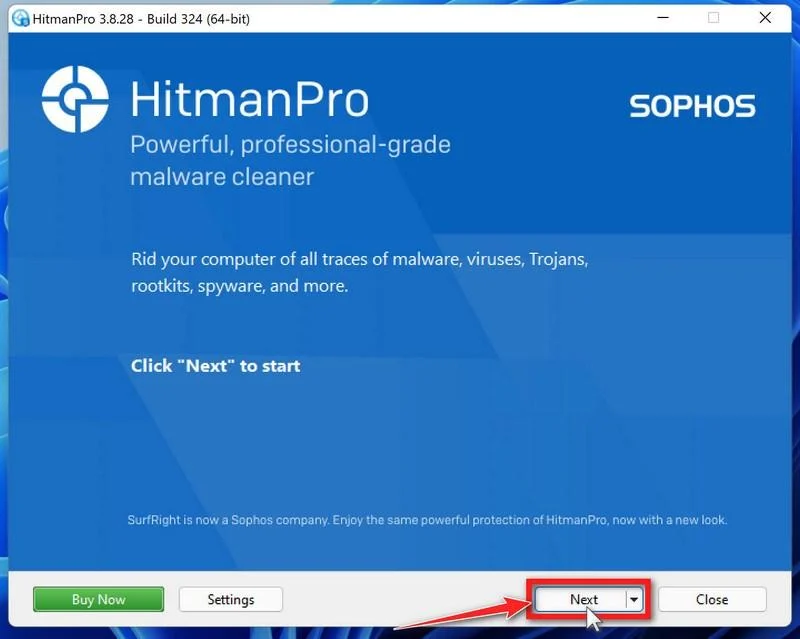
Start the scan.
Open HitmanPro, select Next, and follow its license and setup prompts. Its cloud checks require an internet connection; arrange controlled access if the PC was isolated.
-
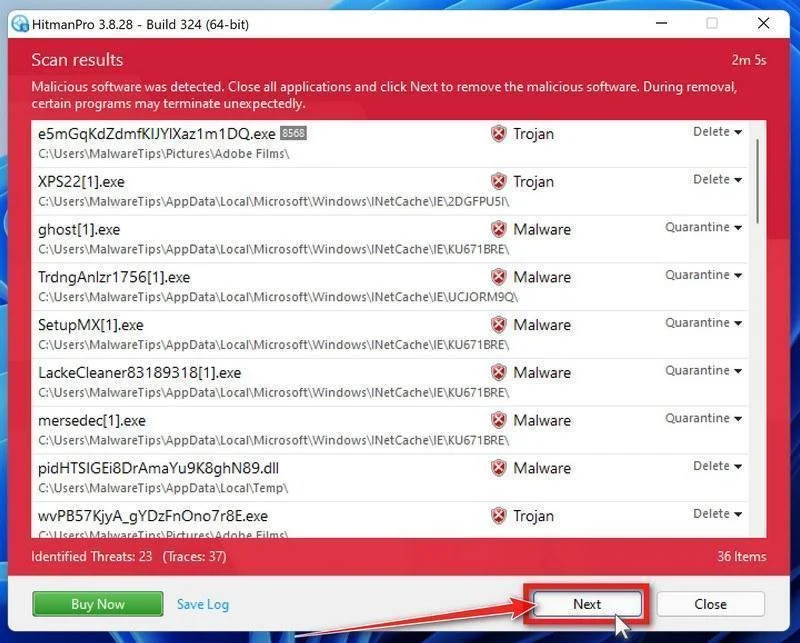
Review the results before removal.
Allow scanning to finish. Inspect the listed objects and proposed actions, then select Next for confirmed unwanted items. Save uncertain findings for qualified assistance.
-
Use an eligible license and complete cleanup.
If available, select Activate free license and follow the trial prompts. Otherwise, use an existing license or retain the report; do not assume purchase is mandatory.
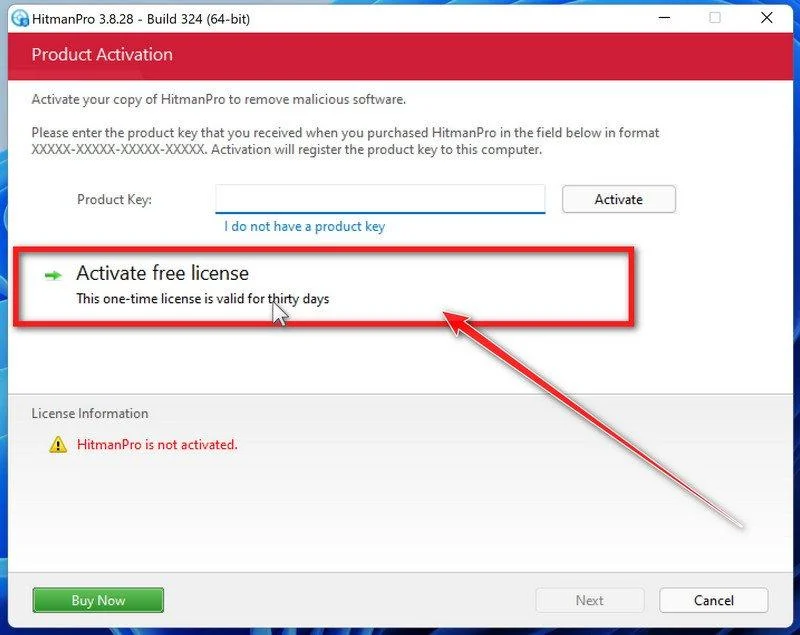
Finish the proposed cleanup and restart if requested. If problems persist, keep both scanners’ reports and seek help rather than repeatedly activating unfamiliar repair tools.
Step 4: Verify the recovery environment before resuming approvals
Keep both scan reports. Recurring detections, disabled protection, or unexplained access require further assistance and may justify a supported Windows rebuild.
Reinstall needed software from genuine publishers. Restore documents without the suspect archive, and keep invoice approval separate from the technical cleanup decision.
Help Support Reconstruct the Download Without Running It
A useful timeline begins with the email, then the browser download, extraction, and any execution attempt. Approximate times are better than omitted steps.
Record which device handled each stage. A file forwarded from a phone may later have been opened on a Windows workstation.
Include any security alert exactly as displayed, but do not interpret a product’s detection name as proof of a different malware family’s involvement.
Tell support whether you signed in to important services afterward. That helps prioritize session review without asking you to reproduce the exposure.
For a shared workstation, identify the relevant users. Someone who did not open the email may still have used the computer after the suspected execution.
Note whether the archive was saved to a synchronized folder. Support may need to check its presence on other devices without asking anyone to open it.
Keep the technical incident reference separate from the genuine invoice number. This prevents an investigation into malware from becoming accidental approval of the claimed payment.
Frequently Asked Questions
Is Progress Claim No. 7R a verified invoice?
No genuine claim or payment obligation is established by the reported email. Ask the actual project contact to supply the document through an approved route.
Why is the .vbs file important?
It is a script type, not a normal invoice page. Running untrusted scripts can initiate actions beyond viewing the promised document.
Does downloading the archive prove infection?
No. Report the download, but distinguish it from running its contents. Your support team can assess the actual exposure and required cleanup.
Which malware will every recipient receive?
That cannot be determined from the subject alone. FormBook and PhantomStealer are reported payloads, not a universal diagnosis for all copies or recipients.
Can I fix it by changing the file extension?
No. Renaming a file does not convert its contents or authenticate its source. Obtain the real document separately instead.
Should accounts payable stop all project payments?
Use the organization’s fraud and approval procedures. Flag the suspicious request and verify relevant transactions without treating unrelated genuine invoices as automatically fraudulent.
The Bottom Line
Do not run the Progress Claim download to review an invoice. Its reported script delivery is incompatible with an ordinary document-certification task.
If it executed, contain the computer and involve trusted support. Recover exposed accounts separately while the real project team verifies any outstanding payment request.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.