

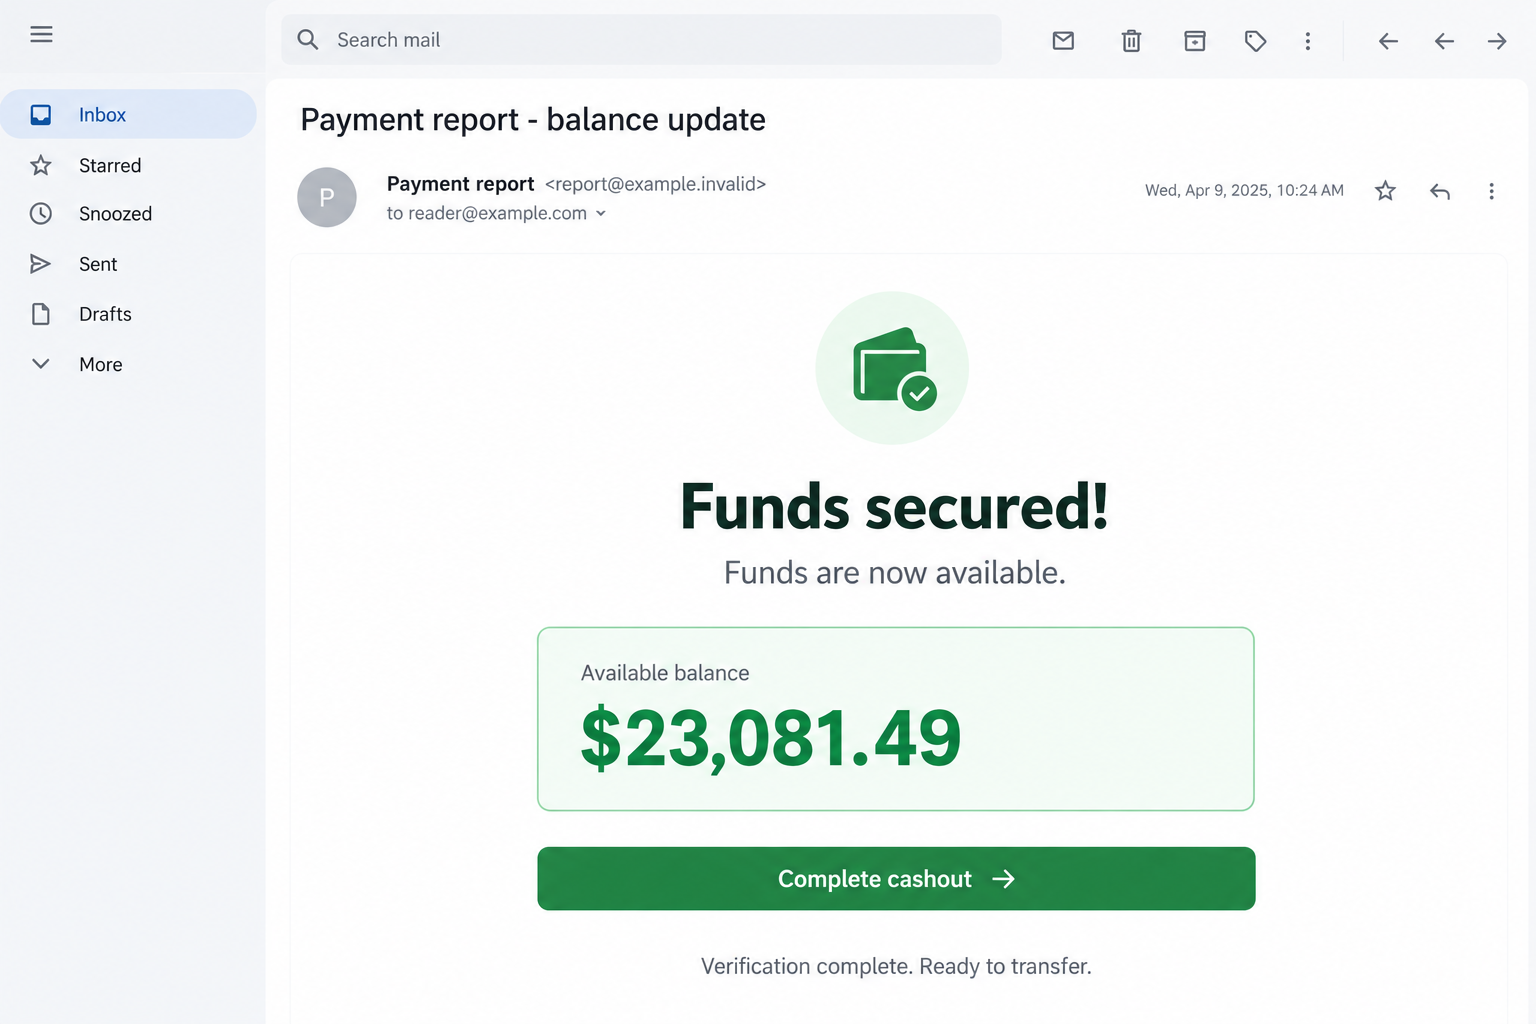
A payment report says your balance has been checked and the money is ready. A large amount sits above a button labeled Complete cashout.
There is no long application to finish, just one more step. Before taking it, ask which account this notice is actually talking about.
Overview
The email treats an unexplained balance as already yours
The Funds Secured email scam claims an account review is complete and a balance is available for withdrawal. One reported version displays $23,081.49.
Words such as verified and secured make the payment sound settled. But the message doesn’t independently establish why the recipient is entitled to that money.
A payment report is not a bank record. Its balance remains a claim until it can be matched to an account and transaction you recognize.
A legitimate Google service appears along the reported route
The Complete cashout link was reported to lead through Google Apps Script, a genuine platform that can host web applications created by other people.
That doesn’t make Google the payer or validate the amount. A legitimate hosting service can carry content or a redirection created by an untrustworthy user.
The distinction matters because a recognizable domain can make a reader relax just before another page asks for information, access, or payment.
The safe response is to verify the supposed account independently
Do not continue through the cashout button. Open any service you genuinely use through its established app or saved address and check its actual records.
The final destination and exact follow-on request are not established here. The email illustration depicts the lure, not money held for a real recipient.
- A substantial balance appears without a clear, independently checked origin.
- The message presents verification as complete before you recognize the account.
- One button supplies the proposed route to the money.
- A familiar intermediate host is not evidence of a trustworthy payout.
Why Ready to Transfer Is Such a Persuasive Phrase
A vague earning opportunity asks you to imagine a future benefit. This notice suggests that the difficult work is finished and only collection remains.
That changes the question in your mind. Instead of asking whether money exists, you may start wondering what to do before the opportunity disappears.
The language also creates a sense of ownership. Ignoring the notice can feel like leaving your own funds behind, even though that ownership hasn’t been demonstrated.
An exact amount strengthens the impression. Cents and a neat balance card resemble accounting, but precision in a display is not evidence of a real financial obligation.
The operator can choose any figure. What matters is whether a genuine service can connect it to transactions, terms, and an account you actually control.
A copied logo or professional email layout doesn’t supply that connection. Nor does an assertion that an unnamed review has already verified everything.
If you cannot identify the payer and the reason for payment without the email’s help, don’t let the amount rush you into a new relationship.
Notice how little the recipient is asked to question. The payment is described as approved, so skepticism can feel like an unnecessary delay rather than sensible verification.
That is a framing trick, not financial evidence. You can decline the invitation without forfeiting money that the sender has never shown belongs to you.
How the Funds Secured Email Scam Works
Step 1: A payment report skips the question of where the money came from
The message starts with completion: the review is finished, the balance is checked, and withdrawal is available. That framing treats entitlement as a fact.
The reader is encouraged to accept the premise before seeing any supporting account history. There is no need for a convincing earning story if collection feels immediate.
Someone who has used reward sites, investment apps, or old payment services might fill that gap from memory. The sender doesn’t need to name the correct one.
Don’t connect the notice to an old account by guesswork. Check that service directly and see whether its own records show the same event.
Step 2: The cashout button takes control of the route
Clicking makes the email the starting point for the entire transaction. The sender decides which page you see and what explanation appears next.
The reported intermediate route uses Google Apps Script. Its presence can look reassuring because the domain belongs to a company the reader already knows.
However, the owner of hosting infrastructure is not necessarily the author of the content. A real domain can serve another person’s application.
The Apps Script web-app documentation describes how developers can publish browser-accessible applications. That capability is not a payment guarantee.
Assess each subsequent destination and request separately. A trustworthy-looking first address does not authenticate whatever follows it.
Step 3: A later request may turn collection into exposure
A deceptive cashout journey can ask for credentials, financial details, software installation, or money. Which request appears depends on the destination.
Those are possible outcomes, not a list of stages verified for this exact message. No completed withdrawal or tested final form is documented here.
The appropriate boundary is still clear: don’t supply sensitive information or authorize access to chase an unexplained balance.
If a page requests a fee before releasing funds, don’t assume that paying will prove the claim. It would create a real outlay for an unverified promise.
If it requests account permissions, read what access is being requested. An application’s technical permission screen cannot establish why it deserves that access.
Step 4: The next message can reuse what you already revealed
Replying or entering contact information can make later approaches more personal. A follow-up may repeat your details or refer to the attempted withdrawal.
That continuity can look like account support. It may simply reflect information gathered during the first interaction.
Another message might claim the payout is pending, blocked, or awaiting confirmation. A changed status label is not proof that money has been transferred.
Stop measuring progress through the sender’s own screens. Look instead at independent account records and at the information or money you have actually supplied.
What a Google Address Can and Cannot Verify
A secure connection helps protect traffic to the site being visited. It doesn’t certify every financial statement displayed there or every person using a hosting platform.
It is possible to trust the platform’s identity while rejecting a particular user’s content. Those are different decisions.
The same principle applies to shared documents, forms, and other hosted pages. An established service may carry an invitation that the service itself did not author.
Do not conclude that Google has been hacked merely because its platform appears in a suspicious journey. User-created applications are part of the platform’s ordinary purpose.
Conversely, don’t assume content has been reviewed or endorsed just because it loads successfully. Hosting availability is not an audit of the offer.
If a sign-in prompt appears, check whose account it concerns and why signing in is necessary. Don’t enter a password simply because you recognize part of the address.
If a genuine permission screen appears, that is a separate decision from entering a password. You could grant unwanted access without typing a password into a counterfeit form.
Read the application’s identity and requested access, not just the provider’s logo. Permission to read mail or files would need its own credible purpose.
Don’t approve broad access because a page describes it as verification. The label used by the promoter does not narrow the permission being requested.
There is no established permission-grant stage in this reported case. The distinction is useful if your own interaction went further than the known email.
Check for a Real Payment Without Following the Cashout Link
First identify a payer you actually recognize. A genuine balance should connect to an existing account, a sale, a refund, work, or another explainable transaction.
Open that service using a route you already trust. Check its activity and balance inside the account rather than searching for the email’s payout button.
If no familiar account shows the claimed funds, don’t create a new one at the sender’s destination just to investigate.
Contact the supposed payer through independently obtained support details if there is a plausible reason for a payment. Give the message’s claim, not your password.
Keep unrelated earnings separate. Having a real balance at one service doesn’t authenticate an unexpected report from someone using a similar payment phrase.
A support reply should answer where the money came from and which account records contain it. A repeated assurance that verification is complete doesn’t answer either question.
If you were expecting a genuine refund, compare its original purchase reference and merchant with the actual service’s records. A similar amount alone isn’t enough.
Keep the expected transaction separate from the unsolicited notice until the payer confirms the connection. Otherwise, a real refund can become the excuse for trusting a false one.
Don’t send a screenshot of your bank account as proof you haven’t received the money. That introduces private information without establishing who is asking.
What to Do if You Have Fallen Victim to This Scam
Stop the cashout process. Don’t retry the button, make a verification payment, or accept new instructions sent by the same contact.
Write down what happened after the click. Distinguish a page you only viewed from a form you submitted, a permission you granted, or software you ran.
Keep a usable incident record. Save the email, its actual link, and any destination addresses already visible in your browser history.
Include dates, requested amounts, and receipts if relevant. Don’t revisit a dangerous page merely to obtain a more complete screenshot.
Replace any password entered at an untrusted destination. Begin with the affected service through its genuine website, not the payment notice.
Replace reused credentials elsewhere too. If the exposed account is a workplace mailbox, notify the responsible administrator so account access can be reviewed.
Review access you authorized. If you approved an application permission, inspect connected applications through the account provider’s real settings.
Remove unfamiliar access and check recovery details. Google’s compromised-account guidance helps separate account recovery, suspicious activity, and device checks.
Tell your bank or payment provider about an actual payment. Describe the promised cashout and the reason given for the charge.
Ask promptly about stopping or disputing the transaction. Preserve payment references, and don’t let the sender delay that call with a promised refund.
Protect financial details that were disclosed. If you entered card information or banking credentials, explain exactly what was shared to the relevant institution.
A payment request and a stolen bank password require different responses. The provider can advise on restrictions, replacement, and monitoring appropriate to the exposure.
Check unwanted software if the page introduced it. Don’t install a cashout helper, remote-support app, or browser extension on the sender’s instruction.
If software was installed, Malwarebytes can help inspect the device. AdGuard may reduce deceptive advertising, but neither establishes a balance or reverses a payment.
Report the deceptive invitation and watch for another approach. Use the email provider’s reporting tools and the hosting platform’s appropriate abuse process.
Reject anyone promising to unlock or recover the same funds for a new charge. Familiarity with the original message does not make a second contact trustworthy.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
If the Page Said Your Withdrawal Was Successful
A success screen is another claim made by the page. Verify an actual credit in the receiving account through that institution’s established app or website.
Don’t treat a transaction number supplied by the promotion as confirmation unless the real payment service can recognize it in its own records.
If an unexpected credit genuinely appears, ask the institution what it represents before moving or returning money at a stranger’s request.
Do not send part of a supposed payout elsewhere to correct an alleged error. That could create a separate loss while the original credit remains uncertain.
The useful test is independent settlement, not a green checkmark. You don’t need to keep following the sender’s instructions to determine whether your bank received anything.
Ask the receiving institution about any uncertainty over a pending credit. Don’t rely on the sender’s explanation of when a displayed amount becomes usable.
If no payment appears, don’t try a different card or another account at the promotion’s request. A failed cashout is not a reason to disclose more information.
Frequently Asked Questions
Is the $23,081.49 in the Funds Secured email real money?
The message does not establish that balance. Treat it as an unsupported claim unless a genuine service you recognize confirms the funds in your account.
Does a Google Apps Script link mean Google approved the payout?
No. Apps Script is legitimate infrastructure for user-created web applications. Its use doesn’t make Google the author, payer, or guarantor of this notice.
Is Google Apps Script itself malicious?
No. The concern is abuse of a legitimate service within a deceptive journey. Do not confuse the hosting platform with the person responsible for the invitation.
What if I clicked but didn’t type or approve anything?
Close the page and note any unexpected download or permission change. A click alone is not evidence that your bank account was accessed.
Should I pay a small fee to test the withdrawal?
No. A test payment would expose real money without verifying the balance. Check the supposed account independently instead of funding an unverified release condition.
Can a scan determine whether the balance exists?
No. A device scan addresses software exposure. Only the genuine financial service’s records can establish whether an actual account holds the claimed money.
The Bottom Line
Do not follow the Funds Secured cashout invitation. An unexplained balance and a familiar hosting domain don’t establish a legitimate payment.
If you already acted, respond to the information, permissions, software, or money actually exposed. Check real account records and contact your payment provider promptly about any payment made.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.