

A free beauty sample email says a familiar pharmacy is giving loyal customers a complimentary beauty pack. The only requirements are a two-minute survey and a small delivery fee. The offer feels harmless because the payment is tiny.
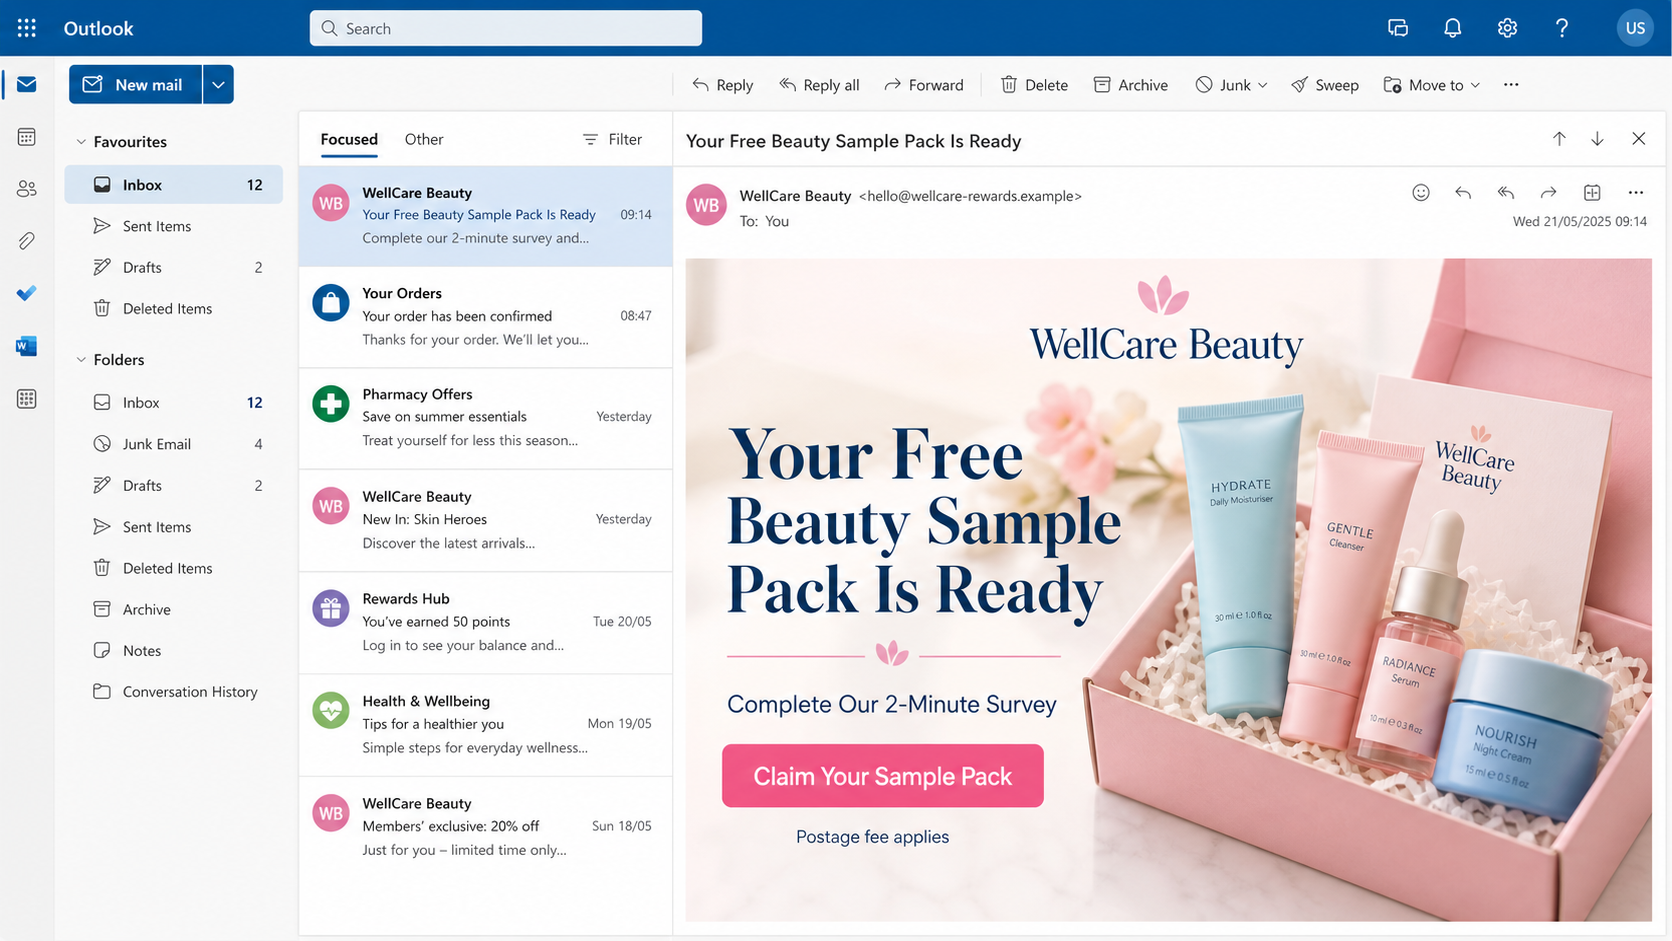
A large campaign uncovered in 2026 impersonated Boots and prepared recipient lists containing 8,894,920 email addresses. The emails used Boots-style branding and personalized subject lines to make a mass operation feel like an individual reward.
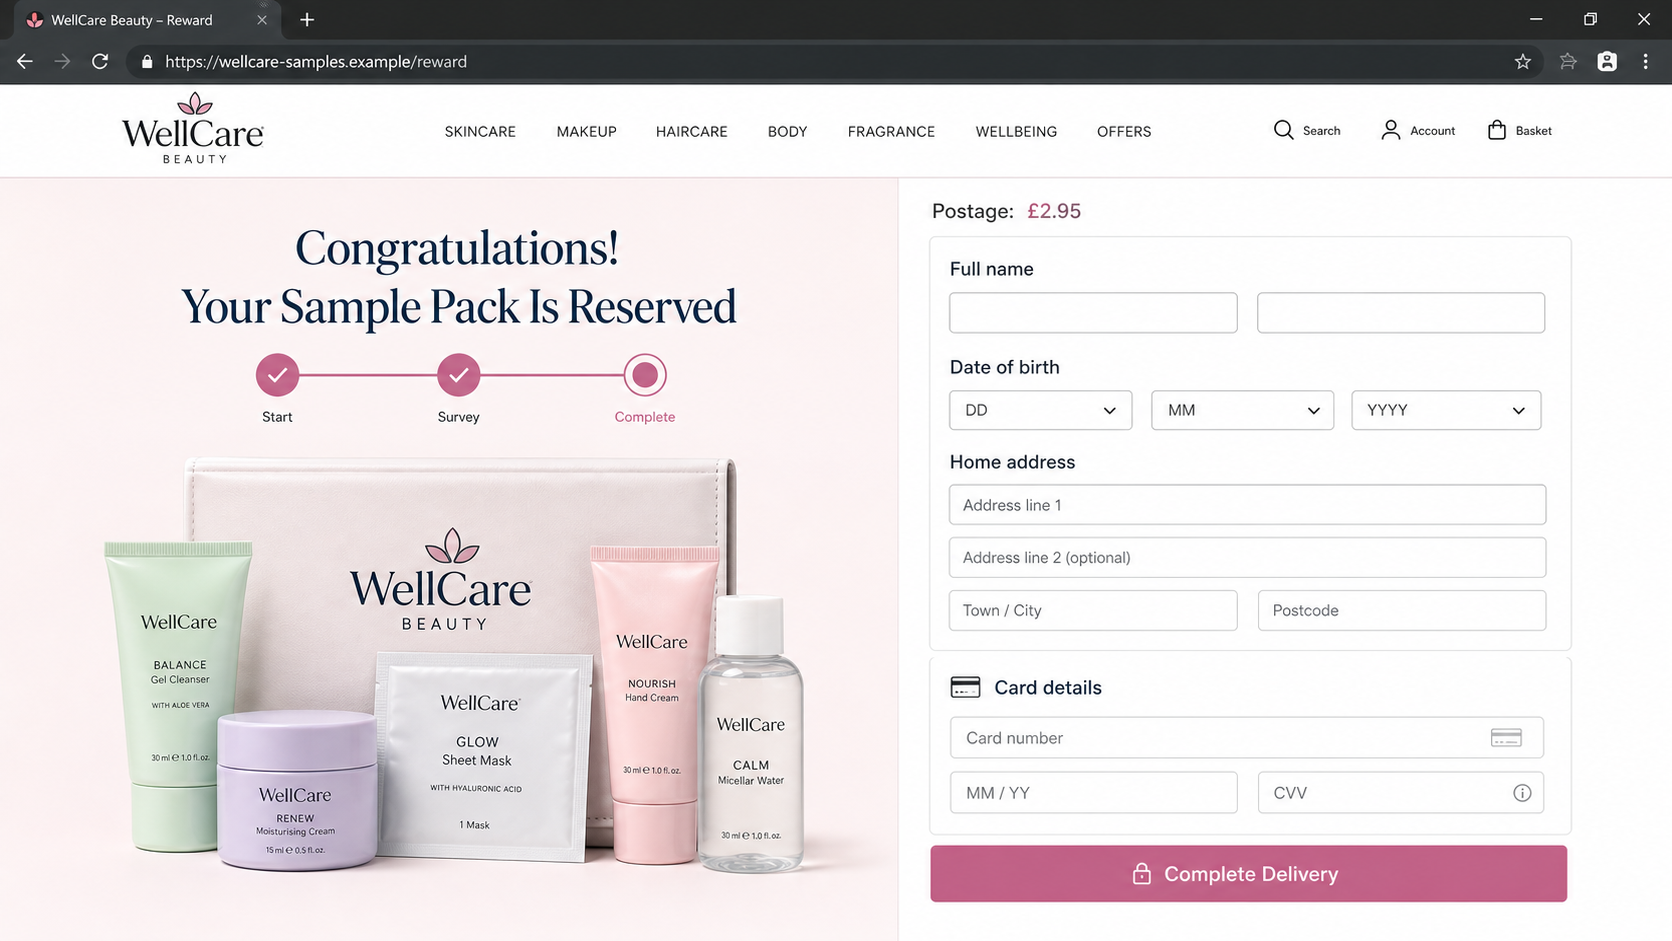
The link opened a cloned retail page with a customer survey. After the visitor supplied a name, email address, date of birth, phone number, and home address, the funnel requested card information to cover a £2.95 delivery charge.
Boots itself was not reported breached. Investigators found that the criminals used a compromised UK business server to send messages and a hacked Bolivian government website to host the fake store.
Overview
Behind that polished promotion, however, the real products being collected are personal information and card details.
A free sample promise lowers the value of every warning sign
Beauty samples are common enough to sound plausible. A shopper may have joined a loyalty program, bought cosmetics before, or received real promotional mail from a pharmacy, so the message does not feel completely random.
The scam adds a short survey because effort creates a sense of qualification. After answering several questions, the visitor feels that the reward was earned rather than offered to everyone who clicked.
The £2.95 postage request seems small beside the displayed sample value. That comparison encourages the victim to enter a full card number for a charge they might otherwise question.
Compromised systems make the campaign harder to dismiss
The messages were not simply sent from a new disposable mail server. Investigators said the attackers compromised a small UK business system and installed legitimate bulk-mailing software to distribute the campaign.
The fake store was placed inside a directory on a compromised Bolivian government cultural institute website. A government domain can appear safer to a person or automated filter than a newly registered shopping address.
Neither compromised organization was the seller of a Boots promotion. Criminals used their infrastructure as camouflage, which is why a familiar-looking sender route or respected domain cannot replace verification.
The survey builds a complete identity and payment profile
The form reportedly collected a name, email address, date of birth, phone number, and home address before reaching the card screen. Those details can support targeted phishing even if the payment is declined.
Card number, expiry date, security code, billing address, and phone number create a useful fraud package. The criminals can attempt charges, sell the record, or contact the victim while pretending to be a bank investigator.
The visible £2.95 amount does not define the risk. A criminal page can store the card details, attempt different amounts, or place the victim into another offer without delivering any sample pack.
- The email impersonates a known retailer with copied colors and product images.
- A short satisfaction survey creates the feeling that the reward was earned.
- The campaign uses compromised third-party systems rather than a Boots data breach.
- The form collects identity information before requesting card details.
- A small £2.95 postage charge makes the payment screen feel low risk.
- The same infrastructure can rotate to HMRC, cryptocurrency, or other retail themes.
How a Nearly 9 Million Address Campaign Was Assembled
Investigators found six recipient lists containing a combined 8,894,920 email addresses. A list that large is not evidence that Boots provided customer data, and reporting did not identify a Boots breach.
The attackers had gained access to a small UK company's terminal server. They installed Gammadyne Mailer, a legitimate program businesses can use for newsletters, and configured it for extremely fast delivery.
Huntress reported blocking 29,954 outbound email connections within 104 seconds after isolating the affected environment. It could not establish how many messages had already reached inboxes before containment.
The phishing kit lived on a compromised website belonging to Bolivia's Instituto Plurinacional de Estudio de Lenguas y Culturas. The criminals placed the fake store in a boots_store path under that unrelated government domain.
This architecture separated the visible brand, sending computer, web host, and final data collector. Each borrowed a little trust while making the real operator harder for the recipient to identify.
Files found during the response also pointed toward other UK-focused themes involving tax and cryptocurrency. That suggests a reusable operation, not a one-off beauty promotion built around one retailer.
What Separates the Fake Boots Survey From a Real Retail Promotion
The email reportedly displayed Boots branding and could show a sender identity resembling Boots hello@boots.com. The actual delivery path and linked page, however, were tied to compromised third parties rather than Boots systems.
The fake survey accepted answers and moved every visitor toward the same sample reward. A legitimate research survey may offer a prize draw, but it should disclose the organizer, eligibility, privacy terms, and exact relationship to the retailer.
The landing page copied the look of a real store while requesting a broad set of personal details. The quantity of data was unnecessary for a simple customer-opinion survey.
The final £2.95 postage form asked for payment-card information. A supposed free gift is not free when an unverified page needs the same data used for online purchases.
The strongest evidence is the infrastructure trail documented during incident response. A compromised business server and hacked government site have no legitimate role in a Boots reward campaign.
How the Free Beauty Sample Email Scam Works
Step 1: A personalized reward email reaches the shopper
The subject may include the recipient's email address, a random reference number, or wording such as Your Free Gift Is Waiting. Personalization makes bulk spam feel connected to a real customer account.
The design uses a trusted retailer's logo, colors, pharmacy imagery, and recognizable beauty products. The actual sender details may be hidden behind a friendly display name.
Nothing in the message proves the retailer selected the recipient. The campaign can send the same reward to millions of addresses obtained from unrelated lists or prior leaks.
Step 2: The click lands on a copied customer survey
The page asks ordinary questions about shopping frequency, product preferences, store cleanliness, or customer satisfaction. Every answer appears to move the visitor closer to the gift.
A progress bar and eligibility messages make the experience look interactive. In many reward scams, the answers do not affect the result because every participant is approved.
The visitor spends time on the survey before seeing a payment form. That investment can make abandoning the process feel like wasting an opportunity already earned.
Step 3: A compromised government domain disguises the fake shop
In the documented campaign, the Boots-themed kit was hosted on a hacked Bolivian government cultural institute site. The address did not belong to Boots, regardless of the page design.
A .gov or national government suffix can reduce suspicion, but compromised legitimate websites are regularly abused to host malicious files and redirects. Domain reputation is not permanent proof of control.
A real Boots promotion should be reachable from Boots' official website or application. An unrelated overseas institution has no reason to process a UK pharmacy reward.
Step 4: The survey becomes an identity-harvesting form
The page requests a full name, date of birth, phone number, email address, and home address. The questions are framed as delivery requirements even before a legitimate offer has been verified.
This information helps criminals tailor later messages. A caller who knows the victim's birthday, address, and recent survey activity can sound like a retailer, bank, or delivery service.
Use data minimization as a warning test. A customer survey does not need a date of birth and full delivery profile simply to record opinions.
Step 5: A small postage fee opens the card-data trap
The fake checkout says the sample pack is free and asks only £2.95 for delivery. Product photos and a high claimed value make the payment appear reasonable.
The form then collects the card number, expiry date, security code, name, and billing details. The criminal receives information worth far more than the small charge shown on screen.
A low initial amount can also be used to test whether the card is active. Later attempts may use a different merchant description or amount.
Step 6: The submitted record feeds follow-up fraud
The victim may receive delivery texts, bank alerts, or calls referencing the sample order. Some will claim the card was compromised and ask for a one-time code or transfer to a safe account.
Email and phone data can be sold to other operators. The recipient may see more pharmacy offers, tax messages, cryptocurrency promotions, and parcel-payment demands.
Even a declined card does not mean the attempt failed. The identity profile remains useful until the victim secures accounts and becomes more cautious about targeted contact.
Step 7: The campaign rotates brands and infrastructure
When a page is removed, the same kit can be uploaded to another compromised site. The retailer, free gift, survey questions, and postage amount can change without rebuilding the operation.
Summer beauty packs can become perfume samples, pharmacy hampers, supermarket vouchers, or holiday rewards. The repeatable path is email, survey, winner message, personal details, and card fee.
Recognizing that sequence protects you after individual domains and screenshots are outdated. Verify every reward through the retailer's real site before supplying data.
Company, Address, and Fulfillment Checks
The retailer name is stolen, not the identity of the sender
Boots is a real retailer, but investigators said its systems were not the source of this campaign. The criminals copied the brand while operating through unrelated infrastructure.
A sender line that visually says Boots can be forged. Expand the technical details and compare them with genuine messages already received from the retailer.
If an offer is real, customer support reached through boots.com should be able to confirm it. Never call a number embedded only in the reward email or cloned page.
The web address belongs to an unrelated compromised organization
The fake store was hosted on a Bolivian government cultural institute domain, not on Boots' official website. The institution was reportedly another victim whose site had been compromised.
A legitimate-looking address can still lead to malicious content when one directory, plugin, or account has been taken over. Always ask whether the organization in the domain logically belongs in the transaction.
Do not send complaints or card details to the unrelated host. Contact the impersonated retailer and your bank through independently verified channels.
There is no accountable support team behind the free gift
The fake checkout does not provide a verifiable merchant responsible for the £2.95 charge, delivery, data handling, refunds, and disputes. Branding is used in place of an accountable legal identity.
A reply to the phishing sender may confirm that the address is active. It can also invite more scripted messages designed to keep the victim engaged.
Real support should know the campaign reference, privacy notice, fulfillment partner, and delivery terms. If Boots support cannot find the offer, stop immediately.
The sample fulfillment trail does not exist
A genuine sample campaign identifies what will be shipped, who fulfills it, when it will arrive, and what happens to the customer's data. The phishing page primarily creates a path to card collection.
The compromised server that sent the email and the hacked site that hosted the form were not product warehouses. Their involvement shows that the campaign lacked a normal retail supply chain.
Do not confuse product photographs with inventory. A page can copy images from a retailer in seconds without possessing any sample packs to send.
Why a £2.95 Charge Can Produce Much Larger Losses
The small amount is a psychological anchor. It tells the shopper that the decision is trivial, even though the form requests the complete information needed for card-not-present transactions.
Criminals may test the card with a small authorization, attempt a larger purchase, or sell the record. They may also combine the card data with the identity profile collected during the survey.
Some reward funnels contain recurring-membership terms. The documented Boots campaign was reported as payment-card theft, so do not invent a subscription if your receipt does not show one.
Monitor for both unauthorized purchases and recurring descriptors.
The best defense is to avoid entering any card data. If a retailer genuinely offers free samples, find the promotion by navigating from its official home page or loyalty application.
Treat a too-perfect page on an unrelated domain as a stronger warning than poor spelling. Modern phishing kits can look cleaner than many legitimate small-business websites.
Warning Signs to Watch For
- An unexpected beauty reward claims you were specially selected.
- The email uses a reference number or your address as superficial personalization.
- Every survey answer produces the same winner result.
- The page is hosted on a domain unrelated to the retailer.
- A survey requests a date of birth, phone number, and full home address.
- A free gift requires complete card details for a tiny postage charge.
- No verifiable merchant explains delivery, privacy, or refunds.
- The offer cannot be found through the official retailer website or app.
The £2.95 figure is meant to feel unimportant. The card number and identity profile behind it are the valuable part of the transaction.
What to Do if You Have Fallen Victim to This Scam
- Stop using the fake survey and save the route. Capture the email, complete sender details, linked domain, survey screens, postage page, time, and any confirmation message. Do not revisit the page to collect more evidence.
- Call the card issuer immediately. Explain that card details were entered on an impersonation site. Ask about blocking the card, replacing it, stopping pending authorizations, and disputing every unrecognized charge.
- Watch for small tests and unfamiliar merchant names. Review transactions daily at first. A test may be smaller than £2.95, and a later charge may not contain the Boots name.
- Secure the email account used in the survey. Change a reused password, enable multifactor authentication, review sign-ins and forwarding rules, and expect more convincing messages addressed to you personally.
- Prepare for targeted calls and delivery texts. Do not share bank codes, card PINs, or one-time passwords with anyone claiming to fix the sample order. Contact the bank using the number on the card.
- Limit identity misuse. If you provided a date of birth and address, monitor important accounts and credit reports. Follow the recovery plan at IdentityTheft.gov if those details appear in fraudulent applications.
- Scan the device if the site downloaded anything. A normal survey should not install software or browser extensions. Remove unknown items and run a full Malwarebytes scan if a file was opened.
- Reduce exposure to cloned promotions. AdGuard can block many malicious ad networks, pop-ups, and known phishing pages. It will not reverse submitted card data, so continue the banking and account-recovery steps.
- Report the campaign. In the UK, forward suspicious email to report@phishing.gov.uk and report card fraud to the bank. Also report the message to the email provider and the impersonated retailer.
Frequently Asked Questions
Was Boots hacked in the free sample campaign?
Reporting said Boots' own systems were not compromised. Attackers impersonated the brand using a hacked UK business server and an unrelated compromised government website.
Is Boots really giving away free beauty samples?
Retailers run genuine promotions, but this specific email path was fraudulent. Confirm any offer by navigating from boots.com or the official application.
Why did the email know my address?
Large recipient lists can come from old leaks, marketing lists, or other sources. Personalization does not prove the sender has access to a Boots account.
What happens if I only completed the survey?
The information submitted can support targeted phishing and identity misuse. Secure the email account and become cautious about calls or texts referencing the reward.
What if the £2.95 charge is still pending?
Contact the card issuer now. A pending test can precede later attempts, and the issuer can advise whether the card should be replaced.
Does a government web address make a reward page safe?
No. Legitimate sites can be compromised. A Bolivian cultural institute domain had no logical role in a UK pharmacy promotion.
The Bottom Line
The free beauty sample email scam wraps card theft in a cheerful customer reward. The survey, product images, and £2.95 delivery fee make a large phishing operation feel like a harmless bargain.
Do not judge the offer by the logo or the size of the fee. Verify the promotion through the retailer's official website, and never submit card details to an unrelated survey domain.
If you paid, secure the card and email account immediately. Then monitor for follow-up messages that use the personal details collected during the fake survey.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.