

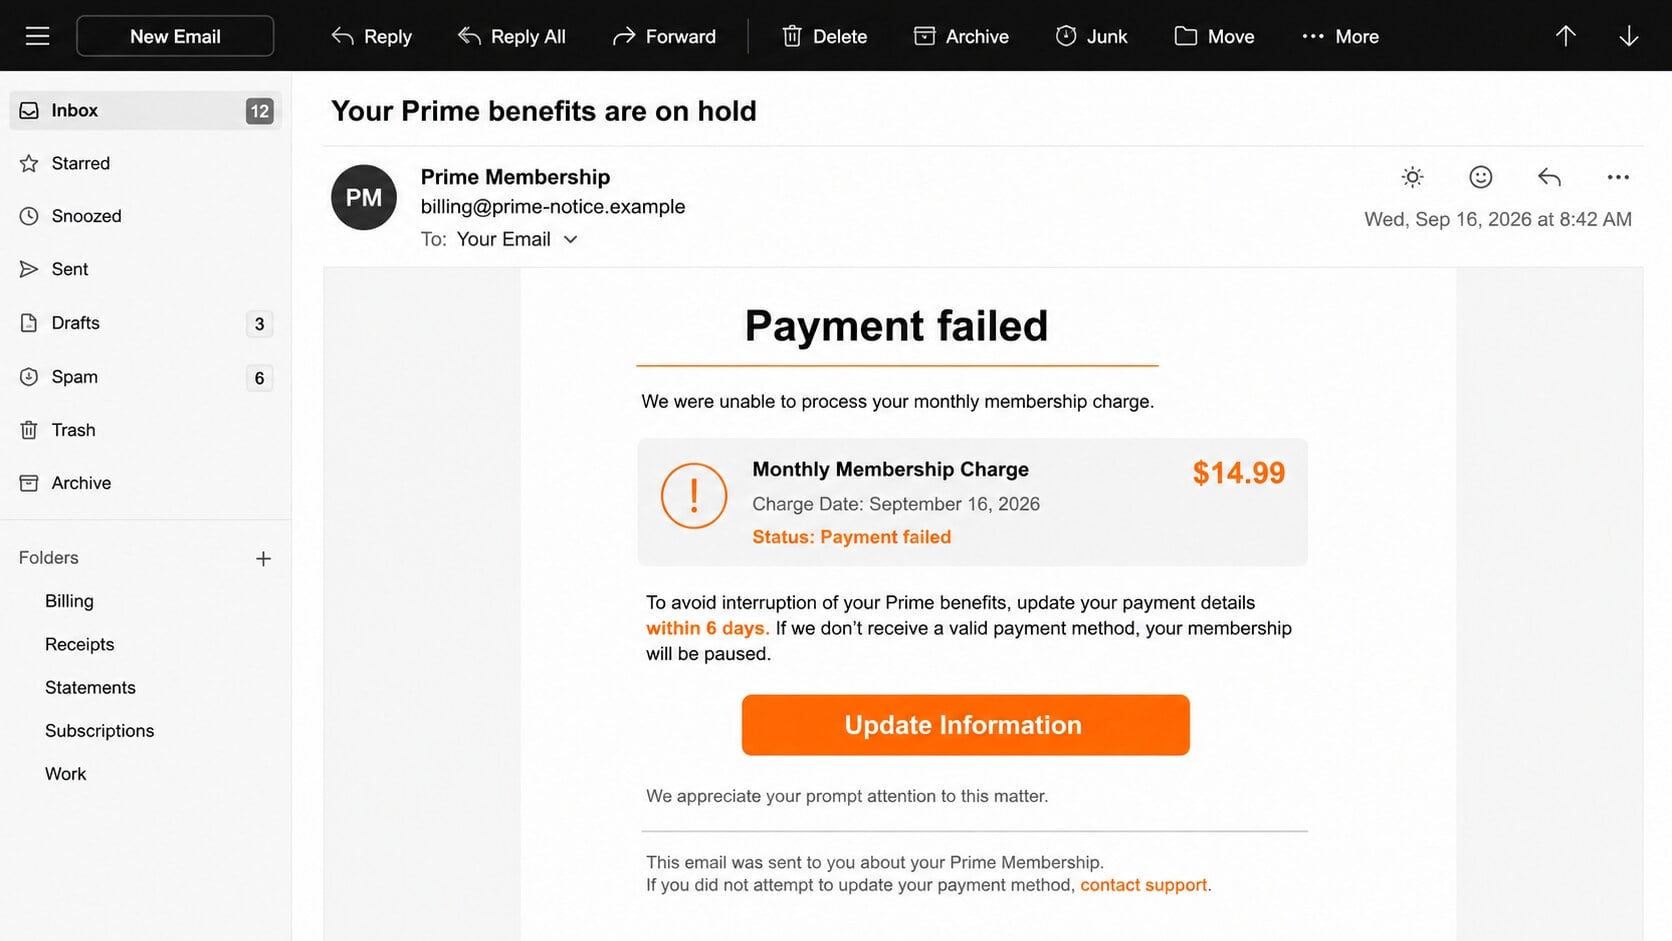
A billing message says a $14.99 Prime payment failed and your benefits are already on hold. Six days remain before the membership may disappear.
The timing, familiar price, and ordinary account language can make the request feel routine. The page behind the orange button tells a different story.
Overview
The email creates a believable subscription problem
The Amazon Prime Payment Method Update email scam claims the next monthly membership charge could not be processed.
One observed version names a $14.99 charge, says benefits are paused, and gives the recipient six days to provide another payment method.
The update button opens a counterfeit account journey
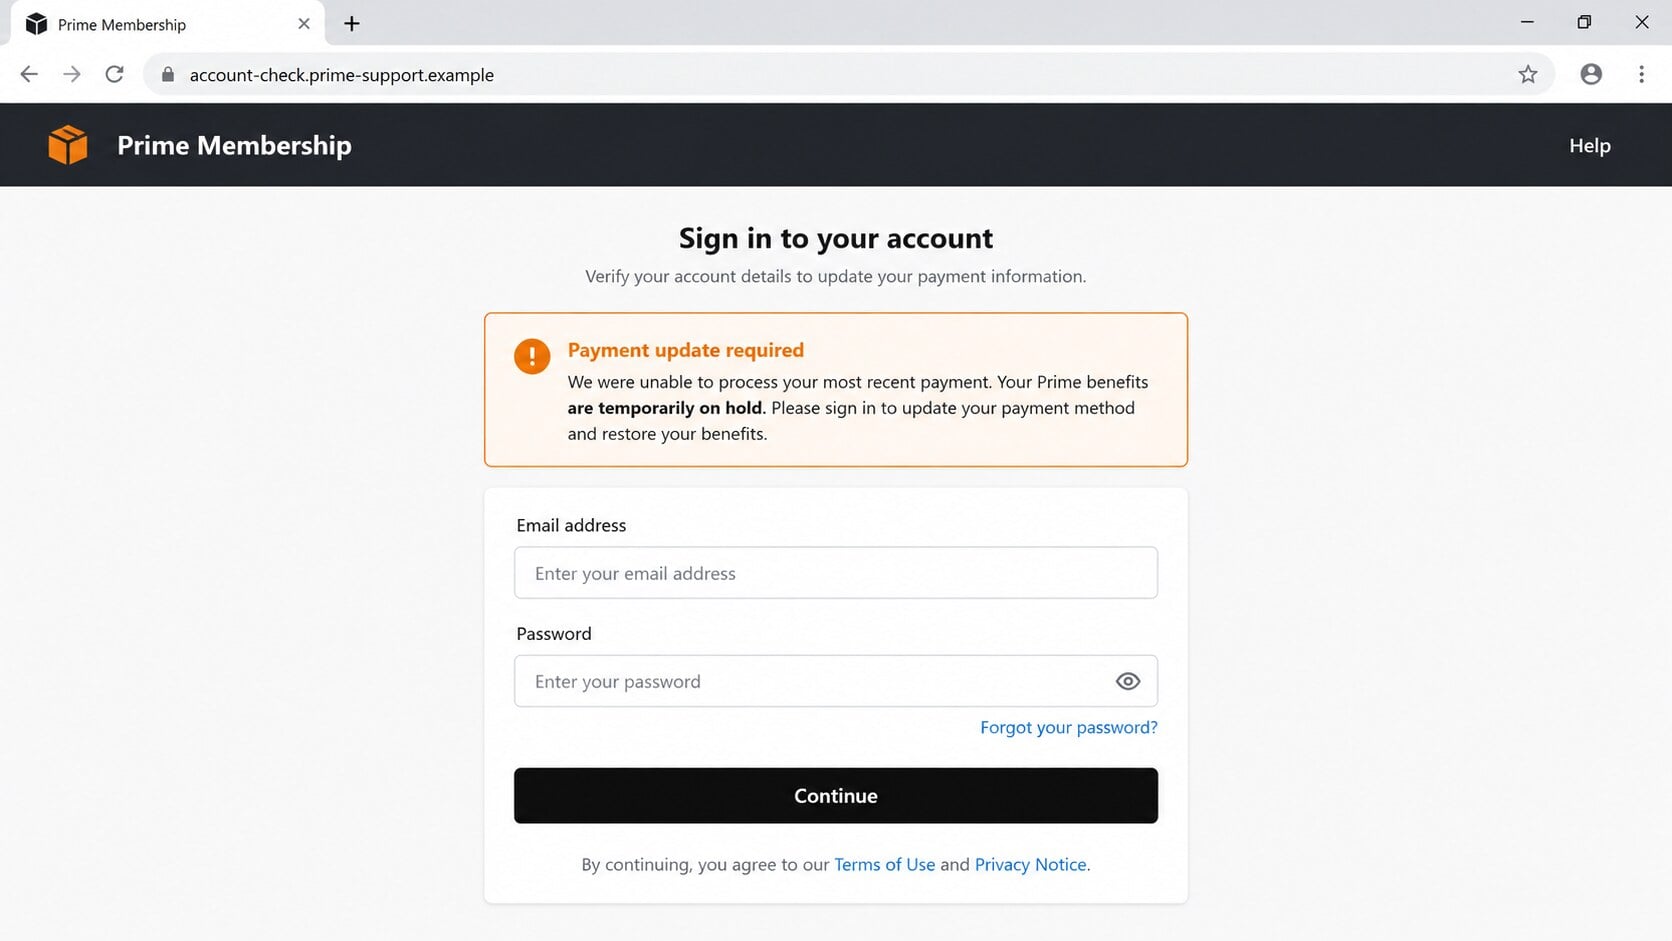
The destination can resemble a familiar retail sign-in screen. It may request an email address, password, payment card, billing address, and telephone number.
Those details do not update the real membership. They are collected by whoever controls the imitation page and its form endpoint.
The stolen information can support several crimes
An exposed retail account may reveal orders, addresses, saved payment methods, gift-card balances, subscriptions, household details, and customer-service conversations.
Card data can be tested elsewhere. Reused passwords can also open email, shopping, streaming, and financial accounts unrelated to the original message.
- The email reports a failed $14.99 monthly charge.
- Prime benefits are said to be temporarily unavailable.
- A six-day deadline pressures the recipient to act.
- The button opens a domain that is not the retailer’s established site.
- The fake flow may collect both login credentials and card details.
- The real company and its membership service are being impersonated.
Why a $14.99 Billing Alert Is Easy to Believe
Subscription renewals are ordinary. People change cards, banks replace expired numbers, and recurring charges sometimes fail for legitimate reasons.
A familiar monthly amount reduces suspicion because it sounds more plausible than an extravagant unauthorized purchase.
The message also threatens a modest inconvenience rather than immediate financial ruin. Losing delivery or streaming benefits feels irritating enough to encourage a quick click.
Recipients may already expect membership emails. The scam relies on recognition, not on proving that this particular notice came from the account.
The fixed deadline gives the story momentum. Six days sounds less theatrical than “act now,” while still discouraging a careful check.
How to Check a Prime Billing Problem Safely
Do not use the email button. Open the retailer’s official application or type the known website address into a new browser tab.
Review membership status, messages, payment methods, and recent orders from inside the authenticated account. A genuine problem should appear there.
Check the card statement for the claimed attempt. A failed charge may not appear, but the absence of any account alert makes the email less credible.
Contact customer service through the application or official website. Do not call a number printed only in the suspicious message.
Remember that a copied postal address, footer, trademark line, or customer-service phrase does not authenticate the sender. Public information is easy to reproduce.
How the Amazon Prime Payment Method Update Email Scam Works
Step 1: A fake billing notice reaches the inbox
The subject announces that Prime benefits are on hold because a payment could not be completed.
The body may include a precise time, amount, and membership period. These details simulate the transaction record found in a real billing system.
However, the sender address may belong to an unrelated domain, bulk-mail service, compromised account, or lookalike spelling.
Step 2: A cancellation deadline creates controlled urgency
The email says the membership may be canceled unless payment information is updated within several days.
This pressure is carefully calibrated. The recipient feels there is time to act, but not enough reason to postpone the task and verify it later.
Benefits are described as already paused, making the consequences feel immediate even before the stated deadline arrives.
Step 3: The update button hides an external destination
The visible button says “Update Information,” but that label reveals nothing about the underlying address.
The link can use redirection services, tracking parameters, compromised websites, or newly created domains before reaching the counterfeit login.
A familiar word such as prime, account, secure, or billing may appear inside the hostname. The complete registered domain remains the important part.
Step 4: A fake sign-in page captures account credentials
The page copies a retail account layout and repeats the payment problem. It asks the visitor to sign in before changing the card.
Submitting the form gives the operator an email address and password. A loading screen or incorrect-password message can encourage another attempt.
The visitor may then be sent to a second page instead of the real account. That continuation makes the first form appear successful.
Step 5: The next form requests payment and identity data
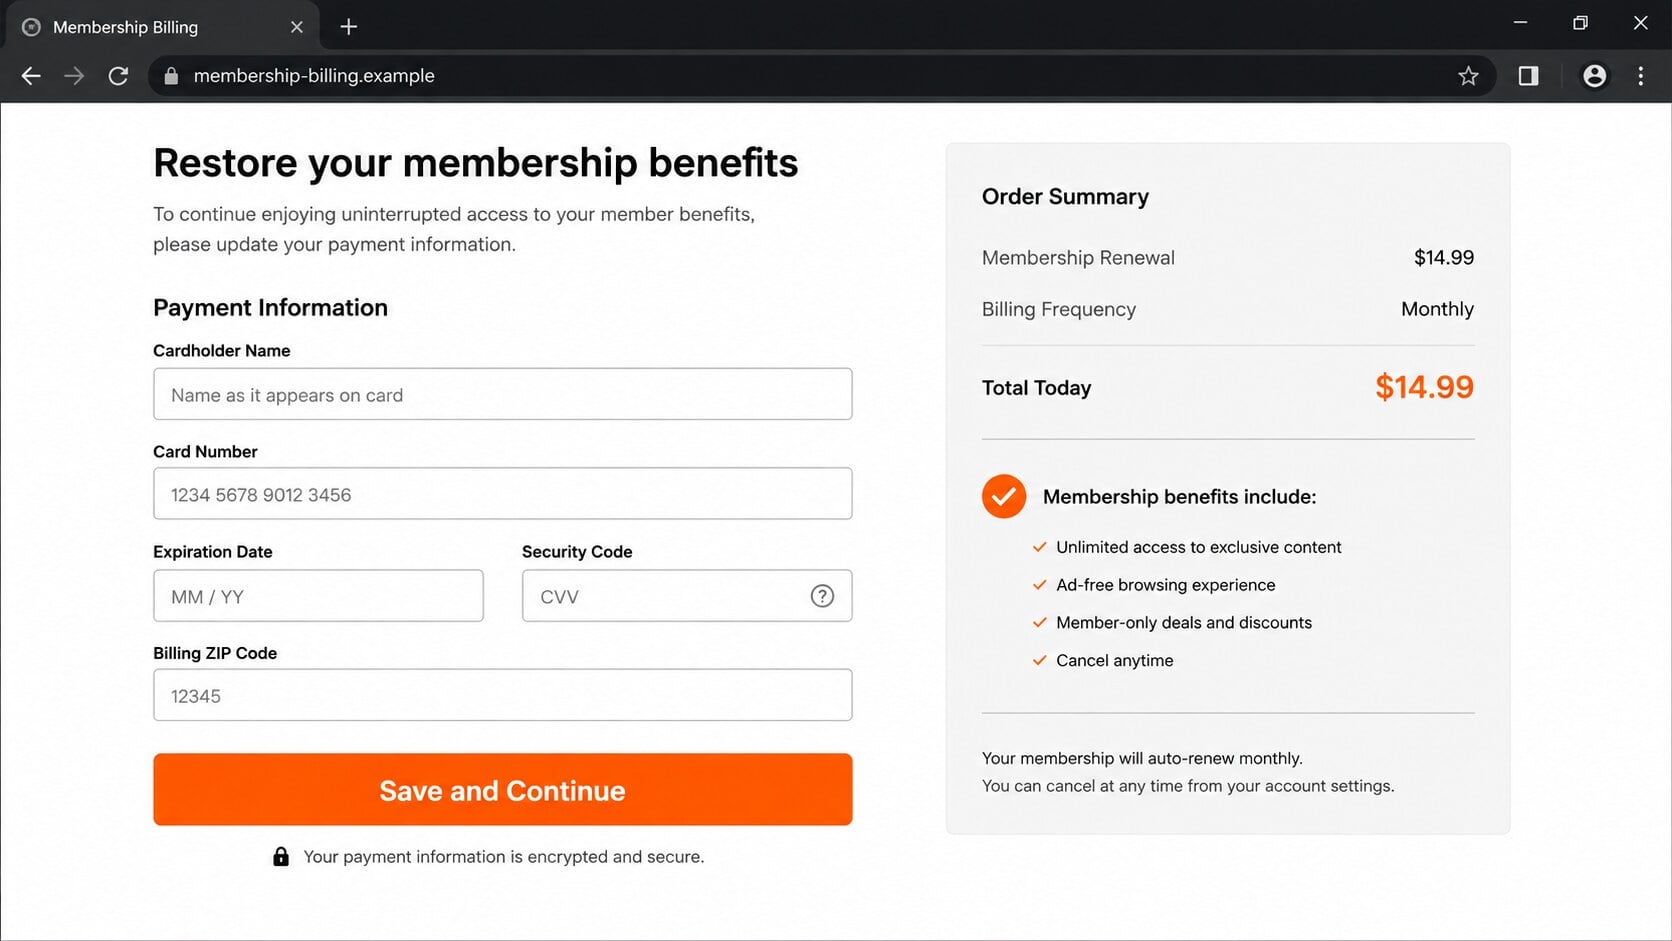
The billing page can ask for the cardholder name, card number, expiration date, security code, billing ZIP code, and telephone number.
Some variants request a full address or date of birth. That information can help criminals pass verification checks or construct stronger impersonation attempts.
The displayed $14.99 summary makes the page seem like a normal renewal. The real value to the attacker is the complete card record.
Step 6: The stolen login is tested against the real account
Criminals may attempt an immediate sign-in, change account details, inspect saved addresses, place orders, or redeem stored balances.
If multifactor authentication appears, another fake screen can request the code. Repeated approval notifications may also be sent to the victim.
A reused password is tested against email and other popular services. Email access can then help reset the shopping password permanently.
Step 7: Charges and follow-up impersonation may continue
Captured card details can be used for online purchases, small verification charges, subscriptions, or resale in criminal marketplaces.
The operator may contact the victim as “fraud support” and claim another verification step is required. This can introduce remote access or additional payments.
A redirect to the real retailer may close the journey. The victim sees a normal page and assumes the update simply took time to appear.
Brand, Domain, Support, and Billing Checks
A copied brand identity proves nothing
Logos, colors, legal footers, corporate addresses, and membership terms are publicly visible. Their presence shows design effort, not sender authorization.
Expand the email headers and compare the actual From, Reply-To, and return-path domains. Lookalike spelling and unrelated senders deserve immediate caution.
The full destination domain controls the form
Read the address from right to left around the registered domain. Extra words placed before an unrelated ending do not make it an official retailer page.
HTTPS is expected on both legitimate and fraudulent sites. Encryption protects transmission to the page owner, including a criminal page owner.
Customer support must be reached independently
Use the official application, a saved bookmark, or an address typed manually. Find support after entering that trusted environment.
Never rely on a telephone number within the questionable email. A callback operator can transform phishing into a remote-access or refund scam.
The real account and card statement settle the claim
Membership status should be visible inside the genuine account. Compare it with the card statement and any message stored in the account’s communication center.
If those records show no problem, the email has no legitimate billing context. Delete it after reporting the impersonation.
What Can Happen After Information Is Submitted
The outcome depends on which fields were completed. A clicked link, submitted password, and submitted card number require different levels of response.
A password exposes the account even if the card page was abandoned. Change it promptly and inspect account activity before deciding nothing happened.
Payment data can be used without entering the retail account. Contacting the card issuer remains necessary even after the shopping password is replaced.
Personal details can strengthen future fraud. A caller who knows the address, membership price, and last four card digits can sound unusually convincing.
Order history can reveal expensive purchases and delivery locations. Criminals may use that information in fake refund, warranty, or package-interception calls.
Gift-card balances and promotional credits deserve review. Unauthorized redemptions can occur without a conventional card charge.
How Criminals Exploit a Real Shopping Account
A captured retail password can reveal far more than a name and delivery address. Order history shows routines, household purchases, and valuable recent transactions.
Criminals may place orders using saved payment methods, then change the delivery address or redirect a package after shipment.
Some attackers buy digital goods because delivery is immediate. Gift cards, software codes, and downloadable products can disappear before a customer notices the confirmation email.
An account can also become material for a second scam. A caller may quote a genuine order number, item, or address to sound like support.
Archived messages can reveal partial card information and refund conversations. Those details make a later fake fraud alert feel specific and believable.
Household profiles deserve attention too. Shared memberships sometimes contain several addresses, stored cards, and linked devices, giving an intruder multiple places to explore.
Review orders, subscriptions, gift-card activity, archived communications, addresses, payment methods, devices, and recent security changes. Do not stop after checking the newest order.
If an unfamiliar purchase appears, contact the retailer and card issuer separately. Canceling an order does not automatically secure the account or dispute the charge.
Remove payment methods you no longer use. Fewer stored details reduce what an attacker can exploit during any future account compromise.
Enable multifactor authentication after changing the password. Choose a method protected by a device or authenticator app that the attacker cannot access.
Warning Signs in the Fake Prime Payment Email
- The sender domain is unrelated, misspelled, or hidden behind a display name.
- The greeting is generic despite discussing a specific membership.
- The email creates a deadline before the recipient checks the real account.
- The Update Information button opens a different registered domain.
- The sign-in page appears without navigation from the official application.
- Card details are requested immediately after credentials are entered.
- The page asks for more identity information than a routine card change requires.
- Spelling, spacing, or footer language contains small inconsistencies.
- No matching alert exists in the genuine account or statement.
A single typo is not the core proof. The untrusted route from email to a credential and payment form is the decisive problem.
If the membership might genuinely need attention, solve it from inside the real application. There is no benefit to using the email’s route.
What to Do if You Have Fallen Victim to This Scam
Move quickly, but keep the response organized. Secure the email account first when it shares or controls recovery for the retail account.
- Close the fraudulent page. Do not submit another password, card, one-time code, or identity document.
- Change the retail account password. Open the official application or website independently and choose a unique replacement.
- Secure the associated email. Replace reused credentials, revoke unknown sessions, and enable strong multifactor authentication.
- Contact the card issuer. Report exposed card details, review recent activity, block unauthorized charges, and request replacement when advised.
- Inspect account changes. Review addresses, orders, archived orders, payment methods, gift balances, subscriptions, household members, and connected devices.
- Cancel unauthorized orders immediately. Contact official customer support when an order cannot be canceled from the account.
- Save useful evidence. Keep the original email, headers, destination address, screenshots, submission time, and transaction records.
- Scan unexpected downloads. Malwarebytes can detect malicious files or unwanted software if the fake page delivered an installer or attachment.
- Reduce malicious-page exposure. AdGuard can block many known phishing and advertising destinations, but it cannot reverse submitted information.
- Report the impersonation. Use the retailer’s official reporting channel, the email provider’s phishing control, and the appropriate fraud authority.
- Reject follow-up callers. Genuine support does not need remote control of online banking, gift cards, cryptocurrency, or secret money transfers.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
If only the link was opened, close it and check for downloads. Account theft is less likely when no information or approval was submitted.
If credentials were entered, assume they were captured even when the page failed. A visible error can be part of the collection process.
Frequently Asked Questions
Is the $14.99 Prime charge in the email real?
The amount alone proves nothing. Check membership and billing records inside the official account and compare them with the card statement.
Will Prime really be canceled after six days?
The deadline belongs to the phishing story. Any genuine membership issue should be confirmed through the official application or independently opened website.
What if the sender copied the correct corporate address?
Public footer information can be copied. Authentication depends on the sender, destination domain, and matching account records, not a familiar postal address.
Can criminals use my card without the retail password?
Yes. Card details can be tested or sold separately. Contact the issuer if the number, expiration date, or security code was submitted.
Should I call the telephone number in the email?
No. Open the official service independently and obtain support there. A number inside a phishing message may connect directly to another scammer.
Does changing my password remove every attacker session?
Not always. Review active sessions, connected applications, recovery methods, and account changes, then explicitly sign out devices you do not recognize.
The Bottom Line
The Amazon Prime Payment Method Update email scam uses a familiar $14.99 renewal problem to lead recipients into counterfeit login and billing forms.
Check membership status through the official application instead of the email button. The real account provides the safest answer without exposing information.
If details were submitted, secure the shopping and email accounts, call the card issuer, review orders, preserve evidence, and report the impersonation promptly.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.