

An email says your Citi debit card has been updated. Then it mentions a Bitcoin wallet, something you may never have used.
The natural reaction is to check immediately. Before signing in through the message, take a closer look at where its security instructions lead.
Overview
The card-update notice is an impersonation
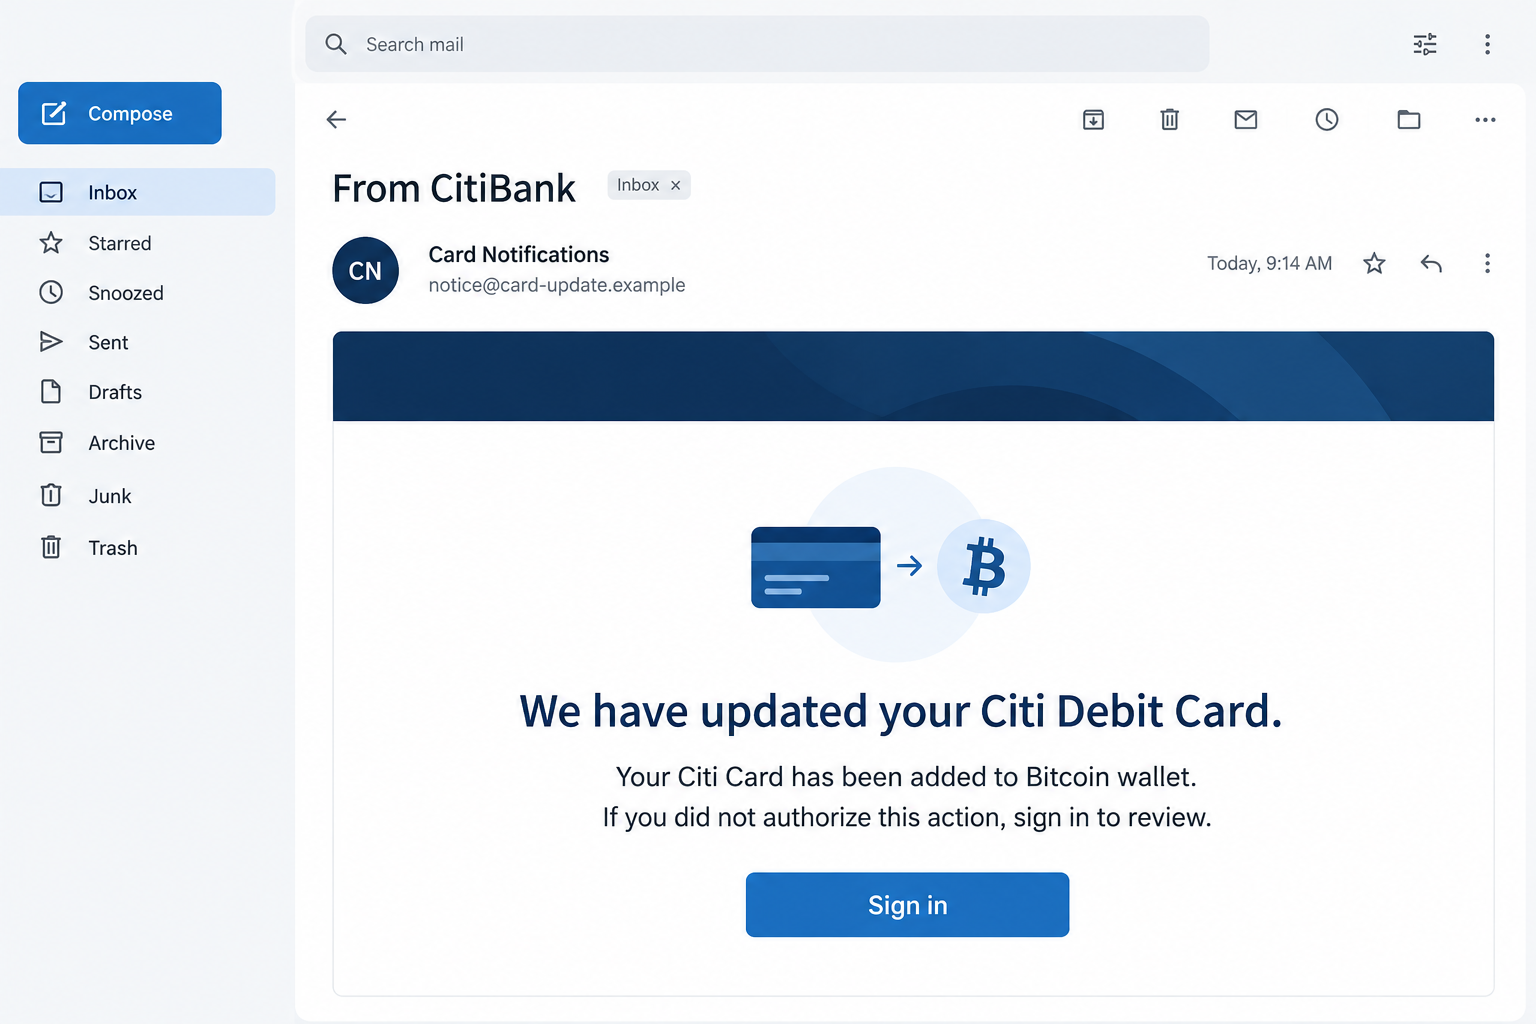
The Citi Debit Card Update email scam claims that a recipient’s card has been added to a Bitcoin wallet. It uses that alarming assertion to solicit a sign-in.
A reported version begins with a Citi-branded update message and asks anyone who did not authorize the action to review it through a link.
The real Citi banking business is being impersonated. The email does not establish an actual card update, wallet enrollment, or unauthorized cryptocurrency purchase.
The destination seeks banking credentials
The documented phishing page imitates a Citibank login and asks for a user ID and password. A reported address is login-citibank.replit[.]app.
A hosting-platform address can carry a convincing bank-themed application without being operated by that bank. Replit’s name does not authenticate the page or implicate the platform itself.
- The unfamiliar wallet claim creates concern about card misuse.
- The “not you” instruction turns that concern into a reason to click.
- A copied banking form makes disclosure feel like account protection.
- Submitting credentials exposes them even if the page later displays an error.
The response depends on what you disclosed
A recipient who ignored the notice faces a different situation from someone who entered a password or approved a sign-in request.
No successful account intrusion or payment was independently tested for this report. The specific malicious request is a banking-login lure, not a verified malware installer.
Our pictured message uses an invented sender to illustrate the pretext. It is not evidence of a real card being linked to a wallet.
Why the Bitcoin-Wallet Claim Makes People Act Quickly
You are asked to prevent harm, not collect a reward
Someone uninterested in cryptocurrency can still be worried by a claim that their debit card is now connected to it. Unfamiliarity makes the situation harder to assess.
The invitation does not require enthusiasm about a new service. It relies on the opposite feeling: you did not request this and want it stopped.
That makes the sign-in button feel protective. The reader may focus on reaching the account quickly rather than checking whether the account page is genuine.
You can investigate a frightening alert without following its route. Open your established banking app or contact the bank through a number you already trust.
Routine card language softens the unusual assertion
The message wraps its wallet claim in familiar language about card benefits, convenience, and security. Those surrounding assurances can make a strange statement seem like a normal product update.
Readers may assume a bank understands the service better than they do. A confident institutional tone can discourage them from questioning what “added to Bitcoin wallet” actually means.
Do not get stuck debating whether that wording is technically plausible. The immediate security question is whether the sender and destination are authenticated.
A genuine bank alert can be checked independently. A false one benefits when the reader believes its embedded sign-in is the only way to find out.
A “not you” link can reverse your normal caution
Most people know not to accept an unexpected financial offer. Fewer notice that a link promising to reject an unauthorized action can be equally dangerous.
The attacker has created both the apparent problem and the proposed fix. Your desire to refuse the action is used to obtain cooperation with a different action.
A button labeled review, secure, cancel, or dispute can still lead to a credential collector. Its purpose cannot be determined from the reassuring verb alone.
How the Citi Debit Card Update Email Scam Works
Step 1: A supposed card change interrupts the reader’s routine
The email announces a completed update rather than asking whether you would like one. That places the recipient in the position of responding to an apparent event.
If you have a Citi account, the message can feel personally relevant. If you do not, the claimed association may still raise concern about identity misuse.
Neither reaction establishes that the event occurred. Check through the real institution instead of using the message as a starting point for a new login.
Do not answer with account details to ask whether the notice was intended for you. That would disclose information before the sender has been verified.
Step 2: The sign-in instruction presents disclosure as protection
The message tells recipients who did not authorize the wallet addition to sign in. This makes entering credentials appear necessary to challenge a potentially unwanted change.
Pause at that transition. An email can describe an account issue, but its description does not authorize the destination it supplies.
Use a known bookmark, the banking app already installed from a trusted source, or the number on your card. Avoid sponsored search results for emergency support.
That separate route lets you assess any genuine activity without giving the suspicious sender control of the next step.
Step 3: A bank-looking page hides a different host
The reported destination uses login-citibank as a subdomain under replit.app. The bank name at the beginning is not the registered domain controlling that address.
A familiar login layout can distract from the address bar. Logos, colors, and ordinary form labels can be copied without access to a bank’s systems.
Similarly, HTTPS protects the connection to the site you reached. It does not certify that the site is the bank you intended to visit.
Do not assume every page on a general hosting service is malicious. The problem here is the unrelated bank impersonation and request for banking credentials.
Step 4: The form collects the user ID and password
The fake sign-in requests information that can be useful for account access. Entering it gives the unverified page an opportunity to record it.
An error after submission is not reassurance. A phishing form can receive data before showing a failure, loading another screen, or returning the visitor elsewhere.
Do not try several passwords to see which one works. That can expose credentials used for other accounts as well as the banking login.
If a later screen asks for a one-time code or push approval, reject it. Such follow-up is a risk to recognize, not a confirmed stage of every recorded sample.
Step 5: Stolen credentials can be used outside the page
The attacker may attempt to sign in to the real bank or reuse the same combination elsewhere. Success depends on the credentials, account protections, and other circumstances.
This is why closing the browser is not enough after submission. The exposed secret remains exposed even when the counterfeit page becomes unavailable.
Contact the bank promptly and explain exactly what you entered or approved. A user ID, password, card number, and verification code are different disclosures.
If an unauthorized payment appears, treat it as a real financial incident. Preserve the details and follow the bank’s reporting process without waiting for the email sender.
Check the Real Account Without Trusting the Alert
Use a route established before this message arrived
The safest check is usually the app or website you already use for banking. Do not install a replacement app introduced by the alert.
Review recent activity and security notifications available through the genuine account. If anything is unclear, call the bank using an independently known number.
Citi’s Security Center provides official security and reporting information. Reach it independently rather than through a lookalike page’s support panel.
Do not let someone claiming to be support move you into screen sharing to resolve the message. Financial access should not be handed to an unsolicited caller.
Read verification messages before approving anything
A one-time code may authorize a login, a payment, an enrollment, or another account action. The actual wording matters more than what a caller says it does.
If you did not initiate the action through a trusted route, do not approve it merely because someone says it will cancel fraud.
Someone who knows the text of the email has not demonstrated bank employment. They may be using the same script or information already supplied during the exchange.
Keep account-recovery questions inside the bank’s real process. A separate “verification agent” introduced by the suspicious contact is not an independent safeguard.
Keep a simple disclosure timeline
Record when the email arrived, which page opened, what you typed, and any approval or payment that followed. Separate what you saw from what you assumed.
For example, “I entered my password and then saw an error” is useful. “The bank rejected it, so nothing happened” adds a conclusion the error cannot support.
That distinction helps the bank assess risk quickly. It also reduces the chance of overlooking an exposure because the counterfeit page did not behave as expected.
Ask which access paths need protection. A concern about a debit card and a concern about online-banking credentials are related, but they are not interchangeable.
Tell the bank if the suspicious contact continues by phone. Keep its instructions and timing with the original email so the full sequence can be assessed.
What to Do if You Have Fallen Victim to This Scam
If you used the fake sign-in, act through the genuine bank now. You can protect the account without replying to the email or finishing its supposed review.
Stop using the linked page.
Reject any remaining prompts and do not enter another password. Save the email and destination address, then report it through your mail provider’s phishing controls.
Avoid forwarding the active link as a casual warning. Share a description or safely captured image instead.
Contact Citi about the exact disclosure.
Use the number printed on your card or the bank’s genuine app. Say whether you supplied credentials, card details, codes, or an approval.
Ask the bank to assess unauthorized access and appropriate safeguards. You do not need proof that money disappeared before reporting a compromised banking password.
Replace the exposed password through the authentic service.
Use an uncompromised device if software was installed during the incident. Change reused credentials on other services, especially the email account supporting account recovery.
Review available sessions, recovery contacts, and authentication settings with the bank’s guidance. A changed password may not address every active access path.
Report unauthorized transactions promptly.
Keep transaction dates, amounts, recipients, and reference numbers. Tell the bank whether you authorized anything under the false instructions or discovered a payment afterward.
Dispute and recovery options depend on the circumstances. Do not accept a stranger’s claim that a transfer is necessary to protect the remaining balance.
Assess the device if the contact introduced software.
If you downloaded an application, installed an extension, or allowed remote access, stop sensitive use and arrange a trusted security check.
Malwarebytes can help investigate malicious software. A clean result cannot make the submitted password private again or replace the bank’s fraud response.
Send the impersonation report to the genuine institution.
Citi identifies spoof@citi.com as a reporting address for suspicious email. Verify reporting instructions through its official Security Center before sending sensitive supporting details.
Keep a private copy of what you reported and any case reference. Do not send account passwords or one-time codes with a report.
Watch for a second contact using the same story.
A supposed fraud investigator may cite the wallet alert to seem informed. End unsolicited contact and call the genuine bank yourself.
AdGuard can limit some malicious advertising, but it does not validate bank messages. A familiar brand or urgent security claim still needs independent confirmation.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Did my Citi card really get added to a Bitcoin wallet?
The scam email does not prove that event occurred. Check genuine account activity and ask Citi through its established channels if you are concerned.
Is login-citibank.replit[.]app a Citi sign-in address?
It is the reported phishing destination in this case. Do not use it to access banking or enter a user ID, password, or verification code.
A bank-themed subdomain on a hosting platform is not proof of bank ownership.
What if the fake page said my password was incorrect?
Treat the password as disclosed if you submitted it. The error message cannot establish that the form failed to collect what you entered.
Stop testing other passwords and secure the real account instead.
Should I approve a code to cancel the wallet addition?
Not through an unsolicited contact. Read what the code actually authorizes and consult the bank independently if you did not initiate that action.
Does the email install malware automatically?
The documented mechanism is a false banking sign-in. No particular malware installation is established. Device cleanup becomes relevant if files, software, or remote access were involved.
Can I ignore it if I do not bank with Citi?
Do not interact with the invitation. Report it as phishing and remove it. Receiving a bank-themed email alone does not prove an account was opened in your name.
The Bottom Line
Do not sign in through the Citi Debit Card Update email. Its Bitcoin-wallet claim is a reason to check independently, not to trust the provided button.
If you entered credentials or approved an action, contact the real bank and secure that exposure promptly. Closing the false page does not undo a disclosure.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.