


A familiar document will not open, and its filename now ends in .citrus. Nearby, a note tells you that your options are running out.
Before trying a repair or contacting anyone, take a breath. The details you preserve now can matter more than the first recovery promise you find.
Overview
The .citrus ending points to an encryption incident
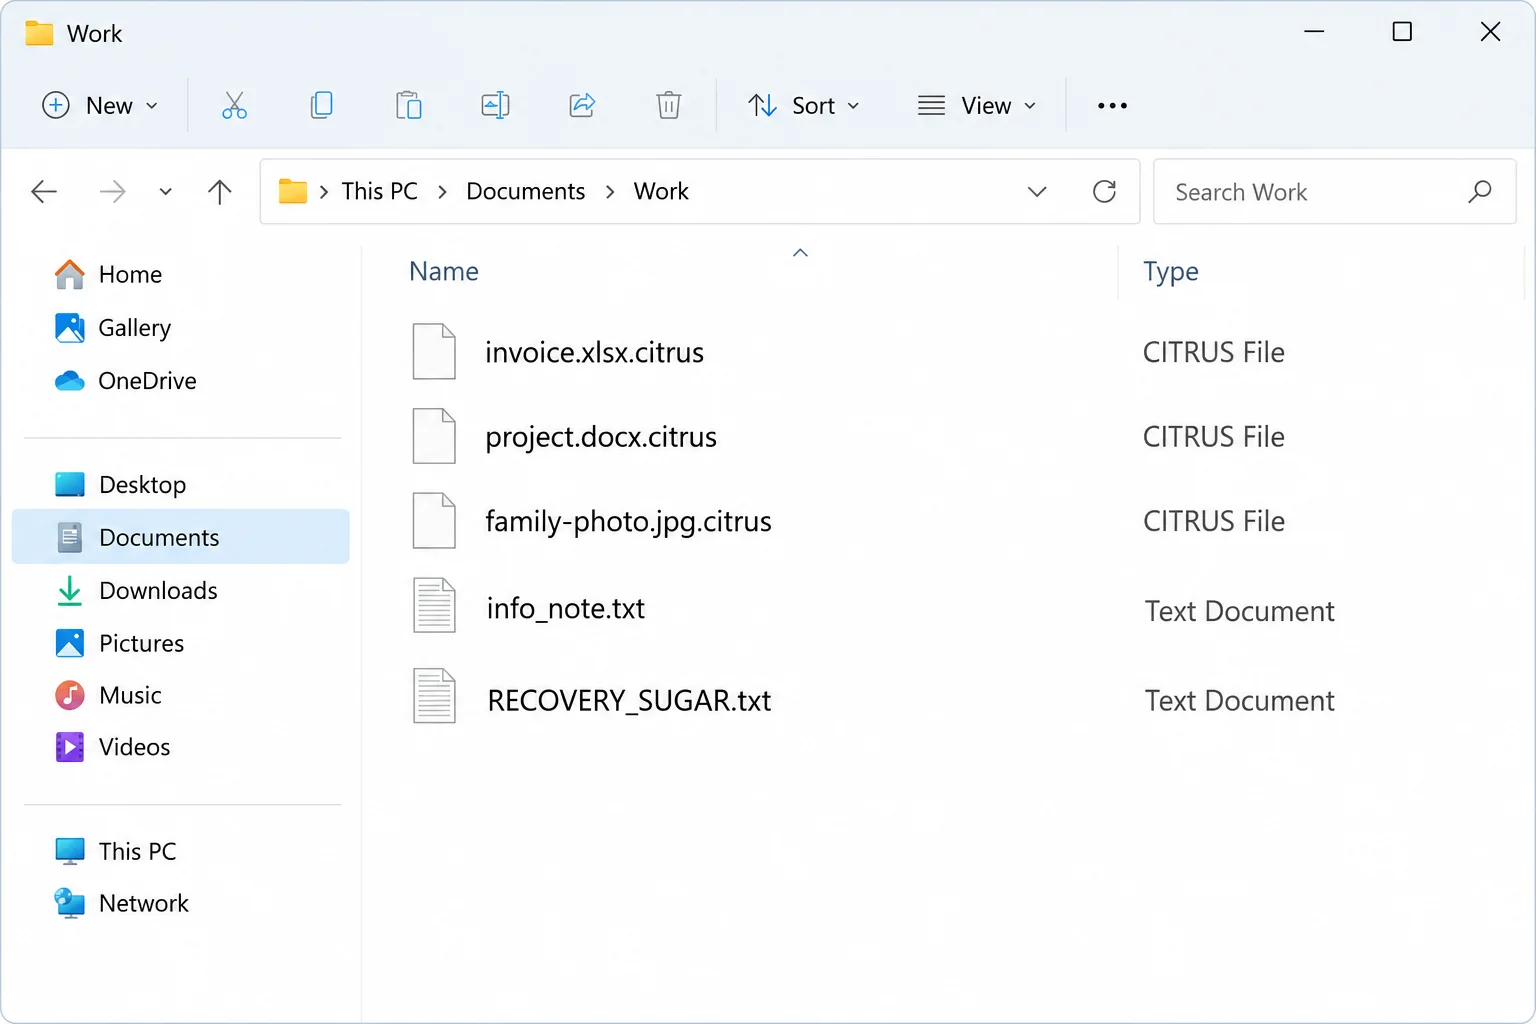
Citrus ransomware locks files and adds the .citrus extension. A photograph previously named photo.jpg may appear as photo.jpg.citrus and stop opening normally.
The reported infection also changes the desktop wallpaper and leaves info_note.txt. The wallpaper references another filename, RECOVERY_SUGAR.txt, which may help identify the demand.
The file list above is an illustration with invented personal filenames. It is not a victim’s directory or proof that both note files were present together.
The ransom demand mixes a deadline with a disclosure threat
The note directs the victim toward Telegram negotiations and gives a 72-hour contact window. It threatens publication of business information if the victim does not cooperate.
That is an extortion claim, not an independent inventory of stolen material. Encryption and data theft need separate investigation, even when the attacker describes them together.
Do not let the deadline determine your response. An attacker’s timer does not establish that paying will restore files or prevent disclosure.
Containment, removal, and recovery are separate jobs
- Containment limits further damage and protects other computers, storage, and backups.
- Investigation establishes what happened and which access routes remain exposed.
- Removal or rebuilding addresses the malicious software and compromised environment.
- Recovery restores usable data from compatible tools or copies that survived.
- A scan does not decrypt documents, and deleting a ransom note does not remove the infection.
No compatible free Citrus decryptor has been verified for this case. Preserve encrypted copies while checking reputable recovery resources rather than trying unrelated decryptors on irreplaceable originals.
Recognize the Incident Without Making the Files Worse
Keep the complete filename and the note
The extension is a useful clue, but it is not a complete diagnosis. Preserve the original directory structure, the full added suffix, and any accompanying instructions.
Do not rename every file to remove .citrus. Changing the label cannot reverse encryption, and it can make later identification harder.
Similarly, opening the damaged file repeatedly in different applications is unlikely to restore it. Stop any repair tool that proposes overwriting your only copy.
A recovered file must contain usable information, not merely regain a familiar icon. Test restored documents carefully before treating the recovery as complete.
Record what you can see, not what you assume
Write down when you discovered the problem, which systems are affected, and whether new files are still changing. Keep any endpoint-security alerts.
A changed wallpaper and matching ransom note help a responder recognize the incident. They do not establish the original entry point or every capability of the malware.
There is no verified initial infection route for the particular computer you are reading this on. An email, remote-access intrusion, or malicious installer requires evidence, not guesswork.
At work, avoid declaring the incident limited to one machine just because that is where the first locked file appeared. Shared storage may require coordinated checks.
How Citrus Ransomware Works
Step 1: Malicious code reaches a system with access to valuable files
Before a ransom message can appear, the attacker needs code to run or access that allows deployment. The visible encryption stage may come after an earlier compromise.
The available Citrus case details do not establish one universal delivery route. Do not assume every infection began with a suspicious email attachment.
Responders should inspect recent downloads, software installations, remote sessions, account activity, and security alerts according to the environment involved.
If a business uses outside technical support, verify its sessions through existing records. A legitimate remote-management product can be abused without its vendor operating the attack.
Finding an entry point matters because a restored computer remains vulnerable if the intruder still controls the account or service used to reach it.
Step 2: Files become unreadable and acquire the added suffix
Citrus processes accessible data and leaves the .citrus filename ending. The practical result is that documents, images, or other affected files no longer function as expected.
The original application cannot repair encryption simply by recognizing its old file type. A spreadsheet remains encrypted even if you change its name back to .xlsx.
Which locations were reachable depends on the system’s access at the time. Examine local storage, relevant network shares, and synchronized folders without reconnecting valuable backups experimentally.
Do not infer that every file on every device has been encrypted. Build an actual affected-data inventory so recovery work targets real damage.
Equally, do not rely on a few files opening successfully as proof the machine is clean. Some data can survive while malicious access remains.
Step 3: The note turns damaged files into a negotiation demand
The ransom note gives instructions for contacting the operator and warns against independent recovery attempts. Its purpose is to make the criminal’s route feel unavoidable.
Warnings about permanent damage contain a manipulative half-truth: careless recovery attempts can damage evidence, but that does not make the attacker your only legitimate source of help.
Preserving originals and using qualified responders is different from randomly experimenting with decryptors. You can reject the criminal’s instructions without taking unnecessary risks with the data.
The wallpaper’s reference to a differently named instruction file is another detail to retain. Do not delete one note because its name differs from the other.
A deadline should prompt organized incident response, not a rushed transfer to an extortionist. Keep communications and payment decisions within the organization’s approved process.
Step 4: The disclosure threat expands pressure beyond file access
The demand threatens business records and sensitive information. That adds concern about employees, customers, contracts, and reputation to the immediate loss of working files.
A note can claim theft without demonstrating it. Responders need logs, forensic findings, credible samples, or other evidence to assess what was actually accessed or removed.
Do not publish confidential material to ask strangers whether the threat is real. Share relevant evidence only with authorized responders and appropriate reporting channels.
If theft is confirmed, restoring files does not resolve the confidentiality issue. Account protection, notifications, and professional advice may be needed alongside technical recovery.
Payment would not create a reliable way to verify deletion of copied data. Treat promises about secrecy and erasure as claims made by the person applying pressure.
What the Leak Threat Changes for a Business
Separate the operational question from the information-security question. One concerns getting systems working; the other concerns what someone may already know or possess.
A clean backup can help restore operations without answering whether customer files were exposed. Conversely, a frightening note does not automatically prove a reportable disclosure occurred.
Bring the relevant decision-makers into a controlled response: IT, incident response, management, and appropriate legal or privacy advisers. Avoid improvising disclosure decisions from a generic online checklist.
Use an unaffected communication channel when necessary. If the attacker may control email, discussing the response inside that same account can reveal your plans.
Keep a decision log with discovery times, containment actions, affected systems, and confirmed findings. It helps responders distinguish what was known from what was only feared.
The CISA ransomware response guide emphasizes coordinated isolation and evidence preservation. A business incident often needs more than running a scanner on the visibly affected computer.
What to Do if Citrus Ransomware Has Affected Your Files
-
Isolate the affected equipment. Disconnect network access and keep backup drives separate. Tell your administrator promptly if work equipment or shared data is involved.
Do not reconnect just to test another website or download. If isolation is impossible and encryption continues, seek immediate guidance about containment and the evidence consequences of shutdown.
-
Preserve identifying material. Keep the note, wallpaper information, full filenames, and relevant alerts. Record the discovery time and which folders you noticed first.
Do not send private documents to the Telegram contact as a test. Any sample shared with a legitimate analyst should be selected with confidentiality in mind.
-
Protect copies that may still be usable. Check backup availability from an unaffected environment. Avoid attaching the only good drive to a machine that remains under investigation.
Cloud version history, an earlier attachment, or another authorized device may hold a usable copy. Confirm the contents before overwriting or discarding anything.
-
Plan cleanup before restoration. Malwarebytes can help identify malicious software, but it cannot turn encrypted Citrus files back into ordinary documents.
AdGuard is relevant to reducing some future malicious-web exposure, not decrypting data. Businesses should follow their responder’s containment, evidence, cleanup, and rebuilding plan.
-
Assess recovery compatibility. Check reputable decryption resources using the actual variant information. Test any suitable tool on duplicates, with its instructions understood.
If no verified option fits, keep an untouched encrypted archive. Do not accept a stranger’s guarantee that every file can be recovered for an advance crypto payment.
-
Report the incident and review exposed access. Retain case numbers, receipts, and correspondence. If you already paid, tell the relevant provider and authorities promptly.
From a trusted system, review accounts the affected device could access. A new password alone may not remove active sessions or an intruder’s separate remote-access route.
Remove the Infection Before Restoring Citrus Files
Step 1: Preserve the incident details before cleanup
Retain info_note.txt, the wallpaper’s RECOVERY_SUGAR.txt reference, and complete .citrus names. Keep disconnected backup storage away from the affected installation.
For business equipment, preserve logs through the incident team before scanning. The 72-hour demand does not determine when evidence can safely be changed.
Step 2: Install Malwarebytes, scan Windows, and quarantine threats
Use this procedure on a personal Windows PC after preserving the incident details. For a managed computer, let your security team decide when scanning should begin.
Malwarebytes can find and quarantine threats. Its free Custom Scan is separate from paid real-time protection and Threat Scan. Neither edition supplies ransomware decryption keys.
-
Download the Windows installer.
Open the official download page using the button below. Select Free Download there and save the Windows installer.
If the affected PC cannot browse safely, use a trusted computer and arrange an appropriate transfer without exposing clean backup media.
Malwarebytes for WindowsManual scanning and quarantine, with optional paid protection.
Opens the official free-scanner page. Choose its Windows download; paid protection is optional.
-
Open the setup file.
Open Downloads and double-click the MBSetup file. If Windows requests permission, check that the prompt identifies Malwarebytes before allowing the installation.

-
Complete setup without accepting unwanted extras.
Select Install, choose the appropriate Personal or Business device option, and continue. Business-managed computers should be handled through their administrator’s process.

Review any browser extension, trial, or subscription offers. Skip optional features you do not want, then select Open Malwarebytes when setup finishes.

-
Choose a supported scan.
Find the Scanner tile on the dashboard. For a free Custom Scan, open its three-dot menu, select Advanced Scan, and choose Custom Scan.
Expand the file-location selector and select the system drive and relevant locations. Review potentially unwanted program settings, then select Start Custom Scan.
A paid or eligible trial edition may also offer Threat Scan. Use the controls available in your edition; do not disable Windows protections to unlock another option.

-
Let the scan complete and inspect its findings.
Keep the computer powered on while scanning and wait for the results. A large Custom Scan can take longer than a scan limited to common locations.
Review each detection and its location. Leave confirmed threats selected and choose Quarantine. Save the report if a detection is unclear rather than adding it to exclusions.
The results illustration uses sample detections to show the Quarantine control. Those names are not identifiers for the malware discussed in this article.

-
Finish removal and handle a requested restart.
Follow the quarantine prompts. If a restart is requested, save your work and coordinate it with anyone preserving evidence before restarting.

Reopen the application afterward and review the result. Repeated detections, blocked removal, or signs of continuing access need further investigation, not an automatic clean-device conclusion.
The screen design can vary by installed release. Follow the named controls and the vendor’s current scan instructions if your version looks different.
Step 3: Use a second opinion if findings remain unresolved
HitmanPro provides an optional second opinion when a Windows infection or unresolved finding warrants another check. Run scanners sequentially, not at the same time.
Scanning is free. Removal needs an eligible one-time 30-day trial or a paid license. A computer that already used its trial may not qualify again.
-
Obtain HitmanPro from the established download route.
HitmanProOptional second-opinion Windows scanner.
Free scan. Removal requires an eligible trial or paid license.
-
Launch the downloaded program.
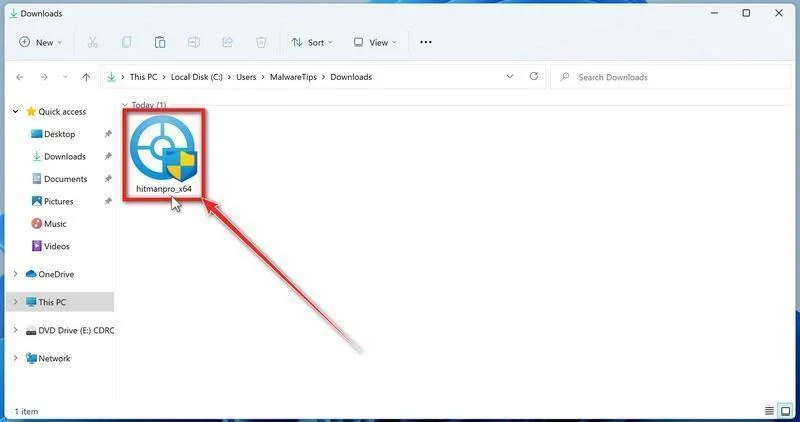
Open Downloads and run the appropriate HitmanPro file for your system. Check the publisher in any Windows permission prompt before allowing it.
-
Start the scan.
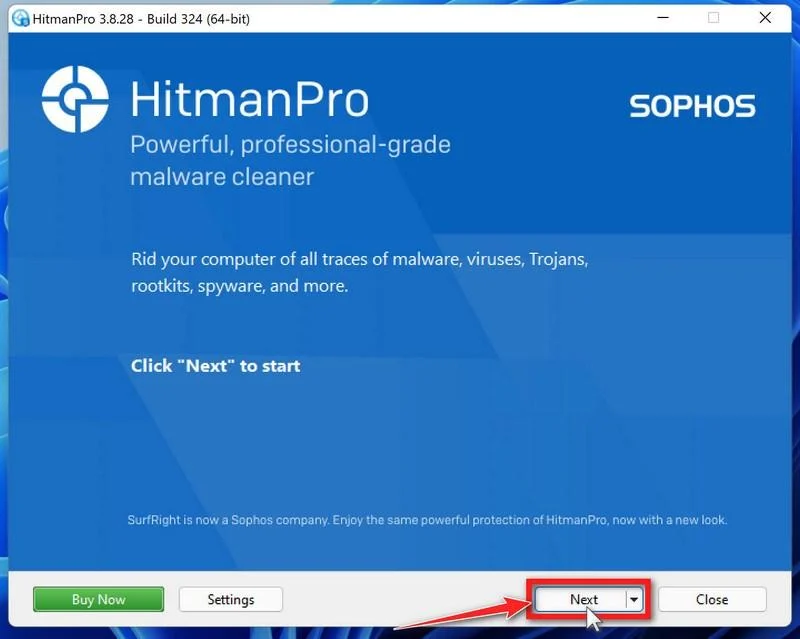
Open HitmanPro, select Next, and follow its license and setup prompts. Its cloud checks require an internet connection; arrange controlled access if the PC was isolated.
-
Review the results before removal.
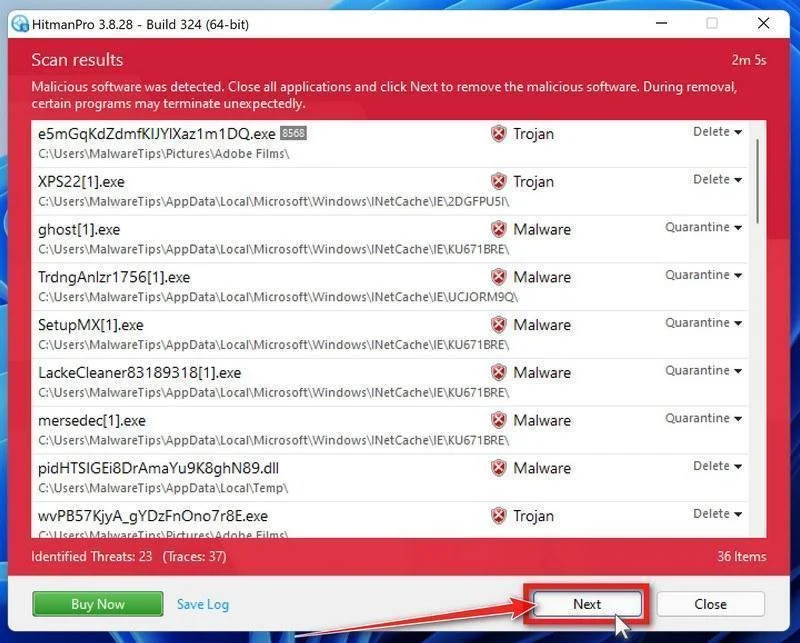
Allow scanning to finish. Inspect the listed objects and proposed actions, then select Next for confirmed unwanted items. Save uncertain findings for qualified assistance.
-
Use an eligible license and complete cleanup.
If available, select Activate free license and follow the trial prompts. Otherwise, use an existing license or retain the report; do not assume purchase is mandatory.
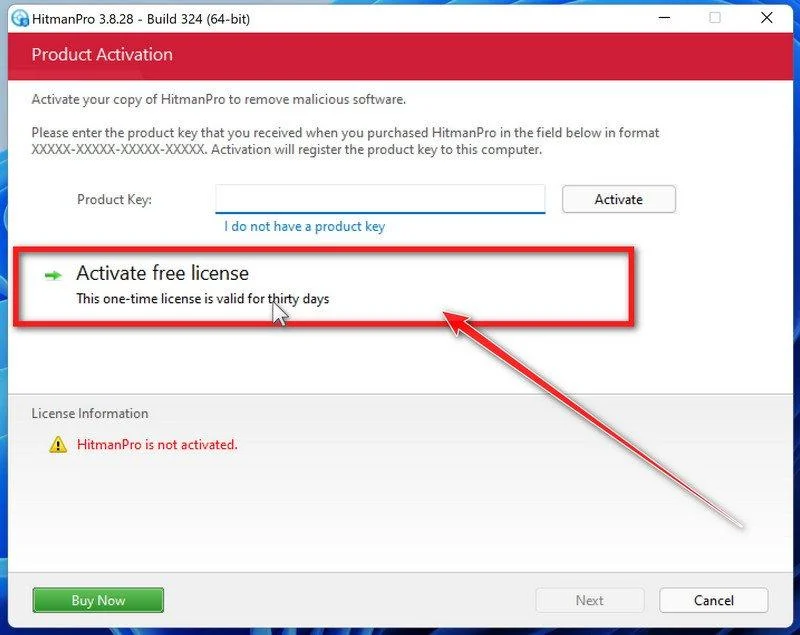
Finish the proposed cleanup and restart if requested. If problems persist, keep both scanners’ reports and seek help rather than repeatedly activating unfamiliar repair tools.
Step 4: Approve a trusted destination before restoring Citrus data
Investigate recurring detections and the original access route with your responder. Arrange a supported rebuild if the previous installation cannot be trusted.
Check the disclosure threat separately from file restoration. Neither a clean result nor a successful backup restore proves that no business information was accessed.
Citrus File Recovery Options
Keep Citrus encrypted originals unchanged. The recovery methods below depend on surviving copies or exact-variant compatibility, not the wallpaper’s promised outcome.
Removing ransomware stops or contains the malicious software. It does not turn encrypted bytes back into working documents. Keep untouched encrypted originals before testing any recovery method.
Use a clean, updated recovery environment and keep it separate from systems still under investigation. Restore files only after the infection and its access path are addressed.
Option 1: Restore a verified backup or earlier cloud version
-
Find a backup dated before the encryption. Keep the original backup unchanged and check that representative documents actually open in a trusted environment.
-
Restore to a separate clean location, not over the only encrypted copies. Use the backup application’s documented restore process for databases and application-specific data.
-
For cloud storage, open its genuine version-history or restore controls from a trusted device. Compare dates and select an unaffected version where one exists.
-
Inspect restored documents and confirm that the required recent work is present. A familiar filename alone does not verify successful restoration.
Windows File History helps only if it was configured and a usable backup survives. Open Control Panel, then System and Security, File History, and Restore personal files.
Browse the available dates and preview the files. Use Restore to for a separate destination when offered, rather than replacing your only copy during testing.
Option 2: Look for a decryptor that matches the actual variant
A decryption tool must support the ransomware family and version involved. A matching extension, similar name, or confident advertisement is not enough.
- No More Ransom’s decryption catalog lists supported families and their tool instructions.
- Emsisoft’s ransomware decryptors provide family-specific tools and limitations.
- ID Ransomware can help identify a family from appropriate evidence, subject to its upload and privacy terms.
-
Record the ransom-note filename, appended extension, and existing detection. Do not identify the ransomware family from a filename extension alone.
-
Check the tool’s exact supported variant and requirements. For sensitive business material, ask your responder what evidence can be shared before uploading anything.
-
Read the developer’s instructions and run a supported tool only on copies in a separate location. Keep the original encrypted data even after an apparent success.
-
If no suitable decryptor is available, retain the copies and revisit trusted catalogs later. Do not pay a stranger to unlock a supposedly hidden download.
Option 3: Assess surviving snapshots without assuming they exist
Some systems retain earlier snapshots or previous versions; others never had them or lost them during the incident. Check availability instead of trusting the ransom note.
On Windows, open the affected folder’s Properties and look for Previous Versions. Open a suitable earlier version first and copy needed data to a different location.
If no version appears, that method has no available copy to restore. It does not establish whether a separate backup or cloud version exists.
Option 4: Consider deleted-file recovery only for recoverable originals
File-recovery software does not decrypt ransomware’s encrypted output. It may help only when readable originals or other usable copies remain recoverable on the storage.
Further writes can overwrite that recoverable data. For valuable files, have a qualified specialist assess or image the source drive before installing software or starting another scan.
Use the procedure below only when that recovery approach is appropriate. Install the tool elsewhere and save recovered files to a separate drive or clean destination.
-
Open the established recovery-tool download route.
EaseUS Data Recovery WizardFile recovery, not ransomware decryption.
View EaseUS Data Recovery Wizard
Check current compatibility, free-edition limits, and licensing before installation or purchase.
-
Install away from the recovery source.
Download and install on a separate suitable system or drive, following a specialist’s plan when necessary. Do not install into the disk you hope to recover.
-
Select the source and scan for recoverable data.
In the recovery application, choose the affected drive or location and begin scanning. Selecting an encrypted file does not make the tool a decryptor.
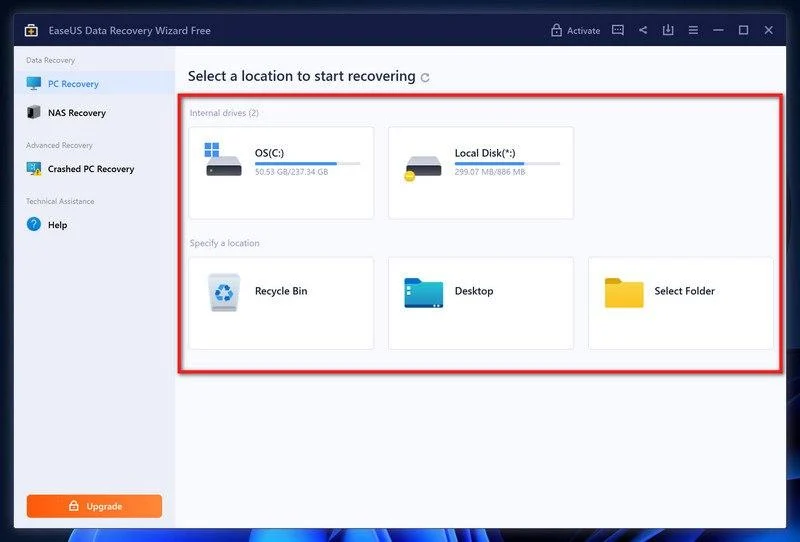
-
Inspect what the scan actually found.
Use the available filters to locate needed document types. Preview representative files to see whether their contents are readable, not merely listed by name.
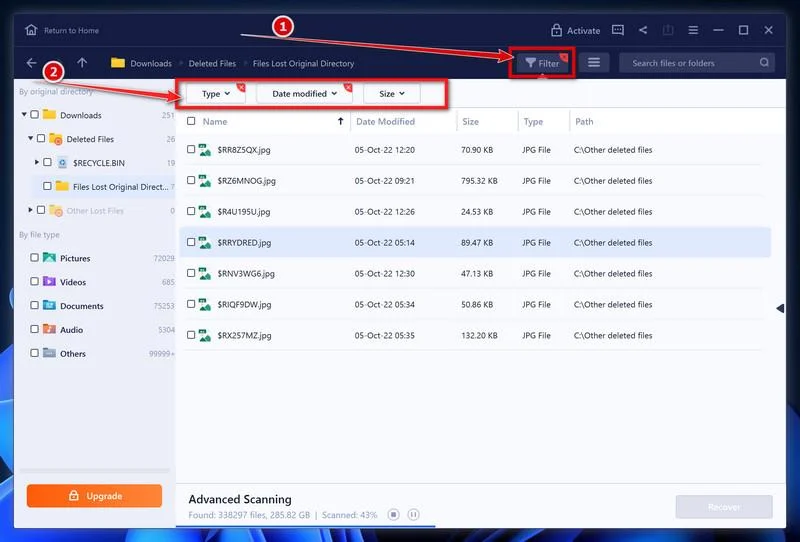
A preview can help evaluate a result, but free-edition export limits may still apply. Do not purchase solely because a scan displays filenames.
An unavailable preview is not a successful recovery. A listed filename may still refer to damaged or unusable data.
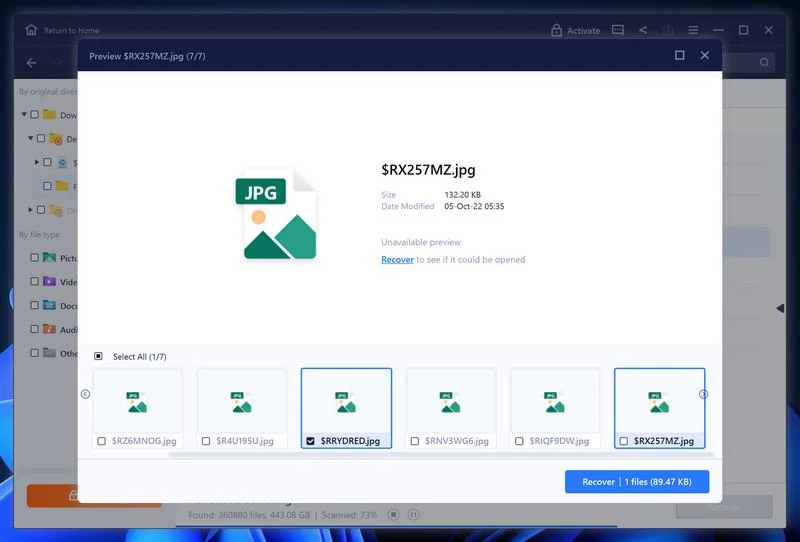
-
Recover to a different destination and verify the files.
Select appropriate readable results, choose Recover, and select a different drive or safe location. Never save the recovered output back over the recovery source.
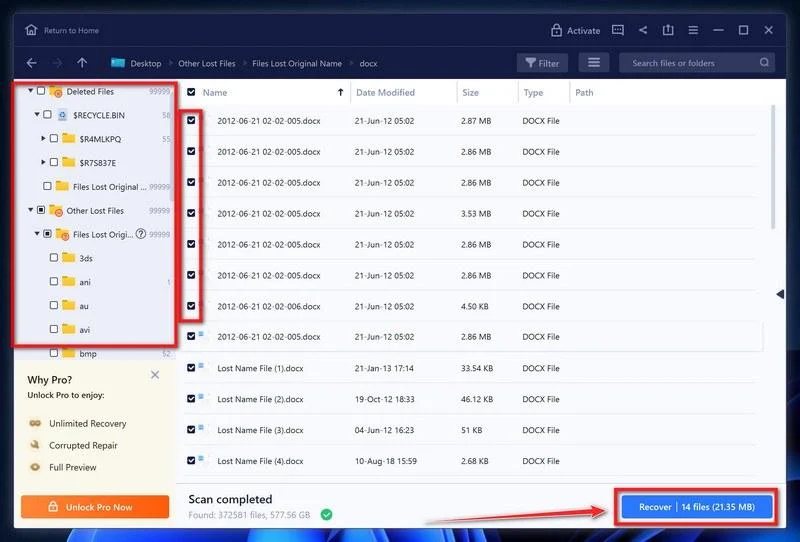
Open representative recovered files in the clean environment. Keep the original encrypted copies, scan reports, and a record of which method recovered each set.
If recovery fails, stop experimenting on the only source. Preserve it for qualified assistance or a future matching decryptor rather than accepting guaranteed-recovery sales claims.
Decide What to Restore First
Recovery is easier to manage when you prioritize real needs. List essential documents, current financial records, customer work, and irreplaceable personal material before starting large restorations.
For each category, note its best surviving source and how current that source is. A file that opens can still be too old to serve its purpose.
Restore to a trusted destination and verify representative items. Database files, archives, and project folders may require application-specific checks rather than a quick visual inspection.
Keep the encrypted archive separate until recovery decisions are settled. A partial success today should not destroy the evidence or data needed for another assessment later.
After rebuilding, close the access gap that allowed the incident. Otherwise, the same restored business files can be exposed to another intrusion.
Test the new backup process with an actual restore. Knowing where copies are stored is useful; knowing they can be recovered is what makes them dependable.
Keep Recovery Decisions Grounded in What You Know
When several people are helping, keep one agreed inventory of affected systems. Otherwise, a computer cleaned by one person may be reconnected while another is still investigating.
Record which copies are encrypted, which are intact, and which have merely not been tested. Those categories prevent a hopeful assumption from becoming a destructive overwrite.
Do not use an irreplaceable document as the first trial for a repair utility. A duplicate gives you room to assess the result without sacrificing the original.
For a business, tell staff which services are unavailable and which temporary workarounds are approved. Avoid encouraging unofficial file sharing while the normal systems are disrupted.
Be equally precise with customers. Saying that systems are being restored is different from promising that no information was accessed or that every record will return.
If the attacker claims a leak, let the authorized response team evaluate it. Do not circulate confidential samples internally just to establish whether they look familiar.
Home users can apply the same principle on a smaller scale. Keep a simple list of attempted tools, recovered folders, and files still missing.
A good recovery plan makes uncertainty manageable. It does not require believing the ransom note, declaring everything lost, or accepting the first paid guarantee.
Frequently Asked Questions
Will removing .citrus from filenames unlock my documents?
No. Renaming changes the label, not encrypted contents. Keep the original names and work on copies if a qualified recovery process requires any changes.
Does a clean antivirus scan decrypt Citrus files?
No. Malware removal and file decryption are different tasks. A scan can help address malicious software while already encrypted data still requires a suitable recovery source.
Is a free Citrus decryptor available?
No compatible tool has been verified here. Check the No More Ransom catalog for current compatibility, and do not assume a similarly named tool will work.
Does the note prove that employee or customer data was stolen?
No. It establishes what the attacker is claiming. Investigate access and exfiltration evidence separately, especially when business records or sensitive personal information may be involved.
Should I trust the 72-hour deadline?
Treat it as extortion pressure, not a reliable recovery rule. Begin containment and professional assessment promptly without allowing the attacker’s timetable to force payment.
What if I have no complete backup?
Preserve the encrypted data and assess surviving cloud versions, partial backups, earlier shared copies, and qualified recovery options. No legitimate helper should guarantee success without examining compatibility.
The Bottom Line
For Citrus ransomware, isolate first and preserve your data. Do not pay on the strength of a deadline or mistake a renamed extension for decryption.
Remove malicious access before restoring anything. If files are already locked, use verified recovery options and keep untouched encrypted copies when a working solution is not available.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.