


A quiet computer is not necessarily a clean computer. Some threats are built to avoid pop-ups, slowdowns, and every warning that might make their owner investigate.
DarkTortilla RAT follows that quieter model. Its interest in browser data and multiple outbound channels makes a suspected infection worth treating seriously.
Overview
What DarkTortilla RAT is
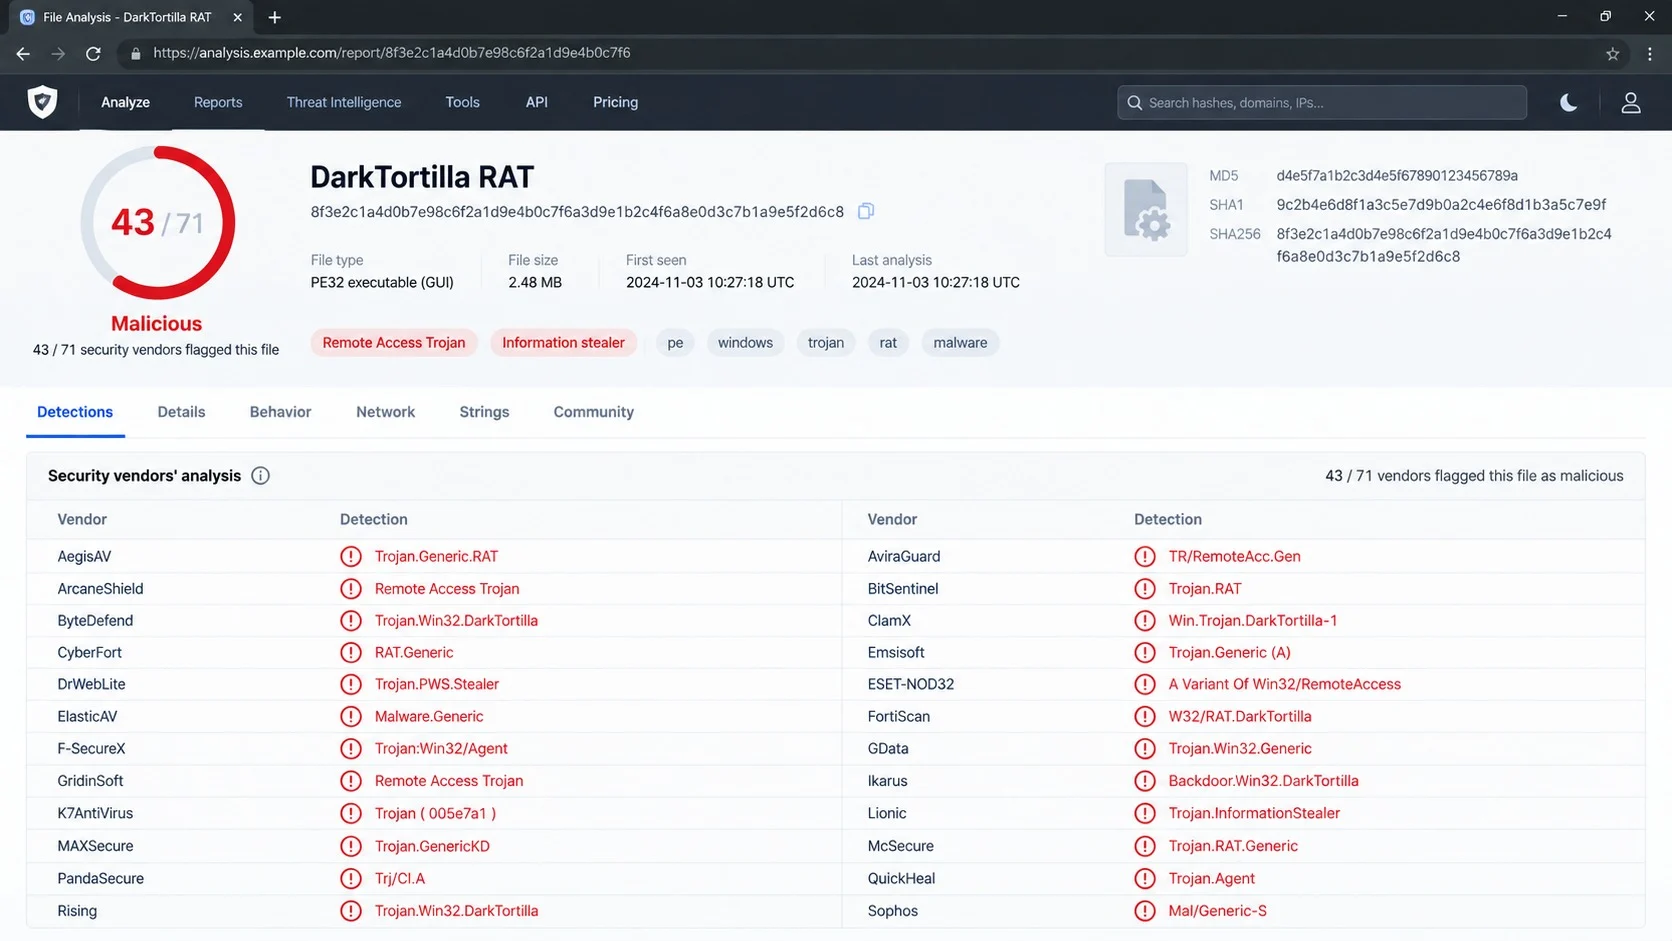
DarkTortilla is a remote access trojan with information-stealing capabilities. A RAT gives an outside operator a path to interact with an infected system.
Its reported collection targets include saved browser passwords, session cookies, browser-profile data, and stored payment card details.
The malware is designed to work silently. A victim may continue browsing normally while sensitive data is gathered in the background.
How stolen information leaves the computer
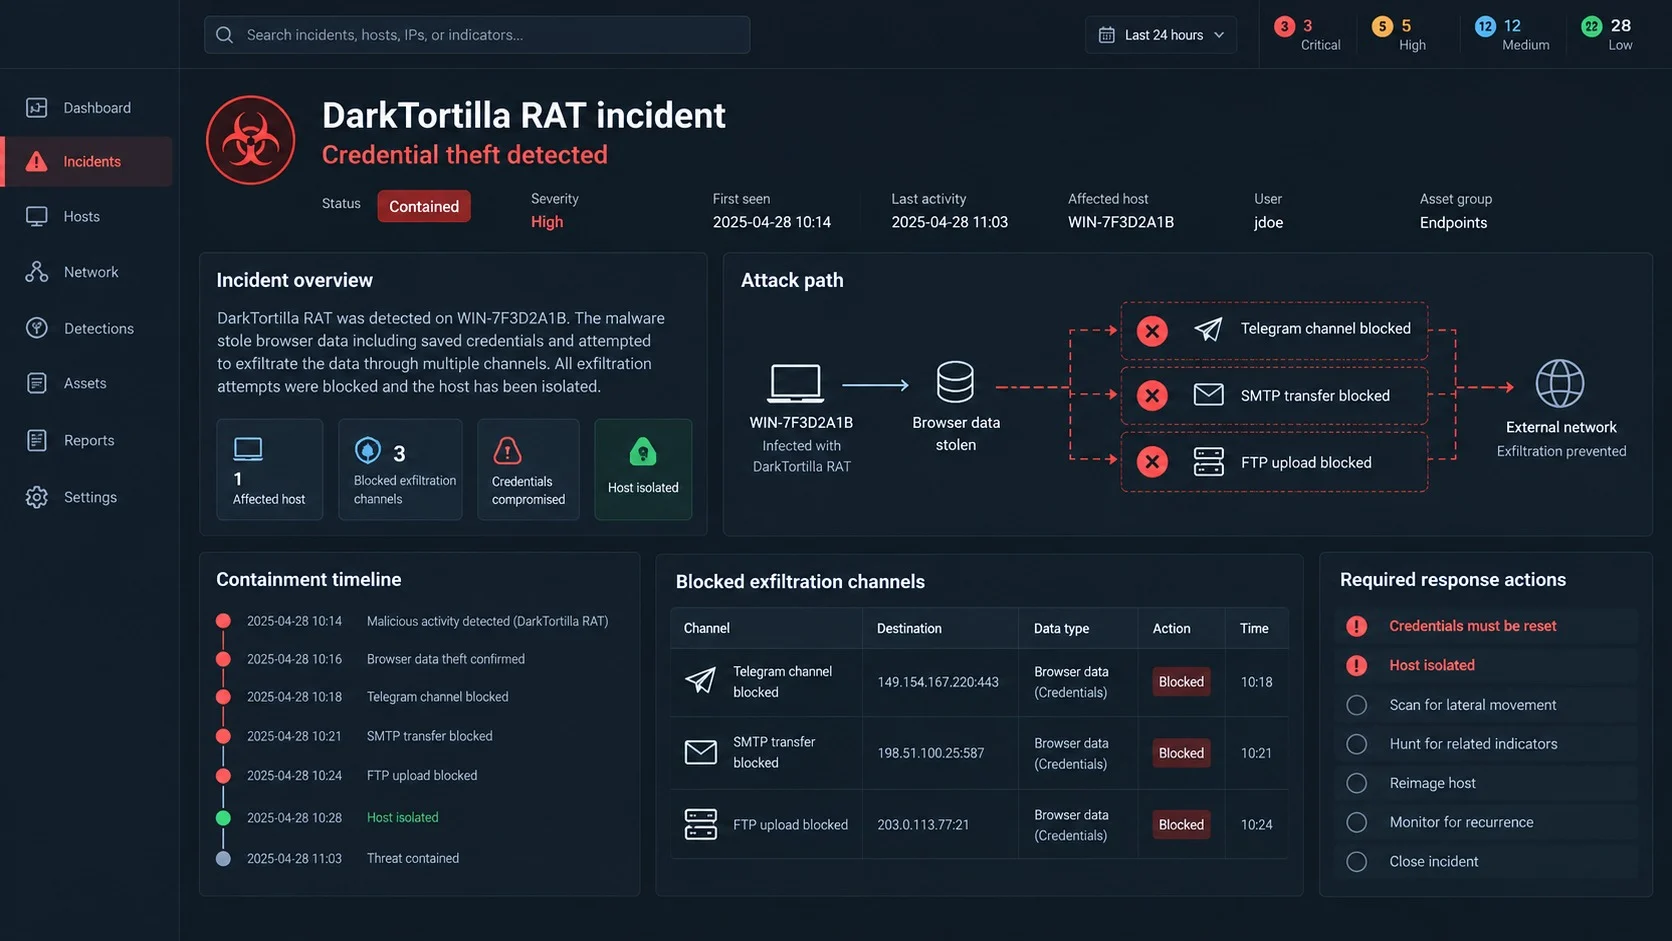
DarkTortilla reportedly uses three exfiltration routes: a Telegram bot, SMTP email, and FTP uploads to an external server.
Using several routes improves resilience. Blocking one service may not stop the same collected package from leaving through another channel.
Before transmission, gathered data can be staged inside a text file placed in a publicly writable Windows location.
What an infection can expose
- Passwords saved in Chromium-based and Gecko-based browsers.
- Session cookies that may bypass an ordinary password prompt.
- Browser profiles containing account and browsing information.
- Stored card numbers, expiration dates, and cardholder names.
- The device’s public IP address and approximate network location.
- Access that can support identity theft, account hijacking, and further malware delivery.
The risk continues after file removal because stolen credentials and cookies remain usable. Endpoint cleanup and account recovery must therefore happen together.
How DarkTortilla RAT Works
Step 1: A malicious file reaches the target
The examined code contains VBScript and VBA components, which are commonly associated with malicious Office documents and phishing attachments.
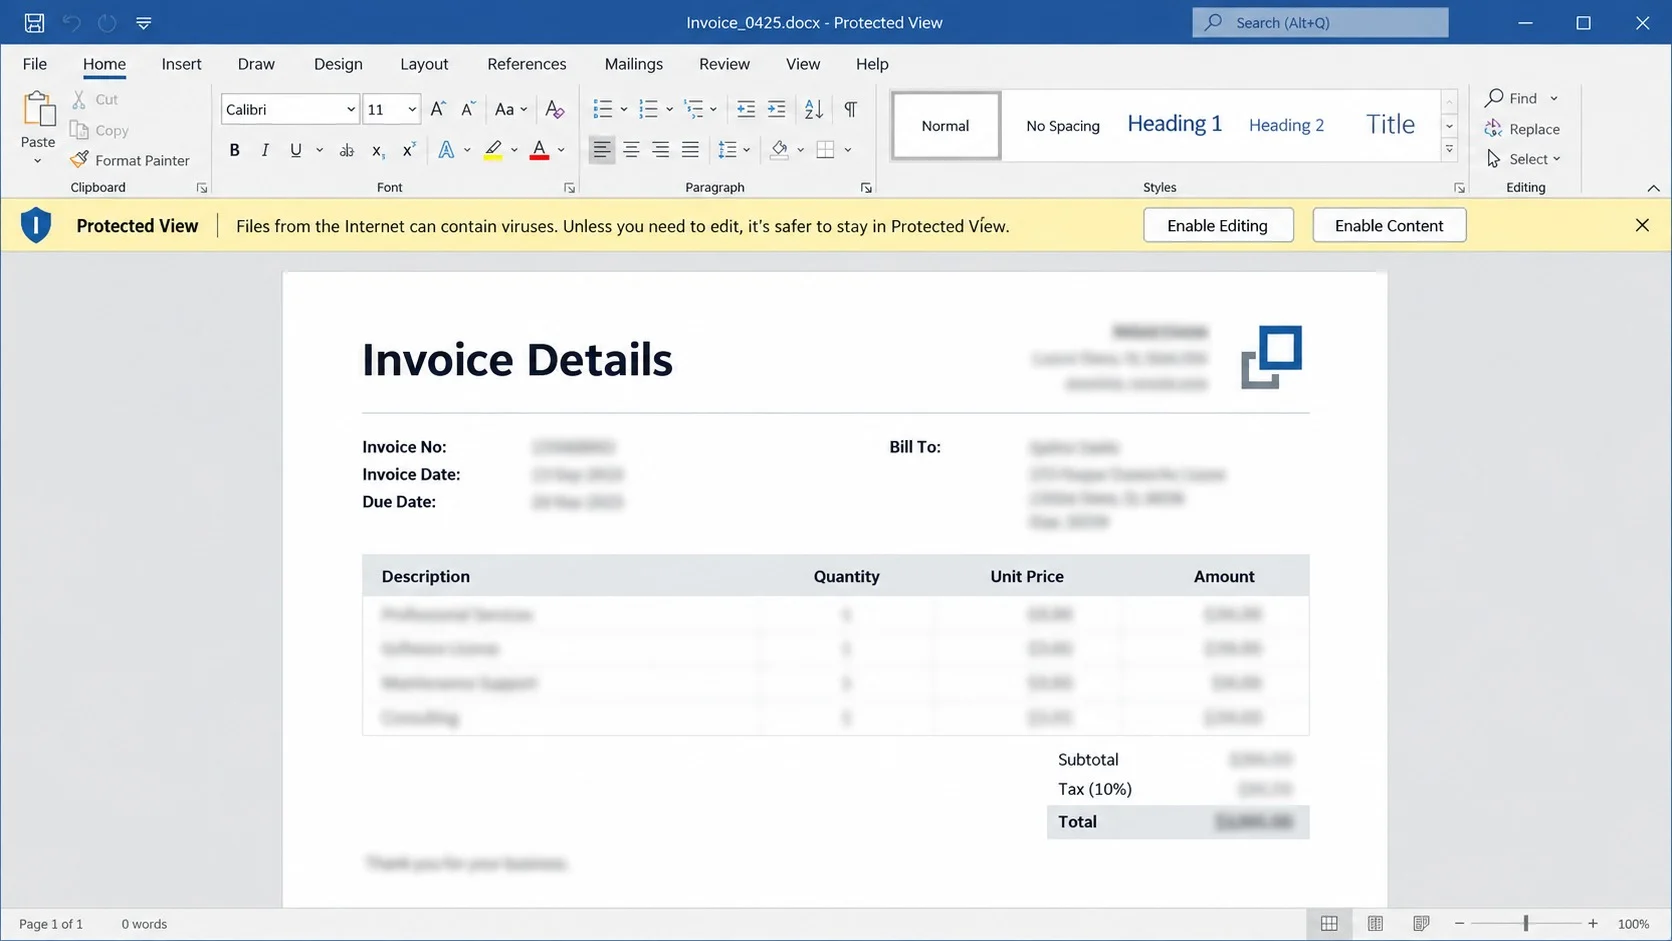
A typical lure may describe an invoice, shipping notice, job document, bank record, or employer file. The attachment appears relevant enough to open.
Protected View initially limits active content. The document may claim that the user must enable editing or macros to reveal hidden information.
That request is dangerous because macros can execute instructions outside the visible document. A blank page can conceal a working installation chain.
DarkTortilla-type threats can also arrive through fake downloads, pirated applications, peer-to-peer packages, malicious advertisements, or illegal activation tools.
The common feature is untrusted execution. Something obtained from outside a verified source is allowed to run with the user’s permissions.
Step 2: Scripted components launch the payload
When active content is approved, a hidden routine can create files, launch a command interpreter, contact a server, or start another embedded component.
VBScript and VBA are legitimate technologies. Their presence becomes suspicious when an unexpected document uses them to start concealed system activity.
The first-stage file may not contain every capability. Downloading a later payload lets attackers change the final malware without rebuilding the original lure.
Security controls can interrupt this chain at several points: attachment scanning, macro restrictions, script blocking, reputation checks, and behavior monitoring.
If those layers fail, the user may see only a document error while the trojan starts behind the application.
A quick close does not reverse code that already executed. The device should be isolated and assessed if active content was enabled.
Step 3: DarkTortilla surveys the infected environment
Once active, the malware can identify system and network details useful for organizing victims. It reportedly queries an external service for the public IP address.
The operator can use that value to estimate region, recognize repeated connections, and distinguish home, business, or hosted environments.
The trojan may locate installed browsers, profile directories, stored-login databases, cookie stores, and encryption material used to protect browser data locally.
This reconnaissance is usually invisible. Task Manager may show an unfamiliar process, but malware can choose names that resemble ordinary software.
CPU and network use may remain low. The absence of obvious performance problems should never be treated as proof of safety.
Endpoint logs and security detections are more reliable than visual symptoms when investigating a stealthy information stealer.
Step 4: Browser credentials and cookies are collected
Modern browsers encrypt saved passwords, but they must also decrypt them for the signed-in operating-system user. Malware running in that context can abuse the same mechanisms.
DarkTortilla reportedly accesses browser databases and local encryption keys to recover credentials saved by Chrome, Edge, Firefox, Brave, Opera, and numerous other browsers.
Session cookies are especially valuable. A valid cookie can represent an already authenticated session, allowing access without entering the account password again.
That is why changing a password alone may not expel an intruder. Existing sessions and refresh tokens need explicit revocation.
Browser profiles can also reveal visited services and account names. This information helps criminals prioritize financial, business, cryptocurrency, and email targets.
Deleting browser history after infection cannot recover data already copied. Incident response must assume collection may have occurred before detection.
Step 5: Payment card and identity data are packaged
DarkTortilla’s reported card module looks for numbers, expiration dates, and cardholder names saved in browser data.
Supported formats span several major card networks. The malware does not need to display a fake checkout when card data already exists locally.
Collected details can be combined with cookies, usernames, IP information, and browser profiles to create a more useful victim package.
The temporary staging file simplifies transmission. It may contain a structured record ready to send through several communications methods.
Data theft can happen quickly, so isolating the machine matters even if the security alert appears moments after the suspicious file ran.
Card issuers should be notified when browser-stored payment information was accessible. Monitoring alone may be insufficient for high-confidence compromise.
Step 6: Three outbound channels carry the stolen package
One route sends information to a Telegram bot, providing near-real-time delivery through a commonly available messaging platform.
Another uses SMTP, the protocol associated with sending email. A third uploads data to an attacker-selected server using FTP.
Redundancy complicates containment. A network that blocks Telegram may still permit outbound mail or FTP traffic.
Likewise, deleting one command destination from a firewall rule does not prove the endpoint has stopped collecting information.
Successful response isolates the host, removes the malware, blocks known destinations, searches for related infections, and resets exposed identities.
Network controls are valuable evidence and containment layers, but endpoint eradication remains necessary.
Why Password Changes Alone Are Not Enough
A password reset protects only one authentication secret. DarkTortilla also targets cookies that can preserve active sessions.
Users should select “sign out everywhere” or its equivalent for affected services. Administrators may need to revoke refresh tokens centrally.
Saved card data creates a separate financial problem. Replacing an account password does not change the card number already copied.
The trojan may also have delivered another payload. Removing a single detected file cannot guarantee that every added component disappeared.
Finally, changing credentials on the infected computer can expose the new values immediately. Recovery should begin from a separate trusted device.
A complete plan cleans or rebuilds the endpoint, invalidates sessions, replaces credentials, protects payment methods, and monitors downstream activity.
How to Identify a DarkTortilla RAT Infection
Review security detections and quarantine history
Different antivirus engines may use generic names such as remote-access trojan, information stealer, injector, or suspicious VB malware.
Record the file path, detection time, hash, action, and original source. Those details help determine what ran and whether similar files exist elsewhere.
Do not restore a quarantined file simply because one engine used a generic label. Context matters more than a friendly-looking filename.
Trace recent documents and downloads
Review email attachments, browser downloads, archives, cracked software, and documents opened shortly before the alert.
Ask whether Protected View was dismissed or macros were enabled. A remembered prompt can establish the likely infection window.
Preserve the original lure for investigation without reopening it. Business users should follow their incident-reporting procedure.
Inspect processes, startup points, and staged files
Look for unfamiliar processes, scheduled tasks, startup entries, services, and files in public or temporary directories.
Manual deletion is risky because malware can mimic system names. Use trusted scanners and experienced incident responders for high-confidence removal.
A process ending after reboot does not confirm eradication. Persistence may launch only under certain user actions or schedules.
Examine account and network evidence
Search for outbound Telegram, SMTP, and FTP activity that the user cannot explain. Correlate it with the suspected execution time.
Review online accounts for unfamiliar sessions, password changes, authorized applications, transactions, or login alerts.
Network evidence can prove data left the host, while clean logs cannot conclusively prove nothing was stolen.
What to Do If DarkTortilla RAT Infected Your Computer
- Isolate the machine immediately. Disconnect Wi-Fi and Ethernet. Do not sign into email, banking, shopping, or work services from the suspected host.
- Preserve evidence when required. On company equipment, contact security from another device before restarting or deleting files. Live information may matter.
- Run trusted offline and full scans. Use Malwarebytes plus the operating system’s built-in protection. Quarantine confirmed threats and scan every attached drive.
- Consider a clean rebuild. Reinstall from trusted media when remote access occurred, additional payloads appeared, or responders cannot establish complete eradication.
- Reset identities from a clean device. Prioritize email, password managers, banking, business accounts, cryptocurrency services, and any credentials saved in browsers.
- Revoke all active sessions. Invalidate cookies, tokens, app passwords, remembered devices, and unknown multi-factor methods rather than relying on password changes.
- Protect payment cards and finances. Contact issuers, replace exposed cards when advised, review transactions, and watch credit or identity records.
- Use AdGuard after recovery. It can reduce malicious advertising and redirect exposure, but it cannot clean an infected endpoint or recover stolen data.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
How to Rebuild Trust in the Computer
After removal, update Windows, browsers, document software, and every installed application. Close vulnerabilities before restoring normal use.
Run a second complete scan after restarting. Review startup entries and confirm that security protections remain enabled.
Restore personal files from a backup created before the suspected infection. Scan the backup and avoid restoring executables, scripts, or unknown documents blindly.
Reinstall browsers rather than importing entire compromised profiles. Bookmarks are safer to restore than extensions, cookies, or synchronized settings.
Install extensions individually from official listings. Remove saved card data and avoid storing highly sensitive credentials directly in browsers.
For high-value or business systems, a clean operating-system installation offers stronger assurance than manual file removal.
How to Prevent Similar RAT Infections
Do not enable macros or active content in documents received unexpectedly. Confirm the sender through a separate channel when a file is genuinely important.
Obtain software from official developers and reputable stores. Pirated applications, key generators, and unofficial activation tools are frequent malware carriers.
Keep real-time protection active and allow cloud-delivered analysis where appropriate. Behavior monitoring can catch malicious scripting that static scanning misses.
Use unique passwords inside a dedicated password manager. Avoid saving payment cards in multiple browser profiles.
Enable multi-factor authentication, preferably passkeys or hardware keys. Remember that stolen sessions still require revocation after endpoint compromise.
Restrict outbound FTP and unnecessary SMTP in managed networks. Alert on unusual messaging-bot connections from endpoints that do not need them.
Back up important data offline or in protected versioned storage. Test restoration before an incident makes the backup essential.
Teach users that an attachment’s appearance is not a safety signal. The dangerous instruction is often “Enable Content,” not the visible invoice.
Frequently Asked Questions
What is DarkTortilla RAT designed to steal?
Reported targets include saved browser passwords, session cookies, browser profiles, card numbers, expiration dates, cardholder names, and basic network identity information.
Those assets can support account takeover, payment fraud, identity theft, and more targeted attacks.
Will I notice DarkTortilla running?
Possibly not. Information stealers and RATs are designed to remain quiet, and visible symptoms may be absent.
Security alerts, strange account sessions, unusual network traffic, or an unexpected macro document may provide the first clue.
Can changing every password solve the problem?
No. The malware must be removed or the computer rebuilt, and active sessions must be revoked because stolen cookies may bypass passwords.
Make changes from a clean device so the new credentials are not collected again.
Why does DarkTortilla use Telegram, email, and FTP?
Multiple outbound routes improve reliability for the operator. If one service is blocked or unavailable, another may still deliver the stolen package.
Defenders need endpoint containment and broader network review rather than blocking only one destination.
Do I need to format the entire drive?
Not in every case. Trusted security tools may remove a contained infection, especially when evidence shows no additional payload or remote activity.
A clean reinstall is safer when the scope is uncertain, sensitive systems were exposed, or detections keep returning.
Is opening a suspicious document enough to become infected?
Protected View can prevent active content from running. Risk increases when the user enables editing, approves macros, or launches an embedded file.
Still, report and scan after suspicious interaction because delivery methods can vary and unpatched vulnerabilities may require fewer steps.
The Bottom Line
DarkTortilla RAT combines remote-access risk with browser and payment-data theft, then uses three separate channels to move collected information away from the infected computer.
Isolation, thorough cleanup, session revocation, credential replacement, and financial monitoring are all necessary. Treat a clean rebuild as the safest option when the intrusion scope remains unclear.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.