

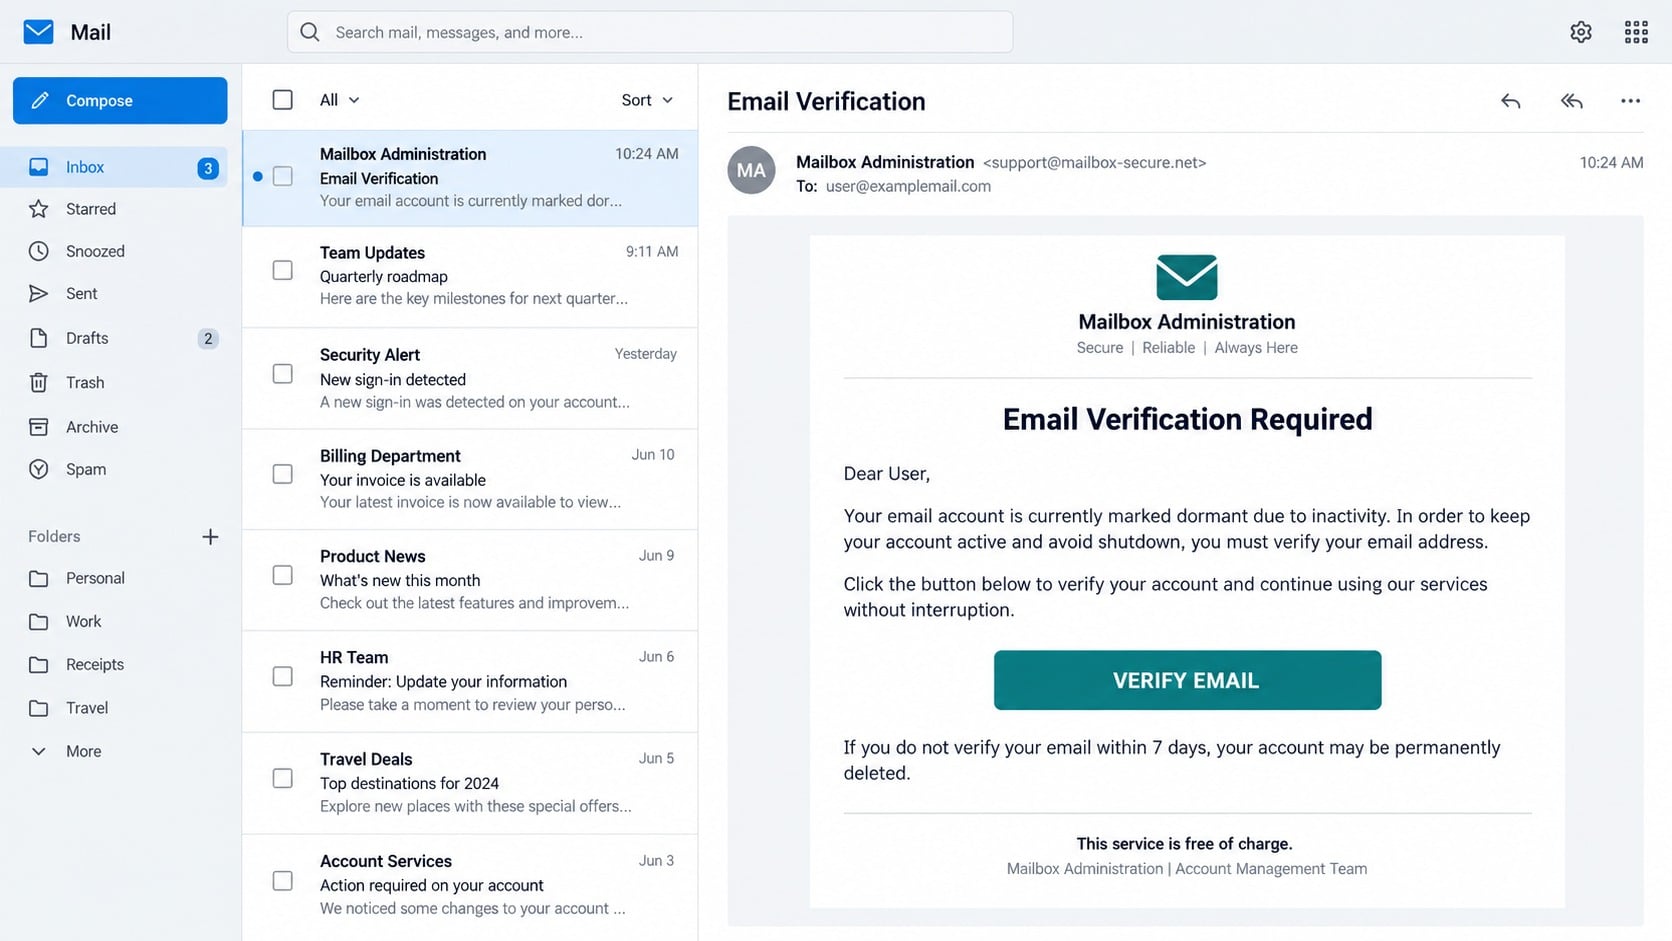
The subject says “Email Verification,” but the message inside sounds more serious. Your mailbox has supposedly been marked dormant and faces shutdown.
The notice promises a free, immediate fix. Its simplicity is reassuring at first, which makes the next click unusually easy to justify.
Overview
The message calls an active mailbox dormant
The Dormant Email Account scam arrives as an automated maintenance notice, often using the unremarkable subject “Email Verification.”
It claims the recipient’s account is currently dormant and asks for immediate verification to prevent shutdown.
A “VERIFY EMAIL” button appears beneath the warning. A line saying the service is free makes the request sound like routine account care.
The contradiction is easy to miss: the account successfully received the message, yet an unidentified sender says it is inactive.
The linked form is not the recipient’s webmail service
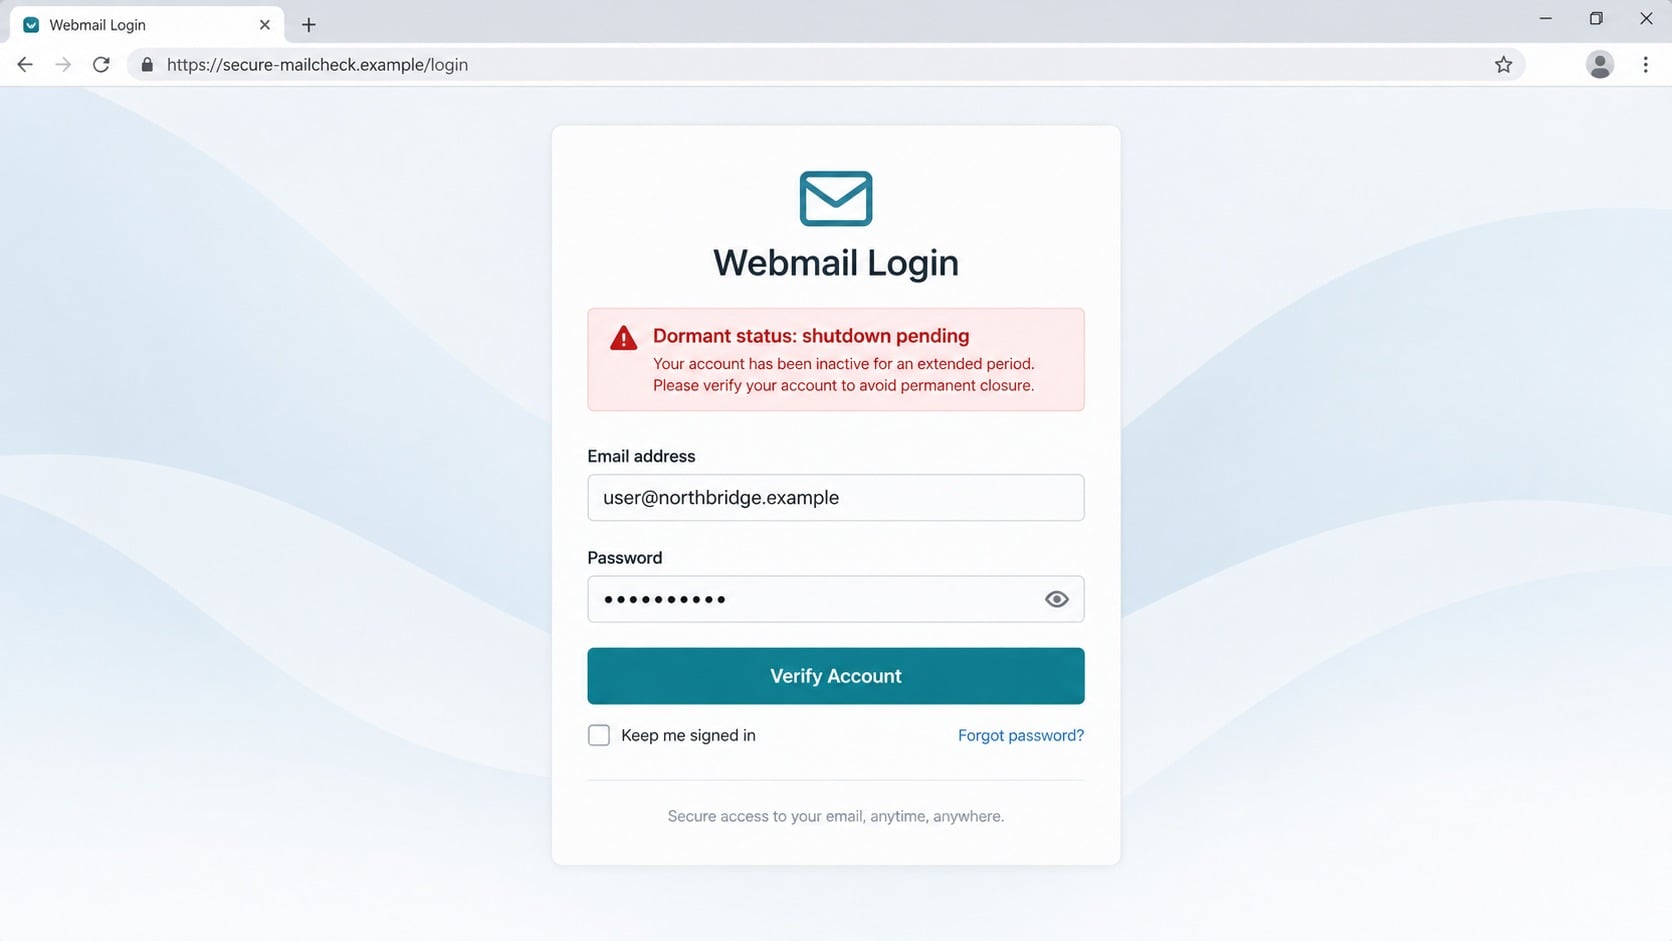
An observed link led to a generic Webmail Login form hosted through jobnep[.]com.np, a domain unrelated to the recipient’s provider.
The form may arrive with the victim’s email address already inserted. That personalization can come directly from a URL parameter.
It then asks for the mailbox password, presenting submission as the final step required to keep the account working.
No genuine provider can safely confirm a user through an unrelated website that collects the account’s secret.
The shutdown story protects a credential-harvesting operation
The scam is designed to capture webmail credentials, not measure account activity or reactivate a dormant address.
Its effectiveness comes from plain language and a narrow choice: verify now or risk losing the mailbox.
Important indicators include:
- A generic support identity with no established provider relationship.
- A claim of dormancy delivered to a mailbox that is receiving mail.
- No date showing when the account supposedly became inactive.
- No explanation of the provider’s actual dormancy policy.
- A verification link leading to an unrelated country-code domain.
- A generic page asking for the complete email password.
- No corresponding warning inside the official account.
What “Dormant” Normally Means
Real providers define inactivity through published policies, account history, product type, and a measurable period without sign-ins or use.
A provider considering account closure typically knows its own name, the exact service involved, and the authenticated channels available to the customer.
Important notices may appear through multiple trusted surfaces, including account settings, an official application, or a recovery address already on file.
A random email cannot declare a mailbox dormant merely because it repeats the recipient’s address.
The message also asks for both the email address and password, information the real provider’s sign-in service already handles on its own domain.
If dormancy genuinely concerns you, start from the provider’s official site and read the account-status policy there.
How the Dormant Email Account Scam Works
Step 1: The sender chooses a claim that applies to every mailbox
Unlike a bank or parcel scam, this campaign does not need to guess which company the recipient uses.
Every target has an email address, and every address could theoretically become inactive someday.
The sender therefore avoids specific branding and writes as though one universal support team administers all mailboxes.
Large recipient lists make that strategy efficient. Even a small response rate can provide valuable credentials.
Step 2: The notice reframes inactivity as an immediate shutdown
The body says the account has been marked dormant and must be verified now to avoid closure.
No documented policy, inactivity period, case number, or account history supports the claim.
Instead, the warning uses an absolute consequence and a single action button.
The phrase “free of charge” quietly reassures readers that the process carries no cost, while distracting from the requested password.
Step 3: Personalization is added through the recipient address
The button may contain the recipient’s email address inside the URL, allowing the next page to display it automatically.
Seeing the correct address makes the page appear connected to the inbox, although no protected account lookup occurred.
Email addresses are commonly available through breaches, mailing lists, business websites, and earlier messages.
Personalization should never outweigh a mismatched domain or an unexplained password request.
Step 4: A generic webmail page collects the password
The landing page uses broad labels such as “Webmail Login” because it must accommodate targets from many providers.
A familiar envelope icon, simple form, and prefilled address mimic the final stage of an ordinary sign-in.
The password entry is transmitted to the site operator when the victim submits the form.
The page may reject the first attempt to encourage a second password, capturing both an old guess and the currently used credential.
Step 5: Attackers establish access and conceal their activity
With valid credentials, an intruder can sign in, read messages, search attachments, copy contacts, and monitor password-reset traffic.
Forwarding can send future mail to an outside account. Rules can move security alerts away from the Inbox.
Recovery details or app passwords may be changed to preserve access after the victim notices something wrong.
A stealthy attacker may avoid changing the visible password immediately, preferring continued access over an obvious lockout.
Step 6: The real mailbox becomes a platform for further fraud
Messages from a compromised account pass an important trust test: contacts recognize the genuine address and existing conversation history.
Attackers can send fake documents, request payments, impersonate the victim, or reset accounts connected to that inbox.
Business accounts may expose contracts, supplier details, invoices, and customer conversations that support targeted fraud.
The dormant-account story ends after the password submission, but the stolen mailbox can support weeks of unrelated abuse.
Sender, Domain, Activity, and Login Verification Checks
Identify the organization actually responsible for the mailbox
For a personal account, the provider is the service shown in the official application or address used for normal sign-ins.
For work or school mail, administration may belong to an internal IT team, managed provider, or institution-specific support desk.
A sender called “Account Support” has not proved any connection. Expand the address and compare its domain with established communications.
When necessary, call or message the known administrator through a directory, intranet, or earlier trusted conversation.
Examine the destination as carefully as the message
Preview the button’s URL and identify the registered domain. Ignore decorative subdomains, path names, or words implying security.
The observed jobnep[.]com.np destination did not belong to the target’s email provider.
A page can display any logo or copy any layout after loading. Ownership of the domain remains the stronger identity signal.
Do not visit the suspicious address for confirmation. Navigate directly to the provider through a known route.
Check whether the account is actually inactive
Review recent sign-ins, sent messages, billing status, service usage, and authenticated notifications inside the official account.
An actively used mailbox with normal access and no dashboard warning does not become dormant because an outside email says so.
Read the provider’s real inactivity policy if long-term use is uncertain. Note the defined timeline and notification procedure.
For managed accounts, ask the administrator whether any deactivation or retention action is scheduled.
Judge the login request by where it occurs
A familiar sign-in form is safe only when it is delivered from the expected official domain and opened through a trusted route.
A generic Webmail Login page on an unrelated domain should never receive a mailbox password.
Password managers can help expose the mismatch because stored credentials are tied to the correct site.
If a page says the password is wrong after submission, treat the credential as exposed rather than trying again.
Why Email Accounts Are High-Value Targets
Most online services treat email as proof that the account owner controls a recovery channel.
An attacker who controls that channel can request resets, intercept confirmation links, and erase the evidence afterward.
Stored correspondence can answer security questions indirectly by revealing dates, relatives, employers, travel, purchases, and addresses.
Attachments may include scans of identity documents, contracts, tax forms, applications, medical records, or bank information.
Contact lists transform one stolen account into a distribution network. Each trusted relationship becomes another potential target.
For organizations, a compromised mailbox can enable:
- Payment-redirection messages inserted into real invoice threads.
- Fake document links sent to customers and colleagues.
- Confidential file collection from cloud invitations.
- Impersonation of managers, vendors, or support personnel.
- Silent monitoring of negotiations and financial timing.
- Harvesting signatures and writing patterns for later campaigns.
How to Find Persistence After a Mailbox Takeover
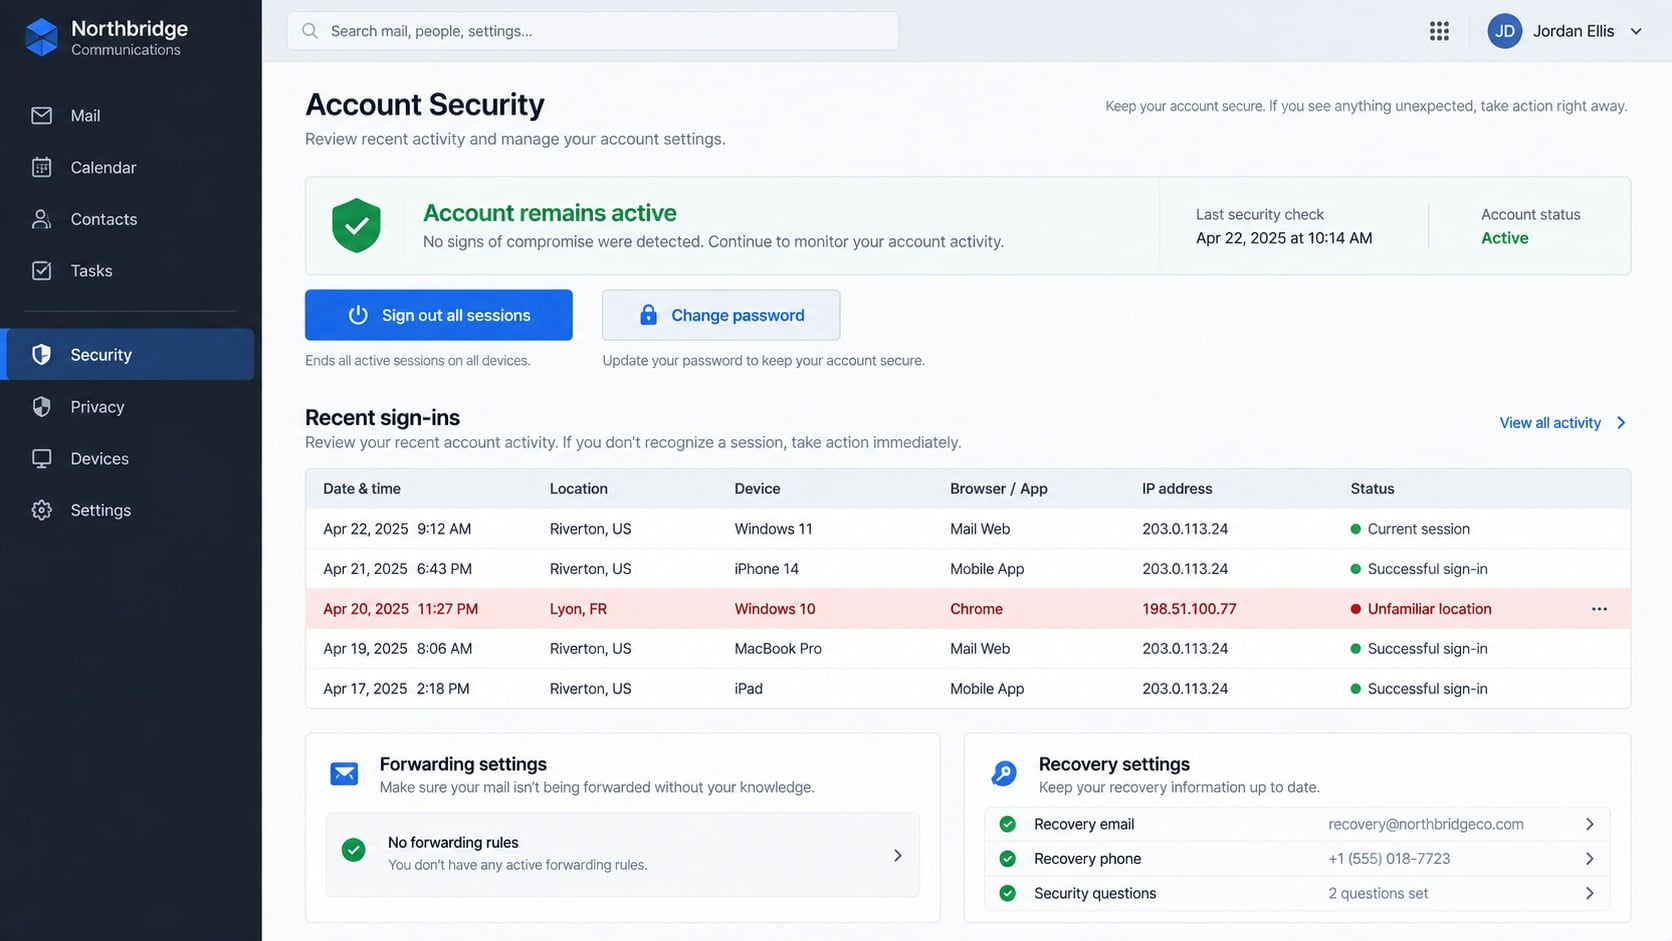
Changing the password blocks many simple intrusions, but it does not automatically reverse every setting changed during access.
Open the official security page and revoke all sessions. Then review devices individually for dates and locations that do not match your activity.
Inspect automatic forwarding, POP and IMAP access, filters, blocked addresses, delegates, connected applications, and application-specific passwords.
Review the recovery address and telephone number. An attacker-controlled recovery method can enable another takeover later.
Look for rules that delete, archive, mark read, or redirect messages containing words such as security, password, invoice, or verification.
Search account activity around the time of the phishing submission. Preserve suspicious entries before removing them if an investigation may follow.
What to Do if You Have Fallen Victim to This Scam
- Stop using the suspicious page. Close it without entering anything else. Do not return to test whether the warning has disappeared.
- Secure email first. From a trusted device and the official provider site, replace the submitted password with a new, unique credential.
- Revoke sessions and tokens. Sign out all devices, remove unknown application passwords, and disconnect applications you do not recognize.
- Correct recovery information. Delete unfamiliar recovery addresses, telephone numbers, passkeys, security keys, delegates, and trusted devices.
- Audit mailbox behavior. Remove unauthorized forwarding, filters, rules, signatures, automatic replies, POP access, and IMAP connections.
- Turn on stronger authentication. Use a passkey, hardware key, or authenticator application. Avoid approving unexpected prompts sent during the incident.
- Replace reused passwords. Update every service that shared the stolen credential, especially financial, cloud, shopping, workplace, and social accounts.
- Run Malwarebytes when exposure included files. Scan fully if you opened a download, installed anything, granted permissions, or noticed browser changes.
- Add preventive filtering. AdGuard can block many known phishing pages and harmful ad routes before they display, complementing browser and email protections.
- Warn administrators and contacts. Report workplace accounts immediately and tell contacts through another channel if fraudulent messages were sent.
- Save useful evidence. Preserve the original email, headers, URLs, screenshots, security activity, and approximate submission time before completing abuse reports.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
What Not to Do After Receiving the Warning
Do not reply to ask whether the notice is real. The person controlling the campaign will simply confirm their own false story.
Do not click an unsubscribe link. Administrative notices do not require marketing opt-outs, and a scam link can record another interaction.
Do not forward the message casually to colleagues with its link still active. Use your organization’s reporting function or attach it for security review.
Do not keep entering different passwords. A malicious form may collect every attempt and test them across multiple services.
Do not assume multi-factor authentication makes the password harmless. Attackers may trigger approval prompts or use the password where authentication is weaker.
Do not pay anyone promising guaranteed account recovery. Work directly with the provider and known administrators.
If the Mailbox Has Truly Been Unused
A real period of inactivity does not make the emailed link trustworthy. Verify the account through the provider’s normal sign-in page first.
Review the published inactivity policy and confirm when you last signed in, sent mail, used storage, or accessed another connected service.
Some providers count several forms of activity, while others apply different rules to paid, workplace, school, or legacy accounts.
Export important mail and contacts if the account remains accessible but is no longer regularly used.
Update recovery information before abandoning an old address. Otherwise, future password resets may continue traveling to a mailbox you rarely monitor.
Remove the address from important accounts once you stop controlling it. An expired recovery mailbox can create long-term security problems.
Frequently Asked Questions
Can my email account genuinely become dormant?
Yes, some providers define inactivity policies. Verify the specific policy and account status through the official service, never through an unsolicited link.
Why was my correct email address already on the fake page?
The link can carry the address as ordinary text and insert it into the form. That does not mean the site accessed the mailbox.
Is a country-code domain automatically malicious?
No. The problem is the domain’s lack of a legitimate relationship to the provider, combined with the deceptive message and password request.
What if the fake page rejected my password?
Change it immediately. A rejection can be scripted after the page has already transmitted the submitted value.
Can attackers remain after I change the password?
They may retain sessions, forwarding, connected applications, or recovery methods. Revoke access and inspect every security and mail setting.
Do I need to scan after only clicking the link?
A scan is prudent if anything downloaded or behavior changed. If you only viewed the page and entered nothing, account monitoring is the priority.
The Bottom Line
The Dormant Email Account message turns a vague maintenance concept into an immediate shutdown threat, then sends recipients to an unrelated password form.
Verify activity from the real provider. If credentials were submitted, change them, remove hidden access, and protect every other account using that password.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.