

A calm administrative notice says updated service terms require confirmation. It even reminds readers to verify websites before entering account information.
That security advice makes the message sound responsible, but one embedded sign-in route tells a very different story when examined carefully.
Overview
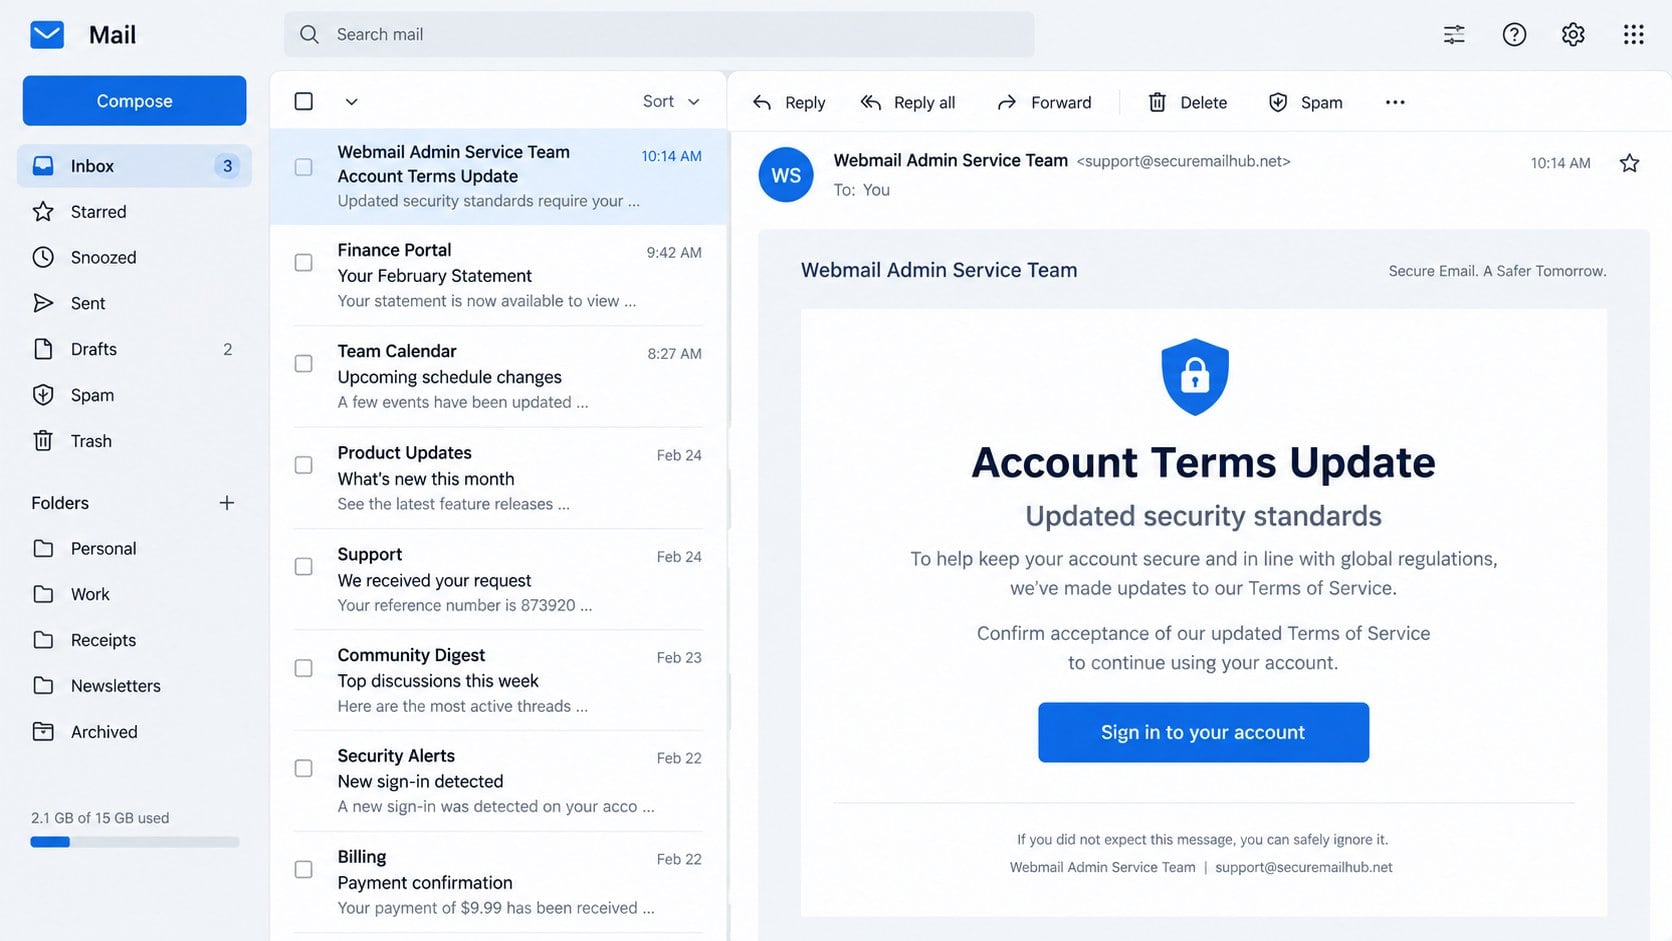
The email frames the request as routine compliance
The Account Terms Update email claims a “Webmail Admin Service Team” is reviewing account information and revised security standards.
It says continued access to features and important notifications may depend on confirming acceptance of updated Terms of Service.
The neutral tone avoids loud threats. A short list instructs the recipient to visit the official website, sign in, and review account settings.
The message contradicts its own safety reminder
The email warns users to avoid signing in through unexpected links, yet its “Sign in to your account” text leads directly to a phishing page.
That contradiction is not accidental carelessness. Security language can lower suspicion and make the dangerous link appear to be the approved exception.
The sender name is generic and identifies no real host, employer, administrator, policy version, effective date, or authenticated service notification.
The destination imitates a webmail login screen
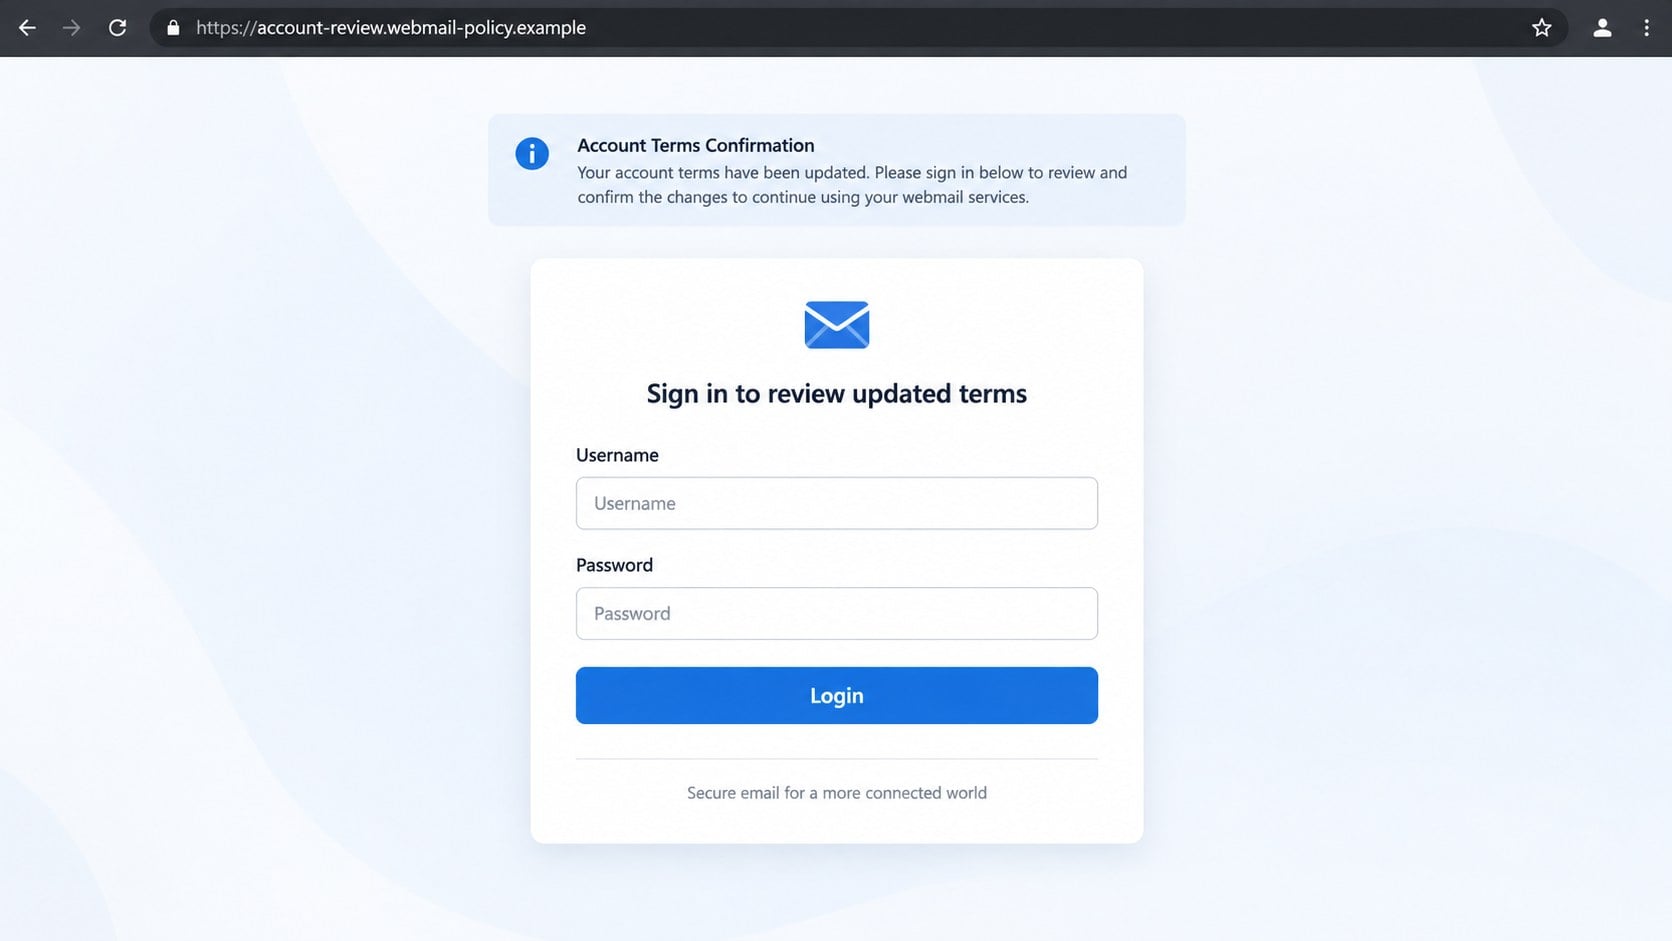
Observed versions lead to a counterfeit Roundcube-style page hosted on an unrelated domain, where the victim is asked for username and password.
The page does not connect to the recipient’s real mail server. It exists to collect the credentials entered into its form.
Warning signs include:
- A fabricated “Webmail Admin Service Team” without organizational identity.
- No direct link to a named policy or revision summary.
- A sign-in request delivered through an unsolicited compliance email.
- A destination domain unrelated to the recipient’s mail host.
- A copied webmail design presented as authentication proof.
- Instructions that contradict the email’s own security warning.
- No corresponding notice inside authenticated account settings.
Why Policy Notices Make Effective Phishing Lures
People regularly accept software agreements, privacy updates, workplace policies, and new security standards. The subject therefore feels ordinary rather than sensational.
Recipients may expect that refusal affects service access. The possibility of missing mail or notifications creates enough pressure without an explicit countdown.
Long legal documents are rarely read closely. Scammers exploit that habit by referring vaguely to “updated terms” without supplying a verifiable revision.
The message also imitates responsible security communication. Terms such as compliance, community safety, account protection, and official website create an administrative voice.
A reader may follow the numbered instructions mechanically, especially when reviewing several workplace notices or account tasks during a busy day.
The safest response is not to debate the email’s language. Open the service independently and look for the same policy notice inside the signed-in account.
How the Account Terms Update Email Scam Works
Step 1: The campaign impersonates an unnamed administrator
The display name uses authority without committing to a provider. “Webmail Admin Service Team” could appear relevant to almost any personal or business mailbox.
This generic identity lets one template target many domains. The recipient may assume their host, employer, or IT contractor sent it.
The real sender address often undermines that assumption. Expand complete headers and compare the domain with established administrator communications.
Step 2: A vague policy update creates a plausible obligation
The message refers to revised security standards and Terms of Service but does not identify specific changes, a document version, or the legal service provider.
It says confirmation maintains access to account features and notifications. That wording encourages action while avoiding a claim that can be checked easily.
Authentic policy notices normally identify the company, effective date, material changes, and a stable policy page that remains readable without surrendering credentials.
Step 3: Security advice is used to camouflage the link
The email may tell users to type the official address directly and avoid unexpected links. Immediately afterward, clickable sign-in text appears within the same message.
Readers who skim can interpret the warning as evidence that the sender understands security. They may not notice the link violates the stated instruction.
This technique borrows trust from good advice, then directs the recipient toward the very action that advice should prevent.
Step 4: The destination copies a familiar webmail interface
The linked page can resemble Roundcube or another common mail client. Logos, form labels, background art, and buttons are easy to reproduce.
Appearance cannot establish ownership. The browser domain may belong to an unrelated host with random characters or misleading security-themed words.
The form requests credentials that should only be entered on the organization’s known webmail address or verified identity provider.
Step 5: The form sends the password to the operator
Submitting the username and password can transmit both to the scam infrastructure. A loading animation or error message may hide what occurred.
The victim might retry, providing another current or historical password. The page can then redirect to a real website to reduce suspicion.
If the account uses multi-factor authentication, attackers may immediately attempt sign-in and pressure the victim to approve a genuine provider prompt.
Step 6: Mailbox access supports impersonation and account recovery abuse
A compromised inbox can reveal personal correspondence, business documents, contacts, invoices, and password-reset messages for connected services.
The attacker may send policy notices or document lures from the real address, where recipients trust the established sender and conversation history.
Forwarding, hidden rules, delegates, applications, and recovery changes can preserve access or conceal warnings after the original phishing page disappears.
Sender, Policy, Domain, and Account Verification Checks
The sender must identify the actual service or organization
A real administrator should be traceable to the provider, employer, school, or hosting company responsible for the mailbox.
Compare the From, Reply-To, Return-Path, and signing information with earlier genuine notices. A display name alone supplies no authority.
Ask internal IT through a known helpdesk or telephone number. Do not use contact information embedded in the questionable notice.
The policy should be available without surrendering a password
Search the provider’s official legal or policy center through a typed address. Look for an effective date, revision summary, and complete organization name.
A legitimate policy can usually be read publicly, even when acknowledgment later occurs inside an authenticated account.
If no matching update exists and support cannot confirm it, the message has failed a basic content check.
The destination must belong to the real mail service
Read the domain from right to left, beginning with the registered name immediately before the first slash. Ignore trusted words placed elsewhere.
A long random hostname, unrelated company domain, raw address, or newly registered site does not become valid because it displays a familiar webmail form.
For cPanel-based hosting, official documentation directs users to their own domain’s secure webmail port or the Email Accounts area, not an arbitrary external host.
The account should show the same notice after independent access
Open the mailbox or administrative panel from a bookmark. Check notifications, policy settings, service messages, and support announcements there.
Authenticated portals can know the account’s provider, organization, and current status. A generic email cannot demonstrate those relationships merely by repeating the address.
When acknowledgment is truly required, complete it inside that verified session rather than returning to the email button.
The Difference Between a Real Policy Update and a Credential Trap
A genuine update names the legal organization issuing it. It supplies stable documents, effective dates, contact routes, and explanations of meaningful changes.
Some services may request acknowledgment, but the action occurs inside the verified application or account dashboard after independent navigation.
The provider does not need users to disclose passwords to the policy itself. Authentication and policy review remain separate, auditable functions.
A phishing notice reverses that relationship. The vague policy is merely a reason to place the victim in front of a password form.
Real notices can still look plain, while fake notices can look excellent. Verification must rely on domains, account records, and confirmed administrators.
What to Examine After Credentials Were Entered
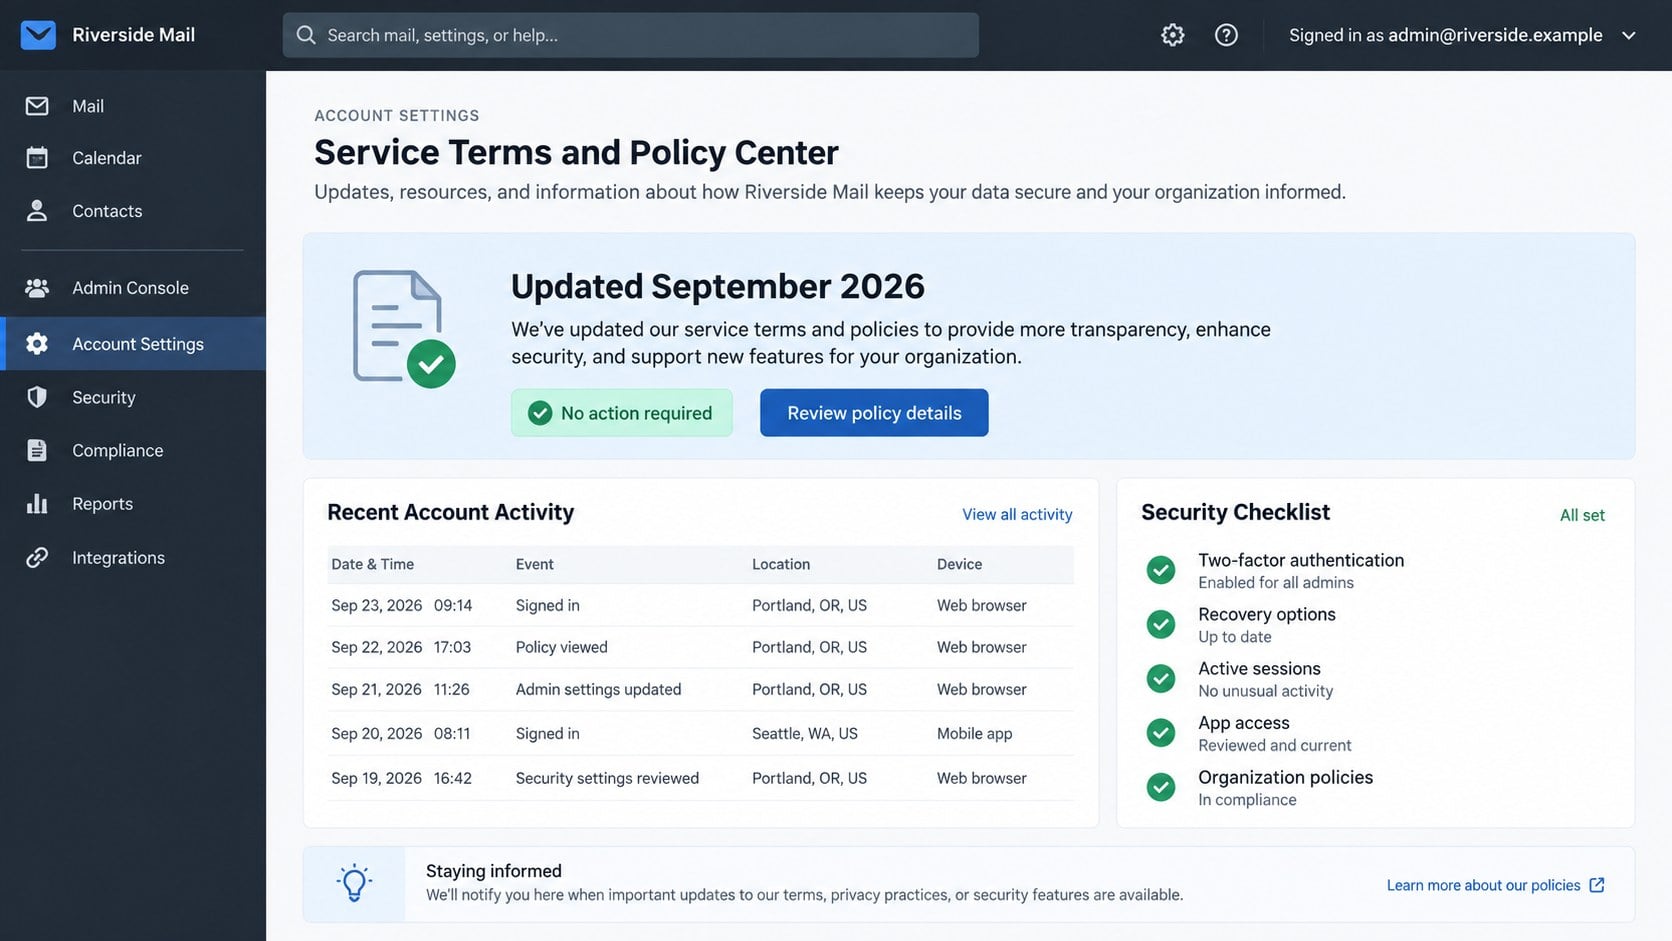
Begin with recent sign-ins and active sessions. Record unfamiliar locations, devices, browser sessions, application passwords, and authentication events before removing them.
Inspect forwarding addresses, delegates, POP or IMAP access, mailbox rules, sent items, deleted messages, and the archive for unauthorized changes.
Review recovery addresses, telephone numbers, security keys, passkeys, backup codes, and trusted devices. Remove anything the account owner cannot explain.
Check connected applications and OAuth grants. A malicious application can retain data access after the primary password changes.
Search for unexpected password resets involving financial services, social accounts, cloud storage, shopping sites, or workplace platforms.
For organizational accounts, preserve administrator logs before retention windows close. Those records can establish which messages and files the attacker accessed.
What to Do if You Have Fallen Victim to This Scam
- Close the counterfeit webmail page. Do not retry credentials, approve prompts, call displayed support numbers, or download supposed policy readers.
- Change the email password through the real service. Use a trusted bookmark or known application on a clean device.
- Terminate every session. Sign out unknown browsers, mobile devices, desktop clients, application passwords, and connected identities.
- Enable stronger authentication. Prefer passkeys or hardware security keys, and regenerate backup codes that may have been exposed.
- Audit mailbox configuration. Remove unfamiliar forwarding, filters, delegates, recovery details, POP access, IMAP connections, and OAuth applications.
- Secure other accounts using that password. Replace every reused credential with a unique value, starting with financial and recovery services.
- Tell the administrator or security team. They can preserve logs, revoke tokens, search related mail, and warn other targeted users.
- Review outgoing activity. Check sent mail, replies, password resets, policy messages, and contact reports for signs of impersonation.
- Run Malwarebytes if files or extensions were involved. A full scan can detect additional payloads delivered beside the password form.
- Use AdGuard for another defensive layer. Its filtering can stop many known phishing destinations and harmful redirect chains during browsing.
- Document and report the event. Keep original headers, URLs, screenshots, sign-in logs, changed settings, and notices received from contacts.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
How Organizations Can Make Policy Notices Safer
Publish policy changes at a stable, bookmarked location and reference them from authenticated dashboards. Avoid requiring action through embedded email login links.
Use consistent sending domains and digitally authenticated mail. Identify the legal entity, effective date, support channel, and account impact clearly.
Tell users that passwords will never be requested by a policy page. Explain exactly where acknowledgment appears inside the official service.
Monitor domain registrations and phishing reports involving organizational names. Remove deceptive pages quickly and alert users through separate trusted channels.
Teach employees to value process evidence over polished design. A copied logo can be perfect while the sending domain remains completely unrelated.
A Safe Method for Reviewing Service-Term Changes
Start from the provider’s known website or application, not the notice. Sign in normally and look for policy or account notifications.
Read the legal entity name, effective date, previous version, revision summary, and instructions explaining whether acknowledgment is actually required.
Compare the announcement with the provider’s public legal pages. A significant change should not exist only behind one emailed password form.
For workplace accounts, ask the administrator whether the organization accepted terms centrally or expects action from individual users.
Take screenshots of contradictions, unusual domains, and missing policy details before reporting. Avoid repeatedly loading the suspected phishing destination.
If the real account displays no notice, contact support through its authenticated portal and provide the email headers without sending your password.
Complete any genuine acknowledgment inside the verified session. Close the original email afterward so its link cannot be opened accidentally.
This approach separates a valid legal update from the delivery message and removes the scammer’s chosen route from the decision.
Organizations should archive official notices and approved delivery dates. Helpdesk staff can compare questionable messages with a reliable internal record.
Users should not interpret legal changes alone. Privacy, legal, or IT teams can confirm whether a notice genuinely affects access.
A real provider benefits when customers verify carefully. Resistance to independent checks is evidence that the requested route is unsafe.
Frequently Asked Questions
Can a real provider update its Terms of Service?
Yes. Genuine updates identify the provider and policy, and the same notice should be verifiable through official legal pages or account settings.
Why does the scam include good security advice?
The advice borrows credibility. The message then contradicts it by directing users through an unexpected sign-in link.
Is Roundcube itself connected to the scam?
No. Criminals can copy the appearance of common webmail software. The counterfeit host is separate from the legitimate product.
Does HTTPS mean the login page is legitimate?
No. HTTPS protects traffic to the displayed domain. It does not prove that domain belongs to the service being impersonated.
What if I entered only my username?
Change nothing solely from panic, but expect targeted follow-ups. Report the page and be cautious with later password or authentication requests.
Should I accept updated terms from the email?
Open the authentic account independently. If acknowledgment is genuinely required, complete it inside the verified service rather than the email route.
The Bottom Line
The Account Terms Update email scam uses calm compliance language and borrowed security advice to guide recipients toward a counterfeit webmail password form.
Verify the policy inside the real account. When credentials were entered, revoke access routes and inspect the mailbox completely, not only the password.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.