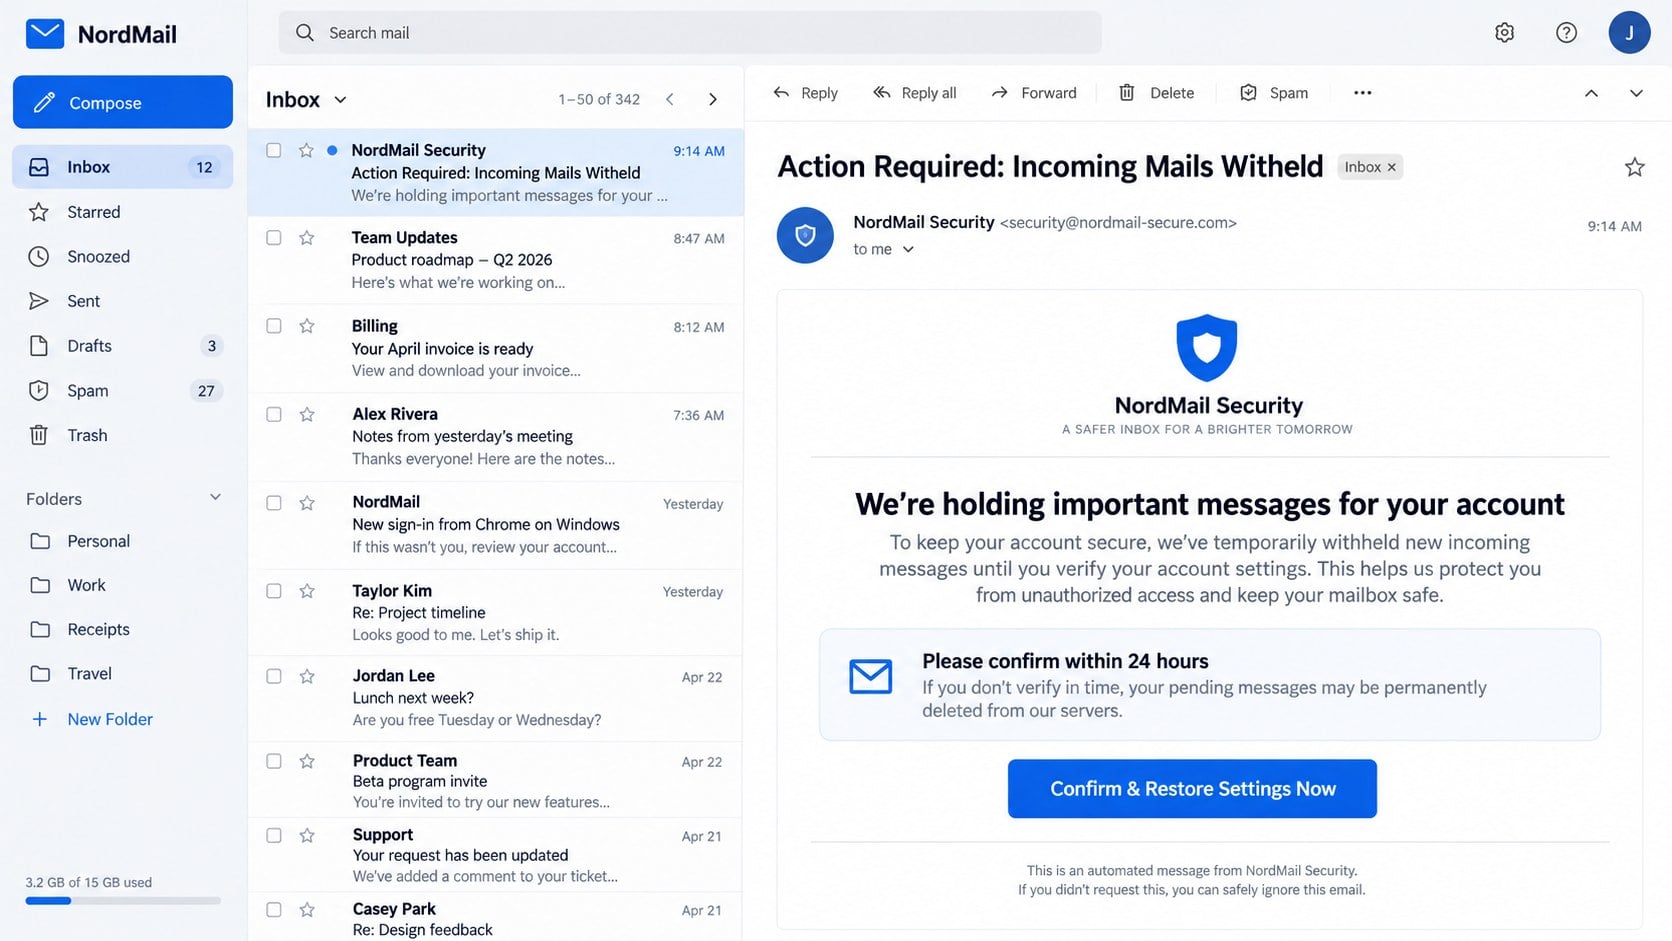
An alarming message says important incoming mail has stopped at the server. A prominent button promises to restore delivery before the waiting messages disappear.
The notice combines a specific timestamp with an obvious spelling error. That odd pairing offers the first clue that its technical story deserves closer inspection.
Overview
The alert claims new messages are being withheld
The Incoming Mails Witheld email says the provider is holding important messages because the recipient must verify account settings.
It often presents a “last check” time and asks for confirmation within 24 hours, implying delayed mail could otherwise be deleted.
A button labeled “Confirm & Restore Settings Now” appears to offer a direct solution to the invented delivery problem.
The misspelled warning leads to a false login
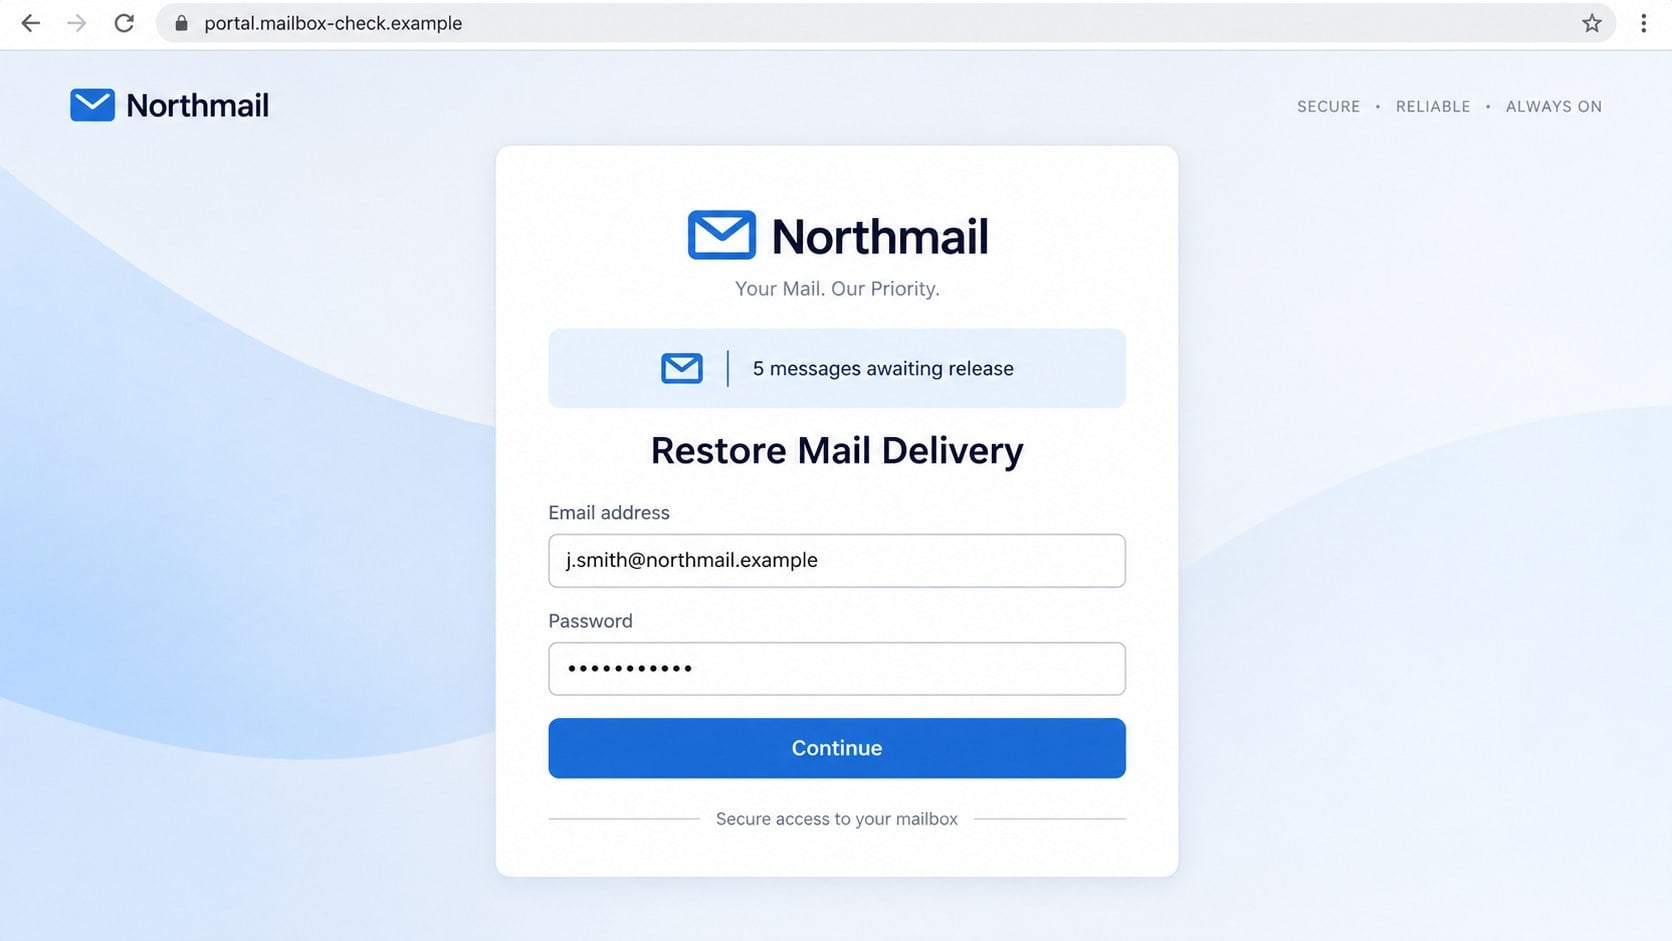
Following the button opens a counterfeit mailbox sign-in page. Some versions imitate Gmail, while adaptable phishing kits can display another provider’s appearance.
The email address may already appear in the username field. This personalization can come from the link and does not prove the provider recognizes the visitor.
The page requests a password to release messages. Information entered there is delivered to the phishing operator rather than an email service.
The mailbox pressure is fabricated
Legitimate providers can report outages, rejected mail, quota limits, or suspicious activity, but those events should be visible inside the authentic account.
An unsolicited link cannot be trusted to diagnose mail delivery. Open the provider independently and inspect status, storage, settings, and administrator notices.
Important warning signs include:
The word “withheld” is misspelled as “witheld.”
No sender, subject, or count identifies the supposed held messages.
A generic service name replaces the actual provider.
The 24-hour deadline is unsupported by account documentation.
The button leads to an unrelated or newly created domain.
The login page pre-fills the address but cannot show real account data.
No matching warning appears after direct access to the mailbox.
Email carries invoices, password resets, customer questions, medical notices, travel confirmations, job offers, and conversations that may feel impossible to miss.
The scam never identifies what is waiting. That ambiguity lets each recipient imagine the message most important to them.
A business user may fear losing an order. A private user may expect a financial, legal, or personal reply. Curiosity supplies the missing details.
The deadline turns uncertainty into urgency. Instead of checking the mailbox normally, a worried reader may choose the button offering instant restoration.
Technical phrases about delivery and verification add authority without providing evidence. Real diagnostics would identify the provider, account, error, and support route precisely.
How the Incoming Mails Witheld Email Scam Works
Step 1: A broad campaign targets active email users
The messages can be distributed widely because every working address receives incoming mail. The story does not depend on a particular subscription or purchase.
Addresses may originate from data breaches, public websites, marketing lists, compromised contact books, or automated discovery across company domains.
Business addresses are particularly useful because one stolen mailbox can expose internal conversations and create trusted routes toward coworkers, clients, and suppliers.
Step 2: The email invents a delivery interruption
The alert says new messages are held until the recipient confirms settings. A timestamp and security language make the unsupported claim appear measured.
No actual mail-server evidence is supplied. There is no bounce report, queue identifier, recipient list, provider status link, or authenticated account notification.
The message frames verification as protection against unauthorized access, turning a suspicious request for credentials into something that appears security-conscious.
Step 3: A short deadline discourages independent checks
The recipient is told to act within 24 hours to ensure delivery. Some versions suggest pending messages may be permanently deleted.
This deadline has no demonstrated connection to a real retention policy. Its purpose is to move the user toward the button before doubts grow.
Unsubscribe links can appear in the footer, but they do not authenticate the sender. On malicious mail, even those links may track or redirect visitors.
Step 4: The button reveals a provider-themed password form
The destination can inspect the target address and display a matching visual theme. Familiar colors and logos create recognition while the actual domain remains unrelated.
A prefilled address gives the impression that the system located a real account. In practice, the email itself can place that address into the URL.
The page asks only for the remaining secret, usually the mailbox password. This streamlined form minimizes the time available for reconsideration.
Step 5: Submitted credentials are tested quickly
Phishing operators can attempt the password against the real provider soon after submission. Automated tools may test common services and identify whether access succeeds.
If multi-factor authentication intervenes, the victim may receive a push notification or code request while the counterfeit page claims verification is continuing.
Approving that prompt can complete the takeover. Reject unexpected authentication requests, even when they arrive moments after a familiar-looking sign-in.
Step 6: The hijacked mailbox becomes a platform for new attacks
Intruders can read messages, search attachments, reset linked accounts, collect personal data, and imitate the owner in existing conversations.
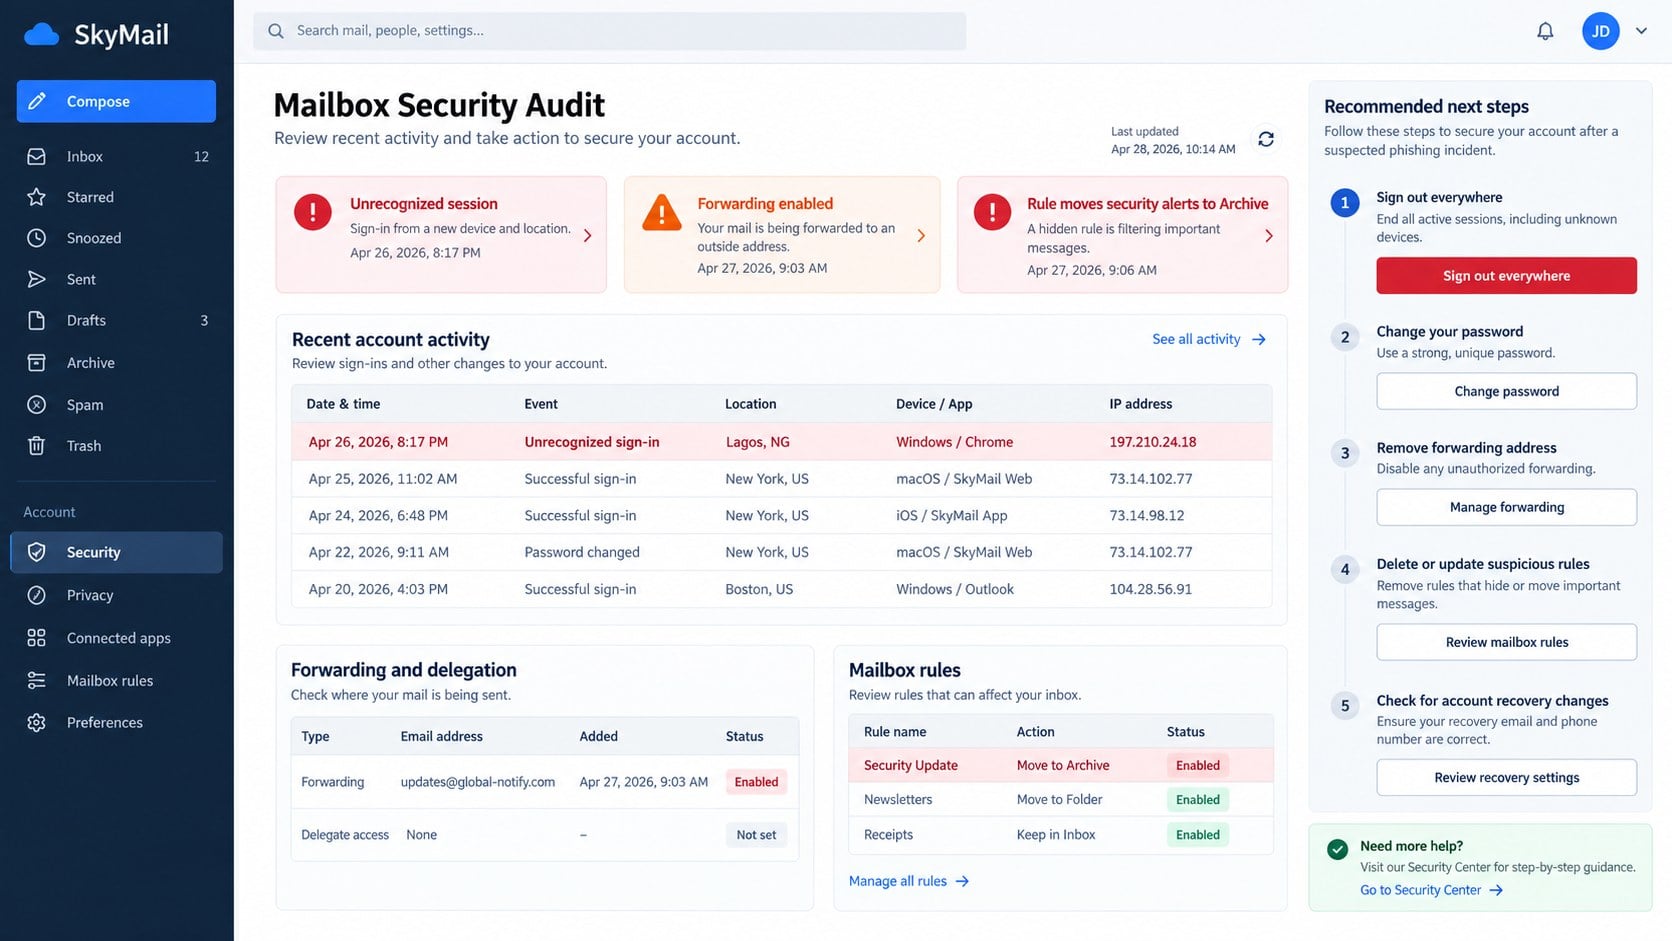
They may establish forwarding, delegates, OAuth access, or hidden inbox rules. Those changes can keep information flowing after the original password is replaced.
Messages sent from the genuine account can spread the same lure to contacts who trust the sender, multiplying the campaign through real relationships.
Sender, Delivery, Destination, and Account Verification Checks
The alert should identify the real service responsible for delivery
Inspect the full sender and Reply-To information. Generic security names or outside domains cannot speak for Gmail, Microsoft, a hosting provider, or workplace IT.
For company mail, forward the message as an attachment to the internal security team through an established reporting channel.
Do not telephone or email contacts supplied inside the alert. Obtain support details from the provider’s official site or existing administrator records.
The mailbox itself should show a genuine delivery problem
Open the service from a trusted bookmark or application. Check storage usage, service status, spam, filters, forwarding, blocked senders, and administrator announcements.
Ask a known contact to send a harmless test message. Administrators can inspect message tracking and server logs without requiring the user’s password by email.
If mail is arriving normally and no authenticated warning exists, the claim that delivery is suspended loses its foundation.
The destination domain matters more than the copied design
Read the registered domain immediately before the first single slash. Logos, provider names, lock images, and page titles can all be reproduced.
Misspelled domains, unusual subdomains, free hosting, raw IP addresses, and unrelated business sites are strong signs the page is not your provider.
Close the page when uncertain. Navigate directly to the real service rather than searching for a similarly named login portal.
The account request should never depend on an email button
Real password changes and security reviews belong inside authenticated settings. Providers do not need users to reveal passwords to release supposed messages.
Password managers can help expose mismatched domains because saved credentials normally appear only on the correct site.
Passkeys and hardware keys provide stronger protection by verifying the website during authentication, making ordinary copied login pages less effective.
What Attackers Look for Inside a Stolen Inbox
The newest messages reveal current priorities, relationships, purchases, and conversations. That context helps attackers choose convincing people and moments to impersonate.
Password-reset mail can lead toward social networks, marketplaces, cloud storage, and financial services. Archived messages may expose answers to identity questions.
Invoices and payment discussions reveal suppliers, account numbers, approval chains, and expected transfer dates. A later reply can redirect money without creating a new conversation.
Attachments may contain tax documents, identity scans, contracts, medical records, or customer data. Search functions let intruders locate valuable terms rapidly.
Contacts and signatures provide names, roles, direct lines, and branding. Those details can make new fraud appear native to the organization.
Mailbox Changes That Signal Persistence
A forwarding address can copy every new message outside the account. Delegated access may let another identity read or send mail without the original password.
Inbox rules can archive security warnings, delete bank replies, or divert messages containing words such as invoice, fraud, password, or payment.
Connected applications may retain tokens after a password change. Review permissions and remove anything added during or after the phishing event.
Unknown recovery details can help an attacker regain entry later. Check telephone numbers, alternate addresses, passkeys, security keys, and backup codes.
Review recent sign-ins for unfamiliar locations and devices, but remember that virtual private networks can complicate location evidence. Evaluate the complete activity pattern.
What to Do if You Have Fallen Victim to This Scam
Leave the false login page. Do not retry the password, approve authentication prompts, download mail tools, or contact support displayed there.
Change the mailbox password immediately. Use the provider’s official application or typed address from a known-clean device.
End every active session. Sign out browsers, mobile clients, desktop applications, app passwords, and devices you do not recognize.
Inspect forwarding and mailbox rules. Remove external addresses, hidden filters, delegates, POP access, and unfamiliar IMAP connections.
Review recovery and authentication methods. Delete unknown details, regenerate backup codes, and enable passkeys or a hardware key when available.
Replace reused passwords. Secure banking, social, shopping, workplace, and cloud accounts that shared the exposed credential.
Notify workplace security quickly. Administrators may need to revoke tokens, preserve logs, search related mail, and warn recipients.
Check sent and deleted items. Identify phishing, invoice changes, password resets, or replies created without your authorization.
Run Malwarebytes if anything downloaded. A full scan can detect malicious files or unwanted software introduced during the fake recovery process.
Use AdGuard for additional filtering. It can block many recognized phishing pages, malicious redirects, and deceptive advertising domains.
Save evidence and report the incident. Preserve headers, URLs, screenshots, sign-in logs, altered settings, and messages sent from the account.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Anti-Malware Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
Adware — the cause of those annoying pop-ups
Browser hijackers — unwanted redirects and changed homepages
Trojans and spyware — hidden programs stealing your data
Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The whole process takes about 5 minutes.
Malwarebytes for WindowsMalwarebytes for MacMalwarebytes for Android
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
(The link opens in a new page where your download will start)
Install Malwarebytes
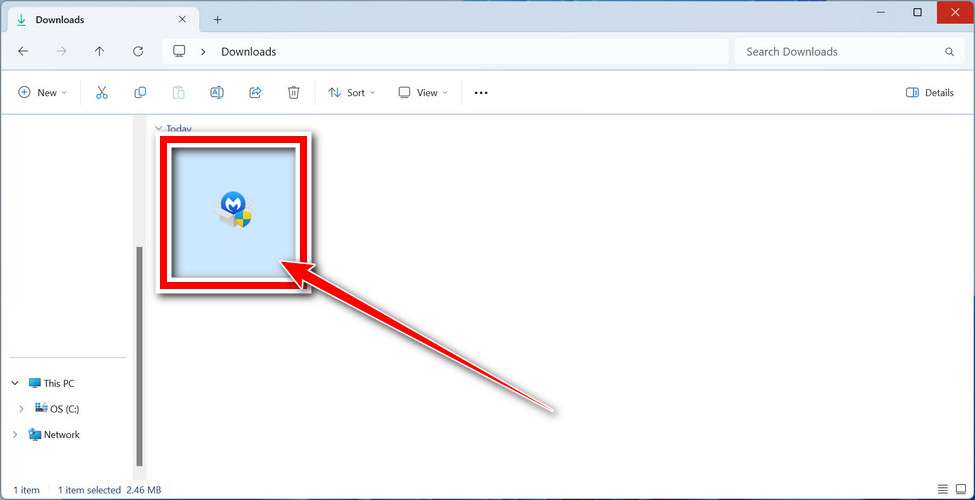
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.
Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
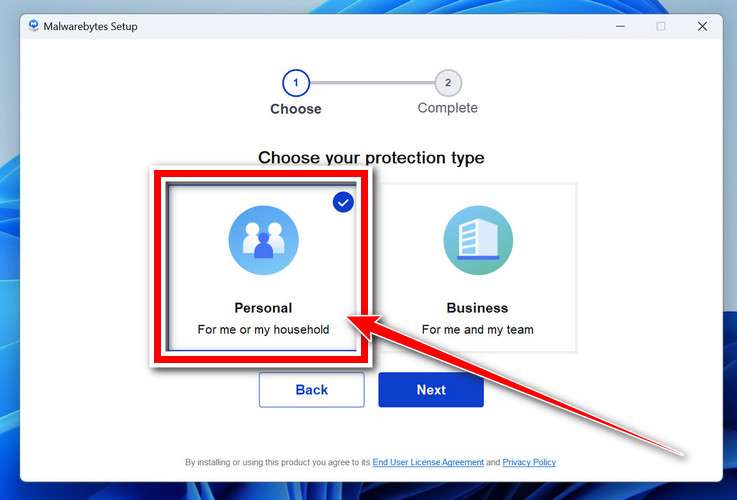
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.
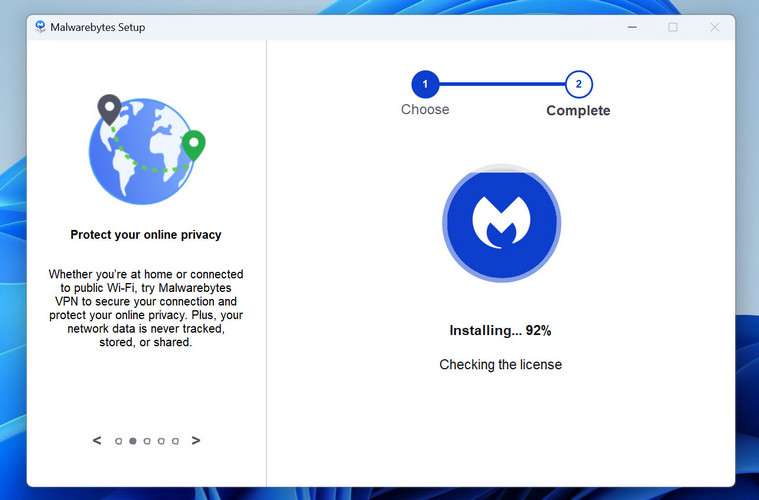
Malwarebytes will now install on your device. This usually takes under a minute.
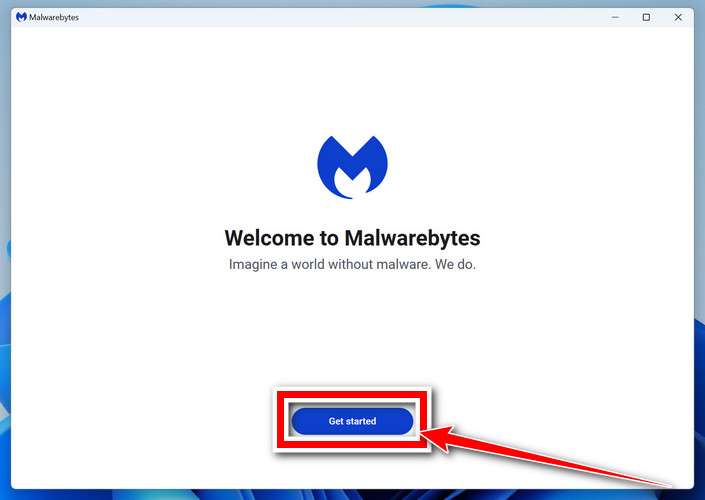
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.
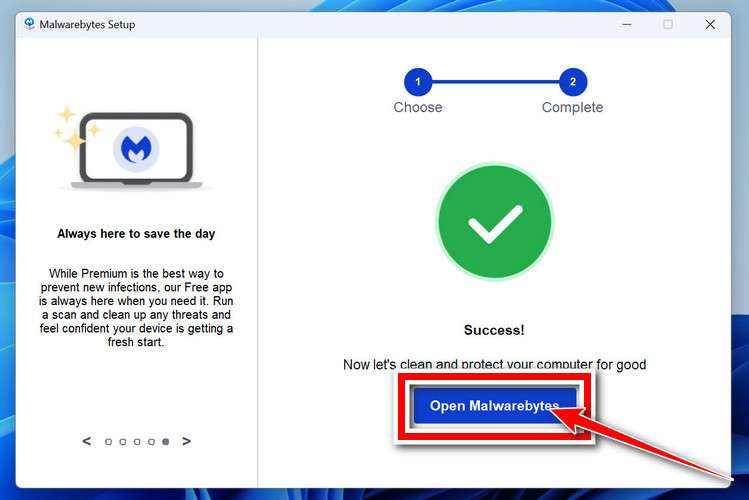
On the final screen, click Open Malwarebytes to launch the program.
Enable “Scan for Rootkits”
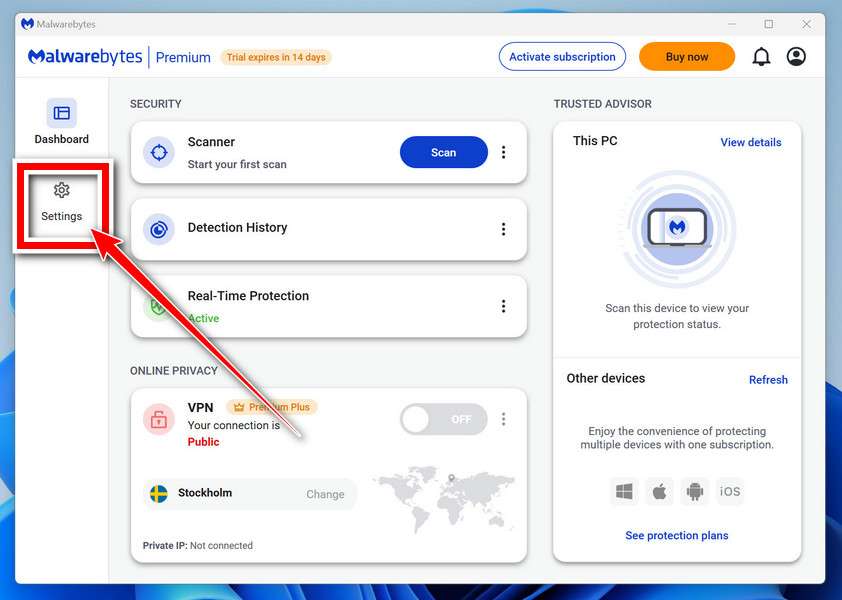
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.
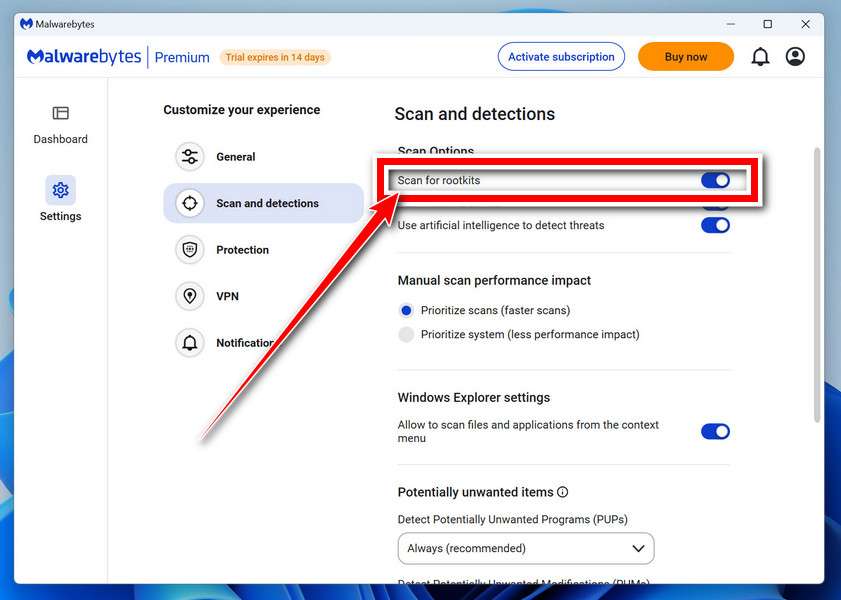
In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.
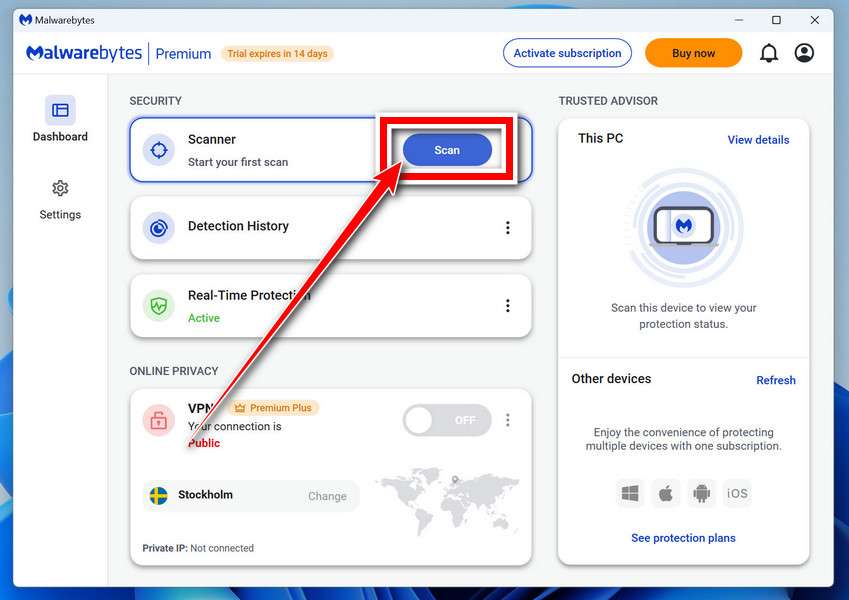
Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
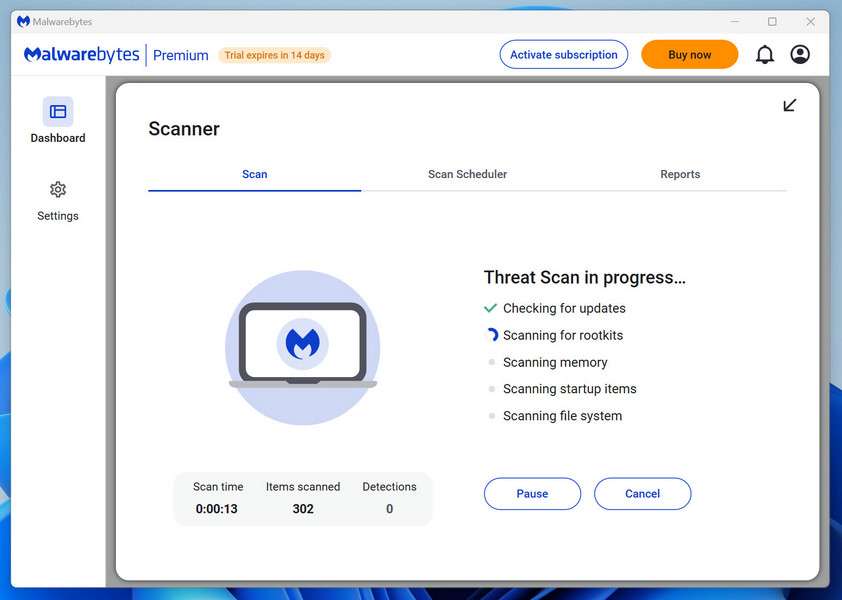
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take several minutes. Feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
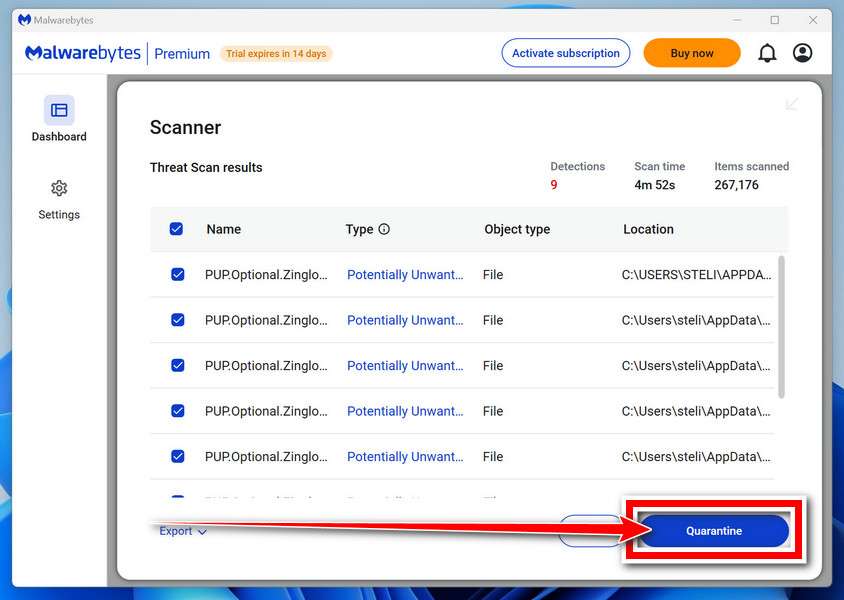
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.
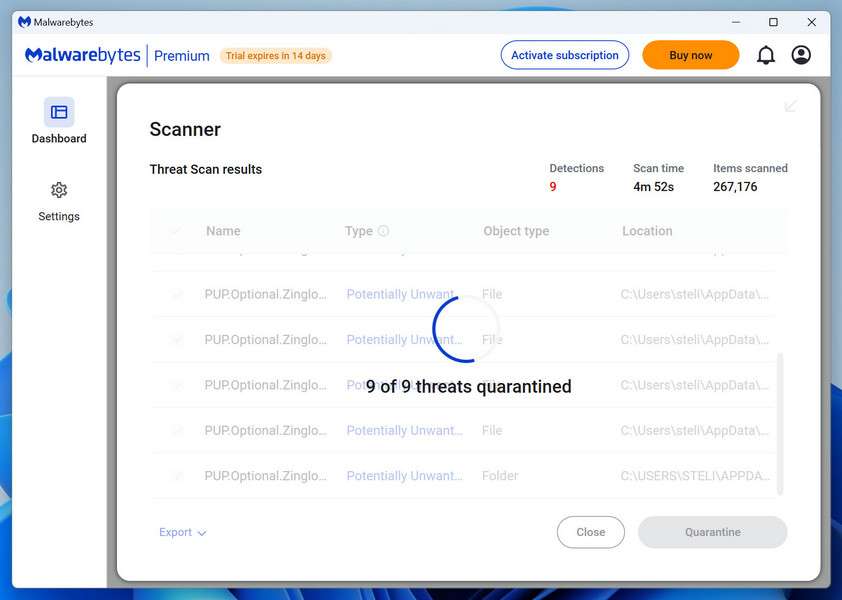
Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.
Restart Your Computer
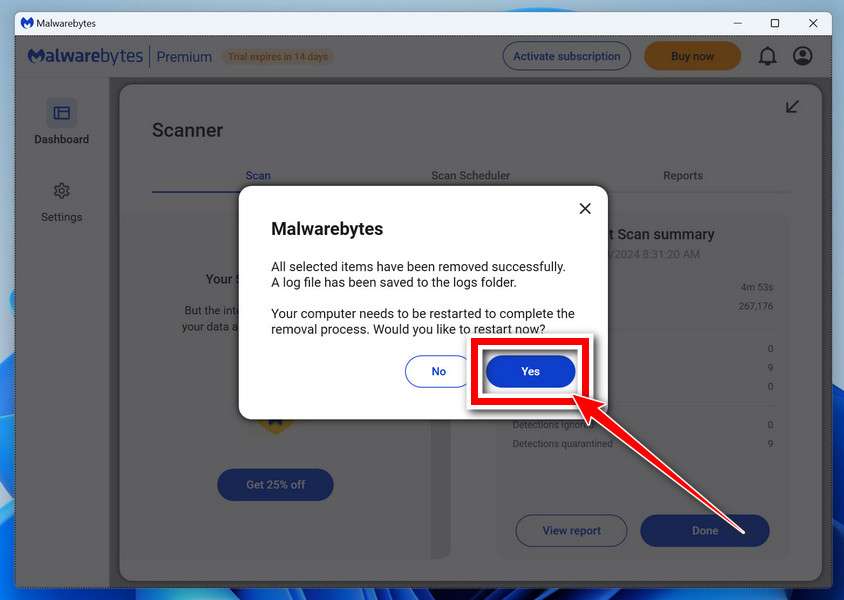
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, your PC is clean and you can continue with the next steps in this guide.
When the scan finishes, click Quarantine to remove everything Malwarebytes found. That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If your current antivirus allowed this malicious program on your computer, you may want to consider purchasing Malwarebytes Premium to protect against these types of threats in the future. If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
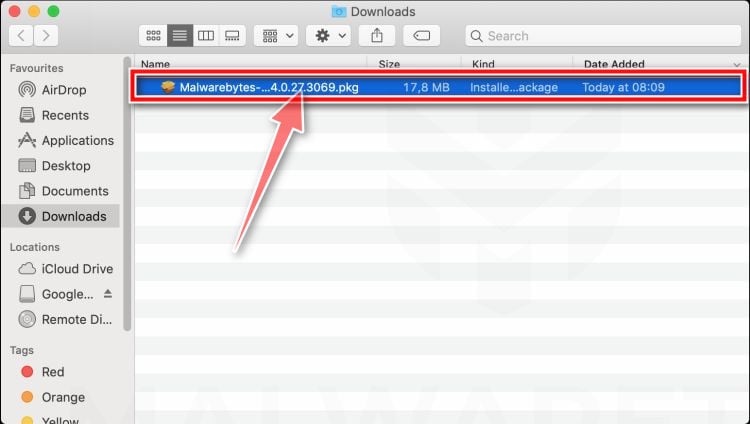
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.
Follow the On-Screen Prompts to Install Malwarebytes
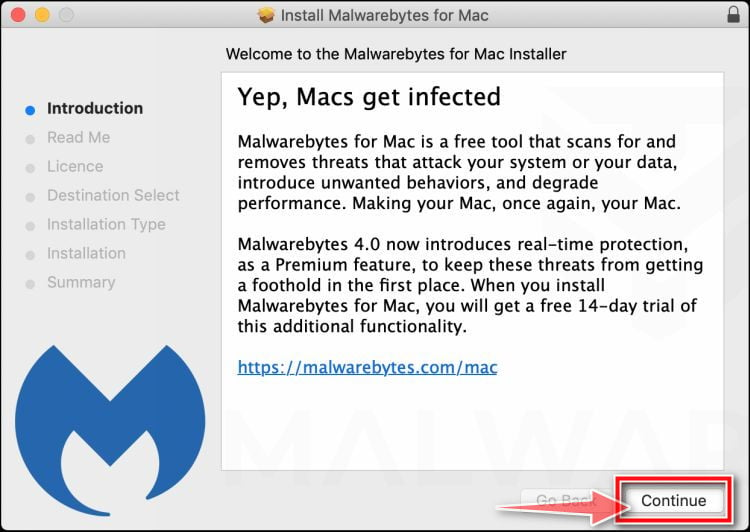
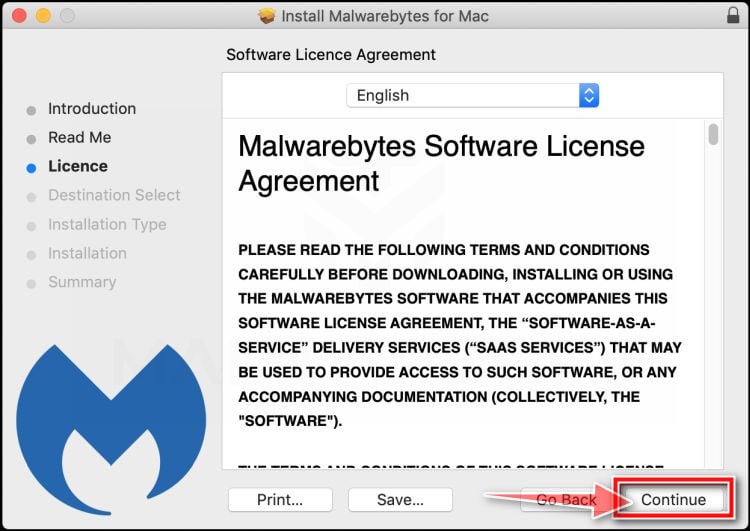
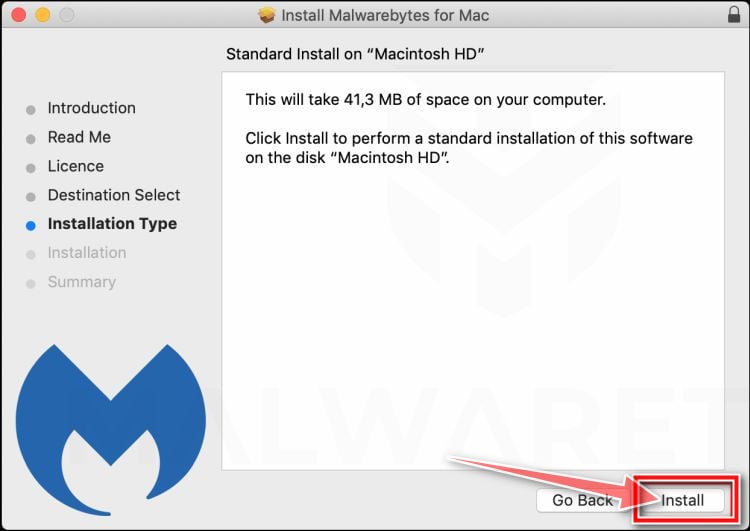
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.
When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
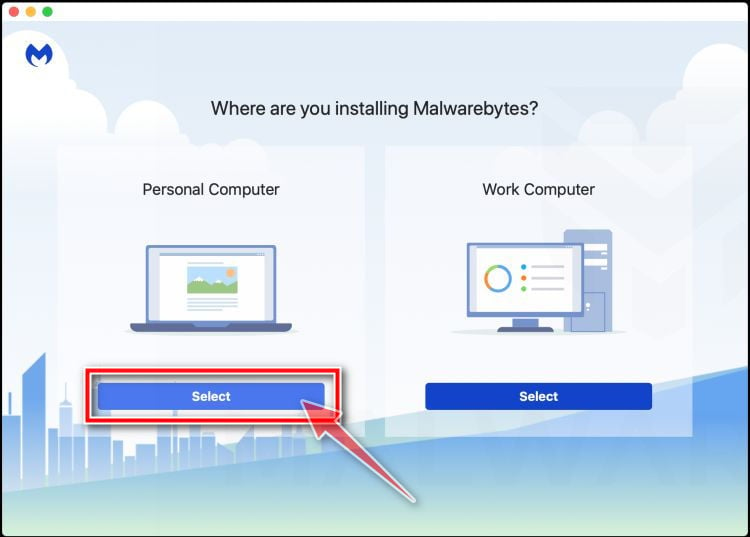
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.
Start the Scan
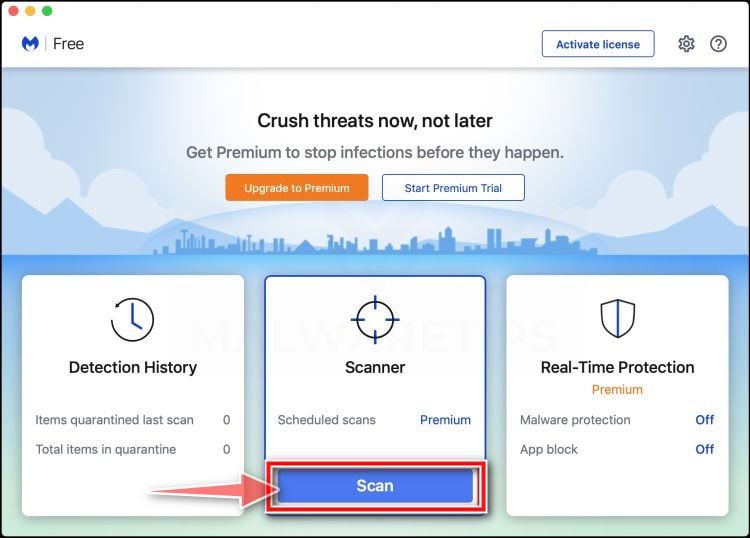
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.
Wait for the Scan to Finish
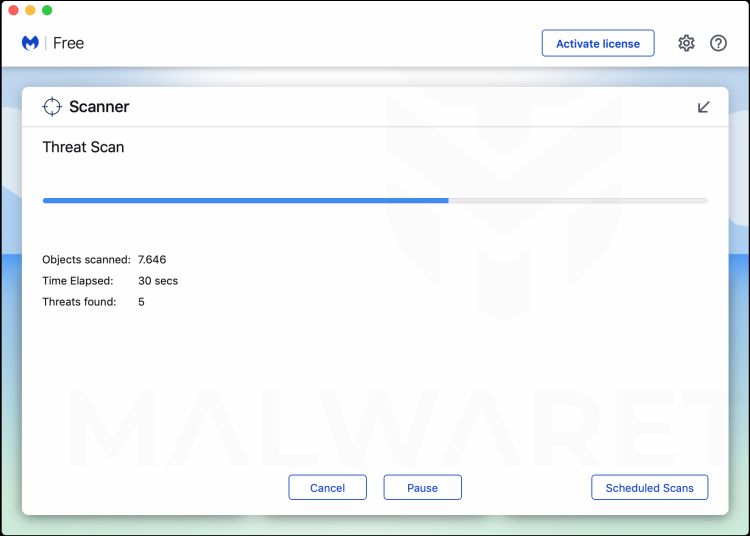
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.
Quarantine the Detected Threats
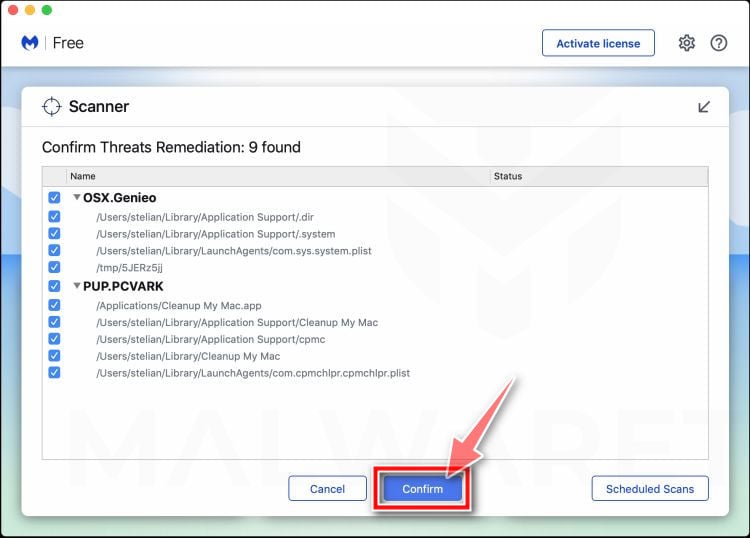
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.
Restart Your Mac
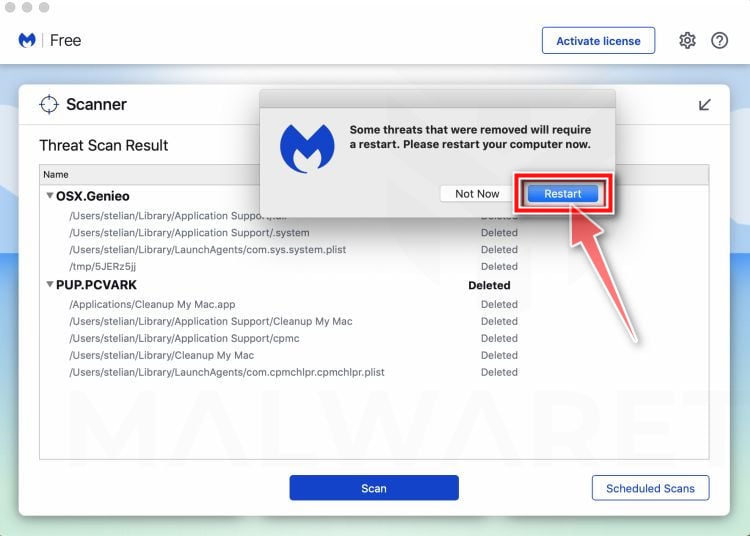
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.
Once the scan is done, remove every threat it detected. Your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If your current antivirus allowed a malicious program on your computer, you might want to consider purchasing the full-featured version of Malwarebytes Anti-Malware to protect against these types of threats in the future. If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
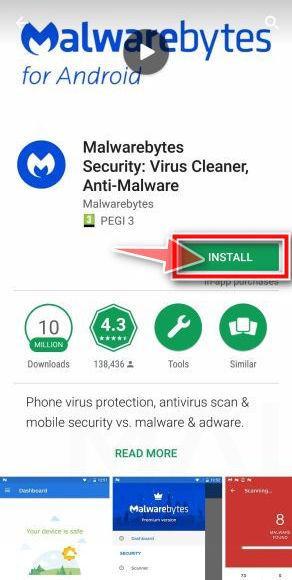
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.
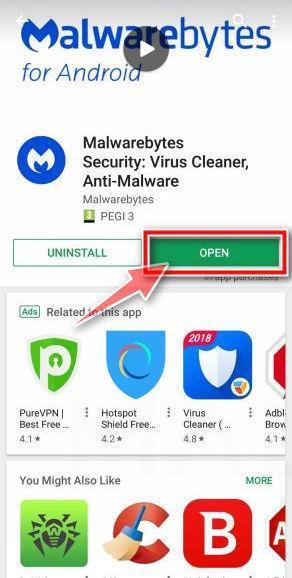
When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.
Follow the on-screen prompts to complete the setup process
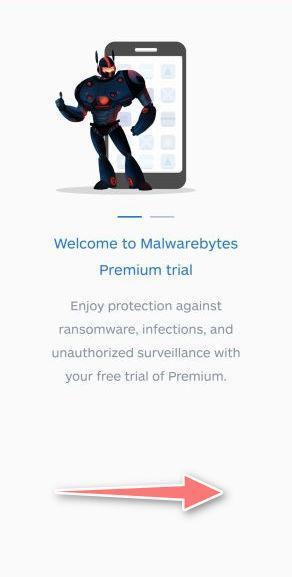
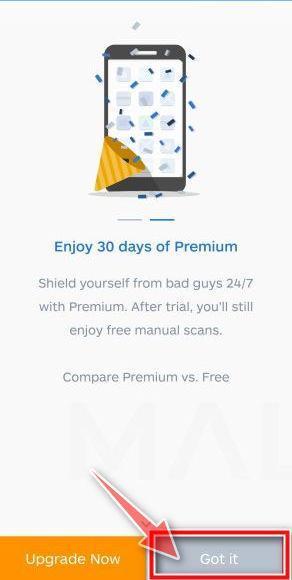
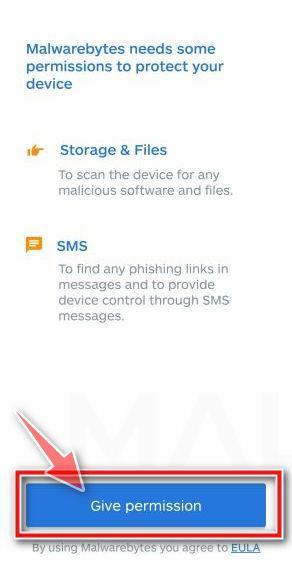
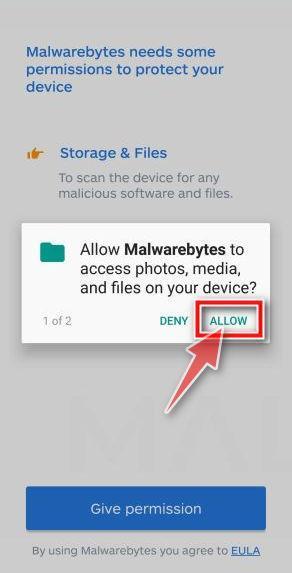
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options. This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue. Tap on “Got it” to proceed to the next step. Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue. Tap on “Allow” to permit Malwarebytes to access the files on your phone.
Update database and run a scan with Malwarebytes for Android
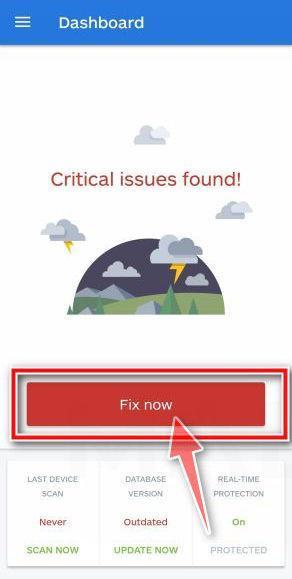
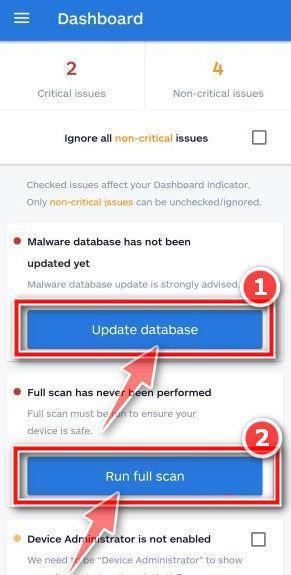
You will now be prompted to update the Malwarebytes database and run a full system scan.
Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.
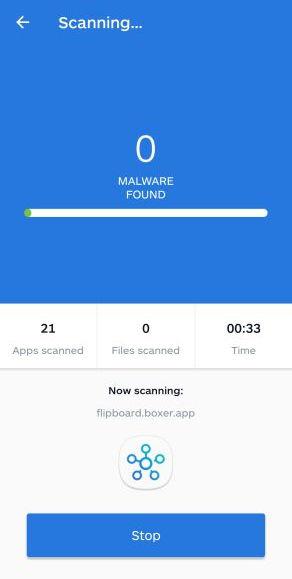
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.
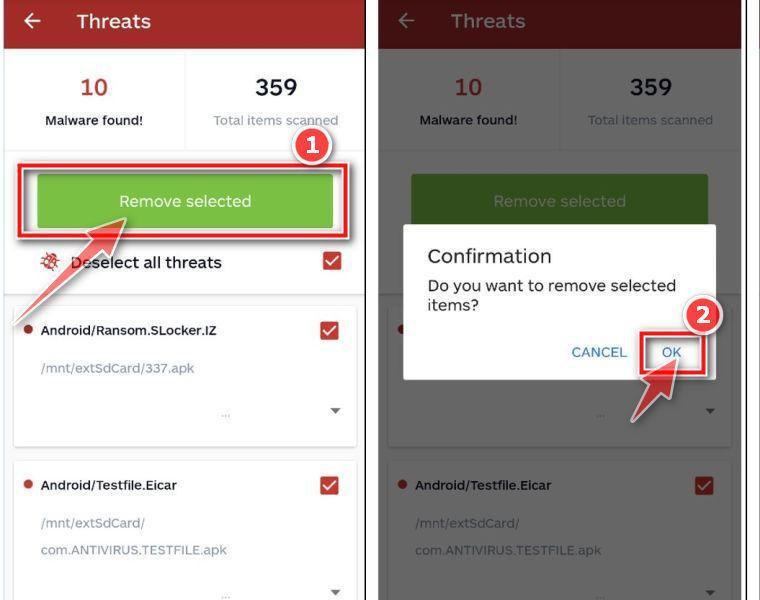
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
After the scan, tap Remove Selected to delete all detected threats. Your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If your current antivirus allowed a malicious app on your phone, you may want to consider purchasing the full-featured version of Malwarebytes to protect against these types of threats in the future. If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
Make the official route for checking quota, delivery, security, and account status easy to find through bookmarks and internal documentation.
Mail administrators should monitor new forwarding, suspicious rules, unusual OAuth grants, impossible travel, and sign-ins from unmanaged devices.
Use provider-specific anti-phishing controls and require multi-factor authentication. Prefer methods that verify the domain rather than relying on one-time codes.
Practice with realistic administrative messages, including quiet technical alerts. Employees should learn to verify through the account instead of the email.
Prompt reporting matters more than blame. A fast report can protect contacts before the stolen mailbox sends another convincing warning.
Held Messages, Quota Problems, and Delivery Failures Are Different
A full mailbox can reject new deliveries, but the authentic account should display measurable storage usage and documented quota limits.
Spam filtering can quarantine individual messages. Users normally review those items inside a junk or quarantine area reached through the verified service.
A sender may receive a bounce when an address fails. That delivery report goes to the sender and includes technical response codes.
Provider outages can delay mail across many accounts. Status pages and administrator notices usually describe the scope, start time, and recovery progress.
Mailbox rules can move messages unexpectedly without stopping delivery. Check filters, sorting, focused inbox settings, forwarding, and blocked-sender lists.
None of these conditions requires entering a password on a website introduced by an unsolicited email.
Ask the administrator which condition actually occurred and which log proves it. A label such as “held” is not a diagnosis by itself.
If a test message arrives normally, preserve that result. It directly contradicts broad claims that all incoming delivery remains suspended.
Technical precision protects users from both phishing and unnecessary account changes made in response to an invented problem.
Keep a screenshot of normal storage and delivery status when reporting. It helps support teams compare the fraudulent claim with actual account conditions.
For company domains, message tracking can confirm whether named senders attempted delivery and whether the server accepted, rejected, or quarantined their mail.
This verification produces actionable facts without exposing a password, visiting the suspicious destination, or trusting the attacker’s artificial deadline.
Frequently Asked Questions
Are my incoming messages really being held?
The email provides no reliable evidence. Check the authentic mailbox, provider status, and administrator tools independently before accepting that claim.
Why is “withheld” spelled incorrectly?
The misspelling is a useful warning, but perfect grammar would not make the message safe. Sender, domain, and account evidence matter more.
Does a prefilled email address prove the page knows me?
No. The phishing link can carry the recipient’s address and insert it automatically into the counterfeit form.
Can opening the message alone steal my password?
Normally no. The main credential risk begins after visiting the linked form and submitting information or approving authentication.
Will changing the password remove an attacker?
Not always. Revoke sessions and inspect forwarding, rules, applications, delegates, recovery details, and app passwords for persistence.
Should I contact people who received messages from my account?
Yes. Warn them through a trusted channel, describe the fraudulent subject, and tell them not to open links or attachments.
The Bottom Line
The Incoming Mails Witheld scam invents a 24-hour delivery crisis and places a familiar-looking password form behind the promised restoration button.
Check mail status inside the real account. If credentials were submitted, secure sessions, rules, applications, recovery settings, and affected contacts without delay.
10 Rules to Avoid Online Scams
Here are 10 practical safety rules to help you avoid malware, online shopping scams, crypto scams, and other online fraud. Each tip includes a quick “if you already got hit” action.
Stop and verify before you click, log in, download, or pay.
Most scams win by creating urgency. Verify using a trusted method: type the website address yourself, use the official app, or call a known number (not the one in the message).
If you already clicked: close the page, do not enter passwords, and run a malware scan.
Keep your operating system, browser, and apps updated.
Updates patch security holes used by malware and malicious ads. Turn on automatic updates where possible.
If you saw a scary “update now” pop-up: close it and update only through your device settings or the official app store.
Use layered protection: antivirus plus an ad blocker.
Antivirus helps block malware. An ad blocker reduces scam redirects, phishing pages, and malvertising.
If your browser is acting weird: remove unknown extensions, reset the browser, then run a full scan.
Install apps, software, and extensions only from official sources.
Avoid cracked software, “keygens,” and random downloads. During installs, choose Custom/Advanced and decline bundled offers you do not recognize.
If you already installed something suspicious: uninstall it, restart, and scan again.
Treat links and attachments as untrusted by default.
Phishing often impersonates delivery services, banks, and popular brands. If it is unexpected, do not open attachments or log in through the message.
If you entered credentials: change the password immediately and enable 2FA.
Shop safely: research the store, then pay with protection.
Be cautious with brand-new stores, “closing sale” stories, and prices that make no sense. Prefer credit cards or PayPal for dispute options. Avoid wire transfers, gift cards, and crypto payments.
If you already paid: contact your card issuer or PayPal quickly to dispute the transaction.
Crypto rule: never pay a “fee” to withdraw or recover money.
Common patterns include fake profits, then “tax,” “gas,” or “verification” fees. Another is a “recovery agent” who demands upfront crypto.
If you already sent crypto: stop paying, save evidence (wallet addresses, TXIDs, chats), and report the scam to the platform used.
Secure your accounts with unique passwords and 2FA (start with email).
Use a password manager and unique passwords for every account. Enable 2FA using an authenticator app when possible.
If you suspect an account takeover: change passwords, sign out of all devices, and review recent logins and recovery settings.
Back up important files and keep one backup offline.
Backups protect you from ransomware and device failure. Keep at least one backup on an external drive that is not always connected.
If you suspect infection: do not connect backup drives until the system is clean.
If you think you are a victim: stop losses, document evidence, and escalate fast.
Move quickly. Speed matters for disputes, account recovery, and limiting damage.
Stop payments and contact: do not send more money or respond to the scammer.
Call your bank or card issuer: block transactions, replace the card if needed, and start a dispute or chargeback.
Secure your email first: change the email password, enable 2FA, and remove unfamiliar recovery options.
Secure other accounts: change passwords, enable 2FA, and log out of all sessions.
Scan your device: remove suspicious apps or extensions, then run a full malware scan.
Save evidence: screenshots, emails, order pages, tracking pages, wallet addresses, TXIDs, and chat logs.
Report it: to the payment provider, marketplace, social platform, exchange, or wallet service involved.
These rules are intentionally simple. Most online losses happen when decisions are rushed. Slow down, verify independently, and use payment methods and account controls that give you recourse.
Hello! I'm Lapain Epuran, your go-to source for detailed and honest product reviews. From tech gadgets to miracle cures, I provide insights to help you make informed choices. Join me as we discover what's truly worth your time and money.