

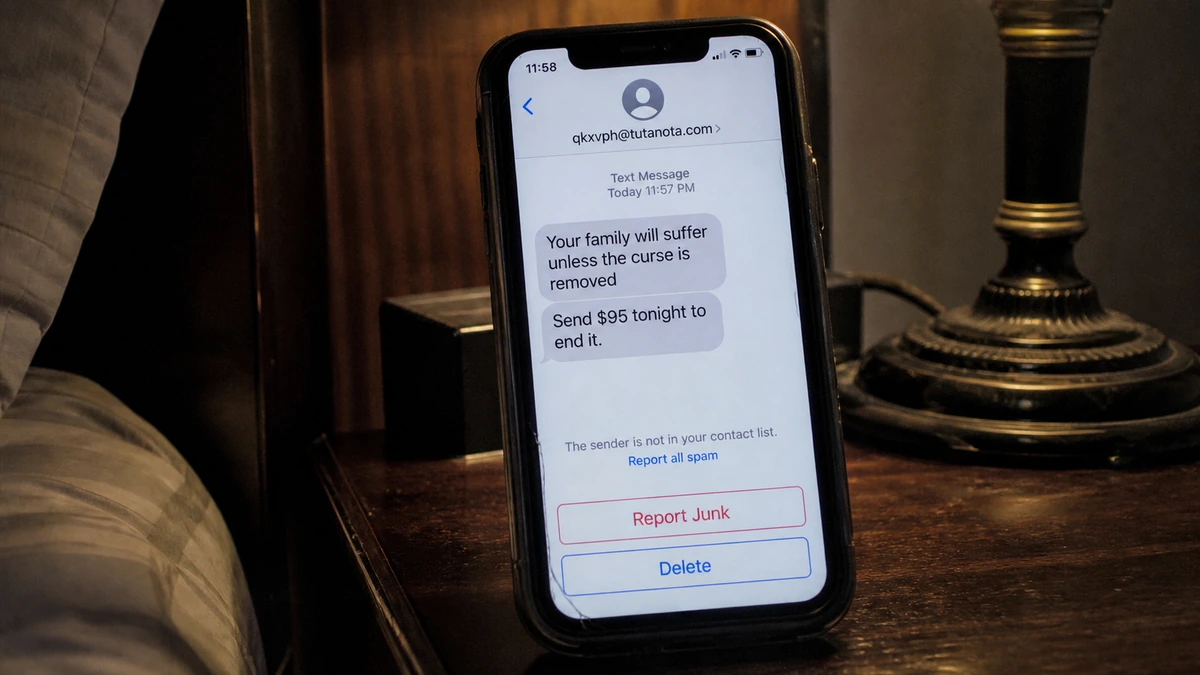
The text does not pretend to be your bank or a delivery company. It claims a stranger has placed a curse on you and can make your family suffer.
Then the message offers a way out: send $95. The supernatural language is dramatic, but the transaction underneath is ordinary extortion.
Overview
The sender invents a danger that cannot be inspected
The message claims that a witch, ancestor, or spiritual force has placed a curse, bondage, illness, or bad luck on the recipient.
Because the threat has no account page, reference number, or objective test, the sender tries to make fear substitute for evidence.
Any unlucky event can be pulled into the story after the fact. A headache, argument, broken appliance, or difficult week suddenly looks like confirmation.
The person making the threat also sells the cure
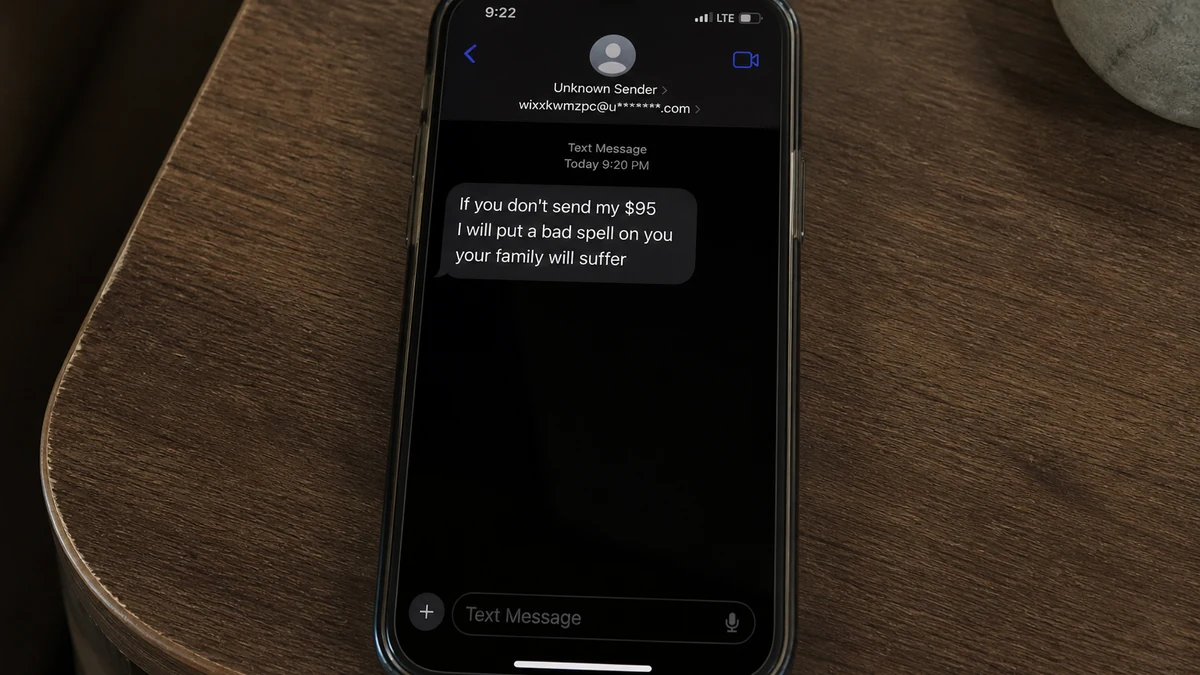
In the case examined here, the sender demanded $95 and implied that refusal would expose the recipient and family to serious harm.
There was no verifiable service. The same stranger created the emergency, set the deadline, described the consequences, and named the price of relief.
A manageable amount can feel worth paying for peace of mind. That is exactly why the first demand is often smaller than the later ones.
Fear and uncertainty do the real work
The sender demonstrated no supernatural power or access to the family. They had a reachable number, a frightening script, and a payment request.
Broad references to family, illness, accidents, and bad luck fit nearly everyone. The recipient supplies the personal connection from ordinary life.
Warning signs include:
- An unexpected curse or spiritual threat from a stranger.
- Claims that cannot be checked independently.
- Family harm used to raise the emotional stakes.
- A payment presented as the only protection.
- Secrecy described as necessary for the remedy.
- Gift cards, payment apps, crypto, or irreversible transfers.
- New dangers appearing after the first payment.
- Follow-up offers to remove, trace, or reverse the curse.
How the Fake Witch Curse Text Scam Works
Step 1: The operator finds a reachable number
The number may come from a breach, public profile, lead list, marketing database, or automated dialing. Receiving the text does not prove someone investigated you.
If it arrives from an email address, a carrier’s email-to-text gateway may have delivered it. That unusual sender format is technical routing, not evidence of special access.
Step 2: An invisible threat removes normal verification
A stolen card can be frozen and a parcel can be tracked. A claimed curse has no measurable state, so the sender keeps the victim inside a story only the sender can interpret.
The language may borrow from religion, folk beliefs, psychic readings, black magic, or ancestors. The commercial structure stays the same: accept the threat, then buy relief.
Step 3: Loved ones make the risk feel unbearable
Many people will tolerate uncertainty for themselves but not for a child, parent, or partner. Threatening family members makes delay feel irresponsible.
“Your family will suffer” is deliberately broad. The recipient can connect it to any vulnerable relative or recent event without the sender knowing either.
Step 4: A modest price promises immediate calm
The first $95 demand may seem cheaper than spending days afraid. In reality, it tests whether the number belongs to someone responsive and willing to pay.
Once payment succeeds, another ritual, ingredient, fee, or hidden danger can appear. The first amount begins the cycle rather than ending it.
Step 5: A reply gives the sender personal material
Even “leave me alone” confirms that a person read the threat. A longer reply may reveal which relative, belief, illness, or fear affected you.
The operator can repeat those details later as supposed proof of insight. They learned them from the conversation, not from supernatural knowledge.
Step 6: Payment moves to a difficult recovery route
The sender may request a payment app, gift card, cryptocurrency, wire, or “friends and family” transfer. Speed and limited dispute options are the attraction.
Secrecy often appears here. The victim is told that discussing the ritual will make it fail, when the real goal is to prevent outside advice.
Step 7: The first success produces another threat
Payment does not buy safety because there was no verified danger to remove. It only proves that the script produced money.
The same sender may demand more, or a new “psychic,” investigator, or recovery specialist may offer help for another upfront fee.
Why a Mass Message Can Feel Deeply Personal
Threat scripts use universal anxieties. Almost everyone knows a vulnerable relative, remembers a recent setback, or worries about an uncertain future.
Once the message arrives, the mind searches for matches. Coincidence becomes evidence because the sender has already supplied a frightening explanation.
Public data can make the approach more specific. Names, relatives, birthdays, memorial posts, locations, and photographs are widely exposed through social networks and data brokers.
Repeating a public fact still does not demonstrate an ability to cause harm. It demonstrates access to information that many ordinary databases contain.
The best question is not whether the message feels eerie. Ask what can be independently verified. Here, the only concrete act was a demand to send $95 to the person making the threat.
Talking to someone trusted interrupts the pattern. Saying the script aloud often reveals that the seller invented both the problem and the paid solution.
When the Message Needs a Police Report
Most curse-payment texts are psychological extortion. Still, do not dismiss a message containing a specific address, schedule, weapon, planned act, or evidence of recent surveillance.
Preserve the original message and screenshots showing the sender, timestamp, threat, and payment instructions. Metadata may matter beyond the visible words.
Do not confront the sender or arrange a meeting. If the threat appears immediate or describes a credible physical act, contact local emergency services.
The FBI’s Threat Intimidation Guide advises preserving electronic threats and recording details rather than destroying the evidence.
A broad supernatural warning tied only to payment can be reported as spam and fraud. A specific real-world threat deserves local law-enforcement review.
These two responses are compatible. You can reject the curse story while still treating concrete stalking or violence details seriously.
How to Respond Without Feeding the Extortion
Do not pay for reassurance and do not ask the sender to prove the curse. Both actions keep you inside a conversation the operator controls.
Take screenshots before blocking. Save the full sender address or number, timestamps, payment destination, and any platform profile.
Use the phone’s Report Junk feature and forward suspicious texts to 7726 if your carrier supports it. The FTC’s spam-text guidance explains additional reporting options.
Tell a trusted person what happened. Fear becomes stronger in isolation, while someone outside the message can see the transaction clearly.
If anxiety persists, speak with a trusted community leader or licensed mental-health professional who will not demand payment to neutralize the message.
Avoid “curse removal” services found through ads or private replies. Searches for relief can lead directly to another person selling the same unsupported cure.
Why Paying Usually Creates More Fear
A successful payment tells the sender that uncertainty has value. They can restore that uncertainty with one new message.
The next claim may involve a stronger curse, another relative, special materials, or a deadline. There is no objective endpoint because the seller controls the diagnosis.
Photographs of candles, certificates, recordings, and ritual receipts do not make the threat verifiable. They are more content built around the same unsupported story.
A payment labeled “gift” may reduce normal purchase protections. The label does not make the demand voluntary or safe.
If gift cards were used, contact the issuer immediately and keep the receipt and card details. Do not send another image of the PIN to anyone offering help.
Recovery pitches are especially dangerous. Someone promising to trace the witch, reverse the payment, or guarantee family protection is targeting the same fear again.
What Email-to-Text Delivery Reveals
An email address in the sender field may mean a carrier gateway converted email into SMS. It does not establish the sender’s location or identity.
Preserve the exact address, spelling, and domain for abuse reports. Do not send a test email, because that confirms another route to reach you.
If messages arrive from changing addresses, use carrier-level spam controls and keep examples. The pattern may matter more than any single disposable sender.
Review whether your phone number and family details are public. Tightening privacy cannot erase old leaks, but it can reduce information available for later intimidation.
Do not change your number solely because of one text. Block, report, and assess whether the harassment continues before disrupting a legitimate long-held contact.
If You Already Replied
A plain reply does not give the sender supernatural power or automatic access to your phone. It does confirm that the number reaches someone who read the message.
Stop answering questions, even if they seem designed to prove the sender is wrong. Every correction can reveal a relative, location, belief, health concern, or recent event.
Review exactly what you disclosed. Write down names, addresses, photographs, payment accounts, religious details, and anything the sender could repeat in a more personal threat.
Warn family members if their names or numbers were mentioned. The operator may contact them separately and claim that you already paid or requested help.
Change passwords only when account information was shared, a link was used, or unfamiliar activity appears. The curse text alone is not evidence that the device was hacked.
Keep new messages without responding. Repeated contact from different addresses can help a carrier or platform recognize the pattern and may support a harassment report.
If the sender publishes private material or threatens a specific action, preserve the evidence and seek local legal or police guidance rather than negotiating.
Company, Address, and Fulfillment Checks
No identifiable company was disclosed
The message named no registered business, licensed service, written terms, or accountable operator.
Assigning a price to a threat does not create a legitimate service.
No verifiable business address was provided
There was no office or service location that could be checked. The only route was an unsolicited electronic message.
That removes the ordinary accountability expected before buying any service.
The sender identity could not be authenticated
An email address inside a text thread is not proof of a real person. Such accounts can be created quickly and abandoned.
The recipient had no independent history or professional record connecting the sender to the claimed role.
There was no measurable fulfillment
The product was relief from a danger the seller alone claimed existed. There was no starting condition, deliverable, completion test, or refund standard.
That makes the promise impossible to verify and easy to extend indefinitely.
What to Do if You Have Fallen Victim to This Scam
- Stop communicating and paying. Another demand means the first payment encouraged the scheme.
- Preserve the threat. Save screenshots, original messages, addresses, numbers, usernames, timestamps, and payment instructions.
- Contact the payment provider. Ask whether the extortion payment can be stopped, reversed, or disputed.
- Protect the payment account. Change passwords, enable multi-factor authentication, and remove unknown sessions.
- Report the sender. Use platform controls, carrier reporting, the FTC, and appropriate local channels.
- Escalate specific threats. Contact police when the sender names a location, weapon, plan, or imminent act.
- Review privacy exposure. Remove unnecessary public family, address, workplace, and location details.
- Run a full Malwarebytes scan. Do this if you opened a link, attachment, or installed anything.
- Use AdGuard after cleanup. It can reduce malicious pages but cannot stop ordinary SMS messages.
- Tell someone you trust. Do not let secrecy keep the threat emotionally powerful.
- Keep gift-card evidence. Contact the issuer and do not share card images with recovery strangers.
- Reject recovery offers. Nobody can guarantee protection or payment recovery for another upfront fee.
Frequently Asked Questions
Can a text message place a curse on me?
The message provides no verifiable mechanism or evidence of supernatural harm. It does show a conventional effort to create fear and collect money.
Why did the sender ask for only $95?
A modest first demand feels easier to pay and tests whether the recipient responds. Larger fees may follow.
Should I reply to show I am not afraid?
No. A reply validates the number and can reveal which claims affected you. Preserve, report, and block instead.
How did the sender get my number?
Numbers circulate through breaches, public profiles, lead lists, apps, and automated dialing. Possession does not prove surveillance.
Should I report a supernatural threat to police?
Report generic payment threats as fraud and spam. Preserve and report any specific physical threat, stalking detail, or imminent plan locally.
What if I paid and the sender wants more?
Do not pay again. Contact the payment provider, secure the account, document every demand, and report the extortion.
The Bottom Line
The fake witch curse text turns an unverifiable supernatural claim into a conventional $95 payment demand. Surprise and family-focused fear make the transaction feel urgent.
Preserve the evidence, do not engage, block and report the sender, and take specific real-world threats seriously. You do not need to buy protection from the stranger who invented the danger.








