


A short email promises a large payment and asks for a few personal details. The bank name makes it feel more substantial than ordinary junk mail.
Why would a bank tell you its branches cannot help? Before using the sender’s special process, take a closer look.
Overview
The offer is an unsolicited $850,000 fund release
The JP Morgan Chase Fund Release email scam impersonates the banking institution to solicit private information under the pretext of remitting a beneficiary payment.
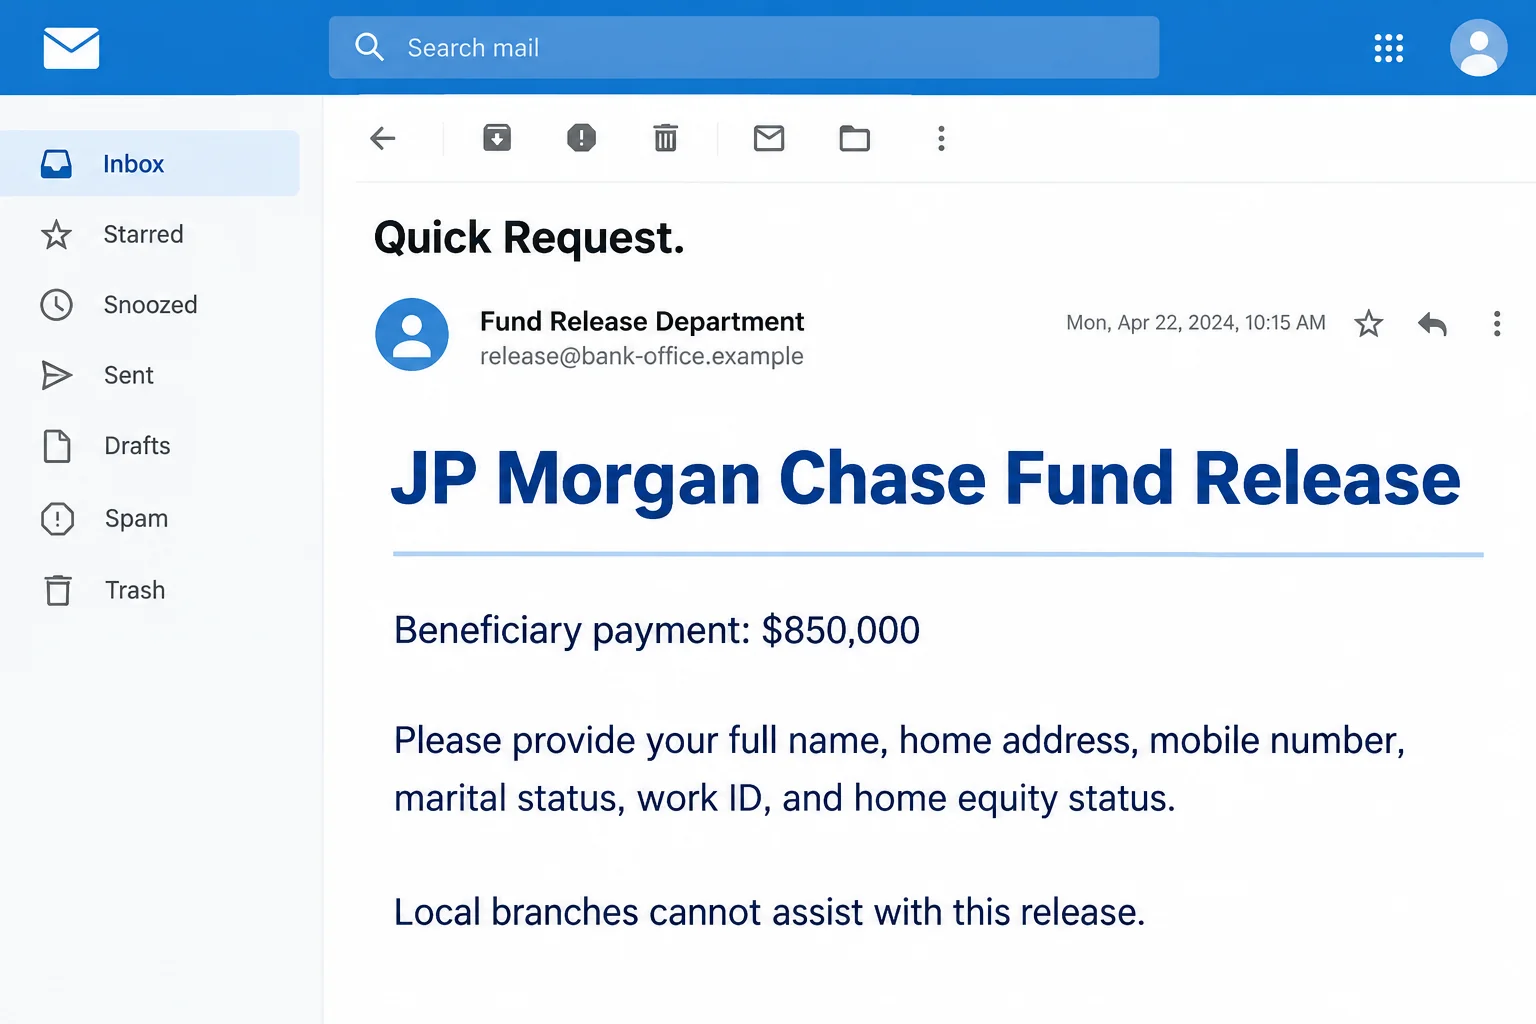
A documented version uses the subject “Quick Request.” It says $850,000 is available and introduces identification and a supposed transfer-security code as conditions.
The institution’s name is being misused. This is not a finding that JPMorgan Chase runs the offer or that the message establishes a genuine bank account.
The request extends well beyond an ordinary reply
The letter seeks a bundle of identifying and financial-context information, including the recipient’s name, residential address, mobile number, marital status, work ID, and home-equity status.
Its claimed bank process also steers the recipient away from local branches. That instruction attempts to keep verification inside the sender’s chosen channel.
- An unexpected windfall is presented as an existing beneficiary entitlement.
- A security-sounding code lends the process an administrative appearance.
- Personal information is requested before the payment can supposedly proceed.
- Independent branch confirmation is discouraged by the explanation in the letter.
A claimed procedure is not proof that funds exist
The documented request establishes information harvesting through bank impersonation. It does not establish a real balance, a completed theft, or a particular fee charged to recipients.
Our illustration uses a fictional email address and sample interface date. It depicts the request without claiming to reproduce an authenticated bank message.
We did not contact the sender or test a payment. Later fee demands, credential requests, and malicious files are risks to watch for, not verified stages here.
The Detail That Deserves More Attention Than the Payment
Why tell you that your local branch cannot help?
A genuine financial institution can have specialized departments and limits on branch services. Specialization alone is not evidence of fraud.
But this email uses that explanation before authenticating either the sender or the underlying payment. It asks you to accept isolation as part of the procedure.
If you ask the real bank and it finds no such matter, the letter has already supplied an excuse: those employees supposedly would not know.
That is a circular verification trap. The person making the claim also defines which independent answers you should disregard.
Do not accept a stranger’s restriction on contacting your own bank. Use a known app, an established website, or the number printed on your card.
“Beneficiary” sounds like a status you already hold
The word suggests that a decision has been made and the money belongs to you. It encourages completion of paperwork instead of scrutiny of the supposed entitlement.
Yet a legitimate payment needs an underlying reason. A settlement, inheritance, contractual payment, or other transfer should connect to something verifiable outside the message.
Without that link, an impressive bank name does not fill the gap. Nor does a quoted amount show that anyone has deposited funds for you.
If the letter happens to resemble a real matter in your life, verify that matter with the people already handling it. Do not merge the two stories.
How the JP Morgan Chase Fund Release Scam Works
Step 1: An administrative subject invites a low-friction reply
“Quick Request” sounds like ordinary office correspondence rather than a dramatic prize promotion. It can make opening and answering the message feel like a small task.
The body then introduces the large payment. That contrast moves the reader from routine inbox processing into a potentially life-changing claim before much skepticism has developed.
Read an unsolicited financial request as a fresh claim, regardless of its subject. Familiar business phrasing does not establish a prior relationship.
Do not reply with a phone number simply to learn more. That gives the sender another route to continue the pitch and make it more personal.
Step 2: The bank identity makes the claim look institution-backed
The message borrows JPMorgan Chase’s name and presents the release as a bank-managed process. The authority comes from branding and assertions, not independent confirmation.
A copied address or formal signature can add apparent substance. Neither proves where a message originated or who controls the account receiving your reply.
The reported letter directs contact to an address outside the bank’s obvious brand domain. That inconsistency is a warning, but a convincing sender display would not be enough either.
Email identities can be imitated or compromised. Verify the request through a route you chose independently rather than treating one visible field as a complete authenticity test.
Step 3: A “security transfer code” creates a sense of a prepared file
A code suggests that the payment has already passed through a formal workflow. The reader may assume it represents authorization known only to the bank.
In reality, text supplied by the sender cannot authenticate that same sender. A reference number, bank identifier, or other copied string does not prove a personal allocation exists.
Do not enter such a code into a website introduced by the email to “verify” the balance. The website and code could be parts of one fabricated process.
The genuine bank can explain what a real reference means through its own channels. You do not need to disclose personal documents to test a stranger’s code.
Step 4: The beneficiary form collects an unusually useful profile
The requested details combine contact information with employment and household context. That bundle can support personalized fraud even without an initial request for a banking password.
A mobile number provides a route for follow-up calls. A work ID can expose employment details. Home-equity information may reveal something about perceived financial circumstances.
Those are potential uses, not proof of how this operator processes every response. The immediate fact is that the request seeks information before its authority is established.
Do not answer only the fields that feel harmless. Partial participation can keep the conversation alive and allow later questions to be tailored around what you supplied.
Step 5: Independent verification is replaced by a special-access story
The letter says ordinary branches cannot release the funds or provide information. It presents restricted handling as a security feature rather than a reason for concern.
This moves the recipient toward the supposed representative as the only useful contact. A familiar institution becomes a backdrop for an unfamiliar person’s instructions.
That isolation can become more persuasive after several replies. The contact may know your address, occupation, or document details because you supplied them earlier.
Recognition is not authentication. A caller repeating your submitted information has demonstrated access to the conversation, not authority to act for the bank.
Step 6: Additional conditions may follow the initial disclosure
Advance-fee schemes can introduce costs before a promised payout. Other impersonation exchanges ask for bank access, verification codes, or files after the recipient begins cooperating.
The opening sample does not establish which, if any, of those follow-ups reached a particular person. Do not confuse a plausible risk with an observed event.
If a later demand arrives, evaluate it independently. Money already promised and time already spent are not reasons to accept another unverified condition.
Stop rather than paying to close, cancel, or release the supposed file. A scammer may invent an exit fee as readily as an entry requirement.
What a Useful Bank Verification Actually Looks Like
Start with the relationship, not the letterhead
Ask what genuine transaction could produce the claimed entitlement. Check your own records and speak to your established adviser if an estate or legal matter is involved.
Then contact the bank independently about the suspicious communication. Existing customers can use the number on their card or the authentic app.
Chase’s security guidance describes bank impersonation and advises customers to contact the bank if personal or account information was given to scammers.
Do not let the email’s branch restriction overrule that advice. You are checking whether the claimed process exists, not asking a stranger for permission to verify it.
Keep a payment claim separate from an account login
A purported incoming transfer should not become a reason to share your password or one-time code with an unknown representative.
If someone says they need a code to confirm a deposit, read the actual message that generated the code. It may authorize an unrelated action.
Never install remote-access software so a supposed banker can help collect a windfall. Remote control can expose information unrelated to the original email.
A balance shown on a newly introduced portal is not equivalent to money in your established bank account. Check funds through the bank you independently verified.
What to Do if You Fell Victim to This Scam
A reply does not obligate you to finish the process. Take the steps that match the information or money actually exposed.
Stop dealing with the supposed release representative.
Save the email, attachments already received, reply addresses, and any call or payment records. Do not send a final form or cancellation charge.
Report the message as phishing after preserving evidence. Warn anyone you involved in the proposed payment, especially if their information was also submitted.
Tell the real bank about relevant disclosure.
Use a trusted contact route, not the email’s representative. Explain whether you provided account details, identity documents, login credentials, codes, or an actual payment.
Ask about safeguards suited to that exposure. A general statement that you “answered an email” can hide details the bank needs to assess the incident.
Secure any account credentials you entered.
Replace the exposed password through the real service and change reused passwords elsewhere. Review active sessions, recovery contacts, and available multifactor authentication settings.
If access has already changed, use the genuine provider’s account-recovery process. Do not pay the release representative to restore an account.
Respond to identification or employment-document exposure.
Contact the document issuer for advice. If a work ID was shared, notify your employer’s appropriate security or personnel contact.
Use IdentityTheft.gov for a U.S. identity-recovery plan where relevant. Monitor for actual unauthorized applications or account changes rather than assuming every possible harm occurred.
Request help with any payment immediately.
Contact the service that handled it and report the scam. Keep the amount, recipient, date, method, and transaction reference available.
Possible cancellation or recovery depends on the payment. Do not send another transfer to someone who claims they can guarantee a refund.
Check the device if the exchange involved software.
If you ran a file, installed a program, or allowed remote access, stop further sensitive activity on the device and assess it.
A Malwarebytes scan can help investigate malicious software. It cannot cancel a bank transfer, retract an ID copy, or replace contacting an affected account provider.
Report and prepare for more targeted contact.
Submit the incident to your local fraud or cybercrime reporting service. Preserve original records privately and avoid publishing personal documents with a warning.
AdGuard may reduce some malicious advertising, but follow-up email and calls still require independent verification. Familiar details in a new pitch may come from your earlier reply.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is JPMorgan Chase responsible for this offer?
No connection to the real institution is established by the scam email. The bank’s name is used to lend credibility to the sender’s information request.
Do not blame a genuine bank for an impersonator’s letter. Contact it through established channels if its identity or your account information was involved.
Does the $850,000 amount prove I am a beneficiary?
No. A figure in an unsolicited email does not establish an entitlement or show that funds exist. Verify the underlying transaction outside the message.
Do not send documents merely to learn where the money supposedly came from. That reverses the proper order of verification.
What is suspicious about the local-branch instruction?
It attempts to disqualify an independent source before you consult it. The sender wants its own special process to remain the only accepted explanation.
Specialized bank departments do exist, but that does not authenticate this unsolicited payment or justify avoiding the genuine bank’s contact channels.
Can a transfer-security code authenticate the email?
No. A code supplied by an unknown sender is part of the claim, not independent confirmation. Copied banking references cannot prove a payment belongs to you.
Ask the authentic institution about any real matter through its established process. Do not verify a code using a portal provided solely by the email.
What if I only sent my name and phone number?
Expect possible follow-up contact and stop cooperating. Those details alone do not prove account takeover, but they can help another pitch sound more personal.
Escalate appropriately if you also shared credentials, documents, financial information, or codes. The response should follow the actual exposure.
Is malware confirmed in this email?
No specific malware payload is established here. The documented scam concerns a false fund-release process and requests for private information.
A device check is appropriate if the subsequent exchange involved software, executed attachments, or remote access. Receiving the message alone does not prove infection.
The Bottom Line
Do not submit information or payment to the JP Morgan Chase Fund Release sender. Verify any genuine financial matter through the bank and contacts you already know.
If you responded, protect the specific documents, credentials, accounts, or payments involved. A special process that discourages independent checks is not a reason to trust it.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.