

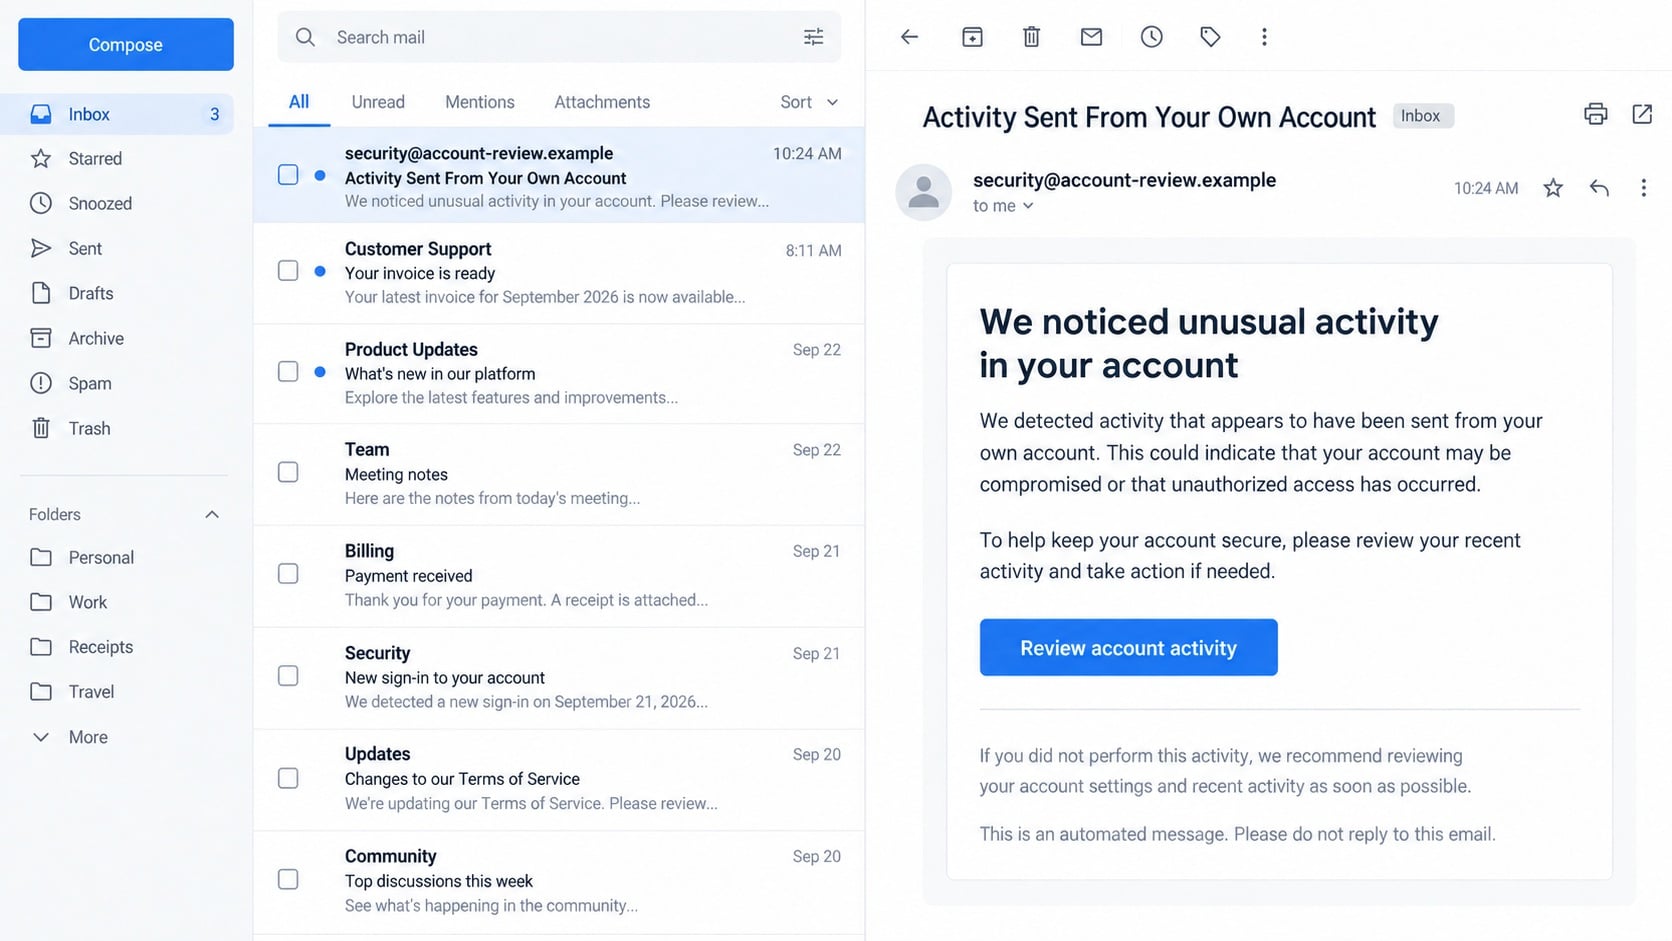
An email says unusual activity came from your own account. It sounds like the sort of warning you would regret ignoring.
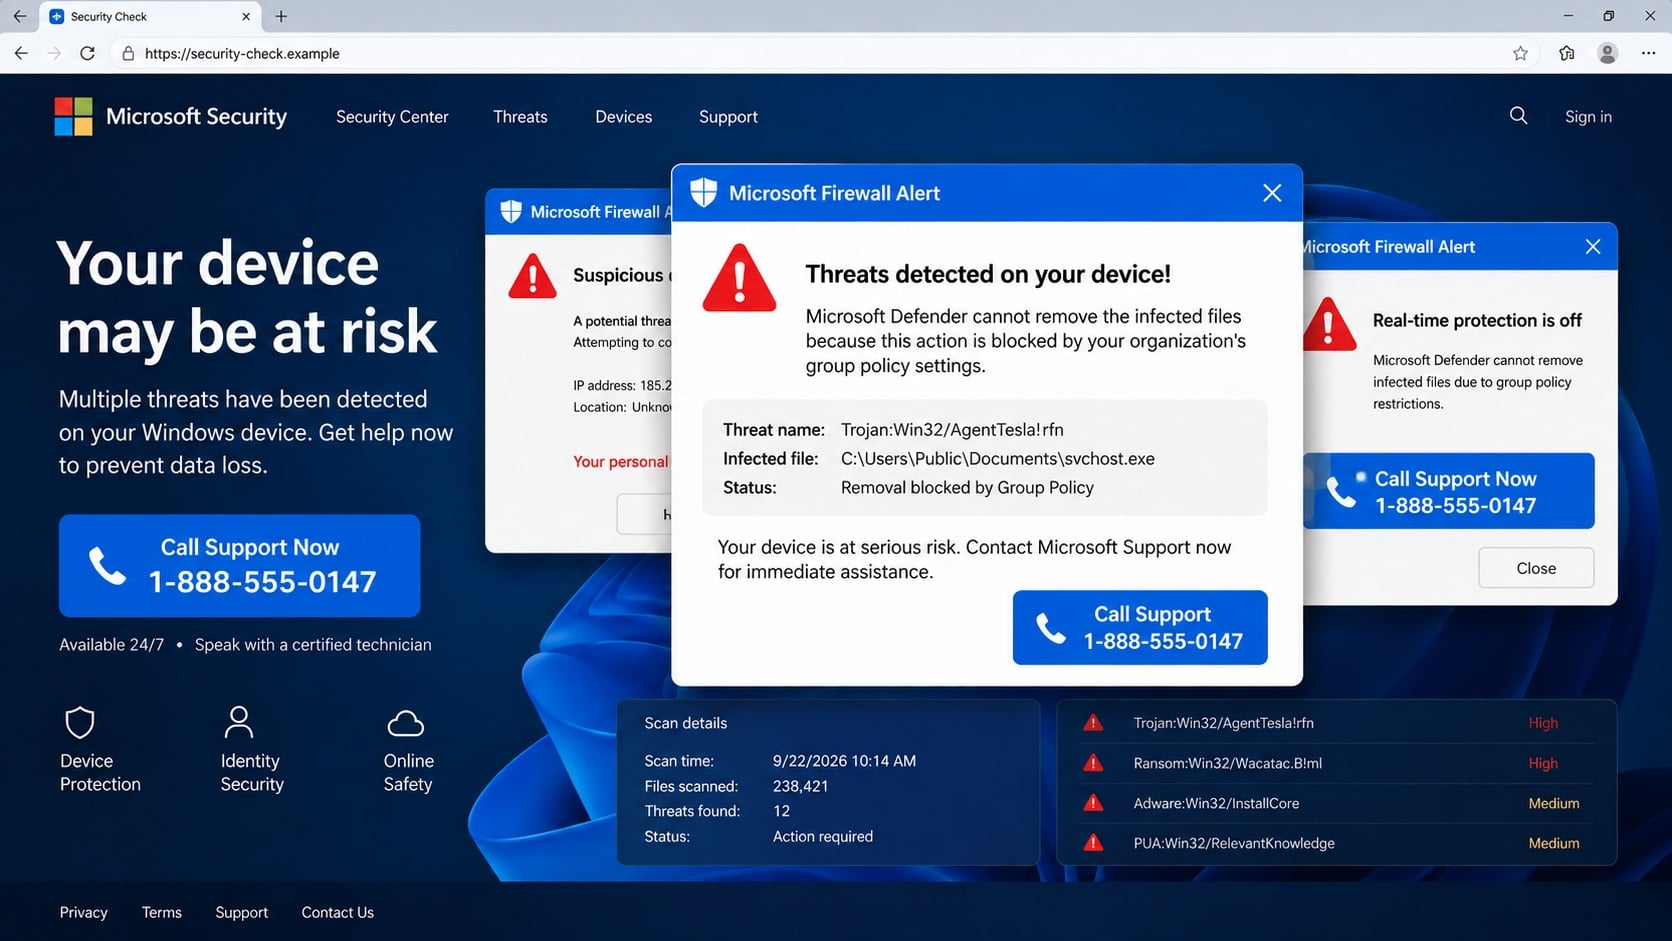
One click later, a Microsoft Firewall Alert fills the browser. The two messages seem connected, but the connection deserves a careful look.
Overview
Two alarms create one false emergency
The observed campaign begins with an email claiming activity was sent from the recipient’s own account. It offers links to review account activity and security settings.
Those links lead to a website that displays a supposed Microsoft Firewall Alert. The page claims Defender found infected files but cannot remove them because of group policy permissions.
That is an unusual leap. A mailbox alert is not proof that a Windows firewall problem exists, and a website cannot inspect Defender’s local findings merely because you opened it.
The page’s immediate objective is a phone call to a number presented as Windows Support. The number belongs to the page’s story, not to a verified Microsoft support channel.
The browser page is not a Windows diagnosis
Warning boxes can be drawn inside a web page with ordinary HTML and JavaScript. They may overlap, play sounds, or resist closing through repeated dialogs.
Those tricks can make a browser tab feel like a locked computer. They do not establish that malware was found, that group policy blocked removal, or that Microsoft contacted you.
Microsoft states that genuine error and warning messages do not contain a support phone number. That single check cuts through much of the page’s visual theater.
The campaign used an Azure-hosted web address. Hosting under a recognizable cloud provider does not make the content a Microsoft security notice.
What the attacker wants next
- A frightened visitor calls the number displayed on the page.
- The caller may be asked to install remote-access software or disclose account details.
- A supposed repair can become a payment request or an opportunity to inspect private files.
- The operator may pressure the caller to remain on the line while the device is controlled.
These are risks of tech-support fraud, not proof that every caller experiences every outcome. What is confirmed here is the deceptive email-to-popup route and the unsolicited support number.
The illustrations in this article are static recreations. They show the message and page design without reproducing a working scam link or phone line.
Why the Email Makes the Popup More Convincing
A random pop-up is easier to dismiss. This one arrives after a message that already primed the reader to think an account has been misused.
The subject suggests activity came from your own address. Someone who knows about address spoofing may still wonder whether the account itself was compromised.
The email then offers a reasonable-sounding task: check recent account activity. That language resembles advice you might receive from a legitimate provider.
The trap lies in letting the email choose where that check happens. A safe investigation starts from the provider’s app or a saved bookmark, not its embedded button.
On the destination page, the story changes from mailbox access to a Windows infection. That abrupt change is a clue, but urgency can blur it.
Many people cannot immediately tell which warnings belong to their browser and which belong to Windows. The page exploits that uncertainty with familiar colors and security vocabulary.
Group policy is a real Windows feature. In this context, the term gives a fake diagnosis a technical explanation for why the page says normal protection cannot help.
No legitimate support procedure begins with an unsolicited email, a browser-generated virus verdict, and a telephone number inside the warning.
How the Microsoft Firewall Alert Scam Works
Step 1: A security email creates the first concern
The message says unusual activity was sent from your own account. It does not provide a trustworthy record of that activity inside the real provider’s account dashboard.
Its links ask the reader to leave the inbox and review a supposed security event. The action sounds defensive, which is why it can succeed without promising a prize.
A sender name or familiar-looking footer cannot verify the message. Email display names and visible text can be chosen by the sender.
Step 2: The link opens a staged firewall page
The destination creates a Windows-like experience inside a browser. Several alerts may appear at once, crowding the screen and making ordinary navigation feel difficult.
One observed version claimed Defender could not remove infected files because of group policy permissions. That sentence is part of the scare script, not a verified scan result.
A web page can read limited information exposed by the browser, but it cannot conduct a full Defender scan or diagnose the machine by displaying a popup.
Step 3: The page supplies its own support line
The warning tells the visitor to call a displayed Windows Support number. This is the conversion point where a static scare page becomes a conversation.
The operator can ask questions, adapt the story, and keep the caller engaged. A phone number is not made official by appearing next to a shield icon.
Microsoft’s guidance is direct: genuine error messages never include a number to call. Use the company’s official support site independently if help is actually needed.
Step 4: The supposed fix can expand the access
A fake technician may ask for remote control so they can show invented problems in system tools. They may also request card details for a repair plan.
Remote access is especially serious because the operator can see files, open accounts, and potentially install software. Do not treat a guided download as harmless because it sounds familiar.
The exact request can vary. Some operations emphasize an unnecessary support fee, while others seek passwords or payment information.
Step 5: Pressure discourages an independent check
The caller may be told not to close the page or restart, supposedly to preserve evidence. That instruction also prevents a simple exit from breaking the illusion.
If you stop and open Windows Security yourself, you can check protection history without relying on the page. An actual alert will exist in the trusted interface.
A legitimate technician will not object to independent verification, especially when you did not request the call.
Email, Domain, Warning, and Support Checks
Check the account inside its real service
Open your email provider through its app, saved bookmark, or manually entered address. Review recent sessions and security notices there.
If the provider shows no matching event, the email’s claim loses credibility. If there is a real event, address it within that account rather than through the message’s link.
Look at the browser address, not the artwork
The observed page used a cloud-hosted address. Cloud infrastructure can serve legitimate software and deceptive pages alike.
A domain ending in a provider’s hosting suffix is still not automatically an official Windows support destination. Branding inside the page cannot override ownership of the address.
Open Windows Security independently
Use the Start menu to open Windows Security, then inspect Virus & threat protection and Protection history. Do not click a button in the alarming tab to get there.
Compare any actual detection with the page’s claim. A browser message that mentions Defender without a corresponding local event is not evidence of an infection.
Find support through a trusted route
If you still need help, visit Microsoft’s support site by typing its address or using a trusted bookmark. Never let a popup provide both the diagnosis and the contact number.
Do not search only the number displayed in the warning. Search results can include copied scam pages and unrelated reports that add confusion.
What to Do if You Have Fallen Victim to This Scam
- If you only saw the page, close it. Try closing the tab, then the browser. If a dialog loop prevents that, use the operating system’s task manager to end the browser and reopen without restoring the tabs.
- If you clicked the email link, check your account separately. Open the real provider’s security page, review unfamiliar sessions, and update the password if the page led you to enter it anywhere suspicious.
- If you spoke to the operator, stop contact. Hang up and do not call back. A forceful warning about impending damage is not a reason to keep an unsolicited support session open.
- If you granted remote access, disconnect the device. Turn off Wi-Fi or unplug the network connection, close the remote-support application, and seek help from a trusted technician or your employer’s IT team.
- Change exposed passwords from a clean device. Start with email, then banking and other accounts that share credentials. Enable multifactor authentication and revoke unknown sessions.
- Check the device for unwanted software. Review recently installed remote-control tools. Run Windows Security and a Malwarebytes scan to look for malware or unwanted programs introduced during the session.
- Call your card issuer if you paid or shared details. Explain that the charge followed a tech-support scam. Ask about card replacement, disputes, and monitoring for further transactions.
- Reduce repeat exposure. Report the deceptive email and page to the provider. AdGuard can help block known malicious ad and phishing destinations, but it is not a substitute for verifying support requests.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
When a Browser Tab Seems to Lock the Computer
A page can request full-screen mode or repeatedly open dialog boxes. That can hide ordinary browser controls and create the impression that Windows itself is blocked.
The browser still has an exit path. Press Escape to leave full screen, then close the tab. If dialogs immediately reappear, end the browser process.
Reopen the browser without restoring the previous session. Restoring all tabs can reload the same page and repeat the warning.
If the page plays a recorded voice or alarm, mute the tab or system audio while you close it. Sound adds urgency, not diagnostic value.
Some people worry that force-closing the browser will damage files. It may lose unsaved form text, but it does not make a fake Defender finding real.
Afterward, inspect Windows Security and your browser’s notification permissions. Remove permission for unfamiliar sites that can send future alerts.
Do not clear every browser setting before preserving the URL if you need to report the page. A screenshot and address are enough for most reports.
Browser alerts can also appear after an accidental click on a malicious advertisement. The path into the page can differ, but the support-number warning remains untrustworthy.
If the Fake Technician Already Controlled Your Screen
Remote-control software changes the situation. The operator may have seen open documents or watched you sign in, even if they claimed only to run a repair.
Start by disconnecting the machine from the internet. This interrupts most live sessions and prevents further commands while you seek trusted assistance.
Make a list of software you were asked to install. Keep receipts, chat logs, and the number called, but do not keep talking to the operator.
A trusted technician should remove the remote-access tool, inspect startup entries, and review whether another account was added to the computer.
Change passwords from another device. If you type a new password on the potentially controlled machine, the operator could learn the replacement too.
For work devices, inform your employer before trying to clean up alone. The incident may affect shared drives, customer data, or company accounts.
If you paid, ask the card issuer whether the charge can be disputed and the card replaced. Do not trust a promised refund from the caller.
Be wary of a second person who offers to recover the money for an upfront fee. Recovery fraud often follows a successful tech-support scam.
There is no need to feel embarrassed. These pages are designed to compress decision-making into a few frightening seconds. Acting promptly now matters more.
Frequently Asked Questions
Can a website know that Microsoft Defender found infected files?
Not merely because you opened it. The browser page’s claim is not a Defender result. Check protection history in Windows Security itself.
Does the Azure-hosted address make the page official?
No. Cloud hosting is infrastructure. A third party can host content there without becoming Microsoft support.
Was my email account really used to send the message?
The subject alone cannot answer that. Check sent mail, login activity, and account alerts through the real provider, then secure any account showing unauthorized access.
Is the phone number in the alert safe to call?
No. Microsoft says genuine error and warning messages do not include telephone numbers. Find support independently if you need it.
Could opening the page install malware by itself?
Seeing a page is not the same as installing a program. The larger risk begins if you download software, grant remote access, or enter credentials.
What if a remote-support app is still installed?
Disconnect the device, remove access with a trusted technician, scan it, and change passwords from another clean device. For a work computer, involve IT immediately.
The Bottom Line
This campaign joins an account-security email to a browser-made firewall warning. The supposed Microsoft diagnosis and support number are part of the deception.
Leave the page, verify both account activity and device security through their real interfaces, and treat any unexpected remote-access request as a serious escalation.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.