

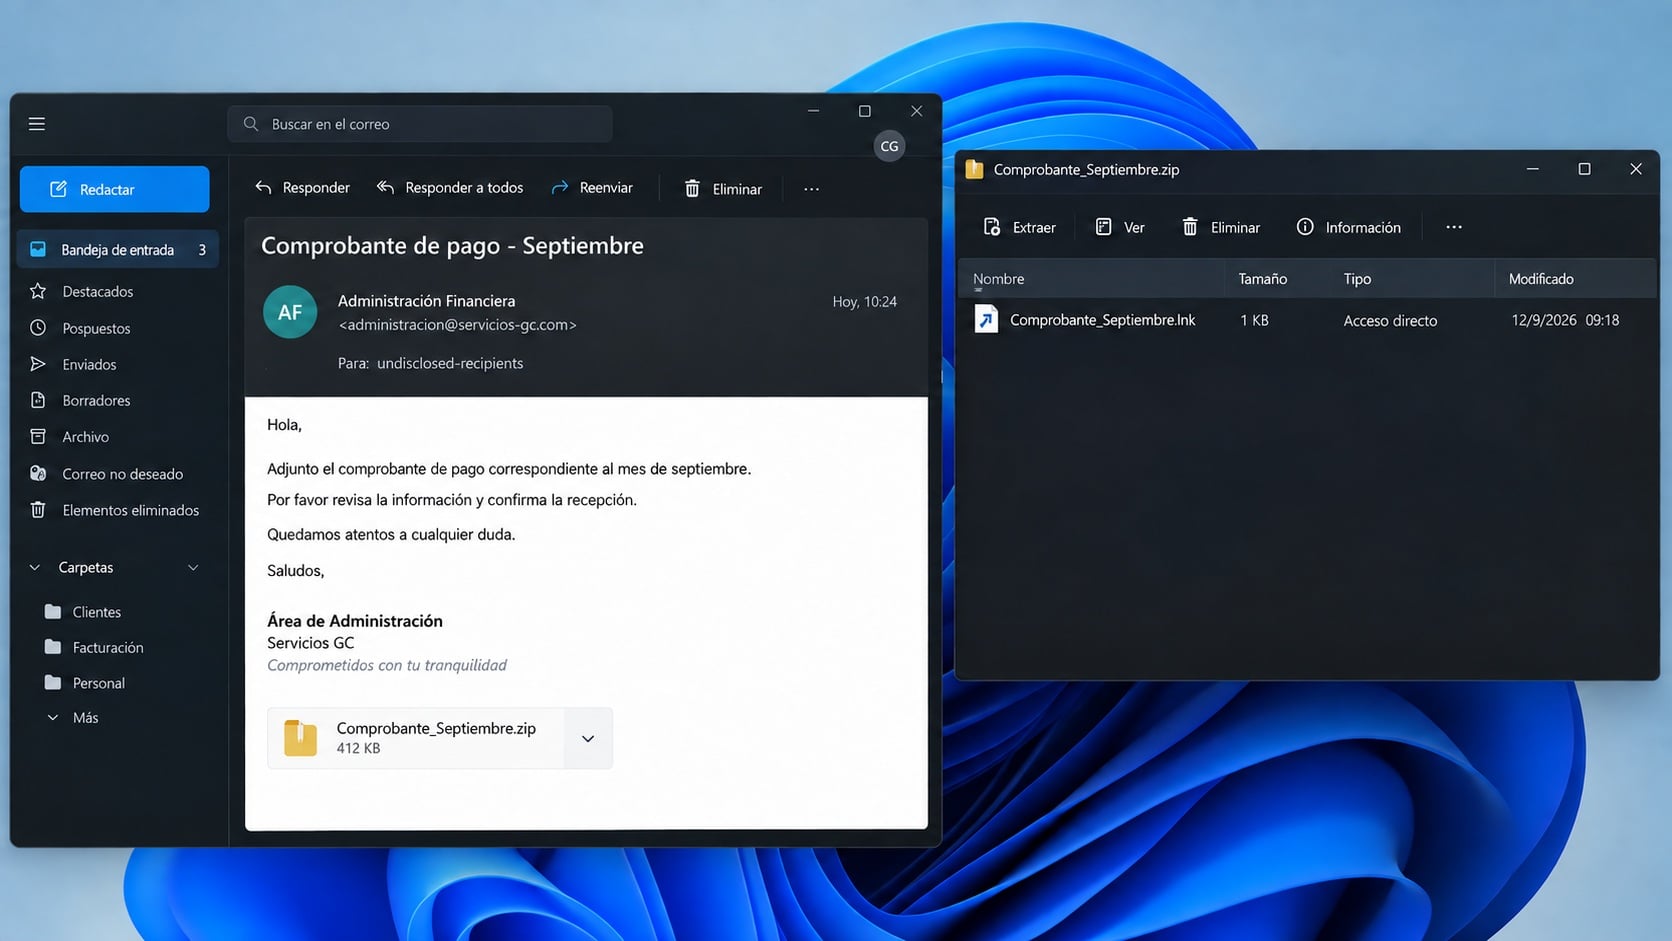
A voucher email asks you to open an archived document. Inside is a shortcut whose name fits the message, so it can look like an ordinary file.
PINHOLE does not depend on a flashy warning. It depends on that one file receiving more trust than it deserves.
Overview
The starting point is a disguised shortcut
PINHOLE is a Windows remote-access trojan found in a separate cluster from E4del. Both investigations involved malicious shortcuts that read instructions from FTP server greeting banners.
In PINHOLE’s observed chain, the shortcut retrieves a command that downloads a script. The script prepares a hidden payload and runs it on the machine.
The lure can be a Spanish-language voucher or other document-themed archive. Do not assume every email using that wording carries PINHOLE; the decisive clue is the execution chain.
A .lnk file is a program launcher, not a passive voucher. Its icon and friendly name can conceal what it starts.
The malware uses familiar services as signposts
PINHOLE stores encrypted configuration data in hidden file streams and uses pages on Pinterest and SurveyMonkey to discover its command server.
Those services are not themselves the attacker. Their public pages are abused as places to hold small pieces of direction, a tactic often called a dead drop.
The malware then routes traffic through Cloudflare Workers. A well-known service in the network path does not make the endpoint benign.
For a reader, the practical lesson is simple: trust the whole sequence, not isolated recognizable brand names.
What PINHOLE can do after installation
- Search, upload, download, or delete files.
- Run commands and launch programs remotely.
- Take screenshots of the desktop.
- Load a module aimed at browser passwords and cookies.
- Persist across sign-ins and hide its active code inside another process.
These are analyzed capabilities. They do not prove that every operator issued every command against every infected device.
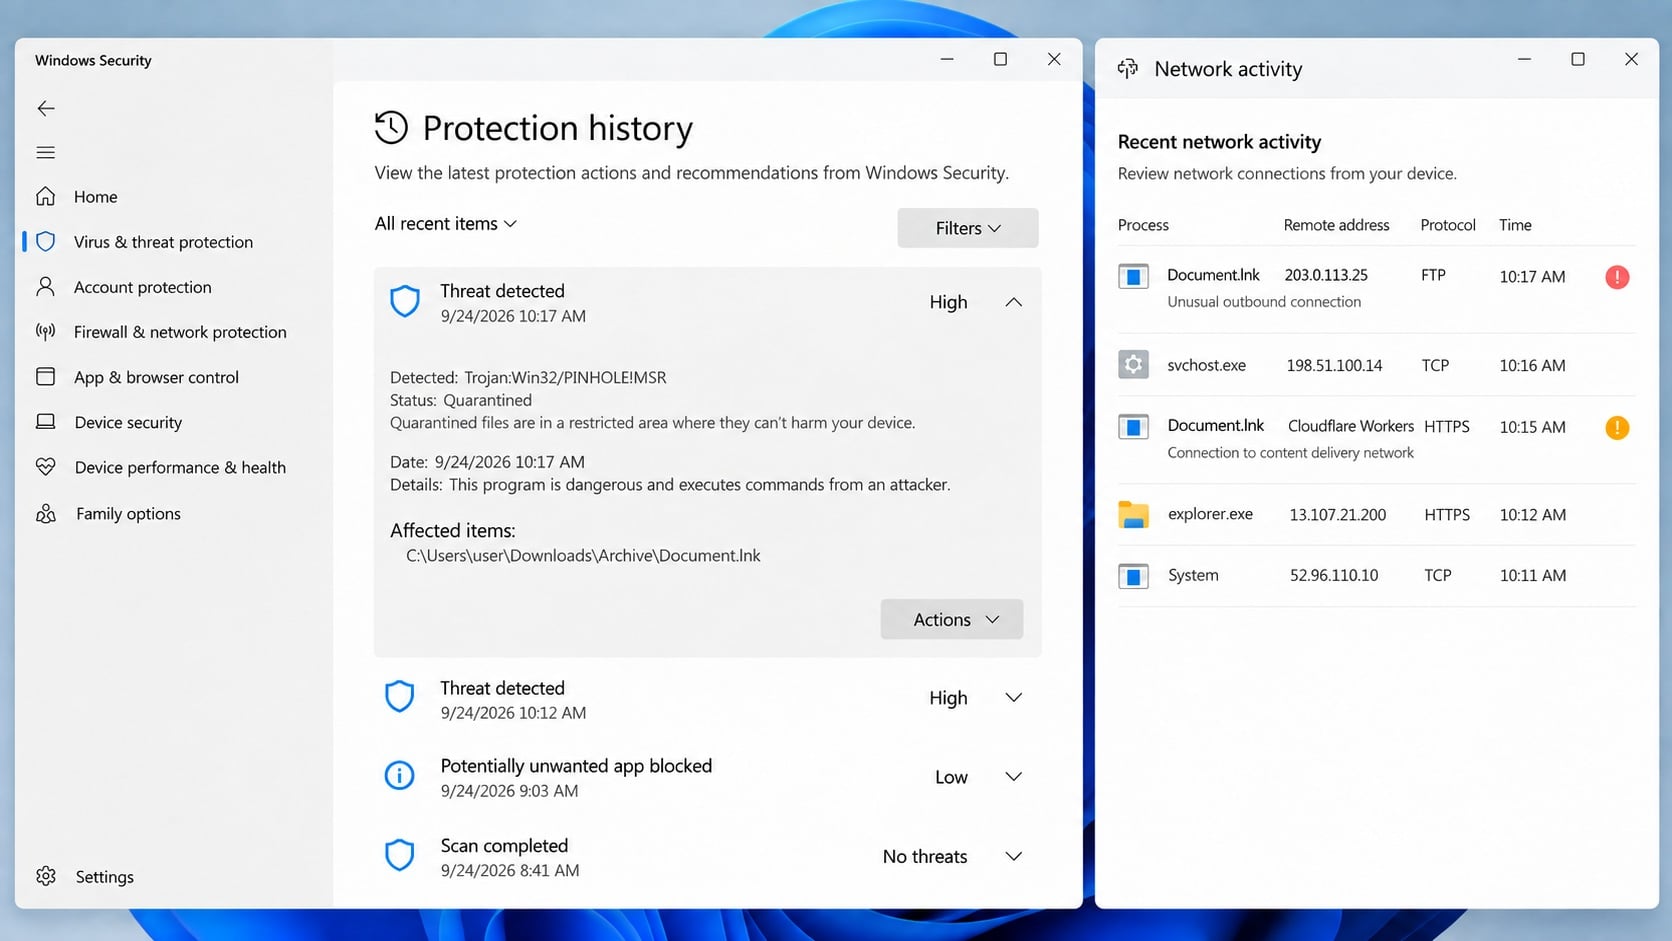
The images are static illustrations of the lure and possible security telemetry, not captures of a live victim or a real detected system.
What Makes This Campaign Different From E4del
The two families share the FTP-banner delivery idea, but researchers assessed them as separate clusters. Shared infrastructure tactics do not establish one operator.
E4del runs altered Electron code through a signed Discord host. PINHOLE uses a different multi-stage payload with layered decoding and process injection.
PINHOLE’s configuration is stored in NTFS alternate data streams. These hidden streams can attach information to ordinary-looking files without showing it in the usual File Explorer view.
Its server-discovery method reads external pages and then communicates through a worker proxy. A defender looking only for a direct connection to a suspicious domain may miss the relationship.
The malware also tries to recognize analysis environments and avoid running in them. That can complicate automated inspection of a suspicious sample.
None of this makes a home user responsible for reverse engineering it. The actionable boundary is much earlier: do not execute unexpected shortcuts from archives.
For organizations, the differences matter because a detection rule tailored only to Discord or E4del may not catch PINHOLE’s later stages.
The shared step, unexpected FTP traffic triggered by an archived shortcut, provides one useful starting point for incident review.
How the PINHOLE RAT Infection Works
Step 1: The recipient receives a document-themed archive
The lure asks the recipient to open a ZIP file. Spanish-language voucher themes were observed in related activity, but wording and filename can change.
Inside, the apparent document is a .lnk shortcut. If Windows hides extensions, the user may see only the first portion of its name.
Receiving the archive is not the same as running the shortcut. That distinction matters when deciding whether a full incident response is needed.
Step 2: The shortcut reads an FTP welcome banner
Once launched, the shortcut contacts an attacker-controlled FTP server. Its greeting message carries commands for the next stage.
Because the shortcut retrieves those instructions, the original file need not contain every later destination. That makes the initial artifact less revealing by itself.
Network records can show the unusual FTP connection. Security teams should preserve those records rather than clearing the machine immediately.
Step 3: A script prepares the hidden payload
The command fetches a script that writes encoded data in a temporary location. Some data is wrapped to resemble a certificate before being decoded and unpacked.
The process uses normal Windows utilities in an abnormal sequence. A legitimate tool’s presence does not make a malicious task legitimate.
Temporary files are removed after execution, reducing the obvious traces a user might notice in Downloads.
Step 4: PINHOLE evades inspection and persists
The payload checks its environment before running fully. It can avoid some emulators and use lower-level system calls to reduce visibility to certain monitoring tools.
Its later code is injected into another Windows process. It also arranges to launch again when the user signs in.
These techniques explain why an empty desktop after opening the shortcut does not indicate safety. Much of the operation is deliberately invisible.
Step 5: The trojan locates its operator and accepts tasks
PINHOLE reads hidden configuration, consults public web pages for server information, and uses a proxy route for its communications.
The operator can then request files, screenshots, commands, or an added browser-stealing module. Which actions occurred on one machine must be confirmed through evidence.
A browser history entry for Pinterest alone is not proof of PINHOLE. Correlate it with the shortcut, hidden streams, persistence, and network timeline.
Attachment, Process, Network, and Data Checks
Verify the archived item before opening it
Turn on file extensions and inspect the archive. A .lnk masquerading as a voucher is not a harmless PDF or image.
If the message came from someone you know, ask through a separate channel whether they really sent a shortcut file.
Examine the execution chain, not one alert
For an affected workstation, record the shortcut, script execution, temporary files, process injection, and persistence indicators where available.
A single antivirus label can vary by vendor. The sequence provides a better picture of whether PINHOLE actually ran.
Interpret public-service traffic carefully
Pinterest, SurveyMonkey, and Cloudflare Workers have legitimate uses. Their names alone are not indicators of compromise.
Look for requests from the suspicious process at the relevant time, along with the abnormal FTP delivery that preceded them.
Assess what data the operator could reach
Browser passwords, cookies, documents, and screenshots are potential targets. Inventory what the affected account could access during the period of suspected infection.
Keep “could access” separate from “did steal.” That distinction is essential when notifying people, investigating fraud, and deciding whether to rebuild systems.
What to Do if You Suspect PINHOLE on Your Computer
- Isolate the device. Disconnect network access and stop using it for passwords, payments, or sensitive documents until it is assessed.
- Preserve the lure. Keep the email, ZIP file, shortcut name, and timestamp for a security team. Do not execute it again to demonstrate the problem.
- Tell IT if it is a work machine. PINHOLE can reach data available to the user account. Early reporting helps protect shared systems and preserve logs.
- Scan and investigate. Run Windows Security and Malwarebytes. A security professional should also check persistence, hidden configuration, and additional payloads.
- Secure accounts from a clean device. Change passwords used on the affected computer, revoke active sessions, and review browser-stored credentials.
- Review financial and cloud activity. Look for suspicious logins, transfers, file downloads, or changed account recovery settings during the possible infection period.
- Rebuild when trust is uncertain. A clean installation may be appropriate for a high-risk endpoint. Restore only vetted files and reinstall applications from official sources.
- Stop the same lure reaching others. Search for matching archives and report the sender. AdGuard can help block known malicious destinations, but it cannot make an executed shortcut safe.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why Familiar Web Services Can Hide an Unfamiliar Attack
A browser visiting Pinterest or SurveyMonkey is ordinary. PINHOLE’s use of those services depends on context, timing, and the process making the request.
The malware does not need the services to knowingly cooperate. Public content can carry encoded directions that another program reads.
Cloudflare Workers can legitimately deliver applications and APIs. In this chain, a worker was used to proxy malicious command traffic.
Blocking every well-known service is not a practical response. Investigators should connect the traffic to the shortcut and infected process.
The same reasoning applies to certificate-looking files. A block of text wrapped in familiar headers can still be attacker-controlled encoded payload data.
A legitimate Windows utility used to decode or unpack data does not make the result safe. The sequence and origin determine its meaning.
For a home user, these details explain why a single glance at browser history cannot prove or disprove infection.
For a business, they support behavior-based detection. Watch for unexpected FTP, script execution, persistence changes, and suspicious child processes.
Do not treat a normal page visit as evidence against an employee. The security question is whether malware used the service in the observed chain.
What Hidden Configuration Means for Cleanup
Windows files can contain alternate data streams that do not appear like ordinary neighboring documents. PINHOLE used this feature to store encrypted configuration.
Deleting the original ZIP may leave later components in place. A cleanup must inspect persistence and the machine’s current state.
The program can inject code into a legitimate process. Task Manager may therefore show a familiar name rather than a visible “PINHOLE” application.
Security products can still detect malicious behavior or artifacts, but an advanced threat may need a deeper endpoint investigation.
Do not manually delete desktop.ini files or random registry values after reading a public indicator list. Those items can be normal Windows components.
Use the original research indicators as hunting leads, not as a universal recipe for removing every variant.
If a machine holds sensitive work data, consider preserving a forensic image before reinstallation. That allows later review of what was accessed.
A clean reinstall from trusted media can reestablish device integrity, but it does not automatically revoke stolen browser sessions or cloud credentials.
Account recovery and endpoint recovery must happen together. Otherwise an attacker can keep using a stolen session after the computer is clean.
Practical Boundaries for a Personal or Work Computer
If you received the archive but did not execute the shortcut, report it and stop. There is no reason to assume the trojan installed itself merely from receipt.
If you ran it, disconnect the network promptly. Write down what you opened and when, then use a separate clean device for sensitive accounts.
On a work computer, avoid self-directed cleanup that destroys evidence. The security team may need logs to identify other targeted colleagues.
On a personal computer, run updated reputable scans and consider professional help if detections appear or the device handled financial credentials.
Do not pay someone from a pop-up advertisement promising instant PINHOLE removal. The incident requires trustworthy tools and account checks, not a miracle cleaner.
Review browser sessions and saved passwords. A browser-stealing module can be deployed on demand, so the absence of a visible banking problem is not decisive.
Check cloud accounts for unfamiliar access and downloads. Note what you find before revoking sessions, so a later investigator has a timeline.
Tell contacts if your email or messaging account was used without authorization. That can prevent the same lure from spreading through trusted relationships.
Prevention is ultimately simpler than recovery: treat a shortcut inside an unexpected ZIP as software, not as a document waiting to be read.
Ask the sender to provide the actual document through a known portal if the business request is real. That lets work continue without testing the suspicious file.
When several people receive the same archive, coordinate one response. Each employee opening it independently creates another possible foothold and complicates the timeline.
After recovery, document which controls caught the activity and which did not. That turns one incident into stronger email filtering and endpoint detection.
Frequently Asked Questions
Are E4del and PINHOLE the same malware?
No. Researchers treated them as separate clusters that share an unusual FTP-banner delivery method.
Are Pinterest and SurveyMonkey malicious?
No. PINHOLE abuses public content on legitimate services to find its command server. Ordinary use of those sites is not an infection indicator.
Can an email infect me without opening the shortcut?
Receiving the message is not the described execution step. Do not run the archived shortcut, and report the email.
Why does the shortcut look like a document?
Its name and icon can be chosen to fit the lure. Windows shortcuts can launch commands even when they appear beside ordinary documents.
Can antivirus alone prove the computer is clean?
A scan helps, but advanced persistence and follow-on modules call for reviewing the execution and network history, especially on business systems.
Should I delete the archive immediately?
On a personal device with no execution, reporting and removal are reasonable. After execution, preserve a copy for responders before cleanup.
The Bottom Line
PINHOLE begins with a deceptive shortcut, then hides its instructions and command route across several stages and services. It is a distinct RAT, not merely another name for E4del.
The safest decision happens before launch. If the shortcut ran, isolate the system, preserve evidence, and investigate both the device and the accounts it could access.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.