


An unexpected invitation promises access to a high-profile UFC prediction market and a generous trading bonus. The message looks polished, timely, and surprisingly personal.
Before connecting a crypto wallet, however, several details deserve careful attention. One careless approval can carry consequences far beyond a missed sporting event.
Overview
A convincing invitation borrows Polymarket’s identity
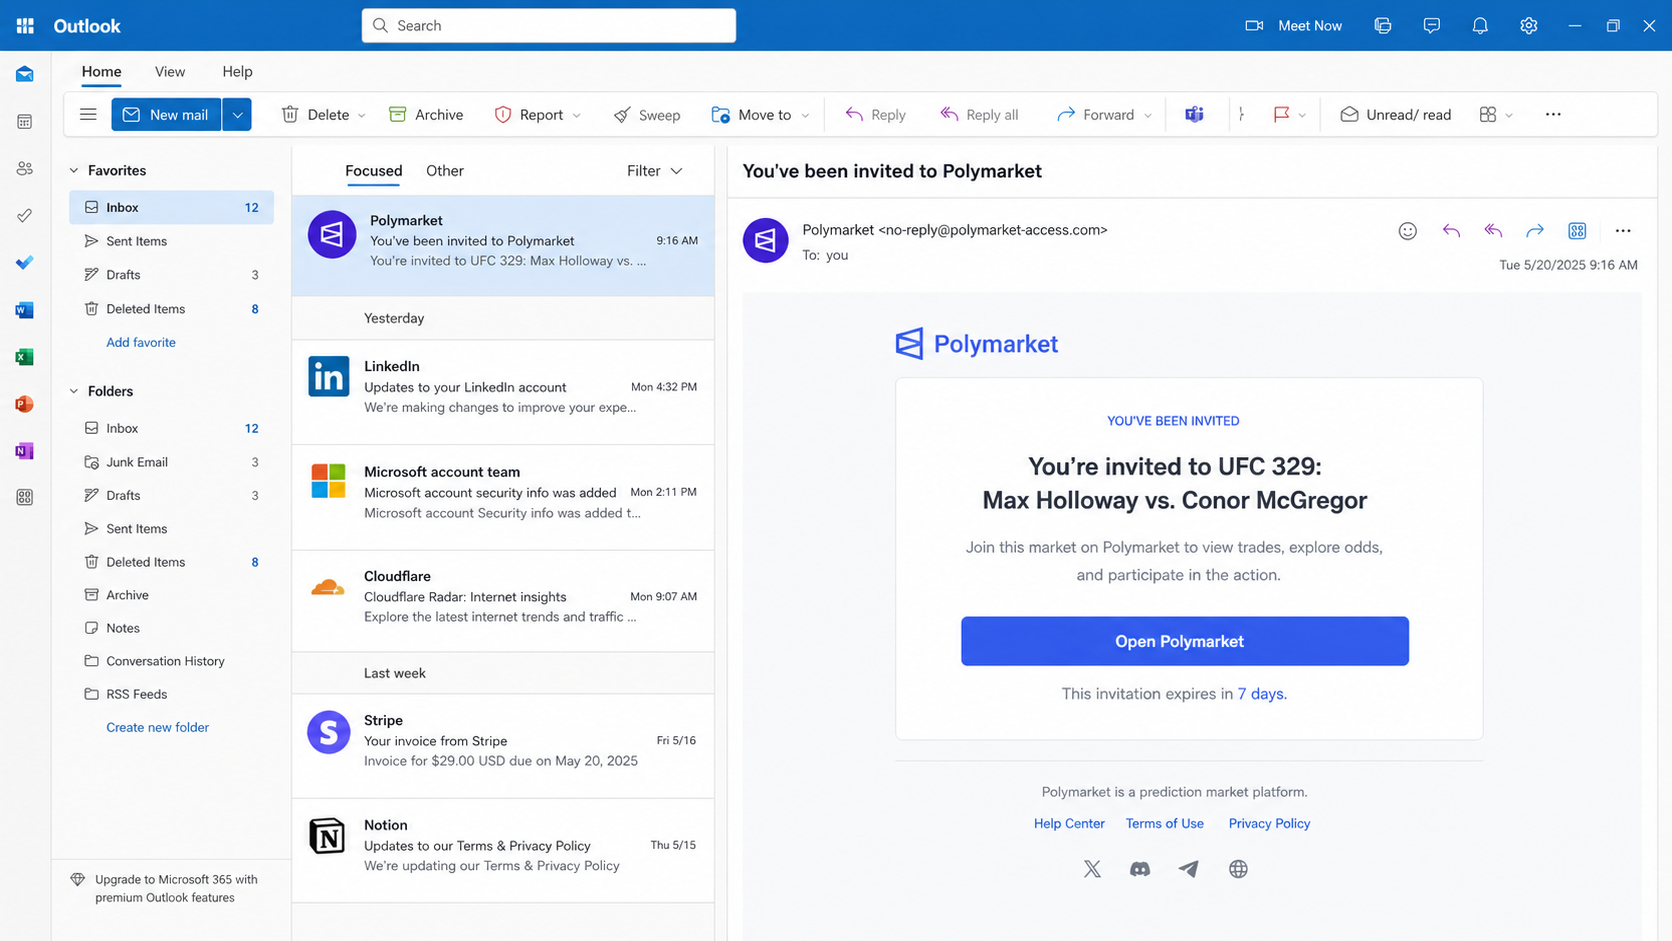
The Polymarket UFC invite scam begins with an email claiming the recipient was invited to a special prediction market.
One observed message promoted a supposed UFC 329 matchup between Max Holloway and Conor McGregor. A prominent button invited the reader to open Polymarket.
The email copied recognizable branding, restrained colors, and professional spacing. It also claimed the invitation would expire after seven days.
Those details make the message feel more like a legitimate product notification than ordinary cryptocurrency spam.
The campaign even used a legitimate transactional email service for delivery. That technical detail can improve appearance, but it does not validate the sender’s offer.
Real companies use outside email platforms every day. Criminals can also abuse or imitate those services when distributing a phishing campaign.
The invitation was not an official Polymarket communication. The promoted event, bonus, and destination were parts of an impersonation scheme.
The destination is a counterfeit trading platform
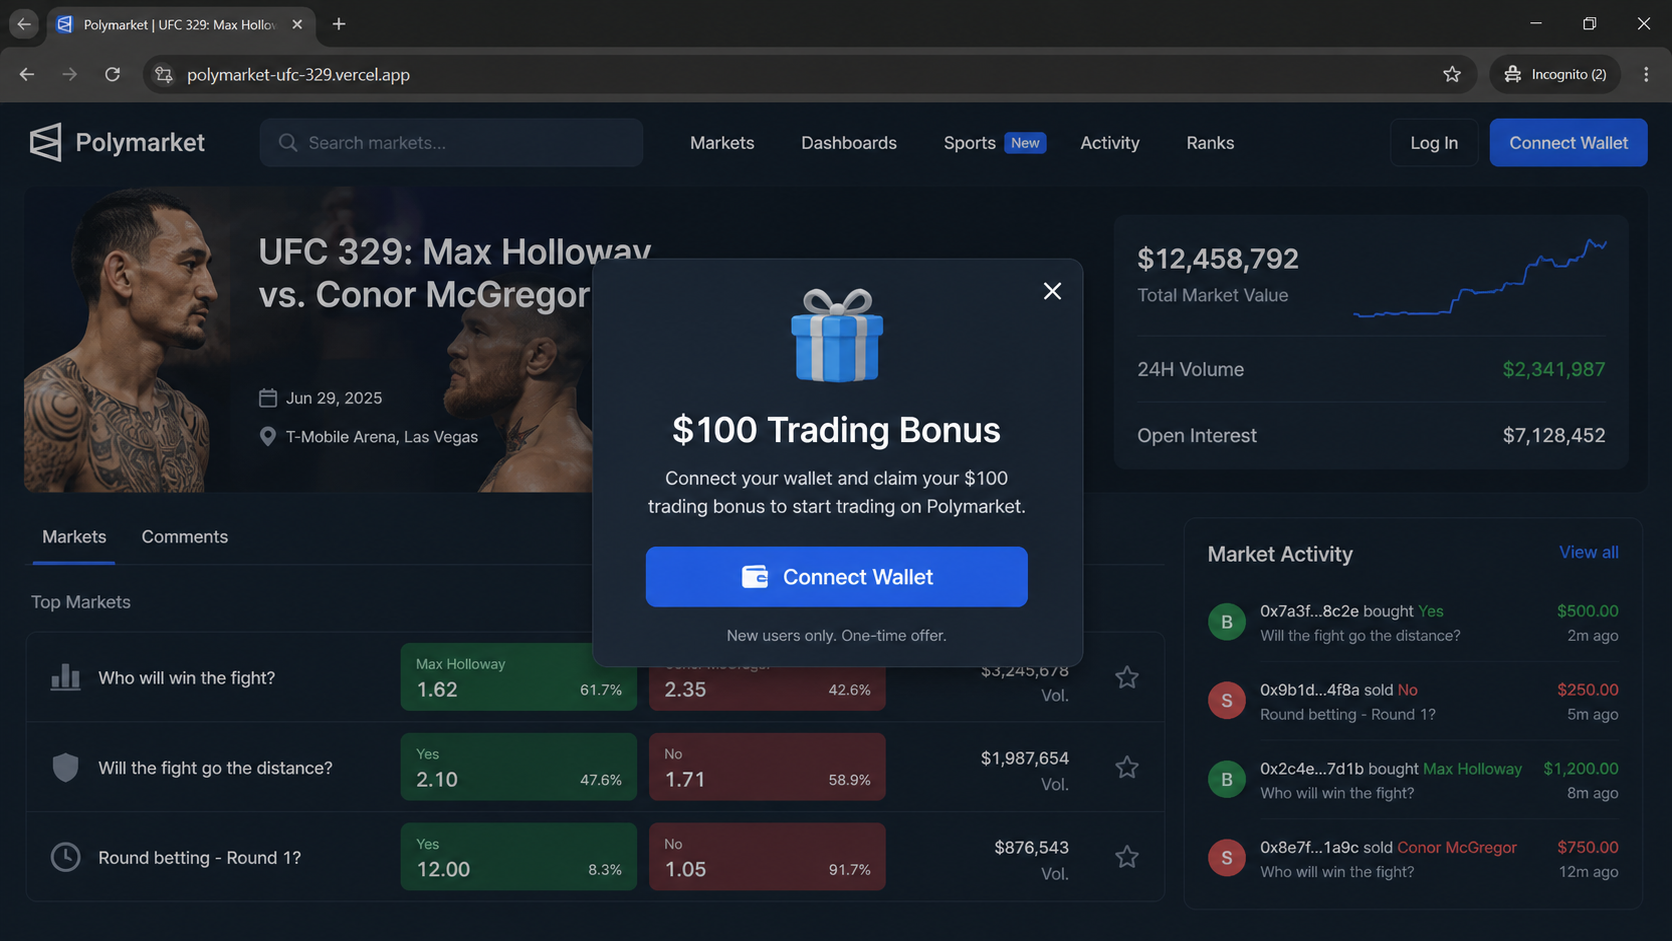
The button led toward a site hosted at polymarket-ufc-329.vercel.app, rather than an official Polymarket domain.
Its pages copied the visual language of an active prediction market. Visitors could see sports listings, trading figures, market volumes, and wallet options.
A free hosting subdomain is not automatically malicious. Developers use such services legitimately for previews, prototypes, and production applications.
In this case, the unrelated host mattered because the page claimed to be an established financial platform while asking visitors to authorize wallet access.
The site presented a $100 trading bonus as an incentive. That promise encouraged visitors to connect quickly instead of checking the address carefully.
No legitimate bonus needs an unknown website to receive unlimited spending authority over tokens already held inside a personal wallet.
Polymarket and the named athletes have no connection with the deceptive email, copied page, or wallet request.
The dangerous moment is the transaction approval
Connecting a wallet does not always move cryptocurrency immediately. It allows a website to request information and present transactions for the owner to sign.
The malicious page uses that familiar process to place a harmful authorization inside what appears to be routine account setup.
Depending on the wallet and contract, the request may grant token spending permission, authorize a transfer, or approve another operation benefiting the scammer.
An unlimited token allowance is especially dangerous. It can permit the approved contract or spender to move eligible assets later without another spending-cap decision.
The wallet may display technical language that a hurried visitor does not understand. Scammers count on the promised bonus carrying attention past those details.
The campaign can be recognized through this sequence:
- An unsolicited email claims the recipient received an exclusive Polymarket invitation.
- A current-looking sports event supplies excitement and urgency.
- The button opens a lookalike platform on an unrelated domain.
- Professional market graphics create the appearance of active trading.
- A $100 bonus encourages the visitor to connect a wallet.
- The wallet receives an approval or transaction request.
- Signing the request can expose cryptocurrency to theft.
The theft happens through blockchain permissions, not through the email itself. Simply reading the message does not empty a wallet.
Risk rises after opening the counterfeit site, connecting a wallet, and approving a transaction or token allowance that was not independently verified.
The safest response is to close the page, reject every request, and access any genuine service through a separately typed or saved official address.
How The Scam Works
Step 1: The email turns a sporting event into an invitation
The campaign starts with a message framed as special access rather than a traditional prize. Being invited feels more credible than being declared a random winner.
The subject announces that the reader has been invited to Polymarket. Inside, the same idea appears again beside familiar branding.
A named UFC matchup gives the message a concrete purpose. It feels easier to verify emotionally because the fighters and sport are recognizable.
The scammers do not need every recipient to follow mixed martial arts. They need enough curiosity to earn one click.
Expiration language adds a quiet deadline. Seven days seems reasonable, yet it still discourages leaving the invitation for later research.
The email contains few obvious distractions. This restrained presentation can appear more authentic than messages filled with flashing prizes and aggressive promises.
Recipients may also assume a friend, coworker, or online community triggered the invitation. The message does not provide reliable evidence of who supposedly invited them.
Step 2: Professional delivery supplies borrowed credibility
The observed email referenced a legitimate service used by companies for account messages and transactional mail.
That footer can lower suspicion because recipients associate established infrastructure with screened, trustworthy businesses. The assumption is unsafe.
An email provider transports messages. It does not guarantee that every customer’s offer, linked domain, or connected application is honest.
Scammers may register accounts using temporary business details, compromise a legitimate account, or imitate service notices inside their own design.
Authentication checks can show whether a server was permitted to send for a domain. They do not prove the business proposition itself is genuine.
The visible sender name can also differ from the actual address. Always expand sender details before trusting a recognizable display name.
Even then, a believable sender is only one clue. The destination domain and requested wallet action carry far more weight.
Step 3: The invitation button crosses into the counterfeit site
The Open Polymarket button does not take the visitor to the official platform. It opens a separate domain built to resemble it.
On a phone, the address bar may be collapsed or shortened. The screen then emphasizes logos, market cards, and buttons instead of ownership.
The fake page can use encrypted HTTPS. A padlock means the browser connection is encrypted, not that the recipient behind the site is trustworthy.
Hosting providers make modern deployment fast and inexpensive. A scammer can publish a polished application without operating a recognizable standalone web server.
The page may disappear after reports and return under another subdomain. Its name matters, but the behavioral pattern remains the stronger warning.
Visitors who navigate directly to the real platform will not find the emailed invitation or identical $100 wallet offer.
That difference is why independent navigation matters. Never let an unsolicited financial message choose the address where a wallet gets connected.
Step 4: Fake market activity makes the page feel occupied
The landing page displays odds, participant counts, prices, charts, or trading volume to suggest other people are already participating.
These numbers may be copied, fabricated, or generated inside the browser. A changing total is not proof that real blockchain trades support it.
Logos and interface elements can be copied from public websites. Producing a familiar screen is far easier than operating a legitimate regulated business.
The sports theme also gives the visitor something engaging to inspect. While attention follows odds and outcomes, the domain mismatch fades into the background.
Some visitors may click several markets before seeing the bonus. That interaction builds comfort and creates the impression of a functioning product.
Nothing shown on the page establishes who controls the wallet request. The decisive evidence appears inside the transaction details, not the attractive dashboard.
When a platform appears through an invitation, compare it with the official site opened independently. Navigation, account history, and documented contracts should agree.
Step 5: A $100 bonus moves attention toward Connect Wallet
The counterfeit platform presents a trading credit to new users. The amount is large enough to attract interest without appearing impossibly extravagant.
Bonuses are common in finance, gaming, and cryptocurrency marketing. That familiarity makes the prompt feel like ordinary customer acquisition.
The offer may imply the wallet connection is only needed to identify an account. In reality, connection begins a sequence of permission requests.
A legitimate wallet connection can reveal the public address and token balances to a site. It cannot reveal a secret recovery phrase by itself.
The danger comes when the page requests a signature, spending allowance, contract interaction, or direct transfer and the visitor approves it.
Scammers often place these requests immediately after a bonus button. The victim expects setup paperwork and treats technical prompts as routine.
A reward should never require an unexplained unlimited allowance. Reject the request and investigate from a clean, independently opened browser tab.
Step 6: The wallet presents authority the website wants
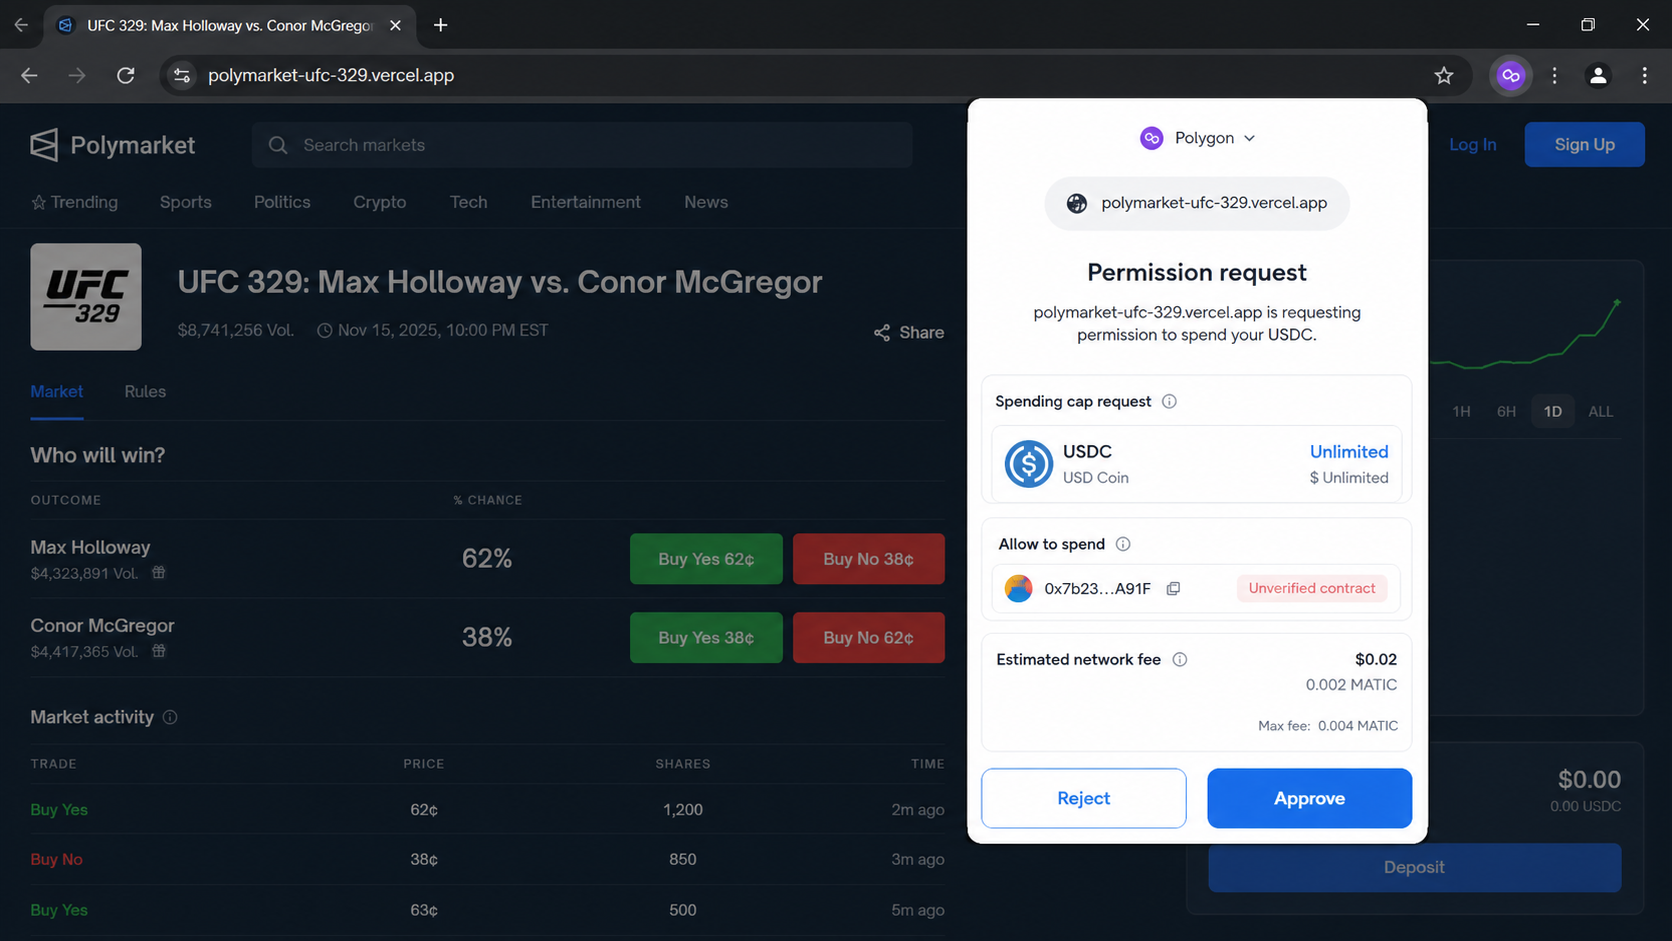
Modern wallets usually display the requesting site, blockchain network, contract, assets involved, and estimated fee. Those details are the final safety checkpoint.
A malicious request may seek unlimited USDC approval or permission to interact with another token held by the connected address.
Spending approval differs from sending a one-time payment. It can authorize a named spender to transfer tokens up to the permitted limit later.
If the limit is unlimited, the potential exposure may exceed the visible $100 offer or the amount expected for a single prediction.
Some signatures are harder to interpret. A typed-data message can look less serious than a transfer while still granting meaningful authority.
Wallet warnings help, but they cannot always determine intent. Users must compare the site, contract, asset, and requested power before signing.
Rejecting the request costs nothing and preserves the assets. A real opportunity remains available after careful verification, while a malicious signature may not be reversible.
Step 7: The attacker uses the approval and disappears
Once useful authority is granted, the malicious spender can attempt to transfer approved tokens from the victim’s address.
The withdrawal may happen quickly or after a delay. Waiting can make the victim forget which site received the permission.
Blockchain transactions are generally final after confirmation. A bank cannot simply reverse them as it might investigate an unauthorized card charge.
The copied website may then show an error, endless loading screen, or false account balance. Support contacts can remain silent.
Operators can abandon the hosting subdomain and launch a new version using another sporting event, bonus, or prediction-market brand.
Stolen funds may move through several addresses, swaps, bridges, or exchanges. Movement complicates recovery, although transaction records remain visible publicly.
Victims can then attract recovery scammers promising guaranteed retrieval for an advance payment. That second payment usually creates another loss.
Why Disconnecting the Wallet May Not Be Enough
Many people disconnect the suspicious website inside their wallet and assume the danger has ended. Disconnecting and revoking are different actions.
Disconnecting removes the site’s current ability to view account information through that browser session. It does not automatically cancel blockchain token approvals.
A spending allowance is recorded on-chain. It remains active until the owner submits a revocation transaction or changes the allowance.
Revocation usually requires a small network fee. Use the wallet’s official approval manager or a reputable explorer reached independently.
Check every asset and network used during the incident. A wallet may have permissions on Polygon, Ethereum, Base, or another chain.
Look for unfamiliar spenders, unusually high caps, and approvals created near the time of the visit. Revoke questionable entries promptly.
If a seed phrase or private key was exposed, approval cleanup is insufficient. Those secrets provide broader wallet control.
Create a new wallet on a clean device and move remaining assets carefully. Never reuse the compromised recovery phrase.
Test with a small transfer before moving larger holdings. Confirm addresses through more than one trusted view to avoid clipboard replacement malware.
Do not enter a recovery phrase into any revocation website. Legitimate approval management works through the wallet’s transaction confirmation process.
Sender, Domain, Wallet, and Contract Checks
Expand the sender and inspect the invitation story
A display name reading Polymarket is not proof of origin. Expand the header and examine the complete address, reply path, and mailed-by information.
Ask why the account received an invitation. A genuine message should connect to an action, account, or person the recipient actually recognizes.
Unexpected exclusivity is a warning. Scammers use invitations because curiosity can replace the skepticism triggered by an obvious prize.
Do not reply to request confirmation. A response tells the sender the address is active and can invite more targeted attempts.
Read the entire domain before touching the wallet
Polymarket-ufc-329.vercel.app is not the same as Polymarket’s official address. The decisive ownership portion appears immediately before the final domain ending.
Brand words can appear inside a subdomain without any relationship to the brand. Attackers deliberately place trusted names where hurried readers will notice them.
Open financial services from a bookmark or a manually entered official address. Do not use search advertisements as the only route.
A polished page, valid certificate, and respected hosting provider cannot repair an ownership mismatch. None proves the copied service controls that site.
Treat wallet prompts as financial contracts
Read every line of a signature or transaction request. Identify the network, token, amount, spender, and action before selecting Approve.
Unlimited allowances deserve special caution. Set a specific spending cap when a legitimate service supports it, then remove unnecessary access afterward.
If the wallet cannot explain the request clearly, reject it. Technical confusion is not a reason to grant broader authority.
Never provide a recovery phrase, private key, remote-control session, or screen-sharing access to someone offering help with a bonus.
Verify contracts and support through independent records
Legitimate decentralized applications publish contract information through official documentation. Compare addresses character by character using a trusted route.
Do not trust a contract address supplied only by the suspicious page, its chat agent, or a reply to the original email.
Search the address on the appropriate blockchain explorer. Review creation time, verified code status, approvals, transactions, and warnings when available.
A new contract is not automatically malicious, but a new unverified spender attached to an impersonation page presents an unacceptable combination.
What to Do if You Have Fallen Victim to This Scam
- Reject pending requests and close the page. Do not retry the bonus, sign corrective messages, or follow support links displayed by the counterfeit platform.
- Disconnect the suspicious site. Remove its active connection inside every wallet and browser profile used, while remembering that disconnection does not revoke allowances.
- Revoke malicious approvals immediately. Use the wallet’s official tools or a trusted blockchain explorer to cancel unfamiliar token allowances on every affected network.
- Move funds if wallet secrets were exposed. Create a fresh wallet on a clean device, transfer remaining assets, and permanently retire the compromised recovery phrase.
- Contact relevant exchanges quickly. Provide transaction hashes, destination addresses, amounts, networks, and timestamps. An exchange may flag an account, although recovery is not guaranteed.
- Preserve evidence. Save the email, complete headers, destination URL, screenshots, wallet prompts, transaction records, and every conversation with supposed support.
- Report the campaign. Notify the impersonated company, email provider, hosting service, wallet provider, local police, and national fraud reporting authority.
- Change exposed account credentials. If a password was entered anywhere, replace it from a clean device and enable strong app-based multifactor authentication.
- Scan the device with Malwarebytes. This is important after installing a file, browser extension, remote-access tool, or software offered by the deceptive site.
- Use AdGuard to reduce malicious advertising. Filtering cannot replace careful wallet review, but it can block many deceptive redirects and known scam destinations.
- Ignore recovery guarantees. Anyone demanding an advance fee, tax, wallet synchronization, or recovery phrase is likely attempting a second scam.
- Monitor every affected address. Watch balances and approvals for delayed movement, then document any new transaction before alerting exchanges and investigators.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the Polymarket UFC invitation email genuine?
No. The documented message impersonated Polymarket and directed recipients to an unrelated site presenting a fake sports market and wallet bonus.
Open the official service independently if an invitation seems plausible. A genuine account notification should also appear within the real account environment.
Can opening the email alone drain a crypto wallet?
Simply reading the email does not authorize token movement. The critical risk begins after visiting the counterfeit site and signing a malicious wallet request.
Avoid loading unexpected attachments or installing anything. Those actions can introduce separate threats beyond the wallet-drainer method documented here.
Does connecting a wallet automatically give away cryptocurrency?
A basic connection generally exposes the public address and permits transaction requests. It does not automatically reveal the recovery phrase or approve every transfer.
However, the next signature can grant dangerous authority. Read each prompt independently rather than treating connection and approval as one harmless setup step.
What does an unlimited USDC approval mean?
It lets a specified spender move USDC up to a very high allowance from that wallet, subject to the token contract’s rules and available balance.
The allowance can remain active after leaving the website. Revoke it on-chain if the spender is unfamiliar or the approval came from this campaign.
Can stolen cryptocurrency be recovered?
Recovery is difficult and never guaranteed. Contact exchanges and law enforcement quickly, preserving transaction hashes and destination addresses for tracing.
Do not send more money to private recovery agents promising certainty. Fraudsters monitor victims and frequently return with a second persuasive story.
Are Max Holloway or Conor McGregor involved?
No evidence connects either athlete with the fraudulent invitation. Their names were used as attention-grabbing material inside an impersonation campaign.
A recognizable person or event can be copied into an advertisement without consent. Celebrity imagery never verifies the website requesting financial authority.
The Bottom Line
The Polymarket UFC invite scam turns a believable sports invitation into a path toward a counterfeit platform and a dangerous wallet authorization.
Its strongest weapons are familiarity and timing. Professional email design, active-looking markets, and a $100 bonus make an unrelated domain seem briefly reasonable.
Pause at the wallet prompt. Verify the site independently, reject unexplained approvals, and remember that unlimited token access is never routine account registration.
If approval was already granted, disconnect the site and revoke allowances immediately. Move funds when secrets were exposed, then document and report the loss.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.