


The ZeroAccess rootkit also known as Sirefef, is a malicious program that has as a primary motivation of to make money through pay per click advertising. It does this by downloading an application that conducts Web searches and clicks on the results. This is known as click fraud, which is a very lucrative business for malware creators.
The threat is also capable of downloading other threats on to the compromised computer, some of which may be Misleading Applications that display bogus information about threats found on the computer and scare the user into purchasing fake antivirus software to remove the bogus threats. It is also capable of downloading updates of itself to improve and/or fix functionality of the threat.
The ZeroAccess rootkit is distributed through several means. Some websites have been compromised, redirecting traffic to malicious websites that host Trojan.Zeroaccess and distribute it using the Blackhole Exploit Toolkit and the Bleeding Life Toolkit. This is the classic “drive-by download” scenario. It also updates itself through peer-to-peer networks, which makes it possible for the authors to improve it as well as potentially add new functionality.
If your antivirus is detecting any of the below files as malicious and it can’t remove them , then you’ll know that you have a ZeroAccess infection:
C:\Windows\assembly\GAC_32\Desktop.ini
C:\Windows\assembly\GAC_64\Desktop.ini
C:\WINDOWS\services.exe << INFECTED
C:\windows\Installer\{random number sequence}\U\80000032.@
C:\windows\Installer\{random number sequence}\U\80000064.@
C:\windows\Installer\{random number sequence}\L\00000004.@
C:\windows\Installer\{random number sequence}\U\80000000.@
C:\windows\Installer\{random number sequence}\U\000000cb.@
How to remove ZeroAccess rootkit virus (Virus Removal Guide)
Please perform all the steps in the correct order. If you have any questions or doubt at any point, STOP and ask for our assistance.
-
To remove ZeroAccess rootkit virus, follow these steps:
- STEP 1: Use ESETSirfefCleaner tool to remove ZeroAccess rootkit
- STEP 2: Use RKill to stop the ZeroAccess rootkit malicious processes
- STEP 3: Scan your computer with Malwarebytes Anti-Malware to remove ZeroAccess rootkit
- STEP 4: Double-check for malicious programs with HitmanPro
- (OPTIONAL) STEP 5: Use Zemana AntiMalware Portable to remove ZeroAccess rootkit
STEP 1: Use ESETSirfefCleaner tool to remove ZeroAccess rootkit
In this first step, we will use the ESETSirefefCleaner tool to remove the ZeroAccess rootkit from your computer.
- You can download ESETSirefefCleaner from the below link.
Download ESET Sirefef CleanerYour download starts right away.Unable to download “ESETSirefefCleaner.exe contained a virus and was deleted”.
More recent variants of Sirefef might prevent you from downloading this removal tool. If you cannot download the tool, follow the steps below:- Click Start → Computer → Local Disk (C:) → Program Files.
- Right-click the Windows Defender folder and select Rename from the context menu.
- Add a unique variation to the filename, such as .old (for example, Windows Defender.old).
- Click the link above to download the ESETSirefefCleaner tool.When the download is complete, make sure to rename the Windows Defender folder back to its original filename before running the ESET SirefefCleaner tool.
- Double-click on ESETSirefefCleaner.exe to start this utility. You may be presented with an User Account Control pop-up asking if you want to allow this to make changes to your device. If this happens, you should click “Yes” to continue.
- The message “Win32/Sirefef.EV found in your system” will be displayed if an infection is found. To remove ZeroAccess rootkit from your computer, press the Y key on your keyboard
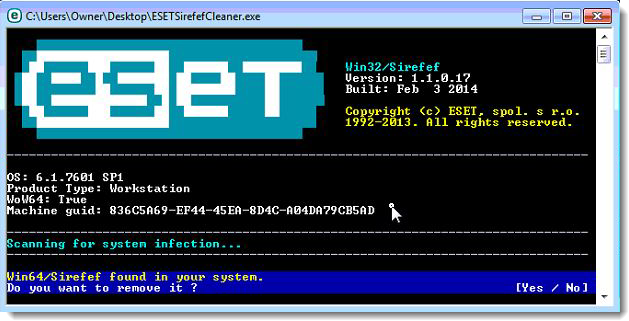
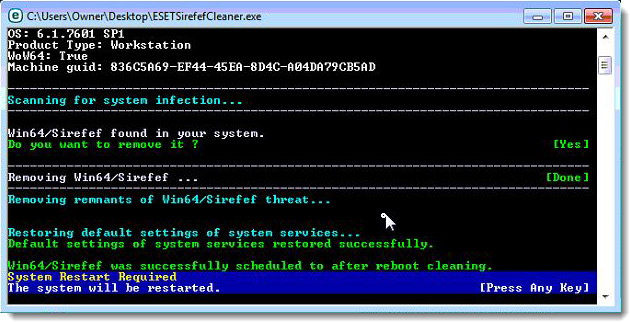
- Once the tool has run, you will be prompted to restore system services after you restart your computer. Press Y on your keyboard to restore system services and restart your computer.
- Once your computer has restarted, if you are presented with a security notification click Yes or Allow. and then continue wit the next step.
STEP 2: Use RKill to stop the ZeroAccess rootkit malicious processes
RKill is a program that will attempt to terminate all malicious processes associated with ZeroAccess rootkit, so that we will be able to perform the next step without being interrupted by this malicious software.
- You can download Rkill from the below link.
Download RKillOpens the download page in a new tab. - Double click on Rkill program to stop the malicious programs from running.
- RKill will now start working in the background, please be patient while this utiltiy looks for malicious process and tries to end them.
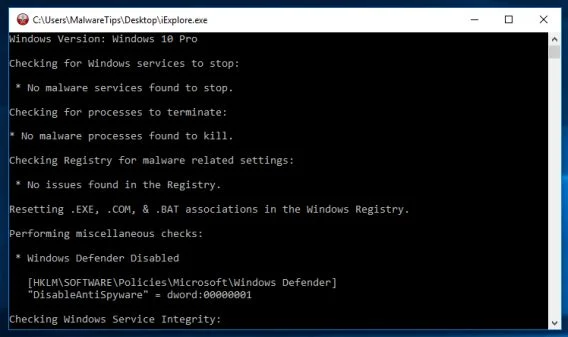
- When the Rkill tool has completed its task, it will generate a log. Do not reboot your computer after running RKill as the malware programs will start again.
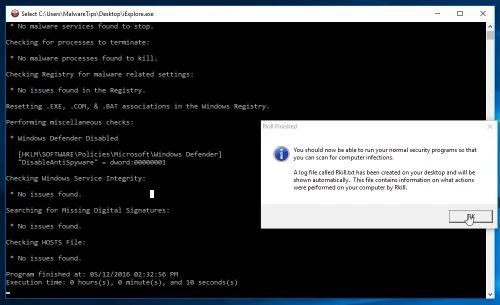
STEP 3: Scan your computer with Malwarebytes Anti-Malware to remove ZeroAccess rootkit
Malwarebytes Anti-Malware is a powerful on-demand scanner which should remove the ZeroAccess rootkit virus from your machine. It is important to note that Malwarebytes Anti-Malware will run alongside antivirus software without conflicts.
- You can download download Malwarebytes Anti-Malware from the below link.
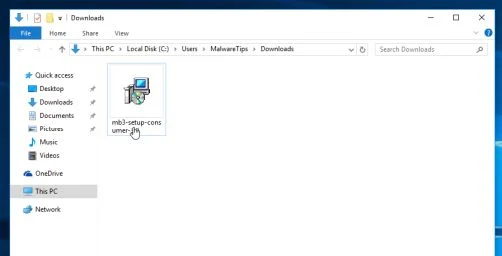
Download MalwarebytesFree official installer. Your download starts right away. - When Malwarebytes has finished downloading, double-click on the “mb3-setup-consumer” file to install Malwarebytes Anti-Malware on your computer.
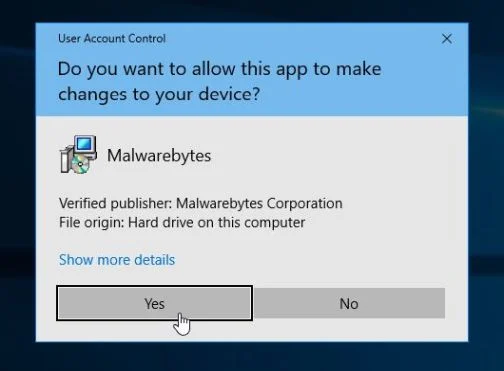
You may be presented with an User Account Control pop-up asking if you want to allow Malwarebytes to make changes to your device. If this happens, you should click “Yes” to continue with the installation.
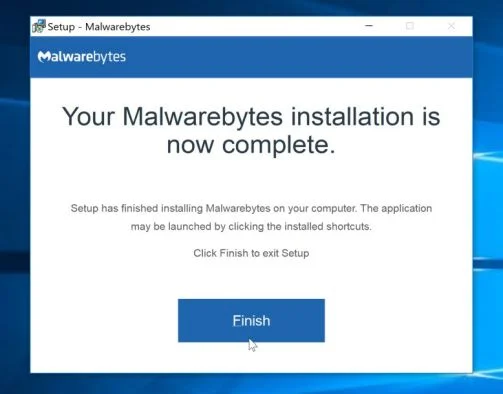
- When the Malwarebytes installation begins, you will see the Malwarebytes Setup Wizard which will guide you through the installation process.
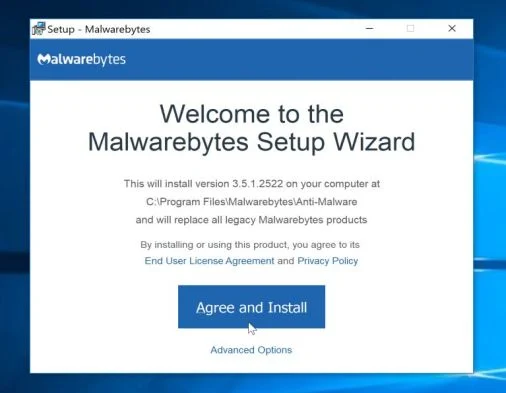
To install Malwarebytes Anti-Malware on your machine, keep following the prompts by clicking the “Next” button.
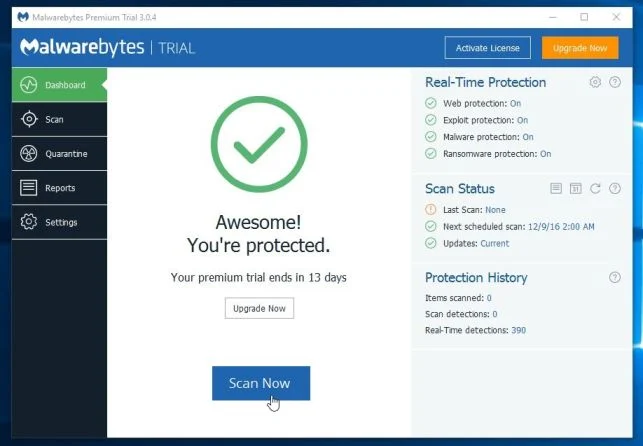
- Once installed, Malwarebytes will automatically start and update the antivirus database. To start a system scan you can click on the “Scan Now” button.
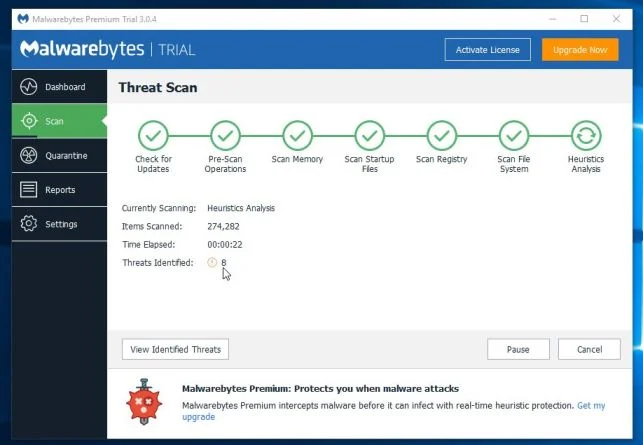
- Malwarebytes Anti-Malware will now start scanning your computer for malicious programs.
This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.
- When the scan has completed, you will be presented with a screen showing the malware infections that Malwarebytes Anti-Malware has detected.
To remove the malicious programs that Malwarebytes has found, click on the “Quarantine Selected” button.
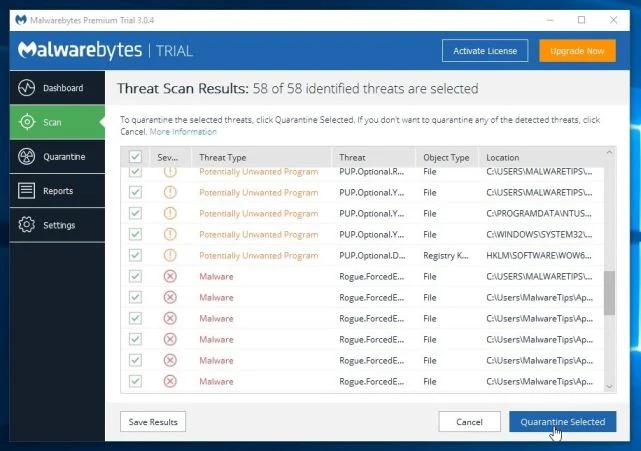
- Malwarebytes Anti-Malware will now quarantine all the malicious files and registry keys that it has found.
To complete the malware removal process, Malwarebytes may ask you to restart your computer.
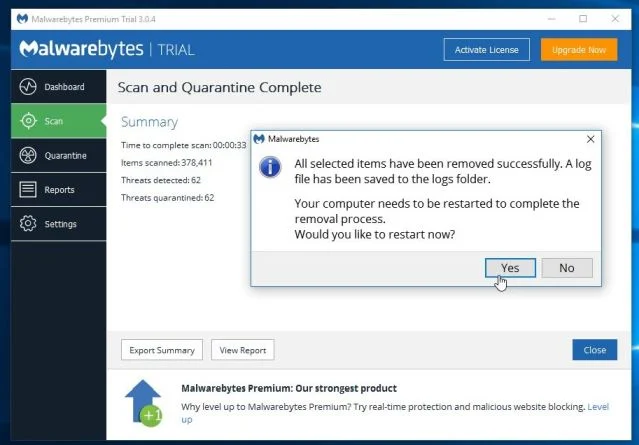
When the malware removal process is complete, you can close Malwarebytes Anti-Malware and continue with the rest of the instructions.
STEP 4: Double-check for malicious programs with HitmanPro
HitmanPro can find and remove malware, adware, bots, and other threats that even the best antivirus suite can oftentimes miss. HitmanPro is designed to run alongside your antivirus suite, firewall, and other security tools.
- You can download HitmanPro from the below link:
Download HitmanProOfficial Sophos download. Free scan, free 30-day trial to remove threats. - When HitmanPro has finished downloading, double-click on the “hitmanpro” file to install this program on your computer.
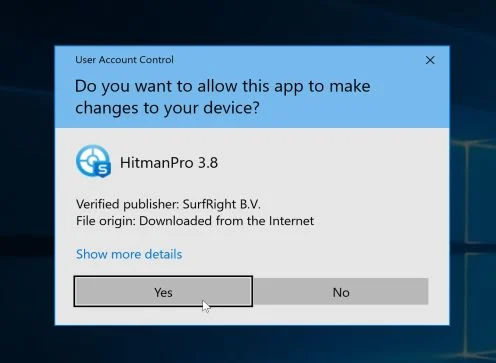
You may be presented with an User Account Control pop-up asking if you want to allow HitmanPro to make changes to your device. If this happens, you should click “Yes” to continue with the installation.
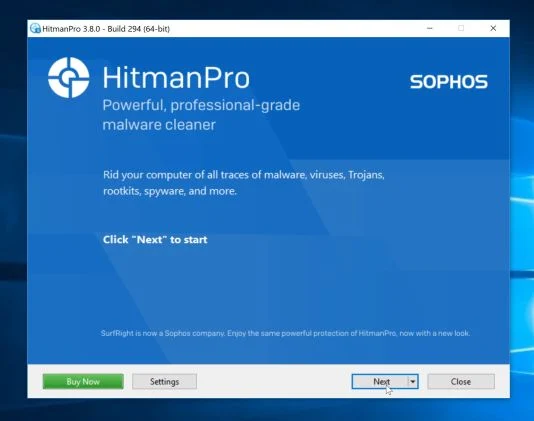
- When the program starts you will be presented with the start screen as shown below. Now click on the Next button to continue with the scan process.
- HitmanPro will now begin to scan your computer for malware.
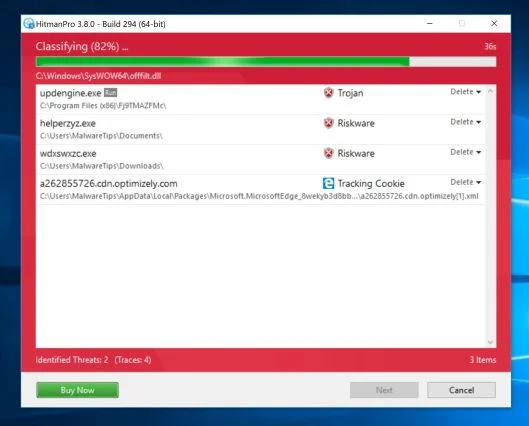
- When it has finished it will display a list of all the malware that the program found as shown in the image below. Click on the “Next” button, to remove malware.
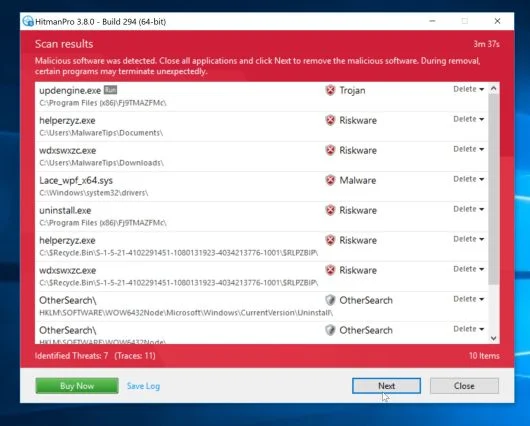
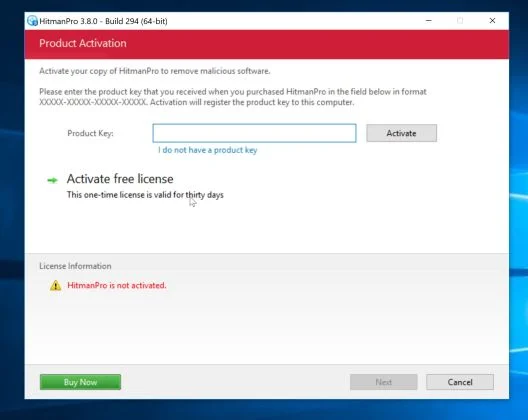
- Click on the “Activate free license” button to begin the free 30 days trial, and remove all the malicious files from your computer.
When the process is complete, you can close HitmanPro and continue with the rest of the instructions.
(OPTIONAL) STEP 5: Use Zemana AntiMalware Portable to remove ZeroAccess rootkit
This step should be performed only if your issues have not been solved by the previous steps.
- You can download Zemana AntiMalware Portable from the below link:
Download Zemana AntiMalwareOpens the download page in a new tab. - Double-click on the file named “Zemana.AntiMalware.Portable” to perform a system scan with Zemana AntiMalware Free.
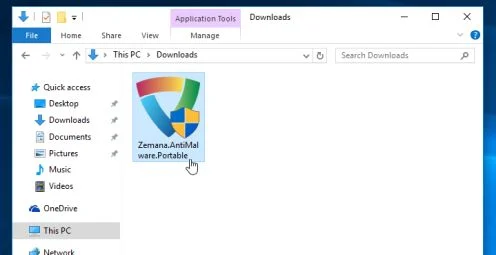
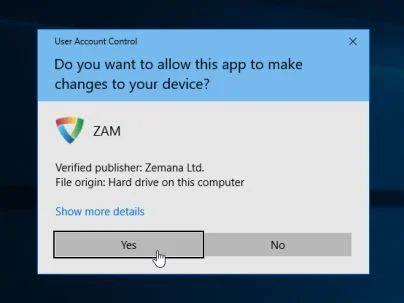
You may be presented with a User Account Control dialog asking you if you want to run this program. If this happens, you should click “Yes” to allow Zemana AntiMalware to run.
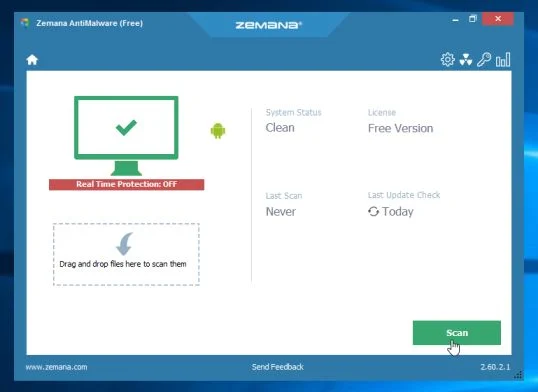
- When Zemana AntiMalware will start, click on the “Scan” button to perform a system scan.
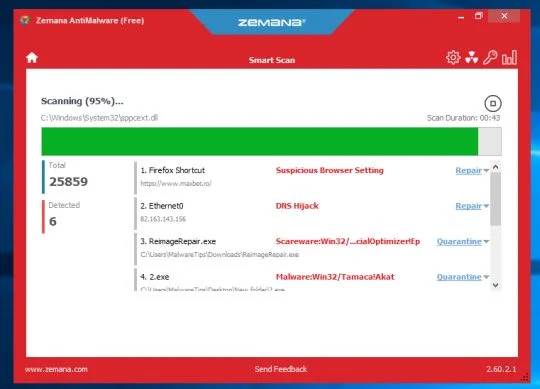
- Zemana AntiMalware will now scan your computer for malicious programs. This process can take up to 10 minutes.
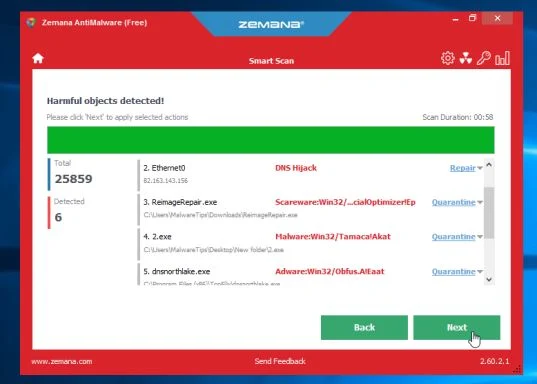
- When Zemana has finished finished scanning it will show a screen that displays any malware that has been detected. To remove all the malicious files, click on the “Next” button.
Zemana AntiMalware will now start to remove all the malicious programs from your computer.

Join the discussion
52 commentsShare your experience or ask a question about this article.
Your progress
Did these steps help?
Let us know how the guide worked for you.
Describe what you see and the step you reached. Keep passwords and other private information out.
Discussion
Hello, I just discovery that I have that trojan in my computer.
But I ill erase all partition of my disk, create new partitions and format using ntfs. And then install a clean windows on it.
my question is, Ill this clean my computer? Or the trojan ill still be there? I ill erase all the partitions of the disk.
I cant found a tutorial about it, only about cleaning, but i prefer the formal, after all i dont have anythin interessing on the computer, i just play games on it.
can pls someone help?
Thx a lot
In reply to Igor
Yes,if you do a reformat you’ll get rid of this virus…. Good luck! :)
In reply to Stelian Pilici
Thx so much for the quick tip. I ill format today, and after ill run the malware scanner.
And post here if it solved completly.
Btw i lost my mcaffe CD is the internet security suite 2012, i have to install the microsoft security essencials, is it anygood? or maybe i have to buy a new securiy suite?
In reply to Igor
Hello Igor,
After you format ,their is no need for you to run Combofix as this is a hard-core tool which needs to be used only in extreme cases…. You can scan with all the other software if you really like. :)
As far as your real time protection goes,I advise to avoid McAfee and Microsoft Security Essetianls because this two products aren’t that great when it comes to zero day malware prevention!
Below you can find some quick suggestions:
Free – Avast 7 Free version or COMODO Internet Security
Paid : Norton Internet Security 2012,Avast Internet Security 7,G-DATA Internet Security 2012 or ESET Smart Security 5.
Anyway ,you should really start a thread in our Security Configuration forum as you need to build a layered security config: http://malwaretips.com/Forum-Security-Configuration-Wizard
Also it would very good if you took the time and read this article that I’ve wrote: http://malwaretips.com/blogs/how-to-easily-avoid-pc-infections/ .. If you follow it,then we’ll never meet again in this conditions:)
In reply to Stelian Pilici
Thx so much for your help.
I ill try the Comodo Internet Security the free version, and the malwarebits free too.
The browser that i use is chrome, can you pls add some addons to use?
I check the forum you said, the the information is to complicated for me, lol.
Thx again