

The MalwareTips app
Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
- Home Screen access
- Optional push alerts
- Your community
You're ready to explore.Explore what's new
Installation instructions
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Keep up with your conversations
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Comodo Internet Security 2025 does not contain RANSOMWARE (bypass, infection and lost of files)

F
ForgottenSeer 114717
Yeah? So what? It is not different than any other security software that misses ransomware. Those other security software miss it way more often than Comodo.
All the videos showing bypasses would be meaningful if 1) the Comodo products had revenue that paid for full-time dedicated development teams and 2) anybody was stating "Comodo is unbeatable" (which there is nobody saying that).
The only credible thing to do is show how Comodo performs against every other security software using many hundreds of samples. If it prevents infection at a greater rate, then it is protecting better than those that do worse. If it does not prevent infection at a greater rate, then it is protecting worse than those that do better.
"One-off" POC and similar videos of Comodo failing to do this or that apply only to the specific POC or malware used. They should not be used to extrapolate or generalize about Comodo - which I think there is a big push here by some that have an agenda against Comodo.
Comodo is software. Software has problems. Comodo software is further problematic because it has no revenue and therefore no dedicated development team.
A few POCs and an undetected ransomware are not very enlightening. Nobody ever expects any software to be 100% bullet proof. Nobody here at MT or elsewhere has ever said that Comodo is unbeatable or not free of weaknesses & vulnerabilities.
But the videos are great click-bait.

Sephirothnight
Level 1
hello,
ah yes... Well who to turn to? it's getting complicated thanks for this video.
ah yes... Well who to turn to? it's getting complicated thanks for this video.
Last edited by a moderator:

vitao
Level 5
Added a caption and description in French.hello,
ah yes... Well who to turn to? it's getting complicated thanks for this video.
Good afternoon.
Listen, I don't know if it's about resorting to something different. It depends on each individual. I particularly continue to use CIS because it protects me as I need and these exploits are specific to it. So far, no malware using this type of technique to affect CIS has reached my computers, so I'm sticking with it. When that happens, we will always have options like Kaspersky Free or Panda Free.

Last edited by a moderator:


Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
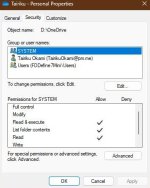
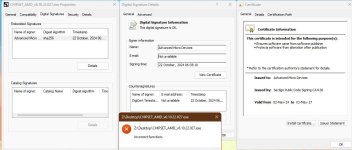
This proves that blindly relying on digital signatures (like SmartAppContol does), even the most trustworthy like DigiCert, can be a mistake. I wonder if denying System permissions would help?
It is different. It uses DLL hijacking = benign application + malicious DLL.
The executed application is truly benign. The POC would work even if the benign application was unsigned, but sufficiently popular.


Last edited:
Well, unsigned apps are not allowed on my PC, by default. Not to mention that ramdisk fails to run signed admin apps in desktop/downloads folder as well.The POC would work even if the benign application was unsigned, but sufficiently popular.

Code:
reg add "HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System" /v "ValidateAdminCodeSignatures" /t REG_DWORD /d "1" /fAttachments
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Well, unsigned apps are not allowed on my PC, by default. Not to mention that ramdisk fails to run signed admin apps in desktop/downloads folder as well.
Code:reg add "HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System" /v "ValidateAdminCodeSignatures" /t REG_DWORD /d "1" /f
It is a good policy.
However, it allows running unsigned applications (only elevation is blocked). It also can be bypassed via UAC bypass.
A stronger way is using SUA and ConsentPromptBehaviorUser = 0.
Do you use another tweak to disable running unsigned apps?
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
This proves that blindly relying on digital signatures (like SmartAppContol does), even the most trustworthy like DigiCert, can be a mistake.
Smart App Control (SAC) can block the attack from the video. The benign application will be allowed, but the malicious DLL will be blocked.
The advantage of SAC (and WDAC) is that it can block DLL hijacking.
Of course, in targeted attacks the attacker can use valid certificate to sign the DLL and then the attack can pass by SAC.
Several, still this is under the assumption that the user would run a random exe, I would never. I just wonder whether the ransomware works without system rights, wannacry sure fails.Do you use another tweak to disable running unsigned apps?
As far as I know ransomware uses SeDebugPrivilege/SeTcbPrivilege, basically system permissions, so without it, it is can not do anything. It is easy to change permissions, but it does not, thus far.
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
It is more complicated. Using SeDebugPrivilege/SeTcbPrivilege is necessary for high privileged operations, but most ransomware attacks will continue without privilege escallation. Simply, the ransomware will skip hight privileged actions and encrypt the files in UserSpace.Several, still this is under the assumption that the user would run a random exe, I would never. I just wonder whether the ransomware works without system rights, wannacry sure fails.
As far as I know ransomware uses SeDebugPrivilege/SeTcbPrivilege, basically system permissions, so without it, it is can not do anything. It is easy to change permissions, but it does not, thus far.
vitao
Level 5
does cis has any sort of compatibility with it, via config files etc? or am i dreaming?It is a good policy.
However, it allows running unsigned applications (only elevation is blocked). It also can be bypassed via UAC bypass.
A stronger way is using SUA and ConsentPromptBehaviorUser = 0.
Do you use another tweak to disable running unsigned apps?
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Those tweaks cannot be done from CIS.does cis has any sort of compatibility with it, via config files etc? or am i dreaming?
The tweak posted by TairikuOkam is well known, but it will prevent many installations of unsigned applications.
Code:
reg add "HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System" /v "ValidateAdminCodeSignatures" /t REG_DWORD /d "1" /fThat tweak can block the original Comodo bypass in your first video. The malware was unsigned, so it will fail to run instead of elevate. If it would be a ransomware, the execution could be continued in the sandbox with standard rights (no escape).
vitao
Level 5
thanks for the tip bt
thanks for the tip but i am not going to mess with reg when cis should solve its problems. but its a nice trick. i wonder if one day microsoft will turn on defender sandbox by default and improve it...Those tweaks cannot be done from CIS.
The tweak posted by TairikuOkam is well known, but it will prevent many installations of unsigned applications.
Code:reg add "HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System" /v "ValidateAdminCodeSignatures" /t REG_DWORD /d "1" /f
That tweak can block the original Comodo bypass in your first video. The malware was unsigned, so it will fail to run instead of elevate. If it would be a ransomware, the execution could be continued in the sandbox with standard rights (no escape).
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
i wonder if one day microsoft will turn on defender sandbox by default and improve it...
Defender sandbox is not auto-containment of unrecognized applications. It is used only to protect some Microsoft Defender processes against exploitation/tampering.

Run Microsoft Defender Antivirus in a sandbox environment - Microsoft Defender for Endpoint
This article describes how to run Microsoft Defender Antivirus in a sandbox to further strengthen against tampering.
learn.microsoft.com
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Such improvement would be impossible, it would be a completely different sandbox. You probably thought about improving Windows Sandbox:thats why i said "improve it"...
Recently browsing
Members who viewed this thread in the last 5 minutes
You may also like...
-

-
-
 Setup Idea Pretty Good PC Security Regimen
-

-
 Serious Discussion Deep Research: McAfee GTI, JTI, Artemis and Other Technologies Explained