

The MalwareTips app
Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
- Home Screen access
- Optional push alerts
- Your community
You're ready to explore.Explore what's new
Installation instructions
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Keep up with your conversations
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Hot Take Comodo is discontinued product its officialy said by Xcitium Staff
- Thread starter Nikola Milanovic
- Start date
Comodo
53 Replies
8,276 Views


They do offer but you have to eneable that in settings in ur profileRight off the bat, the product offers no phishing/web protection, which is how most of the attacks start. Someone correct me if I’m wrong…?
I personally do not use the web filter nor DLP Monitoring i use all of these which are on and of course Xcitium Valkyrie
Web protection did not work in CIS for browsers other than Firefox.Right off the bat, the product offers no phishing/web protection, which is how most of the attacks start. Someone correct me if I’m wrong…?
You should not rely on that feature.
@Trident for VirusScope by default its eneabled to automatically quarantine a file i turned that off so i can see the alert but you can leave it on if you want
Do not show popups alerts is automatically on for VirusScope in Xcitium but i turned that off on my profile in endpoint manager
@Trident my bad actually 1 year of Xcitium AEP for 1 device is 64 $
Also notifications sounds are turned off by default on Xcitium so if you want notifications you will need to eneable them on endpoint manager at ur profile
Last edited by a moderator:
F
ForgottenSeer 114717
If my recall is correct, Valkyrie was originally built bottom-up by Comodo back in the day (as CAMAS).@bazang are you aware how Valkyrie works, all these analysis, are they proprietary or is Xcitium using third-party APIs (like Sophos, Avira)?
The infos is buried somewhere on that old Comodo forum. I never venture there.
Now Valkyrie is called Xcitium Cloud VerdictIf my recall is correct, Valkyrie was originally built bottom-up by Comodo back in the day (as CAMAS).
The infos is buried somewhere on that old Comodo forum. I never venture there.
CAMAS(Comodo Automated Malware Analysis System)If my recall is correct, Valkyrie was originally built bottom-up by Comodo back in the day (as CAMAS).
The infos is buried somewhere on that old Comodo forum. I never venture there.
F
ForgottenSeer 114717
Perhaps Xcitium will be better, but I have my doubts. One can only go by the historical record until proven otherwise.
It is software. All software has bugs. This is just an inherent fact of software.
It is software. All software has bugs. This is just an inherent fact of software.
you mean every antivirus has bugs?Perhaps Xcitium will be better, but I have my doubts. One can only go by the historical record until proven otherwise.
It is software. All software has bugs. This is just an inherent fact of software.

I am not near as smart as you guys, but my thermometer reads room temperature... I think the headstone will read, "here lays Comodo" a once promising product.
Just so sad.
Just so sad.
Take from it what you will.

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
It would be interesting to find evidence on the Comodo, MT, and Wilderssecurity forums if some users were infected.
From known tests (SE Labs), it follows that Comodo Antivirus at default settings can be compromised in targeted attacks:
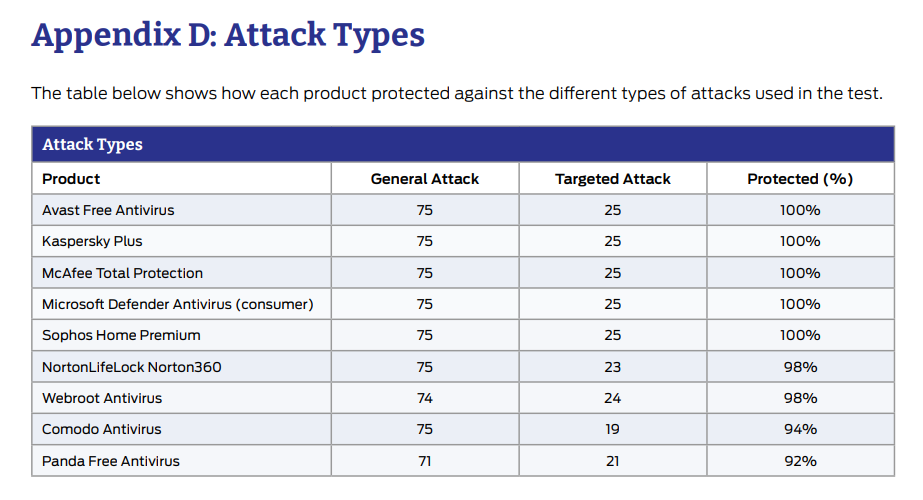
This probably follows from two settings:
From known tests (SE Labs), it follows that Comodo Antivirus at default settings can be compromised in targeted attacks:
This probably follows from two settings:
- Contained files in Comodo AV can call home (it is blocked in CIS).
- Script Analysis settings are not hardened.


Shadowra
Level 42
Verified
Top Poster
Content Creator
Malware Tester
Well-known
High Reputation
Forum Veteran
I don't understand Xcitium's desire to abandon Comodo.
Comodo is a brand known by everyone, but Xcitium? Apart from the Pro version, I didn't know it before...
For me, Comodo has every interest in keeping CIS, but why not make a smooth transition to Xcitium as the name
Comodo is a brand known by everyone, but Xcitium? Apart from the Pro version, I didn't know it before...
For me, Comodo has every interest in keeping CIS, but why not make a smooth transition to Xcitium as the name
F
ForgottenSeer 114717
Nobody pays for Comodo. At least with Xcitium there is a prospect of some enterprises paying for it.I don't understand Xcitium's desire to abandon Comodo.
Comodo is a brand known by everyone, but Xcitium? Apart from the Pro version, I didn't know it before...
Free software is not sustainable, not even by a one man shop.
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Let's look closely at the Melih advertisement:
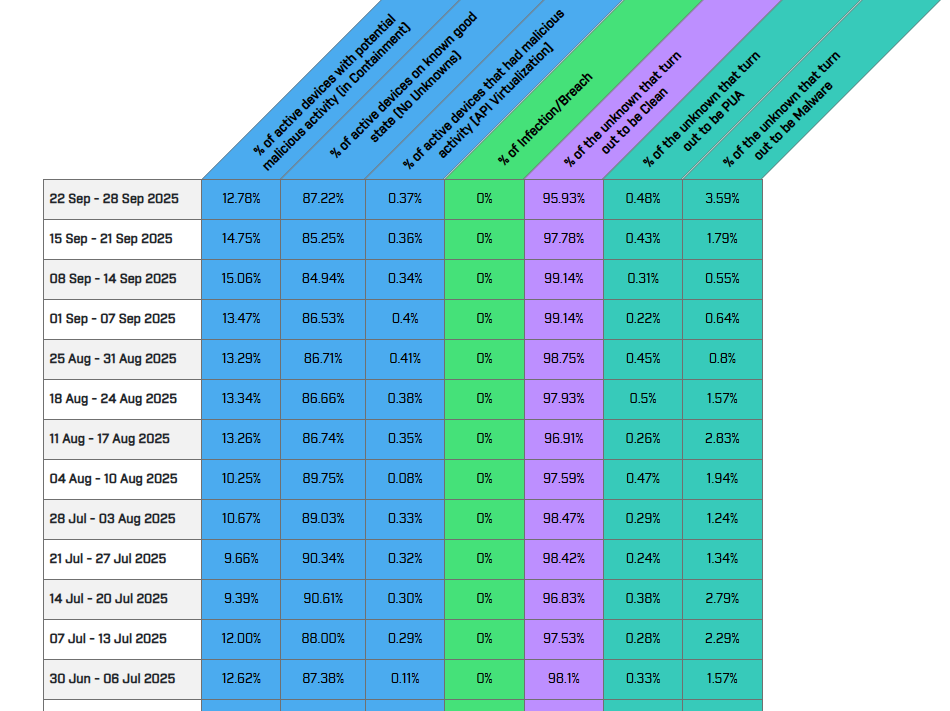
We can see that the first two columns always sum up to 100%. (Contained + No unknowns). However, this skips some possible attacks via abusing or exploiting Trusted files (DLL hijacking, exploits, Office Macros, ClickFix methods with some LOLBins, etc.). So, this advertising should not be taken seriously in targeted attacks. It simply shows that Comodo Sandbox is very strong.
The SE Labs are probably more reliable for Comodo than for popular AVs. Those tests are conducted with a several-hour delay, which is not significant for Comodo (a few-hour EXE malware will be contained), but is important for popular AVs. For example, some few-hour EXE malware can compromise popular AVs in the wild but will be detected in the test.
Currently, there are no convincing tests that could reliably compare the overall effectiveness of Comodo vs. popular AVs.
However, in businesses, the combination of better bug management, anti-phishing, web filtering, email protection, and other next-gen features may give popular business AVs an advantage over Comodo.
Last edited:
F
ForgottenSeer 123960
Love how you make us read a 16-page dissertation before dropping this important fact. Is this for home users or corporate lawyers?Currently, there are no convincing tests that could reliably compare the overall effectiveness of Comodo vs. popular AVs.
However, in businesses, the combination of better bug management, anti-phishing, web filtering, email protection, and other next-gen features may give popular business AVs an advantage over Comodo.

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Love how you make us read a 16-page dissertation before dropping this important fact. Is this for home users or corporate lawyers?
The "16-page dissertation" and some other threads already include this fact. For example, I posted there:
If CIS was maintained at the high level, we should have detailed information about fixed and unfixed bugs.
Better than Comodo bug management (1) does not mean "no bug management" by Comodo (2). The first can be confirmed; the second is untrue.
Last edited:

Abnormal
Level 1
what is the best comodo alternative ?
a free 0day / hips / zero trust software ?
comodo has a lot of bugs / vulnerbilities which render it unsecure against targeted attacks
in the old days we Had Online armor / outpost / private firewall /zone alarm
i see a big opportunity for Online armor comeback
a free 0day / hips / zero trust software ?
comodo has a lot of bugs / vulnerbilities which render it unsecure against targeted attacks
in the old days we Had Online armor / outpost / private firewall /zone alarm
i see a big opportunity for Online armor comeback
Last edited:
Recently browsing
Members who viewed this thread in the last 5 minutes


