


The MalwareTips app
Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
- Home Screen access
- Optional push alerts
- Your community
You're ready to explore.Explore what's new
Installation instructions
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Keep up with your conversations
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
MRG Effitas Consumer Assessment & Certification Programme 03/2026
- Thread starter Parkinsond
- Start date
Security Statistics and Reports
14 Replies
1,682 Views
Thread details
- Disclaimer
This test shows how an antivirus behaves with certain threats, in a specific environment and under certain conditions.
We encourage you to compare these results with others and take informed decisions on what security products to use.
Before buying an antivirus you should consider factors such as price, ease of use, compatibility, and support. Installing a free trial version allows an antivirus to be tested in everyday use before purchase.
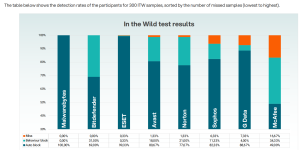

Outstanding Results by Malwarebytes.
As expected sub par results by Gdata, Mcafee and Sophos. Gdata's dual engine got defeated by BD's single engine.

Yeah, BD's behavior blocker shone more than G-Data's in this case.Outstanding Results by Malwarebytes.
As expected sub par results by Gdata, Mcafee and Sophos. Gdata's dual engine got defeated by BD's single engine.
Malwarebytes tends to do well in mrg-effitas's test compared to others, which is a bit surprising to me.
The as Avast/AVG/Norton in AVC tests.Malwarebytes tends to do well in mrg-effitas's test compared to others, which is a bit surprising to me.
Dual engine without B powerful behavioral analysis.Gdata's dual engine got defeated by BD's single engine.
McAfee, MD, Panda; all are cloud-based, all take time to react.McAfee's results were surprisingly poor.

https://forums.malwarebytes.com/topic/334863-zkm-stealer-2600-java-ratinfostealer/ Meanwhile malwarebytes unable to detect Java malware which has been reported to FBI
I do not believe MBAM is good; I use either MD or AVG after removing all component including web protection, just leaving file shield, behavioral shield, and ransomware shield.Oh NO! All the Av's I like are useless, formatting now, starting again, cannot get my head around to using Mbam though so I disagree with the findings
That is why consistency is key. Bitdefender and Kaspersky have made such a solid reputation with their strong showing in thousands of independent tests that one anomaly can be discounted. Meanwhile Malwarebytes 100 percent detection here seems like an anomaly itself.Oh NO! All the Av's I like are useless, formatting now, starting again, cannot get my head around to using Mbam though so I disagree with the findings

'One swallow does not a summer make' - As with all things in life, AV's & tests need to be taken in aggregate, & decisions made for our own needs, one size don't ft all I reckon, interesting though - If someone asks I will give my opinion as to how to set a system up including router internet type OS/ etc but I never feel that I can say this is what you should use because it works for me, ask 20 users on here the ideal way you might get 20 different replies & all are correct at least for them.
Last edited:

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Interesting Real-World test, especially when we look at missed samples.
MCAfee .................... 50 / 300
G Data ...................... 22 / 300
Sophos ..................... 19 / 300
Norton ..................... 4 / 300
Avast ........................ 4 / 300
In the standard Real-World tests, most AVs miss only a few samples per 300 total samples, and by using statistical methods, those that miss 0-3 samples must usually be awarded (Level 1 certificate).
The criteria of the Level 1 certificate seem to be artificial (statistically unsupported).
The Level 2 certificate looks reasonable (can be supported by statistics).
The only thing I find interesting regarding MRG Effitas tests is displaying behavioral-related protection, similar to AVLab tests which display the post-execution detection rate.Interesting Real-World test, especially when we look at missed samples.
MCAfee .................... 50 / 300
G Data ...................... 22 / 300
Sophos ..................... 19 / 300
Norton ..................... 4 / 300
Avast ........................ 4 / 300
In the standard Real-World tests, most AVs miss only a few samples per 300 total samples, and by using statistical methods, those that miss 0-3 samples must usually be awarded (Level 1 certificate).
The criteria of the Level 1 certificate seem to be artificial (statistically unsupported).
The Level 2 certificate looks reasonable (can be supported by statistics).
No i find something even more pleasing about them.The only thing I find interesting regarding MRG Effitas tests is displaying behavioral-related protection, similar to AVLab tests which display the post-execution detection rate.
If an ITW ransomware or wiper sample executes successfully and results in permanent loss of user files or irreversible system damage, the product cannot be
certified, regardless of its overall block rate.
AVLab has one more advantage; it reports time to remediation which can make a difference in mitigating the file encryption and/or data exfiltration, regardless of post-execution detection by behavioral analysis.No i find something even more pleasing about them.
Recently browsing
Members who viewed this thread in the last 5 minutes


