Why are you even asking this? The batch file is not malicious, so I don't see why it would matter if any antivirus does or doesn't detect it.Would ESET and detect the script too or they would flag it as safe.


Your community, one tap away.
Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
iPhone & iPad
- Open MalwareTips in Safari and tap Share. You may need to open the Page Menu first.
- Choose Add to Home Screen. If it is not listed, use Edit Actions to add it.
- Keep Open as Web App enabled if shown, then tap Add.
Android
- Open MalwareTips in Chrome or another browser that supports app installation.
- Open the browser menu and look for Install app, Install and create shortcut, or Add to Home screen.
- Choose Install and confirm. Wording varies by browser.
Desktop
- Chrome: use the install icon in the address bar, or the menu under Cast, save and share.
- Edge: open the menu, then More tools, Apps and Install this site as an app.
- Safari on Mac: choose Share or File, then Add to Dock. Firefox on Windows: look for the web apps button in the address bar.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
Installation is optional. Your notification settings stay under your control.
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Hot Take Kaspersky and various other AVs can't detect simple ransomware script
- Thread starter Ahmed Uchiha
- Start date
- Featured
General Security Discussions
84 Replies
10,510 Views

the new malware:If none of that came true, a new name will be created
Testing for AV capability to discriminate FP.Why are you even asking this? The batch file is not malicious, so I don't see why it would matter if any antivirus does or doesn't detect it.

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
It is an open question whether scripts are required on home users' machines.
It would be better to allow scripting and some administrative tasks only from a special troubleshooting account.
It would be better to allow scripting and some administrative tasks only from a special troubleshooting account.

Malware is not malware just because of the actions it performs, but because these actions are not clearly announced and mentioned. If the renaming behaviour is clearly announced and explained, users download the script with the renaming intention in mind.
If Bitdefender wants to detect and block every micro action remotely resembling ransomware, that’s Bitdefender’s vision for their products, nothing wrong.
But it is not an industry-wide practice and standard that everyone should follow.
If Bitdefender wants to detect and block every micro action remotely resembling ransomware, that’s Bitdefender’s vision for their products, nothing wrong.
But it is not an industry-wide practice and standard that everyone should follow.
F
ForgottenSeer 114717
Microsoft trends towards "Disinclined to permit script execution on home users' machines" to categorically and definitively solve the problem of users generally not knowing what they're doing. In other words, protecting users from themselves - and by extension via the internetworks - everyone else.It is an open question whether scripts are required on home users' machines.
Microsoft agrees, but then there's that troublesome "User Rights" and "Users Want to Use Stuff" dinosaur thinking that infects and poisons the minds of the majority.It would be better to allow scripting and some administrative tasks only from a special troubleshooting account.
And then expecting users to do a little bit of work - like switch accounts or a flipping a few Booleans - well... that's, that's... that's just downright anti-consumer. It's wrong! It's harmful! It causes generational and group trauma! It's anti-hooman!!
Last edited by a moderator:
It is like deciding to stay home because I cannot look right and left before crossing street.If Bitdefender wants to detect and block every micro action remotely resembling ransomware, that’s Bitdefender’s vision for their products, nothing wrong
Sacrificing usability for blind security.
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
It is like deciding to stay home because I cannot look right and left before crossing street.
Sacrificing usability for blind security.
Scripts were not introduced for home users, but for Administrators in Enterprises. Why must home users suffer because of this?
Similarly, why restrict drivers by introducing zebras? Why should drivers and car manufacturers care about creatures that use feet?
Last edited:
Home users need scripts for coding and other reasonsScripts were not introduced for home users, but for Administrators in Enterprises. Why must home users suffer because of this?
Similarly, why restrict drivers by introducing zebras? Why should drivers care about creatures that use feet?

Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
Home users need scripts for coding and other reasons
They do not.
It is like saying that swimmers need muddy waters to swim.

Even if 0.01% home users would like to use scripts for a specific purpose, it does not mean that allowing scripts for the remaining 99.99% is a reasonable idea.
Edit.
Playing with scripts is OK. The tiny percentage of home users who would like scripting might buy the extended Windows version with enabled scripting or play with scripts on the troubleshooting account.
Last edited:

Haha. Usually it's the security researcher who first found the unique malware/attack have the privilege to give it a fancy name.the new malware:
Ahmed Uchiha
Level 2
I would like to know what will smart app control Classify this script will it allow this script to run or it will block it
If it has the motw, it will be blocked regardless of its behavior.I would like to know what will smart app control Classify this script will it allow this script to run or it will block it

Shadowra
Level 42
Verified
Top Poster
Content Creator
Malware Tester
Well-known
High Reputation
Forum Veteran
I would like to know what will smart app control Classify this script will it allow this script to run or it will block it
Your script isn't doing anything... Why are you insisting on seeing it blocked? I don't understand...
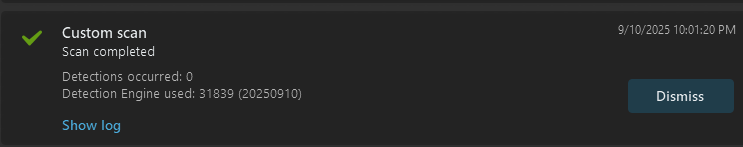
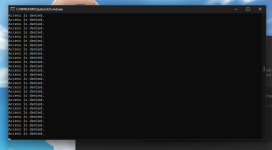
Launched with ESET, access denied even though I launched it in administrator mode...
Windows isn't stupid enough to let a poor BATCH file destroy the system... x)
You have Windows folder protection, etc., but nothing has been touched, not even my files.
SAC is blocking any potentially "dangerous" extension with motw (reg, lnk, vbs, vbe, cmd, ps1, bat, ....) and for lnk even if does not have motw but the file of the shortcut has.Windows isn't stupid enough to let a poor BATCH file destroy the system
Shadowra
Level 42
Verified
Top Poster
Content Creator
Malware Tester
Well-known
High Reputation
Forum Veteran
SAC is blocking any potentially "dangerous" extension with motw (reg, lnk, vbs, vbe, cmd, ps1, bat, ....) and for lnk even if does not have motw but the file of the shortcut has.
Yes, indeed, it works like an Anti-Exe (such as AppGuard or Avast! Free's Smart mode).

On my K, I am using it like this: I uncheck the box "Do not trust digitally signed applications" and also disable "Trust Kaspersky Security Network (KSN)". I leave K very restricted, so that any new or unknown file that tries to run will be blocked and will not have any access to the internet.Yes, indeed, it works like an Anti-Exe (such as AppGuard or Avast! Free's Smart mode).

fwiw sidenote, I just visited my Ludite brother out of town, he had NEVER updated his android, did that for him, also unlocked, so I asked him to pick PIN, set lock, and it autolocked after I we parted, and he threw a sh!tfit.And then expecting users to do a little bit of work - like switch accounts or a flipping a few Booleans - well... that's, that's...
Andy Ful
From Hard_Configurator Tools
Verified
Honorary Member
Top Poster
Developer
Well-known
Forum Veteran
SAC is blocking any potentially "dangerous" extension with motw ...
It is not as good as blocking any potentially dangerous file type.
SAC can only block about 10% of such file types (the most dangerous ones).
It is "incredibly effective" at home, but would not be effective against targeted attacks in Enterprises.
Yes, SRP through WHHL has a wider spectrum and does not need MOTW.It is not as good as blocking any potentially dangerous file type.
SAC can only block about 10% of such file types (the most dangerous ones).
It is "incredibly effective" at home, but would not be effective against targeted attacks in Enterprises.
Recently browsing
Members who viewed this thread in the last 5 minutes
You may also like...
Continue exploring the conversation.
-
 61Hot Take Proper malware testing methodology
- General Security Discussions
- Started by Divine_Barakah
-
 4Serious Discussion Machine Learning for Malware Detection (KasperskyLab)
- General Security Discussions
- Started by Andy Ful
-
F
4
- News Archive
- Started by ForgottenSeer 116559
-
 3Serious Discussion The Necessity of Simulating the Full Malware Infection Chain for Security Suite Testing
- General Security Discussions
- Started by harlan4096
-
 7AV-TEST Cybersecurity: Defense Against the Latest Attacking Techniques in the ATP Test (February 2024)
- Security Statistics and Reports
- Started by Gandalf_The_Grey