I think it does more than that:It starts an installation and closes


Open MalwareTips from your Home Screen or desktop. Follow discussions, find answers and pick up where you left off.
If you cannot find an install option, update your browser or use its bookmark option to keep MalwareTips close.
After installation, open the app and sign in. Enable push notifications in Preferences if you want alerts. On iPhone and iPad, push requires a Home Screen web app and iOS or iPadOS 16.4 or later.
Sign in to manage notificationsInstallation is optional. Your notification settings stay under your control.
I think it does more than that:It starts an installation and closes

But it is malicious.Okay, so perhaps that is why Comodo isn't classifying it as malicious..

You learn something every day. Didn't know that.Agent refers to any malware that is not significant enough to have its own family. It is an industry standard. The file has dual detection, one is Check Point proprietary and one is Kaspersky’s feeds.


Yep, but since it does all this in 2/3sec, I don't have time to look with my little eyes xD
Intelix is good.
How do you know comodo has no analyst's? CuriousBut it is malicious.
Because I’ve seen what people like @struppigel can do with files and in not extremely long time. There is no way analyst will not see the suspicious extension that is being added.How do you know comodo has no analyst's? Curious
Maybe they actually didn't. That's the sad state of affairs today. It's so unbelievable.Because I’ve seen what people like @struppigel can do with files and in not extremely long time. There is no way analyst will not see the suspicious extension that is being added.
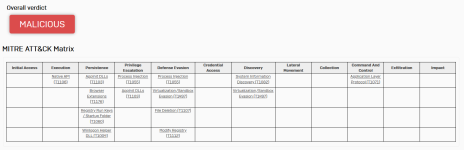
There is InstallExtension.exe which adds the suspicious browser extension.
True. I love it so far. Fast static and dynamic analysis and a detailed but yet pretty compact report.Intelix is good.
And it's free. I remember them charging for it before.True. I love it so far. Fast static and dynamic analysis and a detailed but yet pretty compact report.
You don't say.

@danb might be a bit off-topic but it took me a minute to discover the “Get Second Opinion” link on the screenshot. Maybe having it underlined or blue or something might help

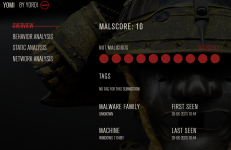
I've used Yomi before, nothing special really...View attachment 276680
Stumbled upon Yomi the other day and the sample got a 10 out of 10 malscore rating. Anybody heard of it?

Because I’ve seen what people like @struppigel can do with files and in not extremely long time. There is no way analyst will not see the suspicious extension that is being added.

Members who viewed this thread in the last 5 minutes