

A polished DHL update says a parcel is already moving and provides a tracking number, service level, and expected arrival. Nothing initially looks dramatic.
The danger sits behind the tracking button. Understanding what changes after that click is the key to recognizing this particular email.
Overview
A Detailed Shipping Update That Leads Somewhere Unexpected
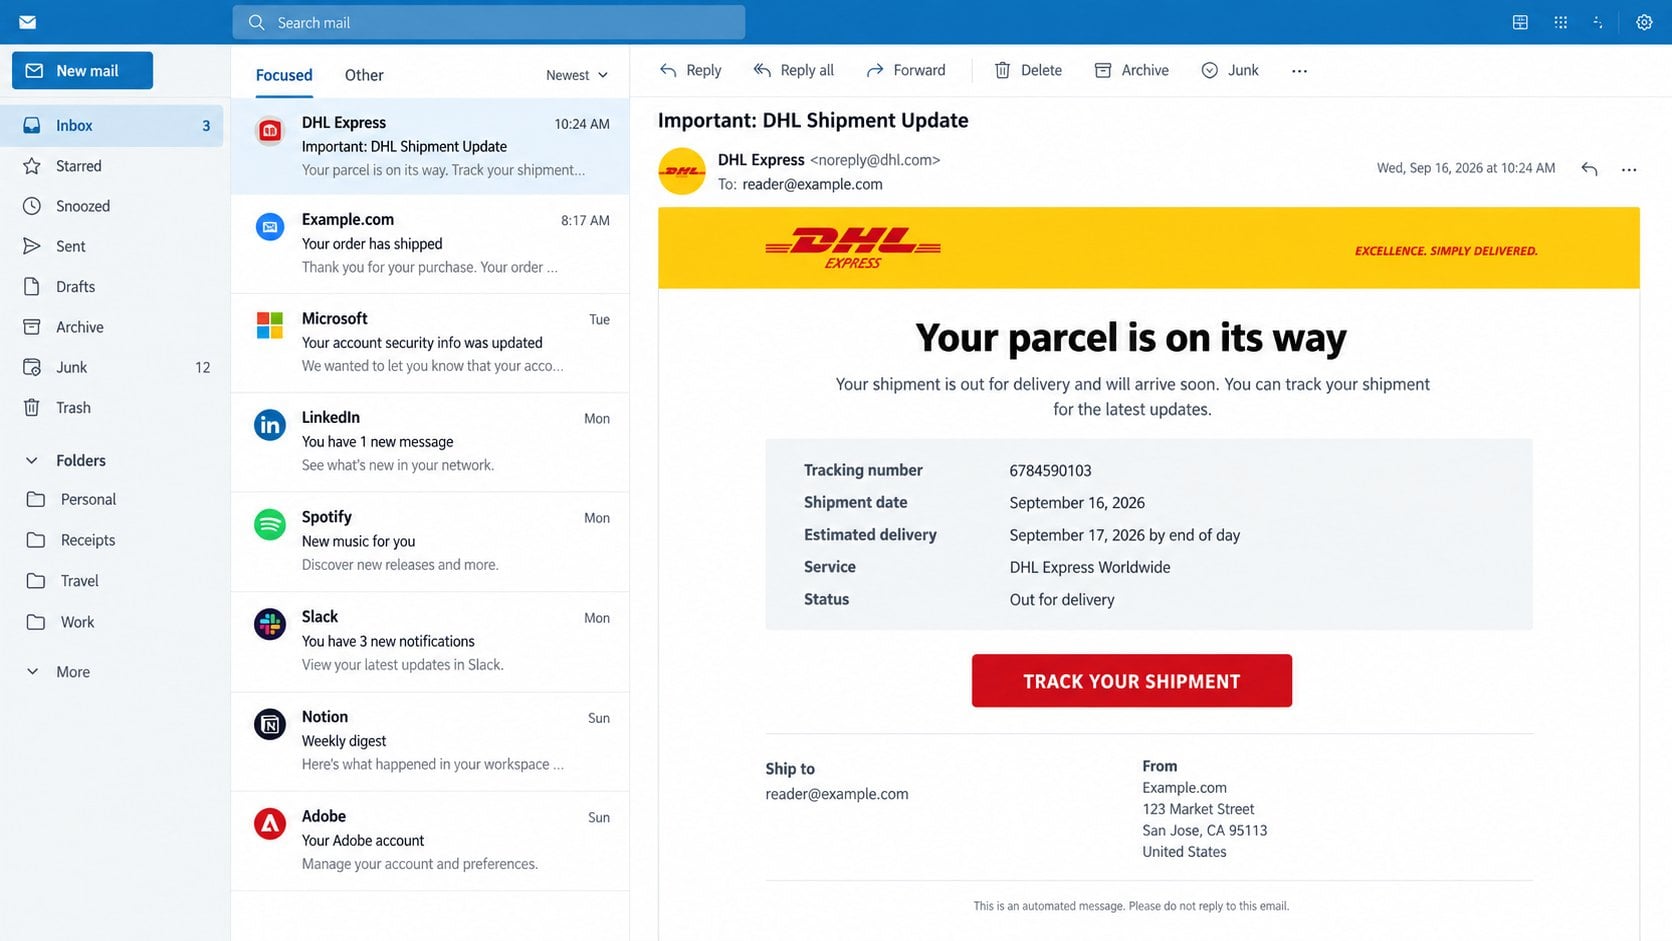
The DHL Express Parcel Is On Its Way email scam copies the format of a routine tracking notification. Its subject reads “Important: DHL Shipment Update.”
The sample displays tracking number 6784590103 and a shipment time of 9/16/2026 at 5:07:05 p.m. It promises delivery on September 17.
It also names DHL Express Worldwide as the service. Those logistics details create the impression that the message came from an established carrier system.
DHL did not send the analyzed email. Its recognizable name and visual identity were copied by an unrelated phishing operation.
This Version Seeks an Email Password, Not a Delivery Fee
Many parcel scams demand a small redelivery payment. This campaign takes a different route after the recipient clicks “TRACK YOUR SHIPMENT.”
- The email supplies professional-looking shipment information.
- The button suggests it will open tracking events.
- The link instead reaches an unrelated hosted page.
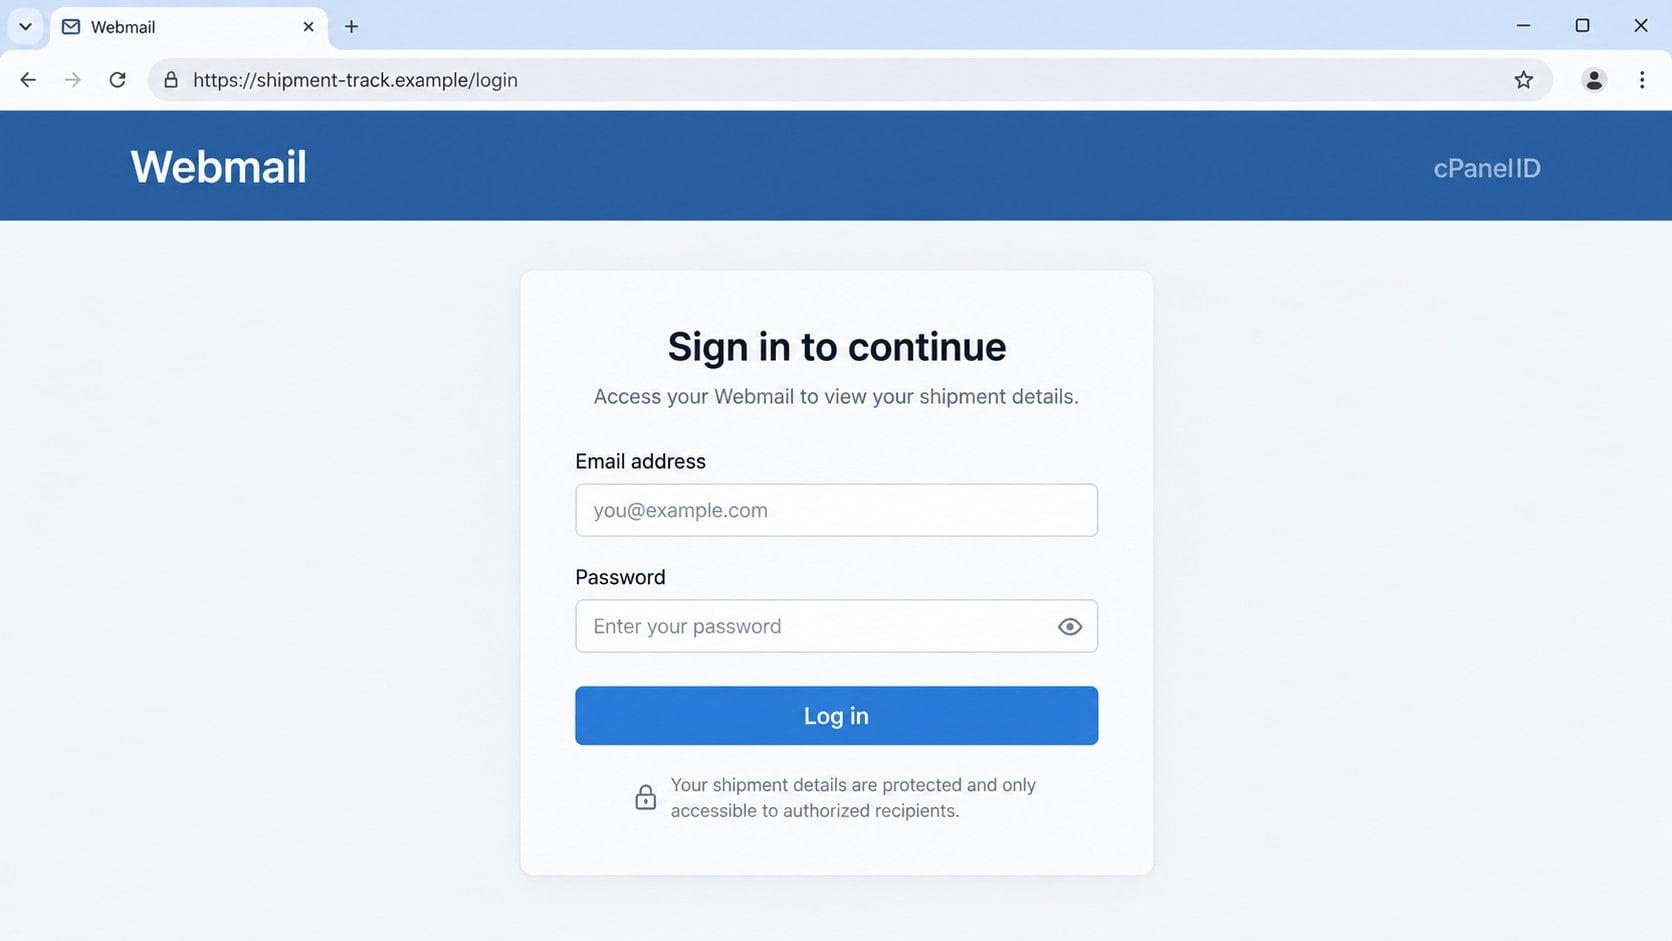
- A generic Webmail screen appears rather than a DHL tracker.
- The form carries a cPanelID label and requests email credentials.
- No legitimate reason connects mailbox authentication with parcel tracking.
That abrupt shift is the campaign’s clearest warning. A courier can show public tracking details without receiving the password to your inbox.
The Email’s Real Value to an Attacker
A working email login can reveal purchase receipts, travel plans, personal records, and password-reset messages. It can also expose which services the victim uses.
Work accounts may contain customer correspondence, supplier invoices, and shared-document invitations. One captured password can therefore support several forms of fraud.
Merely receiving or previewing the notice does not mean those outcomes occurred. The crucial event is credential submission on the counterfeit page.
No evidence from this sample shows a charge, subscription, or automatic malware installation. Its central mechanism is deceptive password collection.
How the DHL Express Parcel Is On Its Way Email Scam Works
Step 1: Realistic Logistics Data Establishes Credibility
The email provides a shipment number, date, service tier, and delivery estimate. Specific data makes the notice feel generated from an actual courier database.
Recipients rarely memorize every tracking number. If they expect any parcel, they may accept the unfamiliar digits as belonging to a recent purchase.
A next-day estimate encourages immediate curiosity. The reader wants to confirm timing, delivery instructions, or the sender before the package arrives.
Fraudsters can invent all these fields cheaply. Their presence matters only when the number produces matching results on DHL’s independently opened tracker.
Step 2: The Tracking Button Conceals an Unrelated Address
The “TRACK YOUR SHIPMENT” button looks like the natural route to more detail. Its visible label does not reveal the real destination.
The examined link used a page hosted through website-building infrastructure. Hosting on a known platform does not mean the platform endorses the content.
Criminals frequently abuse legitimate hosting tools because pages can be created quickly and delivered over HTTPS. The service provider is also a victim of misuse.
Before clicking, preview the full address. An authentic shipment tracker should stay within a domain controlled by the carrier or its disclosed partner.
Step 3: Parcel Tracking Becomes a Webmail Login
Instead of tracking events, the destination displays a generic Webmail form. It asks for an email address and password under a cPanelID-style header.
There is no operational reason for DHL to authenticate against a recipient’s mailbox. The courier already has whatever contact address the shipper provided.
The phishing page may claim shipment details are protected. That explanation tries to make an unrelated password request sound like privacy protection.
Real sensitive deliveries may require a tracking number, postcode, account session, or delivery code. They do not require disclosure of an email password.
Step 4: The Form Collects Credentials Without Authenticating Anything
A counterfeit login does not need to communicate with the mail provider. It can send every typed value to a collection endpoint controlled by criminals.
The visitor may see a spinning indicator, invalid-password warning, or blank page after submission. These responses can disguise successful data theft.
Repeating the attempt with another password makes the situation worse. The operator may record every entry, including credentials for additional accounts.
A later redirect to a real DHL page can create false reassurance. The first form may already have transmitted the password before the redirect occurred.
Step 5: The Stolen Inbox Is Examined and Monetized
Attackers often look for password resets, online receipts, bank correspondence, and active business discussions. Search functions make valuable messages easy to locate.
They may add forwarding rules or recovery details to preserve access. Quiet persistence can be more useful than immediately sending obvious spam.
A compromised business address can impersonate an employee. Suppliers may accept altered payment instructions because the request appears inside a genuine conversation.
Consumer inboxes support account takeovers and targeted delivery scams. Existing order emails reveal which parcel stories will sound believable next time.
Step 6: The Campaign Rotates Links and Shipment Numbers
Once a hosted page is removed, another can replace it. Tracking numbers, delivery dates, and sender addresses can also be changed automatically.
Blocking a single domain remains useful, but recipients need a durable rule: tracking should never require the credentials to an unrelated service.
The safest response is to ignore the button and enter the tracking number directly on the carrier’s official site.
If the number is invalid or describes another parcel, report the message rather than searching for alternative links it supplies.
How to Verify the DHL Shipment
Find the Shipment in Your Purchase Records
Open the retailer’s application, marketplace account, or original order confirmation. Identify which carrier actually received the parcel and copy its tracking number.
Compare that number with 6784590103 and the claimed dates. A genuine update should correspond with an order you recognize.
If the parcel came from a person or business contact, confirm it through an existing conversation or known telephone number.
Use DHL’s Tracker From a Clean Starting Point
Type DHL’s known website address or use its official application. Do not reuse the link embedded in the suspicious email.
Enter the tracking number and compare origin, progress, service, and expected delivery. Avoid sharing sensitive data merely to see basic tracking events.
An invalid number is a strong warning. A valid number can still be copied from another shipment, so verify that its details fit your order.
Inspect the Sender and the Hidden Link
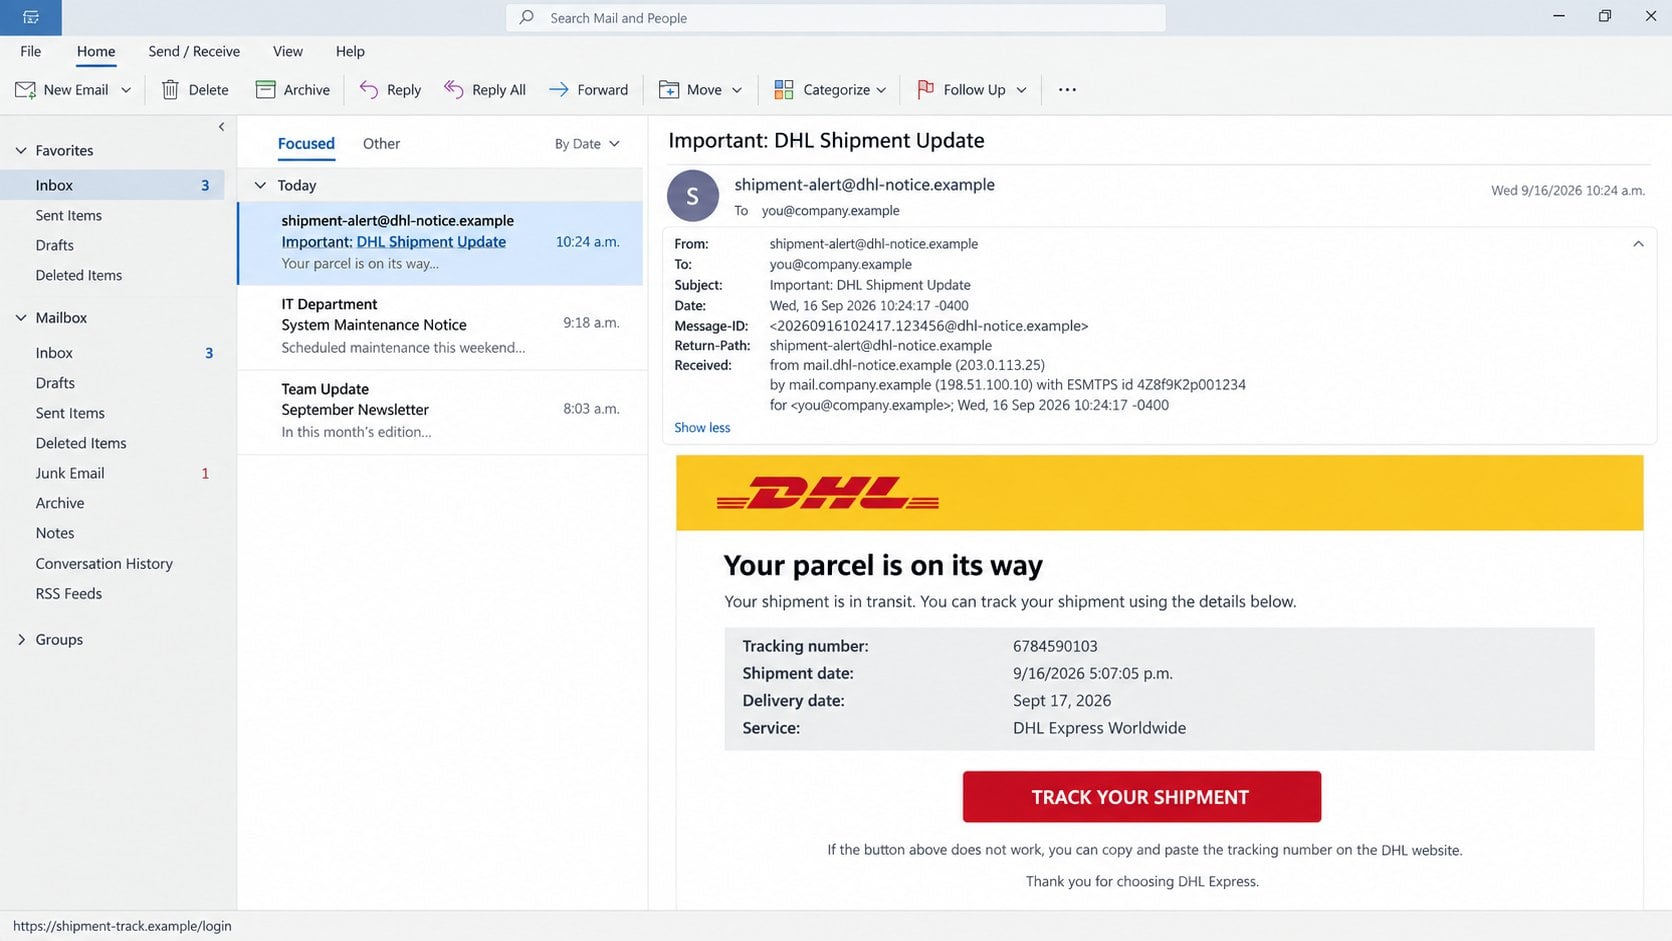
Expand the email header and read the complete sender address. The display name and yellow branding can be reproduced without DHL access.
Hover over the button to reveal where it leads. Website-builder or unrelated domains are not transformed into courier properties by copied artwork.
Check for redirects if your security tools expose them. The first visible address may forward through several services before reaching the phishing form.
Evaluate the Requested Credential
Ask what the requested password controls. A mailbox password grants access to email, not a shipping record.
If a page reached from tracking asks for Webmail, cPanel, Microsoft, Google, or other unrelated credentials, close it immediately.
For unusual deliveries, contact DHL using support details obtained independently. A genuine representative can discuss tracking without learning your email password.
What to Do If You Fell Victim to the DHL Express Parcel Email Scam
Move quickly if you submitted credentials. Email accounts can be abused quietly, so the absence of immediate spam does not mean the password stayed safe.
- Leave the counterfeit login and retain the message.
Close its tab without another attempt. Keep the original email so investigators can inspect headers, hosting details, and link destinations.
Report a workplace incident before deleting anything. Internal teams may need to trace who else received the same campaign.
- Replace the mailbox password using the real provider.
Navigate from a saved bookmark or trusted account portal. Choose a unique password unrelated to the value entered on the fake form.
Update any account that reused it. Begin with services capable of resetting other passwords or moving money.
- Revoke sessions and review account security.
Sign out unfamiliar devices, remove unknown authorized applications, and confirm recovery email addresses and telephone numbers.
Turn on multifactor authentication. Save recovery codes somewhere protected and never type a code into a parcel-tracking page.
- Search for hidden mailbox changes.
Inspect forwarding addresses, rules, filters, delegates, and automatic replies. Remove unauthorized settings after preserving evidence required by your organization.
Review sent and deleted folders for impersonation. Notify affected contacts through a separate channel if suspicious messages left the account.
- Verify the real parcel without the phishing email.
Check the retailer’s order page and DHL’s independently opened tracker. The fraudulent message does not necessarily mean a genuine shipment is compromised.
Contact the merchant if delivery data was exposed. Ask whether any address or redirection request changed in the real order.
- Examine the device if the page triggered a download.
The reviewed route targeted passwords, yet a modified campaign could distribute files. Run Malwarebytes if software, an archive, or a document opened.
AdGuard can help block known phishing and malicious advertising addresses. Continue checking domains because no filter identifies every newly created page.
- Report the impersonation.
Mark the message as phishing and notify DHL through its official reporting route. Provide the suspicious sender and destination without sharing your new credentials.
If financial or identity abuse followed, contact the relevant institution and fraud authority. Maintain a timeline of alerts, calls, and remediation steps.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why Detailed Tracking Data Is Not Proof
Specificity feels expensive to produce, yet shipment templates make it trivial. A scammer can populate thousands of messages with unique-looking numbers and timestamps.
The details mainly keep the recipient focused inside the email. Once attention centers on the delivery estimate, the destination behind the button receives less scrutiny.
Even a valid tracking number would not authenticate the sender. Tracking information can be copied, guessed, leaked, or collected from public shipment pages.
The requested action exposes the deception more reliably. Webmail authentication has no logical role in public parcel tracking.
Separate the two systems mentally. DHL manages the shipment, while your email provider manages the inbox. Neither needs the other service’s password.
That simple boundary remains useful even when logos, dates, and shipping terminology look flawless.
Tracking Information Versus Account Authentication
Standard shipment tracking is designed to share limited logistics information. It does not grant access to the recipient’s private email account.
A carrier may ask for a postcode, shipment number, or delivery code. Each value relates directly to the parcel rather than an outside service.
Webmail credentials control messages, contacts, and recovery links. Their power greatly exceeds anything needed to display a delivery scan.
The mismatch remains suspicious even if the page uses a professional cPanel layout. cPanel manages hosting and mail, not DHL parcel movement.
Corporate users may sign into internal delivery applications through approved single sign-on. That route should begin from a known company or identity-provider domain.
If the organization genuinely protects shipment data, its IT team can confirm the workflow. Do not let the email define its own authentication rules.
Public tracking numbers sometimes reveal limited status information. Treat them as moderately sensitive, but never exchange a stronger credential merely to view them.
A sender who already knows your email can prefill it on a fake form. That small personalization should not be mistaken for secure account recognition.
Saved passwords may also create false confidence by offering autofill. Password managers usually consider domains, so an unexpected absence of autofill is informative.
Do not force autofill or copy the password manually when the manager refuses. First compare the current hostname with the genuine provider.
Organizations can block lookalike pages, but rapidly changing hosts remain challenging. Employee reporting helps defenders identify and remove new campaign infrastructure.
The practical rule is simple: parcel data belongs in a carrier tracker, while mailbox secrets remain exclusively with the email provider.
Frequently Asked Questions
Is tracking number 6784590103 genuine?
It appeared in the analyzed phishing message. Verify any number independently on DHL’s official tracker and confirm that its details match your actual order.
Why did the tracking button open Webmail?
Because the message was designed to steal email credentials. DHL tracking does not require a cPanelID or the password protecting your inbox.
Are DHL or the hosting platform responsible?
No. The campaign impersonates DHL and abuses third-party website infrastructure. Recognizable brands and hosting services do not endorse the fraudulent page.
Can reading the email install malware?
The analyzed route depended on a deceptive link and login form. Risk increases if you submit information or open unexpected files, not from ordinary reading alone.
What if I entered an incorrect password?
Change it if it matches any real account or reveals a predictable variation. Phishing operators can retain every attempted value, not only working credentials.
Should I contact the sender listed in the email?
No. Use DHL’s independently located support route or contact the retailer. Replying can confirm your address is active and continue the manipulation.
The Bottom Line
The DHL Express Parcel Is On Its Way email turns believable tracking details into a path toward a generic Webmail password form. That credential request exposes its purpose.
Track parcels from your order account or DHL’s official route. If you submitted a password, secure the inbox, inspect its settings, and warn affected contacts promptly.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.