


A parcel placed on hold can disrupt travel, work, or an expected gift. Delivery-themed messages exploit that everyday uncertainty with remarkable efficiency.
This warning resembles a standard shipping update at first glance. The route behind its red button tells a very different story.
Overview
An Urgent Shipment That Requires Attention
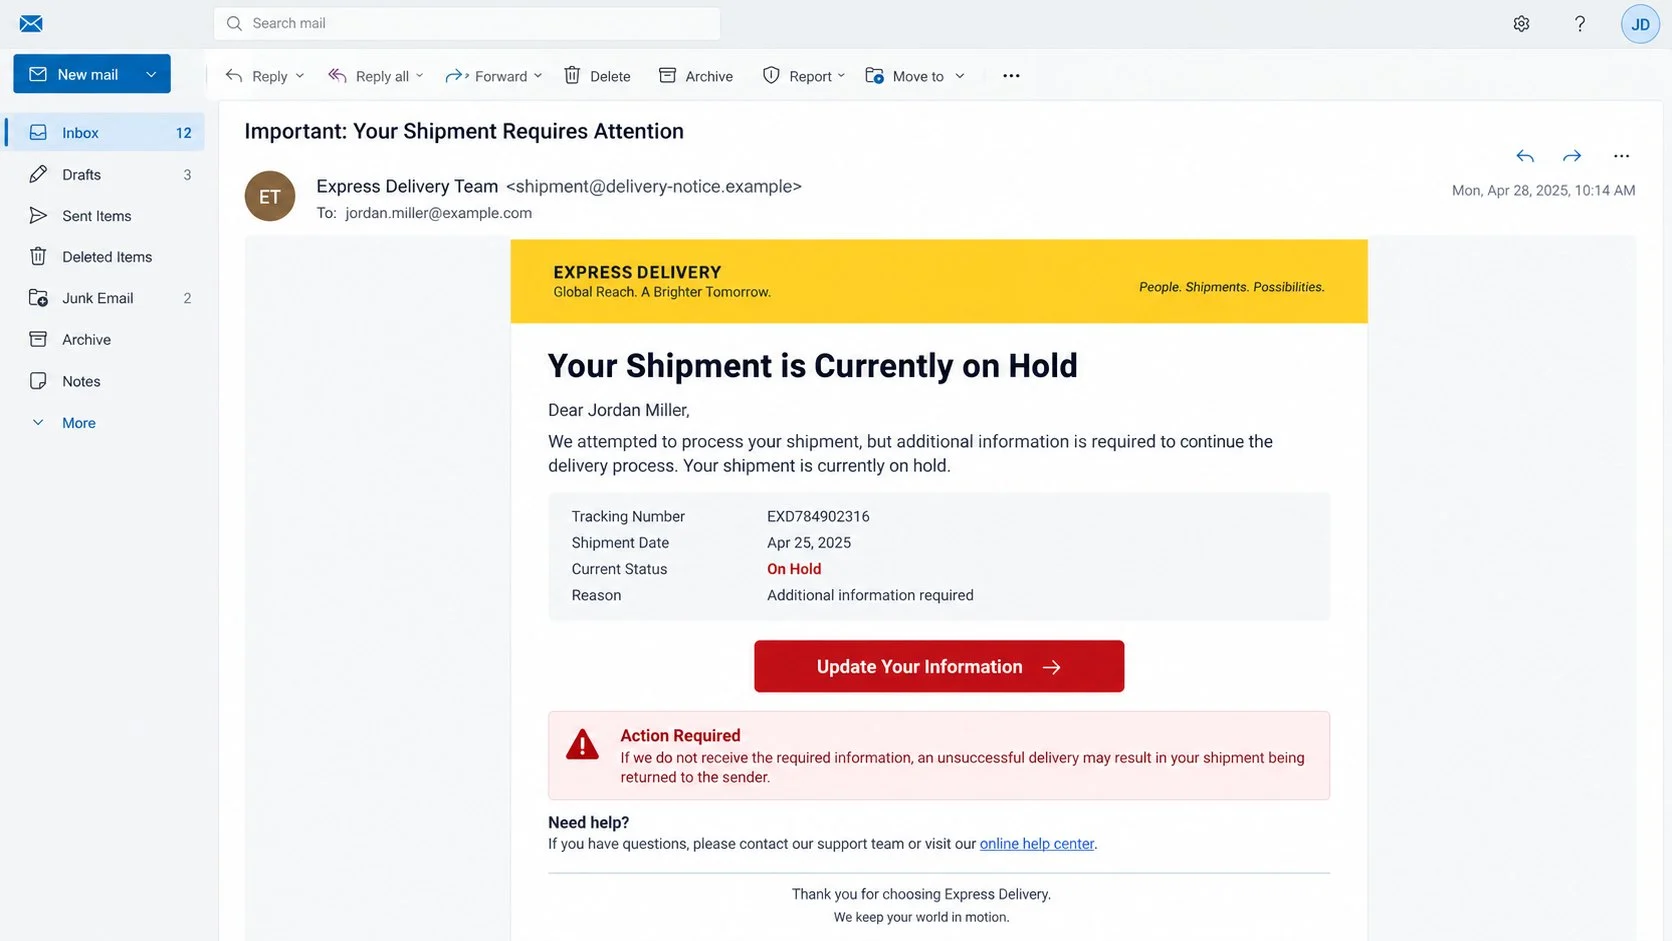
The DHL Express Shipment Is on Hold email scam claims that a delivery cannot continue until the recipient updates missing information.
Its subject says, “Important: Your Shipment Requires Attention.” The message uses the familiar yellow-and-red language associated with express delivery.
A central button labeled “Update Your Information” appears to offer a quick solution. Beneath it, the email warns about a return to sender.
The campaign relies on timing rather than personalization. Many recipients have recently ordered something, making an unexplained shipment seem plausible.
The Destination Is Not a Carrier Portal
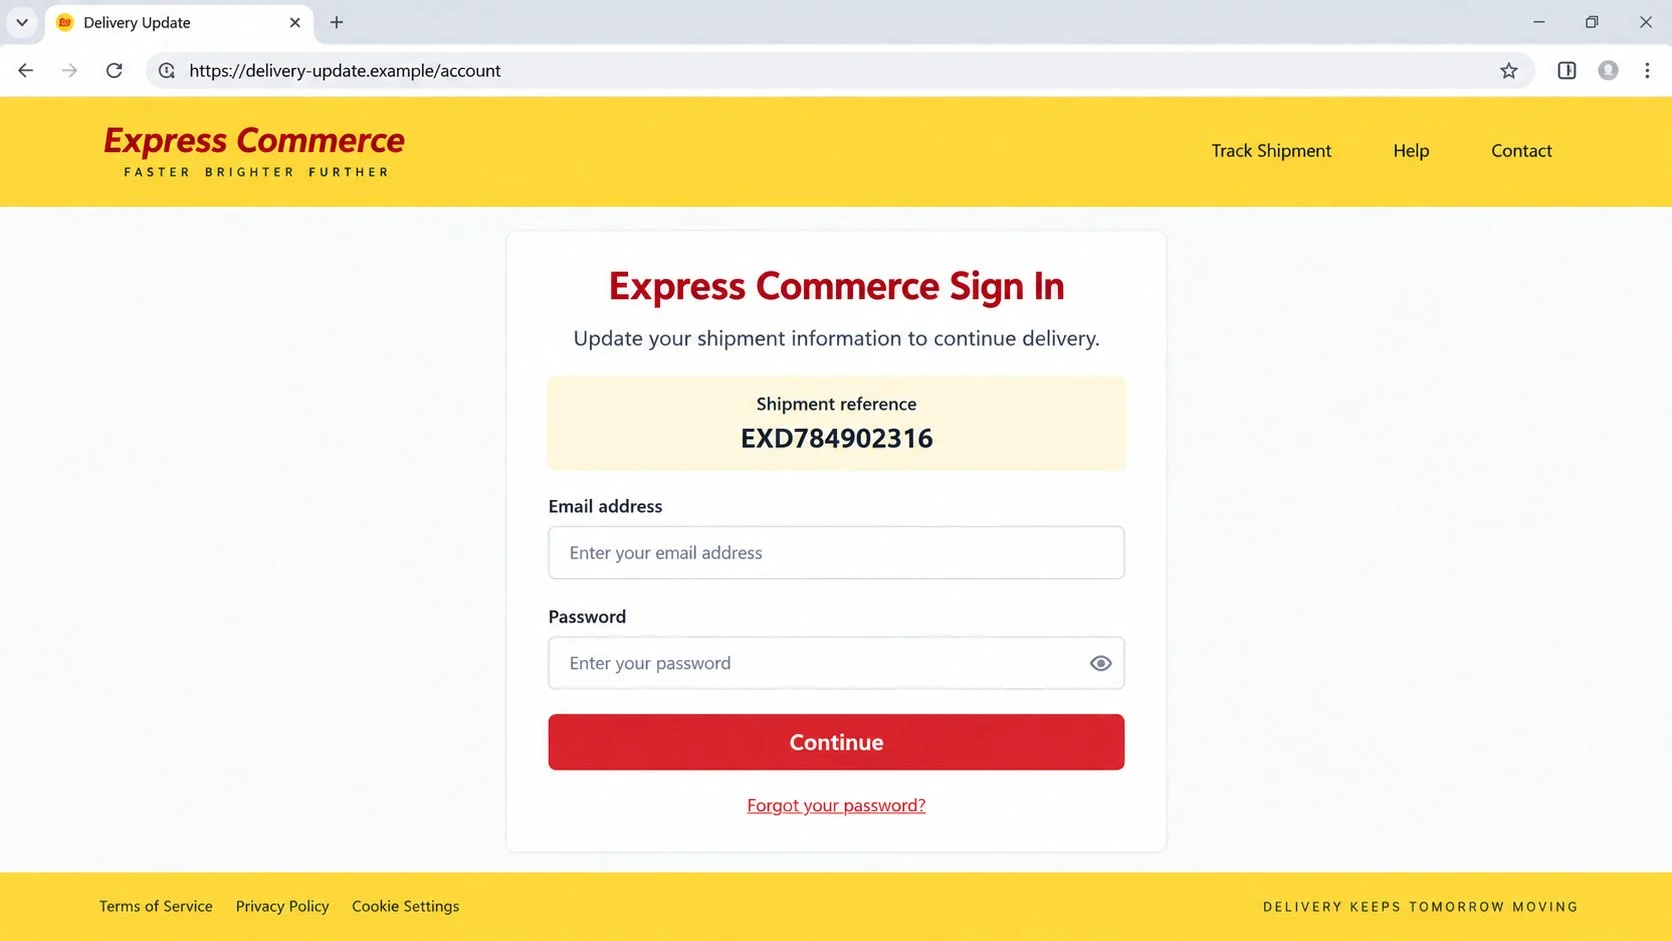
The analyzed button led to an unrelated website, not an official DHL property. It displayed a counterfeit Express Commerce sign-in page.
That page requested an email address and password. A carrier does not need a customer’s mailbox password to correct a delivery address.
- The sender address has no verified relationship with DHL.
- The message provides no independently confirmed shipment history.
- The action button hides a third-party destination.
- A delivery update unexpectedly becomes an email login.
- The form requests credentials unrelated to parcel routing.
- Return-to-sender language creates artificial urgency.
- The recipient is pushed away from normal tracking channels.
DHL is a legitimate global carrier and has no role in this phishing operation. Its identity is being misused to make the request believable.
Why a Mail Password Interests Delivery Phishers
Email access contains order confirmations, receipts, shipping addresses, retailer accounts, and reset messages. It can reveal genuine parcels and customer details.
With that information, an intruder can produce more persuasive follow-ups. The next notice may mention a real merchant, destination, or purchase.
Business DHL accounts can expose shipment records and contact data. If criminals also capture carrier credentials, they may inspect or redirect active deliveries.
The primary observed goal is password theft. No legitimate information update occurs, even if the page eventually redirects to an authentic carrier website.
How the DHL Express Shipment on Hold Scam Works
Step 1: A Broad Delivery Notice Reaches Many Inboxes
The campaign is distributed widely because it does not require knowledge of a specific purchase. Delivery activity is common enough to create frequent coincidences.
Someone awaiting a parcel reads the subject differently from someone expecting nothing. The first person may assume the message concerns their real order.
The wording avoids identifying a merchant or package contents. Missing details are framed as the reason the recipient must open the update page.
This design lets the same email target households, online sellers, procurement staff, and businesses receiving regular shipments.
Step 2: Carrier Colors and Shipping Language Create Recognition
Yellow, red, and logistics terminology establish familiarity before the recipient evaluates the sender. Visual recognition often happens faster than address inspection.
The message may include a tracking-like number, delivery date, or generic status table. Those elements can be invented entirely.
A genuine tracking number should work when entered manually on the carrier’s established website. It should not exist only inside an emailed interface.
Branding is easily copied. The sender domain, link ownership, and independent tracking result provide more meaningful evidence.
Step 3: A Return Threat Makes Delay Feel Costly
The email says an unsuccessful delivery may cause the shipment to be returned. That consequence creates a reason to act before checking the message carefully.
Scammers choose this pressure because it seems ordinary. Carriers do return undeliverable packages, so the threat avoids sounding fantastical.
However, genuine delivery exceptions appear in the official tracking record. A carrier should not require an unrelated mailbox login to prevent a return.
The recipient can safely ignore the button while verifying the parcel through the seller, tracking application, or carrier website.
Step 4: The Update Button Leaves the Official Network
The visible action promises a simple information correction. The underlying URL points toward infrastructure controlled by the phishing operator.
In the observed campaign, the domain had no legitimate connection to DHL. The page used delivery language to disguise that ownership problem.
Some routes pass through advertising redirects, compromised sites, or cloud platforms first. The final destination may change according to location or browser.
Security filters can therefore see a different page than the victim. Redirect chains also make manual investigation harder.
Step 5: A Delivery Correction Becomes a Credential Request
The counterfeit page asks visitors to sign in with an email address and password before updating the shipment.
That transition is logically wrong. A carrier may request a tracking number, postal code, or carrier-account login, but not a third-party email password.
The page may still look polished. Professional typography, a shipment reference, privacy links, and an encrypted connection can all be fabricated.
Once submitted, the credentials leave the victim’s control. A failure message does not mean the form rejected or forgot them.
Step 6: Stolen Access Supports Parcel and Payment Fraud
The attacker can search the mailbox for active deliveries, shopping accounts, invoices, and saved personal information.
Password-reset links may allow entry into retailer accounts. Stored payment methods, loyalty balances, and delivery addresses can then become exposed.
For commercial accounts, criminals may observe high-value shipments or impersonate a carrier representative. They can also send modified invoices to known partners.
Reused credentials broaden the damage. A password first captured by a fake delivery page may unlock unrelated services within minutes.
How to Verify a Shipment Hold Notice
Track the Parcel From an Independent Route
Open the retailer’s order history or type the carrier address yourself. Enter the tracking number from the genuine purchase confirmation.
A real hold should appear in that record with a dated scan, facility, exception code, or delivery instruction.
If the email’s number returns no result, do not assume the parcel is too new. Contact the seller using the marketplace or receipt.
Match the Message to a Real Purchase
Identify the merchant, order date, delivery address, and expected carrier. The suspicious email may avoid all four because it knows none of them.
Check whether the retailer already supplied a tracking link through its own application. Conflicting carrier names or reference numbers are important warnings.
Businesses should compare the notice with receiving logs and purchase orders. An unexpected shipment deserves verification with procurement staff.
Examine the Sender and Hidden Link
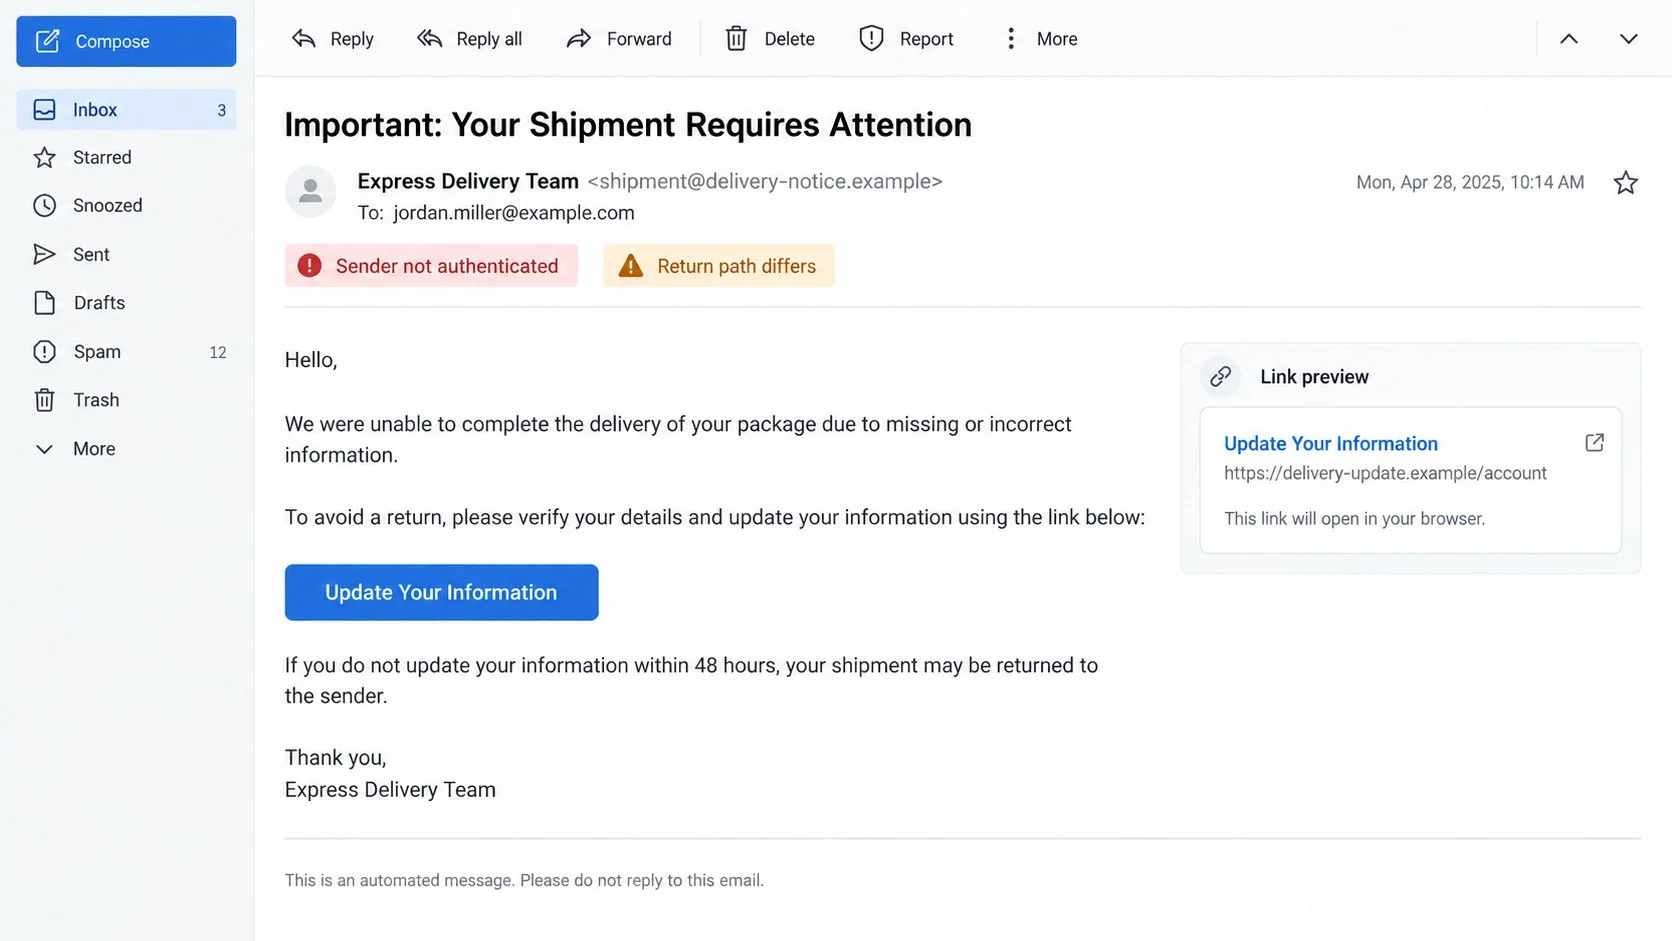
Expand the sender details and look beyond a display name such as “Express Delivery Team.” Compare the address with prior verified notifications.
Preview the update button. A domain unrelated to the carrier is enough reason to stop, even when the page contains authentic-looking logos.
Watch for redirects and shortened links. The address after the browser finishes loading matters as much as the original preview.
Contact the Carrier or Seller Using Known Details
Use the support number shown in the official application, previous receipt, or carrier website. Do not use contact information supplied only by the suspicious email.
Provide the tracking number without sharing a password. A representative can determine whether an address correction or pickup arrangement is genuinely needed.
When the sender is a retailer, its support team may resolve the exception. The carrier should never require access to your private inbox.
What to Do If You Fell Victim to the DHL Shipment on Hold Scam
Act according to the information you supplied. A mailbox credential requires immediate containment, while a simple click usually calls for observation and reporting.
- Close the fraudulent delivery page.
Do not complete another form or enter a different password. Save the original email, full headers, link, and any reference shown.
If a parcel truly is expected, handle it later through independent tracking. Separating recovery from delivery prevents another rushed decision.
- Secure the exposed email account.
Visit the real mail provider directly and create a unique password. Use account recovery immediately if the attacker has already changed access.
Replace reused credentials elsewhere, especially on retailer, payment, carrier, and cloud accounts. Similar passwords can also be guessed.
- Review sessions and security settings.
Terminate unfamiliar logins and inspect recovery addresses, telephone numbers, connected applications, and application passwords. Remove every unknown change.
Check forwarding rules and filters for hidden copies of order or payment messages. Examine sent and deleted folders for impersonation.
- Protect shopping and delivery accounts.
Change retailer and carrier passwords when they match the captured credential. Review orders, address books, saved cards, loyalty points, and recent returns.
Contact sellers about unauthorized changes. Ask carriers to flag rerouting or pickup requests associated with active shipments.
- Contact financial providers when necessary.
If card details, bank information, or unauthorized purchases are involved, call the institution using the number on the card or statement.
Dispute transactions promptly and follow its replacement guidance. Preserve receipts, screenshots, and case references.
- Scan suspicious downloads and strengthen browsing protection.
The analyzed page sought credentials, but related delivery campaigns can attach malicious archives. Scan anything opened with Malwarebytes and remove detected threats.
AdGuard can block many known phishing redirects and malicious advertising chains. Keep browser and security tools updated while treating every parcel notice independently.
- Report impersonation and alert other recipients.
Mark the email as phishing and report the counterfeit page to the carrier through its official abuse channel. Workplace recipients should notify security personnel.
Warn contacts if the mailbox sent fake shipping notices. Share neutral details rather than forwarding the live message.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why Parcel Lures Work So Often
Online shopping creates a steady background of deliveries. People may not remember which retailer selected which carrier for every order.
Households also share addresses. A message can seem relevant even when the recipient personally ordered nothing.
Delivery exceptions are believable and time-sensitive. Nobody wants a needed parcel returned because of one missing detail.
The scam exploits that concern without making an extraordinary promise. It asks for cooperation, not greed, which can lower skepticism.
Mobile screens compound the problem because the full sender and URL are less visible. A large branded button dominates what the recipient sees.
Safer Habits for Online Orders
Use retailer and carrier applications for tracking whenever possible. Their stored order history gives a stronger context than an isolated email.
Keep each shopping account behind a unique password and multifactor authentication. A breached store should not expose the mailbox or payment portal.
Avoid storing cards when convenience does not outweigh risk. Virtual card numbers can limit damage where supported.
Enable purchase and delivery notifications through trusted applications. Conflicting alerts become easier to spot when one channel has verified history.
Businesses should centralize receiving records. Staff can compare unexpected notices against known purchase orders before anyone interacts with a button.
Require independent confirmation for address or payment changes. The person approving the change should use a known vendor contact.
Delivery messages requesting email credentials should be rejected automatically. That request is unrelated to transporting or releasing a parcel.
Finally, remember that urgency is information about the persuasion attempt, not proof about the package. Verification does not cause a legitimate shipment to vanish.
When a Real Delivery Exception Exists
A genuine hold can result from an incomplete address, customs paperwork, weather, restricted access, or an unsuccessful delivery attempt.
The official tracking record should describe the exception and show where the last scan occurred. It may offer pickup, rescheduling, or verified address options.
Customs requests deserve extra care. Import duties should correspond to a real shipment and be payable through the carrier’s established billing route.
Some criminals combine leaked tracking details with a fake fee request. Possessing a real number does not prove that the payment page belongs to the carrier.
Ask the seller which carrier and service level were selected. Marketplaces often preserve that information even when an email notification has been deleted.
If a delivery address truly needs correction, begin from official tracking. Do not disclose account credentials to an agent who contacted you unexpectedly.
For high-value goods, request written confirmation of any reroute. Businesses should involve purchasing and receiving personnel before changing the destination.
A real exception remains visible after the suspicious email is closed. Independent records allow the problem to be solved without accepting the sender’s route.
Frequently Asked Questions
Is my DHL Express shipment actually on hold?
The email alone cannot establish that. Enter the genuine tracking number manually on the official carrier site or check the retailer’s order page.
Did DHL send this information-update message?
No. The analyzed campaign used an unrelated sender and destination. DHL’s branding was copied without the company’s authorization.
Would a carrier ask for my email password?
No. A delivery company does not need the secret protecting your mailbox to correct an address, schedule delivery, or release a shipment.
What if the reference matches a real parcel?
Open the official tracking record independently and contact the carrier. Attackers can obtain real shipping details from compromised accounts or leaked notifications.
I clicked the button but submitted nothing. Am I safe?
The primary credential risk requires submission. Close the page, check downloads and permissions, report the email, and monitor the account for unusual activity.
Can scammers redirect a real delivery?
They may try when they obtain carrier-account access or sufficient shipment details. Notify the seller and carrier quickly about unauthorized rerouting attempts.
The Bottom Line
The DHL Express Shipment Is on Hold email turns a common delivery concern into a password trap, hiding an unrelated login form behind an update button.
Track parcels through the seller or carrier directly. A shipping exception may require an address, but it never requires the password to your private email account.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.