


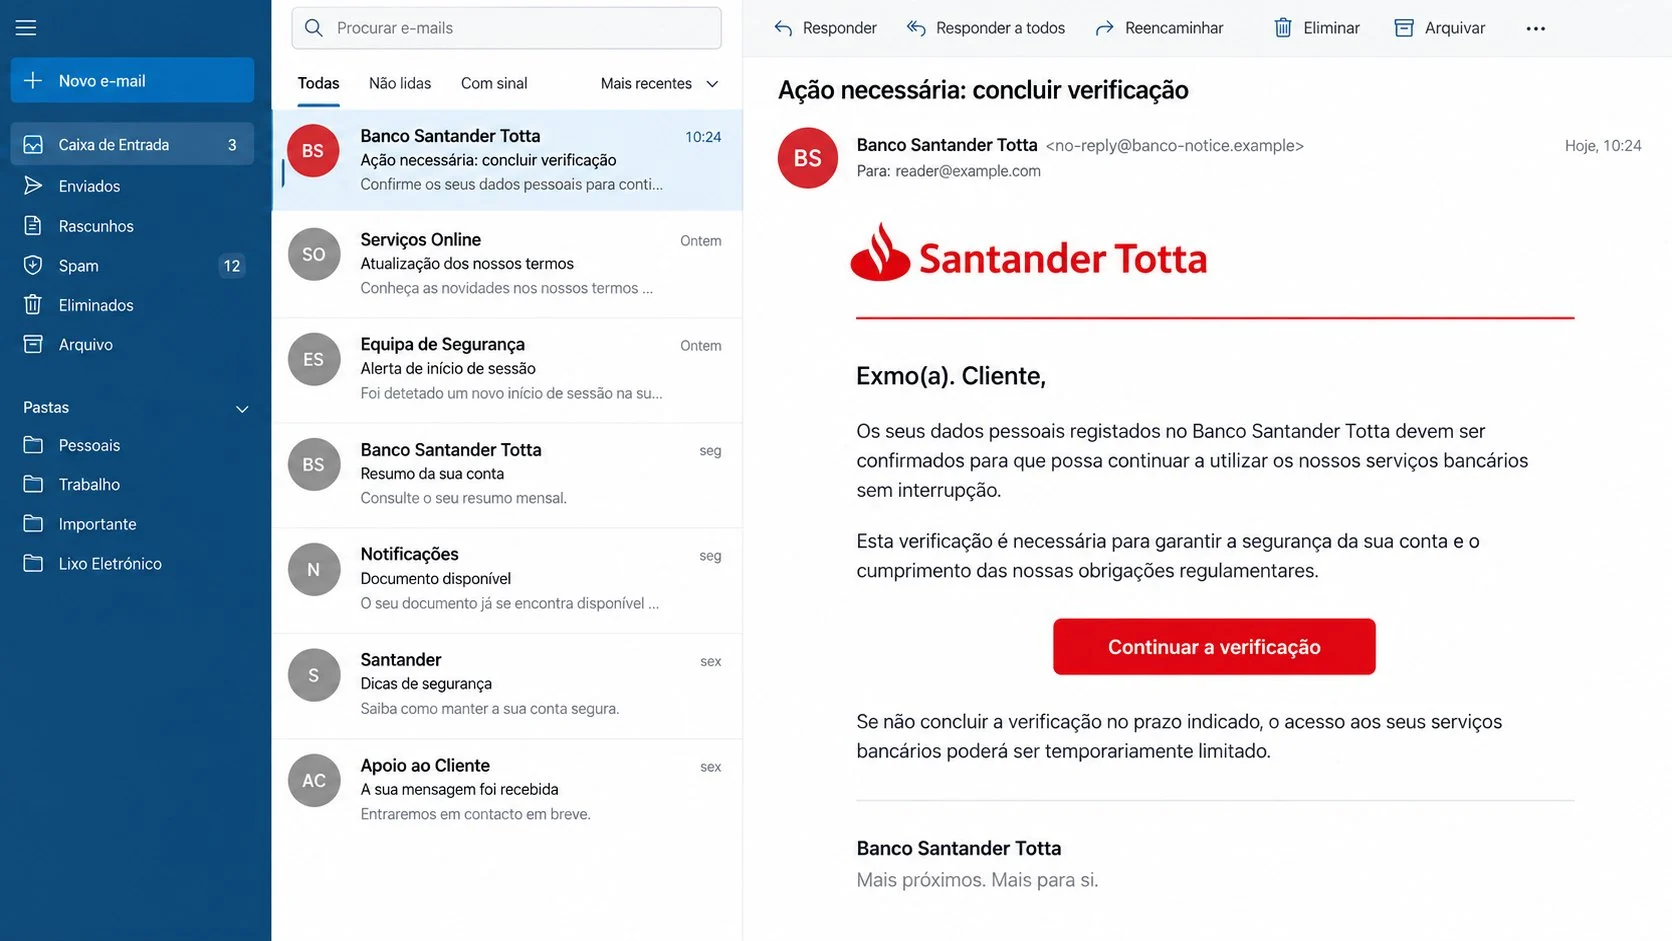
A message in Portuguese says your personal information must be confirmed to keep online banking uninterrupted. Its red button promises a quick verification process.
Account-maintenance notices are easy to take seriously, especially when they resemble a familiar bank. One small spelling change tells a very different story.
Overview
A Banking Interruption Warning Aimed at Portuguese Customers
The Santander Personal Data Confirmation email scam impersonates Banco Santander Totta and says a verification must be completed for security reasons.
Its subject reads “Ação necessária: concluir verificação,” meaning action is required to finish verification. The body warns that banking services could be interrupted.
A button marked “Continuar a verificação” offers to continue. The language is calm, but losing account access remains the pressure behind the request.
Santander and Banco Santander Totta are not responsible for this campaign. Scammers reproduced the bank’s identity to capture customer login information.
The Misspelled Domain Is a Critical Warning
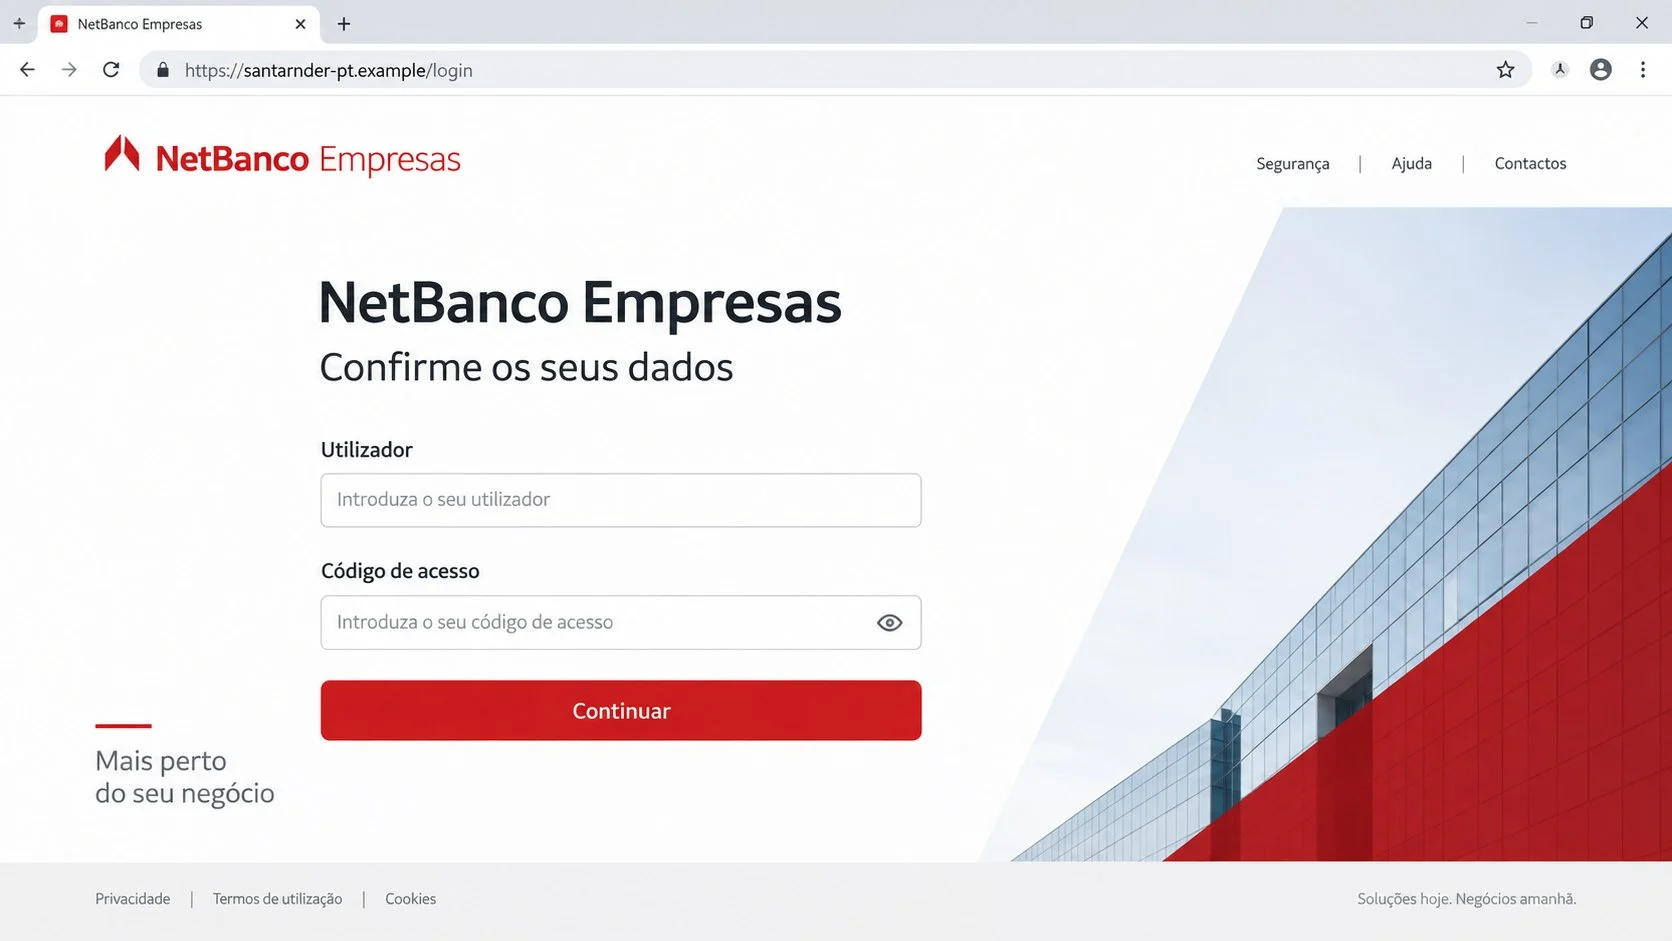
The fraudulent destination used “santarnder” rather than “santander.” The added letter is easier to miss when the reader focuses on the page’s red banking design.
- The email claims a security review must be completed.
- It threatens interruption without describing a specific account event.
- The verification button leaves the bank’s established online route.
- The destination contains a subtle spelling change.
- The copied page resembles NetBanco Empresas.
- It asks for a username and access code under criminal control.
Typosquatting domains are designed for fast reading. They preserve enough of a known name to feel right while remaining separate properties.
Credentials Can Endanger More Than the First Login
A username and access code may allow unauthorized banking attempts. The exact outcome depends on the bank’s additional verification and security controls.
Criminals may continue with calls, text messages, or counterfeit authorization screens. They can use information already submitted to make those contacts more convincing.
Reading the email does not prove that funds are at risk. The serious exposure begins when credentials, codes, card data, or personal information are supplied.
This is bank impersonation and credential phishing. It is not evidence that Santander’s legitimate systems were breached.
How the Santander Personal Data Confirmation Scam Works
Step 1: The Message Frames Verification as Routine Security
The email says personal data requires confirmation to keep banking services working. That explanation resembles genuine compliance and account-maintenance communications.
It does not mention a transaction the recipient can verify. Instead, the threat concerns future access, which is harder to disprove from the inbox.
Security language can suppress skepticism because customers expect banks to protect accounts. The scam turns that expectation into a reason to follow an unsafe link.
The subject announces necessary action without an extreme deadline. This measured tone can appear more credible than a loud “account closed” warning.
Step 2: The Button Opens a Lookalike Address
“Continuar a verificação” appears to begin the official data review. The visible button does not disclose who owns the destination.
The campaign used a domain containing “santarnder-pt.” The extra “r” creates a different name while preserving the bank-like shape at a glance.
A country reference such as “pt” can make a fraudulent address appear regional. It does not prove affiliation with a Portuguese bank.
The operator can secure the page with HTTPS. The padlock only protects the connection to that misspelled domain.
Step 3: The Site Copies NetBanco Empresas
The landing page imitates the appearance of Santander’s business-banking login. Familiar colors, labels, and spacing reduce the chance that visitors inspect the address.
It requests “Utilizador” and “Código de acesso,” terms a Portuguese customer may recognize from online banking.
A copied login interface can be assembled from publicly visible design elements. It does not require access to the legitimate bank’s servers.
The browser address remains the stronger clue. Artwork can be cloned, while a criminal cannot place the page on a domain it does not control.
Step 4: The Form Records the Banking Login
Anything typed into the counterfeit form can be transmitted to the phishing operator. The page is collecting information, not validating the customer for Santander.
After submission, it may ask for card details, telephone information, or a one-time authorization code. Each extra step expands the potential damage.
Some pages deliberately show an error and request the access code again. Repetition can capture alternatives or hide the fact that the first entry succeeded.
Never approve a bank-app notification generated during an unsolicited verification. That action may authorize a login, transfer, or newly registered device.
Step 5: A Follow-Up Caller May Pretend to Protect the Account
Submitted telephone details can support a call from someone claiming to be a fraud specialist. Caller identification can also be spoofed.
The caller may mention the verification attempt as proof of legitimacy. In reality, the scammer knows about it because the victim used the fraudulent page.
Requests to move money into a “safe account” are especially dangerous. Banks do not protect funds by asking customers to transfer them to strangers.
End the call and contact the bank through the official application or a verified number. Do not let the caller transfer you internally.
Step 6: The Domain Changes While the Banking Story Persists
Typosquatting pages can be removed quickly, so operators register replacements with new spelling variations, subdomains, or regional terms.
Email subjects can shift toward account suspension, unusual access, refunds, card expiration, or mandatory updates. The fake-login route remains the common thread.
Memorizing one bad domain offers limited protection. Read the complete address every time a financial page requests credentials.
Starting from the bank’s official application avoids guessing which email link might be safe.
How to Verify the Santander Request
Open Online Banking Independently
Use the Santander application already installed from an official store, a saved bookmark, or a known address typed manually.
Check the secure inbox and account notifications for the same verification request. Do not paste an address copied from the suspicious message.
If the request exists, complete it only inside the independently reached banking environment. If it does not, contact support before taking action.
Read the Domain One Character at a Time
Compare the address with the bank’s established domain. Pay attention to inserted letters, swapped characters, hyphens, unfamiliar endings, and misleading subdomains.
The “santarnder” spelling contains an extra letter. On a small screen, the browser may shorten the address and make that difference less noticeable.
Tap the address bar to reveal the complete hostname before entering anything. Search-result advertisements should not replace a verified bookmark.
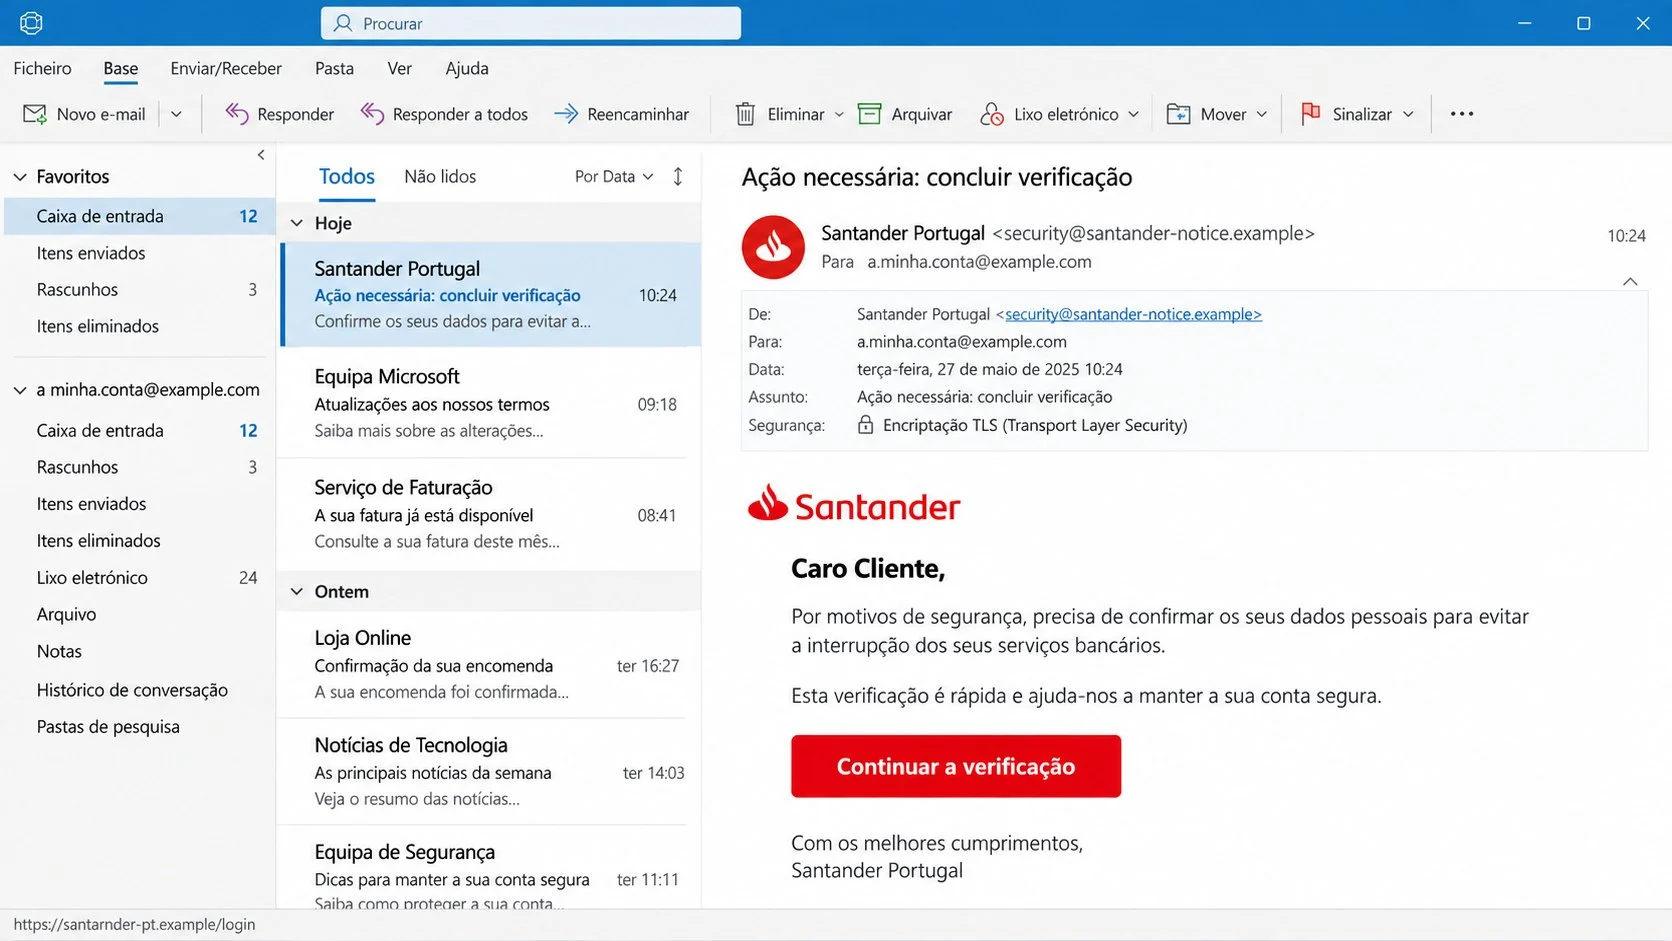
Check the Email’s Full Technical Details
Expand the sender information instead of trusting “Santander Portugal” as a display name. Anyone can type a bank name into that field.
Compare the sender, reply address, and button destination. Several unrelated domains inside one security notice are a strong reason to stop.
Email authentication results can help administrators investigate, but ordinary recipients should not use passing technical labels as permission to disclose banking credentials.
Call the Bank Using a Trusted Contact Route
Use the number printed on your card, shown within the official application, or published on the bank’s independently opened website.
Tell the representative exactly what the email claims. Ask whether personal-data confirmation is pending and whether any unfamiliar login attempt occurred.
Never call a number supplied by the questionable email. A convincing support agent can be another stage of the same operation.
What to Do If You Fell Victim to the Santander Data Confirmation Scam
Bank phishing requires immediate contact with the financial institution. Do not wait for a visible transaction before reporting exposed credentials or authorization codes.
- Stop using the counterfeit page.
Close the site without entering more information. Keep the email, address, screenshots, and approximate submission time for the bank’s fraud team.
Do not return to check whether the page still works. A changed version may request additional secrets or distribute harmful files.
- Contact Santander through an official channel immediately.
Use the application, card number, or independently verified website. Explain which username, access code, card details, and personal data were exposed.
Follow the bank’s instructions for blocking access, replacing credentials, or securing payment instruments. Only the bank can assess current account activity.
- Reject unexpected approvals and inspect transactions.
Review transfers, payees, card charges, device registrations, and login alerts. Report every item you do not recognize.
Do not approve a prompt because a caller says it reverses fraud. Read what the banking application states the approval will authorize.
- Replace reused credentials and secure your email.
If any submitted secret protects another account, change it there immediately. Use unique values rather than predictable variations.
Strengthen the email account connected to banking. Its messages may contain alerts and recovery links valuable to an attacker.
- Prepare for impersonation calls and messages.
Criminals may quote your name, bank, or recent submission to sound informed. Knowledge of those facts does not prove they represent Santander.
End every unsolicited financial call and redial a verified number. Never transfer money into a supposed protective account.
- Check the device if unexpected content ran.
The analyzed path used a web form, but related campaigns can introduce files or extensions. Run Malwarebytes if anything downloaded or installed.
AdGuard provides another layer against many malicious domains and deceptive advertisements. Keep browser and operating-system security updates enabled as well.
- Report identity or financial harm.
File the email through your provider’s phishing controls and send its details to the bank’s official fraud channel.
If money moved or identity documents were exposed, contact the appropriate Portuguese authorities. Keep transaction records, reports, and bank correspondence together.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Why a Single Extra Letter Matters
Human readers recognize word shapes quickly. That useful skill also makes carefully placed extra letters difficult to notice during a stressful account warning.
The fraudulent name begins with the expected bank spelling and adds a regional marker. Those familiar pieces can outweigh the odd character during a glance.
Mobile browsers may hide paths or shorten hostnames. Opening the address bar before authentication provides a clearer view of who controls the page.
No spelling check should stand alone. Attackers can register completely unrelated domains and still create perfect banking artwork.
The strongest routine is behavioral: ignore unsolicited login buttons, open the banking application yourself, and verify warnings inside the protected account.
That approach works even when the fraudulent domain looks flawless and the email contains no grammatical errors.
Banking Actions That Should Never Begin With Blind Trust
A bank may legitimately update customer records, but the customer must know which protected channel receives the information and why it is required.
Identity reviews often involve sensitive documents. Upload them only after independently reaching the bank and confirming the exact request inside your account.
No employee should ask for a complete access code by email, text, or telephone. Authentication secrets are meant for the bank’s verified interface.
One-time codes deserve equal protection. Their short lifetime does not make them harmless because they may authorize an immediate high-risk action.
Read every approval screen in full. A caller may describe “cancellation” while the banking application clearly states that a payment is being authorized.
Fraud teams can place protective controls without transferring money elsewhere. A “safe account” story is a signal to end the conversation.
Businesses should use dual approval for transfers and maintain verified supplier contacts. Compromised email alone should not be able to change payment destinations.
Consumers can set transaction alerts and sensible limits. Early notification cannot prevent every attempt, but it shortens the time before detection.
Keep the bank’s contact number in a trusted place. Searching during a crisis can expose sponsored impersonation pages and fraudulent support numbers.
If you feel rushed, stop. Genuine support will allow you to reconnect through an official channel rather than insisting the current session remain open.
Family members who assist vulnerable customers should agree on a verification routine. A second independent call can interrupt a persuasive social-engineering sequence.
Bank security works best when customers protect both the credential and the route. A correct password entered on the wrong domain still reaches the wrong party.
Frequently Asked Questions
Is the Santander personal data confirmation email real?
The examined version was phishing. It directed recipients to a misspelled address that imitated a NetBanco Empresas login and requested banking credentials.
What is wrong with “santarnder”?
It contains an additional “r” compared with “santander.” That subtle difference creates a separate domain controlled outside the bank’s legitimate online service.
Does the browser padlock make the page safe?
No. A padlock means the connection is encrypted. It does not confirm that Santander owns the domain or that the login form is honest.
What if I entered only my username?
Stop and notify the bank. A username can support targeted follow-up attempts, and the fraud team can advise whether any account safeguards should change.
Will Santander ask me to confirm personal data online?
Banks may conduct legitimate reviews. Begin inside the official application or independently reached website, then ask verified support when a request is uncertain.
Can the scammer call from a bank-looking number?
Yes. Caller identification can be falsified. End the call and dial a number from your card or official application rather than trusting the display.
The Bottom Line
The Santander Personal Data Confirmation scam uses a service-interruption warning and a carefully misspelled domain to place banking credentials inside a counterfeit NetBanco Empresas page.
Open financial accounts independently, inspect every hostname, and contact the bank promptly after any submission. Never authorize activity solely because an unsolicited caller or email requests it.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Community experiences
Did this happen to you?
Your experience could help someone recognize the same scam. Submit a private report for our team to review.
I experienced this tooReports are reviewed before publication. Sharing publicly is always your choice.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.