

A DHL notice says parcel 231433894819 was sent to your home address and will arrive within 3 business days. The only missing piece is a DOC file connected to the shipment.
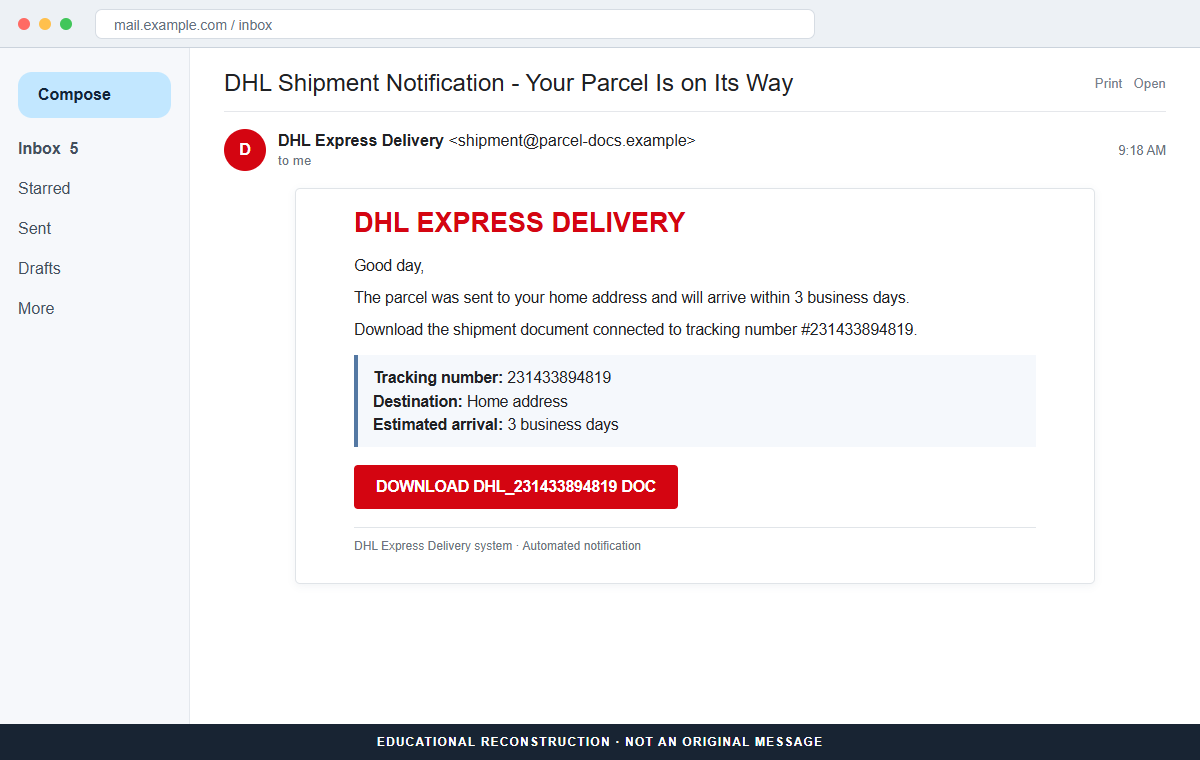
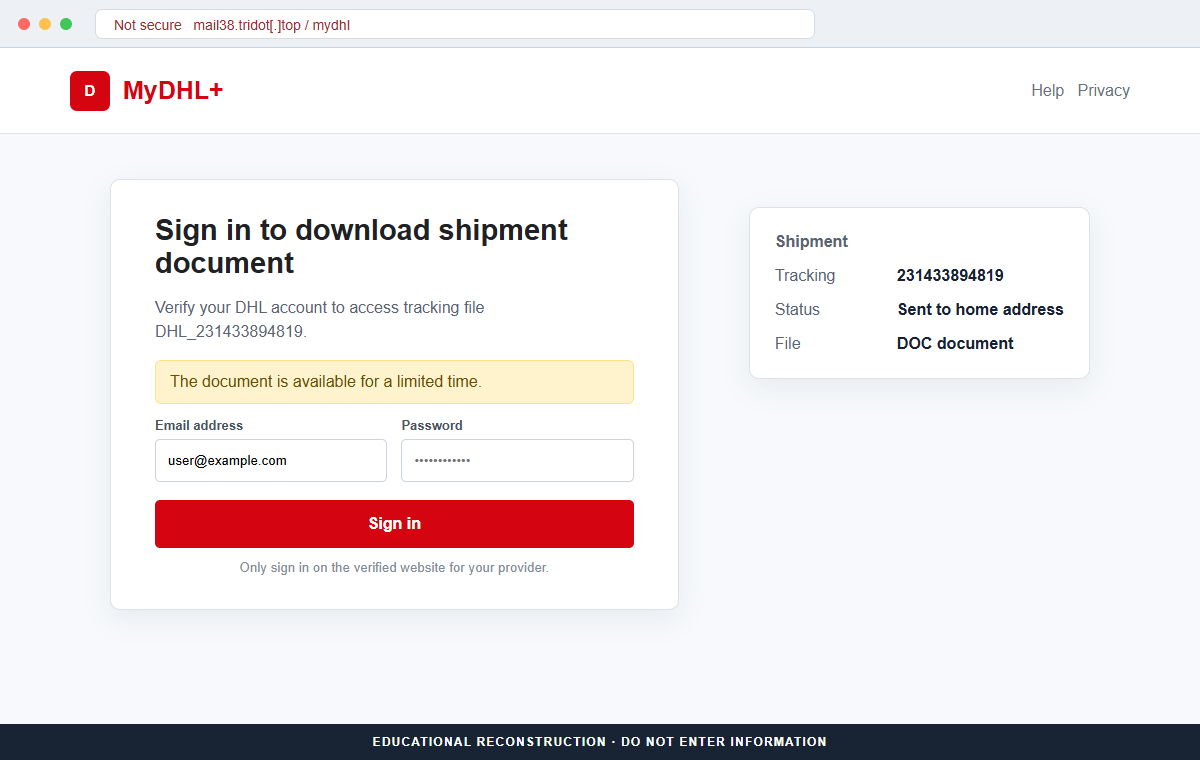
The DHL Parcel Sent to Your Home Address email scam does not deliver that document. Its download link opens a counterfeit MyDHL+ page on mail38.tridot[.]top and asks for an email address and password.
The story is designed to catch people during an ordinary moment of uncertainty. Online orders, gifts, returns, and business deliveries make an unfamiliar tracking number seem possible even when the recipient cannot place it immediately.
DHL International GmbH is not involved in the campaign. The company name, delivery colors, tracking language, and login design were copied to make an unrelated credential form appear trustworthy.
Overview
The email promises a parcel within 3 business days
The subject says DHL Shipment Notification – Your Parcel Is on Its Way. The body claims the parcel was sent to the recipient's home address and provides tracking number 231433894819.
The wording contains obvious errors such as adress and buisness, but the delivery promise and specific number may still persuade someone who is expecting several orders.
The DOC download is only a pretext
The recipient is told to download DHL_231433894819 in DOC format. A real tracking update normally displays the shipment status in the message or on DHL's official tracking page.
The link does not provide a document. It leads to mail38.tridot[.]top, where the campaign imitates the MyDHL+ portal and requests account credentials.
A stolen DHL login can expose shipment data
Credentials entered on the fake page can be captured by the attacker. A compromised DHL account may contain saved addresses, scheduled shipments, contact details, billing records, and payment information.
Password reuse expands the risk. If the same password protects email, shopping, or another service, criminals may test it elsewhere after confirming it works on the victim's DHL account.
- The subject says a DHL parcel is on its way.
- Tracking number 231433894819 is used to make the message specific.
- Delivery is promised within 3 business days.
- The recipient is told to download a DOC file.
- The message misspells address and business.
- The link opens mail38.tridot[.]top instead of dhl.com.
- A copied MyDHL+ login requests an email address and password.
- DHL has no connection with the campaign.
Why an Unknown Parcel Can Still Feel Like Your Parcel
Many households receive packages ordered by several people, subscription services, online marketplaces, and gift senders. A recipient may not recognize every merchant or carrier notice immediately.
A tracking number acts like evidence even when it is invented. The long numeric string resembles a carrier reference and encourages the reader to click rather than first check the retailer that supposedly sent the order.
Home-address language makes the delivery personal while remaining generic. The email does not need to know the address because it never displays it, but the recipient may mentally supply that missing detail.
The promised DOC file introduces curiosity. It may sound like a delivery note, customs form, sender information, or proof of shipment, so opening it appears to resolve why the parcel is unfamiliar.
The campaign finally switches from tracking to authentication. A MyDHL+ login seems reasonable after the recipient has already accepted the idea that account-only shipment details are waiting.
What DHL's Official Fraud Guidance Confirms
DHL warns that phishing emails and fake websites are designed to steal passwords, card numbers, and bank information. The company asks customers to report suspicious messages to phishing@dhl.com.
Official DHL communications use DHL-controlled domains, including dhl.com and recognized country or corporate variants. DHL says it does not link customers to unrelated websites for account actions.
mail38.tridot[.]top fails that basic identity check. A page can reproduce the yellow and red colors, MyDHL+ name, tracking number, and login fields without being connected to DHL.
The shipment can be checked by manually opening DHL tracking and entering 231433894819. The result from the official service, together with the retailer's order history, is more reliable than the page supplied by the message.
The documented campaign is credential phishing, not a confirmed malicious DOC attachment. The file is promised in the email, but the link leads to a login page rather than delivering the stated document.
How the DHL Parcel Sent to Your Home Address Email Scam Works
Step 1: A delivery notification creates curiosity
The inbox receives a message with DHL branding and a subject saying a parcel is on its way. Delivery alerts are common enough that the recipient may open it without remembering a specific order.
The sender display name can include DHL Express Delivery even when the underlying address belongs to an unrelated service. The brand label is not authentication.
Step 2: Tracking number 231433894819 supplies false precision
The body identifies tracking number 231433894819 and says the parcel was sent to the home address. A 3-business-day arrival window makes the claim feel current.
The message does not identify the sender, retailer, actual destination, package weight, service level, or scan history. Those omissions matter because they prevent independent matching.
Step 3: A DOC download promises the missing details
The call-to-action says DOWNLOAD your DHL_231433894819 in DOC format. It suggests that the shipment document contains the information needed to recognize or manage the parcel.
A normal delivery recipient should not need a Word document to see a carrier status. Official tracking can display the event without asking the user to obtain an unknown file.
Step 4: The link opens mail38.tridot[.]top
Instead of downloading a DOC file or opening dhl.com, the click reaches an unrelated domain. A copied MyDHL+ interface fills the screen and shifts the task from tracking to login.
The domain remains the decisive clue. HTTPS and professional graphics do not transfer ownership from the person controlling tridot[.]top to DHL.
Step 5: The counterfeit portal requests credentials
The fake form asks for an email address and password to access the shipment. The tracking number and document name may be repeated beside the fields to preserve the story.
A password manager may refuse to fill a saved DHL credential because the domain is wrong. Typing it manually defeats that useful protection.
Step 6: The login is collected
Submitting the form can send the credentials to the campaign operator. An error, second prompt, or redirect can follow without changing the fact that the first entry was already exposed.
The visitor may eventually reach a real DHL page and assume the session expired. That redirect is camouflage, not proof that the earlier login was legitimate.
Step 7: Shipment and reused-password data are exploited
A captured DHL account can reveal addresses, contacts, shipment history, and saved business information. Criminals may alter details or use the data to make later delivery scams more convincing.
If the password was reused, automated attempts may target the victim's email, stores, social media, and payment services. One fake parcel can therefore create a much broader account-takeover problem.
Company and Checkout Checks
Track the number on dhl.com
Type the official DHL address yourself or use the carrier's saved application. Enter 231433894819 and compare the status, sender, origin, destination, and dates with the email.
A tracking number that returns no result, belongs to another shipment, or lacks the promised details should not be rescued by a login page on another domain.
Check the retailer or sender
Review recent orders, marketplace messages, return records, and household purchases. A genuine shipment should connect to a merchant, person, or business process outside the suspicious email.
Contact the seller using the order history, not information inside the notice. Ask which carrier and tracking number were assigned.
Compare the sender and link domains
DHL lists the domains used for official communications and says it never uses free mail services. Inspect both the From address and final link before entering information.
mail38.tridot[.]top is not a DHL domain. The word DHL in a page title, path, button, or image cannot change that ownership.
Report the message without opening the link
DHL asks users to attach suspicious emails to a new message and send them to phishing@dhl.com. A workplace recipient should also notify the security team.
Preserve headers before deletion. They can help identify the sender infrastructure and protect other recipients from the same campaign.
Warning Signs to Check Before You Act
- An unexpected DHL parcel is supposedly headed to the home address.
- The message does not name the retailer or sender.
- Tracking number 231433894819 cannot be matched to an order.
- Address and business are misspelled.
- A DOC file is required to view basic shipment details.
- The button does not lead to dhl.com.
- The final domain is mail38.tridot[.]top.
- A MyDHL+ login appears on an unrelated host.
- The page asks for credentials before showing the parcel.
- A password manager refuses to autofill the DHL password.
- Official DHL tracking shows no matching shipment.
- The message pressures the user to act within a short delivery window.
The tracking number is not proof of a parcel, and the copied login is not proof of DHL. A genuine shipment should survive independent checks through the retailer and dhl.com. This campaign fails at the moment its DOC download becomes a login on mail38.tridot[.]top.
What to Do if You Have Fallen Victim to This Scam
- Change the exposed password immediately. Open DHL tracking or MyDHL+ through a saved bookmark or its official application, not through the DHL home-address parcel message. Create a strong, unique password and replace it anywhere the same or a similar password was reused.
- Enable stronger multi-factor authentication. Prefer a passkey, hardware security key, or authenticator app when available. Review the methods already registered and remove telephone numbers, recovery addresses, app passwords, or security keys you do not recognize.
- Revoke active sessions and connected applications. Sign out other sessions and inspect OAuth access, browser sessions, mail clients, and third-party applications. A criminal may retain access through an issued token even after the primary password has changed.
- Inspect mailbox rules and forwarding settings. Remove unknown forwarding addresses, delegates, filters, automatic replies, and rules that hide security messages. Review sent mail, trash, deleted messages, and account-recovery notifications for activity you did not initiate.
- Secure accounts that use the mailbox for recovery. Prioritize banking, payment services, cloud storage, shopping, social media, workplace tools, and password managers. Change credentials wherever the compromised inbox could receive a reset link or approval request.
- Protect the service impersonated by the email. Review saved DHL addresses, shipments, contacts, and payment methods through its official account and contact support through a verified channel. Remove unknown addresses, payment methods, documents, devices, or profile changes associated with the scam's story.
- Scan the device if anything was downloaded. Run a complete scan with Malwarebytes or another trusted security product if the page delivered a file, browser extension, or remote-support tool. Remove unfamiliar software and install operating-system and browser updates.
- Add a blocking layer for future attempts. AdGuard or another reputable DNS and content blocker can stop some known phishing pages and malicious advertising from loading. Continue checking addresses because new campaign domains may appear before blocklists update.
- Report the phishing message. Use the mail provider's Report Phishing control and notify DHL at phishing@dhl.com and your workplace security team. Preserve the full message and headers first, especially if multiple employees or customers received the same lure.
- Warn contacts if the account was misused. Contact colleagues, customers, friends, and vendors through another channel. Ask them to ignore recent links, password requests, file shares, shipment notices, or payment instructions sent during the possible compromise window.
- Reject unsolicited recovery offers. A caller or email sender who promises to recover the account or lost money for an advance payment may be extending the fraud. Work only with the provider, financial institution, employer, police, or a verified incident-response professional.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. The fastest way to find out is to scan your device with Malwarebytes Free — one of the most trusted malware removal tools available.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan and clean your PC in just a few minutes.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Enable “Scan for Rootkits”
Before scanning, turn on rootkit detection so Malwarebytes can find even the most hidden threats. Click the Settings gear icon on the left side of the screen.

In the settings menu, find “Scan for rootkits” and click the toggle so it turns blue.

Done? Click “Dashboard” in the left pane to return to the main screen.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

That’s it — your Windows PC is now clean of trojans, adware, and other malware, and should be back to running smoothly.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan and clean your Mac in just a few minutes.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, your Mac is clean.

That’s it — your Mac is now free of adware, rogue browser extensions, and other potentially harmful software.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android automatically detects and removes dangerous threats like malware and ransomware so you don’t have to worry about your most-used device being compromised. Aggressive detection of adware and potentially unwanted programs keeps your Android phone or tablet running smooth.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes will open, you will see the Malwarebytes Setup Wizard which will guide you through a series of permissions and other setup options.
This is the first of two screens that explain the difference between the Premium and Free versions. Swipe this screen to continue.
Tap on “Got it” to proceed to the next step.
Malwarebytes for Android will now ask for a set of permissions that are required to scan your device and protect it from malware. Tap on “Give permission” to continue.
Tap on “Allow” to permit Malwarebytes to access the files on your phone.
-
Update database and run a scan with Malwarebytes for Android
You will now be prompted to update the Malwarebytes database and run a full system scan.

Click on “Update database” to update the Malwarebytes for Android definitions to the latest version, then click on “Run full scan” to perform a system scan.

-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Click on “Remove Selected”.
When the scan has been completed, you will be presented with a screen showing the malware infections that Malwarebytes for Android has detected. To remove the malicious apps that Malwarebytes has found, tap on the “Remove Selected” button.

-
Restart your phone.
Malwarebytes for Android will now remove all the malicious apps that it has found. To complete the malware removal process, Malwarebytes may ask you to restart your device.
That’s it — your Android phone is now clean — no more malicious apps, adware, or browser redirects.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Restore your phone to factory settings by going to Settings > General management > Reset > Factory data reset.
- Ask for help in our Mobile Malware Removal Help & Support forum.
Stay Protected: Block Ads and Malicious Sites
Now that your device is clean, keep it that way. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
Frequently Asked Questions
Is the DHL parcel-to-home email genuine?
No. The documented message uses tracking number 231433894819 and sends recipients to a fake MyDHL+ login on mail38.tridot[.]top.
Is tracking number 231433894819 real?
The number in an email is only text. Enter it on DHL's official tracking page and compare the result with an actual order before trusting it.
Why does the email offer a DOC file?
The promised document creates a reason to click. In the examined campaign, the link opens a phishing login rather than delivering the stated file.
What if I clicked but entered nothing?
Close the page, report the message, and review browser downloads. If no credential was submitted and no file was opened, account theft is less likely.
What if I entered my DHL password?
Change it through the real MyDHL+ service, revoke sessions, review addresses and shipments, remove unfamiliar payment details, and replace the password anywhere it was reused.
How can I report a fake DHL email?
Attach the suspicious message to a new email and send it to phishing@dhl.com. Workplace users should also inform their security team.
The Bottom Line
The DHL Parcel Sent to Your Home Address email scam uses a specific tracking number and 3-day delivery promise to make an unknown parcel feel urgent. Its DOC download is only a bridge to a counterfeit MyDHL+ login.
Check the shipment through the retailer and dhl.com. mail38.tridot[.]top is not a DHL domain, regardless of its colors, logo, or repeated tracking number.
If credentials were entered, change them promptly, revoke sessions, review the DHL account, protect every service using the same password, and report the campaign before the stolen account is used again.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.