


A familiar Cherry page opens, and joining looks easy. There is a name you recognize, a clean layout, and a prompt to get started.
Before you let that page near a wallet, it is worth checking where this particular invitation has taken you.
Overview
The copycat used a separate claim-themed address
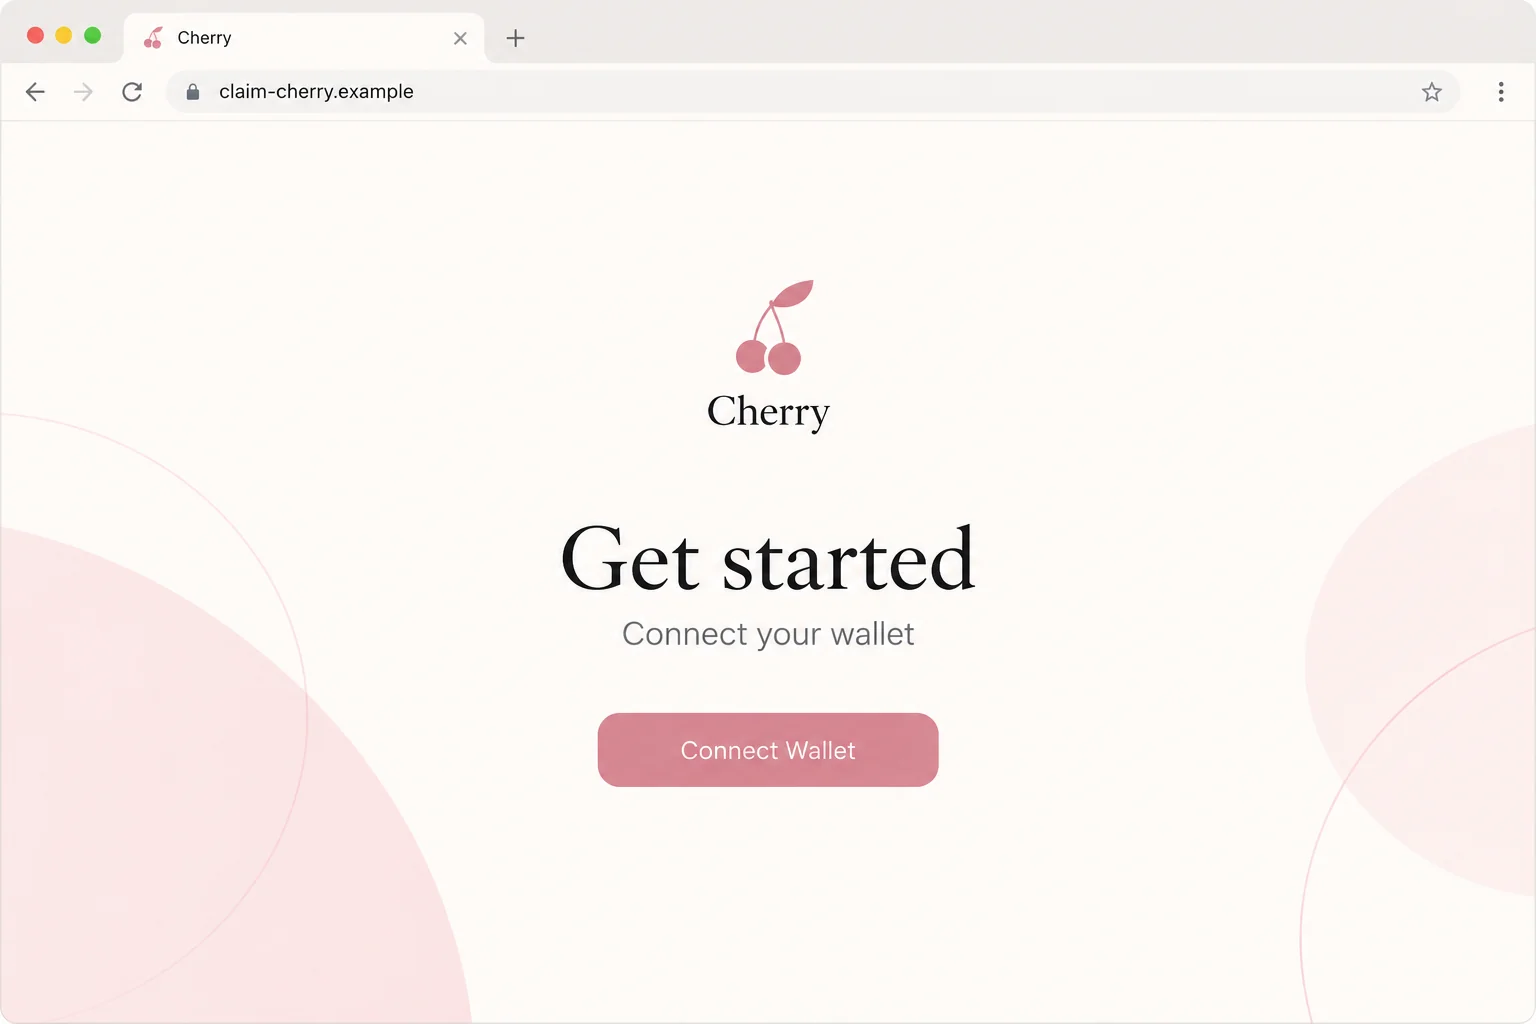
The reported counterfeit was hosted at claim-cherry[.]info. It imitated Cherry’s website and invited visitors to connect a wallet under a getting-started pretext.
The real Cherry service uses cherry.fun. Its current website describes chat, communities, games, and trading features, rather than making every page bearing its name official.
A copied interface is especially misleading when wallet connections already seem normal for the service. The visitor may recognize the activity without checking the operator.
A social invitation can become a financial decision
People may approach a community platform expecting conversation, not a high-stakes financial action. A wallet prompt can appear to be a small part of joining.
Keep these details in view before taking the next step:
- The reported impersonation address was claim-cherry[.]info, not cherry.fun.
- The entry page encouraged a wallet connection.
- A wallet connection and a signed transaction have different consequences.
- A copied community interface does not authenticate the person requesting access.
The fake page was reported as a crypto-theft lure. Its exact post-connection transaction was not independently inspected, so no specific draining instruction is asserted here.
The warning concerns the impersonator, not every Cherry user
Cherry’s genuine platform should not be confused with the separate counterfeit. This is not a finding that the legitimate service created or endorsed that copy.
The illustration above uses a fictional example address. It explains the invitation style without pretending to be a live capture of the removed or unavailable page.
For anyone who already interacted, the useful question is concrete: what did the wallet authorize, and was any secret information shared?
How the Fake Cherry Website Scam Works
Step 1: An invitation makes a new page feel like a familiar destination
A counterfeit service does not need an elaborate story. Sometimes it only needs to appear at the moment someone expects to join a group or explore an application.
A friend might forward a link without inspecting it. A visitor might encounter a claim-style address while browsing. Neither scenario authenticates the destination.
Those are common ways unfamiliar links reach people, not a claim about a specific advertisement or message used in this case.
The essential shift happens when recognition takes over from verification. You see Cherry, assume you have arrived at Cherry, and begin following the page’s instructions.
At that stage, pause before choosing a wallet. Check the complete address while you can still leave without having authorized anything.
Step 2: The copied appearance hides a change of operator
The reported page resembled the real service closely enough to borrow its credibility. A visitor could focus on the familiar layout instead of the separate domain.
But a website’s appearance and its owner are different things. Images, navigation labels, and brand names can be reproduced on infrastructure controlled by someone else.
The word claim in an address may sound like an official feature. It does not establish that the project created a claim program or approved that website.
For comparison, open Cherry’s established website independently. Follow only destinations that can be traced back to its authenticated communications.
This is an identity check, not an endorsement of every app, asset, or community on the real platform. Genuine services can still involve financial risk.
Step 3: Getting started becomes a wallet connection
The counterfeit invitation moves the visitor from reading a page to interacting with a wallet. That is where a casual visit starts requiring deliberate attention.
A basic connection can expose a public address and let an application request further actions. It is not the same as handing over recovery words.
It also is not automatically a transfer. This distinction helps you avoid both complacency and panic when deciding what happened.
The wallet window should identify the requesting site. Read it separately from the page’s reassuring words, especially if several tabs or applications are open.
Do not switch to a different browser, install an unfamiliar extension, or disable protections merely because the copycat says your usual connection method is failing.
Step 4: The next request may do more than join a community
A malicious site can present an authorization as a membership check or routine setup. The risk lies in what the wallet actually permits, not that explanation.
Depending on the network, an approval might grant token access, while a transaction might move assets immediately. Other signatures can have consequences that deserve careful review.
The historical page’s exact request remains unconfirmed. Do not assume an EVM approval checker describes every risk on Solana or that one network’s instructions fit another.
If a wallet request shows an outgoing asset when you expected a simple sign-in, stop. A community invitation is not a reason to ignore a financial action.
Similarly, an application has no legitimate need to collect your recovery phrase merely to let you read a group. Do not type those words into a website.
You can reject the request and leave. A page that makes cancellation feel like losing access to something valuable is still not entitled to your authorization.
Step 5: Confusion after the interaction can invite another loss
A victim may return to the page, hoping to undo a mistake. That gives the same operator another chance to ask for a signature or payment.
Others may seek help in public replies and attract unsolicited recovery messages. An account promising assistance is not necessarily connected to Cherry or your wallet provider.
Bring the incident back to tools and channels you already trust. Use the wallet’s own activity view, not a balance counter on the suspicious website.
If assets moved, preserve the transaction identifier. If nothing moved but an authorization was approved, investigate that permission rather than waiting for a loss to appear.
Do not send a test deposit to see whether the wallet is safe. If access is compromised, the new deposit may simply add to the damage.
Joining a Community Should Not Require Blind Trust
Verify the invitation outside its own chain of links
A link that points to another reassuring page from the same sender is not independent confirmation. Return to a known application, bookmark, or established project website.
When a contact forwards a link, ask where it originated. Their account may have been compromised, or they may have copied a promotion without checking it.
A genuine conversation does not require sending your wallet secrets to prove you are human. Reject that premise even if the person seems familiar.
Be cautious with group announcements asking members to act privately. An impersonator may want to prevent anyone else from noticing the request and challenging it.
A real connection prompt can still come from a bad page
Your wallet can display a malicious website’s request accurately. The presence of the normal wallet interface therefore says little about whether you should accept.
Read the request’s origin and effect. If you cannot explain the action, do not authorize it simply because everyone else in a chat claims it works.
Watch the account you select, too. Opening a wallet containing savings for a casual community test creates an exposure that the invitation may not justify.
A small separate wallet can limit what is at stake, but it is not a fraud detector. Never reuse exposed recovery words for a supposedly safer replacement.
Separate connection privacy from spending authority
Ending a connection helps prevent continued interaction with that application. It does not necessarily remove an authorization already recorded through a separate approved action.
For Phantom users, the provider’s token-approval guidance explains why revocation and disconnection are separate procedures, including network-specific options.
Use the procedure that matches what you approved. Do not give a stranger new access because they claim to have a universal one-click cleanup for every chain.
What to Do If You Used the Counterfeit Cherry Page
Close the fake site and stop responding to its prompts. Keep a note of the address and original invitation without reopening the claim process.
Check whether you approved anything beyond the initial connection. Your own recollection and wallet activity are more useful than the page’s success or error message.
If you only visited, there is no reason to claim that the visit alone transferred your assets. Continue with checks appropriate to your actual actions.
Remove the unfamiliar application connection. Open the wallet normally and inspect its connected-applications list. Disconnect the entry associated with the counterfeit page.
Do not confuse this with deleting the wallet or erasing browser history. Those actions answer different problems and may make the incident harder to reconstruct.
After disconnection, check for relevant approved permissions separately. A disconnected site may still benefit from authority you granted through a transaction.
Get network-specific help for a suspicious approval. Use your wallet provider’s official documentation rather than an unsolicited message offering to inspect your account.
Phantom’s guide for a drained or compromised wallet provides a response path for users of that wallet.
Keep the network name and transaction details available. Instructions designed for a different chain may miss the permission or account change involved.
Replace the wallet if its secret was exposed. Recovery words or a private key entered into the copycat should be considered compromised.
Set up a new wallet through a trusted provider on a device you trust. Changing a local app password cannot take back a disclosed secret.
Move legitimate remaining assets using appropriate provider guidance. Avoid interacting with unknown tokens just to make the old wallet look empty.
Keep an evidence package that does not contain secrets. Save the invitation, page address, transaction hashes, relevant public addresses, and the time of interaction.
If the invitation came from a contact, warn them through another channel. Ask whether they sent it before assuming their account was intentionally involved.
Report the impersonation to the legitimate service and any relevant platform. Financial loss may also warrant an exchange notification and a police or cybercrime report.
Inspect software added during the visit. If you installed a wallet update, extension, or supposed connection helper, treat that as a separate device-security concern.
Use Malwarebytes to check for malicious software where appropriate. Review unfamiliar browser extensions and get help before removing a wallet extension containing access you need.
AdGuard can help reduce some advertising and redirect exposure. It does not repair wallet ownership, cancel permissions, or reimburse missing crypto.
Do not purchase a promised reversal. A person who demands an advance recovery payment or recovery phrase should not receive either.
Legitimate incident help starts with information about what happened. It should not require moving funds to an unknown address so someone can demonstrate trustworthiness.
Document follow-up attempts too. They may use details from your public complaint to sound more informed than they really are.
Is Your Device Infected? Run a Free Malware Scan
Slow performance, constant pop-ups, or strange behavior? These are classic signs of a malware infection. A quick way to check is to scan your device with Malwarebytes Free, one of the most trusted malware removal tools available. If you only visited a scam page and didn’t download or install anything, this scan is optional.
The free version detects and removes the most common threats, including:
- Adware — the cause of those annoying pop-ups
- Browser hijackers — unwanted redirects and changed homepages
- Trojans and spyware — hidden programs stealing your data
- Potentially unwanted programs (PUPs) — software you never asked for
👉 Select your device below — Windows, Mac, or Android — then follow the simple steps to download Malwarebytes, scan your system, and remove any threats it finds. The scan usually takes 5 to 20 minutes.
Run a Malware Scan with Malwarebytes for Windows
Malwarebytes is one of the most popular and trusted anti-malware tools for Windows — and it’s completely free for removing infections. It catches threats that many antivirus programs miss, including adware, browser hijackers, and trojans. Follow the steps below to scan your PC and remove what Malwarebytes finds.
Download Malwarebytes
Click the button below to download the latest version of Malwarebytes for Windows from the official source. The free version is all you need — it will scan your computer and remove adware, browser hijackers, and other malicious software at no cost.
Download MalwarebytesOfficial installer for Windows 11 and 10. Your download starts right away.Want real-time protection? See Malwarebytes Premium Malwarebytes Free for WindowsScans and removes malware at no cost
-
Install Malwarebytes
When the download finishes, open your Downloads folder and double-click the MBSetup file. If Windows shows a User Account Control pop-up, click “Yes” to allow the installation.

Follow the On-Screen Prompts to Install Malwarebytes
The setup wizard will walk you through a few quick screens:
-
Choose where you’re installing the program — “Personal Computer” or “Work Computer” — then click Next.

-
Malwarebytes will now install on your device. This usually takes under a minute.

-
When installation is complete, the “Welcome to Malwarebytes” screen will open automatically.

-
On the final screen, click Open Malwarebytes to launch the program.

-
Optional: Check for rootkits with a Custom Scan
You don’t need to change any settings for a normal scan. The standard Threat Scan in the next step is enough for most problems, so you can go straight to it.
If you also want to check for rootkits, use a Custom Scan. In current versions of Malwarebytes, rootkit scanning is only available there:
- On the Scanner tile, click the three-dot menu and select Advanced Scan.
- Choose Custom Scan. In its options, check Scan for rootkits.
- Select your system drive (usually C:\) as the location to scan, then start the scan. It takes longer than a Threat Scan.
- When it finishes, review and quarantine the results as described in the steps below.
Rootkit scanning isn’t available on Windows devices with ARM processors.
Start the Scan
Click the blue Scan button. Malwarebytes will automatically update its virus database and start checking your computer for malware.

-
Wait for the Scan to Finish
The scan checks your entire system for browser hijackers and other malicious programs, so it can take 5 to 20 minutes depending on your computer. Feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found — malware, adware, and potentially unwanted programs. Click the “Quarantine” button to remove all of them at once.

Malwarebytes will now remove the malicious files and registry entries and move them safely into quarantine.

-
Restart Your Computer
Some threats can only be fully removed after a reboot. If Malwarebytes asks you to restart, click Yes. Once you’re logged back in, Malwarebytes has finished removing the threats it found.

When the scan is done, check whether the problems you noticed have stopped. If they continue, see the options below.
If you are still having problems with your computer after completing these instructions, then please follow one of the steps:
- Run a computer scan with ESET Online Scanner
- Ask for help in our Windows Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Mac
Malwarebytes for Mac is a free on-demand scanner that removes the malware other security software tends to miss — adware, browser hijackers, and unwanted programs included. Cleaning an infected Mac with Malwarebytes has always been completely free, and it’s our go-to recommendation. Follow the steps below to scan your Mac and remove what Malwarebytes finds.
-
Download Malwarebytes for Mac
Click the button below to download the latest version of Malwarebytes for Mac.
Download MalwarebytesOfficial installer for macOS. Your download starts right away.Want real-time protection? See Malwarebytes PremiumMalwarebytes Free for MacScans and removes malware at no cost -
Open the Malwarebytes setup file
When the download finishes, open your Downloads folder and double-click the setup file to begin the installation.

-
Follow the On-Screen Prompts to Install Malwarebytes
The Malwarebytes for Mac Installer will guide you through a few quick screens. Click “Continue” and keep following the prompts until the installation completes.



When the installation is complete, Malwarebytes opens to the Welcome to Malwarebytes screen. Click “Get started“.
Malwarebytes needs Full Disk Access to check your whole Mac. When it asks, open System Settings > Privacy & Security > Full Disk Access, turn on Malwarebytes (it may be listed as Malwarebytes Protection), and confirm with your password or Touch ID. Then return to Malwarebytes. On macOS Monterey and earlier, this setting is in System Preferences > Security & Privacy > Privacy.
-
Select “Personal Computer” or “Work Computer”
Malwarebytes will ask what type of computer you’re installing it on. Click either Personal Computer or Work Computer, whichever applies.

-
Start the Scan
Click the “Scan” button. Malwarebytes will automatically update its detection database and begin checking your Mac for malware.

-
Wait for the Scan to Finish
Malwarebytes will scan your Mac for adware, browser hijackers, and other malicious programs. This can take a few minutes, so feel free to do something else — just check back occasionally to see the progress.

-
Quarantine the Detected Threats
When the scan is done, you’ll see a list of everything Malwarebytes found. Click the “Quarantine” button to remove all the threats at once.

-
Restart Your Mac
Malwarebytes will now remove all the malicious files it found. Some threats can only be fully removed after a reboot — if Malwarebytes asks you to restart, allow it. Once you’re logged back in, check whether the problems you noticed have stopped. If they come back, save the scan report and ask for help in our forum.

If the problems you noticed continue after the scan, see the options below.
If you are still experiencing problems while trying to remove a malicious program from your computer, please ask for help in our Mac Malware Removal Help & Support forum.
Run a Malware Scan with Malwarebytes for Android
Malwarebytes for Android scans your phone or tablet for malware, adware, and potentially unwanted apps. The free version scans only when you start a scan. Real-time protection, which checks apps automatically, is part of the paid Premium version.
-
Download Malwarebytes for Android.
You can download Malwarebytes for Android by clicking the link below.
Get Malwarebytes for AndroidOpens Google Play in a new tab.Want real-time protection? See Malwarebytes Premium for AndroidMalwarebytes for AndroidScans your phone and removes malware at no cost -
Install Malwarebytes for Android on your phone.
In the Google Play Store, tap “Install” to install Malwarebytes for Android on your device.

When the installation process has finished, tap “Open” to begin using Malwarebytes for Android. You can also open Malwarebytes by tapping on its icon in your phone menu or home screen.

-
Follow the on-screen prompts to complete the setup process
When Malwarebytes opens, it walks you through a short setup. Tap Get started and follow the prompts. If you see an offer for a trial or a paid plan, read it before you accept. You can skip it and keep using the free scanner.
Malwarebytes will ask for permission to access the files on your phone so it can scan them. Tap Allow, or turn on the permission in the Android screen that opens, then return to Malwarebytes.
-
Run a scan with Malwarebytes for Android
On the main screen, tap Scan now. In some versions, you open the menu, tap Scanner, and then tap Run a scan.
-
Wait for the Malwarebytes scan to complete.
Malwarebytes will now start scanning your phone for adware and other malicious apps. This process can take a few minutes, so we suggest you do something else and periodically check on the status of the scan to see when it is finished.

-
Remove the detected apps.
When the scan has been completed, you will see a list of the threats that Malwarebytes for Android has detected. Next to each detected item, tap the menu icon (three dots), then choose to uninstall the app or delete the file. Android then asks you to confirm. Tap OK or Uninstall to remove the app.
-
Restart your phone.
When the detected apps are removed, restart your phone if Malwarebytes asks you to. Then check whether the problems you noticed have stopped.
If the problems you noticed continue after the scan, see the options below.
If you are still having problems with your phone after completing these instructions, then please follow one of the steps:
- Ask for help in our Mobile Malware Removal Help & Support forum.
- Only as a last resort, reset your phone to factory settings. Read the warning below first.
- Back up your photos, videos, files, and messages, for example to your Google account or a computer.
- Make sure you know your Google account email and password. The phone asks for them after the reset. If you changed the password recently, Google recommends waiting 24 hours before you reset.
- On a Samsung phone, also make sure you know your Samsung account password.
- If you use an authenticator app for two-step verification, move your accounts to another device or save your backup codes first.
Stay Protected: Block Ads and Malicious Sites
No scan can prove a device is completely clean, so it helps to block threats before they reach you. Most infections start with a malicious ad or a fake download button — so blocking them at the source is your best defense.
We recommend AdGuard, which blocks malicious ads, phishing pages, and dangerous redirects before they can reach you.
👉 Download AdGuard and browse safely
A Better Routine for Wallet-Based Invitations
Decide what you are trying to do before connecting. Reading a community announcement, joining a chat, and making a trade are not interchangeable goals.
When the requested action suddenly changes, stop and reassess. A simple invitation should not silently grow into a transaction involving unrelated assets.
Keep a short list of verified starting points for services you use regularly. Repeatedly following new promotional links makes it easier to lose track of the origin.
For shared accounts or community teams, explain the specific counterfeit address. A precise warning helps others recognize the same page without accusing the legitimate platform.
If you need assistance, describe the wallet and network without publishing private information. A clear incident summary lets trusted support distinguish a connection concern from an executed transfer.
Give yourself permission to abandon an invitation. No community benefit is worth approving an action you cannot understand or allowing someone to hurry you through it.
Frequently Asked Questions
Is claim-cherry[.]info the same website as cherry.fun?
No. The claim-themed address was reported as an impersonation. Do not treat it as an official Cherry destination because its page looks similar.
Is the genuine Cherry service being called a scam?
No. This article addresses a separate fake website. It does not establish that Cherry operated the impersonation or endorse every activity on its real platform.
Can joining a group require a legitimate wallet connection?
Some services use wallets for access. That general fact cannot authenticate an unfamiliar invitation or justify an unrelated transfer or excessive permission.
What if I connected but rejected the next request?
Disconnect the unfamiliar application and inspect wallet activity. A rejected request is different from an approved transaction, so do not assume assets moved without checking.
Can the wallet provider reverse a completed theft?
A self-custodial wallet provider generally cannot reverse completed blockchain transfers. Report promptly anyway, and preserve details that may help exchanges or investigators.
Will a malware scan remove a malicious wallet approval?
No. Scanning addresses software on the device. Wallet permissions and exposed keys require their own response, even when the computer scan finds nothing.
The Bottom Line
Do not connect or sign through claim-cherry[.]info. The counterfeit borrows Cherry’s identity to make a risky wallet interaction feel like ordinary account setup.
If you already used it, review the authorization, disconnect the application, and protect remaining assets. Get wallet-specific help without sharing secrets or paying a recovery stranger.

Join the discussion
0 commentsShare your experience or ask a question about this article.
Discussion
Start the conversation
Have a question or something useful to share? Add the first comment.